 stepsecurity.ioarticle
Team PCP Stole 78,330 Secrets From 2,186 Organizations. CloudSEK Just Published the List.
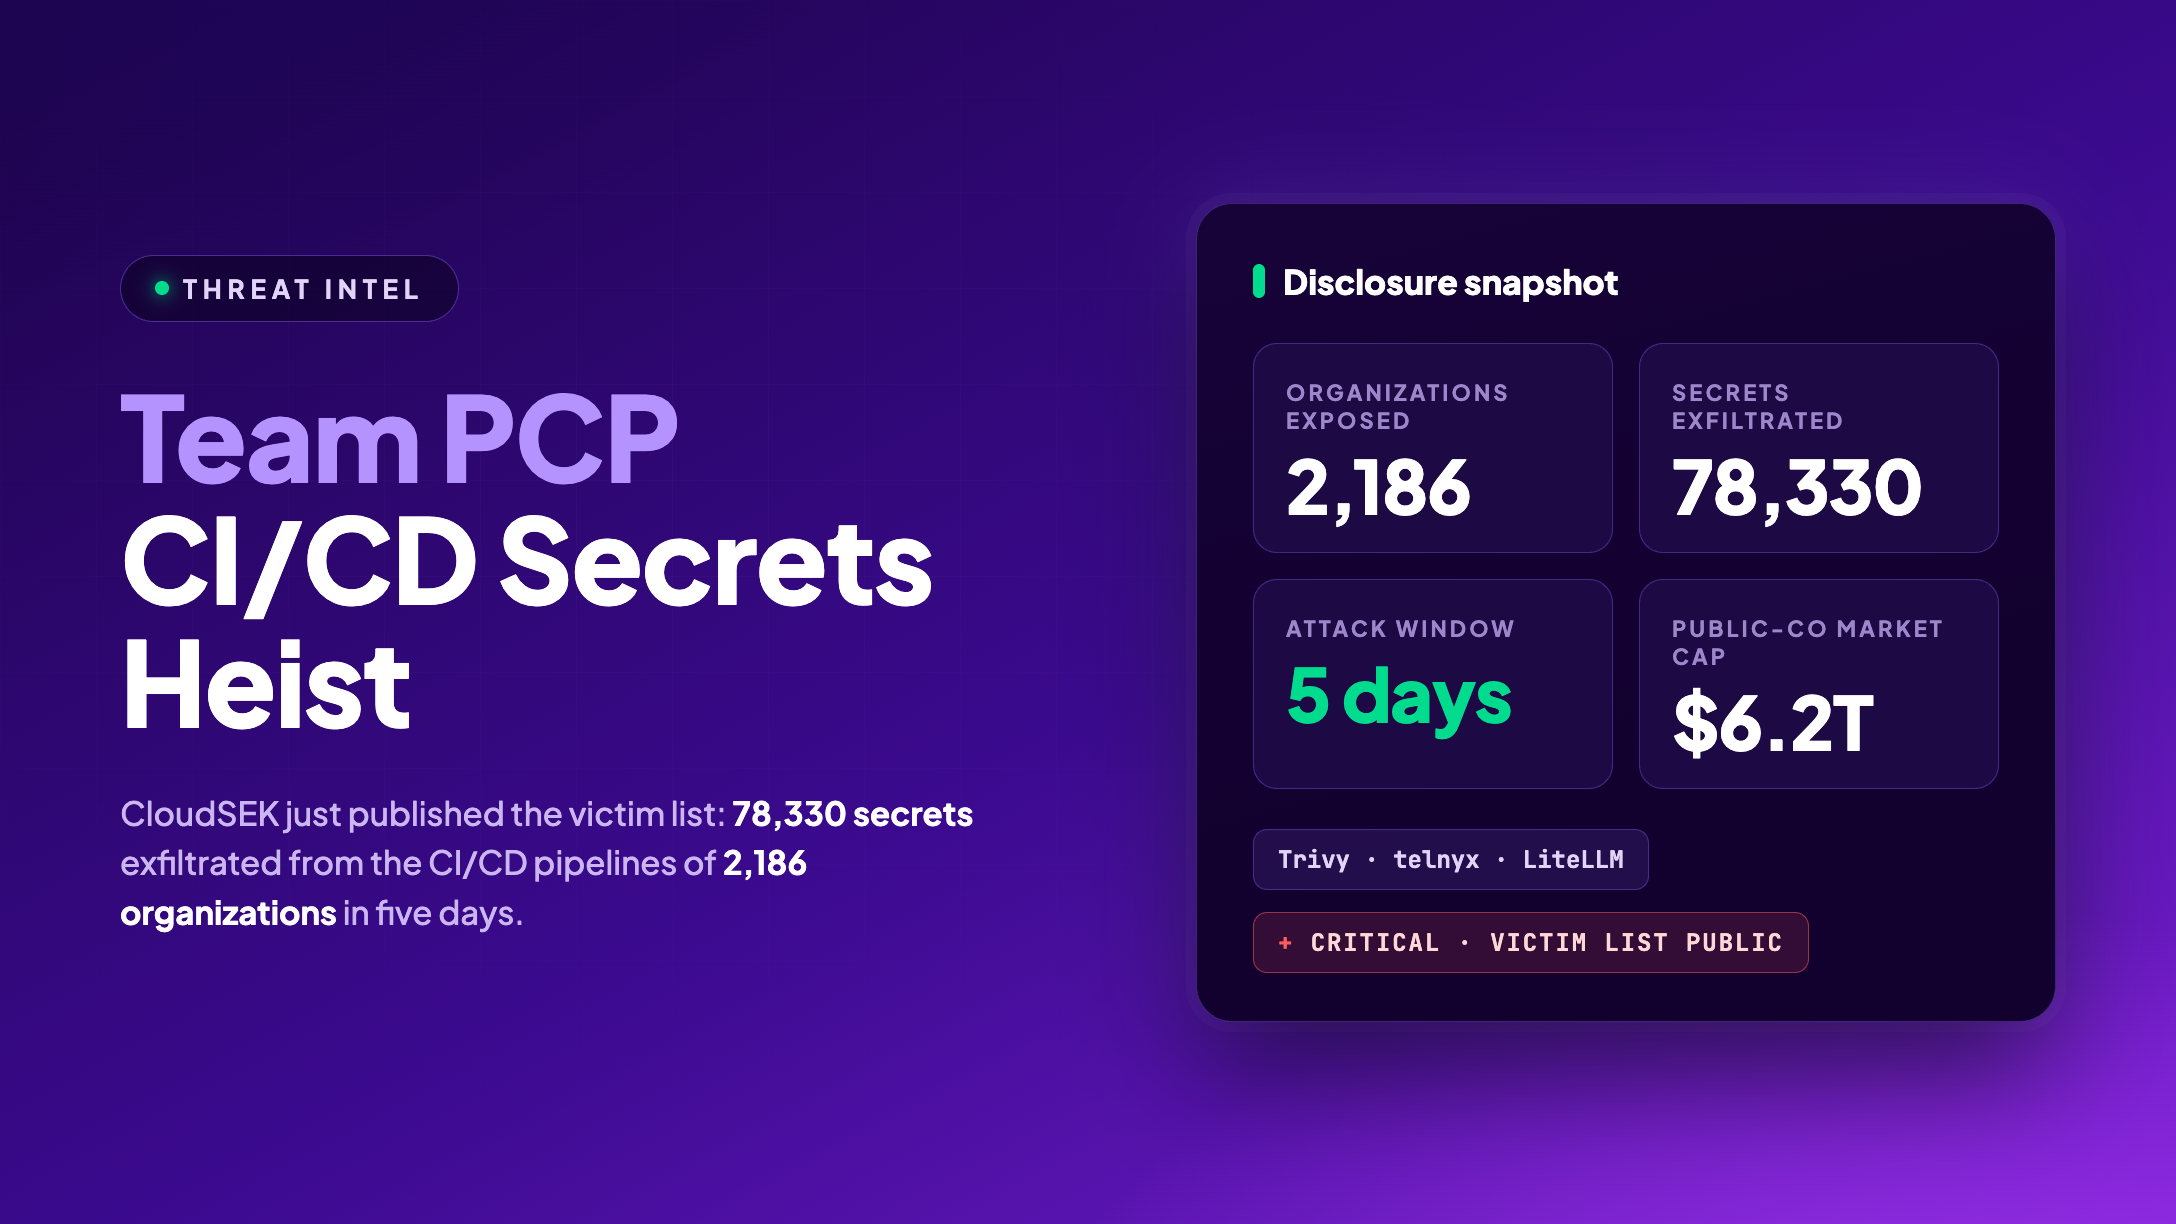
StepSecurity analyzes CloudSEK's newly published dataset on TeamPCP, a threat actor that compromised trusted open-source CI/CD components (Trivy GitHub Action, Checkmarx KICS action, telnyx PyPI package, LiteLLM) to harvest 78,330 secrets from 2,186 organizations' CI/CD pipelines across GitHub Actions, GitLab, and Azure DevOps in five days in March 2026. The post breaks down which platforms and credential types were exposed (GitLab led, 230+ Azure DevOps orgs, 157 leaked OpenAI keys) and maps layered CI/CD runtime controls (egress control, runner lockdown, imposter-commit detection, workflow policies) as mitigations against this class of attack.
What it is
StepSecurity's analysis of the CloudSEK disclosure on Team PCP (TeamPCP), the actor behind the March 2026 wave of CI/CD credential theft. Beyond the scope figures in the summary, the page adds attack specifics: Team PCP injected a credential stealer into 76 of the 77 version tags of the Trivy GitHub Action, used a WAV-steganography stealer in the telnyx PyPI package, and hit LiteLLM (framed by CloudSEK as the largest supply-chain attack on AI infrastructure to date). CloudSEK published a searchable dataset so organizations can check whether they appear.
How it works
The reusable playbook: compromise one trusted component, plant a stealer, collect the secrets CI/CD runners load into memory, then reinvest those credentials into the next compromise — a self-funding flywheel. It works identically across platforms because every CI/CD system shares three weaknesses:
flowchart TD
  A[Compromise trusted OSS component] --> B[Runner loads secrets as env vars]
  B --> C{Runner defenses?}
  C -->|open egress, no runtime monitoring| D[Stealer exfiltrates secrets]
  D --> E[Reuse creds to compromise next component]
  E --> A
  C -->|egress + runtime controls| F[Chain cut]
The three shared weaknesses: secrets enter runners as environment variables any step can read; runners ship with open outbound network access; pipelines trust dependencies by mutable references an attacker can silently repoint (as with the retagged Trivy versions).
Preconditions / Affected
Every major CI/CD platform, not just GitHub Actions — GitLab led by a wide margin, and Azure DevOps appeared in 230+ organizations. A separate set of orgs leaked private keys directly from hosts and mail servers, not pipelines. Stolen credential types: ~1,000 orgs leaked session tokens; hundreds leaked cloud keys and source-control credentials; 157 leaked OpenAI API keys. Any one is often enough to pivot into production or the next OSS project.
What to do
- Check the CloudSEK dataset for your organization.
- Treat CI/CD runners like production hosts. The page names three control categories:
- Runtime security and network egress controls on every runner (block unexpected outbound connections that exfiltration relies on).
- Governance over which OSS packages and actions are allowed to execute with secrets in scope.
- Behavioral monitoring that baselines normal pipeline behavior.
- Pin dependencies to immutable references rather than mutable tags, given the retag technique.
Caveats
The page gives no commands, tool versions, or CVE IDs — the "what to do" is control categories, not a patch. StepSecurity is a CI/CD security vendor and the post doubles as positioning for its own product, so weigh the mitigation framing accordingly. The specific per-platform and credential counts come from StepSecurity's own decoding of the CloudSEK dataset.
Organisations named here
- CloudSEK
Technologies named here
- Trivy GitHub Action
- Harden-Runner
- Workflow Run Policies
- Checkmarx KICS GitHub Action
- Secure Registry
- telnyx PyPI package
- LiteLLM
- StepSecurity GitHub Checks
- Axios npm package
- StepSecurity Maintained Actions
- GitLab CI/CD
- Imposter commit detection
- Threat Center
- Azure DevOps
- Actions, npm, and PyPI Inventory
- GitHub Actions
- Backstage
- Compromised Package Search
- CloudSEK exposure lookup / dataset
- GitLab
- Trivy
- Checkmarx
- axios
- telnyx
Techniques named here
- Credential reinvestment / supply chain flywheel
- Mutable reference/tag repointing
- WAV steganography credential stealer
- Imposter commits
- Outbound exfiltration via runner network egress
- Reading secrets from runner process memory
Threat actors named here
- TeamPCP
- ChainDrop
Related in Supply Chain







