 x.comthread
Dark Web Intelligence (@DailyDarkWeb) on X
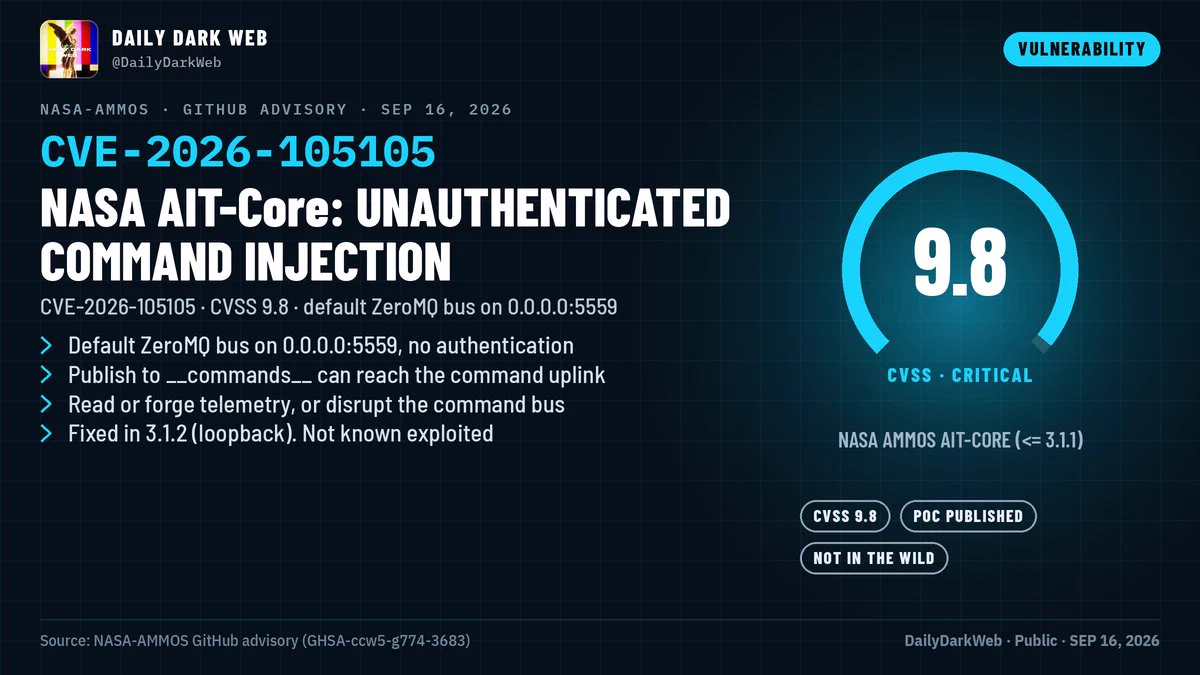
A critical unauthenticated command-injection vulnerability (CVE-2026-105105, CVSS 9.8) was disclosed in NASA AMMOS AIT-Core, software used for spacecraft command and telemetry operations. The flaw stems from AIT-Core's ZeroMQ message bus binding to 0.0.0.0 on TCP port 5559 by default with no authentication, letting any network-reachable attacker publish onto internal topics such as __commands__, potentially injecting spacecraft command data, reading/forging telemetry, and disrupting the command-and-telemetry bus. Affects AIT-Core <= 3.1.1, fixed in 3.1.2 by binding ZeroMQ XSUB/XPUB interfaces to 127.0.0.1; no known in-the-wild exploitation.
TL;DR Unauthenticated ZeroMQ bus exposure in NASA's AIT-Core spacecraft command/telemetry software (CVE-2026-105105, CVSS 9.8) allowed command injection into the uplink path; fixed in 3.1.2.
CVEs named here
- CVE-2026-105105
Technologies named here
- NASA AMMOS AIT-Core
- AIT-Core
- ZeroMQ
Techniques named here
- Unauthenticated command injection via exposed message bus
Related in AppSec
 github.comadvisory
Flowise MCP Security Bypass Enables RCE

 huntress.comwriteup
Inside an Oracle Database SQL Injection Attack | Huntress
github.comrepoOASIS

 blog.trailofbits.comwriteup