 x.comadvisory
Dark Web Intelligence (@DailyDarkWeb) on X
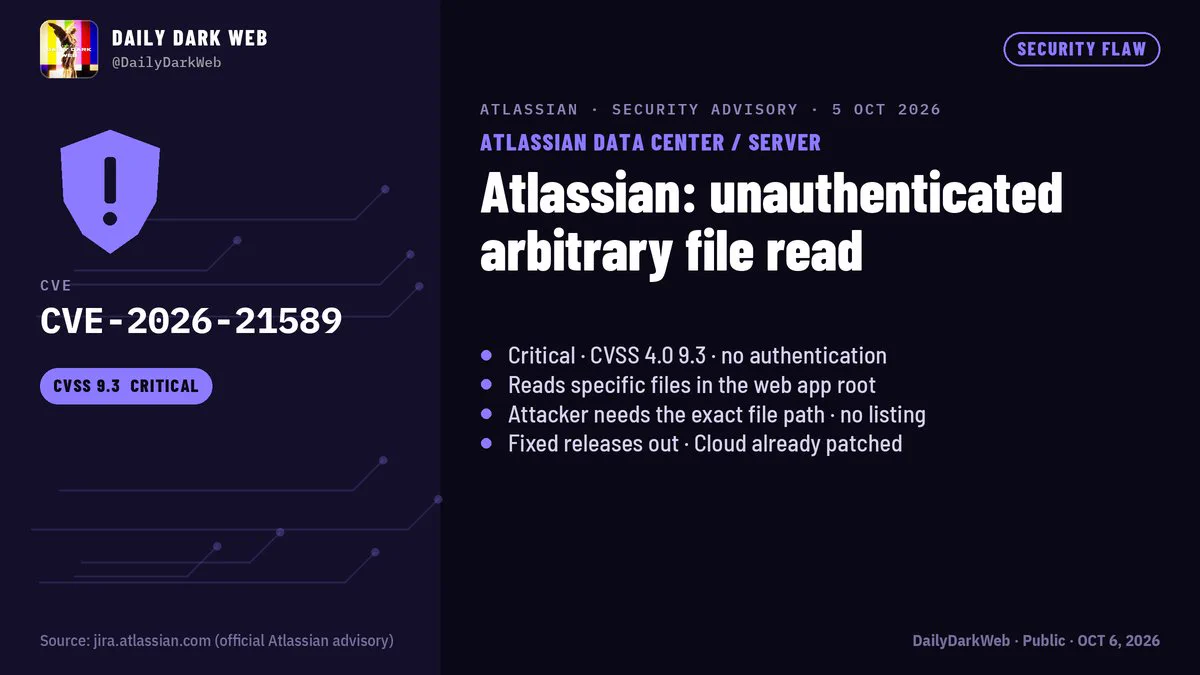
Atlassian disclosed CVE-2026-21589, a critical (CVSS 9.3) unauthenticated path traversal flaw allowing remote attackers to read specific files within the web application root across its self-managed Data Center/Server products — Jira Software, Jira Service Management, Confluence, Bitbucket, Bamboo, Crowd, Crucible, and Fisheye. Fixed versions are listed for each product (e.g. Jira 9.12.40/10.3.26/11.3.12, Confluence 9.2.26/10.2.19), and Atlassian Cloud is already patched; WAF/URL-rewrite mitigations are available for those who can't upgrade immediately. The post's analyst note clarifies exploitation requires knowing the exact target file path (no directory listing), and as of Oct 5, 2026 it is not yet in CISA KEV with no public exploit reported.
CVEs named here
Technologies named here
- WAF / URL-rewrite
- Jira Software
- Jira Service Management
- Confluence
- Bitbucket
- Bamboo
- Crowd
- Crucible
- Fisheye
- Atlassian Cloud
- Jira
- CVSS
Techniques named here
- Path traversal / arbitrary file access
- Path traversal
Related in AppSec
 github.comadvisory
Flowise MCP Security Bypass Enables RCE

 huntress.comwriteup
Inside an Oracle Database SQL Injection Attack | Huntress
github.comrepoOASIS

 blog.trailofbits.comwriteup