 x.comrepo
Dark Web Informer (@DarkWebInformer) on X
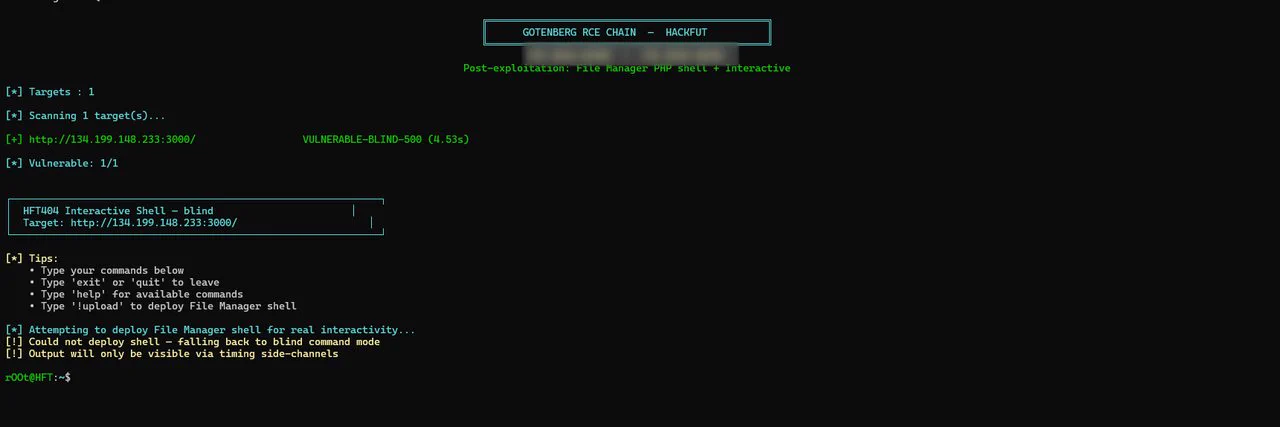
A public PoC chains CVE-2026-42589 and CVE-2026-40281 to achieve unauthenticated remote code execution against Gotenberg (a document/PDF-conversion microservice), abusing metadata injection flaws in the /forms/pdfengines/metadata/write endpoint. The tool supports vulnerability detection, interactive command execution, reverse shell delivery, and multi-target scanning against Gotenberg versions ≤8.30.1 (patched in 8.31.0).
TL;DR Unauthenticated RCE PoC chaining CVE-2026-42589 + CVE-2026-40281 in Gotenberg ≤8.30.1 via metadata injection.
CVEs named here
- CVE-2026-42589
- CVE-2026-40281
Technologies named here
- Gotenberg
- HackfutSecRoot PoC
Techniques named here
- Metadata injection
- Unauthenticated remote command execution
- Reverse shell
Related in Offensive Security

 huntress.comwriteup
AI-Coded Malware | Analyzing Vibe-Coded AD Enumeration | Huntress
 github.comrepo
YesWeHack Claude Kit
 huntress.comwriteup
Inside an Oracle Database SQL Injection Attack | Huntress
 huntress.comwriteup