 huntress.comwriteup
When PUPs Grow Fangs: Dragon Boss Solutions' $10 Supply Chain Risk
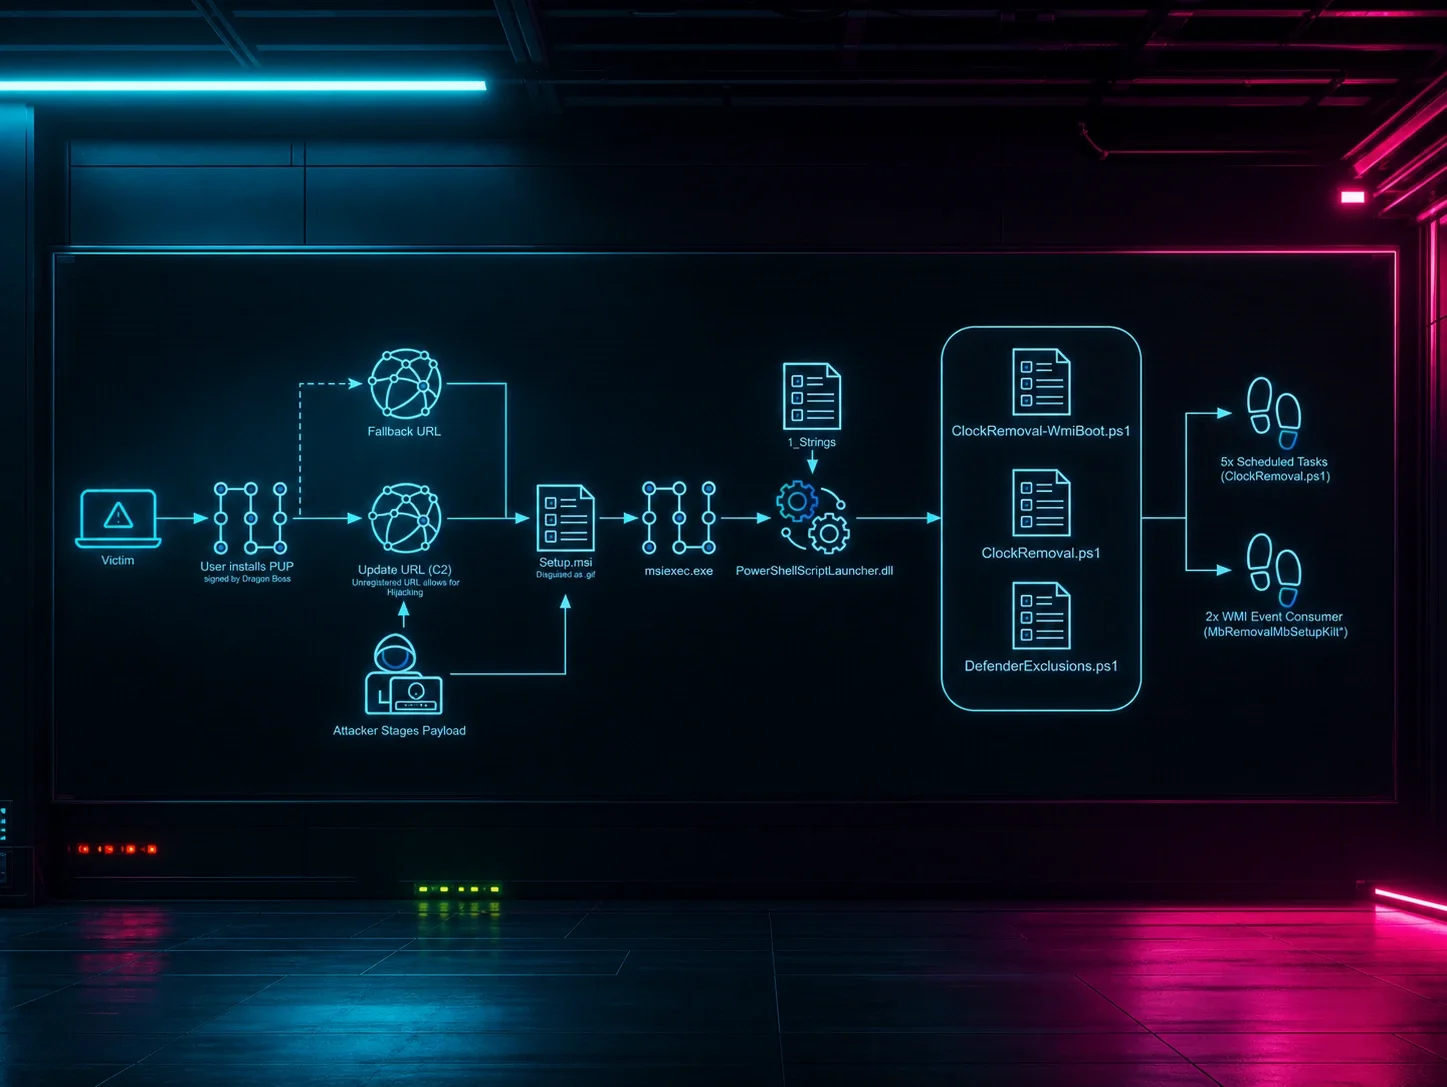
Huntress documents Dragon Boss Solutions LLC, a code-signed adware/PUP vendor whose off-the-shelf Advanced Installer update mechanism was configured to poll an unregistered domain (chromsterabrowser[.]com) for updates, meaning anyone who registered it for $10 could push arbitrary payloads with SYSTEM privileges to every infected host. The deployed payload, ClockRemoval.ps1, kills AV processes via WMI event subscriptions and a 100ms polling loop, disables AV services, poisons the hosts file against AV update domains, and carves out Windows Defender exclusions for future payload staging. Huntress registered the domain first, sinkholed it, and observed 23,565 unique infected hosts across 124 countries within 24 hours, including universities, OT/critical infrastructure networks, government entities, and Fortune 500 companies.
What it is
A malware family distributed as Authenticode-signed PUPs from Dragon Boss Solutions LLC (a firm claiming "search monetization research"). Loaders date to late 2024; the AV-killing payloads appeared late March 2025. Huntress flagged it on 22 March 2025 when adware-looking alerts turned out to conceal a multi-stage chain that disables security tools and blocks their reinstallation, all as SYSTEM. The summary covers the $10 domain-hijack angle — this document carries the hunting artifacts it omits.
How it works
A signed grandparent executable (e.g. RaceCarTwo.exe) uses the Advanced Installer update mechanism to poll a remote server, which returns a Setup.msi (served masquerading as a GIF). The MSI spawns via msiexec, registers four scheduled tasks in rapid succession pointing at a single PowerShell script (e.g. ClockRemoval.ps1), and establishes WMI persistence to kill AV. The poll target lives in an .ini config file left on disk (RaceCarTwo.ini) even after the MSI is gone.
Preconditions / Affected
Any host running a Dragon Boss Solutions signed binary. These follow a recognizable shape:
- Names:
[Word][Word][Number], e.g.TableBoatThree,WinSupportNine; "World Wide Web" appears frequently. - Paths: double-encapsulated
C:\Program Files (x86)\[Name][Suffix]\[Name]\[Name].exe, where[Suffix]isSolutionsorWorkstation(e.g.RaceCarTwoolutions\RaceCarTwo\updates\Update\).
What to do
Hunt for these artifacts:
- WMI persistence with names referencing AV, e.g. containing
Mb(Malwarebytes) andRemoval. - Bursts of four scheduled tasks created together, all invoking one
.ps1(e.g.ClockRemoval.ps1) frommsiexec. - Leftover
*.iniupdate configs matching the naming pattern; check their poll domains against unregistered/sinkholed status.
Known indicators:
RaceCarTwo.exeSHA256909539d3ef8dedc3be56381256713fa5545cc7fd3d3d0e0428f7efb94a7e71cb- Domains:
chromsterabrowser[.]com(primary, was unregistered — now Huntress-sinkholed),worldwidewebframework3[.]com(unregistered fallback),worldwidewebuniverse3[.]com(active), payload hostdl.isready26[.]online(e.g./image/ldk4945jfds.gif).
Caveats
The MSI is typically absent from disk by the time you investigate — the .ini config is your primary lead. The distinction between the two unregistered domains matters: chromsterabrowser[.]com was the primary poll target (no filtering needed to hijack), whereas the RaceCarTwo variant's unregistered domain was only a fallback, reachable only if the active primary failed.
Technologies named here
- RaceCarTwo.exe
- Huntress
- PowerShellScriptLauncher.dll
- Setup.msi
- SoftwareDetector.dll
- Advanced Installer
- AICustAct.dll
- Google Chrome
- Malwarebytes
- VirusTotal
- Kaspersky
- URLScan.io
- CrunchBase
- McAfee
- ESET
- Windows Defender
- chromsterabrowser[.]com
- worldwidewebframework3[.]com
- worldwidewebuniverse3[.]com
- PowerShell
- WMI
- Chrome
- Windows
Techniques named here
- Trojanized/abused software update mechanism
- Code signing abuse
- WMI event subscription persistence
- Scheduled task persistence
- Masquerading payload as image file
- Security software tampering / impairment
- Hosts file poisoning
- Defender exclusion abuse
- Recurring removal/reconnaissance sweeps
- Boot-time defense re-establishment
- Self-termination/anti-forensic timer
- Dual-location script persistence for redundancy
- Unregistered C2/update domain takeover risk
Threat actors named here
- Dragon Boss Solutions LLC
- DragonBoss
- Chromnius
- ClockRemoval.ps1
Related in Threat Intel
 huntress.comwriteup
Reverse Engineering the Six Stages of MacSync Stealer and RAT
 huntress.comwriteup
AI-Coded Malware | Analyzing Vibe-Coded AD Enumeration | Huntress

 blog.talosintelligence.comtool
Introducing CAIRN: Frontier tracking for AI-integrated malware (Cisco Talos)
 huntress.comwriteup