 stepsecurity.ioarticle
Dev Machine Guard Now Scans Extensions Across Every Modern IDE
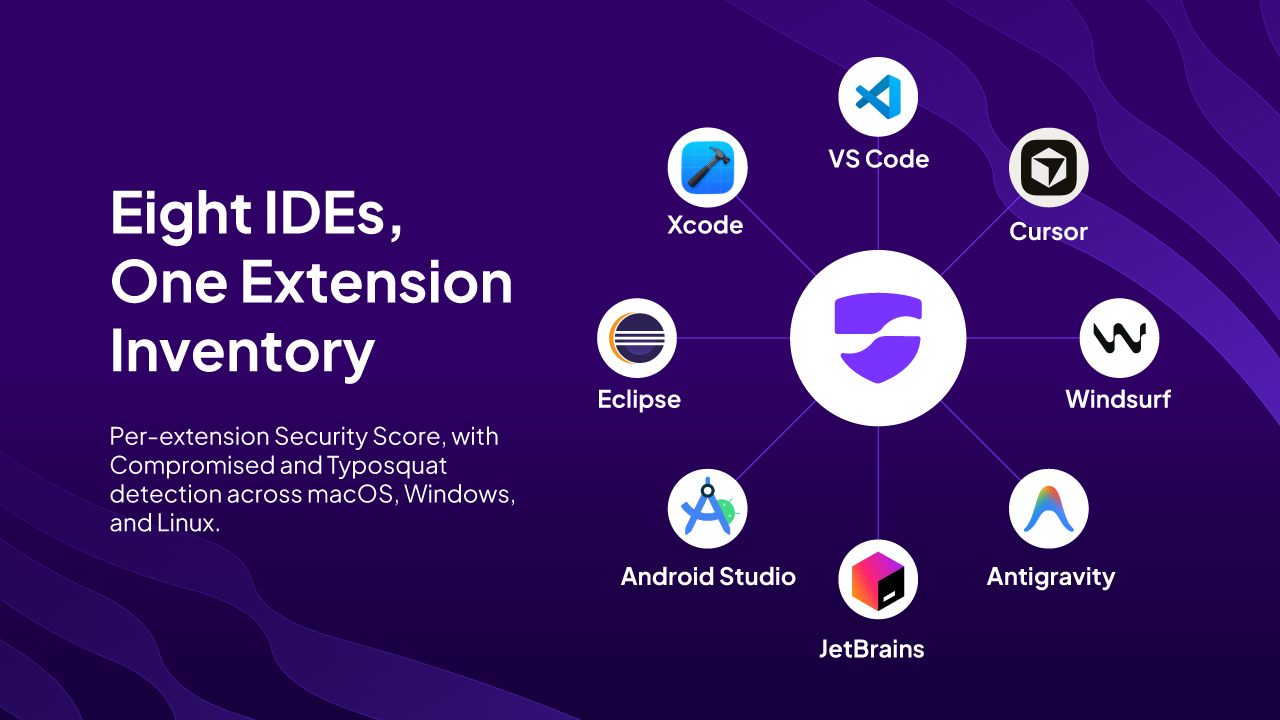
StepSecurity's Dev Machine Guard now inventories and scores IDE extensions/plugins across eight IDE families (VS Code, Cursor, Windsurf, Antigravity, JetBrains IDEs, Android Studio, Eclipse-based IDEs, Xcode) on macOS, Windows, and Linux, not just VS Code. It computes a supply-chain Security Score per extension (adoption, publisher verification, license, known vulnerabilities, repo security posture) and flags known-compromised or typosquatted extensions, motivated by incidents like the October 2025 VS Code publisher token leaks, the s1ngularity Nx compromise, and the Shai-Hulud npm worm reaching extensions via transitive dependencies. The scanning engine is open source; enterprise mode feeds a fleet-wide dashboard for incident response and typosquat/compromise hunting.
Organisations named here
- CISA
- Shai-Hulud
Technologies named here
- Visual Studio Code
- Dev Machine Guard
- Cursor
- StepSecurity dashboard
- Windsurf
- Antigravity
- JetBrains IDEs
- Android Studio
- Eclipse-based IDEs
- Xcode
- macOS
- Windows
- Linux
- npm packages
- VS Code
- StepSecurity
- JetBrains
Techniques named here
- Typosquatting
- Supply chain compromise of extensions/packages
- Credential/token harvesting from developer machines
- Silent auto-update abuse
Threat actors named here
- s1ngularity Nx compromise
- Shai-Hulud npm worm campaign
- VS Code extension publisher token leak incident
- s1ngularity
Related in Supply Chain







