 huntress.comarticle
How EvilTokens Turbocharges Old School Phishing with AI
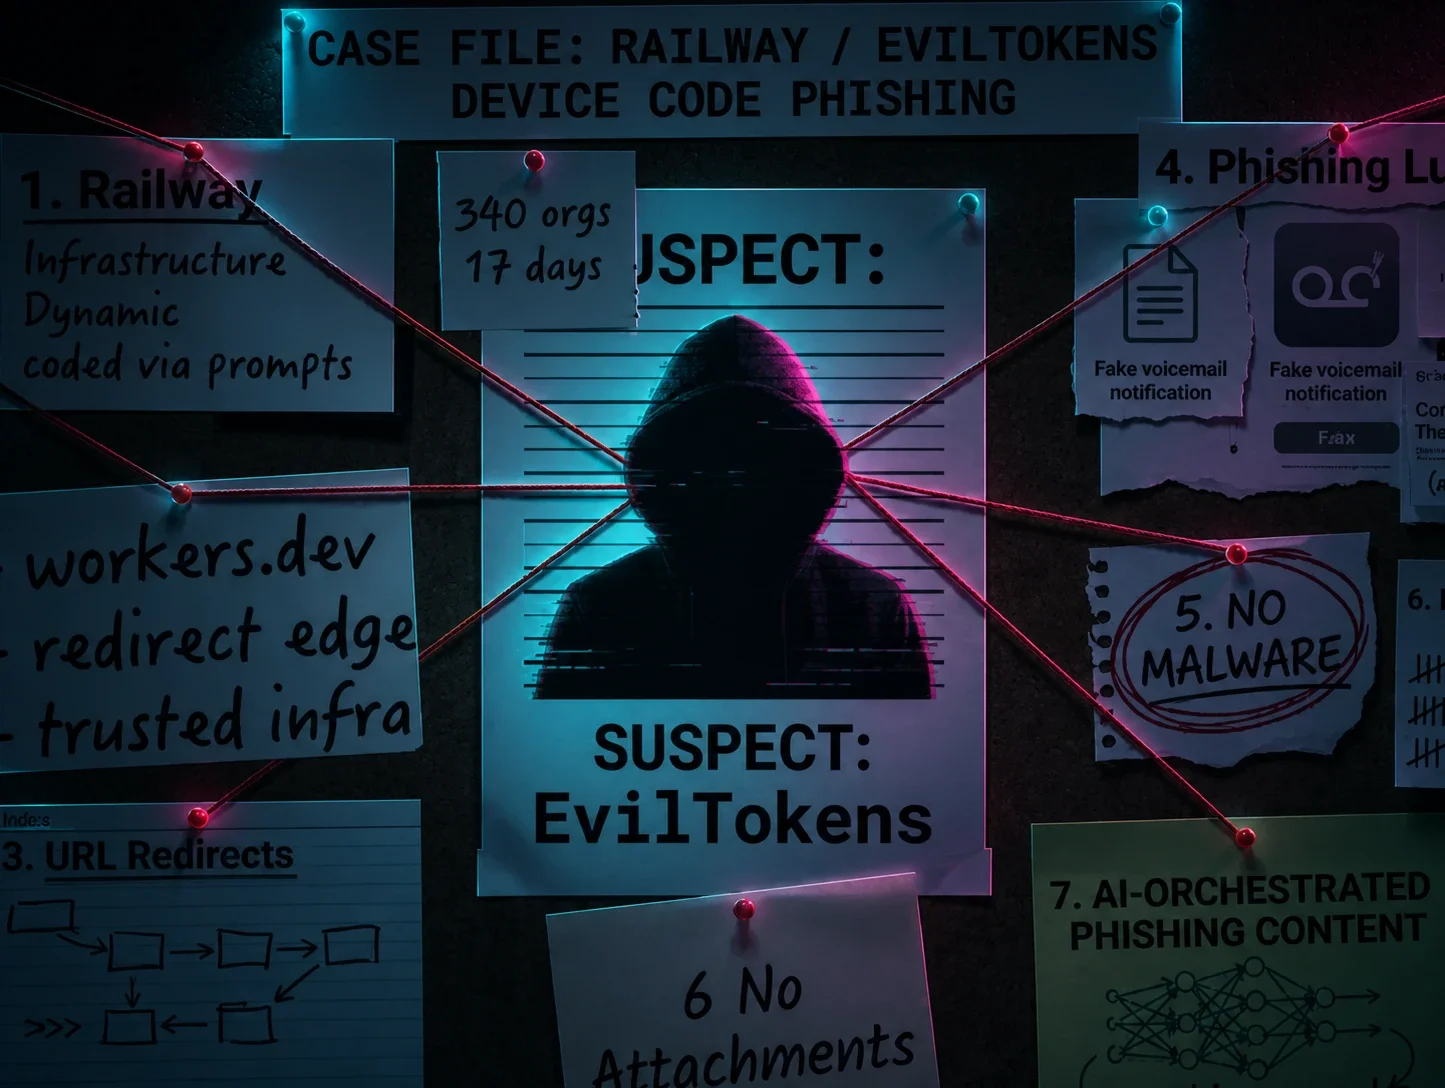
Huntress and Microsoft detail EvilTokens, a phishing-as-a-service (PhaaS) platform sold on Telegram for ~$1,500 that automates OAuth device code phishing to steal valid session tokens and bypass MFA entirely, relaying attacks through the Railway PaaS. The kit integrates AI to generate role-specific, contextually accurate lures, dynamically generate device codes to remove timing constraints, and automatically draft follow-on wire-fraud emails in the victim's own voice after mailbox compromise — a campaign that hit 344 organizations across five countries in 16 days and evaded Cisco Secure Email, Trend Micro, and Mimecast. The piece also covers sibling PhaaS kits (Tycoon2FA, BlueKit, Kali365) and recommends conditional access restrictions, phishing-resistant FIDO2/passkey MFA, and refresh-token revocation as mitigations.
What it is
EvilTokens, a phishing-as-a-service kit ($1,500 + $500 maintenance, sold on Telegram) built around device code phishing — abuse of the OAuth device authorization flow (the same flow you use to log a smart TV into Netflix). Huntress observed it across 344 organizations in five countries; first blips on Feb 19 and Feb 24, then a 16-day flood starting March 2.
How it works
The attacker initiates the device authorization flow themselves, then sends the victim a lure containing the resulting code. The victim clicks, enters the code, and completes MFA normally — but authorizes the attacker's session rather than their own. The result is a fully valid OAuth/session token with no password stolen, no malware, and MFA legitimately satisfied. EvilTokens generated the device code dynamically the moment the victim hit the phishing page, closing the timing window that limited earlier device-code attacks. After token capture, the platform scanned the victim's inbox, calendar, and documents to auto-draft wire-fraud follow-ups in the victim's own voice within minutes.
Why defenses failed
This is the part the summary understates and the reason to act: the attack presents no bad indicators.
- Lure emails passed cleanly through Cisco Secure Email, Trend Micro, and Mimecast.
- URLs were clean; the authentication flow was genuinely Microsoft's; MFA succeeded correctly.
- Traffic was relayed through Railway, a legitimate PaaS, so domain blocklists and spam filters had nothing to flag.
The detection signal Huntress actually caught it on: one cloud IP hitting ~50 organizations in a single week, with hundreds of login events routed through the same Railway infrastructure — a cross-tenant anomaly, not a per-message one.
What to do
The page states no patches or commands. The actionable takeaways it does give:
- Hunt on the cross-org / cross-tenant login pattern (single Railway-hosted IP authenticating many unrelated orgs), since content and URL filtering will not fire.
- Treat device code / device authorization flow as a first-class risk surface — user training does not help, because the user does everything correctly.
- Related PhaaS kits using comparable infrastructure to watch for: Tycoon2FA, BlueKit, Kali365.
Caveats
Huntress provides no CVE, no patch, and no configuration guidance — the flow being abused is working as designed, so mitigation is detection and conditional-access policy rather than a fix. The IP-concentration signal is Huntress's own observation from this campaign, not a durable IOC.
Organisations named here
- Jamie Levy
- Sherrod DeGrippo
Technologies named here
- Microsoft Entra ID authentication
- Railway
- Telegram
- Cisco Secure Email
- Microsoft Entra Conditional Access
- Trend Micro
- Huntress SOC
- Mimecast
- SMS-based MFA
- Microsoft Entra ID
Techniques named here
- Device code phishing
- AI-generated personalized phishing lures
- Dynamic device code generation
- AI-assisted post-compromise follow-on attacks
- AI for evading email security controls
Threat actors named here
- EvilTokens
- Tycoon2FA
- BlueKit
- Kali365
Related in Threat Intel
 huntress.comwriteup
Reverse Engineering the Six Stages of MacSync Stealer and RAT
 huntress.comwriteup
AI-Coded Malware | Analyzing Vibe-Coded AD Enumeration | Huntress

 blog.talosintelligence.comtool
Introducing CAIRN: Frontier tracking for AI-integrated malware (Cisco Talos)
 huntress.comwriteup