 github.comrepo
Momoko-Ayase/Senbei
Senbei is a Rust-based static unpacker for binaries protected by "CrackProof," working against both Windows PE executables and Android AArch64 shared libraries. It performs a purely static, file-local transformation (no vendor code, no key extraction service) to reverse the protection wrapper for legitimate RE, interoperability, and preservation purposes; one Android packaging variant is unwrapped using an XOR keystream the authors recovered during their own analysis.
What it is
Senbei, by GitHub user Momoko-Ayase/Ayase, is a Rust CLI tool that statically unpacks binaries wrapped by "CrackProof" (the project's name is a pun: 煎餅/senbei, rice cracker — "cracks itself"). It targets Windows PE executables and Android AArch64 shared libraries, and is licensed AGPL-3.0.
How it works
Usage is a single invocation: senbei protected.exe, senbei game.apk, or pointing it at a directory (senbei "C:\Games\MyGame"). Output files are written to an unpack directory by default, or to a path given with --out. The page reiterates that the transformation is file-local and derives everything from the input binary, with no vendor code embedded and no key-extraction service called. The one exception is a single Android packaging variant whose embedded metadata layer is unwrapped using an XOR keystream the authors recovered from a known ciphertext/plaintext pair during analysis of one specific build; builds that don't match that build are left untouched.
flowchart TD
    A[Input binary: PE or AArch64 .so] --> B{Android variant with known build match?}
    B -- yes --> C[Apply recovered XOR keystream to metadata layer]
    B -- no --> D[Standard static unwrap, no external key material]
    C --> E[Output written to ./unpack or --out path]
    D --> E
Preconditions / Affected
Applies to Windows PE executables and Android AArch64 .so libraries protected by CrackProof. The XOR-keystream path only applies to one specific Android packaging build the authors analyzed; other builds fall through to the standard static path unmodified. Building requires Rust (cargo build --release).
What to do
cargo build --release
senbei protected.exe
senbei game.apk
senbei "C:\Games\MyGame"
The project's usage notice (linked full documentation at a separate gitbook page is not reproduced here) states: only process binaries you own or are explicitly authorized to analyze, since circumventing technological protection measures may be legally restricted depending on jurisdiction (the page cites DMCA §1201 in the US, which has exemptions for security research/interoperability). The authors state Senbei does not enable online play, license fraud, or cheating, and explicitly instruct users not to redistribute decrypted outputs or upload them anywhere.
Caveats
The authors disclaim warranty and liability for misuse (AGPL-3.0, "as is"). "CrackProof" is stated to be a trademark of a third party, and the project claims no affiliation with or endorsement by that vendor or any software publisher — names are used for identification only. The XOR-keystream mechanism is scoped to one build the authors personally analyzed; it is not described as generalizing to other Android packaging variants.
Technologies named here
- CrackProof
- Senbei
- Windows PE files
- Android AArch64 shared libraries
- Windows
- Android
- Rust
Techniques named here
- Static unpacking of CrackProof-protected binaries
- XOR keystream decryption of embedded metadata
Related in Malware & RE

 huntress.comwriteup
Reverse Engineering the Six Stages of MacSync Stealer and RAT
 huntress.comwriteup
Post-DEF CON Phishing Uses Malicious Google Doc to Deliver Malware
 huntress.comwriteup
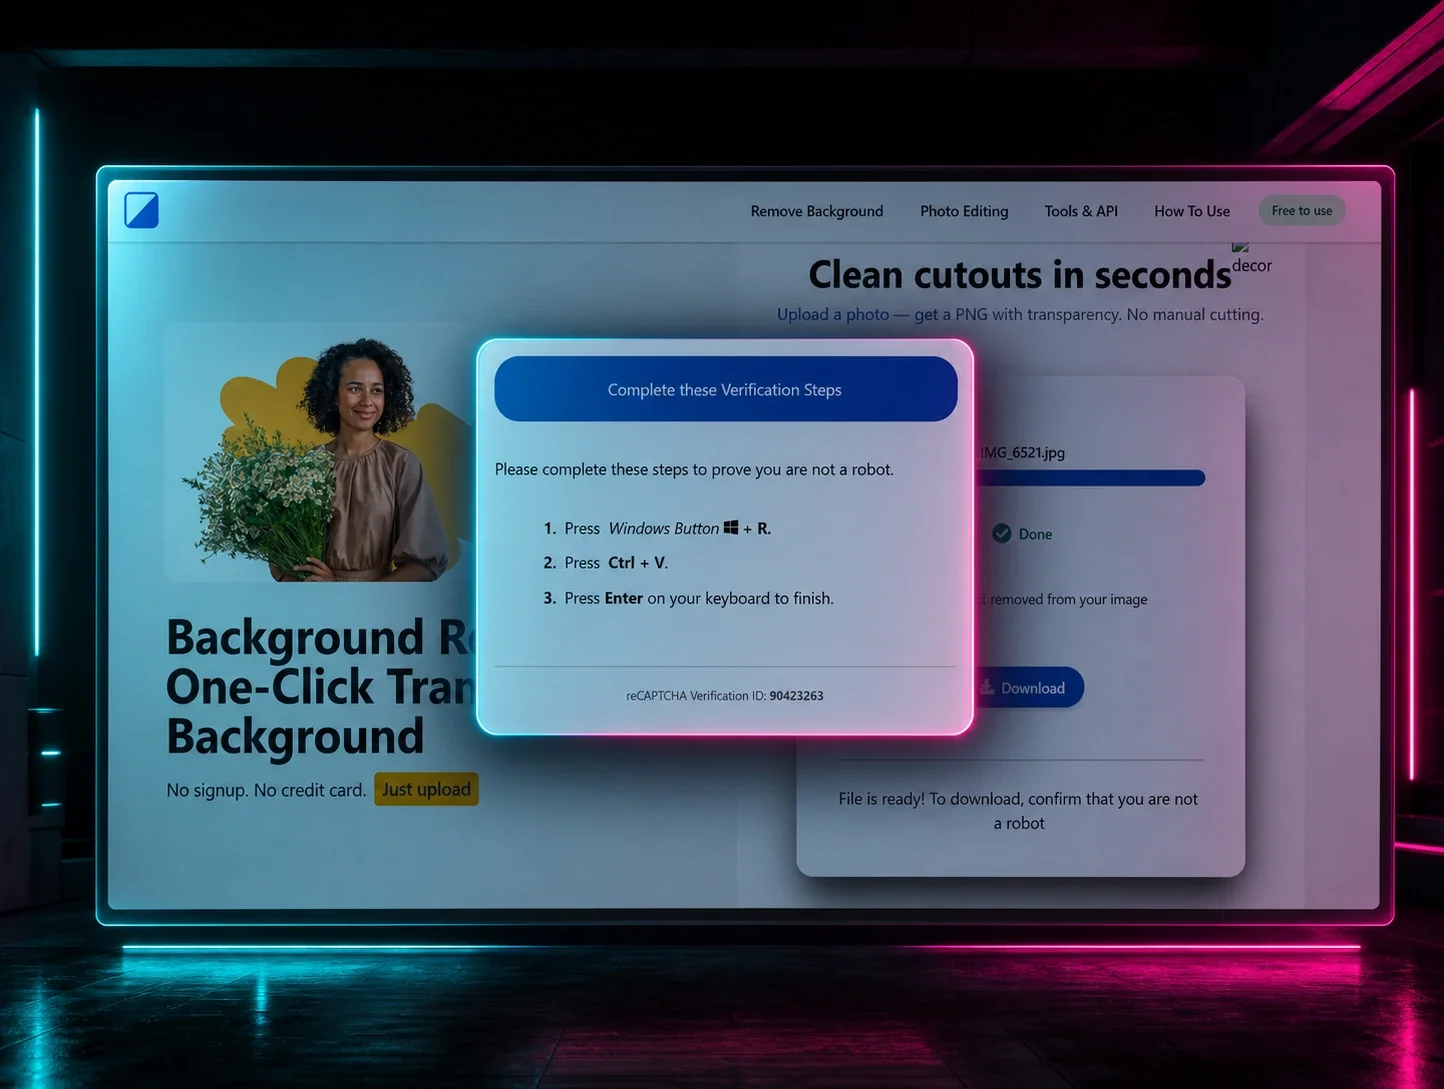
ClickFix Removes Your Background but Leaves the Malware

