 socket.devwriteup
Socket: Miasma Mini Shai-Hulud Hits ImmobiliareLabs npm Packages
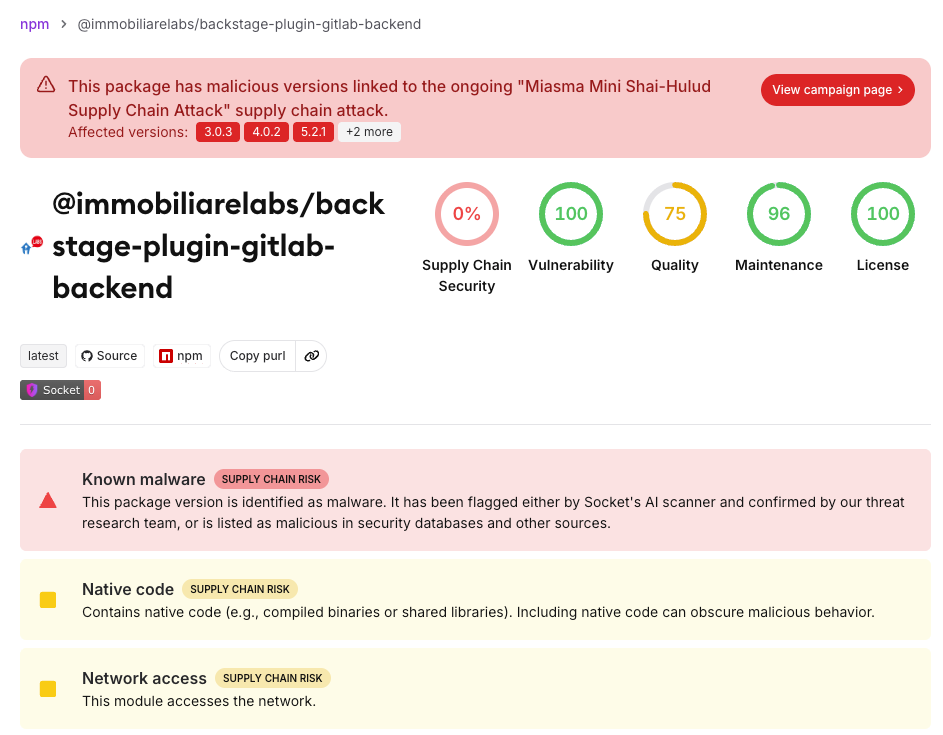
Socket Threat Research documents a new wave of the Miasma Mini Shai-Hulud npm supply-chain campaign compromising @immobiliarelabs Backstage plugins for GitLab integration and LDAP authentication, published on June 26, 2026. The malicious tarballs (e.g. @immobiliarelabs/backstage-plugin-gitlab@7.0.2) add a hidden root-level index.js triggered via the "Phantom Gyp" node-gyp binding.gyp trick, which decrypts an AES-128-GCM payload, bootstraps Bun, and steals npm/GitHub/cloud/SSH/CI-CD secrets while planting GitHub Actions and AI-IDE persistence. The report also traces a plausible root cause to the earlier compromise of codfish/semantic-release-action (tag-hijacking reported by StepSecurity) and highlights abuse of GitHub's deployment event trigger — a technique flagged by researcher Adnan Khan — to run attacker workflows without touching protected workflow files.
What it is
A new wave of the "Miasma Mini Shai-Hulud" npm supply-chain campaign, documented by Socket Threat Research, compromising legitimate @immobiliarelabs Backstage plugins (GitLab integration and LDAP auth families) on June 26, 2026. This is a continuation of activity Socket reported the prior day against LeoPlatform, RStreams, and Verana — same campaign, new maintainer scope, no new malware family.
How it works (beyond the summary)
The tarball's declared entrypoint dist/index.cjs.js is benign; the malicious code is a root-level index.js added to the package root — the path a reviewer inspecting only the declared/compiled entrypoint will miss. That root file is a single-line Caesar-shift loader, followed by AES-128-GCM decryption and multi-stage delivery, with the third stage running under Bun v1.3.13 (downloaded if absent). Install-time execution comes from the "Phantom Gyp" trick: node-gyp command expansion in binding.gyp invokes node index.js without relying on preinstall/postinstall hooks.
The wave also has a GitHub Actions initial-trigger lead: a public run in immobiliare/backstage-plugin-gitlab, workflow named "Dependabot Updates", with release.yml configured on: deployment, triggered via deployment on June 26, 2026 at 15:00 UTC under the simonecorsi account, completing successfully.
Affected
@immobiliarelabsBackstage GitLab and LDAP-auth plugin families; example artifact@immobiliarelabs/backstage-plugin-gitlab@7.0.2.- Multiple historical versions were republished with malicious artifacts — pinning to an older major version does not protect you.
- Highest-risk install environments: Backstage internal developer portals with access to source-control tokens, publishing credentials, CI/CD secrets, cloud credentials, or auth config.
What to do
- Do not trust review of
dist//declared entrypoints alone; inspect the package root for an unexpectedindex.jsand anybinding.gypinvokingnode index.js. - Hunt for the campaign clustering marker string, useful because of its unusual spelling and reuse across waves:
thebeautifulsnadsoftime- Audit workflows for
release.yml/ build configs usingon: deploymenttriggers and injected steps (e.g., "Dependabot Updates" runs) that pivot to downstream repos. - Rotate developer/CI-CD secrets that may have been exposed to affected install/build environments:
.env, npm/PyPI/GitHub/Slack/Twilio/AWS/Azure/GCP/Vault tokens, SSH keys, Docker credentials, Kubernetes configs. - Check AI-coding-assistant plugins and IDE extensions for planted persistence hooks.
Caveats
This is an ongoing investigation; Socket is still confirming affected artifacts, repository indicators, and exfiltration infrastructure, and the full technical payload analysis lives in the prior day's coverage, not this post. The GitHub Actions run is described as a "lead," and the simonecorsi association is stated as workflow metadata, not attribution.
Organisations named here
- ImmobiliareLabs
- RevokeAndItGoesKaboom
- simonecorsi
Technologies named here
- LDAP
- @immobiliarelabs/backstage-plugin-gitlab
- Socket
- @immobiliarelabs/backstage-plugin-gitlab-backend
- Bun
- GitHub Actions
- @immobiliarelabs/backstage-plugin-ldap-auth
- @immobiliarelabs/backstage-plugin-ldap-auth-backend
- StepSecurity
- Backstage
- node-gyp
- codfish/semantic-release-action
- npm
- GitLab
Techniques named here
- Phantom Gyp binding.gyp trick
- Caesar-shift loader + AES-128-GCM decryption
- Multi-stage payload via Bun
- Credential and secret theft
- GitHub Actions workflow abuse
- AI/IDE persistence
- Exfiltration via GitHub API
- Hidden root-level entrypoint
- Deployment-triggered workflow execution
- Mutable tag hijacking
- Camouflaged workflow naming
- Repository poisoning / propagation via stolen tokens
- Phantom Gyp
Threat actors named here
- Miasma Mini Shai-Hulud
- Miasma
- Mini Shai-Hulud
Also named here
- Adnan Khan
- thebeautifulsnadsoftime
Related in Supply Chain






