 huntress.comwriteup
Bank of America Phishing Email Delivers ScreenConnect Malware
Huntress dissects a Bank of America-themed phishing email that lures victims into downloading AccountGuardSetup.vbs, which unpacks through several layers of base64-encoded PowerShell to silently install ScreenConnect RMM with Administrator privileges. The chain uses AES-128-CBC encrypted blobs to deliver a C# UAC-bypass exploit via the ICMLuaUtil COM interface (MITRE ATT&CK T1548.002), then hides the resulting ScreenConnect service (renamed "Windows Security") from users and admins using SDDL/ACL manipulation so it can't be seen, logged, or removed.
What it is
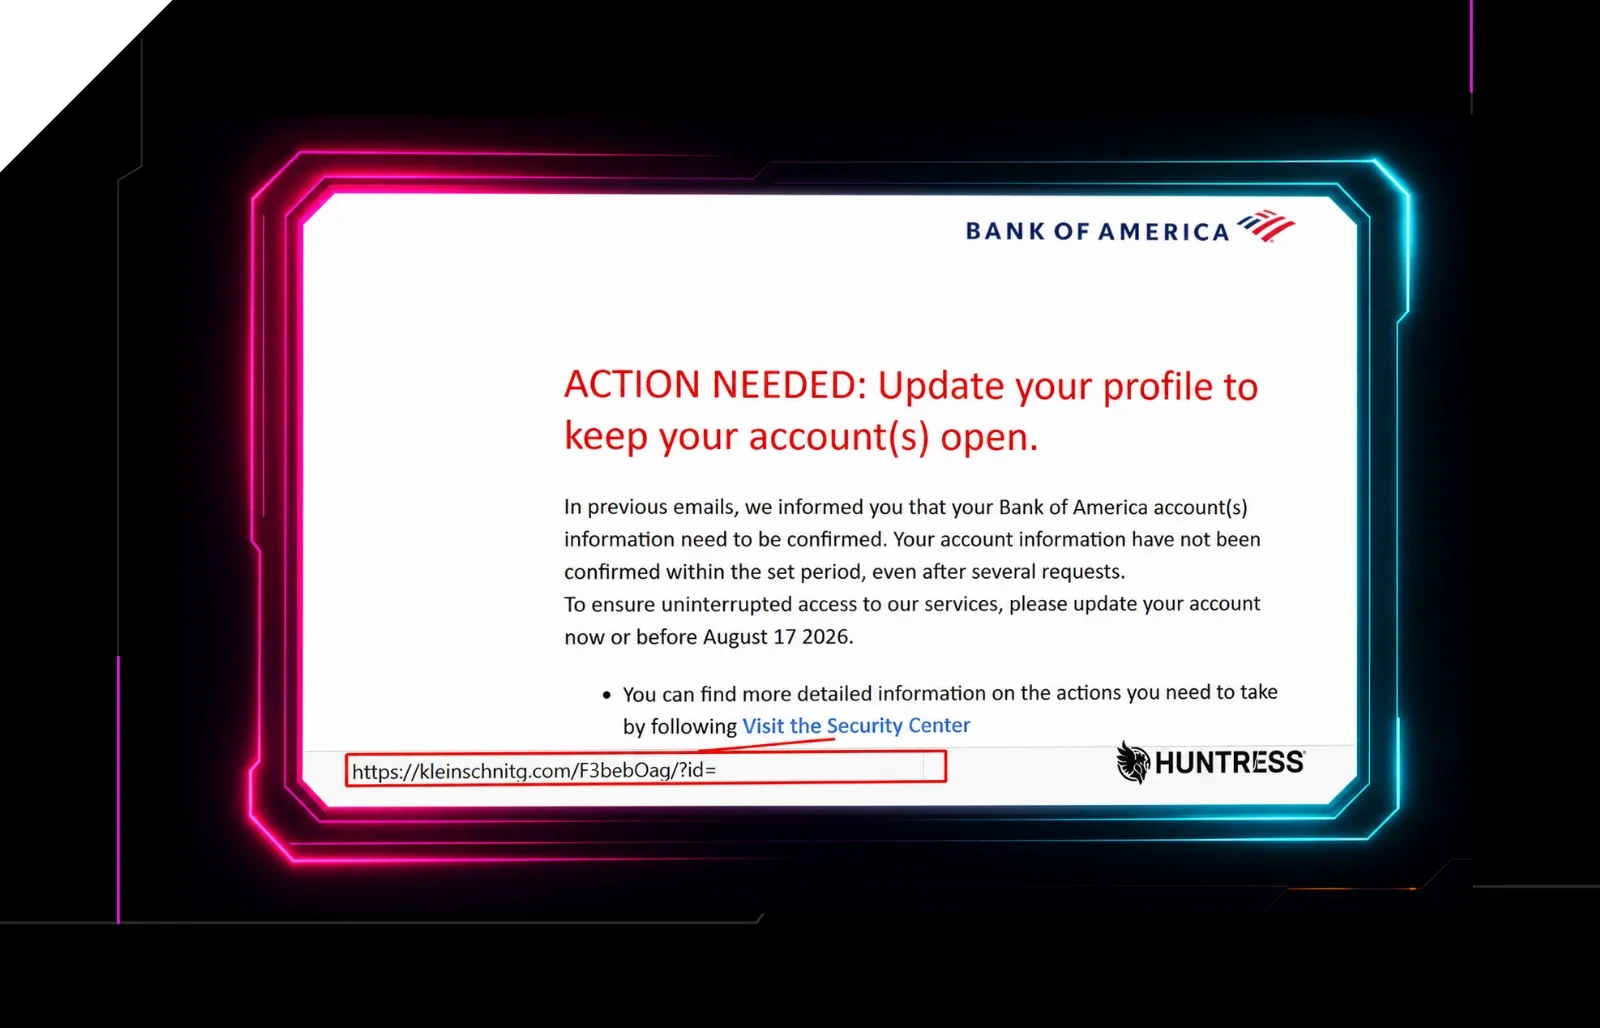
A live Bank of America–themed phishing campaign observed by Huntress on July 28, in a spamtrap account. The lure email spoofs sender onlinebanking@ealerts[.]bkofamerica[.]com and warns the recipient has ~two weeks to "confirm" account information "to act quickly to avoid account restrictions." The embedded link is a redirect to a page mimicking Bank of America's branding. The summary covers the Windows RMM payload chain; what it omits is the OS-based branching, the specific IOCs, and the second (credential-theft) path.
How it works
The phishing page fingerprints the victim by User-Agent and splits:
flowchart TD
    A[Redirect link in email] --> B{User-Agent}
    B -->|Mac / non-Windows| C[Credential + PII harvest page]
    C --> C2[Username/password x2, name, address,<br/>gov ID, SSN, card details]
    B -->|Windows| D[Update My Information button]
    D --> E[AccountGuardSetup.zip -> .vbs]
    E --> F[Nested base64 PowerShell chain]
    F --> G[Download 17MB ScreenConnect .msi]
    F --> H[AES-128-CBC C# -> UAC bypass]
Notable specifics beyond the summary:
- The credential path double-prompts the password (faking an error) and then collects full name, mailing address, government ID, SSN, and payment card details.
- The Windows download is
AccountGuardSetup.zipcontainingAccountGuardSetup.vbs. - The decoded PowerShell is written to the user's My Documents folder and run after a delay; nesting is PowerShell inside base64 script inside base64 blob.
- The ScreenConnect MSI is fetched (base64-encoded) from the legitimate file-sharing site UploadToURL.com, decodes to ~17MB, and is written to
%localappdata%\Microsoft\sc.msi. - The AES-128-CBC key is stored as a plaintext UTF-8 string in
$key; the IV is the first 16 bytes (32 hex chars) of each blob. One decrypted blob ($csharpCodeDecrypted) is compiled and run to perform the ICMLuaUtil UAC bypass (T1548.002).
What to do
Hunt for these observable artifacts:
- Sender domain / address
onlinebanking@ealerts[.]bkofamerica[.]com. AccountGuardSetup.vbs/AccountGuardSetup.zipexecution.- PowerShell scripts written to a user's My Documents and run after a delay.
- Outbound download from
UploadToURL.com. - The file path
%localappdata%\Microsoft\sc.msiand unexpected ScreenConnect installs.
General guidance from the page: never run a .vbs file you didn't create or fully understand.
Caveats
The page text cuts off mid-sentence during the UAC-bypass explanation, so the full C# mechanism and any concluding remediation are not captured here. Domains/addresses are reproduced as the page defanged them; treat as IOCs, not clickable. UploadToURL.com is described as an otherwise-legitimate service abused for hosting.
Organisations named here
- Bank of America phishing
- ICMLuaUtil
- T1548.002
Technologies named here
- ScreenConnect
- Windows
- Visual Basic Script
- PowerShell
- C
- UploadToURL.com
- .NET
- MITRE ATT&CK
Techniques named here
- Abuse Elevation Control Mechanism
- Phishing with spoofed sender domain
- Link redirection chain
- Device-based phishing page differentiation
- Credential and PII harvesting
- Multi-layer base64 obfuscation
- AES-128-CBC encrypted payloads with embedded keys
- Service masquerading
- Defense evasion via SDDL/ACL manipulation
- Registry key deletion to hinder detection
- Command-and-control beaconing
Threat actors named here
- Unnamed threat actor
Related in Threat Intel
 huntress.comwriteup
Reverse Engineering the Six Stages of MacSync Stealer and RAT
 huntress.comwriteup
AI-Coded Malware | Analyzing Vibe-Coded AD Enumeration | Huntress

 blog.talosintelligence.comtool
Introducing CAIRN: Frontier tracking for AI-integrated malware (Cisco Talos)
 huntress.comwriteup