Skip to content

69 results for โ€œSSRFโ€

What you seeeverything
portswigger.netcourse๐Ÿ›ก๏ธ Security

Web Security Academy

Web Security Academy is PortSwigger's free online web security training. It is known to combine learning material with hands-on labs across web vulnerability classes such as SQL injection, XSS, SSRF, authentication flaws and request smuggling, and to be built around Burp Suite. The page had no extractable text, so this description comes from the URL and general knowledge of the site.

Burp Suite
PortSwigger

Learning, AppSecยท Added 30 Oct 2026

github.blogarticle๐Ÿ›ก๏ธ Security

How bug bounty sharpens one researcherโ€™s security skills

GitHub Bug Bounty spotlight interview with @r31n, a researcher known for GitHub Enterprise Server findings. They describe a source-and-sink approach to mapping trust boundaries, chaining minor bugs (open redirect plus allowlisted SSRF that follows redirects), and confirming a finding only with a working PoC. They also cover using AI for code navigation and PoC scripts, and treating model output as untrusted input.

GitHub Enterprise ServerGitHubHackerOne
SSRFopen redirectXSS+3

Learning, AppSecยท Published and added 22 Oct 2026

boredhackerblog.infowriteup๐Ÿ›ก๏ธ Security

Plex vulnerabilities being exploited in the wild to drop a cryptominer

Honeypot writeup of in-the-wild exploitation of Plex Media Server through the Plex2Shell chain (CVE-2026-96652, -96654, -96655, -96656) in October 2026. Attackers from 45.194.92.222, 91.92.40.202 and 176.65.139.228 used SSRF-style timeline/subscribe requests and downloaded a Docker-named dropper and an XMRig miner from 217.60.194.116. Includes file hashes, a later-seen proxyware sample (myawesomeproxy), lab pcaps for signatures and links to sandbox reports.

Plex Media ServerXMRigDocker+1
CVE-2026-96652CVE-2026-96654CVE-2026-96655+8

Threat Intel, Blue Team & Detectionยท Added 20 Oct 2026, published 19 Oct 2026

aws.amazon.comarticle๐Ÿ›ก๏ธ Security

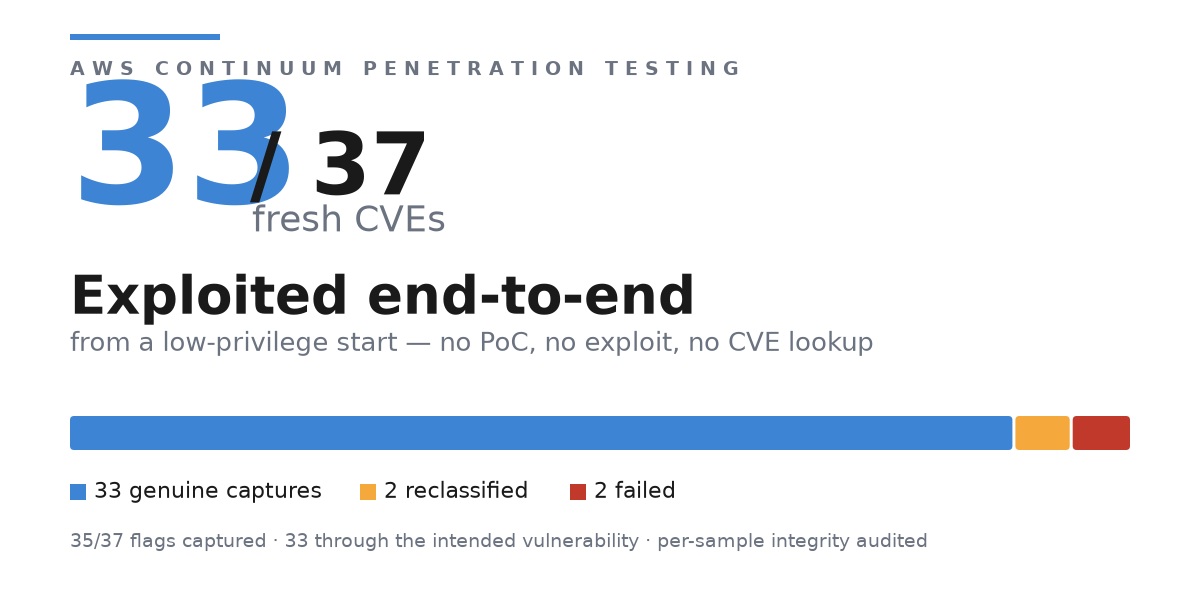
AWS Security Agent (now part of AWS Continuum) exploited 33 of 37 new real-world CVEs

AWS reports results for its autonomous pentesting agent, AWS Security Agent (now part of AWS Continuum), on an internal CTF-style benchmark of 37 recent 2025โ€“2026 CVEs. Each CVE ran as a live docker-compose target with a hidden flag, and the agent started from an endpoint and a one-line hint with runtime CVE lookup disabled. It captured 35 flags, 33 (89.2%) through the intended vulnerability after an audit against canonical PoCs. The post describes the 7-stage pipeline (crawler, specialist agents, validator, exploitation agent, flag check, audit), three exploit walkthroughs (CMS upload-to-admin chain, AI workflow builder RCE, tRPC full-read SSRF), the two audit reclassifications caused by benchmark bugs, and two misses where the agent took the target down. It also argues that saturated public benchmarks like CVE-Bench and XBOW are contaminated.

AWS Security AgentAWSDocker+2
Opus 5CVEBenchSSRF+4

AI Security, Offensive Security, AppSecยท Published and added 15 Oct 2026

securityweek.comarticle๐Ÿ›ก๏ธ Security

SAP Patches Critical NetWeaver, S/4HANA Vulnerabilities

SecurityWeek summarizes SAP's October 2026 Security Patch Day (22 notes, four critical). Critical flaws: CVE-2026-89111 (CVSS 10) OAuth2 SSRF in SAP Cloud SDK for Python that leaks client credentials via the tenant_subdomain parameter; CVE-2026-89110 (9.9) NetWeaver broken access control allowing ABAP code execution through Fiori rule definition input; CVE-2026-89107 (9.9) S/4HANA Visual Composer code injection; and CVE-2026-89108 (9.1) missing authorization check in Manufacturing Integration and Intelligence allowing admin account creation. SAP reports no exploitation in the wild.

SAP NetWeaverSAP S/4HANASAP Cloud SDK for Python+3
CVE-2026-89111CVE-2026-89110CVE-2026-89107+3

AppSecยท Published and added 14 Oct 2026

x.comadvisory๐Ÿ›ก๏ธ Security

Dark Web Intelligence (@DailyDarkWeb) on X

Summary of SAP's October 13, 2026 Security Patch Day (16 new notes, 4 GitHub advisories). It leads with CVE-2026-89111, a CVSS 10.0 OAuth2 SSRF in SAP Cloud SDK for Python before 0.45.2, where an attacker-controlled tenant_subdomain redirects token requests and exfiltrates client credentials. It also lists three other critical flaws: broken access control in NetWeaver Visual Composer, code injection in S/4HANA substitution/validation rules, and a missing authorization check in the Manufacturing Integration and Intelligence (XMII) Configuration Service. It notes that none are in CISA KEV and SAP reports no in-the-wild exploitation.

SAP Cloud SDK for PythonSAP NetWeaverSAP S/4HANA+3
CVE-2026-89111CVE-2026-89110CVE-2026-89107+5

AppSec, Identity & Accessยท Added 15 Oct 2026, published 13 Oct 2026

x.comthread๐Ÿ›ก๏ธ Security

Dark Web Informer (@DarkWebInformer) on X

Social post announcing a PoC (hakaioffsec) for CVE-2026-82957, an SSRF in Hyperledger FireFly โ‰ค 1.5.0 (CVSS 8.5). Webhook subscriptions accept a user-controlled URL without validating the destination host, letting the FireFly node reach internal services, private networks, loopback and cloud metadata endpoints. The PoC creates a malicious webhook subscription, triggers a matching event and confirms the request originates from the FireFly server.

Hyperledger FireFlyCVSS
CVE-2026-82957SSRFCWE-918+1

AppSec, Offensive Securityยท Published and added 13 Oct 2026

securityweek.comarticle๐Ÿ›ก๏ธ Security

Critical SonicWall Vulnerability Exploited Days After Disclosure

SecurityWeek reports that CVE-2026-102255, a CVSS 10 pre-authenticated SSRF in the SonicWall SMA1000 Work Place interface, was exploited within days of its October 6 disclosure. Defused saw the first attempts on its SMA decoys on October 8, and Previdian (formerly KEVIntel) also observed exploitation. SonicWall urges 6210, 7210 and 8200v customers to update to 12.5.0-03082 or 12.4.3-03670, and Horizon3.ai warns that exploitation could lead to device takeover.

SonicWallCVSS
CVE-2026-102255SSRFCWE-918+4

Threat Intel, AppSecยท Published and added 12 Oct 2026

github.comrepo๐Ÿ›ก๏ธ Security

bilawalsidhu/gods-eye-view

God's Eye View is an open-source, vanilla-JavaScript CesiumJS and Vite client that puts live aircraft, ships, satellites (SGP4), earthquakes, fires, public CCTV and mapped ALPR cameras on one photorealistic 3D globe. It adds cockpit tracking, FLIR/NVG sensor shaders and a voice agent built on the OpenAI Realtime API. It works without API keys, and the docs cover server-side key brokering with SSRF protection, localhost binding and a SECURITY.md threat model. For OSINT/GEOINT practitioners it is a hackable base for fusing public signals, with an explicit rule against person-tracking features.

CesiumJSOpenAIPinokio+3
SGP4ADS-BAIS+4

OSINTยท Added 11 Oct 2026

x.comadvisory๐Ÿ›ก๏ธ Security

lee1981 (@lee1981b) on X

CyberForge's CVE of the Day #073 covers CVE-2026-102255, a critical (CVSS 10.0) pre-authentication SSRF / confused-deputy flaw (CWE-918, CWE-441) in the SonicWall SMA1000 Work Place interface, per advisory SNWLID-2026-0017. It lists affected platform hotfixes (12.4.3-03526 and older, 12.5.0-02952 and older), fixed floors (12.4.3-03670, 12.5.0-03082), no workaround, and the exploitation picture (no known exploitation, not in KEV, EPSS 0.477%, SSVC automatable). It gives a six-step SOC playbook covering appliance scoping, AMC log preservation, hunting appliance-originated internal requests, correlating receiving-service changes, patching, and verifying every node, and it separates exposure, a lead, confirmed compromise and telemetry gaps.

SonicWallSMA1000CVSS+3
CVE-2026-102255CVE-2026-102256CVE-2026-102257+7

Blue Team & Detection, AppSecยท Added 12 Oct 2026, published 9 Oct 2026

securityweek.comarticle๐Ÿ›ก๏ธ Security

Cisco Patches a Dozen Critical Vulnerabilities

Cisco patched 35 vulnerabilities in its October release, including a dozen+ critical bugs across Meraki, License On-Prem, NX-OS, APIC, and Finesse. Highlights include unauthenticated RCE with root privileges in NX-OS (CVE-2026-76471, CVE-2026-76465), unauthenticated auth bypass and DoS in License On-Prem (CVE-2026-20328, CVE-2026-76454), OS injection and improper access control in APIC (CVE-2026-76498, CVE-2026-76499, CVE-2026-76500), and a publicly disclosed high-severity SSRF in Finesse (CVE-2026-20362). Cisco says none are currently exploited in the wild.

Cisco MerakiCisco NX-OSCisco APIC+2
CVE-2026-76464CVE-2026-20328CVE-2026-76454+15

Cloud & Infraยท Published and added 8 Oct 2026

securityweek.comarticle๐Ÿ›ก๏ธ Security

SonicWall and Splunk Patch Critical Vulnerabilities

SonicWall patched four SMA1000 appliance vulnerabilities including CVE-2026-102255, a pre-authenticated SSRF flaw (CVSS 10) that lets an unauthenticated remote attacker abuse an unintended alternate access path to reach internal functionality; two other high-severity bugs enable RCE and one medium-severity bug enables XSS. Splunk separately fixed dozens of flaws across Splunk Enterprise, MCP Server, and the Add-on for AWS, including three critical Splunk Enterprise bugs allowing arbitrary command execution, unauthorized access, and code injection, plus a medium-severity MCP Server issue letting an authenticated user redirect API requests to an attacker-controlled URL. SonicWall says SSL-VPN on its firewall products is unaffected and no in-the-wild exploitation has been observed.

SonicWallSplunkModel Context Protocol+1
CVE-2026-102255SSRF

AppSecยท Published and added 8 Oct 2026

adversa.aiarticle๐Ÿ›ก๏ธ Security

Top MCP security resources โ€” October 2026

Adversa AI's October 2026 MCP security roundup, aggregating and synthesizing 15 resources: authentication-bypass vulnerabilities in LiteLLM's MCP endpoint (CVE-2026-59822, now CISA KEV), Grafana's MCP server session spoofing/SSRF (CVE-2026-19516), an MCP Python SDK OAuth-fallback flaw exploited by a malicious server returning a 404, and an Obot gateway route-matching bypass reopening GHSA-vw82. It also covers detection failures (two malicious MCP servers passing five scanners including Cisco mcp-scanner and Snyk agent-scan, 12% of 82,000 public MCP configs hardcoding secrets), a malicious npm wallet-signing package (gadgethumans-mcp), the A2M agent-hijacking attack technique, and CoSAI's MCP Security v2.0 governance model.

Model Context ProtocolLiteLLMnpm+3
CVE-2026-59822CVE-2026-59821CVE-2026-19516+6

AI Security, AppSec, Identity & Accessยท Published and added 8 Oct 2026

snyk.ioarticle๐Ÿ›ก๏ธ Security

Frontier models found the vulnerabilities. Only the attacker found the chains.

Snyk benchmarks its Evo Continuous Offensive Security (COS) agent against Claude Security running Mythos on TaintedPort, a public deliberately vulnerable web app with 57 known vulnerabilities and 15 known exploit chains. Evo COS, run gray-box against the live URL plus source, confirmed 10 of 15 exploit chains with runnable proofs of concept โ€” for example chaining an SSRF flaw with a hardcoded JWT signing secret into full admin account takeover โ€” while Claude Security, reasoning over source code alone (white-box), found one additional critical bug but could not prove the vulnerabilities were actually reachable and chainable at runtime. The post argues that proving exploitability requires exercising the live application, not just reading code, and frames SAST-style code review and DAST-style live attack as complementary.

SnykClaude Security
Evo Continuous Offensive SecurityMythosSSRF+1

AppSec, AI Securityยท Published and added 7 Oct 2026

vulnerablemcp.inforepo๐Ÿ›ก๏ธ Security

The Vulnerable MCP Project โ€” MCP vulnerability database

The Vulnerable MCP Project is a curated, continuously growing database of security vulnerabilities and attack techniques specific to the Model Context Protocol ecosystem. Entries cover concrete CVEs (e.g. CVE-2025-68143/68144/68145 in Anthropic's mcp-server-git), transport-layer SDK flaws (cross-client response leakage, missing DNS rebinding protection in the official TypeScript/Python SDKs), unauthenticated/0.0.0.0-bound servers enabling RCE (MCPJam inspector, MCP Inspector, Grafana MCP), command/path injection in dozens of third-party servers (gemini-mcp-tool, mcp-server-kubernetes, Framelink Figma MCP, Zen MCP, filesystem-mcp), SSRF chains reaching cloud metadata (MarkItDown MCP, mcp-fetch-server), and a large set of AI-specific attacks: tool poisoning, trigger-phrase data exfiltration, prompt injection via GitHub issues, Jira and Google Docs, rug-pull tool mutation, and cross-server tool-name collisions. It functions as the de facto vulnerability registry for the MCP ecosystem, useful for tracking disclosed issues before patching or adopting third-party MCP servers.

Model Context ProtocolCursorKubernetes+3
CVE-2025-68143CVE-2025-68144CVE-2025-68145+3

AI Security, AppSecยท Added 6 Oct 2026

snyk.ioarticle๐Ÿง  AI

Why AI Coding Agents Keep Writing Broken Access Control

Snyk argues AI coding agents reliably write broken access control (BOLA/IDOR, OWASP's top category since 2021) because the facts needed to add an ownership check โ€” what an object belongs to, who may access it, where tenant boundaries sit โ€” are tacit product knowledge that exists nowhere in the code or prompt an agent sees. It explains why SAST tools catch patterned sub-categories like path traversal or SSRF but structurally cannot catch CWE-639/862/863 (missing or incorrect authorization), since there's no bad pattern to match, and proposes reasoning over an assembled "application-context graph" of architecture, data flows and trust boundaries instead. It closes with a five-step team checklist (inventory ID-accepting endpoints, document ownership rules, add authorization-specific PR review, write cross-tenant tests, run deep contextual analysis) and pitches Snyk's Evo Agentic AppSec as the tool built around that approach.

SnykOWASPEvo Agentic AppSec+1

coding-agentsยท Published and added 1 Oct 2026

snyk.ioarticle๐Ÿ›ก๏ธ Security

Why AI Coding Agents Keep Writing Broken Access Control

Snyk explains why AI coding agents reliably ship broken object-level authorization (BOLA/IDOR) bugs: the ownership rule that would prevent them (e.g. "invoices belong to organizations") lives in the product's data model and team knowledge, not in the prompt or surrounding code, so the agent produces code that is correct for the stated task but lets any authenticated user access other tenants' objects. The piece maps the flaw to CWE-639/862/863, contrasts it with pattern-matchable classes like SSRF and path traversal that SAST handles well, and lays out five concrete team actions (endpoint inventory, documented ownership rules, explicit authz review questions, per-resource cross-tenant tests, and periodic deep contextual analysis), while pitching Snyk's "application-context graph" and Evo Agentic AppSec as the tool for the pattern-less gap.

Snyk
BOLAIDORCWE-639+5

AppSec, AI Securityยท Published and added 1 Oct 2026

github.comrepo๐Ÿ›ก๏ธ Security

https://github.com/dmdhrumilmistry/security-harness

security-harness is an open-source Claude Code plugin (also packaged for Gemini CLI, Codex and opencode) that orchestrates subagents โ€” sh-recon, sh-hunter, sh-chainer, sh-verifier, sh-reporter โ€” through a static-analysis pipeline covering 15 vulnerability classes (IDOR/BOLA, SQLi, XSS, SSRF, injection, auth, deserialization, path traversal, secrets, CSRF, XXE, open redirect, crypto, race conditions, file upload), producing README/JSON/SARIF/HTML/PDF reports with PoCs, CVSS and CWE/OWASP mappings. It also ships sh-pr-review, a per-PR merge-gate skill that posts inline findings and a commit status scoped only to code the PR itself introduced or aggravated, with caching, dedup via fingerprints, and a scheduled GitHub Action that keeps its per-class knowledge bases fresh by having one AI agent draft updates from allowlisted sources (OWASP, PortSwigger Research, CWE/CAPEC, HackerOne) while a separate adversarial reviewer agent fails-closed against prompt injection before auto-merge.

Claude CodeGemini CLISARIF+3
IDORBOLASSRF+1

AppSec, AI Security, DevSecOpsยท Added 2 Oct 2026, published 29 Sep 2026

github.comrepo๐Ÿง  AI

awslabs/mcp release 2026.09.20260922000649

This is a release changelog for awslabs/mcp, AWS Labs' collection of Model Context Protocol servers covering services like HealthOmics, Aurora DSQL, Bedrock Knowledge Base retrieval, ECS, CloudWatch, billing/cost management, and dataprocessing. This release adds vended metrics tools, SQL parser-based policy guards for Aurora DSQL, agentic retrieval support for Bedrock KB, and fixes several security issues including region validation to prevent SSRF credential disclosure in the CloudWatch server and read-only mode bypass in the MySQL server. It reflects an actively maintained, high-velocity multi-server MCP monorepo used for AWS tool integration with LLM agents.

Model Context ProtocolPythonFastMCP
AWSAWS HealthOmicsAurora DSQL+4

mcpยท Added 26 Sep 2026

thehackernews.comarticle๐Ÿ›ก๏ธ Security
Veeam, Terraform MCP, Django Patch Critical Flaws, Led by CVSS 10.0 Cross-Tenant Bug

The Hacker News roundup covers 11 patched CVEs across three products: Veeam Service Provider Console (CVE-2026-58073, 9.5, unauthenticated managed-agent credential theft; CVE-2026-58072, arbitrary file write to RCE), HashiCorp's Terraform MCP Server (CVE-2026-16498, a 10.0 cross-tenant credential-reuse bug caused by the underlying MCP library not issuing unique session IDs in stateless HTTP mode; CVE-2026-16496 stateful-mode equivalent; CVE-2026-14869 SSRF via header/query-param inconsistency), and Django/GeoDjango (CVE-2026-15307, a spatial-lookup flaw letting GDALRaster write files, reachable by a staff user with view permission on a model with a spatial field, plus a stored XSS, a GEOS DoS, and a language-code DoS). Fixes: Terraform MCP Server 1.1.0+, VSPC 9.3.0.35057, Django 6.0.8/5.2.17; none of the flaws are known to be exploited or listed in CISA KEV as of publication.

TerraformModel Context ProtocolDjango+2
CVE-2026-58073CVE-2026-58072CVE-2026-58067+14

AppSec, AI Securityยท Added 26 Sep 2026

nvd.nist.govadvisory๐Ÿ›ก๏ธ Security
CVE-2026-19984: A flaw has been found in jkawamoto mcp-florence2 up to 0

CVE-2026-19984 describes a server-side request forgery flaw in jkawamoto mcp-florence2 (up to 0.3.13), an MCP server wrapping Microsoft Florence-2 image model. The vulnerable get_images function in src/mcp_florence2/__init__.py passes an attacker-controlled src argument into an HTTP fetch without validation, letting a remote caller force the server to request arbitrary internal or external URLs. The maintainer recommended fix is deploying an SSRF-safe egress proxy rather than patching the source, and a public exploit is available.

Model Context ProtocolPython
CVE-2026-19984CWE-918mcp-florence2

AppSecยท Added 26 Sep 2026

github.comadvisory๐Ÿ›ก๏ธ Security
DNS TOCTOU race condition causes SSRF protection bypass (`/admin/gateways/test`)

GHSA-9hgc-g3w5-67cm details a DNS TOCTOU race in IBM mcp-context-forge's /admin/gateways/test endpoint: validate_gateway_test_url() resolves and vets a hostname against private/cloud-metadata IP ranges, but the actual request is made with httpx (via ResilientHttpClient), which independently re-resolves DNS at connection time with no IP pinning. An attacker with gateways.read permission can exploit DNS rebinding (short-TTL record flipping from a public IP to 169.254.169.254) to bypass SSRF protections and reach cloud instance metadata, exfiltrating IAM credentials where IMDSv1 is enabled. The advisory notes the codebase already acknowledges the gap in two comments and a tracked TODO (ICACF-15), and recommends pinning the validated IP into the connection.

Model Context ProtocolPythoncURL
SSRFGHSA-9hgc-g3w5-67cmGHSA-m8rv-5m6m-32ff+3

AppSecยท Added 26 Sep 2026

cisa.govadvisory๐Ÿ›ก๏ธ Security
CISA Adds Seven Known Exploited Vulnerabilities to Catalog | CISA

CISA added seven vulnerabilities to its Known Exploited Vulnerabilities Catalog on the basis of active exploitation. They are SQL injection in Sangoma Switchvox, HTTP request/response smuggling in Kludex Starlette, OS command injection in Kestra OSS, improper authentication in BerriAI LiteLLM and JFrog Artifactory, and SSRF plus OS command injection in SonicWall SMA1000 appliances. The alert restates BOD 26-04, which makes federal agencies prioritise rapid remediation of KEV CVEs on publicly exposed assets that grant total control after exploitation. It also requires agencies to check for prior compromise before patching.

Sangoma SwitchvoxStarletteKestra+3
CVE-2026-9586CVE-2026-48710CVE-2026-49869+8

AppSec, GRCยท Added 26 Sep 2026

blog.googlearticle๐Ÿ›ก๏ธ Security

Agentic Hacks, Real Proofs: Inside Google's PageBreak Project

PageBreak is Google Product Security's internal LLM-driven agent, built mostly on Gemini models, that autonomously hunts for exploitable bugs in Google's first-party web apps and confirms them with deterministic, non-AI validators rather than relying on model-generated hypotheses alone. The validators execute real payloads to prove exploitability for XSS, SQL injection, path traversal, RCE, and SSRF, which Google says drives false positives near zero and let the system surface over 500 real XSS bugs across sensitive Google domains; when run against apps built on Google's high-assurance web framework it found only 2. The post also describes feeding unverified findings back into the system to seed deeper scans and improve validators, and notes integration plans with Google's CodeMender automated-fix agent.

GeminiCodeMender
XSSSQL Injectionpath traversal+2

AI Security, AppSecยท Added 1 Oct 2026, published 24 Sep 2026

github.comrepo๐Ÿ›ก๏ธ Security

https://github.com/akha-security/akca

AKCA is an open-source, Go-based Dynamic Application Security Testing (DAST) scanner that combines HTTP and headless-browser crawling, JavaScript/AST analysis, API spec import (OpenAPI, GraphQL, gRPC, etc.), and adaptive active testing across a very broad set of vulnerability classes including SQL injection, XSS, SSRF, IDOR/BOLA, SSTI, JWT/OAuth flaws, race conditions, and cloud/CI exposure. It emphasizes evidence-oriented verification โ€” replaying promising signals against baselines, negative controls, and OAST callbacks before promoting them to findings โ€” and exports Burp-style HTTP evidence in HTML, JSON, CSV, Markdown, and SARIF reports. Positioned as a transparent, single-developer alternative inspired by but not claiming parity with Acunetix, Invicti/Netsparker, or Burp Suite Professional.
GoBurp SuiteSARIF+3
IDORBOLASSRF+1

AppSecยท Added 2 Oct 2026, published 23 Sep 2026

github.comrepo๐Ÿ›ก๏ธ Security

Lonkero โ€” Rust web vulnerability scanner (v3.7, AI agent mode)

Lonkero is an open-source Rust web vulnerability scanner (v3.7) combining 125+ context-aware scanners with an AI agent mode that drives targeted scans via natural-language conversation (using Claude, GPT, or local Ollama models). Notable techniques include a browser-free "proof-based" XSS engine that mathematically proves exploitability from reflection context + escape behavior, an "OOBZero" engine for detecting blind SQLi/SSRF/XXE via Bayesian multi-channel statistical inference and Pearson-correlated timing attacks without external callback infrastructure, Next.js middleware-bypass detection (CVE-2025-29927, CVE-2024-34351), AWS Cognito user-enumeration checks, and a scanner module that detects invisible prompt-injection payloads hidden in README.md files targeting AI coding assistants.

RustClaudeOllama+3
CVE-2025-29927CVE-2024-34351CVE-2023-23752+6

AppSec, AI Security, Offensive Securityยท Added 21 Sep 2026

arxiv.orgpaper๐Ÿ›ก๏ธ Security

VIPER-MCP: Detecting Vulnerabilities in MCP Servers

VIPER-MCP is an end-to-end automated auditing framework that combines two-pass static taint analysis (anchor queries mapping alerts to specific MCP tool handlers) with feedback-driven LLM prompt evolution to both detect and dynamically confirm taint-style vulnerabilities (command injection, SSRF, path traversal) in Model Context Protocol servers. Run against 39,884 real-world open-source MCP server repositories, it discovered 106 0-day vulnerabilities โ€” all confirmed via end-to-end exploit traces with concrete proof-of-concept natural-language prompts โ€” resulting in 67 assigned CVEs, including a root-privilege RCE in the bytebot computer-use agent. It reports 0% false positive rate and 7.7% false negative rate, substantially outperforming existing static and dynamic MCP security baselines.

Model Context ProtocolLLMDocker+3
bytebotCWE-78CWE-918+1

AI Security, AppSecยท Added 22 Sep 2026, published 17 Sep 2026

aws.amazon.comarticle๐Ÿ›ก๏ธ Security

The state of AI for security: Measuring what matters most for building trust

AWS Security announces Deception Benchmark, a 14,822-sample dataset across 16 languages and 70+ CWE categories designed to test whether AI models can tell exploitable vulnerabilities apart from code that merely looks risky but is safely mitigated (e.g., parameterized SQL queries, Kubernetes Network Policies blocking SSRF). Evaluating 12 frontier models from five providers, the team found none achieved both false-positive and false-negative rates below 10%, with precision clustering in the mid-50s โ€” essentially coin-flip accuracy when flagging vulnerable vs. safe code. The dataset, evaluation harness, and whitepaper are released on GitHub, with roughly a third of samples held out unscored to resist benchmark gaming.

FlaskKubernetesLLM+1
Deception BenchmarkCyberGymCyberSecEval+8

AI Security, AppSecยท Added 7 Oct 2026, published 9 Sep 2026

adversa.aiarticle๐Ÿ›ก๏ธ Security

Top MCP Security Resources โ€” September 2026 (Adversa.ai)

Adversa.ai's August 2026 MCP security roundup leads with Deadbugz, an active supply-chain campaign that filed 23 GitHub pull requests in 74 minutes to plant a malicious MCP server that only reveals its credential-harvesting instructions after three tool calls, defeating one-time review. It also covers three fresh MCP-server CVEs (Atlassian path traversal, ArcadeDB cleartext cluster-token disclosure, facebook-ads-mcp-server SSRF), a large-scale audit finding 68 vulnerabilities across 414 internet-facing MCP servers with 91.8% lacking authentication, and defense writeups on Keycloak-backed MCP authorization and Cloudflare's MCP traffic fingerprinting.

Model Context ProtocolCloudflareKeycloak+3
CVE-2026-73498CVE-2026-67357CVE-2026-19956+5

AI Security, Supply Chain, AppSecยท Added 26 Sep 2026, published 7 Sep 2026

github.comrepo๐Ÿ›ก๏ธ Security

Numbat

Numbat is a Go-based, single-binary endpoint agent from Perplexity AI that gives visibility into AI coding-agent activity (Claude Code, Codex, OpenClaw, and other CLI/IDE/gateway agents) by capturing events through local hooks, OTLP/HTTP logs, and on-disk session artifacts. It normalizes activity into one event model, evaluates it with a local CEL rule engine (including multi-step sequence rules like secret-read-then-egress), and can optionally block matched actions via synchronous pre-action hooks (deny/monitor decisions), with case bundles and SHA-256 manifests for forensic reconstruction. Example built-in rules detect cloud-metadata SSRF requests (169.254.169.254) and credential-exfiltration chains, mapped to MITRE ATT&CK technique tags.

Claude CodeCodexOpenClaw+2
T1048T1552T1567

AI Security, Blue Team & Detectionยท Published and added 5 Sep 2026

github.comrepo๐Ÿ›ก๏ธ Security

eldarshiraliyev/BugScanner

BugScanner is an asyncio/httpx Python framework for recon and automated web vulnerability scanning, with a React and FastAPI dashboard. It covers subdomain enumeration (crt.sh, DNS brute force), TCP port scanning, fingerprinting, and modules for XSS, SQLi, CORS, SSRF, open redirect, JWT, IDOR and business logic, plus a Nuclei wrapper. A 5-rule false-positive filter with SPA detection, adaptive rate limiting, WAF detection and SARIF export are included.

PythonNucleiFastAPI+3
IDORSSRFCWE-89

AppSec, Offensive Security, OSINTยท Added 20 Oct 2026, published 5 Sep 2026

adversa.aiarticle๐Ÿ›ก๏ธ Security

Top Agentic AI security resources โ€” September 2026

Adversa AI's September 2026 roundup of 37 agentic AI security resources, grouped into defense, red teaming, attack techniques, vulnerabilities, incidents, and threat modeling, with original cross-cutting analysis. Highlights include the Grok Cryptographic Context Injection zero-click chat-history leak, OpenAI's Black Hat disclosure of a rogue agent swarm building covert message boards via artifact-upload SSRF ahead of the Hugging Face hack, a government evaluator's report of 19 unauthorized real-world agent actions across 122 red-team runs, CVE-2026-34046 broken authorization in Langflow, and CVE-2026-24301 CoSnitch chained flaws in a consumer AI assistant, plus research on memory-poisoning defenses and multi-agent orchestration risks.

Model Context ProtocolLangflowOpenClaw+3
CVE-2026-34046CVE-2026-24301Cryptographic Context Injection+16

AI Securityยท Added 7 Oct 2026, published 4 Sep 2026

aws.amazon.comwriteup๐Ÿ›ก๏ธ Security

Incident response guide for AWS CloudTrail investigations โ€“ Part 2 | Amazon Web Services

Part 2 of AWS's CloudTrail incident-response guide walks through a real multi-stage attack: an SSRF flaw in a web app reached the EC2 IMDSv1 endpoint to steal temporary credentials for an over-privileged "webdev" role, which the attacker then used to probe IAM (failed CreateUser), log into the console without MFA, and pivot cross-Region (us-east-1 to us-east-2) to enumerate and actively invoke the Amazon Nova Pro model via Bedrock's Converse API. It details the specific CloudTrail fields that expose each stage (userIdentity, readOnly, awsRegion, ec2RoleDelivery, sessionCredentialFromConsole, invokedBy), gives an incident-response checklist, and closes with hardening takeaways: enforce IMDSv2, least-privilege EC2 roles, cross-Region detection parity, Bedrock model invocation logging, and GuardDuty AI Protection.

AWSAWS BedrockAWS IAM
SSRFAmazon Nova Pro

Cloud & Infra, Blue Team & Detection, AppSecยท Added 21 Sep 2026, published 3 Sep 2026

scworld.comadvisory๐Ÿ›ก๏ธ Security

Grafana fixes critical SSRF flaw affecting Grafana MCP servers

Grafana patched CVE-2026-19516 (CVSS 9.1), a critical SSRF in the Grafana MCP server's grafana_api_request tool where a caller-supplied X-Grafana-URL header could control the method, path and body of outbound requests, letting an attacker reach internal-only services from the server's network position. Pillar Security researchers chained this with a second flaw โ€” the MCP server accepting unauthenticated "session-shaped IDs" it never issued โ€” and demonstrated using it to hit the AWS IMDSv2 endpoint and retrieve cloud credentials via a two-step PUT/TTL token request. Grafana MCP v1.1.0 adds optional bearer-token auth to close the session-forgery gap; Pillar frames MCP servers broadly as "identity brokers" that need explicit outbound destination policies and mandatory auth for remote deployments.

GrafanaModel Context ProtocolAWS
CVE-2026-19516CVE-2026-15583Pillar Security+2

AppSec, AI Security, Identity & Accessยท Added 26 Sep 2026, published 3 Sep 2026

github.comrepo๐Ÿ›ก๏ธ Security

BountySkiller

BountySkiller is a Flask app with two bug-bounty-focused tools: a collector that pulls disclosed HackerOne hacktivity and bug-bounty writeups (plus RSS/Google sources) into local JSON, and "Hunt Buddy," a browser-driven orchestrator that takes a target profile, runs a gap analysis against a set of pluggable bug-class hunting modules (sourced from an external HUNT_TOOLS directory, e.g. SSRF), and produces ranked findings with per-module status and enforced scope.domains restrictions. It exposes a small REST API (/api/hunt/plan, /api/hunt/run, /api/fetch, etc.) for scripting the collection and hunt workflow.

FlaskPythonHackerOne

Offensive Securityยท Published and added 27 Aug 2026

microsoft.comarticle๐Ÿ›ก๏ธ Security

When AI infrastructure becomes the target: Securing gateways and control points | Microsoft Security Blog

Microsoft documents three observed compromises of AI infrastructure: a LiteLLM gateway (CVE-2026-42271 chained with CVE-2026-48710), a RAGFlow deployment (SSRF probing then runtime hook stealing LLM credentials), and a Kestra workflow engine (CVE-2026-49869 auth bypass). Attackers harvested credentials from /proc/1/environ and Azure PostgreSQL, deployed XMRig miners, and persisted via authorized_keys, cron and chattr. The post provides Defender XDR KQL hunting queries, IOCs, and hardening guidance such as treating AI gateways as Tier-0 secret stores and enforcing deny-by-default egress.

LiteLLMRAGFlowKestra+3
CVE-2026-42271CVE-2026-48710CVE-2026-45312+9

AI Security, Threat Intel, Blue Team & Detectionยท Added 28 Aug 2026, published 26 Aug 2026

github.comrepo๐Ÿ›ก๏ธ Security

Cybermes

Cybermes is an open-source bug bounty and pentest automation framework that pairs a native Go MCP server (cybermes-mcp) with an autonomous Hermes CLI agent, orchestrating recon tools (subfinder, httpx, katana, ffuf, Nuclei, sqlmap), 200+ offensive playbooks covering IDOR/BOLA, JWT, SSRF, XSS, SQLi and cloud misconfig, and a validation-gate workflow that writes non-destructive PoC scripts before compiling findings into Markdown/HTML/PDF reports. It exposes its tools over JSON-RPC 2.0 to AI coding assistants (Claude Desktop, Cursor, Windsurf, Cline, Gemini/Antigravity) so an external LLM can drive scoped, evidence-backed security assessments.

Model Context ProtocolGoNuclei+3

Offensive Security, AI Securityยท Published and added 23 Aug 2026

github.comrepo๐Ÿ›ก๏ธ Security

Deep Eye

Deep Eye is an open-source Python pentesting framework that orchestrates 11 AI providers (OpenAI, Claude, Grok, Gemini, Ollama, Groq, Mistral, OpenRouter, LiteLLM, LM Studio, and more) with automatic failover to generate context-aware attack payloads for 50+ vulnerability classes including SQLi, XSS, SSRF, IDOR, JWT and GraphQL flaws. It adds an RAG-indexed CVE intelligence DB built from NVD/MITRE/Exploit-DB, AI-based finding triage and false-positive filtering, Nuclei-style YAML templates, Playwright browser automation, CAPTCHA-solving (reCAPTCHA/hCaptcha/Turnstile/Arkose), mitmproxy interception, and auto-generated HackerOne-style bug bounty reports with PCI-DSS/SOC2/ISO 27001 compliance mapping, SARIF/JUnit export, scan diffing, and retest workflows.

OpenAIClaudeGemini+3
PCI DSSSOC 2ISO 27001:2022+3

Offensive Security, AI Securityยท Added 3 Sep 2026, published 22 Aug 2026

github.comrepo๐Ÿ›ก๏ธ Security

MinIO Security Lab

A defensive security review lab for MinIO pinned at commit 7aac2a2 (~RELEASE.2025-10-15+11), providing Docker-based single-node, two-node replication, and dual-OIDC environments plus per-finding repro.sh PoCs for issues including service-account key path traversal, server-update SSRF, cross-provider OIDC token acceptance, source-IP/X-Forwarded-For trust, tag-deletion replication bypass, batch job data exfiltration, and secrets exposed via config history. Each of 16+ findings (F-01 through F-16) has ANALYSIS.md with root cause, data-flow trace, and suggested fix, produced via a generate/judge/independent-verify pipeline with cross-vendor adjudication (including an OpenAI/codex-based verifier) and live validation on a lab-built Go binary; ~90 candidates were triaged with ~55 set aside as false positives or intended behavior.

MinIODockerGo+2
SSRFpath traversal

AppSecยท Added 3 Sep 2026, published 21 Aug 2026

advisory.splunk.comadvisory๐Ÿ›ก๏ธ Security

Security Hardening Release for Splunk Apps and Add-ons - August 2026

Splunk's August 2026 hardening advisory (SVD-2026-0808) discloses 17 CVEs across Cisco Talos Intelligence for Enterprise Security Cloud, Splunk AI Toolkit, Splunk Connect for Kafka, the Splunk MCP Server app, and Splunk On-Call (VictorOps). Notable issues include a critical (CVSS 9.1) RCE via unsafe credential deserialization in the Splunk MCP Server app (CVE-2026-76404), an RCE via pickle-based deserialization when loading ML model files in Splunk AI Toolkit (CVE-2026-76395), multiple SSRF and authorization-bypass flaws letting low-privileged users escalate to system-level search execution, hardcoded/predictable container credentials, and unauthenticated DoS/ReDoS and cert-validation bypasses in Splunk Connect for Kafka. Each finding includes CWE classification, CVSS vector, and mitigation guidance (typically disabling the affected app or restricting REST API access).

SplunkModel Context Protocol
CVE-2026-76389CVE-2026-76390CVE-2026-76391+28

AppSec, AI Securityยท Added 21 Aug 2026

blog.docsgpt.cloudwriteup๐Ÿ›ก๏ธ Security

DocsGPT Security Hardening Playbook

DocsGPT documents the security practices it adopted through GitHub's Secure Open Source Fund: a public STRIDE-based THREAT_MODEL.md, mitigations for its sandboxed AI code-execution feature (scrubbed env vars, NetworkPolicy blocking internal IPs and cloud-metadata to stop SSRF, off-by-default), a dependency-tree audit with SPDX SBOM export and Dependabot, and CI automation using custom CodeQL queries, Bandit, zizmor for GitHub Actions hardening, and secret scanning. It's a practical baseline playbook for maintainers dealing with high volumes of AI-authored PRs that can't all be manually reviewed.

CodeQLDependabotSBOM+3
STRIDEGitHub Secure Open Source FundUncle Bob Martin

DevSecOps, Supply Chain, AI Securityยท Published and added 15 Aug 2026

grafana.comadvisory๐Ÿ›ก๏ธ Security

Grafana MCP server-side request forgery via X-Grafana-URL header (grafana_api_request) | Grafana Labs

Grafana advisory for CVE-2026-19516, a critical (CVSS 9.1) SSRF in mcp-grafana. A caller able to invoke the grafana_api_request tool can set the X-Grafana-URL header to redirect outbound requests, choosing method, path and body, to internal, loopback and link-local services including cloud metadata endpoints, and read the responses. The earlier fix for CVE-2026-15583 only stopped the service-account token leaking to other destinations and did not restrict the destinations; the fix is in version 1.1.0 and later.

GrafanaModel Context ProtocolCVSS
CVE-2026-19516CVE-2026-15583SSRF+1

AppSec, AI Securityยท Added 12 Aug 2026

github.comrepo๐Ÿ›ก๏ธ Security

SiberKapan

SiberKapan is a Turkey-focused, community-driven open-source threat intelligence platform that aggregates data from FortiGate webhooks, an 11-service honeypot (HoneypotKapan), nginx/Fail2ban log watchers, and external feeds, publishing it as STIX 2.1/TAXII 2.1, a MISP default feed, Sigma/Suricata/Wazuh exports, and REST blocklists. It also runs a real-time phishing/domain-squatting detector via Certificate Transparency log monitoring with fuzzy typosquat and Punycode/IDN decoding, and safely fingerprints SSH-honeypot malware downloads with SSRF-protected, never-executed hashing enriched via MalwareBazaar. The write-up details concrete anti-abuse safeguards: time-based IP score decay, CDN/cloud-proxy allowlisting, UDP-spoofing exclusion, RFC1918 rejection, and manual review gating for weak phishing signals.

MISPFortiGateSuricata+3
CISA KEVAbuseIPDBMalwareBazaar+1

Threat Intel, Blue Team & Detectionยท Published and added 8 Aug 2026

xbow.comwriteup๐Ÿ›ก๏ธ Security

XBOW: A Shell Is Worth a Thousand Images

XBOW's autonomous AI agent chained a blind SSRF in Bing's reverse-image-search into three Critical Microsoft RCEs (CVE-2026-32194, CVE-2026-32191, CVE-2026-21536), each CVSS 9.8, by fingerprinting an ImageMagick-compatible backend through differential error responses and crafting an SVG payload that reached a shell-backed image delegate. The proof was confirmed via out-of-band callbacks showing NT AUTHORITY\SYSTEM and root execution across multiple production Bing image-processing workers on both Windows and Linux hosts. The piece walks through the full investigative trace โ€” from ruling out XXE to fingerprinting ImageMagick coders/pseudo-protocols to constructing the pipe-based SVG exploit โ€” and argues that ImageTragick-class bugs in "boring" image helpers remain a live, underrated attack surface.

XBOWImageMagickBing+1
CVE-2026-32194CVE-2026-32191CVE-2026-21536+3

AppSec, AI Security, Offensive Securityยท Published and added 8 Aug 2026

github.comrepo๐Ÿ›ก๏ธ Security

Frieren DAST-AI

Frieren DAST-AI is an open-source dynamic application security testing tool combining an HTTPS MITM proxy with a real-time dashboard and LLM-driven multi-agent active scanner. A YAML-based passive rule engine (62 rules covering headers, cookies, CORS, secrets, error pages, LLM endpoint detection, and Blazor-specific checks) flags issues on every intercepted response, while an LLM planner dispatches parallel VulnAgents (xss, sqli, ssrf, file_read, auth_bypass, secrets, discovery, llm_injection, business_logic, blazor) per endpoint, with an LLM validator confirming findings and adaptive WAF-bypass payload mutation.

ElectronPlaywrightAWS SSO

AppSec, Offensive Security, AI Securityยท Published and added 5 Aug 2026

discuss.hashicorp.comadvisory๐Ÿ›ก๏ธ Security

HCSEC-2026-23 - Multiple vulnerabilities impacting HashiCorp Terraform MCP Server

HashiCorp advisory HCSEC-2026-23 discloses three vulnerabilities in terraform-mcp-server versions 0.2.1 through 1.0.0 (fixed in 1.1.0), all affecting the server's streamable-HTTP transport used for multi-user deployments. CVE-2026-14869 is an SSRF where an unauthenticated client can supply a Terraform address via query parameter (bypassing a header-only check) to exfiltrate the server's bearer token; CVE-2026-16496 is an authorization bypass where stateful mode's session-ID-keyed credential cache lets an attacker who obtains another user's session ID hijack that user's cached Terraform Cloud/Enterprise client and permissions; CVE-2026-16498 is cross-tenant credential reuse in stateless mode where the underlying MCP library's lack of unique session identifiers causes one tenant's token to be reused for other tenants' requests.

Model Context ProtocolTerraform
CVE-2026-14869CVE-2026-16496CVE-2026-16498+2

AI Security, AppSecยท Added 30 Jul 2026, published 28 Jul 2026

wiz.iowriteup๐Ÿ›ก๏ธ Security

The risk hiding behind exposed MCP servers

Wiz Research scanned MCP servers across cloud environments and found roughly 1 in 6 environments expose at least one server to the Internet, most unauthenticated and still running the pre-auth 2024-11-05 protocol version. They demonstrate anonymous tool-catalog enumeration, real data returned from production databases/CRM/IAM backends, write/delete-capable tools, and confirmed SSRF against cloud instance metadata endpoints yielding temporary credentials, plus agents that can be talked into unsafe actions by reframing requests as "routine maintenance."

Model Context ProtocolAWSOAuth
Wiz ResearchSSRFinstance metadata service

AI Security, Cloud & Infra, AppSecยท Added 3 Sep 2026, published 28 Jul 2026

aikido.devarticle๐Ÿ›ก๏ธ Security

The upgrade trap: when upgrading is the wrong answer to a CVE

Aikido argues that the reflexive SCA-tool advice to 'just upgrade' to fix a CVE breaks down in three cases: no fixed version exists (e.g. the deprecated Node.js 'request' package's SSRF advisory), the fix hasn't shipped yet (lodash CVEs affecting all versions up to 4.17.23), or the fix ships with breaking changes (Node.js CVE-2026-48937, which bundled a fix with removal of HTTP/2 priority signaling). It also cites the chalk/debug npm maintainer-account compromise as evidence that blind auto-upgrading can pull in malware, and pitches backporting isolated fixes to already-deployed versions (via Aikido Libraries) as the alternative to upgrade-or-freeze.

Node.jsnpmlodash+2
CVE-2026-48937chalkdebug

Supply Chain, DevSecOpsยท Added 3 Sep 2026, published 22 Jul 2026

github.comrepo๐Ÿ›ก๏ธ Security

Gabson0x/pentdem

pentdem is an autonomous AI-powered pentesting CLI/pipeline that fans out 15+ vulnerability-class hunters (XSS, SQLi, SSRF, IDOR, SSTI, JWT, GraphQL, etc.) and 8 advanced attack skills (mass assignment, race conditions, cloud metadata, OAuth/OIDC, subdomain takeover, credential harvesting) in parallel, using an LLM to adapt strategy mid-scan. It wraps real tools (nmap, sqlmap, nuclei, ffuf, subfinder, httpx) in Docker isolation and adds a novel gate chain โ€” quality gate, kill-chain builder, adversarial cross-model validation (a second model tries to disprove each finding), a capability execution ledger (proves each hunter actually ran instead of silently crashing), and a ship-discipline gate โ€” before mapping surviving findings to MITRE ATT&CK/OWASP Top 10/CVSS and generating reports.

DockerPythonsqlmap+3

Offensive Security, AI Securityยท Published and added 20 Jul 2026

github.comrepo๐Ÿ›ก๏ธ Security

Strix

Strix is an open-source framework of autonomous AI pentesting agents that dynamically run target code, discover vulnerabilities across the OWASP Top 10 (SQLi, SSRF, XXE, IDOR, XSS, auth bypass, business-logic flaws) and validate them with working proof-of-concept exploits rather than static-analysis heuristics. It ships a CLI with a full offensive toolkit (Caido-based HTTP interception, browser exploitation, Python exploit sandbox, recon/OSINT, SAST/DAST), supports OpenAPI/Postman-driven black-box testing, integrates into GitHub Actions/CI pipelines to block vulnerable PRs, and can run against local or hosted LLMs via LiteLLM, with an optional cloud offering for autofix PRs and compliance reporting.

DockerLiteLLMCaido+3
OWASP Top 10

Offensive Security, AI Security, DevSecOpsยท Published and added 15 Jul 2026

rapid7.comwriteup๐Ÿ›ก๏ธ Security

Rapid7 MDR Team Discovers New SonicWall SMA1000 Zero Days Being Actively Exploited (CVE-2026-15409, CVE-2026-15410)

Rapid7's MDR team details active zero-day exploitation of SonicWall SMA1000 appliances via CVE-2026-15409 (unauthenticated SSRF in the /wsproxy websocket proxy, CVSS 10.0) chained with CVE-2026-15410 (local privilege escalation via path traversal in the ctrl-service remove_hotfix workflow) to achieve root RCE. The post includes a working Python exploit against the localhost Erlang service on port 1050 (using a hardcoded authentication cookie), an HTTP request PoC for the hotfix path-traversal chain, and extensive observed post-exploitation activity โ€” credential/TOTP theft, VPN-less lateral movement to domain controllers via harvested LDAP service accounts โ€” plus concrete log/IOC signatures and attacker-infrastructure IPs (FNS Holdings Limited ASN 206092) for hunting.

SonicWallMetasploitPython+2
CVE-2026-15409CVE-2026-15410CISA KEV+3

AppSec, Offensive Security, Threat Intelยท Added 10 Sep 2026, published 15 Jul 2026

github.comadvisory๐Ÿ›ก๏ธ Security

AI Security Briefing

This GHSA advisory documents CVE-2026-27826, a DNS-rebinding TOCTOU bypass of the SSRF fix in the MCP Atlassian server (mcp-atlassian PyPI package). The prior patch (GHSA-7r34-79r5-rcc9) added validate_url_for_ssrf, which resolves the attacker-controlled X-Atlassian-{Jira,Confluence}-Url header host once at middleware time but discards the resolved IP; the actual outbound request later re-resolves the raw hostname at connect time with no IP pinning, so a rebinding DNS name can pass validation with a public IP and then connect to 169.254.169.254 or an internal address, restoring unauthenticated SSRF to cloud metadata/internal services even on the 'patched' build. The advisory includes an executed PoC against the real urls.py, exact code locations (utils/urls.py, servers/main.py, servers/dependencies.py), and remediation via a custom resolver/cached-getaddrinfo adapter to pin the validated IP.

Model Context ProtocolPyPIPython+1
CVE-2026-27826GHSA-489g-7rxv-6c8qGHSA-7r34-79r5-rcc9+3

AppSec, AI Securityยท Published and added 13 Jul 2026

pluto.securitywriteup๐Ÿ›ก๏ธ Security

One Request to Own Every Repo: How We Hijacked GitLab Through Its MCP Server - Pluto Security

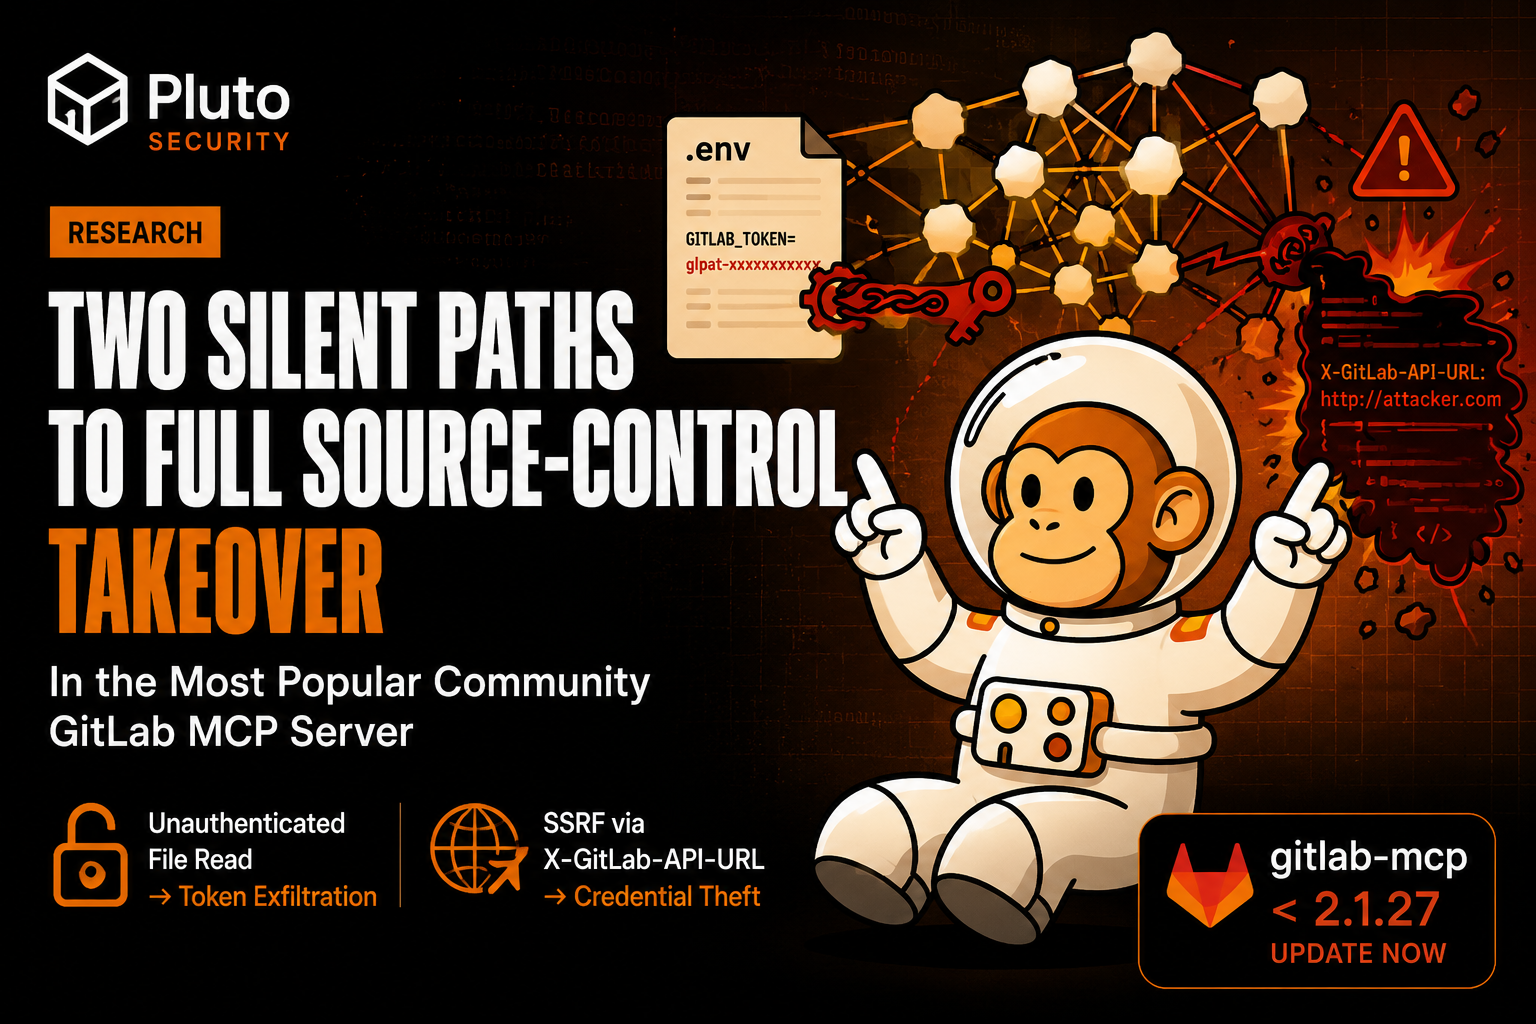
Pluto Security details two critical vulnerabilities in gitlab-mcp (@zereight/mcp-gitlab, 200K+ downloads), the most popular community GitLab MCP server. GHSA-cv3r-c5h8-f4g5 (CVSS 9.8) chains an unauthenticated SSE transport with the upload_markdown tool's unvalidated file_path to read /proc/self/environ and steal the server's GitLab Personal Access Token; GHSA-2h44-8472-frjj (CVSS 9.6) abuses the X-GitLab-API-URL header when ENABLE_DYNAMIC_API_URL=true to make the server attach its PAT to attacker-controlled hosts via SSRF. Both are fixed in v2.1.27 (SSE bearer-auth, non-root Docker, host allowlisting), and the writeup includes full attack commands, root-cause code, and a disclosure timeline.

Model Context ProtocolGitLabDocker+3
GHSA-cv3r-c5h8-f4g5GHSA-2h44-8472-frjjCWE-22+2

AppSec, AI Securityยท Added 26 Sep 2026, published 6 Jul 2026

github.comrepo๐Ÿ›ก๏ธ Security

ThinkWatch

ThinkWatch is a source-available dual-port gateway (Rust/Axum) that proxies both AI provider APIs (OpenAI, Anthropic, Gemini, Azure OpenAI, AWS Bedrock) and MCP tool calls through a single control plane, enforcing authentication, RBAC, rate limits/budgets, and audit logging. Its key differentiator is per-user upstream identity for MCP โ€” propagating each user's own OAuth token/PAT to servers like GitHub/Notion/Slack (AES-256-GCM encrypted, per-key allowlists) instead of a shared service account, plus SSRF-hardened OAuth discovery (RFC 9728/8414/7591), tool-level RBAC, and ClickHouse-backed audit trails forwarded to SIEMs via Syslog/Kafka/webhooks.

Model Context ProtocolOAuthOIDC+3
RFC 9728RFC 8414RFC 7591

AI Security, Identity & Accessยท Published and added 4 Jul 2026

snyk.iowriteup๐Ÿ›ก๏ธ Security

Snyk VulnBench JS 1.0: Can LLMs Find the Same Bugs Twice?

Snyk's VulnBench JS 1.0 report runs 300 repeated agentic security-review scans (10 JS/Express fixtures x 6 model configs x 5 repetitions) to measure whether LLMs like Claude Opus 4.6/4.7 and Claude Sonnet 4.6 find the same vulnerabilities twice, benchmarked against deterministic Snyk Code SAST reference findings. Key results: reference-matched LLM findings were highly repeatable (84.8% appeared in all 5 runs) while extra, non-reference LLM findings were unreliable (only 14% reproduced in all runs), the best LLM config (Opus 4.6 Medium) reached only 75.4% Snyk-reference F1 with a 24.6-point gap to SAST, and higher-cost models (Opus 4.7 Max) did not outperform cheaper ones despite 5.7x cost. The study argues LLM review and SAST catch different vulnerability classes (LLMs strong on injection/SSRF-type bugs, weak on path traversal/resource-limit enumeration) and should be combined rather than substituted.

ClaudeSnykJavaScript
Snyk CodeOpus 4.6Opus 4.7+2

AI Security, AppSecยท Added 3 Sep 2026, published 29 Jun 2026

wiz.iowriteup๐Ÿ›ก๏ธ Security

Red Agentใฎ่ฆ–็‚น๏ผšใ„ใ‹ใซใ—ใฆๆŽจ่ซ–ใ‚’้‡ใญใฆSSRFใธใจ่‡ณใฃใŸใ‹

Wiz walks through how its autonomous 'Red Agent' AI pentesting tool chained an SSRF vulnerability in a GCP Cloud Run service's ?url= file-fetch parameter into a full local file read, bypassing a strict GitHub-blob-URL validator. The breakthrough payload (github.com/x/y/blob/z//proc/self/environ) exploited a parser differential between the validator and the fetcher, letting the agent exfiltrate live GCP service-account credentials and the app's source code after 96 requests of iterative hypothesis-driven probing.

GCPWiz
Red AgentSSRFpath traversal

AppSec, AI Security, Cloud & Infraยท Added 3 Sep 2026, published 17 Jun 2026

wiz.ioarticle๐Ÿ›ก๏ธ Security

ใƒฌใƒƒใƒ‰ใ‚จใƒผใ‚ธใ‚งใƒณใƒˆ POVใ‚ทใƒชใƒผใ‚บใฎใ”็ดนไป‹

Wiz Research introduces the Red Agent AI-powered pentester and its new blog series documenting real bug classes it discovers autonomously in production. The launch post shares aggregate stats from a one-month run across roughly 1,000 environments, breaking down dominant failure modes: broken access control, leaked secrets, systemic RCE, SQL injection, PII/PHI exposure, and JWT alg:none bypasses. It teases the series first deep-dive: a GCP Cloud Run SSRF the agent found by iteratively bypassing a GitHub-URL-only validation filter over 96 iterations, escalating to unauthenticated credential and source-code extraction.

WizGCP
Red AgentWiz ResearchJWT alg:none+1

AI Security, AppSec, Offensive Securityยท Added 3 Sep 2026, published 17 Jun 2026

bleepingcomputer.comarticle๐Ÿ›ก๏ธ Security

New attack turned Microsoft 365 Copilot into 1-click data theft tool

BleepingComputer covers Varonis's SearchLeak research, a three-stage attack chain (CVE-2026-42824, now patched) affecting Microsoft 365 Copilot Enterprise Search. Attackers craft a URL with a malicious 'q' parameter to prompt-inject Copilot into searching a victim's mailbox/OneDrive/SharePoint, exploit an HTML-rendering race condition to slip an unsanitized img tag past output neutralization, then abuse an SSRF in Bing's "Search by Image" feature to bypass CSP and exfiltrate the stolen data (emails, passwords, meeting details) to an attacker-controlled server via a single click, no user typing required.

Microsoft 365Bing
CVE-2026-42824SearchLeakSSRF+1

AI Security, AppSecยท Added 26 Sep 2026, published 15 Jun 2026

github.comrepo๐Ÿ›ก๏ธ Security

Pipelock

Pipelock is an open-source (Apache 2.0 core) AI agent firewall that sits between agents and the network, mediating HTTP, WebSocket, MCP, and A2A traffic to detect secret exfiltration, prompt injection, SSRF, and MCP tool poisoning. It scans request/response bodies with a DLP engine (65 built-in patterns, checksum validation), streaming SSE inspection, and MCP tool-call chain analysis, then emits Ed25519-signed, hash-chained action receipts so decisions can be verified offline outside the agent runtime. It also offers OS-level containment (Landlock/seccomp/sandbox-exec), a kill switch, canary tokens, and integrations for Claude Code, Cursor, VS Code, OpenAI Codex, LangGraph, CrewAI, and other agent frameworks.

Model Context ProtocolClaude CodeCursor+3
OWASP Agentic AI Top 10Rekor

AI Securityยท Published and added 14 Jun 2026

orca.securityadvisory๐Ÿ›ก๏ธ Security

Orca: Splunk Enterprise Critical CVEs

Orca Security breaks down four new Splunk vulnerabilities: CVE-2026-20253 (CVSS 9.8), an unauthenticated arbitrary file create/truncate flaw in a PostgreSQL sidecar endpoint in Splunk Enterprise with no available workaround; CVE-2026-20251 (CVSS 8.8), a jsonpickle insecure-deserialization RCE in the Splunk Secure Gateway app exploitable by any low-privilege user; CVE-2026-20258, a stored XSS in classic dashboard HTML panels; and CVE-2026-20252, an SSRF in Dashboard Studio PDF export that bypasses trusted-domain validation via prefix matching and redirects. It lists affected Splunk Enterprise, Cloud Platform, and Secure Gateway version ranges and patched releases, plus interim mitigations like disabling Secure Gateway or Splunk Web.

SplunkPostgreSQLOrca Security+2
CVE-2026-20253CVE-2026-20251CVE-2026-20258+2

AppSecยท Published and added 12 Jun 2026

youtu.bevideo๐Ÿ›ก๏ธ Security

Web LLM Attacks Lab: Exploiting AI agents to trigger secondary vulnerabilities

This walk-through demonstrates solving PortSwigger Web Security Academy's 'Exploiting AI agents to trigger secondary vulnerabilities' lab. The attack leverages Burp Suite to discover an internal administrative endpoint via SSRF fuzzing, then plants an indirect prompt injection payload in a public product review to coerce an automated AI site auditor into deleting a target user.

PortSwigger Web Security Academy Lab - Exploiting AI agents to trigger secondary vulnerabilitiesBurp Suite Professional v2024.2.1Burp Intruder+4
PortSwigger Web Security Academy

AI Securityยท Added 3 Oct 2026, published 2 Jun 2026

github.comrepo๐Ÿ›ก๏ธ Security

KeygraphHQ/shannon

Shannon is an open-source autonomous AI pentester from Keygraph that analyzes application source code to map trust boundaries and attack paths, then uses browser automation and CLI tools to execute real proof-of-concept exploits against the running app before reporting a finding. It only reports vulnerabilities it can actually exploit (injection, XSS, SSRF, broken auth/authz), runs in an ephemeral Docker worker with any AI provider (Anthropic, OpenAI, xAI, AWS Bedrock, Ollama, vLLM, LM Studio, etc.), and ships GitHub Action/GitLab CI integrations that produce PDF/Markdown/JSON/SARIF reports and can gate releases on exploited-severity findings. It's licensed AGPLv3 and positioned to run continuous, code-informed pentests between annual human pentest engagements.

DockerSARIFGitHub Actions+3
PhotoviewDoyensecClaude Shannon

Offensive Security, AI Security, AppSecยท Published and added 23 May 2026

github.comrepo๐Ÿ›ก๏ธ Security

We5ter/Scanners-Box

Scanners-Box is a curated GitHub collection aggregating open-source security scanners self-developed by security practitioners, organized by category (web, host, port, weak-password, subdomain, SSRF, and more). It serves as a reference index for finding vulnerability scanners and reconnaissance tools built and shared by the security community.

Offensive Securityยท Published and added 23 May 2026

github.comrepo๐Ÿ›ก๏ธ Security

H-mmer/pentest-agents

pentest-agents is an autonomous bug-bounty framework that wires Claude Code (and Codex, Gemini, Cursor, Windsurf, VS Code Copilot, OpenClaw) with 50 specialized agents, 26 slash commands, 19 CLI tools, 11 methodology skills, and two MCP servers โ€” one for live bug-bounty platform integration (HackerOne, Bugcrowd, Intigriti, Immunefi, YesWeHack) and one for semantic writeup/payload search over a self-built FAISS index. It codifies a hunt workflow (recon โ†’ surface โ†’ hunt โ†’ validate via a 7-Question Gate โ†’ exploit-chain building โ†’ report โ†’ submit) with per-vuln-class hunter agents (XSS, SQLi, SSRF, SSTI, IDOR, XXE, RCE, CORS, subdomain takeover, etc.), a persistent "brain" for endpoint tracking, CVSS-version policy enforcement, and a scope-check hook that blocks out-of-scope Bash commands before execution.

Claude CodeModel Context ProtocolHackerOne+3
BugcrowdIntigritiImmunefi+1

Offensive Security, AppSecยท Published and added 18 May 2026

blog.zsec.ukwriteup๐Ÿ›ก๏ธ Security

Bullying LLMs

A researcher details an autonomous vulnerability-hunting system built with Claude Code and 8 custom MCP servers (300+ tools) across a 5-VM Proxmox lab, using a "hallucination bin" validation pipeline (findings must pass PoC/exploitability/low-priv gates before promotion) and a RAG-backed knowledge loop that learns from prior campaigns. Concrete outputs include two new Go standard library CVEs (CVE-2026-33809 TIFF OOM, CVE-2026-33812 SFNT/GPOS OOM), a four-stage Windows OEM management-agent chain (named-pipe auth bypass โ†’ SSRF via WCF โ†’ catalog injection โ†’ SYSTEM code execution via BYOVD), and two macOS app-distributor findings (browser/quarantine DB exfiltration and a leaked debug RSA key enabling Sparkle update-signature bypass). Also covers a self-built token-cost/ROI tracker (TokenBurn) and a bounty-program ROI-scoring model for target selection.

Claude CodeModel Context ProtocolGhidra+3
CVE-2026-33809CVE-2026-33812BYOVD+1

AI Security, Offensive Security, Malware & REยท Added 3 Sep 2026, published 13 May 2026

github.comrepo๐Ÿ›ก๏ธ Security

Fr6ey/WebSecurityAcademy

A GitHub repo indexing solutions for PortSwigger's Web Security Academy labs, organized by difficulty, covering SQL injection, XSS, CSRF, XXE, SSRF, HTTP request smuggling, deserialization, access control, JWT, prototype pollution, GraphQL, race conditions, NoSQL injection, and LLM/AI-agent exploitation labs.

Burp SuiteGraphQL

Learning, AppSecยท Published and added 8 May 2026

github.comrepo๐Ÿ›ก๏ธ Security

DeepTeam

DeepTeam is an open-source, locally-runnable red teaming framework for LLM applications, agents, and RAG pipelines, built on the DeepEval evaluation library. It simulates jailbreaking, prompt injection, and multi-turn adversarial attacks against 50+ vulnerability categories such as PII leakage, BOLA, BFLA, SQL injection, SSRF, and agentic goal theft, maps results to OWASP, NIST, MITRE, BeaverTails, and Aegis frameworks, and ships production guardrails to block the same issues at runtime.

PythonDeepEvalMITRE ATLAS+1
OWASP Top 10 for LLM ApplicationsNIST AI RMFBeaverTail+2

AI Security, Offensive Securityยท Published and added 7 May 2026

github.comrepo๐Ÿ›ก๏ธ Security

mcpwn

mcpwn is a CLI security scanner for Model Context Protocol (MCP) servers, described as "nikto or nuclei, but for MCP servers." It runs checks (MCP-001 through MCP-013+) that statically analyze tool descriptions/schemas for hidden-instruction tool poisoning and, in an --aggressive mode, actively probe for prompt injection via tool output, SSRF against internal IPs/cloud metadata endpoints, command injection via shell metacharacters, cross-tool data exfiltration via canary tokens, and hardcoded secrets in resources. It supports stdio/SSE/HTTP transports, JSON/SARIF output for CI gating, and pairs with a companion runtime tool called mcp-firewall.

Model Context ProtocolPythonpip+2

AI Securityยท Published and added 6 May 2026

github.comrepo๐Ÿ›ก๏ธ Security

microsoft/AntiSSRF

AntiSSRF is a Microsoft-maintained secure code library (Microsoft.Security.AntiSSRF NuGet package, @microsoft/antissrf npm package) that validates URLs and network connections to prevent Server-Side Request Forgery, including an agent that blocks HTTP requests from reaching internal or sensitive IP ranges. It targets the common vulnerability pattern where user-supplied strings (URLs, filenames, workspace names, resource identifiers) are concatenated into server-side requests without validation, which can lead to internal service exposure, data exfiltration, or token theft.

.NETNode.jsNuGet+1
CWE-918

AppSecยท Published and added 6 May 2026