securityweek.comarticle🛡️ Security
China-Linked Hackers Exploit PHP2Shell to Root Firewalls
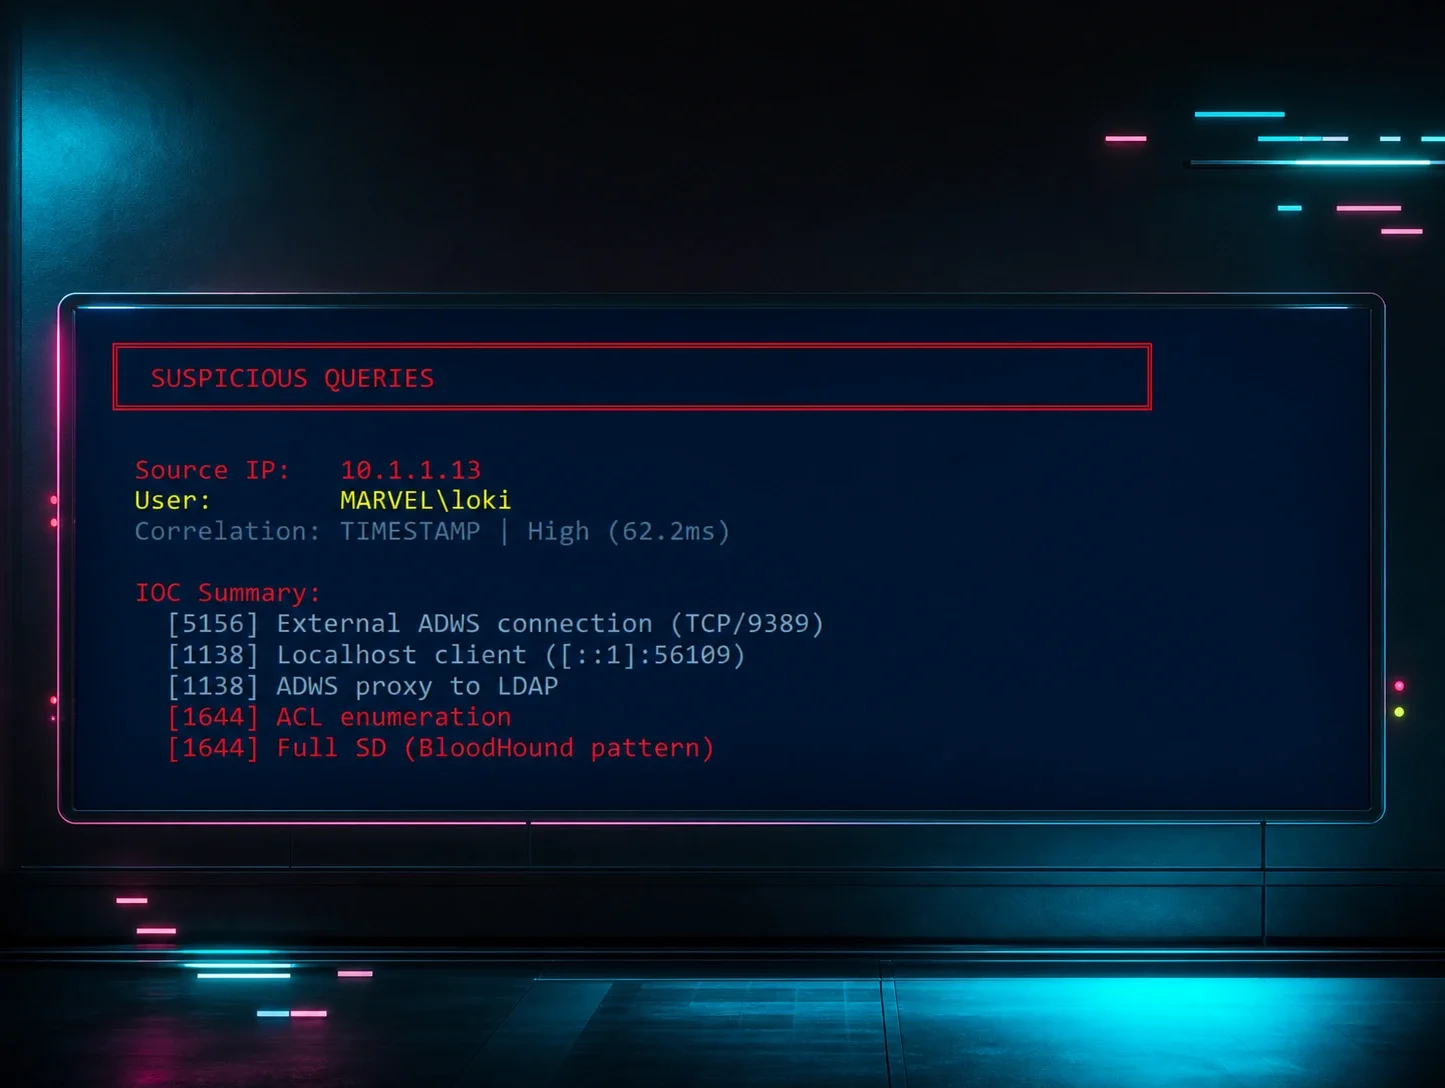
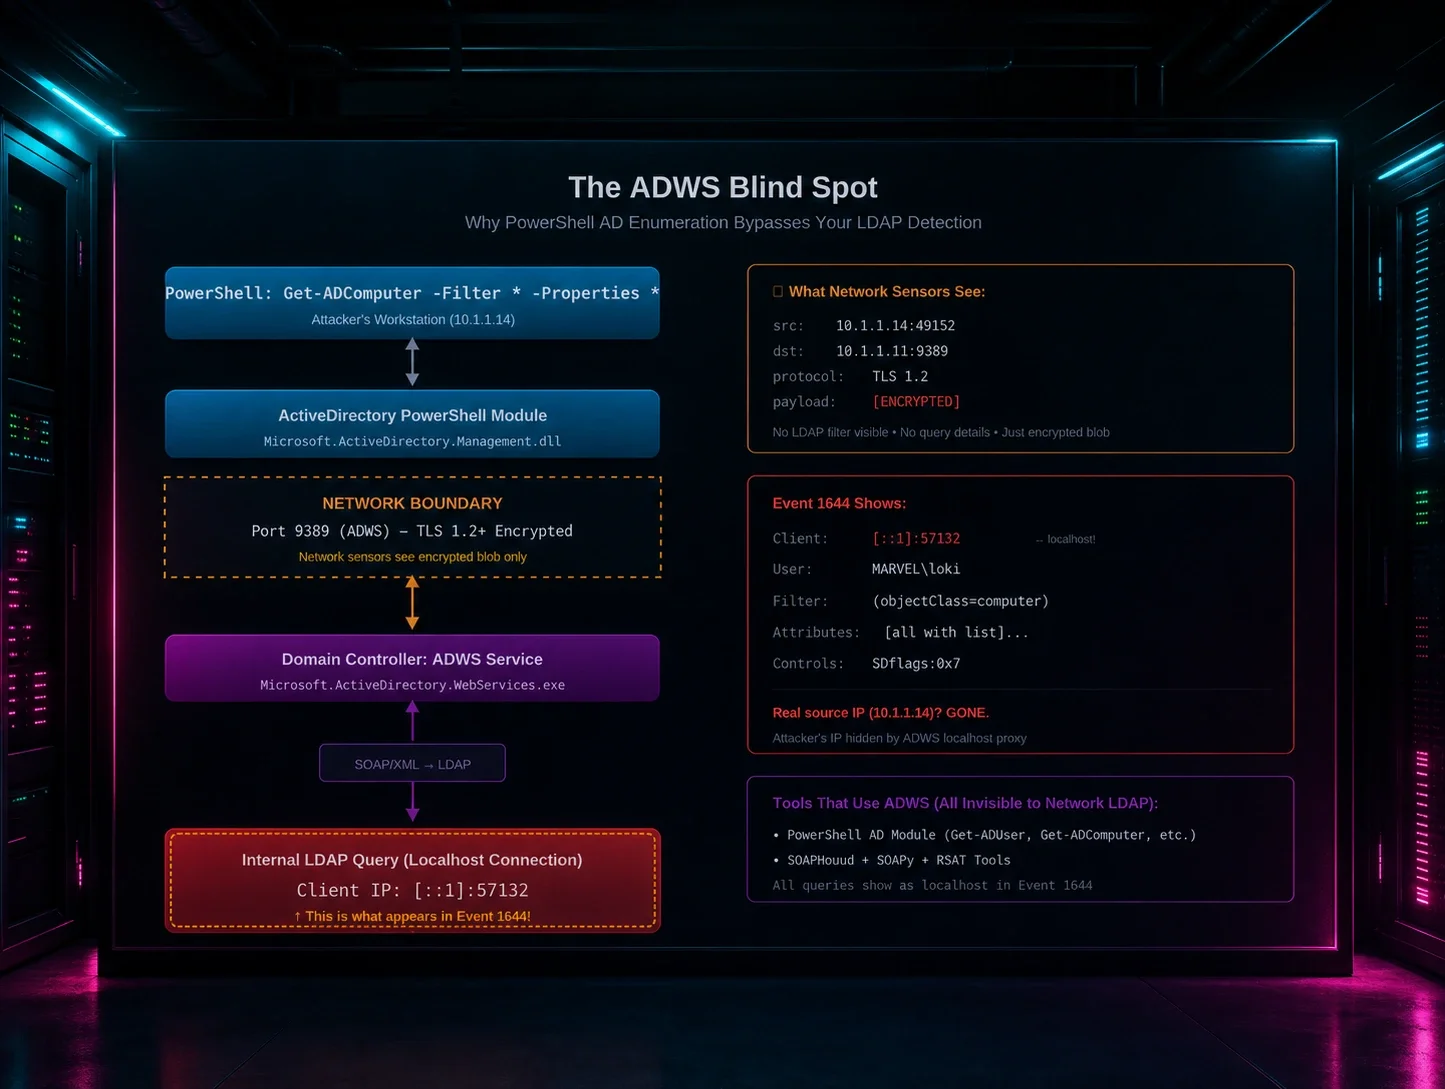
A China-linked actor chained PHP2Shell (CVE-2026-109618, CVE-2026-109619) with the Fragnesia Linux kernel privilege escalation (CVE-2026-46300) to root firewalls and drop PHP webshells, per Dream. Using FOFA, the actor narrowed 19,000 firewalls to 240 targets and rooted 24 on 23-24 October. On two US government-affiliated devices it used a reverse SSH tunnel, hit the firewall management server, and attempted LDAP and Active Directory abuse.
PHPLinux kernelSSH+2
CVE-2026-109618CVE-2026-109619CVE-2026-46300+7
Threat Intel, Offensive Security· Published and added 28 Oct 2026