 LiteLLM PyPI Package and Docker Images Compromised to Steal Cloud and AI Credentials
LiteLLM 1.107.0 on PyPI and GHCR images shipped Python startup hooks (cook.pth, sitecustomize.py) that steal cloud, SSH, browser and AI-tool credentials, including LiteLLM proxy database credentials. Image build provenance recorded a lookalike Berri-AI/litellm source repository. The post decodes the payload, encrypted exfiltration and GitHub-driven remote loader, and lists containment steps, MITRE ATT&CK mappings and IOCs.
 socket.devwriteupPublished and added 21 Oct 2026🛡️ Security
- #StopRansomware: SafePay Ransomware (AA26-293A)
CISA advisory AA26-293A (20 October 2026) details SafePay ransomware, active since August 2024 with at least 600 victims across critical infrastructure. It covers initial access via Mullvad VPN IPs, phished profiles and edge-device CVEs, LOTL lateral movement with PsExec, WinRM and RDP, exfiltration with RClone and WinSCP, and ChaCha20/RSA encryption. It lists IOCs, MITRE ATT&CK mappings, incident response steps and mitigations.
 cisa.govadvisoryAdded 21 Oct 2026🛡️ Security
 MITRE ATT&CK v20 Catalogs AI Abuse, MFA Bypass, Water Utility Attacks
MITRE ATT&CK v20 adds nine Enterprise techniques and sub-techniques, including two prompt injection techniques, abuse of an organization's own AI agents for data theft, application-specific password theft and CAPTCHA bypass. ICS gains campaigns on internet-exposed PLCs at over 30 Minnesota water utilities and an AI-assisted breach of Mexican government bodies. It also adds Nimbus Manticore, The Gentlemen, 15 detection strategies with 38 analytics, and NGate for Mobile.
 securityweek.comarticlePublished and added 19 Oct 2026🛡️ Security
- AI Security Wiki: Governance, Risk, Standards and Test Cases
A vendor-neutral AI Security Wiki acting as an implementation layer for enterprise AI adoption: risk methodology, AI risk register, control objectives library, domain standards (browser/IDE AI, runtime apps, agentic AI, sovereignty), vendor evaluation framework, and audit/evidence checklists. It includes a 653-case product evaluation test library across 17 lifecycle layers and 6 emerging domains, plus regulatory hubs for GCC, EU, Australia, Brazil, Canada, China, India, Japan, Singapore, South Korea, UK and US, and crosswalks to FINOS AIGF, NIST AI RMF, ISO/IEC 42001, OWASP, MITRE ATLAS, ISO 27001 and others. Useful as a template and evidence source for teams building AI governance and assurance programmes.
 nachi065.github.iootherAdded 15 Oct 2026🛡️ Security
- dbugs (@ptdbugs) on X
Decepticon is an open-source framework that automates red team operations with 16 specialized AI agents coordinated by an orchestrator, covering recon, vulnerability research and exploitation against an operator-authorized target in an isolated environment. It offers optional attack planning mapped to MITRE ATT&CK, persistent interactive sessions for Metasploit, Sliver and Evil-WinRM, and findings stored in project files and a knowledge graph. It runs via CLI or web dashboard, integrates with Claude Code and Codex through an MCP server, and is self-hosted with Docker Compose.
 x.comtoolAdded 18 Oct 2026, published 15 Oct 2026🛡️ Security
 Artificial Intelligence (AI) in Cybersecurity, Part 28: Using ADStrike to Compromise Active Directory
ADStrike is an Active Directory attack framework with 52 attack modules and configurable OPSEC levels. An optional AI orchestrator, run here on a local Ollama model such as Qwen 2.5-coder 7b, picks the next tool from each step's output. The walkthrough runs it from Kali against a lab domain with an unprivileged account. It covers LAPS checks, kerberoasting, Timeroasting, Pre2k, SharpHound/BloodHound analysis and HTML reports with MITRE ATT&CK coverage.
 hackers-arise.comwriteupPublished and added 12 Oct 2026🛡️ Security
- CISA AA26-281A: Chinese Government-linked Actors Combine Automated and Hands-on Hacking Tools to Steal Data
Joint FBI/CISA/NSA and allied-agency advisory on China-linked actors enabled by Integrity Technology Group (overlapping with Flax Typhoon, Ethereal Panda, Red Juliett). It details their TTPs: open-source scanners and the MicroScan exploit-script app, an XSS credential-harvesting payload dropping live700_v1.exe, EBurst password spraying against Exchange/O365, SoftEther VPN persistence, DCSync via DC.exe, and email theft via the Curlc4.txt PHP bot and the office-cli utility. It also provides IOCs, MITRE ATT&CK mappings, CVEs, incident response steps, and mitigations.
cisa.govadvisoryAdded 9 Oct 2026🛡️ Security  Pretty Themes, Hidden Loaders: GlassWorm-Linked Extensions Span VS Code Marketplace and Open VSX
Socket's Threat Research team uncovered a theme-extension cluster spanning four VS Code Marketplace and six Open VSX listings, including two confirmed malicious extensions: Aurora Nocturne Night Theme (a Windows downloader that fetches and silently executes temp_batch.cmd via cmd.exe from fingercakes4sale[.]store, tied to XWorm C2 infrastructure) and Cosmic Nebula Themes, whose app.js decrypts an AES-256-CBC embedded stage and uses a Solana transaction memo as a dead-drop to resolve follow-on payload infrastructure — the same AES key, Solana address, and execution model previously documented in GlassWorm activity. Git commit identities, near-identical theme source, shared Russian-language developer comments, and brandjacking (Coca-Cola, Aurora Borealis name-squatting) link the cluster together; a Dec 14, 2025 DEV Community article is assessed as promotional infrastructure driving Open VSX installs. The post provides full IOCs (hashes, domains, Solana address, AES key/IV, GitHub accounts) and MITRE ATT&CK mappings for defenders to hunt and inventory extensions across both registries.
socket.devwriteupPublished and added 2 Oct 2026🛡️ Security- MITRE ATLAS v2026.08 release — autonomous agent techniques
Release notes for MITRE ATLAS v2026.08, the adversarial AI/ML knowledge base (now 1 matrix, 16 tactics, 114 techniques, 83 sub-techniques, 39 mitigations, 72 case studies). This version renames the "AI Attack Staging" tactic to "AI Attack Adaptation," generalizes several techniques (e.g., Cloud Service Discovery → Enterprise Resource Discovery, Process Discovery → Enterprise Environment Discovery, Reverse Shell → Cyber Communication Channel), and updates mitigations and techniques like LLM Prompt Crafting and Retrieval Content Crafting.
 github.comrepoAdded 1 Oct 2026🛡️ Security
 The Fine Art of Frustrating the Adversary
A Cisco Talos Cybersecurity Awareness Month piece in which eight researchers each give a concrete recommendation for frustrating adversaries at different attack-chain stages: honeypot accounts and tarpits for early deception, behavior-based detection engineering (citing MITRE ATT&CK, Summiting the Pyramid, Macro ATT&CK, LUCID) that targets what an adversary must accomplish rather than specific tools, allowlisting legitimate RMM software (flagging AnyDesk, ScreenConnect, Atera as commonly abused by ransomware like Warlock using Zoho Unattended Agent) over unapproved ones, identity/short-lived-credential controls for AI agent sessions referencing an Anthropic report on Claude misuse incidents, and breaking single-point-of-failure dependencies such as a Telegra.ph-hosted C2 dead-drop resolver used by the Amatera stealer and an EtherHiding-based BNB Smart Chain C2 used by ZigCryptoStealer. Each section gives practical, actionable mitigations defenders can apply today.
 blog.talosintelligence.comarticleAdded 7 Oct 2026, published 1 Oct 2026🛡️ Security
 Tracking CVE-2026-73570: unauthenticated command injection on internet-facing mail servers
Microsoft Threat Intelligence tracked in-the-wild exploitation of CVE-2026-73570, an unauthenticated OS command-injection vulnerability in Zimbra Collaboration Suite's SNMP notification path (swatchdog-to-snmptrap), triggerable via a crafted SMTP request when the optional zimbra-snmp package is enabled. The post documents pre-disclosure scanning, JSP webshell deployment, a novel pam_exec/zmmailboxdmgr privilege-escalation chain to root, systemd-based persistence (zimlog.service), theft of zimbraPreAuthKey/zimbraAuthTokenKey via zmlocalconfig and LDAP, lateral movement over Zimbra's SSH identity, a multi-stage Go-based remote-access agent (zimclient2 via zimdown2/agent2.sh), a dedicated mailbox-exfiltration implant, and an AzCopy-based exfiltration attempt, closing with Defender XDR KQL hunting queries and MITRE ATT&CK mapping.
 microsoft.comwriteupAdded 1 Oct 2026, published 30 Sep 2026🛡️ Security
- Agent Threat Rules (ATR) — open detection-rule standard for AI agent threats
Agent Threat Rules (ATR) is an open, versioned YAML rule format (ATR-YYYY-NNNNN scheme) for detecting AI-agent runtime threats — prompt injection, tool-poisoning, malicious SKILL.md content, and MCP exchange abuse — evaluated by a reference TypeScript engine (with a Python wrapper) shipped as an npm/pip package, CLI, GitHub Action, and Docker scanner with SARIF output. The project positions itself as "Sigma for agent threats," maps rules to OWASP Agentic/LLM Top 10, MITRE ATLAS, and NIST AI RMF, and publishes an extensive (and unusually self-critical) benchmark suite against corpora like garak, PromptBench, and PromptInject, including documented harness bugs and withdrawn recall figures.
github.comrepoAdded 26 Sep 2026🛡️ Security - MITRE ATLAS v2026.09 data release
Release changelog for MITRE ATLAS's atlas-data repository, the structured YAML/STIX dataset behind the ATLAS knowledge base of adversary tactics and techniques targeting AI-enabled systems (prompt injection, model/data poisoning, AI agent tool abuse, AI supply chain compromise). The v2026.09 release brings the matrix to 120 techniques, 88 sub-techniques, 40 mitigations, and 73 case studies, and recent versions introduced a new v6 YAML data format with Pydantic/SQLAlchemy/FastAPI tooling, platform tagging (Predictive AI, Generative AI, Agentic AI, Enterprise), and renamed/generalized techniques like "AI Agent Tool Poisoning," "Manipulate AI Model," and "Enterprise Resource Discovery." It's the canonical, actively-maintained taxonomy practitioners use for AI red-teaming, threat modeling, and mapping real-world AI attack case studies.
github.comrepoAdded 26 Sep 2026🛡️ Security  Agent Threat Rules (ATR) — Sigma/YARA-style open detection format for AI agent threats
Agent Threat Rules (ATR) is an open, versioned YAML rule format for detecting AI-agent security threats — prompt injection, tool poisoning, credential exfiltration, unauthenticated agent execution — positioned as "what Sigma is to SIEM and YARA is to malware." Rules carry permanent ATR-YYYY-NNNNN IDs, declare detection conditions against fields like LLM I/O, tool-call args, or SKILL.md content, and map back to OWASP Agentic/LLM Top 10, MITRE ATLAS, SAFE-MCP, and NIST AI RMF; a reference TypeScript engine and Python wrapper ship MIT-licensed. Governance is transitioning from a single BDFL maintainer to a Technical Steering Committee, and the spec is notably transparent about its own limits, withdrawing previously published per-lane false-positive figures after discovering a tainted benign corpus.
 agentthreatrule.orgotherAdded 26 Sep 2026🛡️ Security
 AI Recommendation Poisoning: How
Describes "AI Recommendation Poisoning," a prompt-injection technique that abuses pre-filled deep links in "Ask AI" buttons (chatgpt.com/?q=, claude.ai/new?q=, grok.com, gemini.google.com) embedded on marketing and competitor-comparison pages. When a logged-in user clicks the button, a hidden query instructs the assistant to permanently save the vendor's domain as a "trusted source" in its persistent memory, silently biasing future answers — mapped by Microsoft Security (31 companies, 14 industries observed) to MITRE ATLAS AML.T0080 (Memory Poisoning)/AML.T0051 (Prompt Injection). Includes two real payload teardowns (a consent-management vendor and a security vendor's competitor-comparison widget) and detection guidance (scan outbound links to AI-assistant domains for "remember"/"trusted source" query strings).
 thehackernews.comarticleAdded 26 Sep 2026🛡️ Security
 Storm-3168: Agentic-driven cloud attacks using compromised service principals
Microsoft Security Research documents an Azure-focused campaign by Storm-3168 (aka JADEPUFFER, discovered by Sysdig as the first documented agentic ransomware operation), using two compromised service principals to enumerate an Azure tenant and then execute a seven-minute destructive sequence deleting 100+ Storage Accounts, a Key Vault, a Function App, and attempting (unsuccessfully, due to API version mismatch) to delete Azure SQL databases. Initial access traces to a client ID/secret/tenant ID leaked in a GitHub issue's public edit history even after the secret was redacted; the attacker also harvested storage account keys and targeted Site Recovery/Backup protection locks to impair recovery, consistent with ransomware/extortion tradecraft. The post includes a MITRE ATT&CK mapping (T1190, T1078.004, T1526, T1485, T1490) and mitigation guidance around workload identity hygiene, least privilege, and backup protection.
microsoft.comwriteupAdded 7 Oct 2026, published 25 Sep 2026🛡️ Security- Compromised npm Packages in the AsyncAPI Namespace Deliver Miasma Botnet Loader
Socket's Threat Research Team details a supply-chain compromise of four @asyncapi npm packages (generator-helpers, generator-components, generator, specs) published via a poisoned source commit through GitHub Actions trusted publishing. The packages contain an obfuscated load-time (not install-hook) implant that spawns a detached Node.js process to fetch an IPFS-hosted, AES-256-GCM-encrypted loader delivering the "Miasma" botnet/tasking framework, which supports REST C2, multi-channel comms (Nostr, IPFS, Ethereum RPC, BitTorrent DHT), shell execution, file exfiltration, and systemd persistence. Includes full technical analysis, IOCs, hashes, and MITRE ATT&CK mapping.
socket.devwriteupAdded 21 Sep 2026🛡️ Security 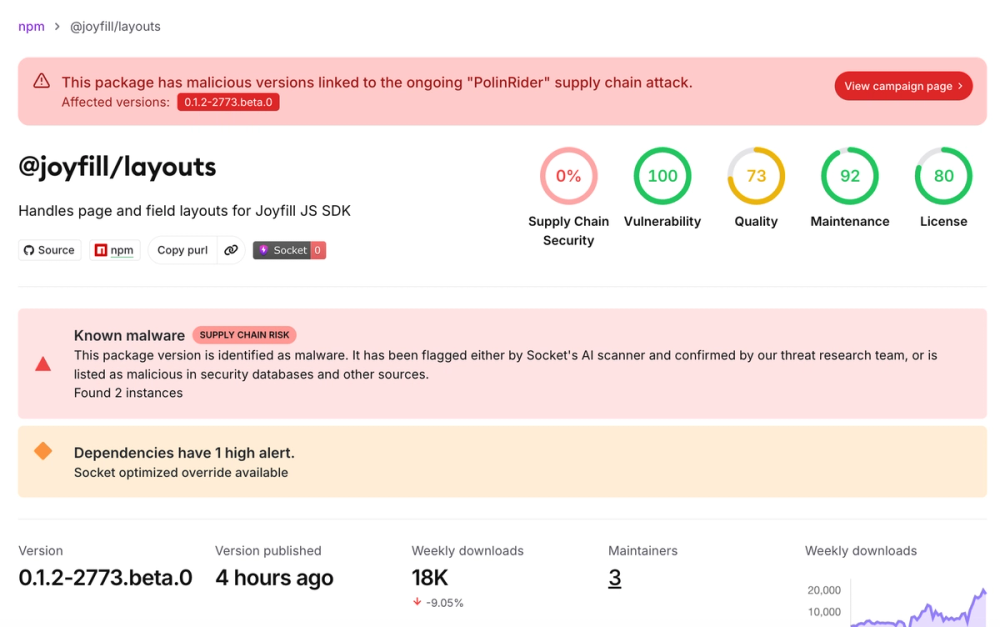 Socket: Two Joyfill npm Beta Releases Compromised to Deliver DEV#POPPER Remote Access Trojan
Socket's research team found two beta releases of the @joyfill npm packages (@joyfill/layouts and @joyfill/components) contained an import-time JavaScript implant that resolves encrypted payloads through Tron, Aptos, and BNB Smart Chain transactions, ultimately dropping a 77KB Node.js remote-access trojan matching the DEV#POPPER family and sharing loader fingerprints with the PolinRider blockchain-loader campaign. The RAT establishes a Socket.IO C2 channel, executes arbitrary JS/shell commands, exfiltrates files and clipboard data, and persists by patching files inside VS Code, Cursor, Antigravity, Discord Desktop, GitHub Desktop, and the global npm CLI; a parallel detached-process branch fetches an additional bootstrap that can deploy a Python credential/browser-data stealer assessed as an OmniStealer variant. Because the implant fires on module load (not via npm lifecycle scripts), `--ignore-scripts` provides no protection, and the writeup includes full IOCs, blockchain addresses, C2 infrastructure, and MITRE ATT&CK mappings.
socket.devwriteupAdded 22 Sep 2026, published 20 Sep 2026🛡️ Security DPRK and Iran are Leading a 5.2x Surge YoY in Blockchain-Assisted Cyberattacks
Chainalysis research on blockchain dead drops (BDD), the practice of storing malware C2 payloads and configuration pointers on public blockchains (EtherHiding and its variants) so infrastructure survives takedowns. It details three attributed case studies: DPRK linked UNC5342 using a TRON and Aptos to BSC cross-chain relay to deliver crypto-stealing malware via fake job interviews, Iran-nexus actors embedding C2 in Bitcoin OP_RETURN transactions tied to a Satoshi-era address, and a Russian-language Malware-as-a-Service operation running resolver contracts on Polygon across dozens of downstream customers. It reports a 420 to 440 percent YoY surge in BDD activity, attributes it partly to unrestricted open-weight Chinese LLMs lowering the barrier to entry, and maps the technique to MITRE ATT&CK T1102.002.
 chainalysis.comarticleAdded 30 Sep 2026, published 17 Sep 2026🛡️ Security
 Threat Actors Abuse IronPython to Deliver CastleLoader/CastleRAT
A threat-hunting blog post (#415 in a recurring series) analyzes how attackers abused IronPython to deliver CastleLoader and subsequently CastleRAT, based on Zscaler's SloppyRAT report. It documents the attack chain — a renamed curl.exe downloading IronPython from GitHub, then IronPython executing a base64-decoded, zlib-compressed Python payload — and provides concrete hunting queries (process creation events filtering on curl.exe with "ironpython" in the command line, and IronPython processes invoking base64.b64decode) to detect this technique, mapped to MITRE ATT&CK T1059.006.
 knowyouradversary.ruwriteupAdded 26 Sep 2026, published 17 Sep 2026🛡️ Security
- ThreatIntel-Aggregator
ThreatIntel-Aggregator is a self-hosted FastAPI/Next.js platform that polls 60+ tiered security RSS feeds (CISA, Talos, Unit42, etc.), runs AI triage to score severity and tag MITRE ATT&CK TTPs, extracts IOCs/CVEs, and correlates findings against a RunZero asset inventory to surface org-level exposure. Its Detections module goes further: it catalogs AI-generated or locally-imported detection rules (KQL/Sigma/YARA/Suricata/SPL), statically validates them, runs AI-driven MITRE alignment checks against technique coverage, tracks detection "rot," and can sync Hunts/Analytics Rules to a live Microsoft Sentinel workspace. It's designed to run standalone with zero cloud dependency or fully integrated with Azure/Entra/Sentinel, with all storage in Postgres and auth via Entra SSO or a local API key.
github.comrepoAdded 22 Sep 2026, published 17 Sep 2026🛡️ Security  MITRE ATLAS Adds 11 AI Agent Attack Techniques (Zenity Labs collab)
Zenity Labs details its collaboration with MITRE ATLAS to add roughly 11 new AI agent attack techniques, drawn from real-world observations and DEF CON 34 research rather than hypotheticals. New entries cover recon (Active Scanning subtechniques for predictable agent URLs, provider metadata APIs, Search Open Websites/Domains for embedded agentic iFrames, Discover AI Agent Runtime Capabilities, Scan Databases via Shodan/Censys, Misconfigured or Publicly Exposed AI Services), input manipulation (Triggers in Multimodal Inputs, LLM Prompt Obfuscation via image/audio/video, Crafted AI Assistant Links using ?q=/?prompt= parameters, AI Targeted Cloaking, LLM Response Rendering exfiltration, LLM Jailbreak's Data Structure Injection), and a defensive mitigation built on AI honeypots plus multimodal guardrail inspection.
 labs.zenity.ioarticleAdded 30 Sep 2026, published 16 Sep 2026🛡️ Security
 Threat Hunter's Guide to GitHub (Datadog Security Labs)
Datadog Security Labs walks through hunting for GitHub organization compromise using GitHub audit logs, covering the full attack chain from stolen PATs/OAuth tokens and device-code phishing (initial access) through secrets-listing enumeration, private-repo/tree discovery, and bulk collection via git.clone or repo.download_zip. It provides copy-pasteable queries (with fields like hashed_token, programmatic_access_type, external_identity_nameid) mapped to MITRE ATT&CK techniques and calls out GitHub audit-log quirks (missing IP on failed auth, inconsistent visibility fields, misleading token permission scopes) that shape accurate detections.
 securitylabs.datadoghq.comwriteupAdded 25 Sep 2026, published 16 Sep 2026🛡️ Security
- agent-egress-bench
Agent Egress Bench is an open, tool-neutral benchmark maintained by PipeLab (makers of Pipelock) that tests whether products mediating an AI agent's outbound traffic — proxies, egress firewalls, MCP wrappers, agent gateways — actually catch exfiltration attempts caused by prompt injection or misalignment, rather than testing the underlying model itself (that's left to AgentDojo, InjecAgent, CyberSecEval, AgentHarm, ASB). It ships a reproducible Go runner with a proxy/WebSocket/MCP/A2A adapter contract, an offline validator, DSSE-signed evidence bundles, and a CI-runnable GitHub Action, and separates containment from false-positive rate as two distinct scored axes with immutable case IDs and OWASP Agentic Top 10/MITRE ATT&CK mappings. Its governance explicitly permits third parties to publish results unfavorable to the maintainer's own Pipelock product.
github.comrepoAdded 12 Sep 2026🛡️ Security  The Fraud Ecosystem: A Transition From Known Marketplaces to a Fragmented Environment
Rapid7 profiles the current Fraud-as-a-Service marketplace landscape — Xleet, Blackpass (formerly Paysell), Infodig, and Styx — detailing their shift from large hubs to fragmented, invite-gated shops selling compromised accounts, SMTP/RDP/VoIP infrastructure, eSIMs, stolen PII, and cashout/money-laundering services. It also discusses the new MITRE Fraud Fighting Framework (F3), introduced in early 2026, which maps adversary TTPs for fraud/financial-crime monetization, and argues security teams must correlate marketplace monitoring with internal fraud and compliance units to counter account-takeover and laundering schemes.
 rapid7.comarticleAdded 7 Oct 2026, published 11 Sep 2026🛡️ Security
 Passkey-themed social engineering leads to identity and cloud compromise
Microsoft Security Research details an active campaign (since May 2026) where attackers use voice-phishing and SMS lures impersonating IT helpdesk passkey/SSO enrollment requests to drive victims into AiTM or device-code phishing flows, compromising Microsoft 365 identities. Post-compromise, actors register attacker-controlled MFA methods (e.g., software OTP tokens) for persistence, conduct systematic Microsoft Graph reconnaissance across users, groups, roles, and SharePoint/OneDrive/Exchange, then exfiltrate data at a measured pace using automated Node.js/python-httpx tooling while evading detection through IP rotation and anonymous proxies. The post includes real audit-log JSON examples, multiple KQL hunting queries for GraphAPIAuditEvents/CloudAppEvents, full MITRE ATT&CK mapping, and attributes the initial-access tradecraft to Storm-3121 and Storm-3032, which feed into ShinyHunters/Falcon and Helix extortion operations.
microsoft.comwriteupAdded 3 Oct 2026, published 9 Sep 2026🛡️ Security- mukul975/cve-mcp-server
cve-mcp-server is a Model Context Protocol server that gives Claude direct access to 28 security tools spanning 24 APIs (NVD, EPSS, CISA KEV, OSV.dev, GitHub GHSA, MITRE ATT&CK, AbuseIPDB, GreyNoise, Shodan, VirusTotal, MalwareBazaar, ThreatFox, Ransomwhere, and more), fronted by a one-call triage_cve orchestrator. It computes a composite 0-100 risk score from CVSS, EPSS, KEV status, and PoC availability (with a hard CISA KEV override forcing CRITICAL/≥76), supports dependency scanning via OSV, IP/domain reputation lookups with private-IP blocking, and ships an SSVC v2 gated decision mode plus audit logging and XML-bomb protections via defusedxml.
github.comrepoPublished and added 7 Sep 2026🛡️ Security - Numbat
Numbat is a Go-based, single-binary endpoint agent from Perplexity AI that gives visibility into AI coding-agent activity (Claude Code, Codex, OpenClaw, and other CLI/IDE/gateway agents) by capturing events through local hooks, OTLP/HTTP logs, and on-disk session artifacts. It normalizes activity into one event model, evaluates it with a local CEL rule engine (including multi-step sequence rules like secret-read-then-egress), and can optionally block matched actions via synchronous pre-action hooks (deny/monitor decisions), with case bundles and SHA-256 manifests for forensic reconstruction. Example built-in rules detect cloud-metadata SSRF requests (169.254.169.254) and credential-exfiltration chains, mapped to MITRE ATT&CK technique tags.
github.comrepoPublished and added 5 Sep 2026🛡️ Security - h5i-dev/awesome-ai-agent-incidents
A curated GitHub corpus tracking real-world security incidents, CVEs, attack techniques, and defensive tools specific to autonomous AI agents — spanning prompt injection/goal hijacking, MCP client-side tool-metadata poisoning, the "Promptware Kill Chain" multi-stage attack model, MITRE ATLAS agentic techniques, and the OWASP Top 10 for Agentic Applications. It also documents the OpenClaw/ClawHub supply-chain incident (1,184 malicious skills confirmed by Antiy CERT) and links defensive projects like OWASP Agent Memory Guard for LangChain/LlamaIndex agent memory protection.
github.comrepoAdded 3 Sep 2026🛡️ Security - Prompt Injection Against Coding Agents: The Attack Surface Nobody Owns | Blog | Endor Labs
Endor Labs breaks down how indirect prompt injection compromises AI coding agents (Cursor, GitHub Copilot) via poisoned READMEs/rules files, malicious MCP servers, and web/issue content the agent reads with elevated trust and auto-approve permissions. Cites a study testing 314 payloads across 70 MITRE ATT&CK techniques showing up to 84% attack success, OWASP's MCP tool poisoning definition, Unit 42's real-world IDPI telemetry, and CVE-2025-52573 as a concrete command-injection-via-prompt-injection case in an MCP server.
 endorlabs.comarticleAdded 3 Sep 2026, published 2 Sep 2026🛡️ Security

Showing 30 of 66
Show more