 winternl.comwriteup
Unpacking the AAD Broker LocalState Cache
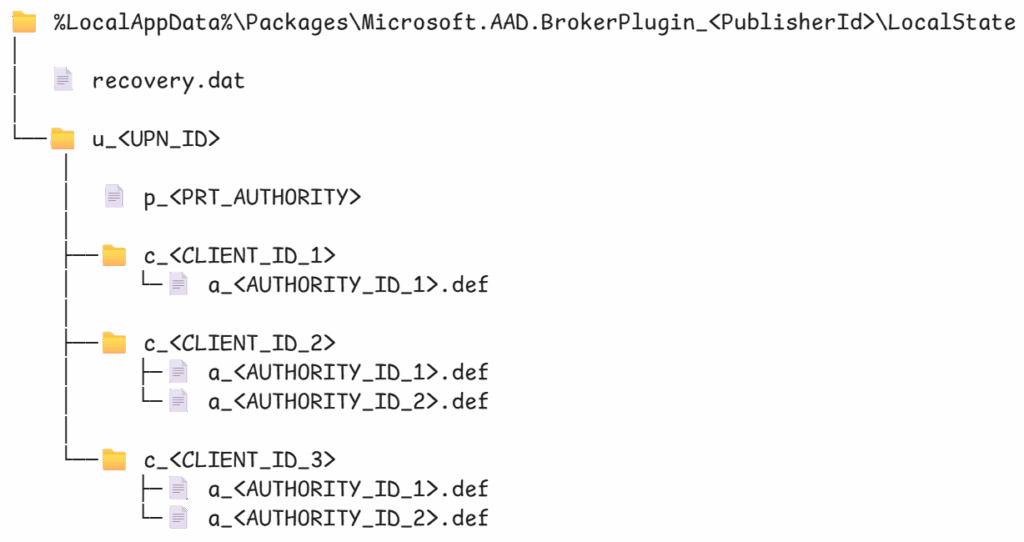
Deep technical teardown of the Entra ID (Azure AD) Broker's LocalState cache on Windows 11, reverse-engineering the file naming scheme derived from identity material, the AES-GCM/DPAPI-wrapped Packer::V3 format inside AAD.Core.dll, and the JSON/binary serialization of AuthenticationContext objects used for PRT and per-application authority files. The author shows how to decrypt cached PRT and authority token files, derive the TPM-bound PRT session key via NCryptKeyDerivation (replicating mimikatz's dpapi::cloudapkd), and extract cached access/refresh tokens and JWTs — giving an attacker with local SYSTEM context a path to long-lived, MFA-bypassing cloud access and rich identity reconnaissance data. Companion extraction code is released as AADBrokerDecrypt on GitHub.
Offensive Security, Identity & Access· 2025-09-30T19:42:17+00:00