 huntress.comarticle
Hardening the Hypervisor | Huntress
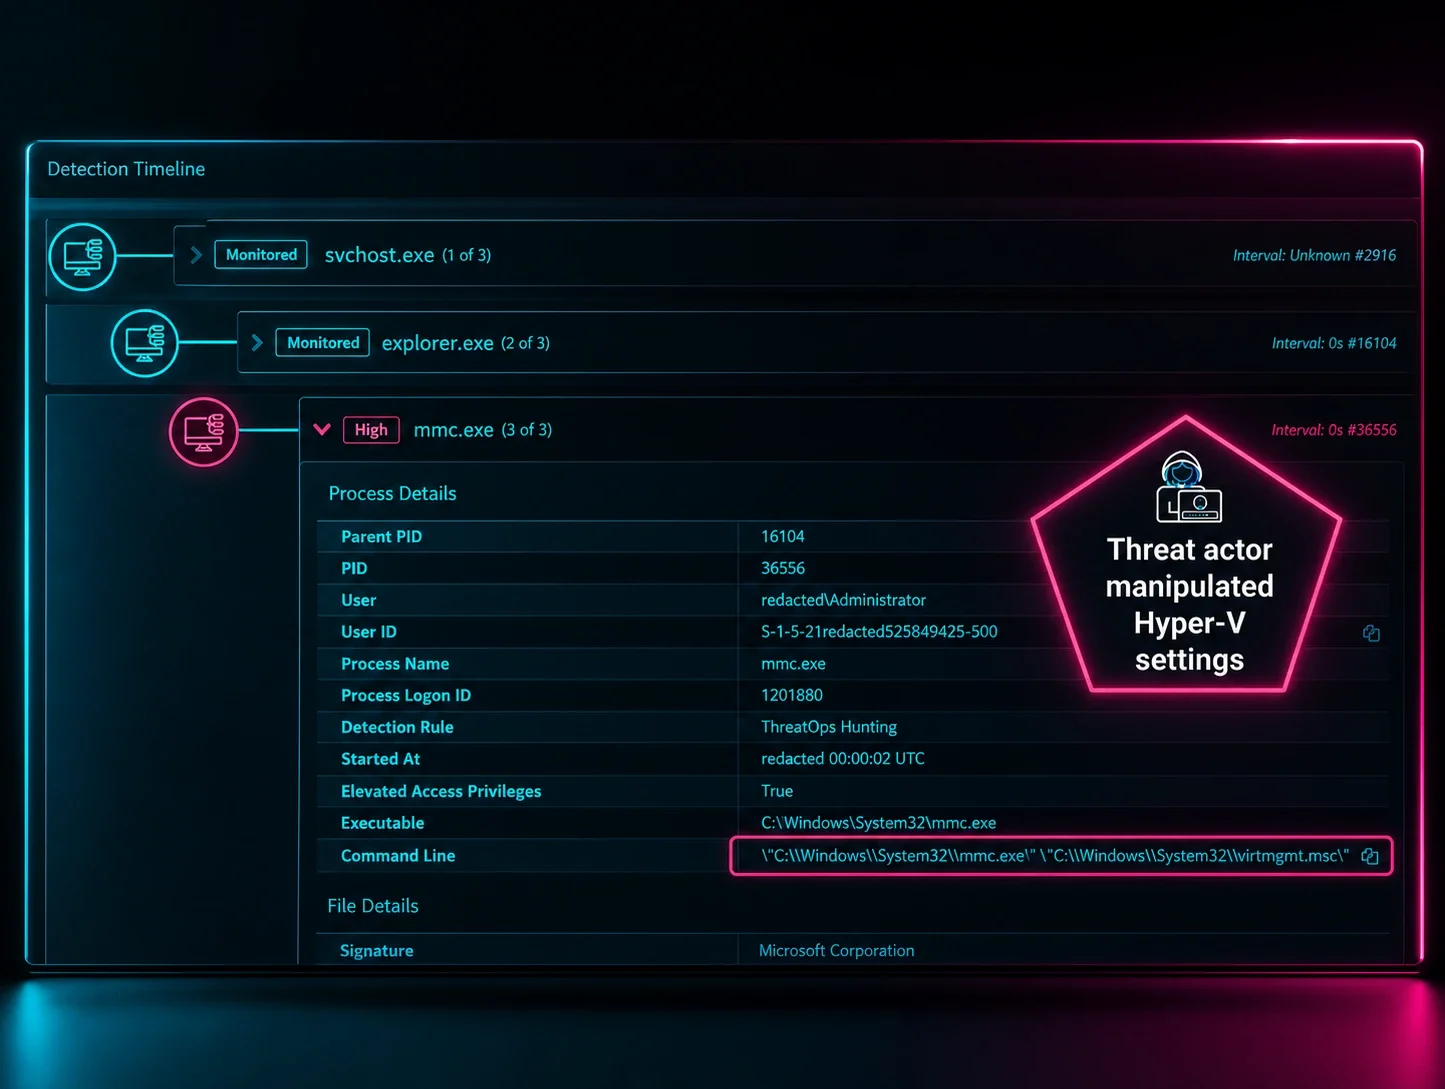
Huntress details a sharp 2025 rise in hypervisor-targeted ransomware (from 3% to 25% of malicious-encryption cases), driven mainly by the Akira group abusing ESXi and Hyper-V management interfaces to bypass endpoint EDR and encrypt VMs at scale. It provides hardening guidance: local non-AD ESXi accounts, MFA, jump boxes, least privilege, VMkernel.Boot.execInstalledOnly and lockdown mode, patching against CVE-2024-37085 and disabling exposed SLP (port 427, abused by ESXArgs), immutable 3-2-1 backups, and forwarding ESXi logs to a SIEM.
TL;DR Huntress breaks down the surge in Akira-driven hypervisor ransomware and gives ESXi/Hyper-V hardening, patching (CVE-2024-37085), and log-monitoring guidance.
CVEs named here
- CVE-2024-37085
Technologies named here
- VMware ESXi
- openssl
- VMware vCenter
- Huntress platform
- SIEM
- Microsoft Hyper-V
- Hyper-V
- Active Directory
- SSH
- VPN
- vCenter
Techniques named here
- Hypervisor-level ransomware deployment
- Encryption via built-in tools
- Credential-based lateral movement to hypervisor management
- Hyper-V management utility misuse
- AD 'ESX Admins' group recreation
- Exploitation of exposed SLP protocol
Threat actors named here
- Akira
- ESXArgs
Related in Cloud & Infra



 orca.securityarticle
Orca Security: GenAI Risks in Cloud Environments

 aikido.devwriteup
Google API keys keep working after you delete them

 attackthesoc.comarticle