 huntress.comarticle
What Good Identity Hardening Looks Like
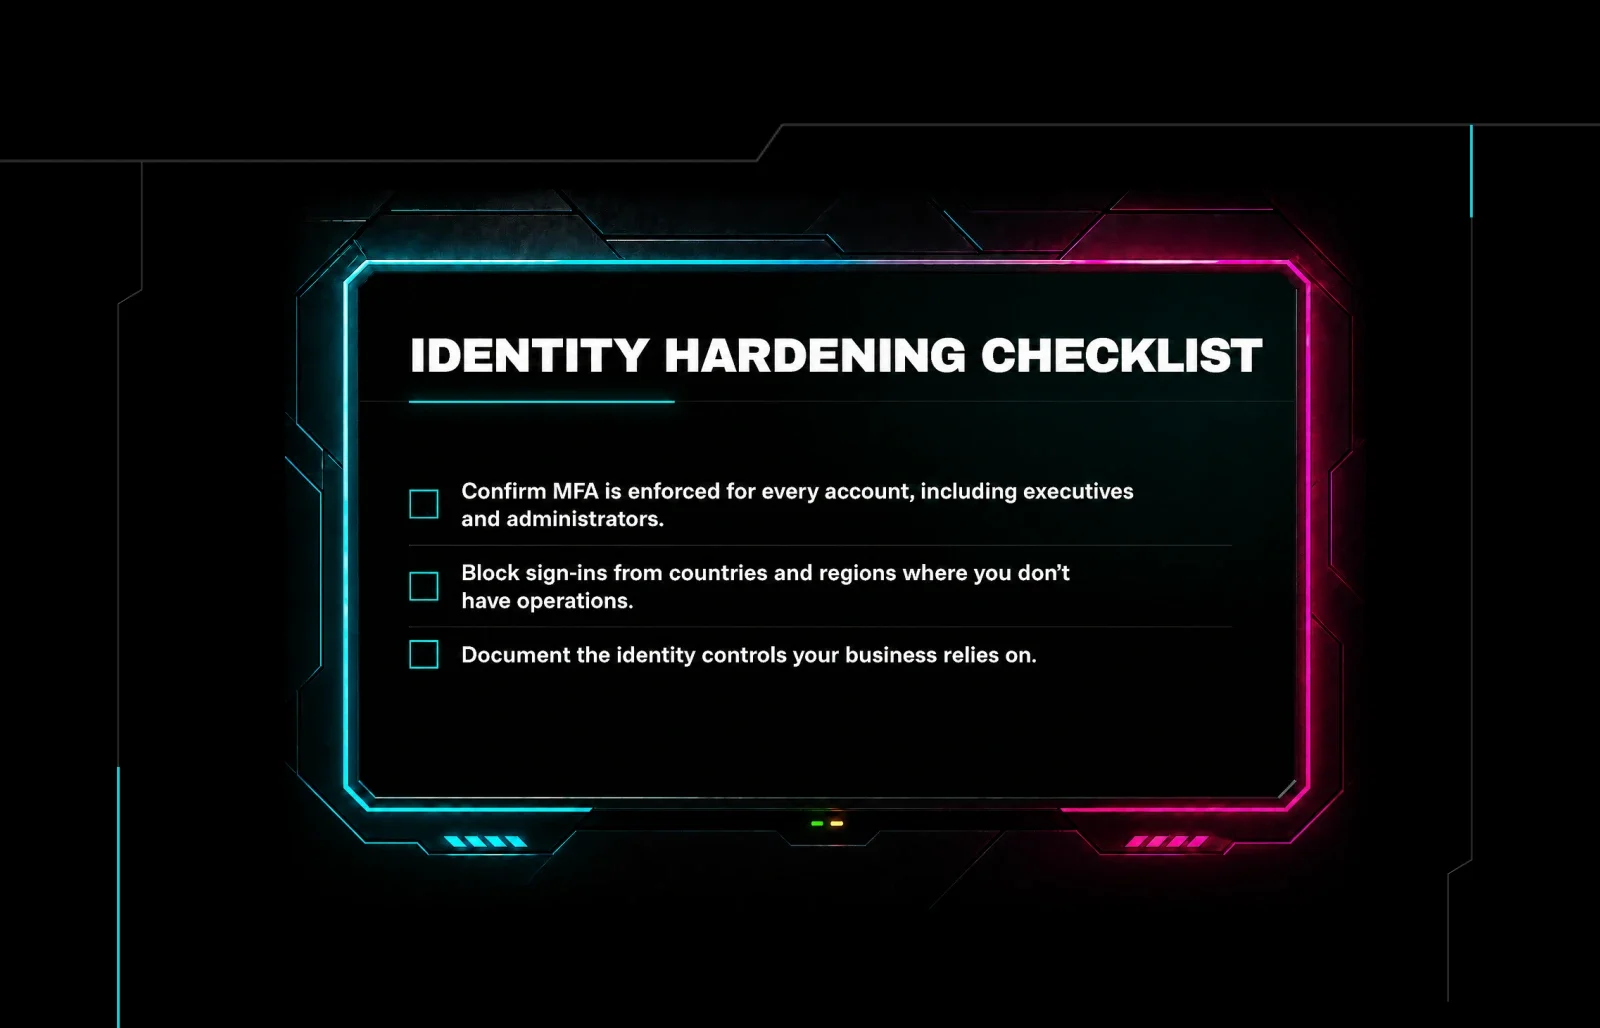
Huntress blog post arguing that MFA is only a starting point for identity security, walking through how credential/session theft (e.g. via ClickFix fake-CAPTCHA lures that trick users into pasting commands into the Windows Run dialog) bypasses single-sign-on defenses. It includes a real-world case study of a small real estate firm where a CEO's MFA exception led to a business email compromise and fraudulent wire transfers, followed by a practical identity-hardening checklist covering conditional access by geography/device, closing MFA exceptions, monitoring for configuration drift, and reducing stale privileged accounts.
TL;DR Huntress explains why MFA alone isn't enough, using a ClickFix credential-theft example and a real BEC case study to build an identity-hardening checklist (conditional access, exception tracking, drift monitoring).
Organisations named here
- ClickFix
Technologies named here
- Microsoft Defender Safe Links
- Microsoft Entra
- Windows
- Outlook
- Microsoft Entra ID
- Microsoft Defender
- Microsoft 365
- Huntress
Techniques named here
- ClickFix social engineering
- Credential/session token theft via infostealer
- MFA-approved session hijacking
- MFA bypass via trusted device abuse
- MFA bypass via risky app consent
- MFA bypass via emergency exceptions
- Business Email Compromise
Threat actors named here
- ClickFix
Related in Identity & Access
 huntress.comarticle
Education Under Attack: The Pattern Behind Recent University Breaches
 huntress.comarticle
Next-Gen Phishing Tactics Users Aren’t Ready For | Huntress

 aikido.devwriteup
Google API keys keep working after you delete them

