Skip to content

56 results for โ€œESETโ€

What you seeeverything
securityweek.comarticle๐Ÿ›ก๏ธ Security

Chainalysis Discloses Data Breach Following AI-Driven Cyberattack

Chainalysis disclosed a data breach in which an external actor used offensive agentic techniques to access its systems and internal tools. Exposed data was non-sensitive customer data: user IDs, full names, email addresses and organization role labels. Investigation content, query results and credentials were not compromised. The company says the incident is unrelated to the $6.36 billion Binance heist, and advises users to enable MFA and watch for password reset prompts. Scope and victim count are undisclosed.

LLM
ChainalysisBinanceDPRK

Threat Intel, AI Securityยท Published and added 2 Nov 2026

bleepingcomputer.comarticle๐Ÿ›ก๏ธ Security

Alpine Linux rebuilds GitLab after attempted RCE attack

Alpine Linux rebuilt its GitLab server and reset all passwords after attackers tried to exploit CVE-2026-97229, a maximum-severity integer overflow in the Onigmo regex engine bundled with Ruby, on October 20-21. Eight worker crashes occurred and four were partially successful. Missing logs and outbound connection records meant compromise could not be ruled out. Alpine had run GitLab 19.3.4, then 19.3.6, which lacked the Ruby patch; the fixed image is alpinelinux/gitlab:19.3.6 with Ruby 3.3.13.

GitLabAlpine LinuxDocker+1
CVE-2026-97229integer overflowOnigmo

Supply Chain, Blue Team & Detection, DevSecOpsยท Published and added 1 Nov 2026
x.comthread๐Ÿ›ก๏ธ Security

ESET Research (@ESETresearch) on X

ESET Research thread summarising its APT Activity Report for April to September 2026 on Russia-aligned groups targeting Ukrainian defense, government and infrastructure. Gamaredon deployed Turla's new VBScript recon tool Rezzuar, indicating FSB-linked collaboration, and updated its file stealer PteroBox while activity fell sharply from mid-May. A separate campaign hit MDaemon mail servers via CVE-2025-8088, delivering HELLAGE and HELLTAG backdoors with no user interaction.

MDaemonClamAVWinRAR+1
CVE-2025-8088GamaredonTurla+6

Threat Intelยท Added 31 Oct 2026, published 30 Oct 2026

arxiv.orgpaper๐Ÿง  AI

Don't Lose the Thread: Empowering Long-Horizon LLM Agents with Cognitive Resource Self-Allocation

CORAL (Cognitive Resource Self-Allocation) is an agent-callable working-memory toolset that lets an LLM agent checkpoint task progress and verified facts, then reset its cluttered context and resume from a clean state. A Multi-episode Agentic Reinforced Policy Optimization algorithm trains the checkpointing. With an 8B model it reaches 42.8% average accuracy on GAIA, uses 6-7x fewer input tokens than a ReAct agent, and adds 8.0 points to a proprietary agent on BrowseComp.

LLMReActCORAL
Multi-episode Agentic Reinforced Policy OptimizationGAIABrowseComp

agents, research, trainingยท Added 31 Oct 2026, published 29 Oct 2026

securityweek.comarticle๐Ÿ›ก๏ธ Security

Hackers Steal 2.6 Million Records From Sonyโ€™s Japanese ISP So-net

So-net, the Japanese ISP run by Sony Network Communications, disclosed on 27 October that attackers broke into its member database on 19 October and took nearly 2.6 million records of So-net and Plala subscribers. Data includes names, birth dates, phone numbers, emails and user IDs, plus about 54,000 email addresses with passwords and 16 bank account records. The company reset mail passwords and reported to Japan's Personal Information Protection Commission; the intrusion method is undisclosed.

So-netPlalaSony Network Communications+4

Threat Intelยท Published and added 29 Oct 2026

en.cryptonomist.charticle๐Ÿง  AI

Hygentra: AI Trading Agents Kept 97.5% of Losses by Value Within Limits

Hygentra's six-month study (February to August 2026) audited four AI trading agents, each with its own strategy and preset risk rules, through a 29% Bitcoin decline and recovery. 97.5% of losses by value stayed within limits, 23 of 24 runs respected the five-open-trade cap, and no agent raised risk after a loss. Trade records and testing tools were published; 18% of positions were real Hyperliquid orders, the rest simulated with a 0.09% round-trip fee.

Hyperliquid
HygentraSaad NajaBitcoin+2

evals, agentsยท Published and added 28 Oct 2026

securityweek.comarticle๐Ÿ›ก๏ธ Security

Vendor Key Leak Puts Data of 238,000 Denver Health Plan Members at Risk

Denver Health Medical Plan is notifying 238,083 members that vendor SquareML leaked an access key on a public website. The key was online from 27 June 2025 until it was revoked on 18 August 2026 and gave read-only access to a database of names, dates of birth, health metrics, eligibility and admission data. DHMP found no evidence of misuse and reset passwords for all accounts with access.

Denver Health Medical PlanSquareMLHealth First Colorado+2

Threat Intelยท Published and added 27 Oct 2026

securityweek.comarticle๐Ÿ›ก๏ธ Security

Unexplained DreamHost Incident Prompts Email, FTP Password Resets

DreamHost suspended its File Manager (files.dreamhost.com) and reset passwords for some email and FTP/SFTP users after an unexplained issue affecting File Manager and webmail. Account owners were told to set new passwords and change reused ones; users questioned whether passwords were compromised or properly hashed. DreamHost deployed a fix on Monday. Root cause and number of affected users were not disclosed.

DreamHostSFTP

Threat Intelยท Published and added 27 Oct 2026

securityweek.comarticle๐Ÿ›ก๏ธ Security

11 Million Impacted by Capcom Data Breach

Capcom disclosed a breach of CAPCOM ID, its shared login service for online games, discovered on 19 October. Attackers took 11,774,247 email addresses plus account metadata (creation date, last login, login count, last IP). For 43 users dates of birth, gender, country and nicknames were also exposed, and passwords were changed on 196 accounts. Capcom says no passwords were stolen, reset the affected accounts, and warns of impersonation emails. The root cause is not stated.

CapcomCAPCOM ID

Threat Intelยท Published and added 23 Oct 2026

unit42.paloaltonetworks.comarticle๐Ÿ›ก๏ธ Security

The Current Landscape of OAuth Attacks

Unit 42 survey of OAuth attacks that steal tokens after MFA, so access survives password resets. It covers account hijacking (device authorization and authorization code misuse), permission hijacking (vague or impersonating app names), and malicious redirects, including the error-triggered redirect campaign Microsoft documented in March 2026. It also describes COSF and OAuth-as-a-service flaws, PhaaS and LLM evasion trends, and defenses such as admin-only consent and redirect_uri audits.

OAuthMicrosoft Entra IDCloudflare Workers+2
Cross-User OAuth Session FixationCross-Tenant Client ID ConfusionCross-Connector OAuth Account Takeover+7

Identity & Access, Threat Intel, Blue Team & Detectionยท Added 30 Oct 2026, published 22 Oct 2026

x.comrepo๐Ÿง  AI

Sadra Majidi (@SadraMajidi04) on X

Impeccable is an open-source skill for AI coding agents that steers them away from generic UI output such as purple gradients and nested cards. It provides 24 commands (critique, audit, polish, typeset) and 61 detector rules that run without an LLM. It works with Claude Code, Cursor and Codex, and the repo is pbakaus/impeccable on GitHub. The source is a short tweet and gives no further detail.

Claude CodeCursorCodex+1
Impeccable

coding-agents, promptingยท Added 23 Oct 2026, published 22 Oct 2026

huggingface.cowriteup๐Ÿง  AI

Train in Simulation, Deploy on a Real Robot: Microduck with Isaac Lab 3.0

Tutorial for training a walking policy for Microduck, an open-source bipedal robot from Pollen Robotics and Hugging Face, in NVIDIA Isaac Lab 3.0 with Newton. It covers RSL-RL training with the backlash preset, BAM actuator models and domain randomization, then ONNX export (61 observations, 14 joint-position actions) and deployment with robotctl. Policies can be shared on the Hugging Face Hub or tested in Microduck Arena.

Isaac LabNewtonMJWarp+7
NVIDIAPollen RoboticsMicroduck+2

trainingยท Published and added 21 Oct 2026

blog.cloudflare.comarticle๐Ÿ›ก๏ธ Security

Cloudflare deploys protections against php2shell vulnerability

Cloudflare describes its WAF protections for php2shell (CVE-2026-109618 and CVE-2026-109619), two PHP runtime memory-handling flaws affecting PHP 5.4 and later that can cause denial of service, remote code execution and data exposure. Rules shipped 21 October 2026, about 9 hours before disclosure, using a new "full transaction detection" that matches request and origin response together. It lists ruleset IDs and says patching PHP is still required.

PHPCloudflareWordPress
CVE-2026-109618CVE-2026-109619PHP2Shell+2

Blue Team & Detection, AppSecยท Added 22 Oct 2026, published 21 Oct 2026

arxiv.orgpaper๐Ÿง  AI

SpikeQ: Spike-Guided Post-Training Quantization for Spiking Neural Networks

SpikeQ is a spike-guided post-training quantization framework for spiking neural networks on neuromorphic chips. It picks each weight level by simulating downstream neurons to minimize spike errors, and uses a reset-aware grid for pre-fire membrane potentials. With 4-bit weights and potentials, models stay within 2.59 points of full precision, with 7.8 to 7.9 times smaller memory and 6.4 to 6.9 times less energy.

spiking neural networksneuromorphic chips
SpikeQ

research, inferenceยท Added 20 Oct 2026, published 16 Oct 2026

github.comrepo๐Ÿ›ก๏ธ Security

gichirimaku/wp2shell-PoC

wp2shell-PoC is a Python proof-of-concept exploiting a pre-authentication RCE chain in WordPress core, combining CVE-2026-63030 (REST API batch route confusion) and CVE-2026-60137 (SQL injection in WP_Query). It demonstrates escalation from the route-desync bug through blind SQLi, customize_changeset forgery, and hook re-entry to administrator account creation and arbitrary command execution via a malicious plugin upload. The tool supports vulnerability checking, data extraction (union, error-based, blind techniques), and full shell access with or without existing admin credentials.

WordPressPython
CVE-2026-63030CVE-2026-60137SQL injection+1

AppSec, Offensive Securityยท Added 23 Oct 2026, published 15 Oct 2026

sunshowers.ioarticle๐Ÿง  AI

More on Anthropic's Scion ripping off Mononoke

A followup blog post by a former Meta source control team member. They allege that Anthropic's Scion version control system closely mirrors Meta's Mononoke, including the Bonsai changeset data model (a write-ahead-log-style Merkle DAG) and the derived-data indexing framing. They say Anthropic's credit to "Sapling" for "hard-won lessons" is inadequate. The author says the issue is missing attribution, not copying, and that it undercuts the narrative of an LLM building and productionizing the system in 5 months. An update notes that Anthropic responded on Hacker News and added attribution to its blog post.

MononokeSaplingGit+1
AnthropicScionBonsai+4

ai-policy, coding-agentsยท Added 16 Oct 2026, published 15 Oct 2026

securityweek.comarticle๐Ÿ›ก๏ธ Security

Supermarket Refrigeration Attack Widens to Copeland, Dixell Controllers

ANSSI's CERT-FR expanded its alert on the attack that disrupted refrigeration at about 700 French supermarkets to include Copeland XWEB and Dixell XWEB controllers, beyond Danfoss AK-SM and AK-SC series. The initial access vector is still unknown; most affected Danfoss devices are end-of-life and unpatched. Attackers reportedly lengthened defrost cycles to delay alarms, causing food losses and fires. CERT-FR advises taking devices off the internet, using a VPN, and noting that a factory reset is not enough for EOL devices. Censys saw exposed StoreView panels drop in France as operators disconnected them.

Danfoss AK-SMDanfoss AK-SCCopeland XWEB+3
ANSSICERT-FRClaroty+8

Hardware & RF, Threat Intelยท Published and added 15 Oct 2026

securityweek.comarticle๐Ÿ›ก๏ธ Security

ICS Patch Tuesday: Siemens Issues 17 Advisories, Rockwell Fixes ArmorBlock Takeover Flaw

Roundup of ICS Patch Tuesday advisories. Siemens published 17 advisories, including critical flaws in Simatic S7-1500 CPUs (400+ flaws in the GNU/Linux subsystem), Industrial Edge and Ruggedcom Crossbow SAC. Rockwell fixed a critical 1732E ArmorBlock flaw that lets an unauthenticated attacker change the web server password and take over the admin account, plus a DoS bug. Also covered: two high-severity Schneider Electric advisories (Pro-Face STW6000/Harmony STW6 and Sage RTUs), CISA and CERT@VDE advisories, and other vendor advisories since the last Patch Tuesday. ABB's dynovaPRO credential-reset bypass came with 26 password change events across 9 customers that may indicate reconnaissance.

Simatic S7-1500Ruggedcom1732E ArmorBlock+2
SiemensSchneider ElectricRockwell Automation+13

Hardware & RF, otherยท Published and added 14 Oct 2026

daniel.haxx.searticle๐Ÿ›ก๏ธ Security

curl HTTP/2 upload UAF turned RCE (CVE-2026-92392)

CVE-2026-92392 is a use-after-free in curl's HTTP/2 upload path, fixed in curl 8.23.0 and rated HIGH. After a server zeroes the window and resets the stream, a dangling easy-handle pointer survives. On multi handle cleanup, server data lands in the freed memory and can overwrite a function pointer, giving remote code execution. Daniel Stenberg lists why exploitation is hard (~135KB upload, ~23-byte payload, allocation-dependent) and says Luna Tong at Anthropic found it with an OSS Scanner.

cURLCnghttp2+2
CVE-2026-92392use-after-freeLuna Tong+2

AppSec, Malware & REยท Added 23 Oct 2026, published 14 Oct 2026

anthropic.comarticle๐Ÿง  AI

Redesigning source control at Anthropic

Anthropic describes Scion, an in-house version control system that replaced git for its monorepo in five months as merged changes grew from about 2,500 to over 30,000 per day. Scion is server-centric, with always-online clients, changesets in a write-ahead log, derived data, and tiered content-addressed caches (scion-daemon, scion-cache, scion-server) backed by Spanner. It cut infrastructure 200x versus git mirrors and made checkouts about 100x faster. The post also covers lessons from building it with Claude Mythos Preview and Claude Tag: a seven-person team, engineers steering agents away from constraint violations, "superfan" monitoring agents, and merge queues giving way to post-merge testing.

GitClaudeSpanner+1
AnthropicScionAntique+8

coding-agents, ai-infra, ai-policyยท Published and added 13 Oct 2026

x.comthread๐Ÿ›ก๏ธ Security

Dark Web Intelligence (@DailyDarkWeb) on X

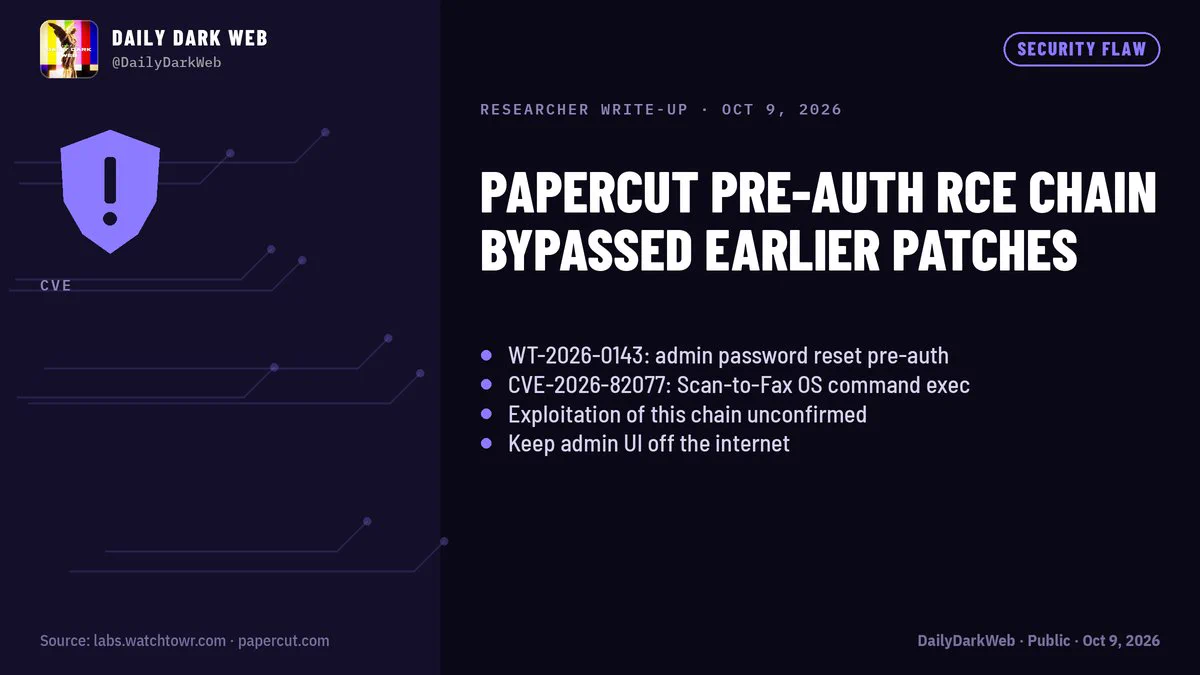
Social post summarizing watchTowr's Oct 2026 research on an unauthenticated RCE chain in PaperCut NG 26.0.4-PO build 76508: an auth bypass (WT-2026-0143, no CVE) re-runs the Setup Wizard via the Home page to reset the admin password, then CVE-2026-82077 (Scan-to-Fax path traversal) gives OS command execution. It lists fix versions (build 76530, 26.0.5, 25.0.13), notes watchTowr's detection tool covers only the bypass, and says exploitation of this chain is unconfirmed, unlike the August attacks using CVE-2026-81578 and CVE-2026-82078.

PaperCut
CVE-2026-82077CVE-2026-81578CVE-2026-82078+5

AppSec, Offensive Securityยท Added 13 Oct 2026, published 12 Oct 2026

securityweek.comarticle๐Ÿ›ก๏ธ Security

Insider Cyber Extortion Plot Against Industrial Firm Lands Engineer in Prison

SecurityWeek reports that Daniel Rhyne, a core infrastructure engineer, was sentenced to 32 months for sabotaging and extorting his employer, an industrial firm in New Jersey. In November 2023 he planted scheduled tasks on the domain controller that deleted 13 domain admin accounts and reset passwords on 301 domain users, 254 servers and 3,284 workstations, mostly to 'TheFr0zenCrew!'. He then emailed a 20 bitcoin (about $750,000) ransom demand. Internal log correlation with physical access records, plus FBI work, traced the activity to his home IP address.

Active DirectoryBitcoin
Daniel RhyneTheFr0zenCrew!FBI+1

Threat Intelยท Published and added 10 Oct 2026

labs.watchtowr.comwriteup๐Ÿ›ก๏ธ Security

Death By A Thousand PaperCuts (PaperCut Pre-Auth RCE Chain and Patch Bypasses WT-2026-0141-0144/CVE-2026-82077/CVE-2026-82078/CVE-2026-81578)

watchTowr's analysis of the PaperCut NG 26.0.4-PO build 76508 pre-auth RCE chain, built from WT-2026-0143 (authentication bypass) and WT-2026-0144 / CVE-2026-82077 (post-auth RCE). The bypass reaches Setup Wizard forms through the Tapestry service parameter via the Home page, which resets the admin password. The RCE uses path traversal in the Scan to Fax connector. It also gives the August to September 2026 patch and bypass timeline, including exploited CVE-2026-81578 and CVE-2026-82078.

PaperCut NGApache TapestryJava
CVE-2026-82077CVE-2026-82078CVE-2026-81578+12

AppSec, Offensive Security, Identity & Accessยท Added 30 Oct 2026, published 9 Oct 2026

securityweek.comarticle๐Ÿ›ก๏ธ Security

FortiBleed Attackers Locking Victims Out of Fortinet Devices

The FortiBleed campaign targets internet-exposed Fortinet FortiGate firewalls and SSL VPN appliances using stolen credentials and brute force. SOCRadar confirms about 86,644 compromised devices in 194 countries. A joint FBI and US Secret Service advisory says attackers change passwords and delete accounts to lock victims out and keep persistence, and lists hardening steps such as phishing-resistant MFA and credential resets.

Fortinet FortiGateVPN
FortiBleedFBIUS Secret Service+5

Threat Intel, Identity & Accessยท Published and added 8 Oct 2026

github.comrepo๐Ÿ›ก๏ธ Security

deepfence/YaraHunter

YaraHunter is Deepfence's open-source scanner that applies YARA rulesets against container images, running Docker containers, and filesystems to detect indicators of compromise such as malware and cryptominers. It supports CI/CD build-time scanning, at-rest image scanning, and runtime container scanning, with JSON output for automation, and is designed to eventually integrate into the Deepfence ThreatMapper platform. The README walks through detecting the XMRig cryptominer inside a container image as a worked example.

DockerYARA
XMRig

Blue Team & Detection, DevSecOps, Malware & REยท Added 8 Oct 2026

decrypt.coarticle๐Ÿ›ก๏ธ Security

Engineer Gets 32 Months for Bitcoin Extortion Plot Against His Own Employer

A former core infrastructure engineer, Daniel Rhyne, was sentenced to 32 months for extorting his own New Jersey employer: he created a hidden virtual machine on the company network, reset passwords on hundreds of accounts to "TheFr0zenCrew!", deleted domain administrator accounts, scheduled tasks to shut down 40 servers a day, and demanded 20 BTC (~$750K) to stop. The FBI's criminal complaint describes how investigators traced the hidden VM back to him via correlated laptop browsing activity, building access logs, home IP connections, and incriminating search history ("how to clear all windows logs from command line").

BitcoinActive Directory
Daniel RhyneFBITheFr0zenCrew!

Threat Intelยท Published and added 7 Oct 2026

arxiv.orgpaper๐Ÿง  AI

ScienceClaw: Benchmarking Continual Self-Evolution of AI-for-Science Agents Across the Natural and Social Sciences

ScienceClaw formalizes a fixed-parameter program self-evolution framework for LLM agents doing scientific tasks, where verified task executions are turned into persistent Skill and Operator updates to the agent's program rather than being discarded. ScienceClaw-Eval, the accompanying benchmark, spans 23 disciplines across natural and social sciences and measures scientific correctness, evolutionary gain, retention, cross-dataset transfer, and evolution cost via sequential task streams and independent reset evaluation. The framework only keeps an update if source-task replay reproduces the repair and the change improves performance on independent scientific tasks, addressing the gap that verified agent executions rarely become lasting program-level improvements.

ScienceClawScienceClaw-Eval

evals, agents, researchยท Added 7 Oct 2026, published 6 Oct 2026

arxiv.orgpaper๐Ÿง  AI

Beyond Reward Hacking: Proxy Divergence Across Four Layers of a Staged Humanoid Learning Pipeline

This arXiv preprint extends the concept of reward hacking to four distinct "proxy" layers in a staged RL training pipeline for legged robots: the reward itself, the curriculum gate, the evaluation statistic, and the reference motion. Using measurements from a continuous PPO policy lineage trained on a simulated 1.91m humanoid over four stages and 13,500 iterations on a single laptop GPU, the author shows concrete divergence failures โ€” e.g., a curriculum gate built on averaged error that advanced at its rate limit while the gated skill was absent, and a batched push test whose synchronized resets aliased gait phase and misranked push magnitudes by danger. For each layer it proposes a reformulation that closes the divergence, including L1 costs, peak/outcome statistics, gate reachability checks, deterministic/phase-desynchronized evaluation, and function-preserving input widening for growing a single policy instead of retraining.

PyTorch
PPO

research, trainingยท Added 5 Oct 2026, published 2 Oct 2026

microsoft.comwriteup๐Ÿ›ก๏ธ Security

โ€‹โ€‹Beyond source code: A path to the keys to the kingdom

Microsoft's DART team details an investigation into Storm-3068, a threat actor that escalated from a self-service password reset account takeover into full control of an organization's Azure DevOps environment, then weaponized a malicious pipeline to harvest kubeconfig files and gain access to Kubernetes clusters. The actor also deployed the Atera remote management agent and the Chisel tunneling tool to establish reverse tunnels and alternate remote access, and exfiltrated seven stolen kubeconfig files into a repository. The report lays out the attack chain, DART's response, and hardening recommendations around SSPR monitoring, phishing-resistant MFA, branch protection, and pipeline permission controls.

Azure DevOpsKubernetesAtera+3
Storm-3068

Threat Intel, Cloud & Infra, Identity & Accessยท Added 7 Oct 2026, published 29 Sep 2026

github.comrepo๐Ÿ›ก๏ธ Security

Adversarial-Detection-Engineering/adeskills

adeskills is a working knowledge base for "Adversarial Detection Engineering" (ADE), a taxonomy of four categories and 16 subcategories of detection-logic bugs (e.g. Reformatting in Actions, Omit Alternatives, Context Development, Logic Manipulation) that explain why a SIEM/EDR/XDR rule fails to catch what it intends to. It ships 38 worked technique files with vulnerable/hardened rule examples and detection-layer guidance, a cross-platform bug-pattern catalog, a pre-engagement scoping checklist, and a Redamon-packaged skill (ade_scoper), all grounded in analysis of real public rulesets from Sigma, Elastic Security, and Microsoft Sentinel. It's explicitly scoped for defensive detection engineering and purple-team rule hardening, with several files documenting real vendor-rule weaknesses.

SigmaMicrosoft SentinelElastic Security+3
Nikolas BielskiDaniel Koifman

Blue Team & Detectionยท Added 2 Oct 2026, published 27 Sep 2026

Showing 30 of 56

Show more