Skip to content

31 results for โ€œSHIELDโ€

What you seeeverything
decrypt.coarticle๐Ÿง  AI

House Oversight Chair Comer Probes Delaware Plan for AI-Run Companies

House Oversight Chairman James Comer opened an investigation on 26 October 2026 into Delaware's proposed Artificial Intelligence Company (AIC), a legal entity run day-to-day by an AI agent. His letter to Gov. Matt Meyer requests documents, including internal AI chat logs, by 9 November. The AIC would run in a 30-month sandbox with a single member shielded from debts, and Delaware's draft legislation is expected in January 2027.

James ComerHouse Oversight CommitteeMatt Meyer+8

ai-policyยท Published and added 28 Oct 2026
mcpmarket.comtool๐Ÿง  AI

Search Search results for "security" | MCP Market

MCP Market search results for "security" in its skills category, listing about 20 installable AI agent skills. Entries cover OWASP Top 10 audits, secure PHP coding, STRIDE threat modeling, CVE remediation, security header analysis, misconfiguration finding, bug bounty triage and AgentShield scans of Claude Code configurations. One is a paid D365FO security-role XML skill. Each entry has only a one-line description and a category label.

Claude CodeAgentShieldPHP+1
MCP MarketOWASPSTRIDE

coding-agents, promptingยท Added 25 Oct 2026

mcpmarket.comother๐Ÿ›ก๏ธ Security

Search Search results for "security" | MCP Market

MCP Market search results for "security" in the skills category, listing about 20 installable AI agent skills. Entries cover OWASP Top 10 audits, secure coding for PHP, STRIDE threat modeling, CVE remediation, security header analysis, misconfiguration finding, bug bounty triage and AgentShield scans of Claude Code configurations. One is a paid D365FO security-role XML skill. Each entry has only a one-line description and a category label.

Claude CodeModel Context ProtocolPHP
OWASPSTRIDEAgentShield+1

AppSec, AI Securityยท Added 25 Oct 2026

github.comrepo๐Ÿ›ก๏ธ Security

Spectrmachina/Ztrust

ZTrust is a Python supply-chain scanner that checks manifests, lockfiles, source and GitHub workflows for vulnerable or malicious dependencies (via OSV.dev), typosquats, leaked secrets, unsafe lockfiles and risky CI patterns such as pwn requests and script injection. It outputs console, JSON and SARIF 2.1.0 and ships as a GitHub Action. It also includes a FastAPI bounty service using commit-reveal and shielded Zcash payouts for researchers.

PythonGitHub ActionsOSV+3
xz-utilstj-actions/changed-filesevent-stream+3

Supply Chain, DevSecOpsยท Added 27 Oct 2026, published 22 Oct 2026

decrypt.coarticle๐Ÿ›ก๏ธ Security

Zcash Developer Zakura Proposes Fix to Stop Quantum Computers Linking Shielded Swaps

Zakura, a Zcash full node developer, proposed one-time incoming viewing keys so a future quantum computer running Shor's algorithm cannot link a user's shielded payments. The target is NEAR Intents swaps, which post a shielded refund address on a public chain. The fix needs no network upgrade and uses private information retrieval for seed restores. Wallets such as Vizor can add it within weeks.

Zcash
Shor's algorithmNEAR IntentsZakura+5

Blockchainยท Published and added 19 Oct 2026

huggingface.coarticle๐Ÿง  AI

HiRO-ACEv2: Simulating extreme weather at 3 km resolution for a fraction of the cost

Ai2 announces HiRO-ACEv2, an update to its AI climate emulator. ACE simulates at 100 km, and the new HiROv2 downscaling model sharpens its output to 3 km. HiROv2 predicts rain, wind and pressure together and matches X-SHiELD high-resolution statistics to within 3%, even for events that occur once in a million data points. It also reproduces tropical cyclone energy, including storms unseen in training. The full system generates global 3 km climate data at about 1/300th the cost of X-SHiELD. Limitations are that it only works with the X-SHiELD-tuned ACE and cannot yet handle warmer climates or ERA5. Models, tutorial notebooks and a web demo are available.

HiRO-ACEACEX-SHiELD
Ai2HiRO-ACEv2HiROv1+3

models, researchยท Published and added 14 Oct 2026

ethereum-magicians.orgarticle๐Ÿ›ก๏ธ Security

ERC-8443: Quantum Bridge Shield

Draft ERC from Quantova Inc proposing a "Quantum Bridge Shield" for Ethereum bridges. A committee signs the Merkle root of each message batch with RFC 8554 LMS hash-based signatures instead of ECDSA/BLS keys that Shor's algorithm can break. The guard contract requires a strict majority of distinct unfrozen keys, records used leaves, freezes any key that signs a leaf twice, binds digests to domain, chain, guard and epoch, and applies a 60-second delay. The post gives gas costs (LMS W4 height-10 verification about 205k gas, a LayerZero packet 128,683 gas, worst-case rotation 12.44M gas under the EIP-7825 cap) and cites a NioLabs assessment with no critical or high findings. It is relevant as a worked post-quantum migration design for bridge key custody, including hybrid ECDSA+LMS mode and stateful-signature pitfalls such as leaf reuse and rollback.

EthereumLayerZeroLMS
ERC-8443Quantova IncShor's algorithm+11

Blockchainยท Published and added 14 Oct 2026

ethereum-magicians.orgpaper๐Ÿ›ก๏ธ Security

ERC: Quantum Bridge Shield

Draft ERC from Quantova Inc that has Ethereum bridges accept cross-chain message batches only when a committee signs the Merkle root with RFC 8554 LMS hash-based signatures. The guard contract requires a strict majority of distinct unfrozen keys, records used leaves, freezes any key that signs a leaf twice, binds digests to domain tag, chain ID, guard address and epoch, and enforces a 60-second delay. It reports gas benchmarks (about 205k per LMS W4 height-10 verify, 12.44M worst-case rotation under EIP-7825), a hybrid LMS+ECDSA migration mode, and a NioLabs assessment with no critical or high findings. It argues that Shor's algorithm makes secp256k1 and BLS committee keys a quantum theft target.

EthereumLayerZero
Quantova IncNioLabsRFC 8554+7

Blockchainยท Published and added 14 Oct 2026

decrypt.coarticle๐Ÿ›ก๏ธ Security

Ledger Says All Confirmed Cases in Suspected $87M Drain Tied to Reseller CryptoBilis

Decrypt reports Ledger's 72-hour update: all confirmed wallet-draining cases involve devices sold by Southeast Asian reseller CryptoBilis, which has stopped hardware wallet sales. Onchain investigators Specter and YFarmX traced over $86M in suspected thefts across Ethereum, Tron and Bitcoin. They describe laundering through Tornado Cash, Zcash's shielded pool and a USDT-to-USDD swap to avoid Tether freezes. An unverified claim of tampered devices (extra cables, LTE module) bought at European retail stores is also covered. Ledger advises CryptoBilis buyers not to set up devices and to move funds to a new seed phrase on a device bought from Ledger.

LedgerEthereumBitcoin+2
CryptoBilisSpecterYFarmX+5

Blockchain, Hardware & RF, Threat Intelยท Published and added 12 Oct 2026

bleepingcomputer.comarticle๐Ÿ›ก๏ธ Security

Ledger confirms spy chip implant behind wallet crypto thefts

Ledger confirmed that devices sold by Southeast Asian reseller CryptoBilis carried an unauthorized hardware implant that drained users' crypto wallets. Researchers Mark Karpelรจs and Tibane Labs describe the implant: an STM32G431 MCU, eSIM and shielded LTE module hidden behind the OLED screen, which captures display output and button presses to recover the seed phrase and sends it out over LTE. The article covers two implant variants, the telltale antenna wire, and Ledger's guidance (avoid unauthorized resellers, move funds to a new seed). Ledger also warns that its Genuine Check cannot detect implants when the original Secure Element is intact.

Ledger
CryptoBilisMark KarpelรจsTibane Labs+3

Hardware & RF, Blockchain, Threat Intelยท Added 13 Oct 2026, published 12 Oct 2026

coindesk.comarticle๐Ÿ›ก๏ธ Security

Zcash developers set January target for quantum-resistant payments after โ€˜bunker modeโ€™ scare

Zcash developer Roman Akhtariev, writing for the Zakura client team, announced a January target for adding post-quantum signature opcodes supporting hash-based signatures to Zcash's transparent (public) payment pool, which holds about 70% of issued ZEC. The move responds to Ethereum researcher Justin Drake's "bunker mode" warning that AI could soon break the elliptic-curve math behind Bitcoin and Ethereum wallet keys. Zakura has also built a private-information-retrieval balance-lookup tool, now experimentally available in the Vizor wallet, that lets a wallet check address balances without revealing to the server which addresses are linked, separate from the shielded-pool quantum-recovery work still needed to defend against store-now-decrypt-later attacks.

ZcashVizor
Roman AkhtarievJustin DrakeML-DSA+1

Blockchainยท Published and added 9 Oct 2026

galaxy.comarticle๐Ÿ›ก๏ธ Security

โ€˜Shielded Bitcoin

Galaxy Research newsletter piece covering "Shielded Bitcoin," a paper by [[alloc] init] researchers Clara Shikhelman, Mikhail Komarov, and Aleksei Moskvin proposing a Zcash-style shielded pool (encrypted notes, public nullifiers, zero-knowledge proofs) run as a Bitcoin L1 metaprotocol via OP_RETURN envelopes, with peg-in/peg-out deliberately left to a future "PIPEs v2" paper. The article's security-relevant angle flags that novel ZK circuits need battle-testing โ€” citing Zcash's own Orchard Pool soundness bug that survived professional audits for four years before being fixed in the Ironwood upgrade โ€” and that bridge/peg mechanisms (the likely weak point) have historically been the most exploited component in crypto, naming Ronin, Wormhole, Nomad, and KelpDAO. It also notes a growing AI-driven deanonymization threat to transparent blockchains, citing ETH Zurich/Anthropic research showing LLM agents can re-identify pseudonymous users from profile data alone.

BitcoinZcash
RoninWormholeNomad+5

Blockchainยท Added 8 Oct 2026
galaxy.comarticle๐Ÿง  AI

Weekly Research Brief: AI Governance, Shielded Bitcoin, and Mention Markets

Galaxy Research's weekly brief devotes its lead section to AI governance: it recaps Sam Altman's and Dario Amodei's UN Security Council remarks calling for international AI safety coordination, contrasts a disclosed OpenAI agent incident (an agent accessed non-public Medicare data in Australia, reported three months late) with Anthropic's 950-agent DNA-database research run, and cites concrete agent-economy data โ€” OpenRouter's agent token usage overtaking human usage and growing ~14x since February, Cloudflare's agent-traffic crossover, and Vercel AI Gateway data showing a 23% monthly price drop and open-weight models rising to 56% of token volume. The analysis argues that as inference gets cheaper and open-weight models gain share, AI governance's hard problem shifts from controlling frontier labs to controlling where cheap, widely available agents can act. The rest of the newsletter covers an unrelated Bitcoin privacy protocol proposal and CFTC guidance on prediction "mention markets."

OpenRouterCloudflareVercel AI Gateway+1
Sam AltmanDario AmodeiOpenAI+7

ai-policyยท Added 8 Oct 2026

x.comwriteup๐Ÿ›ก๏ธ Security

lee1981 (@lee1981b) on X

A detailed "CVE of the Day" thread analyzing CVE-2026-76471, a critical (CVSS 9.8) Cisco advisory covering insufficient NX-API input validation (CWE-122 heap-based buffer overflow) on Nexus 3000/9000 standalone NX-OS and a lower-severity credentialed variant on UCS 6300 Fabric Interconnects via UCS Manager XML API. It compiles Cisco's fixed-software versions per platform, notes the temporary Live Protect shield lp00074, and walks through a six-step SOC evidence-preservation and correlation playbook (scoping affected devices, preserving logs/crash artifacts, reviewing API/shield telemetry, correlating device outcomes, remediating, and verifying post-patch state) while flagging that CISA KEV and FIRST EPSS had no data on the CVE at research time.

CVSSNVDCISA KEV+1
CVE-2026-76471

Cloud & Infraยท Published and added 8 Oct 2026

ncsc.gov.ukarticle๐Ÿ›ก๏ธ Security

NCSC: "One does not simply defend agentically"

NCSC CTO for Architecture Dave Chismon argues that while attackers can freely use agentic AI tooling for technical offensive tasks, defenders face organisational/political constraints (Halvar Flake's maxim) that make equivalent autonomous defensive action far riskier. The piece proposes a framework for assessing the 'riskiness' of automating defensive actions (potency, harm to the business, scope of control), points to low-risk starting points like AI-assisted log summarisation and vulnerability triage, and previews NCSC/DCMS's 'Cyber Shield' agentic defence ecosystem and an upcoming 'AI for Cyber Defence' problem book, alongside references to CETAS's Autonomous Cyber Defence work and the Defra AI Legacy Modernisation Playbook.

SOAR
Halvar FlakeCETASCyber Shield+4

AI Security, Blue Team & Detectionยท Added 1 Oct 2026

x.comthread๐Ÿ›ก๏ธ Security

When Models Turn Brutal

A vendor thread from ZeroShieldAI argues the patch window has collapsed because AI models can now find and weaponize vulnerabilities faster than defenders can fix them. It cites ZeroDayBench (success jumping from ~13% on blind zero-days to 78% once patch location is known), Aikido Security's benchmark where DeepSeek V4 Pro found 28 of 32 recent CVEs for about 98 dollars per run, a Unit 42 finding that 92% of AI-discovered flaws are logic bugs fuzzers miss, and a Hugging Face stat that 16 of the top 300 models advertise removed safety guardrails with 16.8M downloads. It promotes an attached 6-page case study and lists five defender recommendations: treat disclosure as exploit day, maintain SBOM/AIBOM, inventory models and agents, gate agent tool calls with policy, and red-team code and AI apps.

DeepSeekAikido SecurityHugging Face+1
ZeroDayBenchUnit 42

AI Security, Threat Intelยท Published and added 1 Oct 2026

decrypt.coarticle๐Ÿ›ก๏ธ Security

Bitget Hacker Turns to Zcash Privacy Pool After Near Rejects $50M in Swaps

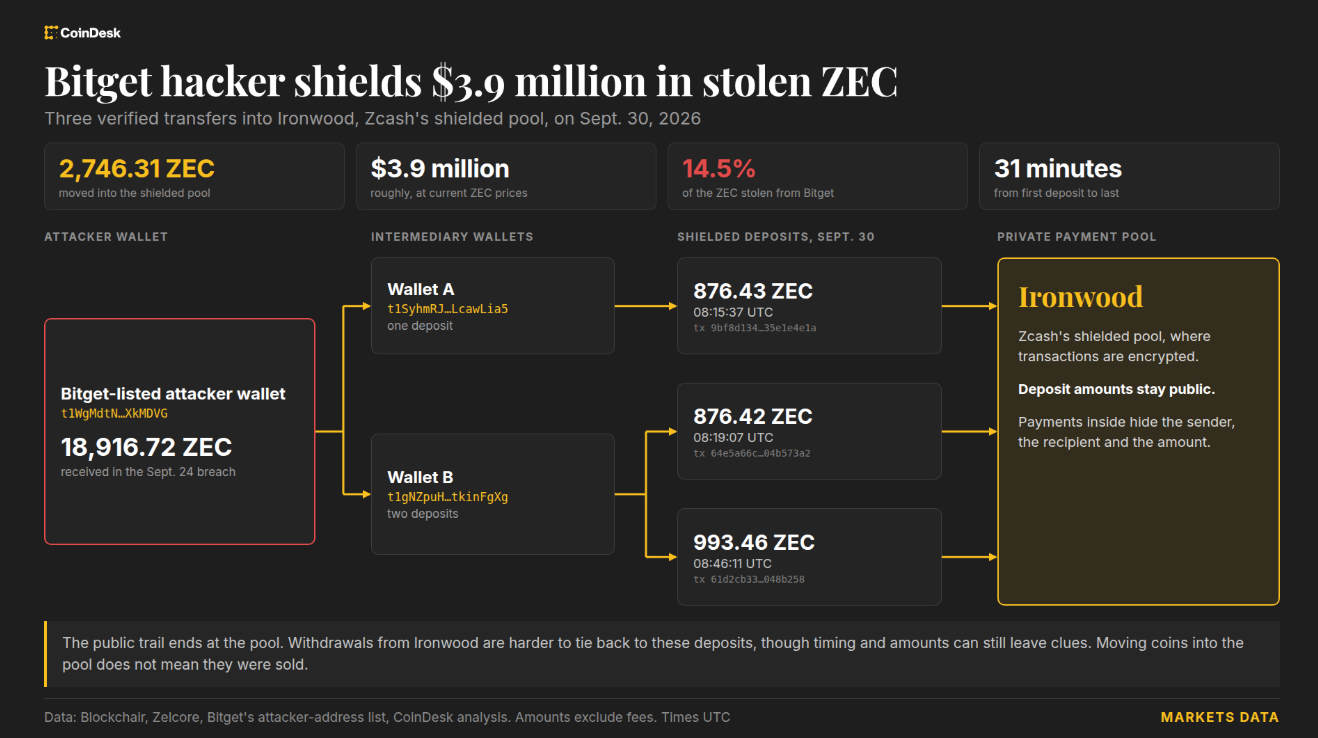
Decrypt reports that the attacker behind Bitget's $387.5M hot-wallet theft (Sept. 24) began shielding ~2,700 ZEC (~$3.8M) in Zcash's new Ironwood privacy pool, per on-chain investigator ZachXBT. Bitget's CEO and Elliptic attribute the heist to North Korea, and TRM Labs traced laundering through round-number wallet splits and cross-chain swap services including Thorchain, Across, Bridgers, Chainflip, and FixedFloat. Near Intents' SHIELD screening blocked over $50M in related swaps while Thorchain refused to selectively halt the attacker's addresses, spotlighting the gap between blockchain "permissionless" design and real-time sanctions/freeze response during active exchange-hack laundering.

ZcashTHORChain
ZachXBTTRM LabsElliptic+3

Blockchainยท Published and added 30 Sep 2026

coindesk.comarticle๐Ÿ›ก๏ธ Security

Bitget hackers move $4 million into Zcashโ€™s private pool, making funds harder to trace

CoinDesk traces wallets linked to the Sept. 24 Bitget hack ($387.5M stolen) moving 2,746 ZEC (~$3.9M, ~15% of stolen ZEC) into Zcash's Ironwood shielded pool via two intermediary addresses, obscuring sender, recipient and amount once inside the pool. Blockchain investigator ZachXBT first flagged the transfers; separately, other attacker-linked proceeds were previously traced swapping ~$6.3M ether to bitcoin via THORChain despite the exchange's request to block the hacker. The piece illustrates real-world laundering tradecraft (privacy-pool deposits plus cross-chain DEX swaps) and the limits of on-chain tracing once funds enter a shielded pool.

ZcashTHORChainEthereum+1
Bitget hackZachXBTIronwood shielded pool

Blockchain, Threat Intelยท Published and added 30 Sep 2026

bankless.comarticle๐Ÿ›ก๏ธ Security

NEAR Stopped Bitget's Hackers Without Breaking Privacy

Following the ~$387.5M Bitget hack on September 24th (attributed to North Korea-pattern tactics), attackers tried to launder funds via crosschain rails: THORChain refused Bitget's request to block the hacker's address and later saw $6M+ swapped through it, while NEAR Intents' SHIELD risk-intel layer rejected nearly all of a $50M+ attempted transfer, letting only $166k through. The piece explains the architecture: deposits/withdrawals are public on-chain transactions, but balances/routes/trades happen inside NEAR's Confidential Intents, and SHIELD acts as a gate checking public deposit addresses against shared stolen-funds intel before allowing Intents execution โ€” without unmasking or freezing wallets, since Intents sits atop NEAR's consensus rather than being part of it. It also notes SHIELD's limits (funds simply got rerouted elsewhere) and NEAR co-founder Illia Polosukhin's pitch to make SHIELD shared infra other protocols can adopt.

NEAR IntentsTHORChainEthereum+1
Bitget hackBybit hackDPRK+4

Blockchain, Threat Intelยท Added 30 Sep 2026, published 29 Sep 2026

coindesk.comarticle๐Ÿ›ก๏ธ Security

Near Intents blocks $50 million in Bitget hacker swaps, here's what happened

After attackers stole $388M from Bitget, they tried routing $50M+ through the cross-chain swap service NEAR Intents; its SHIELD system โ€” which ingests KYT and intelligence-provider signals to flag deviations in flow โ€” froze roughly $503,000 mid-swap while $166,000 slipped through. The piece contrasts this with THORChain's refusal to block the same attacker addresses, letting $6.3M complete ether-to-bitcoin swaps, and details the resulting debate over whether a "permissionless" protocol can hold user funds without a defined process for release or appeal.

NEAR IntentsTHORChainBitcoin+1
Bitget hackSHIELDAlex Shevchenko+1

Blockchain, Threat Intelยท Added 30 Sep 2026, published 29 Sep 2026

arxiv.orgpaper๐Ÿ›ก๏ธ Security

Delegation Without Trust: An Empirical Gap Analysis of Identity, Authorization, and Runtime Governance in Multi-Agent LLM Systems

This arXiv paper defines a threat model for multi-agent LLM delegation covering four adversaries (confused deputy, token theft/replay, prompt-injection privilege escalation, compromised sub-agents) and derives eight security requirements for governed agent systems. It shows that LangGraph, CrewAI, AutoGen, and the MCP authorization model each fail to meet the full requirement set, then implements and adversarially tests an authorization broker that blocks all four threats, rejects 0 of 200,000 forged tokens, and confines a compromised sub-agent to a mean of 1.5 reachable actions (vs. 8,100 under bearer delegation) at ~2.6 microseconds per decision. The broker's principles are said to be productized in VotalAI's LLM Shield.

Model Context ProtocolLangGraphCrewAI+2
confused deputytoken theft and replayprompt-injection privilege escalation+2

AI Security, Identity & Accessยท Added 26 Sep 2026

arxiv.orgpaper๐Ÿ›ก๏ธ Security

From Shield to Target: Denial-of-Service Attacks on LLM-Based Agent Guardrails

Researchers show that LLM-based guardrails deployed to catch prompt injection and jailbreaks can themselves be attacked: crafted natural-language payloads trap the guardrail's reasoning in extended loops, causing a systematic denial-of-service. A beam-search optimization framework (an LLM proposer guided by a strategy bank) and a lighter mechanism-aware structural-mutation attack both generalize across guardrail architectures and safety templates, with payloads optimized on one open-source surrogate transferring to Claude, GPT, Gemini, DeepSeek, and Qwen backbones, achieving 13-63x token amplification and up to 148x latency amplification in real web, desktop, code, and multi-agent deployments โ€” enough for a single poisoned document to starve co-located agents on shared guardrail infrastructure.

ClaudeGPTGemini+2

AI Securityยท Added 26 Sep 2026

blog.talosintelligence.comarticle๐Ÿ›ก๏ธ Security

We've got one word for it, and it's usually the wrong one

Cisco Talos's weekly Threat Source newsletter opens with a personal essay distinguishing burnout from secondary traumatic stress, vicarious trauma, and moral injury among security practitioners, then covers Talos's disclosure of a WebDAV-based infection chain used by Russian-aligned actor UAT-10820 against a Ukrainian government target, delivering the Amatera stealer alongside ZigCryptoStealer and NetSupport Manager, abusing BNB Smart Chain for bulletproof hosting and fake CAPTCHA lures, with a vulnerable driver used to kill EDR. The roundup also flags active exploitation of Cisco Secure Firewall Management Center (CVE-2026-20079, CVE-2026-20316), a ClickFix campaign abusing the Google Visualization API for command and control, and a new Defender zero-day dubbed ShieldCrash.

WebDAVNetSupport ManagerCisco Secure Firewall Management Center+2
CVE-2026-20079CVE-2026-20316UAT-10820+5

Threat Intel, Blue Team & Detectionยท Added 7 Oct 2026, published 10 Sep 2026

github.comrepo๐Ÿ›ก๏ธ Security

Awesome Cybersecurity Agentic AI

A curated GitHub awesome-list cataloging the emerging agentic-AI security ecosystem: dozens of Model Context Protocol servers that give LLM agents access to security tools (Nuclei, Shodan, VirusTotal, Burp Suite, Ghidra, BloodHound, x64dbg), autonomous penetration-testing and CTF-solving agent frameworks (CAI, pentagi, BreachSeek, Dark-Moon, D-CIPHER), scanners/guardrails that audit agent skills, MCP servers, and multi-agent chains for prompt injection and other risks (Aguara, Inkog, MCP Doctor, AI-Infra-Guard, ATR), agentic SOC/detection platforms (Vigil), threat-modeling frameworks for agentic systems (MAESTRO, ATFAA/SHIELD), research papers, benchmark datasets, and community/learning resources. It functions as a living index for anyone building or defending AI-agent-driven security tooling.

Model Context ProtocolLangChainCrewAI+3
OWASP Top 10 for LLM ApplicationsEU AI ActOWASP FinBot CTF+1

AI Security, Offensive Security, Blue Team & Detectionยท Added 3 Sep 2026, published 31 Aug 2026

socket.devwriteup๐Ÿ›ก๏ธ Security

Socket: Fake Corepack Site Distributes Infostealer and Proxyware to Developers

Socket's Threat Research team analyzed corepack[.]org, a fake site impersonating the Node.js Corepack tool that exploits its 2025 removal from Node.js bundling to rank in search results and trick developers into downloading a fake VPN installer. The installer drops OpenShield (an infostealer with browser-data/SSH-key theft, PowerShell execution, and run-key persistence) plus a bandwidth-sharing proxyware component that turns victim machines into proxy exit nodes, while a second click path delivers adware/trojan activity via OperaGXSetup.exe. The post includes full IOCs and details community/OpenJS Foundation takedown efforts against the domain.

CorepackNode.jsnpm+3
OpenShieldApprunnercorepack[.]org+3

Threat Intel, Supply Chainยท Published and added 25 Jul 2026

github.comrepo๐Ÿ›ก๏ธ Security

meta-llama/PurpleLlama

Purple Llama is Meta's umbrella repo of tools and evals for building safely with generative AI, bundling Llama Guard (input/output content moderation fine-tuned on Llama 3.1/3.2), Prompt Guard (detects prompt injection and jailbreak attempts), Code Shield (inference-time filtering of insecure LLM-generated code and code-interpreter abuse prevention), and the CyberSec Eval benchmark suite (CWE/MITRE ATT&CK-based tests now spanning insecure code generation, offensive cyber capability, spear-phishing, and visual prompt injection). It matters as one of the first industry-wide, MIT-licensed benchmark and safeguard sets specifically for LLM cybersecurity risk.

LlamaHugging FaceMITRE ATT&CK
Llama GuardPrompt GuardCode Shield+1

AI Securityยท Published and added 14 Jul 2026

github.comrepo๐Ÿ›ก๏ธ Security

affaan-m/agentshield

AgentShield is a CLI/GitHub Action security auditor that scans a Claude Code .claude/ directory for hardcoded secrets, overly permissive Bash/tool allow rules, hook injection, risky MCP server configs, and agent prompt-injection surfaces, producing an Aโ€“F graded report with 268 rules across 15 modules. It adds runtime-confidence classification (active-runtime vs. template/docs/plugin-cache) to reduce false positives, a three-agent Claude Opus red-team/blue-team/auditor pipeline for adversarial analysis, MCP supply-chain provenance checks, SOC2/PCI/ISO compliance control mapping, SARIF output for GitHub code scanning, and tamper-evident evidence packs for CI/audit handoff.

Claude CodeModel Context ProtocolGitHub Actions+3
Moltbook breach

AI Security, DevSecOps, Supply Chainยท Added 30 May 2026

reco.aiwriteup๐Ÿ›ก๏ธ Security

Salesforce Pentest: Apex Predator

A deep technical guide from Reco on pentesting Salesforce Experience Cloud "Aura" sites, covering how to enumerate guest-user-accessible sObjects via HostConfigController and SelectableListDataProviderController, and how to discover and invoke custom server-side Apex controller methods exposed to guest/authenticated users. It introduces novel techniques for extracting Apex method parameters from compiled Lightning Web Component JS (via the lri/moduleDefs structures), using ComponentController.getComponent and siteforce:routerInitializer to enumerate every site route/page and its Apex-backed components beyond what standard tools like AuraInspector find, plus an appendix of undocumented native controllers including an Aura-exposed GraphQL execution endpoint (RecordUiController.executeGraphQL). It closes with defensive guidance on monitoring AuraRequest events via Salesforce Shield to detect abuse.

SalesforceGraphQLBurp Suite

Offensive Security, AppSecยท Added 3 Sep 2026, published 13 May 2026

owasp.orgarticle๐Ÿ›ก๏ธ Security

OWASP Free AppSec Tools

OWASP's community-maintained catalog of application security tools that are free for open source projects, organized by category: SAST (GitHub CodeQL, Coverity, HCL AppScan CodeSweep), DAST (OWASP ZAP, StackHawk, Akto, Arachni), IAST (Contrast CE), software composition analysis/dependency scanning (Dependabot, Snyk, Mend, retire.js, Debricked), secrets detection (Gitleaks, TruffleHog, GitGuardian, Kingfisher), code quality (SonarQube, SpotBugs, MegaLinter), CI/CD security (GitLab built-ins, Faraday), and automatic remediation (Mobb, Corgea). It also covers newer entrants like Zennoxa Shield, cloud-audit, Cynative, and post-quantum crypto risk tools (CARAF, PQBench). Serves as a practical shopping list for securing an OSS project's SDLC end-to-end.

OWASP ZAPCodeQLSnyk+3
OWASP Top 10-2017 A9

AppSec, DevSecOps, Supply Chainยท Published and added 6 May 2026

youtu.bevideo๐Ÿ›ก๏ธ Security

SecTor 2025 | Ghost SIM Attack: Hacking Mobile Network Authentication Policies

Security researchers from Ethon Shield introduce the Ghost SIM attack, demonstrating how extracting non-cryptographic SIM metadata without the secret key (Ki) enables cellular network impersonation across 2G, 3G, 4G, and 5G networks. The exploit takes advantage of permissive, event-based or time-based carrier authentication policies that skip cryptographic verification during network attachment. Defenses include enforcing SIM PINs on end-user devices and mandating cryptographic authentication on all initial network attachments by cellular operators.

2G GSM mobile networks3G UMTS mobile networks4G LTE mobile networks+17
CVE-2016-4030CVE-2016-4031CVE-2016-4032+16

Mobile Securityยท Added 12 May 2026, published 25 Apr 2026

Showing 30 of 31

Show more