 Earliest Known PolinRider Malware Found in 2025 npm Packages
OpenSourceMalware traces nine itsa-* npm package versions published on 4 May 2025 from a hijacked maintainer account to the PolinRider campaign, eight months before documented victims. It decodes the EtherHiding chain (BNB Smart Chain and Ethereum calldata, JADESNOW, INVISIBLEFERRET bootstrapper, Socket.IO RAT, Python stealer) and links the 2025 sample to 2026 force-push infections. It lists IOCs, hashes, a timeline and hunting guidance.
 opensourcemalware.comwriteupPublished and added 30 Oct 2026🛡️ Security
 How a Misconfigured CI Workflow Became an npm Supply-Chain Compromise | Blog | Endor Labs
Endor Labs breaks down the May 11, 2026 compromise of 42 @tanstack/* npm packages (84 malicious versions) that carried valid SLSA provenance. The attacker chained a pull_request_target "Pwn Request", GitHub Actions cache poisoning across the fork/base boundary, and OIDC token extraction from Runner.Worker memory, then published directly to npm without stealing any credential. It explains why 2FA, trusted publishing, provenance and branch protection all failed, and lists mitigations: split pull_request_target workflows, treat the cache as untrusted, scope id-token: write to a publish job, pin actions to SHAs, require environment approval, use egress allowlists.
 endorlabs.comwriteupPublished and added 12 Oct 2026🛡️ Security
 Tensorlake npm Package Compromised: A Worm With a Hostage Token That Wipes Your Machine If You Revoke It
StepSecurity details how tensorlake@0.5.144 was pushed to npm after malicious commits landed directly on the tensorlakeai/tensorlake GitHub repo's main branch under a maintainer's identity, carrying a valid npm provenance attestation despite being malicious. The preinstall hook downloads Bun to run an obfuscated payload that steals GitHub/npm tokens, cloud and Vault/Kubernetes secrets, SSH keys, browser logins, and AI-tool configs (Claude, Cursor, Windsurf), then self-propagates by republishing stolen npm packages and committing persistence files (.claude/settings.json, .vscode/tasks.json) to reachable repos. A "hostage token" mechanism installs a gh-token-monitor service that runs a home-directory wipe if the stolen GitHub token is revoked before the monitor is removed, inverting the normal incident-response order.
 stepsecurity.iowriteupPublished and added 8 Oct 2026🛡️ Security
 The MCP Ecosystem Is Speaking Five Revisions at Once
A dated research report (Pennyforge, 2026-10-02) that probes the live MCP ecosystem to show it is fragmented across five spec revisions at once: it POSTs initialize/server/discover calls against 186 deduplicated endpoints pulled from the official MCP registry's v0 API, plus 10 popular npm stdio servers spawned via npx. It finds only ~9.7% of responding endpoints speak the new stateless 2026-07-28 wire (which removes Mcp-Session-Id, the initialize handshake, and adds server/discover), that the flagship @modelcontextprotocol/server npm packages still only speak the older 2025-06-18 revision, and documents a "version-echo" methodology pitfall where servers negotiate within a supported range rather than reporting a fixed version — illustrated with a parallel failure mode found in the x402 payment protocol.
 dev.towriteupPublished and added 2 Oct 2026🧠 AI
- Compromised npm Packages in the AsyncAPI Namespace Deliver Miasma Botnet Loader
Socket's Threat Research Team details a supply-chain compromise of four @asyncapi npm packages (generator-helpers, generator-components, generator, specs) published via a poisoned source commit through GitHub Actions trusted publishing. The packages contain an obfuscated load-time (not install-hook) implant that spawns a detached Node.js process to fetch an IPFS-hosted, AES-256-GCM-encrypted loader delivering the "Miasma" botnet/tasking framework, which supports REST C2, multi-channel comms (Nostr, IPFS, Ethereum RPC, BitTorrent DHT), shell execution, file exfiltration, and systemd persistence. Includes full technical analysis, IOCs, hashes, and MITRE ATT&CK mapping.
 socket.devwriteupAdded 21 Sep 2026🛡️ Security
 Socket: Two Joyfill npm Beta Releases Compromised to Deliver DEV#POPPER Remote Access Trojan
Socket's research team found two beta releases of the @joyfill npm packages (@joyfill/layouts and @joyfill/components) contained an import-time JavaScript implant that resolves encrypted payloads through Tron, Aptos, and BNB Smart Chain transactions, ultimately dropping a 77KB Node.js remote-access trojan matching the DEV#POPPER family and sharing loader fingerprints with the PolinRider blockchain-loader campaign. The RAT establishes a Socket.IO C2 channel, executes arbitrary JS/shell commands, exfiltrates files and clipboard data, and persists by patching files inside VS Code, Cursor, Antigravity, Discord Desktop, GitHub Desktop, and the global npm CLI; a parallel detached-process branch fetches an additional bootstrap that can deploy a Python credential/browser-data stealer assessed as an OmniStealer variant. Because the implant fires on module load (not via npm lifecycle scripts), `--ignore-scripts` provides no protection, and the writeup includes full IOCs, blockchain addresses, C2 infrastructure, and MITRE ATT&CK mappings.
socket.devwriteupAdded 22 Sep 2026, published 20 Sep 2026🛡️ Security WeaselBiscuit Strips BeaverTail and OtterCookie Down to Essentials
OpenSourceMalware researchers detail WeaselBiscuit, a newly discovered lightweight JavaScript infostealer found hidden in 11+ npm packages (e.g. process-tailwind, engin1, the @biz44 scope), which shares tradecraft with DPRK-linked BeaverTail/OtterCookie but strips out wallet-draining, password decryption, and remote-shell features. The writeup walks through the full infection chain - a package auto-running a detached Node loader, fetching a Base64-encoded second stage from Npoint dead-drop URLs, and beaconing to a hardcoded HTTP C2 (103.170.217.184:8787) - plus its capabilities (Chrome extension-storage theft, clipboard capture, Windows keylogging) and a campaign-cluster graph tying packages together via shared hashes and resolver URLs. Attribution to DPRK is explicitly labeled a tentative hypothesis rather than confirmed.
opensourcemalware.comwriteupPublished and added 17 Sep 2026🛡️ Security NPM Isn't Prepared For North Korean PolinRider Attack
OpenSourceMalware's case study on npm packages fetch-page-assets and html-to-gutenberg, maintained by a legitimate developer (DiogoAngelim) whose GitHub account was compromised by the DPRK-linked PolinRider campaign in March 2026. The post shows GitHub server-side push timestamps proving all seven of the maintainer's repos were force-pushed with an identical NullReceiver loader in two coordinated bursts, and that after npm pulled the flagged v1.2.9 (GHSA-vxq2-vhm7-7mhq), every subsequent release (v1.2.10-v1.2.14) kept shipping the same .vscode/tasks.json auto-run trigger, with the attacker later adding a second obfuscated payload appended to babel.config.cjs. It argues npm/GitHub's per-version advisory model can't scale against thousands of PolinRider-compromised maintainers and lists specific IOCs (hashes, C2 wallet, RPC endpoints).
opensourcemalware.comwriteupAdded 3 Sep 2026, published 25 Aug 2026🛡️ Security Russian AI Slopsquatting Publishes 700+ Malicious NPM Packages
OpenSourceMalware documents WEL1DROPPER (aka Flooding Dropper), a campaign that published 788+ slopsquatted npm packages (e.g. checkout-mobile-bnpl) which execute on require() with no install script, downloading cross-platform RAT/infostealer payloads via rotating Cloudflare Workers URLs with a DNS TXT-record fallback channel. The writeup reverse-engineers the Linux (UPX-packed ELF) and macOS (universal Mach-O) second-stage payloads, detailing anti-analysis checks, LaunchAgent persistence disguised as com.apple.windowserver.helper, XOR-obfuscated C2 domains, a suspected Sliver C2 final stage, and ties the campaign to Russian financial-sector lures and the earlier Moika npm campaign.
opensourcemalware.comwriteupAdded 3 Sep 2026, published 6 Aug 2026🛡️ Security keyv and cacheable npm Package Hijacked in Supply Chain Attack
Wiz Research documents an ongoing supply chain attack in which a compromised GitHub maintainer account was used to publish malicious versions of keyv, cacheable, and 400+ dependent npm packages. The payload is a variant of the open-sourced 'Mini' Shai-Hulud malware (linked to the TeamPCP and antv campaigns) that steals cloud, CI/CD, AI-agent, and cryptocurrency credentials, persists via Claude Code hooks and VS Code tasks.json, exfiltrates data to attacker-controlled GitHub repos, and retrieves its C2 domain dynamically via an Ethereum smart contract (StringListStore) eth_call rather than hardcoding it.
 wiz.iowriteupAdded 3 Sep 2026, published 4 Aug 2026🛡️ Security
 'ChainDrop' worm compromises hundreds of popular npm packages
ChainDrop is an npm worm that compromised hundreds of packages on 4 August 2026, some with over 150 million weekly downloads, starting from a malicious commit (174f6a5) in the keyv repository. Datadog dissects the Bun-based loader, the obfuscated second stage, credential theft (files, GitHub Actions runner memory, AWS, Kubernetes, Vault), Ethereum smart-contract C2 discovery, AES/RSA exfiltration, an eval channel, and propagation via stolen npm tokens, GitHub branches and Sigstore provenance. IOCs and a list of affected packages are included.
 securitylabs.datadoghq.comwriteupAdded 29 Oct 2026, published 4 Aug 2026🛡️ Security
 NullReceiver's Blank Crypto Transfers Solves the Challenges of EtherHiding
Researchers analyzing the DPRK-linked npm packages bianira-ui@1.27.0 and fluid-type-ui@2.0.8 (Contagious Interview campaign, trojanized clones of Tailwind CSS plugins) identified NullReceiver, a new blockchain C2-resolution technique that encodes the C2 IP address directly in the bytes of the recipient address of a zero-value, zero-data Ethereum transfer, rather than in calldata as with EtherHiding. Because it uses a disposable, never-reused destination address and carries no data field, it avoids the fixed "burn address" landmark that let Google's GTIG detect EtherHiding, making it harder to fingerprint. The writeup includes the malware's wallet-lookup logic, a code snippet, and full IOCs (packages, attacker wallet, encoded address, C2 IPs).
opensourcemalware.comwriteupAdded 3 Sep 2026, published 2 Aug 2026🛡️ Security PolinRider Caused Dozens of npm, Go, PHP Compromises
OpenSourceMalware's research ties together JFrog's, Nextron's, and Socket's separate reports on compromised html-to-gutenberg/fetch-page-assets npm packages, 16 Go modules, and Joyfill's poisoned beta releases, attributing all of them to DPRK's PolinRider campaign via shared XOR keys, TRON/Aptos wallets, C2 infrastructure, and the fa-solid-400.woff2 loader file hash. The piece argues these aren't targeted account takeovers but automated propagation from infected maintainer machines (via temp_auto_push.bat git history rewriting and stolen .npmrc tokens), and uses GH Archive to prove that 43 of 64 analyzed Go module pseudo-version timestamps were forged to appear years older than the actual malicious push. Delivered payloads include InvisibleFerret/DEV#POPPER RAT and the OmniStealer Python infostealer, and the article links a PolinRider crossover into a compromised Packagist/PHP package (roberts/leads) via shared C2 infrastructure.
opensourcemalware.comwriteupAdded 3 Sep 2026, published 31 Jul 2026🛡️ Security Compromised npm Packages: @joyfill/components and @joyfill/layouts Ship an Obfuscated Remote Access Trojan
StepSecurity dissects malicious beta versions of @joyfill/components and @joyfill/layouts published to npm on July 28, 2026, which inject a five-stage obfuscated payload that executes on import rather than via a postinstall hook, so npm install --ignore-scripts does not stop it. The chain resolves its C2 server by reading a transaction on the Tron blockchain (with Aptos as fallback), decrypts a BNB Smart Chain transaction to find the next stage, and deploys a Socket.IO remote access trojan with worm-like self-propagation that patches the global npm CLI, VS Code/Cursor's @vscode/deviceid module, Discord desktop, and GitHub Desktop, plus a Python credential stealer targeting browser data, wallets, and Git/GitHub tokens. The writeup includes fully deobfuscated source code, IOCs (C2 IPs, Tron addresses, file hashes), and results from detonating the packages under Harden-Runner in a sandbox.
stepsecurity.iowriteupAdded 3 Sep 2026, published 30 Jul 2026🛡️ Security ChainVeil and ViteVenom are DPRK’s PolinRider Campaign
OpenSourceMalware analyzes Checkmarx Zero's ChainVeil (nine malicious npm packages using a 77KB RAT and a TRON/Aptos/BSC blockchain C2 channel) and ViteVenom (seven Vite-ecosystem typosquats) reports, and shows five values -- two TRON wallets, one Aptos address, and two XOR decryption keys -- are byte-for-byte identical to infrastructure they published in March for the DPRK/Lazarus Group campaign PolinRider, predating Checkmarx's report by over 70 days. They conclude ChainVeil/ViteVenom (maintainer "successkeyteck"/SuccessKey) are PolinRider running directly against npm and Vite, and list the full chronological table of typosquatted packages, versions, and maintainers.
opensourcemalware.comwriteupAdded 3 Sep 2026, published 17 Jul 2026🛡️ Security M-Red-Team: AsyncAPI Supply Chain Compromise via GitHub Actions
Wiz Research details how an attacker used 37 decoy pull requests to mask exploitation of a pull_request_target "pwn request" misconfiguration in the asyncapi/generator GitHub Actions workflow, stealing a privileged PAT belonging to the asyncapi-bot service account. The attacker then published four malicious npm packages (five versions) under the @asyncapi namespace with over 3 million weekly downloads, delivering a self-identified "M-RED-TEAM v6.4" multi-stage payload that fetches an 8.25MB encrypted bundle from IPFS and installs a 92,000-line trojan framework with systemd persistence and HTTP/Nostr/Ethereum/libp2p C2 channels, targeting browser credentials, SSH keys, npm/GitHub tokens, AWS credentials, and crypto wallets. The piece also analyzes partial technical overlap with the Miasma malware framework and the unrelated prt-scan campaign without making definitive attribution.
wiz.iowriteupAdded 3 Sep 2026, published 14 Jul 2026🛡️ Security AsyncAPI npm packages backdoored via GitHub Actions
Aikido Security details how five @asyncapi npm packages (specs, generator, generator-helpers, generator-components), combined ~2.9M weekly downloads, were backdoored after an attacker exploited an unmerged pull_request_target GitHub Actions vulnerability in asyncapi/generator to steal the npm publish token via 37 flooded PRs. The injected runtime code spawns a detached Node process that downloads an encrypted stage-2 loader from IPFS, decrypts it via HKDF/AES-256-GCM, and drops a persistent remote-shell implant self-identified as 'M-RED-TEAM v6.4' with Miasma-branded artifacts, though credential harvesting and self-propagation are disabled in this build. The post includes full technical detail on the exfiltration flow, IOC strings, IPFS CIDs, and inconclusive attribution linking it to the prior Miasma toolkit and prt-scan campaign.
 aikido.devwriteupAdded 3 Sep 2026, published 14 Jul 2026🛡️ Security
 Cybersecurity Startup Publishes Infostealers to NPM
A security research team traces six typosquatted npm packages (anthropic-toolkit, ai-sdk-helpers, ollama-helpers, openai-agents-helpers, @langgraphjs/toolkit, and @aspect-security/argon2) impersonating Anthropic, Vercel, Ollama, OpenAI, LangChain, and Aspect Security back to the founder of a stealth-mode cybersecurity startup. The packages use npm preinstall/postinstall hooks to silently exfiltrate a rich identity fingerprint — hostname, git/GitHub emails, SSH key comments, reflog committer emails, AWS/GCP config metadata, corporate DNS domain, and host project name — to a Google Cloud Run endpoint, while deliberately avoiding literal credentials to look benign and offering a fake telemetry opt-out. The writeup also documents version backfilling to fake package maturity and shows the payload evolving from a crude April beacon to a polished June "identity graph" collector, with full IOCs provided.
opensourcemalware.comwriteupAdded 3 Sep 2026, published 9 Jul 2026🛡️ Security Mass npm Supply Chain Attack: 20 Leo Platform Packages Compromised
StepSecurity documents a June 24, 2026 attack that published malicious versions of 20 Leo Platform npm packages (including leo-logger and leo-sdk) within a 3-second window, using the same "Phantom Gyp" binding.gyp install-hook technique, three-layer obfuscation chain, and Bun runtime evasion seen in the earlier Miasma campaign (57 packages, June 3, 2026). The payload steals GitHub Actions runner memory, cloud/registry/password-manager credentials, exfiltrates via GitHub dead-drop commits using the victim's own token, self-propagates by publishing to any package the victim can access via the npm bypass_2fa mechanism, and escalates privileges via passwordless sudo on runners. The post includes IOCs and maps defenses (Harden-Runner, Secure Registry cooldowns, PR-based compromised-package checks) to each stage of the attack.
stepsecurity.iowriteupAdded 3 Sep 2026, published 1 Jul 2026🛡️ Security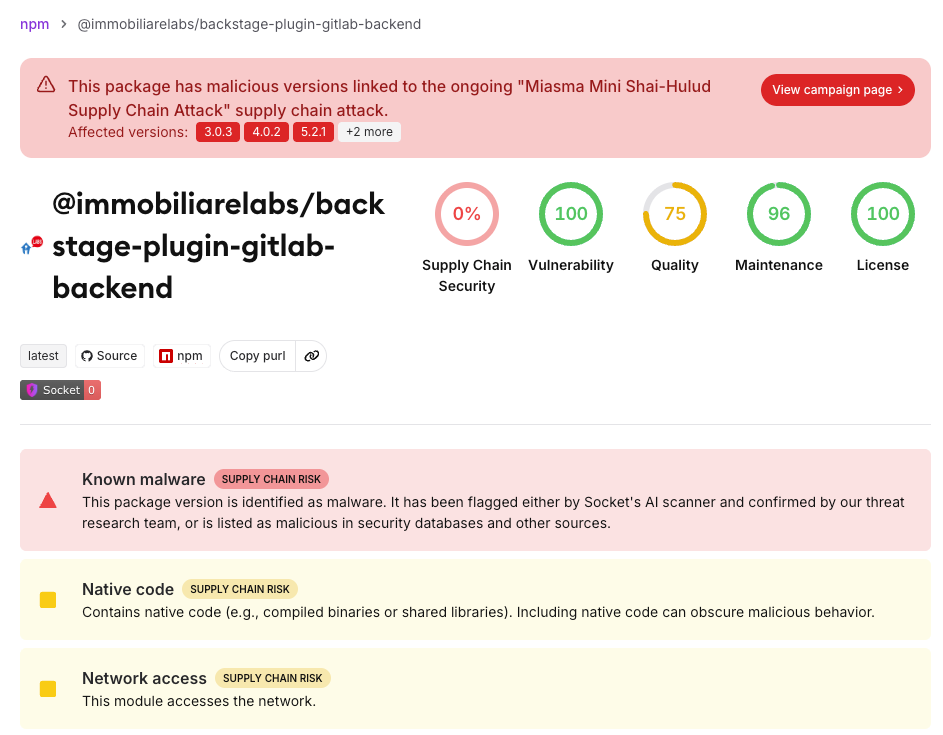 Socket: Miasma Mini Shai-Hulud Hits ImmobiliareLabs npm Packages
Socket Threat Research documents a new wave of the Miasma Mini Shai-Hulud npm supply-chain campaign compromising @immobiliarelabs Backstage plugins for GitLab integration and LDAP authentication, published on June 26, 2026. The malicious tarballs (e.g. @immobiliarelabs/backstage-plugin-gitlab@7.0.2) add a hidden root-level index.js triggered via the "Phantom Gyp" node-gyp binding.gyp trick, which decrypts an AES-128-GCM payload, bootstraps Bun, and steals npm/GitHub/cloud/SSH/CI-CD secrets while planting GitHub Actions and AI-IDE persistence. The report also traces a plausible root cause to the earlier compromise of codfish/semantic-release-action (tag-hijacking reported by StepSecurity) and highlights abuse of GitHub's deployment event trigger — a technique flagged by researcher Adnan Khan — to run attacker workflows without touching protected workflow files.
socket.devwriteupPublished and added 27 Jun 2026🛡️ Security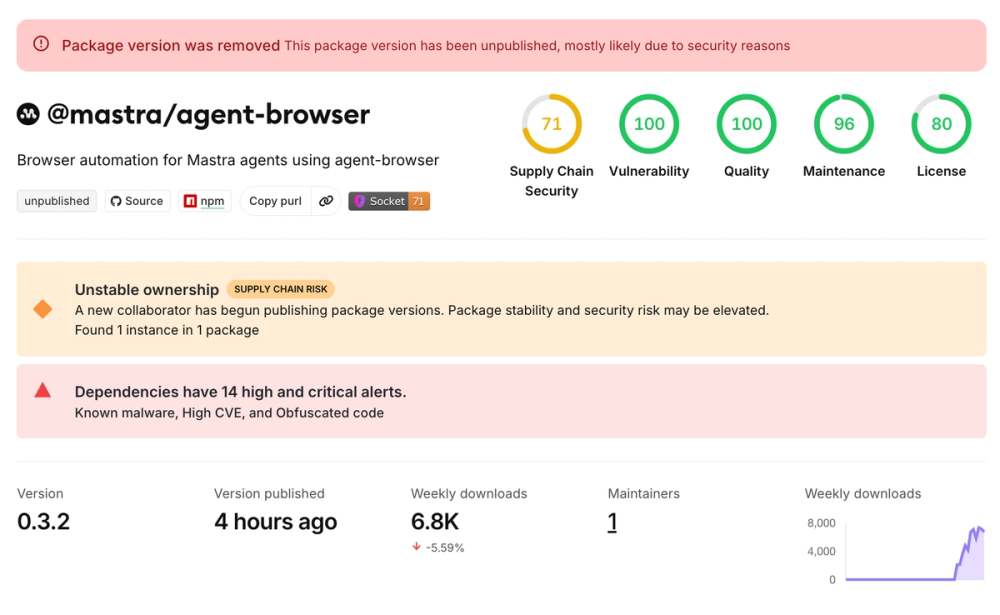 Socket: 141 Mastra npm Packages Compromised via Typosquatted Dependency
Socket's research team documents a supply chain attack in which npm account "ehindero" mass-published 141 malicious versions of @mastra/* packages (including @mastra/core, 918K weekly downloads) that were byte-identical to legitimate code but added a single new dependency: the typosquatted package easy-day-js. That package's postinstall hook (setup.cjs) disables TLS validation, fetches a second-stage cross-platform Node.js implant (protocal.cjs) that installs OS-specific persistence (Windows Run key, macOS LaunchAgent, Linux systemd unit disguised as Node/NVM tooling), inventories 166 cryptocurrency wallet browser extensions, steals Chrome/Edge/Brave history, and accepts arbitrary remote tasking (Node/Shell runners) from a hardcoded C2 over a custom ICAP-style protocol. The writeup includes full IOCs, SHA-256 hashes, and remediation guidance (rotate npm/CI/SSH credentials, treat affected hosts as compromised, disable install scripts).
socket.devwriteupPublished and added 20 Jun 2026🛡️ Security Over 140 popular Mastra npm Packages Hit by Supply Chain Attack
Aikido details a supply chain attack in which an attacker took over the entire @mastra npm scope, republishing 141 packages (including @mastra/core with 918K weekly downloads) to add a malicious dependency, easy-day-js, a dayjs clone. A staged clean-then-malicious version (1.11.21 → 1.11.22) exploited npm's caret resolution so the postinstall script setup.cjs fetched a second-stage payload from a C2 server, spawned it as a detached background process targeting 160+ browser crypto wallet extensions, and self-deleted to erase forensic evidence. Aikido notes the attack closely mirrors the earlier axios compromise (same Hostwinds infrastructure pattern, decoy-then-malicious staging, postinstall hook, self-deletion).
aikido.devwriteupAdded 3 Sep 2026, published 17 Jun 2026🛡️ Security Multiple redhat-cloud-services npm Packages compromised
StepSecurity's analysis of a supply-chain compromise affecting multiple @redhat-cloud-services npm packages, where malicious versions were published to the npm registry. The writeup details which packages/versions were affected and the indicators of compromise, helping downstream consumers assess exposure.
stepsecurity.iowriteupAdded 3 Sep 2026, published 2 Jun 2026🛡️ Security Nx Console VS Code Extension Compromised
StepSecurity's technical teardown of the May 2026 compromise of the Nx Console VS Code extension (nrwl.angular-console v18.95.0, 2.2M+ installs), where a stolen contributor GitHub token was used to push a dangling orphan commit to nrwl/nx and publish a malicious extension via stolen VSCE_PAT credentials. The payload silently ran `npx github:nrwl/nx#<sha>` to fetch a heavily obfuscated 498KB Bun/Node credential stealer that harvests secrets from GitHub, npm, AWS, Vault, Kubernetes, 1Password and Claude Code config, exfiltrates via HTTPS/GitHub API/DNS tunneling, installs a macOS Python backdoor using the GitHub Search API as a C2 dead-drop, and can forge valid Sigstore/SLSA provenance attestations for downstream npm packages. The writeup ties this to a later GitHub breach (3,800 repos, attributed to TeamPCP) and provides detection signals, IOCs, and full recovery steps.
stepsecurity.iowriteupAdded 3 Sep 2026, published 2 Jun 2026🛡️ Security Red Hat npm Packages Compromised to Spread a Credential-Stealing Worm
Aikido details a June 2026 compromise of 96 versions across 32 @redhat-cloud-services npm packages (116,991 weekly downloads) with "Miasma," a new variant of the TeamPCP-authored Mini Shai-Hulud credential-stealing worm whose source was open-sourced in May 2026. Attackers compromised a Red Hat employee's GitHub account to push malicious orphan commits containing a GitHub Actions workflow that abused OIDC id-token: write permissions to authenticate to npm's trusted publishing endpoint and republish backdoored packages; each package's preinstall script then ran a 4.2MB obfuscated payload that swept GitHub Actions, AWS, GCP, Azure, Vault, Kubernetes, npm/PyPI, SSH, Docker, GPG, and .env credentials. The piece also lays out the broader Mini Shai-Hulud campaign timeline (Bitwarden CLI, SAP, PyTorch Lightning, Mistral/TanStack, Microsoft DurableTask) and full IOC package/version list.
aikido.devwriteupAdded 3 Sep 2026, published 1 Jun 2026🛡️ Security Miasma: Supply Chain Attack Targeting RedHat npm Packages
Test summary.
wiz.iowriteupAdded 3 Sep 2026, published 1 Jun 2026🛡️ Security Miasma supply chain attack: malicious code found in @redhat-cloud-services npm packages
Snyk researchers discovered malicious code injected into several @redhat-cloud-services npm packages, dubbed the "Miasma" supply chain attack. The malicious payload was designed to harvest sensitive data or execute unauthorized code when the compromised packages were installed, illustrating how trusted-looking scoped npm packages tied to a major vendor namespace can be weaponized.
 snyk.iowriteupAdded 3 Sep 2026, published 1 Jun 2026🛡️ Security
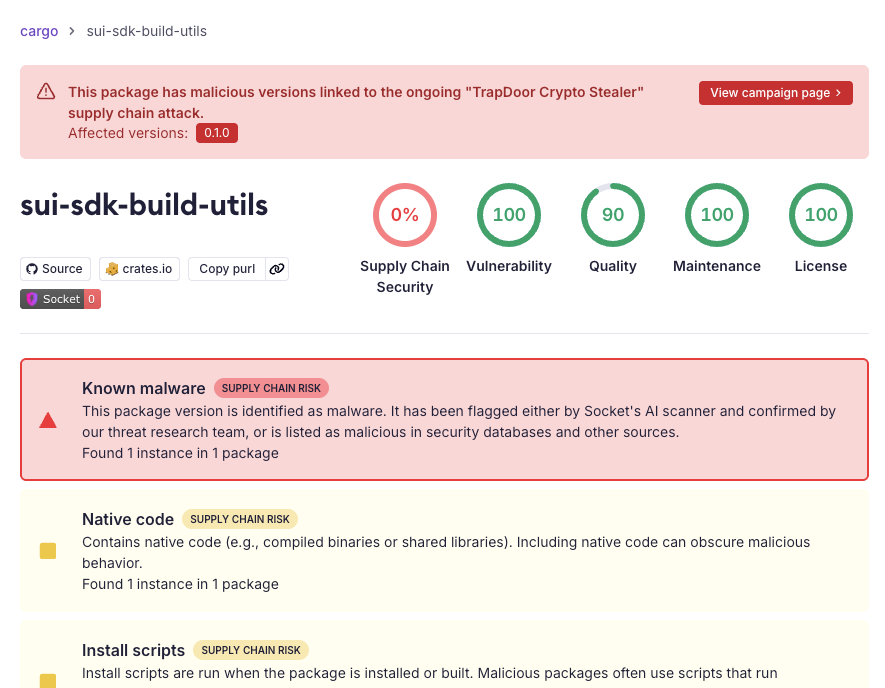 Socket: TrapDoor Crypto Stealer
Socket researchers uncovered TrapDoor, a coordinated crypto-stealer campaign spanning 34+ malicious packages and 384+ versions across npm, PyPI, and Crates.io, targeting crypto, DeFi, Sui/Move, and AI developer communities. The npm packages use postinstall hooks to run a shared trap-core.js payload that harvests SSH keys, AWS/GitHub credentials, wallet data, and browser data, then persists via .cursorrules, CLAUDE.md, git/shell hooks, systemd, cron, and SSH lateral movement; PyPI packages fetch and run remote JS on import, and Crates.io packages use malicious build.rs to XOR-encrypt and exfiltrate Sui/Move keystores to GitHub Gists. The attacker (GitHub account ddjidd564) also opened PRs against major AI/dev tooling repos (browser-use, LangChain, Langflow, llama_index, MetaGPT, OpenHands) attempting to plant hidden .cursorrules/CLAUDE.md instructions designed to trick AI coding assistants into running exfiltration under the guise of a 'security scan'.
socket.devwriteupPublished and added 26 May 2026🛡️ Security Socket: TanStack npm Packages Compromised
Socket's Threat Research team found 84 compromised @tanstack npm package artifacts (including @tanstack/react-router, 12M+ weekly downloads) injected with an obfuscated router_init.js credential-stealing payload targeting GitHub Actions CI secrets and OIDC tokens. The attack chained a pull_request_target "Pwn Request" pattern, GitHub Actions cache poisoning across the fork-to-base trust boundary, and runtime OIDC token extraction, allowing attacker publishes via TanStack's legitimate trusted-publisher OIDC binding without stealing npm tokens. Socket ties it to the ongoing Mini Shai-Hulud campaign, attributed to a likely-compromised GitHub account, and provides hashes, IOCs (filev2.getsession[.]org), and hardening/remediation steps.
socket.devwriteupPublished and added 20 May 2026🛡️ Security Microsoft's durabletask package on PyPi Compromised. Mini Shai Hulud attacks again... again!
Aikido Security reports that Microsoft's durabletask package on PyPI was compromised in a new "mini" wave of the Shai Hulud self-propagating supply-chain worm, which previously hit npm packages and spreads by stealing credentials and republishing malicious versions of dependencies. The post covers indicators of compromise, the malicious payload behavior, and which packages/versions are affected.
aikido.devwriteupAdded 3 Sep 2026, published 19 May 2026🛡️ Security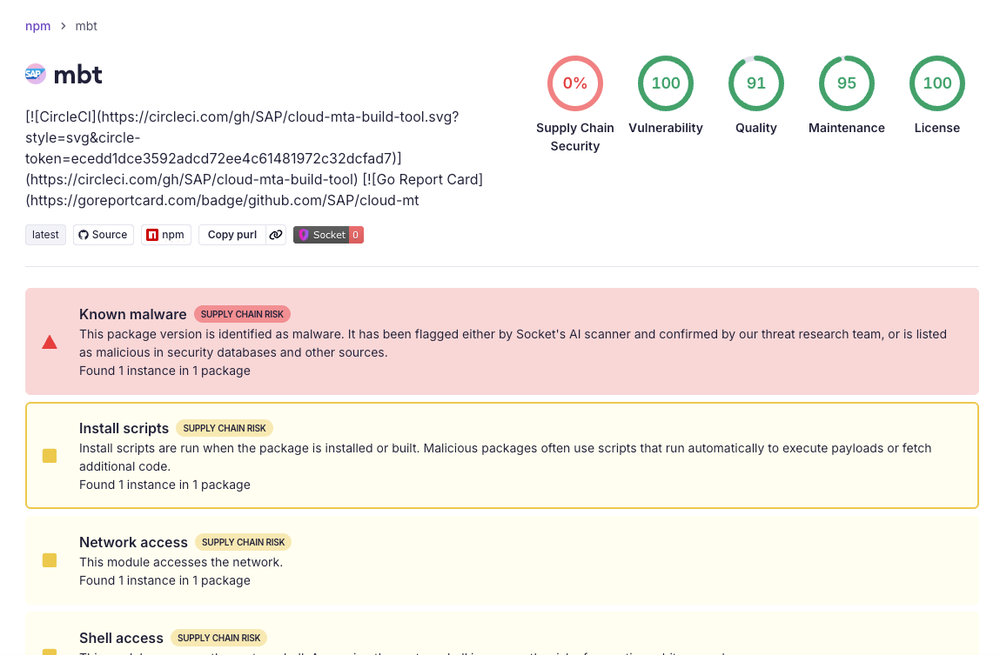 TeamPCP SAP CAP Attack
Socket documents a TeamPCP-linked supply chain attack compromising four SAP-affiliated npm packages (mbt, @cap-js/sqlite, @cap-js/db-service, @cap-js/postgres) via a malicious preinstall script that downloads and runs Bun to execute an 11.7MB obfuscated payload. The payload steals SSH keys, cloud/K8s/npm/GitHub credentials, AI tool configs, and crypto wallets, scrapes secrets from CI runner memory bypassing log masking, exfiltrates via attacker-created GitHub repos, self-propagates by publishing trojanized versions of hardcoded SAP CAP dependencies, and persists via Claude Code and VSCode hooks. Socket attributes the campaign with medium confidence to TeamPCP based on shared __decodeScrambled cipher, Russian-locale kill switch, and GitHub-as-C2 patterns previously seen in Checkmarx, Bitwarden CLI, and Trivy incidents.
socket.devwriteupPublished and added 6 May 2026🛡️ Security