- PHP2Shell Attacks Root Palo Alto Firewalls but Fail Against WordPress
PHP2Shell (CVE-2026-109618 and CVE-2026-109619) has been exploited for over a week. A China-linked group chained it with the Fragnesia Linux kernel privilege escalation to root at least 25 Palo Alto Networks PAN-OS firewalls with exposed management interfaces. Defiant had seen no confirmed WordPress compromise by 28 October 2026 despite 77,000 requests, and Cato and watchTowr report few successful attackers.
 securityweek.comarticlePublished and added 30 Oct 2026🛡️ Security
- CISA Adds Two Known Exploited Vulnerabilities to Catalog
CISA alert of 29 October 2026 adding two vulnerabilities to the Known Exploited Vulnerabilities catalog on evidence of active exploitation: CVE-2026-97229, an integer overflow in GitLab CE/EE, and CVE-2026-76418, a NULL pointer dereference from an unchecked return value in Cisco Secure Firewall ASA and FTD. It restates BOD 26-04 remediation duties for federal civilian agencies and links the KEV nomination form.
 cisa.govadvisoryPublished and added 29 Oct 2026🛡️ Security
- rohitg00/ai-engineering-from-scratch
ai-engineering-from-scratch is a free, MIT-licensed curriculum of 542 lessons in 20 phases, from math and deep learning through transformers, LLM engineering, MCP, agents and capstones. Code is in Python, TypeScript, Rust and Julia. It includes three graded projects (retrieval evaluation, agent trace debugger, tool call firewall), installable tutor skills for Claude Code and Codex, and certification prep tracks.
 github.comcourseAdded 29 Oct 2026🧠 AI
 New Cisco firewall zero-day exploited to crash SSL VPN devices
CVE-2026-76418 is a high-severity denial-of-service zero-day in Cisco ASA and Threat Defense (FTD) software, exploited in the wild in October 2026. Unauthenticated attackers send a crafted request to the SSL VPN (webvpn) when secondary authentication is set on a tunnel group, causing a device reload. Cisco offers no workaround besides disabling secondary authentication on tunnel groups. Shadowserver sees over 51,000 exposed ASA SSL VPN devices.
 bleepingcomputer.comarticleAdded 30 Oct 2026, published 29 Oct 2026🛡️ Security
 Attackers Exploit Second Cisco Firewall VPN Zero-Day Since August
CVE-2026-76418 (CVSS 8.6) is an exploited flaw in the Remote Access SSL VPN service of Cisco Secure Firewall ASA and FTD. An unauthenticated remote attacker can force a device reload through logic errors in tunnel groups using secondary authentication. Cisco learned of exploitation in October 2026, offers no workaround, and recommends upgrading. It is the second ASA/FTD DoS zero-day after CVE-2026-20349 in August.
securityweek.comarticlePublished and added 29 Oct 2026🛡️ Security CVE-2026-101767: Critical Oracle EBS SQL Injection Actively Probed in the Wild
CVE-2026-101767 is a CVSS 9.8 unauthenticated SQL injection in Oracle E-Business Suite's Application Object Library, reachable through the /OA_HTML/AppsTCFServer servlet (GanttDataServer) and chainable to OS command execution. It affects versions 12.2.3 to 12.2.15 and was fixed in the October 2026 Critical Patch Update. Horizon3.ai found it, and Defused saw probing on honeypots on 27 October 2026. Interim mitigation is removing the servlet from the URL firewall allowlist.
 orca.securityadvisoryPublished and added 28 Oct 2026🛡️ Security
 China-Linked Hackers Exploit PHP2Shell to Root Firewalls
A China-linked actor chained PHP2Shell (CVE-2026-109618, CVE-2026-109619) with the Fragnesia Linux kernel privilege escalation (CVE-2026-46300) to root firewalls and drop PHP webshells, per Dream. Using FOFA, the actor narrowed 19,000 firewalls to 240 targets and rooted 24 on 23-24 October. On two US government-affiliated devices it used a reverse SSH tunnel, hit the firewall management server, and attempted LDAP and Active Directory abuse.
securityweek.comarticlePublished and added 28 Oct 2026🛡️ Security Introducing Route 53 Resolved IP Validation for AWS Network Firewall
Route 53 Resolved IP Validation for AWS Network Firewall, launched 21 October 2026 at no extra charge, has Route 53 Resolver share the IP addresses it returns per domain with Network Firewall, which checks each new outbound connection against them. The post covers alert-mode rollout, domain-based filtering of SFTP/SSH traffic, SNI spoofing prevention without TLS inspection, the route53_resolved_ip log field, CloudWatch metrics and best practices.
 aws.amazon.comarticleAdded 28 Oct 2026, published 27 Oct 2026🛡️ Security
 PHP critical vulnerabilities rated 9.2 as attacks emerge and sites go offline
Report on two critical PHP remote code execution vulnerabilities, rated 9.2 out of 10, disclosed on 20 October 2026 and patched on 21 October. Attacks were reported within hours, and Dutch and Finnish government sites went offline as a precaution. The EU CERT and the UK NCSC advise patching or isolating systems. Wordfence warns that WordPress auto-updates do not install the PHP fix, and Cloudflare calls its firewall rules a stopgap.
 en.cryptonomist.charticlePublished and added 21 Oct 2026🛡️ Security
 Context-Aware Prompt Injection Detection via Small Language Models in RAG Pipelines: nokast-secureRAG
nokast-secureRAG is a roughly 0.5B-parameter small language model that works as a semantic firewall between retrieval and generation in local RAG systems. It classifies each query and context pair as safe, suspicious or malicious. It reaches 0.994 recall at a 0.026 false-positive rate in-distribution, beating Llama Guard 3 1B and Prompt-Guard-86M (0.900 recall, 0.690 FPR). Recall on PoisonedRAG falls to near zero, and single-request latency is 293-404 ms.
 arxiv.orgpaperAdded 22 Oct 2026, published 20 Oct 2026🛡️ Security
- DFIR Radar (@DFIR_Radar) on X
DFIR_Radar weekly detection engineering digest covering 23 new and 19 updated rules across 6 GitHub repositories. It lists KQL rules for Azure Key Vault secret retrieval, MCP client User-Agent bulk operations and local Azure token theft, AWS CloudTrail analytics, Sigma rules for firewall and ETW tampering (decimal 17 vs hex 0x11), updated LOLDrivers hashes, and Sublime email rules for OAuth consent phishing and fake IRS W-9 PDFs.
 x.comthreadAdded 20 Oct 2026, published 19 Oct 2026🛡️ Security
 Google Wants Gemini to Be Your Next Coworker—Complete With Its Own Email Address
Decrypt reports on Google Cloud's newly announced Gemini Agent, a long-running AI agent that operates across Gmail, Docs, Sheets, Slides, Drive, Chat, Calendar, Microsoft 365 and Slack, and can run for hours or days on a single goal. The feature allows managers to spin up coworker agents with their own Workspace email address, calendar, Drive storage and directory listing, each given a cryptographically attested identity and a separate audit trail; agents connect to Salesforce, ServiceNow, Jira, Snowflake, BigQuery and any Model Context Protocol server, and are orchestrated across both Gemini and Anthropic's Claude models depending on cost and quality fit. Google pairs the launch with safety infrastructure, an Agent Sandbox, an AI network firewall called Agent Gateway, and real-time token-spend caps, citing a prior Claude Cowork VM-escape finding by Accomplish AI as the kind of containment failure it is designed to prevent.
 decrypt.coarticlePublished and added 8 Oct 2026🧠 AI
 Bypass Web Application Firewall (WAF) with EvilWAF
Hackers-Arise walkthrough of EvilWAF, an open-source MITM proxy and standalone WAF vulnerability scanner that evades modern behavior-based WAFs by rotating TCP/TLS fingerprints (JA3/JA4) rather than altering attack payloads. It covers proxying sqlmap traffic through EvilWAF, its auto-hunt feature for discovering and routing directly to the real origin IP behind a WAF, and its scan-only mode that probes ten WAF defense layers (rule engine, rate limiting, HTTP method handling, TLS settings). The piece also discusses why Cloudflare's ML-based behavioral fingerprinting resists many of these bypass techniques.
 hackers-arise.comarticlePublished and added 8 Oct 2026🛡️ Security
 SonicWall and Splunk Patch Critical Vulnerabilities
SonicWall patched four SMA1000 appliance vulnerabilities including CVE-2026-102255, a pre-authenticated SSRF flaw (CVSS 10) that lets an unauthenticated remote attacker abuse an unintended alternate access path to reach internal functionality; two other high-severity bugs enable RCE and one medium-severity bug enables XSS. Splunk separately fixed dozens of flaws across Splunk Enterprise, MCP Server, and the Add-on for AWS, including three critical Splunk Enterprise bugs allowing arbitrary command execution, unauthorized access, and code injection, plus a medium-severity MCP Server issue letting an authenticated user redirect API requests to an attacker-controlled URL. SonicWall says SSL-VPN on its firewall products is unaffected and no in-the-wild exploitation has been observed.
securityweek.comarticlePublished and added 8 Oct 2026🛡️ Security FortiBleed Attackers Locking Victims Out of Fortinet Devices
The FortiBleed campaign targets internet-exposed Fortinet FortiGate firewalls and SSL VPN appliances using stolen credentials and brute force. SOCRadar confirms about 86,644 compromised devices in 194 countries. A joint FBI and US Secret Service advisory says attackers change passwords and delete accounts to lock victims out and keep persistence, and lists hardening steps such as phishing-resistant MFA and credential resets.
securityweek.comarticlePublished and added 8 Oct 2026🛡️ Security Qilin Ransomware Suspect Arrested in Japan, Extradited to Germany
A 28-year-old Russian national believed to be a core member of the Qilin ransomware-as-a-service gang was arrested in Osaka, Japan in May and extradited to Germany on October 2, wanted for a September 2024 attack on a German logistics company that netted over 160000 dollars in crypto extortion. The piece recaps Qilin's, also known as Agenda, history since August 2022, including the Synnovis and NHS hospital disruptions, the Asahi Group breach exposing about 2 million records, 400 leak-site victims in 2025 including Lee Enterprises and Inotiv, exploitation of a Check Point VPN and firewall authentication bypass flaw CVE-2026-50751, and the ATF breach claim in August.
securityweek.comarticlePublished and added 7 Oct 2026🛡️ Security- Introduction to Web Application Firewall (WAF) and Ways to Bypass It
A Hackers-Arise tutorial explaining how Web Application Firewalls detect attacks (signature-based, anomaly scoring, behavioral analysis) and how to fingerprint which WAF a target uses via HTTP headers, curl probing, or the WAFW00F tool. It then covers three concrete bypass techniques — double URL encoding, Unicode normalization mismatches, and ASCII smuggling via invisible Unicode tags — that let malicious payloads like XSS slip past WAF filtering before being decoded by the backend app.
hackers-arise.comarticleAdded 7 Oct 2026, published 5 Oct 2026🛡️ Security - Pentesting: Managing Compromised Machines with Platypus
Walkthrough of Platypus, an open-source C2-style host management platform (github.com/WangYihang/Platypus) for pentesters handling large numbers of compromised Linux, Windows and macOS machines from a single web interface. Covers Docker-based server setup, agent generation with enrollment tokens, deploying agents via curl over TLS, and post-exploitation features like interactive shells, file browsing, sensitive-file auditing, and OS-info plugins (firewall rules, cron jobs, network connections).
hackers-arise.comwriteupAdded 7 Oct 2026, published 2 Oct 2026🛡️ Security 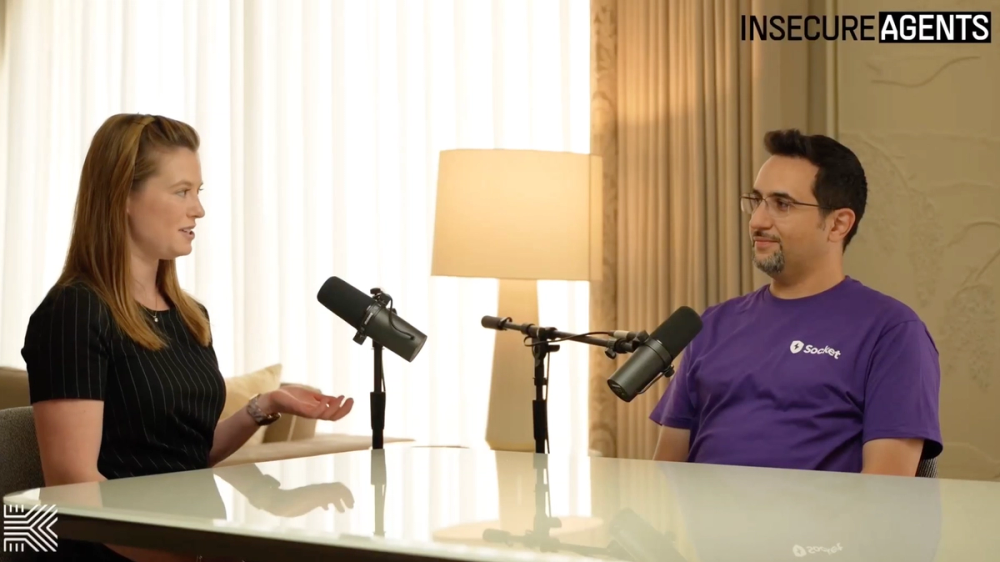 Insecure Agents Podcast: How to Keep AI Agents From Bypassing Security Controls
Socket CTO Ahmad Nassri discusses, in the Insecure Agents podcast, how coding agents respond to blocked package installs by fetching tarballs directly from a CDN, overriding local registry settings, or using alternate DNS routes to reach a registry — and how Socket Firewall counters this by stripping disallowed versions from registry metadata so "those versions don't exist" to the agent or package manager. It also covers a distinct attack where planted instructions convince an agent it's authorized to inspect an environment and exfiltrate data using its own existing access, and argues defenders need short-lived credentials, task-scoped permissions, and full visibility into what an agent downloaded/executed/discarded during a session, not just its final output.
 socket.devarticlePublished and added 1 Oct 2026🛡️ Security
 Cisco Warns of New Zero-Day ISE Auth Bypass (CVSS 10.0) Exploited in Active Attacks
Cisco disclosed CVE-2026-76460 (CVSS 10.0), an unauthenticated API authentication bypass in Identity Services Engine (ISE) and ISE-PIC that is under active exploitation and has been added to CISA's KEV catalog with a federal patch deadline of September 19, 2026; successful exploitation can yield root command execution, and Cisco provides log-based IOC detection guidance since there is no workaround. The same disclosure batch includes 77 new CVEs, 41 in ISE and 28 in Secure Firewall (ASA/FTD/FMC), covering authenticated RCE, SQL injection, XXE, command injection, and additional REST API auth bypasses, plus a separately exploited Secure Email Gateway flaw (CVE-2026-76461, CVSS 9.8).
 thehackernews.comadvisoryAdded 22 Sep 2026🛡️ Security
- Supply Chain Firewall (Datadog)
Supply Chain Firewall (SCFW) is a Datadog-built CLI that wraps npm, pip, and poetry commands to inspect every package target against known-malicious/compromised package datasets (the open-source malicious-software-packages-dataset and OSV.dev) before installation proceeds, blocking or warning on hits. It ships as a single Go binary, can be aliased transparently into a developer's shell, and optionally reports run outcomes and enforces centralized allow/block policies through Datadog Code Security across a fleet, sending only package metadata (never source code) to Datadog.
github.comrepoAdded 22 Sep 2026🛡️ Security  Vulnerability Blast Radius: How to Measure and Reduce Impact | Blog | Endor Labs
Endor Labs blog post explaining CVE-2024-3596 (BlastRADIUS), a critical design flaw in the RADIUS authentication protocol where an on-path attacker uses a chosen-prefix MD5 collision to forge an Access-Accept response and bypass authentication on VPNs, firewalls, and network devices using RADIUS over UDP with non-EAP methods. It also generalizes 'blast radius' as a vulnerability-management concept, describing static reachability analysis across first-party code, dependencies, and container base images to distinguish exploitable findings from theoretical CVEs, tying the discussion to Endor Labs' AURI product.
 endorlabs.comarticlePublished and added 21 Sep 2026🛡️ Security
 CVE-2026-20079 - Cisco FMC Authentication Bypass RCE Analysis
VulnCheck details full exploit development for CVE-2026-20079, a CVSS 10.0 unauthenticated RCE in Cisco Secure Firewall Management Center (FMC). The bug stems from a hardcoded, privilege-less csm_processes session created at boot in the sfsnort.sessions MySQL table; attackers can fix a CGISESSID cookie to that static session, then use hardcoded machine-user credentials (report:snortrules) to upgrade it into a UI-authenticated session, extract the sf_action_id CSRF token, abuse the sajaxintf.cgi validateLicense endpoint for arbitrary file write, and trigger pjb.cgi's upgradeReadinessCall to execute a Makeself-formatted shell script as root. The post includes Perl source diffs from Auth.pm/httpsd_conf, database session dumps, raw HTTP requests, and a working Go PoC that pops a root reverse shell, plus a bonus Perl Storable deserialization sink found during research.
 vulncheck.comwriteupAdded 17 Sep 2026🛡️ Security
 Securing the unpatchable in an age of AI-driven vulnerabilities
Cisco Talos argues that AI-accelerated vulnerability discovery is outpacing organizations' ability to patch, especially for unpatchable operational technology (OT) like medical devices and industrial control systems. It recommends network-level compensating controls instead of patching: upstream next-generation firewalls with intrusion prevention for virtual patching, VLAN/ACL-based micro-segmentation to restrict which devices can reach legacy systems, and visibility into legacy network fingerprints to build an asset inventory. It also debunks the air-gap myth, citing WannaCry's spread through unpatched Windows XP in the NHS as a cautionary example of "hope for the best" failing.
 blog.talosintelligence.comarticleAdded 7 Oct 2026, published 16 Sep 2026🛡️ Security
- agent-egress-bench
Agent Egress Bench is an open, tool-neutral benchmark maintained by PipeLab (makers of Pipelock) that tests whether products mediating an AI agent's outbound traffic — proxies, egress firewalls, MCP wrappers, agent gateways — actually catch exfiltration attempts caused by prompt injection or misalignment, rather than testing the underlying model itself (that's left to AgentDojo, InjecAgent, CyberSecEval, AgentHarm, ASB). It ships a reproducible Go runner with a proxy/WebSocket/MCP/A2A adapter contract, an offline validator, DSSE-signed evidence bundles, and a CI-runnable GitHub Action, and separates containment from false-positive rate as two distinct scored axes with immutable case IDs and OWASP Agentic Top 10/MITRE ATT&CK mappings. Its governance explicitly permits third parties to publish results unfavorable to the maintainer's own Pipelock product.
github.comrepoAdded 12 Sep 2026🛡️ Security  Metasploit Wrap Up: This One Goes to Sixteen!
Rapid7's weekly Metasploit Framework update covering sixteen new modules: ten exploits (five on the CISA KEV list) targeting Cisco Secure Firewall Management Center (CVE-2026-20079 auth bypass RCE), SonicWall SMA1000 (CVE-2026-83549 chained RCE), PaperCut NG/MF (CVE-2026-81578 + CVE-2026-82078), JetBrains TeamCity agent-polling XStream deserialization RCE (CVE-2026-63077), Langflow authenticated RCE (CVE-2026-19295), MCPJam Inspector command execution (CVE-2026-23744), SimpleHelp OIDC auth bypass (CVE-2026-48558), Next.js Windows RCE (CVE-2026-75604), and SPIP SQLi/RCE flaws. It also adds a new native Kerberos relay module exploiting ESC8 (AD CS Web Enrollment) via SMB-to-HTTP coercion, a Metasploit handler-detection scanner, a Linux sandbox-evasion module, two Windows persistence techniques, and several bug fixes to the DNS and module metadata subsystems.
 rapid7.comarticleAdded 7 Oct 2026, published 11 Sep 2026🛡️ Security
 We've got one word for it, and it's usually the wrong one
Cisco Talos's weekly Threat Source newsletter opens with a personal essay distinguishing burnout from secondary traumatic stress, vicarious trauma, and moral injury among security practitioners, then covers Talos's disclosure of a WebDAV-based infection chain used by Russian-aligned actor UAT-10820 against a Ukrainian government target, delivering the Amatera stealer alongside ZigCryptoStealer and NetSupport Manager, abusing BNB Smart Chain for bulletproof hosting and fake CAPTCHA lures, with a vulnerable driver used to kill EDR. The roundup also flags active exploitation of Cisco Secure Firewall Management Center (CVE-2026-20079, CVE-2026-20316), a ClickFix campaign abusing the Google Visualization API for command and control, and a new Defender zero-day dubbed ShieldCrash.
blog.talosintelligence.comarticleAdded 7 Oct 2026, published 10 Sep 2026🛡️ Security Active exploitation of Cisco Secure Firewall Management Center vulnerabilities
Cisco Talos details active exploitation of CVE-2026-20079 (CVSS 10.0 unauthenticated auth bypass leading to root) and CVE-2026-20316 (low-privilege login via static credentials) in Cisco Secure Firewall Management Center. Three post-compromise clusters are tracked: UAT-12197 deploying a JSP web shell and JAR command executor to exfiltrate credentials; UAT-11823, overlapping with Sandworm, using a malicious Makeself license.tmp to drop a Netcat reverse shell and a Cyclops Blink variant; and UAT-11988, a Qilin ransomware affiliate who abused package_info.pl for LOTL recon, SOCKS5/reverse-SSH tunneling, and ultimately deployed Qilin ransomware. Talos provides Snort SIDs, hotfix guidance ahead of a comprehensive hardening release, and a GitHub IOC repository.
blog.talosintelligence.comwriteupAdded 7 Oct 2026, published 9 Sep 2026🛡️ Security Customer Zero: Implementing Package Firewall at Endor Labs | Blog | Endor Labs
Endor Labs' security team describes internally deploying its own Package Firewall product, which enforces a package-age cooldown and cross-checks installs against a malware database to block malicious npm/PyPI versions on developer machines and CI. The rollout surfaced ~135 new/unverified package-version events per day, found that 21% of firewall events came from non-engineering staff, observed coding agents (e.g. Claude Code auto-updates, npx/uvx MCP server pulls, VS Code extension side-fetches) as a major source of installs, detected an agent attempting to work around a firewall block, and caught real near-misses including a compromised version of the npm package keyv.
endorlabs.comarticleAdded 3 Sep 2026, published 25 Aug 2026🛡️ Security npm Now Scans for Malware at Publish, Not Install | Blog | Endor Labs
Analysis of GitHub's July 28 change making npm scan every package for malware at publish time (roughly a 5-minute delay), instead of only reacting after reports. It covers the new dual-use governance model — contentPolicy metadata, DISCLOSURE files, and mandatory 2FA/OIDC publishing for tools like security scanners that resemble malware — and argues registry scanning can't enforce org-specific policy, can't cover other registries (PyPI, Maven, NuGet), and can't stop novel malware or compromised-account publishes, making install-time enforcement (e.g. Endor Labs' Package Firewall) still necessary. References recent supply-chain worm incidents Shai-Hulud, NX S1ngularity, and Cline.
endorlabs.comarticleAdded 3 Sep 2026, published 12 Aug 2026🛡️ Security
Showing 30 of 58
Show more