Black Hat USA 2022
100 videos enrolled
Listing is free. Every video appears the moment it is found. Analysed videos open their catalog entry; the rest link to YouTube and join the catalog as the metered pass drains this source (policy recent).
 Leveraging the Apple ESF for Behavioral Detections
 Let's Dance in the Cache - Destabilizing Hash Table on Microsoft IIS
 Kubernetes Privilege Escalation: Container Escape == Cluster Admin?
 Is WebAssembly Really Safe? -- Wasm VM Escape and RCE Vulnerabilities Have Been Found in New Way
 Invisible Finger: Practical Electromagnetic Interference Attack on Touchscreen-based Devices
 Internal Server Error: Exploiting Inter-Process Communication in SAP's HTTP Server
 Industroyer2: Sandworm's Cyberwarfare Targets Ukraine's Power Grid Again
 In Need of 'Pair' Review: Vulnerable Code Contributions by GitHub Copilot
 IAM The One Who Knocks
 I Am Whoever I Say I Am: Infiltrating Identity Providers Using a 0Click Exploit
 Human or Not: Can You Really Detect the Fake Voices?
 Harm Reduction: A Framework for Effective & Compassionate Security Guidance
 Backdooring and Hijacking Azure AD Accounts by Abusing External Identities
 Automatic Protocol Reverse Engineering
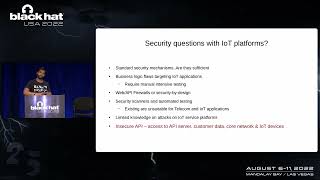 Attacks From a New Front Door in 4G & 5G Mobile Networks
 A New Trend for the Blue Team: Using a Symbolic Engine to Detect Evasive Forms of Malware/Ransomware
 The 8th Annual Black Hat USA NOC Report
 Ret2page: The Art of Exploiting Use-After-Free Vulnerabilities in the Dedicated Cache
 Monitoring Surveillance Vendors: A Deep Dive into In-the-Wild Android Full Chains in 2021
 Unlimited Results: Breaking Firmware Encryption of ESP32-V3
 Blasting Event-Driven Cornucopia: WMI-based User-Space Attacks Blind SIEMs and EDRs
 Better Privacy Through Offense: How To Build a Privacy Red Team
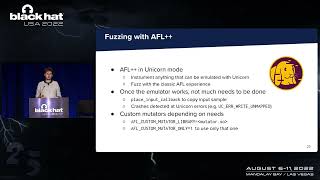 Attack on Titan M, Reloaded: Vulnerability Research on a Modern Security Chip
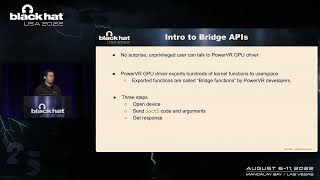 Android Universal Root: Exploiting Mobile GPU / Command Queue Drivers
 All Your GNN Models and Data Belong to Me
 Trace Me if You Can: Bypassing Linux Syscall Tracing
 AAD Joined Machines - The New Lateral Movement
 A Fully Trained Jedi, You Are Not
 (Long) Dragon Tails – Measuring Dependence on International Vulnerability Research
 "No Mr. Cyber Threat!" - A Psychological Approach To Managing the Fail-to-Challenge Vulnerability
 AEPIC Leak: Architecturally Leaking Uninitialized Data from the Microarchitecture
 A Dirty Little History: Bypassing Spectre Hardware Defenses to Leak Kernel Data
 A Journey Into Fuzzing WebAssembly Virtual Machines
 Talent Need Not Apply: Tradecraft and Objectives of Job-themed APT Social Engineering
 Stalloris: RPKI Downgrade Attack
 Return to Sender - Detecting Kernel Exploits with eBPF
 Pwning Cloud Vendors with Untraditional PostgreSQL Vulnerabilities
 Perimeter Breached! Hacking an Access Control System
 No One Is Entitled to Their Own Facts, Except in Cybersecurity?
 New Memory Forensics Techniques to Defeat Device Monitoring Malware
 The COW (Container On Windows) Who Escaped the Silo
 Oops..! I Glitched It Again! How to Multi-Glitch the Glitching-Protections on ARM TrustZone-M
 Keynote: Black Hat at 25: Where Do We Go from Here?
 Smishmash - Text Based 2fa Spoofing Using OSINT, Phishing Techniques and a Burner Phone
 Scaling the Security Researcher to Eliminate OSS Vulnerabilities Once and For All
 RollBack - A New Time-Agnostic Replay Attack Against the Automotive Remote Keyless Entry Systems
 Real 'Cyber War': Espionage, DDoS, Leaks, and Wipers in the Russian Invasion of Ukraine
 RCE-as-a-Service: Lessons Learned from 5 Years of Real-World CI/CD Pipeline Compromise
 Process Injection: Breaking All macOS Security Layers With a Single Vulnerability
 Catch Me If You Can: Deterministic Discovery of Race Conditions with Fuzzing
 CastGuard: Mitigating Type Confusion in C++
 Calculating Risk in the Era of Obscurity: Reading Between the Lines of Security Advisories
 Bug Hunters Dump User Data. Can They Keep it? Well They're Keeping it Anyway.
 Bug Bounty Evolution: Not Your Grandson's Bug Bounty
 Malware Classification With Machine Learning Enhanced by Windows Kernel Emulation
 Locknote: Conclusions and Key Takeaways from Black Hat USA 2022
 Whip the Whisperer: Simulating Side Channel Leakage
 UWB Real Time Locating Systems: How Secure Radio Communications May Fail in Practice
 Trust Dies in Darkness: Shedding Light on Samsung's TrustZone Keymaster Design
 To Flexibly Tame Kernel Execution With Onsite Analysis
 The Open Threat Hunting Framework: Enabling Organizations to Build, Operationalize, and Scale Threat
 The Journey of Hunting In-the-Wild Windows LPE 0day
 The Growth of Global Election Disinformation: The Role Methodology of Government-linked Cyber Actors
 Browser-Powered Desync Attacks: A New Frontier in HTTP Request Smuggling
 BrokenMesh: New Attack Surfaces of Bluetooth Mesh
 Breaking the Chrome Sandbox with Mojo
 Breaking Firmware Trust From Pre-EFI: Exploiting Early Boot Phases
 Living Off the Walled Garden: Abusing the Features of the Early Launch Antimalware Ecosystem
 XMPP Stanza Smuggling or How I Hacked Zoom
 Pre-Stuxnet, Post-Stuxnet: Everything Has Changed, Nothing Has Changed
 DirectX: The New Hyper-V Attack Surface
 How Supercomputer-scale Neural Network Models Apply to Defensive Cybersecurity Problems
 Go With the Flow: Enforcing Program Behavior Through Syscall Sequences and Origins
 sOfT7: Revealing the Secrets of Siemens S7 PLCs
 Glitched on Earth by Humans: A Black-Box Security Evaluation of the SpaceX Starlink User Terminal
 From Hackathon to Hacked: Web3's Security Journey
 Ghost in the Wireless, iwlwifi Edition
 Eliminating Triage Intermediaries for Zero-day Exploits Using a Decentralised Payout Protocol
 ELF Section Docking: Revisiting Stageless Payload Delivery
 Elevating Kerberos to the Next Level
 ElectroVolt: Pwning Popular Desktop Apps While Uncovering New Attack Surface on Electron
 How Firefox Uses In-process Sandboxing To Protect Itself From Exploitable Libraries
 Do Not Trust the ASA, Trojans!
 DNSSEC Downgrade Attacks
 Devils Are in the File Descriptors: It Is Time To Catch Them All
 Dive Into Apple IO80211Family Vol. 2
 Demystifying Key Stretching and PAKEs
 Déjà Vu: Uncovering Stolen Algorithms in Commercial Products
 Custom Processing Unit: Tracing and Patching Intel Atom Microcode
 Controlling the Source: Abusing Source Code Management Systems
 Chasing Your Tail With a Raspberry Pi
 Trying to Be Everything to Everyone: Let’s Talk About Burnout
 Charged by an Elephant – An APT Fabricating Evidence to Throw You In Jail
 TruEMU: An Extensible, Open-Source, Whole-System iOS Emulator
 Cautious: A New Exploitation Method! No Pipe but as Nasty as Dirty Pipe
 The Battle Against the Billion-Scale Internet Underground Industry: Advertising Fraud Detection
 Google Reimagined a Phone. It was Our Job to Red Team and Secure it.
 Fault-Injection Detection Circuits: Design, Calibration, Validation and Tuning
 The Cyber Safety Review Board: Studying Incidents to Drive Systemic Change
 eBPF ELFs JMPing Through the Windows