Skip to content

Black Hat USA 2016

playlist๐Ÿ›ก๏ธ Securityon YouTube โ†—part of Black Hat, found on its playlists tab

120 videos enrolled

Listing is free. Every video appears the moment it is found. Analysed videos open their catalog entry; the rest link to YouTube and join the catalog as the metered pass drains this source (policyย recent).

  1. Keynote: The Hidden Architecture of our Time: Why This Internet Worked, How We Could Lose It...Keynote: The Hidden Architecture of our Time: Why This Internet Worked, How We Could Lose It...28 Oct 20161:12:49not yet analysed
  2. When the Cops Come A-Knocking: Handling Technical Assistance Demands from Law EnforcementWhen the Cops Come A-Knocking: Handling Technical Assistance Demands from Law Enforcement28 Oct 201643:50not yet analysed
  3. Certificate Bypass: Hiding and Executing Malware from a Digitally Signed ExecutableCertificate Bypass: Hiding and Executing Malware from a Digitally Signed Executable28 Oct 201625:49not yet analysed
  4. HEIST: HTTP Encrypted Information can be Stolen Through TCP-WindowsHEIST: HTTP Encrypted Information can be Stolen Through TCP-Windows28 Oct 201649:33not yet analysed
  5. A Lightbulb Worm?A Lightbulb Worm?28 Oct 201625:54not yet analysed
  6. AirBnBeware: Short Term Rentals Long Term PwnageAirBnBeware: Short Term Rentals Long Term Pwnage28 Oct 201644:38not yet analysed
  7. HTTP Cookie Hijacking in the Wild: Security and Privacy ImplicationsHTTP Cookie Hijacking in the Wild: Security and Privacy Implications28 Oct 201646:12not yet analysed
  8. Behind the Scenes of iOS SecurityBehind the Scenes of iOS Security28 Oct 201651:32not yet analysed
  9. Panel: Removing Roadblocks to DiversityPanel: Removing Roadblocks to Diversity28 Oct 20161:40:30not yet analysed
  10. Defense at Hyperscale: Technologies and Policies for a Defensible CyberspaceDefense at Hyperscale: Technologies and Policies for a Defensible Cyberspace28 Oct 201652:24not yet analysed
  11. A Retrospective on the Use of Export CryptographyA Retrospective on the Use of Export Cryptography28 Oct 201750:47not yet analysed
  12. Abusing Bleeding Edge Web Standards for Appsec GloryAbusing Bleeding Edge Web Standards for Appsec Glory28 Oct 201743:08not yet analysed
  13. Augmenting Static Analysis Using Pintool: AblationAugmenting Static Analysis Using Pintool: Ablation28 Oct 201742:42not yet analysed
  14. Beyond the Mcse: Active Directory for the Security ProfessionalBeyond the Mcse: Active Directory for the Security Professional28 Oct 201749:53not yet analysed
  15. Breaking Payment Points of Interaction (POI)Breaking Payment Points of Interaction (POI)28 Oct 201749:49not yet analysed
  16. Can You Trust Me Now? An Exploration Into the Mobile Threat LandscapeCan You Trust Me Now? An Exploration Into the Mobile Threat Landscape28 Oct 201743:58not yet analysed
  17. Capturing 0Day Exploits With Perfectly Placed Hardware TrapsCapturing 0Day Exploits With Perfectly Placed Hardware Traps28 Oct 201748:09not yet analysed
  18. HTTP/2 & Quic - Teaching Good Protocols to Do Bad ThingsHTTP/2 & Quic - Teaching Good Protocols to Do Bad Things28 Oct 201751:13not yet analysed
  19. The Linux Kernel Hidden Inside Windows 10The Linux Kernel Hidden Inside Windows 1028 Oct 201752:29not yet analysed
  20. $Hell on Earth: From Browser to System Compromise$Hell on Earth: From Browser to System Compromise28 Oct 201749:09not yet analysed
  21. A Journey From JNDI/LDAP Manipulation to Remote Code Execution Dream LandA Journey From JNDI/LDAP Manipulation to Remote Code Execution Dream Land28 Oct 201748:18not yet analysed
  22. Applied Machine Learning for Data Exfil and Other Fun TopicsApplied Machine Learning for Data Exfil and Other Fun Topics28 Oct 201743:39not yet analysed
  23. Exploiting Curiosity and Context: How to Make People Click on a Dangerous Link...Exploiting Curiosity and Context: How to Make People Click on a Dangerous Link...28 Oct 201743:10not yet analysed
  24. Hackproofing Oracle Ebusiness SuiteHackproofing Oracle Ebusiness Suite28 Oct 201749:49not yet analysed
  25. Measuring Adversary Costs to Exploit Commercial Software...Measuring Adversary Costs to Exploit Commercial Software...28 Oct 201749:53not yet analysed
  26. Memory Forensics Using Virtual Machine Introspection for Cloud ComputingMemory Forensics Using Virtual Machine Introspection for Cloud Computing28 Oct 201732:54not yet analysed
  27. Nonce-Disrespecting Adversaries: Practical Forgery Attacks on GCM in TLSNonce-Disrespecting Adversaries: Practical Forgery Attacks on GCM in TLS28 Oct 201749:21not yet analysed
  28. Subverting Apple Graphics: Practical Approaches to Remotely Gaining RootSubverting Apple Graphics: Practical Approaches to Remotely Gaining Root28 Oct 201754:05not yet analysed
  29. Adaptive Kernel Live Patching: An Open Collaborative Effort...Adaptive Kernel Live Patching: An Open Collaborative Effort...28 Oct 201747:24not yet analysed
  30. Canspy: A Platform for Auditing Can DevicesCanspy: A Platform for Auditing Can Devices28 Oct 201742:24not yet analysed
  31. Drone Attacks on Industrial Wireless: A New Front in Cyber SecurityDrone Attacks on Industrial Wireless: A New Front in Cyber Security28 Oct 201742:56not yet analysed
  32. Gattacking Bluetooth Smart Devices - Introducing a New BLE Proxy ToolGattacking Bluetooth Smart Devices - Introducing a New BLE Proxy Tool28 Oct 201739:40not yet analysed
  33. Secure Penetration Testing Operations: Demonstrated Weaknesses in Learning Material and ToolsSecure Penetration Testing Operations: Demonstrated Weaknesses in Learning Material and Tools28 Oct 201746:55not yet analysed
  34. Towards a Holistic Approach in Building Intelligence to Fight CrimewareTowards a Holistic Approach in Building Intelligence to Fight Crimeware28 Oct 201749:40not yet analysed
  35. 1000 Ways to Die in Mobile Oauth1000 Ways to Die in Mobile Oauth28 Oct 201747:19not yet analysed
  36. Xenpwn: Breaking Paravirtualized DevicesXenpwn: Breaking Paravirtualized Devices28 Oct 201753:23not yet analysed
  37. AMSI: How Windows 10 Plans to Stop Script-Based Attacks and How Well It Does ItAMSI: How Windows 10 Plans to Stop Script-Based Attacks and How Well It Does It28 Oct 201746:35not yet analysed
  38. An Insider's Guide to Cyber-Insurance and Security GuaranteesAn Insider's Guide to Cyber-Insurance and Security Guarantees28 Oct 201750:51not yet analysed
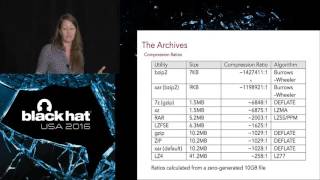
  39. I Came to Drop Bombs: Auditing the Compression Algorithm Weapon CacheI Came to Drop Bombs: Auditing the Compression Algorithm Weapon Cache28 Oct 201728:18not yet analysed
  40. Does Dropping USB Drives in Parking Lots and Other Places Really Work?Does Dropping USB Drives in Parking Lots and Other Places Really Work?28 Oct 201734:00not yet analysed
  41. Into the Core: In-Depth Exploration of Windows 10 IoT CoreInto the Core: In-Depth Exploration of Windows 10 IoT Core28 Oct 201750:07not yet analysed
  42. Intra-Process Memory Protection for Applications on ARM and X86: Leveraging the ELF ABIIntra-Process Memory Protection for Applications on ARM and X86: Leveraging the ELF ABI28 Oct 201751:33not yet analysed
  43. Pwning Your Java Messaging With Deserialization VulnerabilitiesPwning Your Java Messaging With Deserialization Vulnerabilities28 Oct 201748:36not yet analysed
  44. Recover a RSA Private Key From a TLS Session With Perfect Forward SecrecyRecover a RSA Private Key From a TLS Session With Perfect Forward Secrecy28 Oct 201742:25not yet analysed
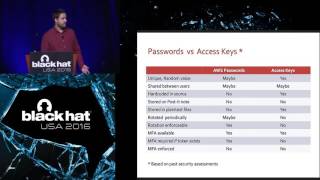
  45. Access Keys Will Kill You Before You Kill the PasswordAccess Keys Will Kill You Before You Kill the Password28 Oct 201731:58not yet analysed
  46. Account Jumping Post Infection Persistency & Lateral Movement in AWSAccount Jumping Post Infection Persistency & Lateral Movement in AWS28 Oct 201734:58not yet analysed
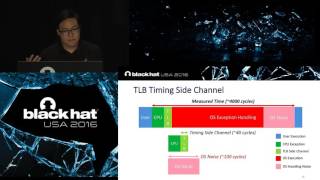
  47. Breaking Kernel Address Space Layout Randomization (KASLR) With Intel TSXBreaking Kernel Address Space Layout Randomization (KASLR) With Intel TSX28 Oct 201750:27not yet analysed
  48. Crippling HTTPs With Unholy PACCrippling HTTPs With Unholy PAC28 Oct 201743:46not yet analysed
  49. Design Approaches for Security AutomationDesign Approaches for Security Automation28 Oct 201737:57not yet analysed
  50. GreatFET: Making GoodFET Great AgainGreatFET: Making GoodFET Great Again28 Oct 201745:42not yet analysed
  51. Using EMET to Disable EMETUsing EMET to Disable EMET28 Oct 201751:56not yet analysed
  52. Viral Video - Exploiting SSRF in Video ConvertersViral Video - Exploiting SSRF in Video Converters28 Oct 201734:14not yet analysed
  53. AVLeak: Fingerprinting Antivirus Emulators for Advanced Malware EvasionAVLeak: Fingerprinting Antivirus Emulators for Advanced Malware Evasion28 Oct 201727:59not yet analysed
  54. Brute-Forcing Lockdown Harddrive Pin CodesBrute-Forcing Lockdown Harddrive Pin Codes28 Oct 201725:38not yet analysed
  55. Building a Product Security Incident Response Team: Learnings From the HivemindBuilding a Product Security Incident Response Team: Learnings From the Hivemind28 Oct 201728:43not yet analysed
  56. Cyber War in Perspective: Analysis From the Crisis in UkraineCyber War in Perspective: Analysis From the Crisis in Ukraine28 Oct 201728:35not yet analysed
  57. Security Through Design - Making Security Better By Designing for PeopleSecurity Through Design - Making Security Better By Designing for People28 Oct 201728:21not yet analysed
  58. Side-Channel Attacks on Everyday ApplicationsSide-Channel Attacks on Everyday Applications28 Oct 201723:49not yet analysed
  59. The Risk From Power Lines: How to Sniff the G3 and Prime Data and Detect the Interfere AttackThe Risk From Power Lines: How to Sniff the G3 and Prime Data and Detect the Interfere Attack28 Oct 201718:14not yet analysed
  60. Unleash the Infection Monkey: A Modern Alternative to Pen-TestsUnleash the Infection Monkey: A Modern Alternative to Pen-Tests28 Oct 201731:01not yet analysed
  61. Watching Commodity Malware Get Sold to a Targeted ActorWatching Commodity Malware Get Sold to a Targeted Actor28 Oct 201731:05not yet analysed
  62. BadTunnel: How Do I Get Big Brother Power?BadTunnel: How Do I Get Big Brother Power?28 Oct 201724:41not yet analysed
  63. Blunting the Phisher's Spear: A Risk-Based Approach...Blunting the Phisher's Spear: A Risk-Based Approach...28 Oct 201726:47not yet analysed
  64. Dungeons Dragons and SecurityDungeons Dragons and Security28 Oct 201721:55not yet analysed
  65. Dark Side of the DNS ForceDark Side of the DNS Force28 Oct 201724:31not yet analysed
  66. Keystone Engine: Next Generation Assembler FrameworkKeystone Engine: Next Generation Assembler Framework28 Oct 201723:39not yet analysed
  67. Pindemonium: A DBI-Based Generic Unpacker for Windows ExecutablePindemonium: A DBI-Based Generic Unpacker for Windows Executable28 Oct 201724:59not yet analysed
  68. Samsung Pay: Tokenized Numbers Flaws and IssuesSamsung Pay: Tokenized Numbers Flaws and Issues28 Oct 201719:09not yet analysed
  69. What's the DFIRence for ICS?What's the DFIRence for ICS?28 Oct 201724:51not yet analysed
  70. Defense At Hyperscale: Technologies and Policies for a Defensible CyberspaceDefense At Hyperscale: Technologies and Policies for a Defensible Cyberspace28 Oct 201752:24not yet analysed
  71. Ouroboros: Tearing Xen Hypervisor With the SnakeOuroboros: Tearing Xen Hypervisor With the Snake28 Oct 201724:45not yet analysed
  72. Advanced CAN Injection Techniques for Vehicle NetworksAdvanced CAN Injection Techniques for Vehicle Networks28 Oct 201750:08not yet analysed
  73. TCP Injection Attacks in the Wild - a Large Scale StudyTCP Injection Attacks in the Wild - a Large Scale Study28 Oct 201738:43not yet analysed
  74. The Remote Malicious Butler Did It!The Remote Malicious Butler Did It!28 Oct 201749:14not yet analysed
  75. Windows 10 Segment Heap InternalsWindows 10 Segment Heap Internals28 Oct 201742:14not yet analysed
  76. The Art of Defense - How Vulnerabilities Help Shape Security Features and Mitigations in AndroidThe Art of Defense - How Vulnerabilities Help Shape Security Features and Mitigations in Android28 Oct 201752:55not yet analysed
  77. Understanding HL7 2.X Standards, Pen Testing, and Defending HL7 2.X MessagesUnderstanding HL7 2.X Standards, Pen Testing, and Defending HL7 2.X Messages28 Oct 201746:13not yet analysed
  78. Analysis of the Attack Surface of Windows 10 Virtualization-Based SecurityAnalysis of the Attack Surface of Windows 10 Virtualization-Based Security28 Oct 201751:13not yet analysed
  79. Cunning With CNG: Soliciting Secrets From SchannelCunning With CNG: Soliciting Secrets From Schannel28 Oct 201746:38not yet analysed
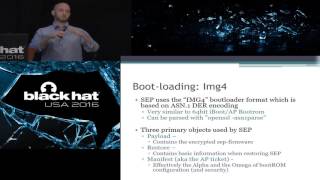
  80. Demystifying the Secure Enclave ProcessorDemystifying the Secure Enclave Processor28 Oct 201747:39not yet analysed
  81. Hacking Next-Gen ATMs: From Capture to CashoutHacking Next-Gen ATMs: From Capture to Cashout28 Oct 201733:04not yet analysed
  82. Next-Generation of Exploit Kit Detection By Building Simulated ObfuscatorsNext-Generation of Exploit Kit Detection By Building Simulated Obfuscators28 Oct 201722:41not yet analysed
  83. Investigating DDOS - Architecture Actors and AttributionInvestigating DDOS - Architecture Actors and Attribution28 Oct 201751:56not yet analysed
  84. O-Checker: Detection of Malicious Documents Through Deviation From File Format SpecificationsO-Checker: Detection of Malicious Documents Through Deviation From File Format Specifications28 Oct 201719:11not yet analysed
  85. Language Properties of Phone Scammers: Cyberdefense At the Level of the HumanLanguage Properties of Phone Scammers: Cyberdefense At the Level of the Human28 Oct 201748:44not yet analysed
  86. The Tao of Hardware the Te of ImplantsThe Tao of Hardware the Te of Implants28 Oct 201743:10not yet analysed
  87. BadWPADBadWPAD28 Oct 201724:50not yet analysed
  88. Hardening AWS Environments and Automating Incident Response for AWS CompromisesHardening AWS Environments and Automating Incident Response for AWS Compromises28 Oct 201746:15not yet analysed
  89. Horse Pill: A New Type of Linux RootkitHorse Pill: A New Type of Linux Rootkit28 Oct 201749:28not yet analysed
  90. Discovering and Exploiting Novel Security Vulnerabilities in Apple ZeroConfDiscovering and Exploiting Novel Security Vulnerabilities in Apple ZeroConf28 Oct 201741:38not yet analysed
  91. SGX Secure Enclaves in Practice: Security and Crypto ReviewSGX Secure Enclaves in Practice: Security and Crypto Review28 Oct 201748:11not yet analysed
  92. Weaponizing Data Science for Social Engineering: Automated E2E Spear Phishing on TwitterWeaponizing Data Science for Social Engineering: Automated E2E Spear Phishing on Twitter28 Oct 201741:55not yet analysed
  93. Windows 10 Mitigation ImprovementsWindows 10 Mitigation Improvements28 Oct 201751:22not yet analysed
  94. Bad for Enterprise: Attacking BYOD Enterprise Mobile Security SolutionsBad for Enterprise: Attacking BYOD Enterprise Mobile Security Solutions28 Oct 201738:31not yet analysed
  95. Breaking FIDO: Are Exploits in There?Breaking FIDO: Are Exploits in There?28 Oct 201738:21not yet analysed
  96. Iran's Soft-War for Internet DominanceIran's Soft-War for Internet Dominance28 Oct 201751:44not yet analysed
  97. OSS Security Maturity: Time to Put on Your Big Boy Pants!OSS Security Maturity: Time to Put on Your Big Boy Pants!28 Oct 201751:44not yet analysed
  98. Pangu 9 InternalsPangu 9 Internals28 Oct 201746:52not yet analysed
  99. PLC-Blaster: A Worm Living Solely in the PLCPLC-Blaster: A Worm Living Solely in the PLC28 Oct 201737:43not yet analysed
  100. The Year in FlashThe Year in Flash28 Oct 201740:23not yet analysed