Skip to content

🗂️ Other170

What you seeeverything
interconnects.aiarticle

Was I wrong about open models & cyber risks?

Interconnects post in which Nathan Lambert revisits his claim that an open-weight release of Claude Mythos in April 2026 would have been survivable. He argues GLM-5.3 already crosses that capability threshold with little visible harm. He cites Epoch AI's GLM-5.3 Firefox file-exfiltration exploit and Joshua Saxe's trend data, and says recent vulnerability waves come mostly from closed models and general AI diffusion.

GLMFirefoxGitLab+1
MythosProject GlasswingPHP2Shell+9

AI Security, other· Published and added 30 Oct 2026

rekt.newsarticle

Rekt - News or Hype?

Rekt News piece tracing three AI-security headlines back to their sources. It covers Justin Drake's October 2026 "bunker mode" warning about AI breaking ECDSA, OpenAI's report of a model spending Sepolia test ETH from a default developer mnemonic, and Wiz's "70% of the Internet" claim for PHP CVE-2026-109618 and CVE-2026-109619. It closes with four questions for checking a claim.

OpenAIPHPEthereum+3
CVE-2026-109618CVE-2026-109619Justin Drake+13

AI Security, other· Added 29 Oct 2026

socket.devarticle

OpenCode User Hit with Hostile Backlash After Reporting Free AI Loophole

Socket reports on a GitHub issue for OpenCode, opened 28 June, describing a bypass of per-IP usage limits on its free hosted models by switching VPN addresses. The reporter first proposed account-based limits, then reopened the issue in August to promote the workaround and claimed to run 130 agents. After the thread drew harassment and was deleted in October 2026, it is unclear whether OpenCode fixed the bypass.

OpenCodeVPNGitHub+1
AnomalySarah GoodingDeepSeek V4 Flash+1

other· Published and added 29 Oct 2026

securityweek.comarticle

Adobe, Veeam, Juniper Networks Patch Critical Vulnerabilities

SecurityWeek roundup of patches from Adobe, Veeam and Juniper Networks covering over three dozen vulnerabilities. Adobe fixed 12 flaws (eight critical in Campaign Classic), Veeam fixed nine (including a cross-tenant RCE in Backup for Microsoft 365), and Juniper fixed 18 in Session Smart Router and Conductor. None were reported exploited. Juniper said CVE-2026-109618 (PHP2Shell) affects Junos OS but is not exploitable there.

Adobe Campaign ClassicVeeam Backup & ReplicationVeeam Backup for Microsoft 365+2
CVE-2026-109618PHP2Shell

other· Published and added 29 Oct 2026

securityweek.comarticle

Chrome and Firefox Updates Patch Over 200 Vulnerabilities

Chrome 156 and Firefox 159 security updates fix over 200 vulnerabilities. Chrome 156 patches 52 flaws, four critical, including CVE-2026-118306, a FileSystem memory corruption bug that allows code execution outside the sandbox via a crafted HTML page. Firefox 159 fixes 167 flaws, 108 high severity, mostly use-after-free, plus Thunderbird and ESR releases. No in-the-wild exploitation is reported.

ChromeFirefoxThunderbird+1
CVE-2026-118306use-after-freesandbox escape

AppSec, other· Published and added 28 Oct 2026

eprint.iacr.orgpaper

Shor's algorithm compiled on cat qubits: 22 593 qubits for RSA-2048 in 3.14 days

Shor's algorithm compiled on cat qubits is an IACR ePrint (2026/2665) giving an end-to-end resource estimate on superconducting cat qubits, using repetition and LDPC cat codes. Factoring RSA-2048 needs about 23,000 cat qubits and 3.14 days, assuming phase-flip noise p_Z = 5e-4 and no bit-flips. secp256k1 ECDLP needs at most 30,000 qubits and 1 hour. A space-for-time trade runs RSA-2048 in 1.25 hours on about 611,000 qubits.

Bitcoin
Shor's algorithmRSA-2048secp256k1+5

other· Published and added 28 Oct 2026

eprint.iacr.orgpaper

Beyond the Event Horizon of Keccak, Extending the Observation from 2011 and applications

Beyond the Event Horizon of Keccak extends a 2011 observation that a path in the Keccak sponge from a zero-capacity state back to one yields infinite second-preimage families. Three theorems cover loops from any capacity value x, k-block loops and cycles, and Joux-style multicollisions with search cost independent of k. Verified examples run on Keccak-f[200] and Keccak-f[1600] with c=32; it also proposes bridge-based protocols.

KeccakSHA-3Lean
Danilo GligoroskiJoux multicollisionssecond preimages+2

other· Published and added 28 Oct 2026

akamai.comarticle

TLP Is Not a Suggestion

Akamai SIG argues that vendors and researchers broke embargo norms during the October 2026 PHP2Shell leak, when the PHP fix shipped a day early on 21 October. It explains the four TLP 2.0 labels, tabulates past embargo breaks (Heartbleed, a collapsed six-month kernel-era embargo, the Alibaba Cloud and MIIT case), and lists seven practices, such as no proofs of concept or CVE numbers before the fix.

PHP
CVE-2026-111497PHP2ShellTraffic Light Protocol+11

other· Added 30 Oct 2026, published 28 Oct 2026

eprint.iacr.orgpaper

Radical isogenies on every model

Radical isogenies on every model is an IACR ePrint paper by Thomas Decru (October 2026). It gives radical isogeny steps of every odd degree N directly on short Weierstrass, Montgomery, twisted Edwards, Huff, Jacobi quartic, twisted Hessian, Legendre and Jacobi intersection curves, plus Kummer lines. In Tate normal form a step drops from 12.5N to 10N multiplications. Montgomery and twisted Edwards curves cost 10.5N+O(1) per step and 2N to push a point. All algorithms are inversion-free, with exact operation counts.

CSIDH
Thomas Decruradical isogeniesVélu's formulae+1

other· Added 28 Oct 2026, published 27 Oct 2026

blog.cloudflare.comarticle

What took the Internet offline in Q3 2026

Cloudflare's Q3 2026 review of the 49 Internet disruptions seen by Cloudflare Radar between July and September 2026. Government-directed shutdowns led with 19 (18 exam shutdowns in Iraq), followed by 14 power outages and 5 natural disasters. It gives traffic-drop figures and durations for Cuba, Honduras, Ukraine, Guam, Colombia, Ethiopia's Tigray region and others, including a Honduran interconnection facility power failure that cut HTTP traffic 63%.

Cloudflare
Iraq exam shutdownsTigray shutdownSuper Typhoon Bavi+10

other· Added 29 Oct 2026, published 27 Oct 2026

securityweek.comarticle

iOS, macOS 27.2 Patch 286 Bugs; Fix for Exploited Flaw Backported to iOS 18

Apple's 27.2 releases fix 286 vulnerabilities across iOS/iPadOS (163) and macOS Golden Gate (263), with memory corruption in WebKit and the kernel, sandbox escapes, Gatekeeper bypasses and a remote code execution bug in Remote Management. iOS and iPadOS 18.7.11 backport the fix for CVE-2026-86950, an exploited zero-day found by Meta's product security team and first patched in 26.7.1. Patch counts for tvOS, watchOS, visionOS, Safari and the 26.7.2 and Sequoia 15.8.2 releases are also listed.

iOSmacOSSafari+2
CVE-2026-86950Metasandbox escape+2

Mobile Security, other· Published and added 27 Oct 2026

securityweek.comarticle

This is Fine: What NetScaler Zero-Days Tell Us About the New Normal

This SecurityWeek commentary covers the September 2026 Citrix NetScaler ADC and Gateway zero-days, exploited from mid-month and patched on 27 September as unauthenticated RCE flaws CVE-2026-88771 through CVE-2026-88778. The author argues the fast response shows stronger defence. Cited evidence: Citrix disclosure time fell from about 40 days to 17 in 2026 after it set up a NetScaler CNA, and CISA made a rare Sunday KEV addition.

Citrix NetScaler
CVE-2026-88771CVE-2026-88772CVE-2026-88773+9

other, Threat Intel· Published and added 27 Oct 2026

eprint.iacr.orgpaper

Alg\{Ossa\}: Decentralized Secure Aggregation with Rotating Committees and Eventual Delivery

AlgOssa is a decentralized secure aggregation protocol built on Ossa, a generic committee-aided, single-server construction for one-shot clients (following OPA and Willow, CRYPTO 2025). Ossa realizes secure aggregation with non-selective abort against a malicious server. AlgOssa adds Algorand-style sortition to rotate leaders and committees, bounds the chance of an honest server, and gives eventual delivery. Classical and post-quantum routes are evaluated.

Algorand
OssaAlgOssaOPA+2

other· Added 28 Oct 2026, published 27 Oct 2026

coindesk.comarticle

Solana bug reports now cost 1 SOL as AI floods security teams with spam

Firedancer, the Solana validator client built by Jump Crypto, now requires researchers to burn 1 SOL (about $100) per bug report, nonrefundable. A $1 million audit contest from 9 April to 9 May 2026 drew 809 reports from 162 researchers but only 127 unique findings, and nearly half of valid reports were duplicates. Rewards are doubled through 20 November, with Alpenglow criticals up to $300,000.

FiredancerSolanaAgave
Jump CryptoAlpenglowIshan Bhatt+2

other· Published and added 27 Oct 2026

ethresear.charticle

Inventory of PQ P2P Migrations in the Consensus Layer

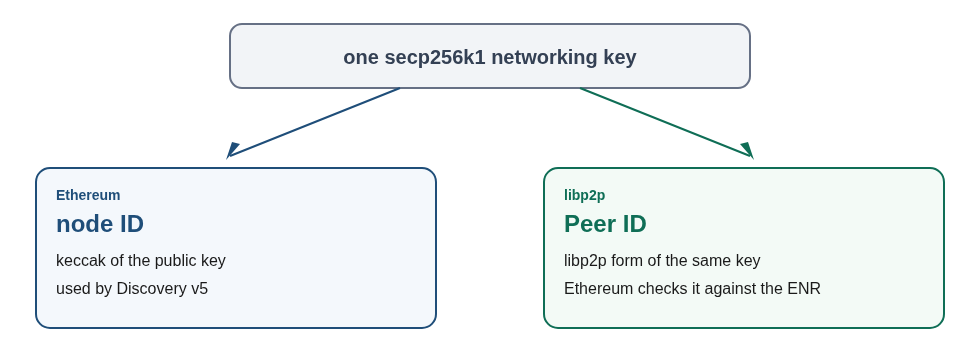
Inventory of post-quantum migration work for Ethereum consensus-layer networking, by adust09 of Nyx Foundation. It maps three targets: Discovery v5/ENR signatures and key exchange, TLS 1.3 key agreement in QUIC, and libp2p TLS identity binding and CertificateVerify. It covers the 300-byte ENR and 1,280-byte packet limits, why hybrid KEMs do not authenticate peers, and downgrade and DoS concerns. It selects no algorithm or schedule.

Ethereumlibp2pQUIC+3
ML-KEMECDSAFIPS 203+8

other· Published and added 27 Oct 2026

securityweek.comarticle

Maritime Coalition Launches Free Vulnerability Database for Ship and Port Systems

Blue Initiative is a free public vulnerability database for maritime IT and OT, built by Cydome, ClassNK, Bureau Veritas, MTS-ISAC and Rakuten Maritime. It holds nearly 30,000 entries, over 2,000 rated critical by CVSS and more than 580 known exploited. Only 37 affect ship and port products. Most entries are pulled from CISA ICS advisories and the KEV catalog and mapped to maritime systems.

CISA KEVCVSS
Blue InitiativeCydomeClassNK+5

other· Published and added 27 Oct 2026

arxiv.orgpaper

Measuring Users' Security and Privacy Concerns About Third-Party Community Bots on Discord

Measurement study of 23,102 third-party Discord bots and 183,142 user reviews (2021-2026, 49 languages). A fine-tuned DeBERTa classifier plus manual validation yields 8,832 security and privacy reviews, mapped to a 31-theme taxonomy; Data Sharing (30.5%) and Data Collection (16.2%) dominate. Permission count and admin status correlate only weakly with user concerns. The authors build BotLens, an MCP-server auditing framework with six tools.

DiscordModel Context ProtocolLLM
BotLensDeBERTa

other, AI Security· Added 28 Oct 2026, published 27 Oct 2026

eprint.iacr.orgpaper

Revisiting ZMAC+: Birthday-Bound Attacks and a Beyond-Birthday-Bound Repair

ZMAC+ is a tweakable-block-cipher MAC (List and Nandi, ToSC 2017) with claimed beyond-birthday-bound security. This ePrint paper (2026/2647) shows a tag-swap attack: for two-block tags, a distinguisher and a fresh-message forgery with constant success probability using O(2^{n/2}) queries in the ideal-TBC model. It also corrects a counting error in the published Lemma 4 and proposes a repaired variant with an adaptive PRF bound of order q^2/2^{n+min(n,t)}.

ZMAC+
DoveMACZHashZAE+4

other· Published and added 26 Oct 2026

eprint.iacr.orgpaper

Cryptanalysis and Repair of "Decentralized Multi-authority ABE for NC$^1$ from BDH"

Cryptology ePrint 2026/2642 presents a plaintext-recovery attack on the DBDH and CBDH variants of the Datta, Komargodski and Waters multi-authority ABE for NC1 (Journal of Cryptology, 2023). It needs one corrupt authority and two users, and succeeds with probability one in the static model. The flaw is an invalid extension of the Rouselakis-Waters LSSS matrix-normalization lemma. The paper also attacks two Datta-Pal (PKC 2023) attribute-based inner-product schemes and proves repaired versions secure in the random oracle model.

Datta-Komargodski-Waters multi-authority ABEDatta-Pal attribute-based inner-product functional encryptionRouselakis-Waters LSSS matrix-normalization lemma+3

other· Published and added 26 Oct 2026

eprint.iacr.orgpaper

A Memory-efficient Implementation of Wiedemann XL

A Memory-efficient Implementation of Wiedemann XL is an ePrint paper (2026/2641) giving the first efficient on-the-fly implementation of XL with block Wiedemann for the multivariate quadratic problem. It builds on the CCNY SSE implementation, removes column-index tables, and computes column indices with O(n^2) instead of O(n^3) look-ups. It runs in comparable BW1 time with up to five times less memory, and an AVX2 port covers F256, the main field of UOV.

MQOMSNOVAMAYO+7

other· Published and added 26 Oct 2026

eprint.iacr.orgpaper

Subexponential Algorithms for LWE via Rejection Sampling on Superlattices

Subexponential Algorithms for LWE via Rejection Sampling on Superlattices is an ePrint paper by Ligeng Fan, Changpeng Shao, Hongbo Li and Dingkang Wang. It extends the Ducas, Engelberts and Loyer superlattice framework to give a provable classical search-LWE algorithm for prime q in [n^2, 2n^2], using m=4n samples and time and space exp(O(n/ln ln n)). A second variant runs in 2^((1/2+o(1))n/ln R) for general parameters. It resolves a gap left by Kirchner and Fouque.

Ducas, Engelberts and LoyerKirchner and FouqueBKW algorithm+1

other· Published and added 26 Oct 2026

eprint.iacr.orgpaper

Private Information Retrieval with Accountability at Erasure-Optimal Server Redundancy

SynTrace is a single-round compiler that adds accountability to linear private information retrieval (PIR). The client mixes the retrieval query with m audit queries, so audit syndromes identify up to d deviating servers among t colluding ones before reconstruction. The paper proves perfect query privacy and zero false identification within the threshold. For Shamir-based PIR it needs k=t+d+1 servers. For a 32 KiB record from a 1 GiB database it uses 2.25 MiB, against 8.96 MiB for the Eriguchi, Kurosawa and Nuida (TCC 2022) homomorphic-MAC construction.

SynTraceEriguchi-Kurosawa-Nuida homomorphic MACTCC 2022

other· Published and added 26 Oct 2026

eprint.iacr.orgpaper

Decision Attacks on Known-Covariance Ring-LWE via Public Gram Determinants

Anis Bkakria's ePrint 2026/2638 gives polynomial-time decision attacks on Known-Covariance Ring-LWE (KCov-RLWE), the assumption Micciancio and Suhl introduced for simulation-secure threshold encryption. The public sample and covariance hint form a bordered Gram matrix whose determinant leaks a residual that differs between real and uniform samples. The attacks cover broad prime-modulus families at ring rank one and transfer to composite moduli with an odd prime divisor. Power-of-two moduli are not covered, and the paper does not break the full threshold-encryption scheme.

Ring-LWE
Known-Covariance Ring-LWEMicciancio and SuhlGram determinant+2

other· Added 26 Oct 2026, published 25 Oct 2026

eprint.iacr.orgpaper

Maximum-Likelihood Decoding of Gabidulin Codes Is NP-Hard Even in Dimension One

Philippe Gaborit proves that maximum-likelihood decoding of Gabidulin codes is NP-hard even for dimension one: deciding rank distance at most n-2 from the code {λg} is NP-complete. The reduction is deterministic, so Rank Syndrome Decoding and Rank Minimum Distance for F_{q^m}-linear codes are NP-complete under deterministic reductions, where the earlier reduction was randomized. It goes through a new pivot problem, Twisted Square Membership.

Gabidulin codes
Philippe GaboritGuruswami-Vardy theoremTwisted Square Membership+2

other· Added 26 Oct 2026, published 25 Oct 2026

eprint.iacr.orgpaper

Revisiting AES Key Wrap: Forgery Bounds, Structural Observations, and Recommendations for the Revision of NIST SP 800-38F

Revisiting AES Key Wrap is an ePrint paper (2026/2636) by John Preuß Mattsson, expanded from technical comments to NIST on the SP 800-38F revision. It shows the stated forgery probabilities ignore adaptive attacks and gives corrected bounds for KW, KWP and TKW. It also shows KW lacks beyond-birthday-bound security, since a forgery leaks a plaintext prefix and an encryption-only distinguisher exists.

AES Key WrapAES
NISTNIST SP 800-38FKW+4

other, GRC· Added 26 Oct 2026, published 25 Oct 2026

eprint.iacr.orgpaper

A Kelsey–Kohno Attack Variant against SHA-2 Message Digests in HSS/LMS and XMSS

Falko Strenzke's ePrint 2026/2635 presents a multi-target second-preimage attack on message hashing in HSS/LMS and XMSS with SHA-256 and SHA-256/192. It herds chaining states from many collected signatures into one state, defeating the key and leaf-index prefix. With 2^64 signatures, SHA-256 cost falls from 2^256 to about 2^166 (2^156 at maximal message length). SHAKE256 parameter sets are unaffected.

HSS/LMSXMSSSHA-256+2
Kelsey–Kohno herding attackKelsey–Schneier expandable messagemulti-target second-preimage attack+2

other· Added 26 Oct 2026, published 25 Oct 2026

interconnects.aitalk

Podcast: Kimi K3.1 Pro, the new cyber reality, and Muse musings

Interconnects podcast with Nathan Lambert and Florian Brand on Kimi K3.1 Pro and the AI cyber landscape. Kimi says it down-weighted cyber data in mid-training so its open weights do not extend offensive capability. They discuss the PHP2Shell remote code execution bug, the repeat LiteLLM compromise from an API key left in GitHub for five months, abliterated model APIs, and trusted-access programs from OpenAI and Anthropic. The transcript was truncated at the very end.

Kimi K3.1 ProLiteLLMPHP+3
PHP2ShellPatch the PlanetPHP Foundation+10

AI Security, other· Published and added 25 Oct 2026

eprint.iacr.orgpaper

On the Inapplicability of Residue-Confined Error Attacks to CRT-FHE with Non-Degenerate Error Distributions

Anil Kumar Pradhan's October 2026 ePrint rebuts the Olejnik and Naskrecki (2026) key-recovery and plaintext-recovery attack on the Pradhan CRT-RLWE fully homomorphic encryption scheme. It argues the attack works only because the chosen error distribution lies in the kernel of the CRT encoding, which makes the effective error zero. It also argues that the intended centered-binomial errors make that event negligible at the reported parameters. This is the author's own response, not independent verification.

CRT-FHERLWE
Olejnik and NaskreckiAnil Kumar PradhanKey Recovery from Residue-Confined Errors in the Pradhan CRT-RLWE Construction+1

other· Added 26 Oct 2026, published 24 Oct 2026

eprint.iacr.orgpaper

Chosen Commitments and Certified Decoding Regions in the Adaptive Threshold Schnorr Attack

This IACR ePrint 2026/2632 paper by Demirtaş and Yayla analyses the Crites–Stewart adaptive forgery attack on threshold Schnorr signatures, which needs one call to a sparse linear search oracle (bounded distance decoding of a scaled Reed–Solomon code). It shows that choosing the commitment coefficient vector does not help much: a wrapper adversary with Q challenges succeeds with probability at most QM/p, even if its solvers decode every witness for free. For the six original (N, τ) pairs, M stays below 2^24, so the bound is under 2^-100 after 2^128 challenges at p = 2^252.

Schnorr signaturesReed–Solomon codesfolded Reed–Solomon codes
Crites and Stewart attackGuruswami–WangAshvinkumar–Habib–Srivastava+2

other· Added 26 Oct 2026, published 24 Oct 2026

eprint.iacr.orgpaper

VeilDNS: Post-Quantum DNS Privacy from the First UDP Packet

VeilDNS is a DNS-native protocol that uses a post-quantum KEM and AEAD to encrypt DNS questions and answers and authenticate the resolver in one UDP exchange on port 53, preserving the DNS wire format. It has stateless and stateful modes plus optional forward secrecy from the second query. Against ML-DSA-authenticated DoT/DoH/DoQ it reports up to 3.5x higher cold-session throughput and 13.7x fewer bytes; Tamarin proves query confidentiality, response authentication and forward secrecy.

DNSML-DSATLS+1
VeilDNSTamarinDoT+3

other· Added 26 Oct 2026, published 24 Oct 2026

eprint.iacr.orgpaper

The Exact Bit Security of Hash-Based Signatures

The Exact Bit Security of Hash-Based Signatures is a 2026 IACR ePrint paper that analyses XMSS with 128-bit digests and SLH-DSA-128s in the random oracle model, with proofs formalised in Lean4. Strong unforgeability comes to 127 bits under most accounting modes but only 122 bits if just direct random oracle queries are counted. The authors give matching attacks, and show how resource accounting changes the result.

XMSSSLH-DSALean
Mikhail KudinovBenedikt WagnerEmile Wambsgans

other· Added 26 Oct 2026, published 24 Oct 2026

eprint.iacr.orgpaper

Provable Security of SHA-256-Based LMS Revisited in the Ideal-Cipher Model

Provable Security of SHA-256-Based LMS Revisited in the Ideal-Cipher Model is an October 2026 ePrint paper by Chun Guo, Hao Cheng, Bart Preneel and Meiqin Wang. It shows forgery attacks on LMS_SHA256_M32 and LMS_SHA256_M24 that exploit Merkle-Damgård structure, so the Katz and Fluhrer random-oracle bounds do not apply. It proves ideal-cipher-model bounds: about 256 minus log2 of the block count for M32, and a minimum of two terms for M24.

LMSSHA-256
KatzFluhrerLMS_SHA256_M32+4

other· Added 26 Oct 2026, published 24 Oct 2026

eprint.iacr.orgpaper

Faster Matrix Multiplication Leads to Faster Lattice Sieving

Gao and Hu's IACR ePrint 2026/2622 shows that if the matrix multiplication exponent satisfies ω ≤ 9/4 − η, heuristic lattice sieving runs in (3/2 − δ)^(n/2+o(n)) time under the spherical heuristic from the BDGL analysis. It builds on OpenAI's recent result that ω ≤ 9/4. With known matrix multiplication algorithms, the method already gives subquadratic search inside BDGL buckets. Only the abstract is available, so concrete parameters are not shown.

BDGLspherical heuristicmatrix multiplication exponent

other· Added 26 Oct 2026, published 24 Oct 2026

eprint.iacr.orgpaper

When Elliptic-Curve Semiprimality Certificates Reveal Factors

The paper formalizes elliptic-curve semiprimality certificates by adapting the Goldwasser-Kilian primality criterion. For certificates built with complex multiplication, a norm-lattice reconstruction factors N from (N, S, D) alone in expected polynomial time. The author uses it, plus public-point and quadratic-twist attacks, to factor Reble's 1084-digit and Broadhurst's 5061-digit moduli, and shows that hidden-cofactor, withheld-CM-map and private-isogeny repairs also fail.

Goldwasser-Kilian primality criterionReble modulusBroadhurst modulus+4

other· Added 26 Oct 2026, published 24 Oct 2026

bankless.comarticle

Crypto's Two Answers to AI Bug Hunters

Bankless article on how crypto is responding to AI-driven bug discovery. It cites Bitcoin Core's 22 October 2026 policy change to fix and ship bugs findable with a simple LLM prompt instead of embargoing them, DefiLlama's 112 hacks over $1M in 2026 versus 70 in 2025, and the Initia exploit (~$2.7M). It contrasts an agility approach (Starknet, bunker mode) with minimalism and AI-assisted formal verification (Anthropic and Theorem proofs across 123 libraries).

BitcoinEthereumClaude+3
Antoine PoinsotInitiaStarknet+10

AI Security, other· Published and added 23 Oct 2026

eprint.iacr.orgpaper

Tight Post-Quantum Multi-Key Security of the FX Construction

Rentaro Shiba and Tetsu Iwata prove a tight multi-key security bound for the FX construction (the DESX generalization) in the quantum ideal cipher model. Security holds up to about 2^((n+κ)/3) total classical and quantum oracle queries against fully adaptive adversaries, for any number of keyed instances μ≥1. This improves their ToSC 2026 bound and matches the offline Simon's algorithm attack in the exponent.

FX constructionDESXoffline Simon's algorithm+4

other· Added 24 Oct 2026, published 23 Oct 2026

eprint.iacr.orgpaper

Learning with Quantization and Worst Case Lattice Problems

Learning with Quantization and Worst Case Lattice Problems is an IACR ePrint paper (2026/2613) by Ziwei Hong and Zhongqiu Fang. It proves that search and decision learning with quantization (LWQ) with public dither is as hard as quantum GapSVP and SIVP on arbitrary lattices, using the randomized polar lattice quantizer of Lyu et al. It also shows that a complete reduction for interval uniform error LWE (MAMBA Frost) and hardness at concrete MAMBA parameters are not established.

LWE
MAMBAMAMBA FrostGapSVP+4

other· Added 24 Oct 2026, published 23 Oct 2026

eprint.iacr.orgpaper

Pairwise Independence of Ten-Round AES

Pairwise Independence of Ten-Round AES (Zhongfeng Niu, Kai Hu, ePrint 2026/2608) proves that ten rounds of AES with independent uniform round keys and input/output whitening are within 3017/2^141 (below 2^-129) statistical distance of pairwise independent. The proof bounds the averaged difference-distribution matrix over five superbox layers, using Gram moments and MDS code constraints. Final-round MixColumns omission is retained.

AES
pairwise independencedifference-distribution matrixMDS code+1

other· Added 24 Oct 2026, published 23 Oct 2026

eprint.iacr.orgpaper

Mímir: A Stateless Private Search Engine

Mímir is a cryptographic protocol for stateless semantic private search over highly dynamic public databases. It uses homomorphic ciphertext switching, relies on (Ring) Learning with Errors, and needs no offline communication. Against Tiptoe it matches search quality with 84x less per-query communication (0.24 MiB). Against PACMANN it raises quality from 76% to 81% of non-private search, with a 9.54 MiB one-time cost instead of 2.68 GiB, but is 2.1x slower.

TiptoePACMANNLearning with Errors+1

other· Added 24 Oct 2026, published 22 Oct 2026

eprint.iacr.orgpaper

Balsamic: One-round Threshold UOV from GPU-Accelerated FHE

Balsamic is a complete homomorphic Unbalanced Oil and Vinegar (UOV) signer, used to build one-round threshold UOV signatures from a packed discrete-CKKS FHE circuit. A paired-pivot linear solver and pivot-success certificates allow encrypted retry selection. In 2-out-of-3 semihonest signing, each online partial signature takes 10.7 s on an RTX 6000 Ada and 7.77 s on a GB300, with 5.25 MB per response.

UOVCKKSFHE+2
Balsamicuniversal thresholdizerspaired-pivot solver+1

other· Added 24 Oct 2026, published 22 Oct 2026

eprint.iacr.orgpaper

Integer Coordinate Families and Threshold RSA Signatures for Any Prime Exponent

Paper by Shivansh Jaiswal and Somitra Sanadhya (IACR ePrint 2026/2601) on integer coordinate families for threshold RSA signatures with prime exponent e. It shows the CT-RSA 2026 Ng-Lau scheme admits trivial forgeries and has a flawed proof. It proposes repaired scheme PiIC and integer secret-sharing scheme PiZ for any prime e and any (t,n), both proven TS-UF-CMA secure under the standard RSA assumption. It also gives super-polynomial coordinate lower bounds for pairwise families.

RSA
Ng-Lau schemePiICPiZ+3

other· Added 24 Oct 2026, published 22 Oct 2026

eprint.iacr.orgpaper

Linear Cryptanalysis of TFHE-Friendly Cipher FRAST in the Average Key Setting

Linear cryptanalysis of FRAST, a TFHE-friendly stream cipher, in the average key setting. It fixes the false-positive problem left open in the earlier attack by Bak et al., showing key differences fall into five indistinguishable classes per round. The Contract algorithm recovers the master key for 10 rounds and, on weak keys of density 2^-11.8 to 2^-5.4, reaches full FRAST within the claimed security.

FRASTTFHE
Contract algorithmBak et al.linear cryptanalysis+1

other· Added 24 Oct 2026, published 22 Oct 2026

phoronix.comarticle

Several Linux kernel vulnerabilities accidentally posted to public mailing list

Phoronix reports that Trend Micro's Zero Day Initiative mistakenly sent several Linux kernel vulnerability reports to the public kernel mailing list instead of the private security list. They include two CVSS 9.0 remote code execution bugs (SMB Direct integer underflow, ksmbd race condition), a skb_zerocopy local privilege escalation, a vmwgfx out-of-bounds write, an NVMET information disclosure and a search-domain TCP stack buffer overflow. Some have patches in -next branches, and none were yet in mainline.

Linux kernelksmbdSMB Direct+3
ZDI-CAN-33549ZDI-CAN-33774ZDI-CAN-33367+10

Cloud & Infra, other· Added 23 Oct 2026, published 22 Oct 2026

securityweek.comarticle

Oracle Patches Over 1,200 Vulnerabilities With October 2026 CPU

Oracle's October 2026 Critical Patch Update ships 1,295 fixes covering 1,209 unique CVEs, per Tenable's analysis: 95 critical, 439 high and 582 medium. Fusion Middleware got the most patches (206, 134 remotely exploitable without authentication), followed by E-Business Suite, Siebel CRM, Communications, PeopleSoft, JD Edwards, MySQL and Java SE. Oracle flags no exploitation in the wild and issued a separate alert for CVE-2026-91403 (eMudhra weak-key incident).

Oracle Fusion MiddlewareOracle E-Business SuiteSiebel CRM+3
CVE-2026-91403TenableeMudhra+2

other· Published and added 22 Oct 2026

eprint.iacr.orgpaper

Getting to the right root: radical isogenies of every degree

Thomas Decru's ePrint 2026/2595 proves a corrected version of radical isogeny formulae for every N≥4, odd and even, over fields of characteristic coprime to 2N. It settles the sign choice for even N so that 2-isogeny walks stay on the volcano surface. One radical step costs about 12.5N multiplications and one exponentiation, and the paper shows how to evaluate radical isogenies on points, so a CSIDH class group action needs no torsion point sampling.

CSIDH
radical isogeniesKronecker theta function2-isogeny volcano+3

other· Added 24 Oct 2026, published 22 Oct 2026

eprint.iacr.orgpaper

Efficient Laconic Oblivious Transfer with Malicious Security

Efficient Laconic Oblivious Transfer with Malicious Security is an ePrint paper (2026/2593, ASIACRYPT 2026 revision) giving the first maliciously secure laconic OT that uses its primitives only as black boxes. It adds equivocal vector commitments and maliciously secure witness encryption to the commitment-plus-witness-encryption paradigm. Security is proven in the UC model against malicious senders and in the context model against malicious receivers. Instantiations use LWE and bilinear Diffie-Hellman assumptions in the standard model.

laconic oblivious transferequivocal vector commitmentswitness encryption+3

other· Added 24 Oct 2026, published 22 Oct 2026

socket.devarticle

PHP Foundation Says Chainguard Broke Security Embargo Ahead of Emergency Patches

The PHP Foundation's October 21, 2026 postmortem says Chainguard broke an embargo by publishing patched PHP container images over six hours before the coordinated release of fixes for CVE-2026-109618 and CVE-2026-109619, two critical RCE flaws. The piece covers the leaked CVE IDs, Calif's accidentally published exploit video, Chainguard CEO Dan Lorenc's defence citing exploitation in the wild, and the 2024 origin of the memory management bug.

PHPDockerCloudflare+2
CVE-2026-109618CVE-2026-109619Calif+8

Supply Chain, AppSec, other· Published and added 21 Oct 2026

danielmangum.comarticle

Your MCU likely escaped the eMudhra intermediate CA compromise

Analysis of the eMudhra intermediate CA compromise disclosed 20 October 2026, in which eight intermediate CA private keys were weak P-384 keys (top 376 bits zero, one key equal to 4) and publicly accessible. It explains web PKI chains and why browsers enforcing Certificate Transparency were not exposed. It argues MCU firmware that bundles only the single root it needs, as in Zephyr's HTTP GET sample, is likely safe unless it trusts an eMudhra or Sectigo cross-signing root.

ZephyrOpenSSLFirefox+1
eMudhraSectigoCertificate Transparency+6

Hardware & RF, other· Added 22 Oct 2026, published 21 Oct 2026

thephp.foundationarticle

Today's PHP security release, and how we're strengthening security

The PHP Foundation explains the 21 October 2026 release of PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35, which fix two critical unauthenticated RCE flaws in memory management and error handling, including an OOM problem behind CVE-2026-109618. It covers the 2024 Quarkslab audit, the stalled fix, the August 2026 reports from Calif, OpenAI and Wiz, and the embargo leaks (CVE IDs, a Calif video, Chainguard images). It also lists new security team structure and AI-assisted triage.

PHPChainguardOpenAI+2
CVE-2026-109618CalifPatch the Planet+8

AppSec, other· Added 22 Oct 2026, published 21 Oct 2026

eprint.iacr.orgpaper

Rerandomizable Garbling for Arithmetic Circuits

Rerandomizable Garbling for Arithmetic Circuits is an IACR ePrint paper (2026/2590) by Acharya, Meyer, Orlandi and Roy. It gives the first rerandomizable garbling scheme for arithmetic circuits, built on techniques from garbling via homomorphic secret sharing. Communication is O(|C| log B), with 17 group elements per multiplication gate and free additions. Security rests on subgroup-indistinguishability assumptions such as DCR and class groups.

Decisional Composite ResiduosityYao's garbled circuitshomomorphic secret sharing+4

other· Added 24 Oct 2026, published 21 Oct 2026

securityweek.comarticle

Browsers Block eMudhra Intermediate CAs Over Recoverable Private Keys

Eight intermediate CA certificates issued by Indian CA eMudhra in April 2025 had private keys generated with weak entropy, effectively all zeroes except the last byte, so they could be recovered almost instantly with baby-step giant-step. Mozilla and Google blocked them on 17 October 2026, Apple on 19 October and Microsoft on 20 October. eMudhra blamed a key ceremony script flaw that created a second, weaker key pair.

ChromeFirefoxCloudflare
eMudhraDennis Jacksonbaby-step giant-step+5

other· Published and added 21 Oct 2026

eprint.iacr.orgpaper

Modeling Modular Multiplication for Monomial Prediction and Impossible Differentials, with Application to MSX

This ePrint paper gives the first exact bit-level models of modular multiplication z=(x·y) mod 2^n. One model is for monomial prediction under 3SDP-woU, the other for impossible differential search. Applied to the MSX lightweight cipher, it yields a 7-round integral distinguisher (2^96 data) for MSX-128, key recoveries on 8 and 9 of 18 rounds at about 2^228 operations, and 1,984 seven-round impossible differentials. Both models are implemented in CLAASP.

MSXCLAASP
MSX-128monomial predictionthree-subset division property+5

other· Added 24 Oct 2026, published 21 Oct 2026

eprint.iacr.orgpaper

Rounded Gaussians are Discrete Gaussians

Rounded Gaussians are Discrete Gaussians is an IACR ePrint paper (2026/2583) by Corentin Jeudy. It shows that setting the rounded Gaussian parameter to sigma = s - 1/(24s) gives a distribution within Rényi divergence 1 + O(1/s^8) of a discrete Gaussian of parameter s. Lattice schemes can then use the simple, constant-time-friendly, low-memory rounded sampler while analyzing security against an ideal discrete Gaussian.

Rényi divergenceCorentin JeudyHülsing, Lange and Smeets

other· Added 24 Oct 2026, published 21 Oct 2026

eprint.iacr.orgpaper

SoK: Design-Level Backdoors in Block Ciphers Constructions, Detection, and Key Recovery

SoK on design-level backdoors in block ciphers. It places four published designs (Rijmen and Preneel, Paterson, Bannier and Filiol, Peyrin and Wang) in one taxonomy and gives a sound algorithm that recovers a partition trapdoor from S-box tables. It attacks KG-DES, BEA-1 and LowMC-M: KG-DES key recovery takes minutes, and the LowMC-M MALICIOUS backdoor yields the key from 35 to 409 queries. Trapdoors hidden in linear layers leave no trace, so the authors recommend deriving constants verifiably from a public seed.

KG-DESBEA-1LowMC-M+2
Rijmen and PreneelPatersonBannier and Filiol+5

other· Added 24 Oct 2026, published 21 Oct 2026

coindesk.comarticle

A company that vouches for websites had secret keys so weak that 8 of them were cracked

eMudhra, an Indian certificate authority with over 60 million issued certificates, had eight CA private keys that were tiny integers such as 4, 56 and 237. Researcher Scott Helme recovered all eight from public certificates in under a second, and the keys were exposed from April 2025. Mozilla, Chrome, Apple and Microsoft blocked them between 17 and 20 October 2026, but curl, Python, Node.js, Go and Java accepted a forged Stripe API certificate because they skip revocation checks.

cURLPythonNode.js+3
eMudhraSectigoScott Helme+5

other· Published and added 21 Oct 2026

eprint.iacr.orgpaper

RDK-CKKS: A Framework for Rigorous Error Analysis for CKKS Computation

RDK-CKKS is a framework for rigorous probabilistic error analysis of CKKS homomorphic encryption. It injects randomization keys (encryptions of zero) at key-switching and rescaling so each operation's error has provable tail bounds, which noise flooding needs for IND-CPA^D and threshold settings. It gives a full rigorous analysis of binary bootstrapping, at about 3% extra modulus and 27% extra key communication over bootstrapping keys.

CKKS
IND-CPA^Dnoise floodingrandomization keys+1

other· Added 24 Oct 2026, published 21 Oct 2026

eprint.iacr.orgpaper

Broadcast and Trace from Lattices: Collusion-Resistant and Publicly Traceable

Broadcast and Trace from Lattices is a 2026 ePrint preprint by Jeffrey Champion. It builds collusion-resistant broadcast and trace with public tracing from attribute-based encryption with succinct ciphertexts and lockable obfuscation, both known from decomposed LWE. Ciphertexts are sqrt(N)·poly(λ, log N) in size, with poly(λ, log N) keys. It is the first such scheme based on a simple, instance-independent lattice assumption.

Jeffrey ChampionNassar, Waters and Wupositional witness encryption

other· Added 24 Oct 2026, published 21 Oct 2026

simonwillison.netarticle

eMudhra Intermediate CA Compromise

eMudhra Intermediate CA Compromise is a 20 October 2026 link-blog post reporting that private keys of eight eMudhra intermediate CA certificates were compromised. They chain to roots trusted by the Mozilla, Microsoft, Apple and Chrome programs. Software bundling trust lists needs updating: Linux distros must update ca-certificates, and uv 0.13.4, pip 26.2.2 and certifi 2026.10.19 ship new lists. The post does not describe how the keys were compromised.

Pythonpipuv+2
eMudhra

other· Added 21 Oct 2026, published 20 Oct 2026

eprint.iacr.orgpaper

Further Elaborations on the Provable Dual Attack

Further Elaborations on the Provable Dual Attack is an October 2026 ePrint paper by Kaveh Bashiri presenting a provable dual attack on LWE that recovers a subvector of the secret, with an explicit success-probability bound and no heuristic assumptions. It unifies the analyses of Pouly and Shen (EUROCRYPT 2024) and Bashiri and Wiemers (2025). Applied to ML-KEM it improves the first provable dual attack by 22 to 100 bits; it is also applied to ML-DSA and tested on small instances. The author states ML-KEM and ML-DSA are not threatened.

ML-KEMML-DSA
Pouly and ShenBashiri and WiemersQu, Tian, Wang, and Xu+1

other· Added 21 Oct 2026, published 20 Oct 2026

eprint.iacr.orgpaper

Regular Syndrome Decoding Is Easier Than Previously Estimated

Preprint by Jiseung Kim, Minkyu Kim, Changmin Lee and Hochang Lee on the Regular Syndrome Decoding (RSD) problem. It presents a hybrid-algebraic attack that balances zero-coordinate guesses and syndrome-based eliminations across regular blocks. Parameter sets in Ferret, Wolverine and committed VOLE fall below 128-bit targets by up to 67 bits, and the revised Liu et al. (EUROCRYPT 2024) PCG sets cost under 2^111 field operations.

Regular Syndrome DecodingFerretWolverine+4

other· Added 21 Oct 2026, published 20 Oct 2026

eprint.iacr.orgpaper

Regular Syndrome Decoding Is Easier Than Previously Estimated

Preprint 2026/2563 presents a refined hybrid-algebraic attack on Regular Syndrome Decoding (RSD) that balances zero-coordinate guesses and syndrome-based eliminations across all regular blocks. It puts at least one parameter set each from Ferret (CCS 2020), Wolverine (IEEE S&P 2021) and committed VOLE (CCS 2025) below the 128-bit target, with losses up to 67 bits. PCG attack costs improve by up to 29.77 bits (non-binary) and 25.91 bits (binary), and the revised Liu et al. (EUROCRYPT 2024) 128-bit sets fall below 2^111 field operations.

FerretWolverine
Regular Syndrome Decodinginformation-set decodingpseudorandom correlation generator+3

other· Added 21 Oct 2026, published 20 Oct 2026
eprint.iacr.orgpaper

Graphs and cycles in curve-based collision walks

Graphs and cycles in curve-based collision walks is an IACR ePrint paper (2026/2560) on van Oorschot-Wiener style collision attacks in the multi-user setting. It covers elliptic curve discrete logarithms and isogeny pathfinding on supersingular F_p^2 and F_p curves, and proposes new pseudorandom walks. For F_p^2 curves, L keys need about L + log(L) useful collisions with no infiltrator. For F_p curves, about 0.75L keys fall to L collisions with an infiltrator.

van Oorschot-Wienerisogeny pathfindinginfiltrator+1

other· Added 21 Oct 2026, published 20 Oct 2026

eprint.iacr.orgpaper

Registered ABE via Predicate Encodings, Revisited

Registered ABE via Predicate Encodings, Revisited is an ePrint paper by Junichi Tomida (October 2026) that gives a new definition of predicate encodings suited to registered attribute-based encryption. It yields the first Reg-ABE schemes for (non-)zero inner product and for conjunctions/disjunctions with O(log L)-size ciphertexts. It also gives a registered broadcast encryption scheme with O(log L)-size ciphertexts under the standard k-Lin assumption, not the generic group model.

Junichi TomidaHoeteck WeeZhu et al.+2

other· Added 20 Oct 2026, published 19 Oct 2026
eprint.iacr.orgpaper

Analysis of an AI based code distinguisher

Analysis of DeepDistinguisher, a transformer model that tells Goppa codes from random linear codes. Using saliency maps and attention visualization, the authors find a low-weight-row artifact in the random training instances that the model partly uses. They propose a pairwise-XOR rule on generator matrix rows that correlates strongly with the model's predictions. On random matrices meeting the minimum distance and XOR constraints, the model loses most of its accuracy, so it exploits general combinatorial properties rather than hidden algebraic structure.

DeepDistinguisherGoppa Distinguisher problemGoppa code

AI Security, other· Added 20 Oct 2026, published 19 Oct 2026

eprint.iacr.orgpaper

Post-quantum commutative group actions from oriented superspecial abelian varieties

Castryck, Dina, Kutas and Lorenzon study the Shimura class group action on superspecial principally polarized abelian varieties with a CM orientation, as a post-quantum commutative group action for key exchange. They give tools to represent CM orientations through higher-dimensional isogenies and to compute the action in the restricted effective group action model. These rely on a CM version of Kani's lemma and a trick that often halves the ambient dimension. The paper also gives a method for finding oriented superspecial abelian surfaces and analyses obstructions to transitivity.

Shimura class group actionKani's lemmaIbukiyama-Katsura-Oort correspondence+5

other· Added 20 Oct 2026, published 19 Oct 2026

eprint.iacr.orgpaper

Concrete LDVR Attacks with Fewer Signers

Concrete LDVR Attacks with Fewer Signers is an ePrint paper by Renas Bacho on the low-dimensional vector representation (LDVR) problem behind adaptive security of threshold Schnorr. It combines a Chinese remainder theorem construction with a generalized birthday search to attack 488 signers with 173 corruptions over the Curve25519 scalar field, down from 5,020 signers. For adversarial evaluation points, it reaches optimal success probability and breaks 228 signers with 114 corruptions in 168.60 seconds.

Threshold SchnorrCurve25519SHA-512
LDVRgeneralized birthday attacksubset sum+4

other· Added 20 Oct 2026, published 19 Oct 2026

eprint.iacr.orgpaper

Evasive Inner Product Functional Encryption Is Broken Too

Evasive Inner Product Functional Encryption Is Broken Too is a 2026 ePrint paper by Agrawal, Modi, Yadav and Yamada. It gives a counterexample showing the evasive IPFE assumption of Hsieh, Lin and Luo (Eurocrypt 2024) is false in full generality. The attack extends the 2025 PRFE counterexample and needs only the weak inner product functionality, not pseudorandom function computation. The authors conclude that letting the adversary choose unrestricted private coins breaks the Evasive LWE family.

Evasive LWEEvasive IPFEPRFE+2

other· Added 20 Oct 2026, published 19 Oct 2026

eprint.iacr.orgpaper

New IND-CPA-D Attacks on BFV and BGV

New IND-CPA-D Attacks on BFV and BGV is an ACM CCS 2026 paper by Choe, Kang and Stehlé presenting three attacks on FHE schemes whose parameters rely on heuristic noise bounds. Two attacks recover the secret key and one breaks the IND-CPA-D game. Experiments use HElib for BGV and OpenFHE for BFV, where full key recovery takes minutes to hours.

BFVBGVOpenFHE+1
IND-CPA-Dbootstrapping failure attackCheon et al. CCS'24+3

other· Added 20 Oct 2026, published 19 Oct 2026

eprint.iacr.orgpaper

A Note on the Security of ECDSA with Presignatures or Biased Nonces

A Note on the Security of ECDSA with Presignatures or Biased Nonces (Couteau and Makriyannis, ePrint 2026/2545) examines alternative ECDSA modes built for faster distributed signing. It shows that the security of some variants used in deployed libraries is equivalent, in the generic group and random oracle model, to the average-case hardness of k-SUM. It also proves fine-grained lower bounds on generic group attacks against modes analyzed by Groth and Shoup (Eurocrypt 2022).

ECDSAk-SUMGroth and Shoup

other· Added 20 Oct 2026, published 19 Oct 2026

eprint.iacr.orgpaper

A Key-Recovery Attack on the GTLN Knapsack Cryptosystem via Continued Fractions

This ePrint paper (2026/2543) gives a key-recovery attack on the GTLN knapsack public-key cryptosystem of Gómez-Torrecillas, Lobillo and Navarro. Continued fractions recover small-denominator ratios of public-key differences, and gcd computations then yield private-key integers, the modulus and the shift, using only the public key. The Python implementation recovered the full private key in all 2,400 trials across 24 recommended parameter sets, each in under 0.05 seconds.

GTLN knapsack cryptosystemGómez-TorrecillasLobillo+1

other· Added 20 Oct 2026, published 19 Oct 2026

eprint.iacr.orgpaper

Provable Lattice Reduction in Nearly the Time of QR Factorization

Provable Lattice Reduction in Nearly the Time of QR Factorization (IACR ePrint 2026/2541, October 2026) presents a deterministic lattice-reduction algorithm with running time Õ(n^ω(1+log κ_col(B))), free of heuristic assumptions. Its implementation used fewer instructions than flatter (CRYPTO 2023) in all 153 runs on q-ary, NTRU-like, scaled q-ary and Coppersmith inputs. Median flatter-to-new instruction ratios are 1.55 for q-ary and 1.86 for NTRU-like inputs.

flatter
CoppersmithLLL

other· Added 20 Oct 2026, published 19 Oct 2026

eprint.iacr.orgpaper

Optimizing HQC with Enhanced Parallel Binary Polynomial Multiplication on GPUs

This paper presents an end-to-end GPU implementation of the HQC code-based key encapsulation mechanism. It speeds up GF(2) polynomial multiplication with a parallel Frobenius additive FFT and a Toeplitz matrix-vector mapping onto INT1 tensor cores. On an RTX 4090 the multiplier reaches 3,828k polymul/s, about 2.9x the earlier HIGH implementation. Full KEM throughput is 1.56x, 1.55x and 2.03x higher for keygen, encaps and decaps. Five thread-to-KEM mapping variants are tested on RTX 3090 and Jetson AGX Orin.

HQCCUDANVIDIA RTX 4090+1
HIGHFrobenius additive fast Fourier transformReed-Muller/Reed-Solomon coding+2

other· Added 20 Oct 2026, published 19 Oct 2026

eprint.iacr.orgpaper

Off-Key: Inconsistent MAC Keys Compromise Privacy in SPDZ-Family MPC

Off-Key is a privacy attack on SPDZ-family maliciously secure MPC protocols that exploits inconsistent MAC keys. Depending on the MAC check protocol, a corrupted party recovers a shared secret from one authentication check or tests guesses through selective failure. The authors show it in MP-SPDZ, SCALE-MAMBA and FANNG-MPC, where a corrupted party can use different keys across batches, threads or runs, and describe the preprocessing state that enforces key consistency.

MP-SPDZSCALE-MAMBAFANNG-MPC
Off-Keyselective failureMAC key inconsistency+1

other· Published and added 19 Oct 2026

eprint.iacr.orgpaper

Computing endomorphisms of superspecial principally polarized abelian surfaces in time and memory \(p^{4/5+o(1)}\)

Computing endomorphisms of superspecial principally polarized abelian surfaces is a cryptanalysis preprint by Marc Houben and Lam L. Pham, posted to IACR ePrint in October 2026. It gives an algorithm that, under a standard heuristic, finds a non-scalar polarized endomorphism in expected time and memory p^(4/5+o(1)). The abstract is the only text available, so the method and its effect on specific schemes are not described.

Marc HoubenLam L. Pham

other· Added 19 Oct 2026, published 18 Oct 2026

eprint.iacr.orgpaper

Revisiting the Security of VDOO

Revisiting the Security of VDOO is an ePrint paper (October 2026) on VDOO, a multivariate signature scheme submitted to China's NGCC program. It models VDOO as a multilayer Rainbow construction, keeps only the last oil space to get a generalized UOV instance, and applies wedge attacks. For the 512-bit parameter set it estimates 2^432 gates (reconciliation) and 2^379 gates (intersection), below the claimed level and the specification's figures.

VDOORainbowUOV
NGCCwedge attackreconciliation attack+1

other· Added 19 Oct 2026, published 18 Oct 2026

eprint.iacr.orgpaper

How Secure are NTRU+ Keys? Analysing the Best Module Attacks

ePrint 2026/2527 by Paola de Perthuis and Filip Trenkić analyses module-BKZ attacks on NTRU+, the South Korean KEM standard. It introduces relative canonical and coefficient embeddings and shows they agree up to scaling exactly when rad(c)/rad(ℓ) is 1 or 2. Simulation-based estimates show the best module attack saves 4 to 10 blocksizes, costing NTRU+ keys at most three bits of Core-SVP security. NTRU+ parameters stay safe in the overstretched regime.

NTRU+BKZ
Core-SVPoverstretched NTRUPaola de Perthuis+1

other· Added 19 Oct 2026, published 18 Oct 2026

securityweek.comarticle

US Cybersecurity Job Postings Fall 26% as AI Security Engineer Demand Soars

SecurityWeek summarises CyberSN's Cybersecurity Jobs Report. US cybersecurity postings fell 26.4% to 235,786 for January–September 2026, a four-year low. AI Security Engineer demand rose 268.3% and Cyber Data Scientist demand rose 203.5%. Penetration Tester (-45.9%), Threat Hunter (-40.0%) and CISO (-38.9%) postings dropped, and the CISO figure matches 2024 after an unusually strong 2025. Just under 15% of postings mention AI, peaking at 20.0% in September. The report counts postings by work required (CyberSN's 45-role taxonomy) rather than by job title, and it describes what changed, not why.

CyberSNJobSpikrCyberSN Taxonomy

other· Published and added 18 Oct 2026

eprint.iacr.orgpaper

GKS FHE: Security Analysis

"GKS FHE: Security Analysis" is a Cryptology ePrint Archive preprint (2026/2523, October 2026) giving a formal security analysis of the Gribov-Kahrobaei-Shpilrain private-key fully homomorphic encryption scheme. The abstract says the scheme needs no bootstrapping or de-linearization, gives bit-exact decryption, supports native encrypted search and has unbounded depth. The page shows only the abstract, so the analysis's methods and results are not visible.

GKS FHE

other· Added 19 Oct 2026, published 18 Oct 2026

ethereum-magicians.orgpaper

Post-Quantum Stateless Steganography & MTU Bounds: Bridging P2P Censorship Resistance to Quantum Networks

Forum announcement of a Zenodo preprint on post-quantum migration for censorship-resistant P2P steganographic tunnels. It argues that ML-KEM's prime modulus (q=3329) makes naive bit-packed ciphertexts statistically distinguishable from uniform noise, which gives a cheap passive DPI distinguisher. It also argues that composite PQ 0-RTT envelopes over 4.4 KB force fragmentation, which requires stateful reassembly before AEAD verification and reopens memory-exhaustion DoS in eBPF/XDP filters. Proposed fixes are algebraic uniformization (LWR lattices or inverse rejection sampling), sub-MTU hybrid or pure-PQ envelopes (Falcon-512, signcryption), and Fujisaki–Okamoto implicit rejection for constant-time silent drops. Aimed at Ethereum validator, libp2p and RPC transports facing harvest-now-decrypt-later threats.

eBPFXDPlibp2p+1
ML-KEMML-DSAHarvest-Now-Decrypt-Later+8

other· Published and added 17 Oct 2026

eprint.iacr.orgpaper

Superspecial points on Humbert surfaces and the probability of (N,N)-splitting

Determines, to first order in 1/p with an explicit error bound, the proportion of superspecial principally polarized abelian surfaces over F_p-bar (p ≡ 3 mod 4) that are optimally (N,N)-split. The expected number of optimal splittings is exactly 5N·J_2(N)(p-1)/(p²+1), so the split proportion is about 5N·J_2(N)/p. This gives the stationary target density of the splitting-detection attack on the dimension-two superspecial isogeny problem, which was previously known only from experiments or a one-sided bound. The proofs use Siegel's mass formula and genus averages over refined Humbert invariants, and every formula was checked by exact computation at twelve primes.

splitting-detection attackRichelot random walkHumbert surfaces+3

other· Published and added 17 Oct 2026

eprint.iacr.orgpaper

Efficient Fixed-Point Implementation of Mitaka

Presents a fixed-point C implementation of the Mitaka signing algorithm, a simpler, parallelizable Falcon (FN-DSA) variant. It replaces MitakaZ's wide integral Gram root decomposition with a fixed-point square Cholesky decomposition, which cuts the cost of integer Gaussian sampling, and proves bounds on intermediate values and representation errors without empirical assumptions. Signing averages 361 kcycles (Mitaka-512) and 707 kcycles (Mitaka-1024) on AVX2, and 4.0 and 7.8 Mcycles on an STM32F411 Cortex-M4F. This makes floating-point-free lattice signatures practical on constrained devices.

MitakaFalconC+1
MitakaZFN-DSAGaussian sampling+1

other· Published and added 17 Oct 2026

coindesk.comarticle

‘Wow, it’s a real discovery’: Claude cracks a 25-year NSA number mystery

CoinDesk reports that an Anthropic internal research model traced five NSA-supplied NIST elliptic-curve seeds to the C library generator lrand48 fed with 1997–98 timestamps. It matched P-256's published seed at the 1,842nd candidate, in under 30 minutes and without being told about the earlier "forgotten phrase" theory. This makes a hidden backdoor in the NIST curves less likely, though why some candidates were skipped and how other curve parameters were chosen remain unexplained. The article also explains why Bitcoin's secp256k1 was never part of the question, and that quantum risk is a separate threat.

ClaudeAnthropiclrand48+1
NISTNSAP-256+9

AI Security, other· Published and added 17 Oct 2026

eprint.iacr.orgpaper

Associated-Data Correlations in Eevee: Deterministic Forgeries against Nonce-Misuse Security

Cryptanalysis of the Eevee forkcipher-based AEAD modes Umbreon and Espeon, which claim online AE security under nonce reuse. Associated-data correlations give probability-one non-empty-message forgeries with three encryption queries and one verification query. The paper adds an affine treatment of partial final blocks (n-r+3 queries, or n-r+2 with adaptive choices). It also checks the published Umbreon attack with the official ForkSkinny primitive and reports a two-query attack accepted by the unmodified public C modes.

EeveeForkSkinnyC
UmbreonEspeonnonce misuse

other· Published and added 17 Oct 2026

anthropic.comwriteup

Claude reveals ECDSA curve origins

Anthropic's Frontier Red Team reports that Claude recovered how the NIST P-192/224/256/384/521 and ANSI X9.62 curve seeds were generated. They are outputs of the C library's lrand48 LCG seeded with 1997–98 Unix timestamps, not hashes of a passphrase. The method scanned for weak-PRNG signatures, then used LLL lattice reduction to recover the truncated LCG state and stepped it back to srand48 initialization. Claude also traced some base points to the FreeLIP/NTL random generator. Reproducible Python is included. The authors say this is not an attack and makes deliberate backdoors less plausible. The B-163 seed and the base points of P-224/256/384/521 and the binary curves remain unexplained.

ClaudeNTLFreeLIP+1
NISTECDSANIST P-256+16

other· Added 17 Oct 2026, published 16 Oct 2026

a16zcrypto.comarticle

Fast post-quantum signature aggregation with lattice SNARKs

a16z crypto announces Aerie, a lattice-SNARK system that aggregates Falcon-512/1024 signatures into one ~66 KiB proof. On an M4 Max laptop it handles 32,768 signatures in 0.65 s (~50k/s), verifies in 54 ms, and costs ~42 bytes per signature. It benchmarks against Orthus and Ethereum's leanVM hash-based XMSS aggregation, and argues that recursion-free lattice aggregation is simpler than hash-only designs. It also covers Falcon's hardware-wallet and side-channel constraints and why private payments need lattice encryption such as ML-KEM.

FalconEthereumSolana+1
AerieAkitaLattice Jolt+17

other· Published and added 16 Oct 2026

a16zfrontier.comarticle

Fast post-quantum signature aggregation with lattice SNARKs

Aerie is an a16z crypto and LayerZero Labs system that aggregates Falcon-512 and Falcon-1024 lattice signatures into one lattice SNARK. On an Apple M4 Max it aggregates 32,768 Falcon-512 signatures in 0.65 seconds, with 54 ms verification and about 42 bytes per signature. The post compares it with Ethereum's hash-based leanVM and XMSS plan and Orthus, and covers Falcon signing limits on hardware wallets.

AerieFalconEthereum+2
AlpenglowleanVMXMSS+11

other· Added 22 Oct 2026, published 16 Oct 2026

eprint.iacr.orgpaper

CHAMP: Cayley HAshing with Matrix Products

CHAMP is a Cayley hash function that hashes binary strings by mapping each bit to a 2x2 matrix over a finite field and multiplying the matrices. The product's semigroup structure gives the hash homomorphic properties. The authors (Demin, Ovchinnikov, Shpilrain) discuss its collision resistance, implementation and performance. Cayley-style hashes have a history of structural attacks, so the security analysis is what a cryptographer would check.

CHAMPCayley hash functionsAlexander Demin+2

other· Added 17 Oct 2026, published 16 Oct 2026

eprint.iacr.orgpaper

Analysis of the Multi-Key Optimization for SPECK

The paper revisits the multi-key optimization for SPECK, a code-based signature scheme that uses the Permutation Code Equivalence Problem (PEP) as a trapdoor for the Permuted Kernel Problem (PKP). Each SPECK round has soundness error 1/2, which inflates signatures, and the SPECK authors had warned that naively using multiple public keys creates security concerns. The authors analyse those concerns, give conditions and parameter constraints under which multiple keys can be integrated securely, and show that conservative parameters perform poorly but leave room for improvement. They also build a ring signature scheme on the same construction.

SPECKLESSPermuted Kernel Problem+6

other· Added 17 Oct 2026, published 16 Oct 2026

eprint.iacr.orgpaper

SLEEK: Sparse Quasi-Cyclic Codes with Closed-Form DFR Key Encapsulation

Introduces SLEEK, a QC-MDPC code-based KEM using a three-iteration parallel bit-flipping decoder and a closed-form decoding-failure-rate (DFR) estimate, enabling parameters with analytically bounded failure probability and standard IND-CCA transforms. SLEEK-LT targets IND-CCA for long-term keys; SLEEK-E targets IND-CPA for ephemeral keys using a new QC key structure with security equivalent to QC-MDPC and cheaper key generation. Parameter sets cover 80/128/192/256-bit security, and the optimized AVX2 implementation gives ciphertexts 4.9x smaller than HQC (47% slower) and 1.3x–2.7x faster than BIKE.

AVX2
SLEEKSLEEK-LTSLEEK-E+5

other· Added 17 Oct 2026, published 16 Oct 2026

eprint.iacr.orgpaper

I Want to Ride My BIKE: Customizing Bit-Flipping Decoders for Ephemeral Key KEMs

ePrint paper presenting the first optimized implementation of the BF-max bit-flipping decoder for the code-based KEM BIKE, combined with other decoders to trade off decoding failure rate, runtime, public-key and ciphertext size in ephemeral-key settings. It cuts public-key and ciphertext sizes by 7.8% versus LeanBIKE at similar speed and DFR, and gives a combined size 22% below BIKE and 2.79x below HQC. It shows BIKE can fit constrained protocols such as IKEv2, which matters for practical post-quantum migration.

BIKEHQCIKEv2
BF-maxLeanBIKEQC-MDPC+1

other· Added 17 Oct 2026, published 16 Oct 2026

eprint.iacr.orgpaper

safeRNSgcd: Accelerating Falcon key generation with RNS in SafeGCD

ePrint paper presenting safeRNSgcd, which computes the single Bézout coefficient needed at the deepest level of Falcon's NTRU solver while keeping large integers in a residue number system. Centered explicit CRT recovers the exact low bits needed by SafeGCD batches using single-word fixed-point arithmetic. A C implementation integrated into ntrugen reduces inversion and private-key basis-generation cost on a Raspberry Pi 5 and two x86-64 CPUs, versus the original ntrugen and a variant that skips the unused coefficient.

FalconntrugenSafeGCD+2
safeRNSgcdCesare HuangBo-Yin Yang

other· Added 17 Oct 2026, published 16 Oct 2026

eprint.iacr.orgpaper

Shorter Hash-Based Signatures via Guarded Sharing in a DAG Model

Proposes "guarded sharing", a technique that moves few-time signatures in SPHINCS-style stateless hash-based schemes from a tree model to a DAG model. Combined with bucket thinning, hash chains and rejection sampling, it yields BGS-CC, which improves on the prior best few-time scheme BPORS-C+BFP. For 128-bit security and a use quota of Q=2^24 it gives 2,228-byte signatures, the first SPHINCS-based stateless signature shorter than ML-DSA-44's 2,420 bytes. This matters for PQ migration because signature size is the main drawback of SLH-DSA.

SLH-DSAML-DSA
BGS-CCBPORS-C+BFPSPHINCS+1

other· Added 17 Oct 2026, published 16 Oct 2026

blog.talosintelligence.comarticle

The Q3 Vulnerability Pulse: Discovery ≠ Exploitation

Talos Threat Source newsletter arguing that record CVE volume (over 70k by end of Q3, six-digit CVE IDs) is not the same as exploitation. KEV grew only 37% YoY against 105% for CVEs, about a third of KEV entries are CVEs from 2025 or earlier (a patch gap), and 29% of 2026 KEV CVEs were added on their publication date. It also notes the new KEV "forensicTriage" column (BOD 26-04), summarizes the Talos/Insikt report on UAT-6275 espionage against CIS governments with GitHub-hosted payloads and a WinRAR exploit, and lists weekly headlines.

CISA KEVGitHubPowerShell+2
CVE-2026-104935CVE-2014-125110CVE-2015-1000013+7

Threat Intel, other· Published and added 15 Oct 2026

eprint.iacr.orgpaper

GhostFaceMPC: Privacy-Preserving Face Recognition with Multi-Party Computation

GhostFaceMPC is presented as the first end-to-end face recognition system that runs a deep CNN feature extractor (GhostFaceNet) and the matching step under secure multi-party computation. Raw images and biometric embeddings are never exposed during extraction, storage or matching. The authors contribute an MPC-friendly quantization of GhostFaceNet and circuit optimizations that make the approach practical, and they release code at crypto-unict/GhostFaceMPC.

GhostFaceNet
GhostFaceMPC

other· Published and added 15 Oct 2026

eprint.iacr.orgpaper

Structural Cryptanalysis of the Eevee AEAD Family

ePrint paper cryptanalysing Eevee (Umbreon, Jolteon, Espeon), forkcipher-based AEAD modes proposed at CCS 2023 for IoT-to-cloud computation. It gives a two-encryption AD-free prefix distinguisher, a four-encryption nonce-misuse distinguisher, a deterministic AD-only forgery, and nonce-respecting forgeries on Jolteon and Espeon (fresh one-block forgery reusing the tag; arbitrary AD substitution). It traces these to proof flaws (online-prefix consistency, domain separation, checksum freshness), derives design requirements, and concludes the failures are in the mode design, not the C implementation.

C
EeveeUmbreonJolteon+2

other· Published and added 15 Oct 2026

eprint.iacr.orgpaper

Robust ECDSA Threshold Signing at Scale

Presents a robust threshold ECDSA signing protocol for t ≤ (n-1)/3 corrupted signers. It batch-computes pre-processing material for fast online signing and scales to many signers, for uses such as bridging consensus between blockchains. It combines batched verifiable secret sharing (Fitzi & Hirt), randomness extraction (Beerliova-Trubiniova & Hirt), efficient share opening (Damgård & Nielsen) and Attema–Cramer zero-knowledge proofs. The authors implement it and show it is practical for large n.

ECDSACarsten BaumAnders Dalskov

other· Published and added 15 Oct 2026

eprint.iacr.orgpaper

Threshold Post-Quantum E-Voting from Lattice Commitments

T-EVOLVE extends the lattice-commitment e-voting protocol EVOLVE to threshold tallying. Votes are Shamir-shared, so any t of n authorities can finish the tally. Privacy holds against t-1 colluding authorities and verifiability holds even if all of them collude. The voter proves her committed shares form a Reed-Solomon codeword whose value at zero is a valid vote. Complaints about ciphertexts that do not decrypt are publicly verifiable, using an LWE-instantiable encryption scheme with publicly verifiable opening. Privacy, verifiability, individual verifiability and robustness are proven in the classical random oracle model, and the verifiability reduction is not tight. In a C implementation, a yes/no ballot for four authorities takes 109 KB, and an authority aggregates 10^4 ballots in about three minutes on one core.

C
T-EVOLVEEVOLVEShamir secret sharing+2

other· Added 17 Oct 2026, published 15 Oct 2026

eprint.iacr.orgpaper

Reaction Attack on CKKS Deployments with Asymptotically Optimal Query Complexity

Shows a protocol-level reaction attack on CKKS homomorphic-encryption deployments that publish coefficient-to-slot (C2S) evaluation keys and let the client return a 1-bit validity response. A malicious evaluator shifts a public encryption key, uses the public C2S layer to repack it into a ciphertext whose validity depends on one secret coefficient, and recovers a ternary secret key with O(H) queries, within a factor 2/log2(3) of the entropy lower bound. Each query is re-randomized with a fresh encryption of zero to evade trivial detection. The authors implemented it end to end in Lattigo v6.2.0 and recovered full keys across four standard CKKS parameter sets. It does not break RLWE or CKKS IND-CPA security.

LattigoCKKS
reaction attackcoefficient-to-slotRLWE+1

other· Published and added 15 Oct 2026

eprint.iacr.orgpaper

FAEST on GPUs: Addressing Field Multiplication as a Bottleneck

ePrint paper presenting an NVIDIA GPU implementation of FAEST (a post-quantum signature scheme built on VOLE-in-the-Head and QuickSilver), covering key generation and OWFProve/OWFVerify for standard and EM constructions in s and f variants. Profiling shows field multiplication takes about 82% of FAEST-128f signing time once AES is hardware-accelerated. Using PTX clmad carry-less multiplication plus Karatsuba, it reaches up to 26.6x kernel throughput and about 2.9-3.1x full 256-bit OWFProve throughput over the software-multiplication build on an RTX A5000.

CUDANVIDIA RTX A5000PTX+1
FAESTQuickSilverVOLE-in-the-Head+3

other· Published and added 15 Oct 2026

bankless.comarticle

Crypto's Quantum Defense Is Being Built in the Open

Bankless article on Eigen Labs' Yukon platform, which runs open challenges where researchers and AI agents attack and improve cryptography. It covers ECDSA.fail (quantum circuit cost for attacking Bitcoin/Ethereum ECDSA, cut about 88% from baseline), HashSmash (SHA-256 weakness hunting, so far only on reduced versions), sig.golf (hash-based signatures), StarkWare's Quantum Safe Bitcoin (cost down from about $320 to $59) and better.codes (provable security raised from 64 to about 68 bits). The argument is that public, measurable attack-cost data helps defenders prepare better than withholding circuits does. All gains are theoretical and no quantum computer has run an attack at this scale.

YukonBitcoinEthereum+1
Eigen LabsECDSA.failHashSmash+10

other, AI Security· Published and added 14 Oct 2026

securityweek.comarticle

ICS Patch Tuesday: Siemens Issues 17 Advisories, Rockwell Fixes ArmorBlock Takeover Flaw

Roundup of ICS Patch Tuesday advisories. Siemens published 17 advisories, including critical flaws in Simatic S7-1500 CPUs (400+ flaws in the GNU/Linux subsystem), Industrial Edge and Ruggedcom Crossbow SAC. Rockwell fixed a critical 1732E ArmorBlock flaw that lets an unauthenticated attacker change the web server password and take over the admin account, plus a DoS bug. Also covered: two high-severity Schneider Electric advisories (Pro-Face STW6000/Harmony STW6 and Sage RTUs), CISA and CERT@VDE advisories, and other vendor advisories since the last Patch Tuesday. ABB's dynovaPRO credential-reset bypass came with 26 password change events across 9 customers that may indicate reconnaissance.

Simatic S7-1500Ruggedcom1732E ArmorBlock+2
SiemensSchneider ElectricRockwell Automation+13

Hardware & RF, other· Published and added 14 Oct 2026

eprint.iacr.orgpaper

Post-Quantum Certificate-Based PSK Provisioning for WireGuard via Mutual TLS, DTLS, and QUIC: Design and Performance Study

The paper proposes a post-quantum architecture for WireGuard that leaves the core protocol unchanged. A mutually authenticated TLS 1.3 control channel runs over TCP, UDP (DTLS) or QUIC and uses ML-KEM key establishment, with X.509 certificates from a PKI signed with ML-DSA. A shared secret derived from the session's exported keying material is injected into WireGuard's native PSK interface. A Tamarin model of the TLS–WireGuard composition layer checks secrecy, binding and provisioning-order properties and identifies the conditions needed for secure deployment. The authors benchmark handshake latency and CPU time for classical, pure-PQ and hybrid key establishment across the three transports, and compare against the Rosenpass PQ WireGuard baseline.

WireGuardVPN
ML-KEMML-DSARosenpass+5

other· Added 15 Oct 2026, published 14 Oct 2026

eprint.iacr.orgpaper

Connecting Cryptanalytic Distinguishers through Divisibility

Paper that links linear, integral, differential-linear and restricted differential distinguishers through two-way conversions with explicit divisibility guarantees and data complexity. It gives automated MILP/SAT models (Walsh and ultrametric representations, exact mix-basis models) and a black-box FWHT histogram search for zeros and finite divisibility. It improves Beyne–Verbauwhede divisibility bounds in 674 SIMON cases (e.g. 2^5 to 2^11 on 9-round SIMON32) and PRESENT. It also gives first higher-divisibility proofs for 8-round SPECK and BEANIE, new bounds for GIFT-64 and Ascon, and new properties on RC5, ChiLow-32, KeeLoq and KATAN32.

SIMONSPECKPRESENT+3
Hosein HadipourBeyne and VerbauwhedeBEANIE+4

other· Published and added 14 Oct 2026

eprint.iacr.orgpaper

Refined Application of the XL Algorithm within the Algebraic Approach to the Regular Syndrome Decoding Problem

Furue and Aikawa build and analyze algebraic attacks on the Regular Syndrome Decoding Problem (RSDP), which underlies code-based post-quantum schemes. They extend the Wang et al. hybrid algorithm to allow an arbitrary XL solving degree d, and add two variants: an XFL-based one (partial Gaussian elimination plus variable guessing) and a WXL-based one that exploits Macaulay matrix sparsity. Complexity analysis shows the WXL variant with d>2 wins for small block size β, while the original hybrid wins as β grows. This matters for setting RSDP-based scheme parameters.

Regular Syndrome Decoding ProblemSyndrome Decoding ProblemXL algorithm+4

other· Published and added 14 Oct 2026

eprint.iacr.orgpaper

Accelerating Pollard Rho with GPU Field Arithmetic on NVIDIA Blackwell

Preprint that speeds up Pollard rho on GPUs by rebuilding field arithmetic: packed normal-basis representation, the CUDA 13.3 PTX carry-less multiply (clmad), and three-input logic instructions. On one RTX PRO 6000 Blackwell it goes from 0.85 to 14.64 billion iterations/s (17.2x) on the Certicom ECC2K-130 challenge, which puts the whole challenge under five GPU-years. The same levers give 1.52x on P-256 and 2.61x on P-384, which leaves P-256 about 6e21 card-years away. It also reports twelve GPUs from Turing to Blackwell, an FPGA engine on AWS F2 and a campaign that covered 5.4% of the expected work, with code and a Dockerfile on GitHub (rho-blackwell). It claims no improvement on the generic-group bound.

CUDANVIDIA BlackwellAWS+1
Pollard rhoECC2K-130Certicom challenge+5

other· Published and added 14 Oct 2026

coindesk.comarticle

Coinbase, which holds 5% of all bitcoin, wants the quantum fix started now

CoinDesk summarizes Coinbase's recommendations for making Bitcoin quantum-resistant before a cryptographically relevant quantum computer (CRQC) can derive private keys from public keys. The proposals are: a transaction format that can carry new signature types (P2MR/BIP-360, P2TRv2), staged hybrid "1-of-2" spends with ECDSA/Schnorr or a post-quantum key, and stateless options alongside stateful schemes to avoid key-reuse forgery. They also ask that evaluation favor constant-time, RNG-failure-safe implementations, require MPC compatibility, and handle dormant or late-migrating coins as a separate debate. It is a useful overview of the defensive migration design space, but it is secondary reporting and not the primary Coinbase paper.

BitcoinECDSA
CoinbaseCRQCBIP-360+3

other· Published and added 14 Oct 2026

eprint.iacr.orgpaper

Snapshots of TEE-Based Encrypted Databases Leak Plaintext Histograms via Dendrochronology

ePrint entry for an ACM CCS 2026 paper in the "Attacks and cryptanalysis" category. By its title and keywords, it shows that snapshots of encrypted databases built on trusted execution environments leak plaintext frequency histograms, using a technique called "dendrochronology". The abstract and full text are embargoed until the end of October 2026, so the attack mechanics are not available yet. It matters to anyone assessing the real leakage of TEE-backed encrypted databases against snapshot adversaries.

Zachary EspirituACM CCS 2026

other· Added 14 Oct 2026, published 13 Oct 2026

securityweek.comarticle

Employee Arrested After Listening Device Found in OpenAI Conference Room, FBI and the Company Say

SecurityWeek reports that an OpenAI engineer, Abdulrahman Alfozan, was arrested by the FBI and charged with illegally intercepting oral communications. A recording device, concealed in toilet paper, had been plugged into a USB port on the back of a conference-room TV. OpenAI says it used its own models to analyse the device and identify the employee, and that it has no indication model weights, source code or customer data were accessed. The complaint cites CCTV footage, a camera later added to the room, and the employee's productivity-tool queries about meeting rooms and calendars.

OpenAI
Abdulrahman AlfozanFBI

other· Published and added 13 Oct 2026

rapid7.comadvisory

Patch Tuesday - October 2026

Rapid7's analysis of Microsoft's October 2026 Patch Tuesday, which covers 1,413 vulnerabilities, 1,102 of them in Windows. It highlights the exploited Windows Shell Mark of the Web bypass (CVE-2026-96951) and the publicly disclosed .NET Framework WDAC bypass (CVE-2026-108398). It also covers five no-interaction Outlook preview-pane RCEs, the Edge advisories that list no CVEs, and end-of-support dates for Server 2012/2012 R2, Office 2021, Exchange 2016/2019 and Windows 11 24H2. The page text is truncated, so the later CVE tables are not seen.

Windows.NETMicrosoft Edge+2
CVE-2026-96951CVE-2026-108398CVE-2026-70242+63

Blue Team & Detection, other· Published and added 13 Oct 2026

sfstandard.comarticle

OpenAI engineer arrested in bugging of executive conference room

Reports the federal arrest of OpenAI engineer Abdulrahman Alfozan, charged with using a device to intercept oral communications after an encrypted audio recorder was found in a San Francisco executive conference room. The recorder was hidden in toilet paper and plugged into a TV's USB port. Prosecutors say he used an internal productivity tool to scout rooms and calendars, and a chatbot account tied to his spouse asked how to build, encrypt and remotely access a recorder. OpenAI's technical surveillance countermeasures team found the device, and OpenAI says it used its own models for forensic analysis. It then restricted his access in stages, timed with the FBI, before firing him. A useful insider-threat case study that also covers physical security.

OpenAI
Abdulrahman AlfozanFBItechnical surveillance countermeasures

other· Published and added 13 Oct 2026

securityweek.comarticle

Google Partially Reverses Chrome Bug Bounty Cuts

Google is raising Chrome Vulnerability Reward Program payouts for memory safety bugs. The base rate goes from $500 to $2,000, with up to $20,000 for browser, GPU and network process bugs and up to $8,000 for renderer use-after-free and memory write bugs. V8 sandbox bugs move to a flat $5,000 and V8 logic bugs to $4,000. A $2,000 fuzzer bonus returns, and submissions made after April 30, 2026 are rewarded under the new rules. The rates are still well below the pre-April 2026 levels. The article also notes that Google temporarily closed the OSS VRP to product vulnerability submissions because of a flood of AI-generated reports.

ChromeV8
Chrome Vulnerability Reward ProgramOSS VRPV8 sandbox+1

other, AppSec· Published and added 13 Oct 2026

eprint.iacr.orgpaper

Hybrid Quantum–Computational Key Distribution with Reduced Assumptions (Short Paper)

Short paper analysing the HM-QCT hybrid quantum–computational time-lock QKD protocol (Mazzoncini et al., 2025). It spells out the two "harvest now, decrypt later" strategies (quantum memory and classical memory) and shows each is excluded by exactly one of the two assumptions: short-term encryption and low-fidelity quantum storage. It then proposes HM-PRF, which replaces the short-term encryption with a locally evaluated pseudorandom function, so security needs only one-way functions rather than a predicted lasting gap in quantum memory technology.

HM-QCTHM-PRFharvest now, decrypt later+3

other· Added 14 Oct 2026, published 13 Oct 2026

eprint.iacr.orgpaper

Leakage-Resilient Incompressible Cryptography: Constructions and Barriers

Introduces leakage-resilient incompressible cryptography, a security model combining leakage resilience (partial key leakage plus full ciphertext) with incompressibility (full key but only part of the ciphertext or signature). It gives a transformation from incompressible symmetric-key encryption (SKE) to leakage-resilient incompressible SKE, a leakage-resilient incompressible PKE built from a new leakage-resilient non-committing KEM, and an incompressible SKE with ciphertext and compression rate 1/2 using invertible extractors. It also gives a leakage-resilient incompressible signature scheme in the random oracle model under DCR or LWE plus Decisional Linear. Black-box impossibility results show barriers to improving these parameters.

DziembowskiDecisional Linear assumptionLWE+3

other· Added 14 Oct 2026, published 13 Oct 2026

eprint.iacr.orgpaper

Cube Attacks with Elimination Strategy: Key Recovery Attacks on Trivium

Introduces a cube-attack framework with an elimination strategy. It finds key conditions and cubes whose conditional superpolies are cheap to compute, then solves the resulting equation systems to recover key bits. The supporting techniques are a nested coefficient solver, conditional monomial prediction, an automated cube search combining numeric mapping with monomial prediction, and two testing methods for large equation systems. Against round-reduced Trivium it gives a practical key recovery at 840 rounds (complexity below 2^55, 77.8% success) and at 845 rounds (below 2^56, 98.1% success on 59.1% of keys). It also gives a theoretical weak-key attack at 855 rounds for 2^74 keys. These are the best known results, extending prior practical attacks by 13 rounds and theoretical attacks by 4.

Trivium
cube attackmonomial predictionsuperpoly+2

other· Added 14 Oct 2026, published 13 Oct 2026

eprint.iacr.orgpaper

Causal Awareness in End-to-End Encrypted Group Messaging

Cryptography paper that extends Chen and Fischlin's two-user Signal analysis (Eurocrypt 2024) to group chats. It introduces "causal awareness": a receiver can reconstruct part of the causal context in which an accepted message was sent. Network delay or adversarial interference can otherwise show an authentic message in a misleading context. Senders transmit records of what they have sent and received, and receivers verify these records and compare them with their own. The paper gives correctness and security definitions parameterized by how much causal information must be recovered, baseline constructions with proofs, and checkpoint-aided and server-aided variants. It also discusses how to surface this information in a messenger's UI.

Signal
Chen and Fischlincausal awarenessLamport clocks+1

other· Added 14 Oct 2026, published 13 Oct 2026

eprint.iacr.orgpaper

Master-Key Recovery from Internal Activation Leakage in ReLU Realizations of Camellia

The paper builds explicit ReLU neural-network realizations of Camellia-128/192/256 from exact Boolean gates, S-box selectors and bit permutations, and reports known-answer-test agreement for Camellia-128. It shows that whitening and round-key quantities leaked from internal activations determine the master key through public key-schedule identities. Under a synthetic internal-oracle model, symmetric real-valued perturbations recover subkey bits with 128 queries (Camellia-128) or 256 (Camellia-256). Camellia-192 is handled by deterministic key-schedule inversion from direct access to round keys. All 3,000 trials (1,000 keys per variant) recovered the key exactly. The authors state this is not a plaintext/ciphertext-only attack on standard Camellia.

Camellia
Kwangjo Kim

other· Added 14 Oct 2026, published 13 Oct 2026

eprint.iacr.orgpaper

On Secure Sorting and Its Application to Privacy-Preserving Graph Pattern Matching

Marcel Keller's ePrint compares the two fully secure MPC sorting approaches, Quicksort (Araki et al., CCS'21) and radix sort (Asharov et al., CCS'22). The comparison covers a range of parameters, for both honest- and dishonest-majority settings. The paper then extends the sparse matrix multiplication of Damie et al. (CODASPY'26), which avoids oblivious RAM, so the output comes out in the same format as the inputs. That makes repeated multiplication of graph adjacency matrices possible, which the paper uses to find cycles and scatter-gather patterns associated with money laundering. The result is privacy-preserving anti-money-laundering detection.

Marcel KellerAraki et al.Asharov et al.+2

other· Added 14 Oct 2026, published 13 Oct 2026

eprint.iacr.orgpaper

On the Expected Number of Iterations in ML-DSA Signing: A Complete Accounting of the Rejection Conditions

ePrint paper showing that FIPS 204 Table 1's expected iteration counts for the ML-DSA signing loop cover only the line-23 validity checks (z and r0 norms). They omit the two line-28 encoding-correctness checks (‖c·t0‖∞ and hint weight). It accounts for all four conditions: z by exact counting, c·t0 by an Irwin-Hall tail, and hint weight by a closed-form conditioned per-coefficient probability with a Monte Carlo tail estimate. Corrected expected iterations are 4.36, 5.14 and 3.91 for ML-DSA-44, -65 and -87, within 0.14% of an end-to-end measurement and consistent with NIST's FIPS 204 errata.

CRYSTALS-Dilithium
ML-DSAFIPS 204NIST+2

other· Added 14 Oct 2026, published 12 Oct 2026

wired.comarticle

Feds got warrants to use fake cell towers to hunt down Don Lemon's producer

WIRED reports that federal agents obtained warrants in Minnesota and Pennsylvania to use cell-site simulators (Stingrays/IMSI catchers) to locate Jerome Richardson, a producer for Don Lemon charged over the Cities Church protest. Agents also applied for simulator warrants and pen register orders targeting journalist Georgia Fort and others. The piece notes that simulators collect data from bystanders' devices, that affidavits contained a false claim about chanting, and that WIRED used EFF's detection software to find signs of a simulator near the 2024 DNC in Chicago.

StingrayIMSI catchercell-site simulator+8

other· Published and added 12 Oct 2026

eprint.iacr.orgpaper

CUTS: Chained Uniform-sum Tree Signatures

The paper analyses stateful hash-based signatures whose key is a tree of hash chains, and asks what a second signature from the same one-time key reveals after state loss or rollback. It proves that the values derivable from several signatures are exactly the union of those from each signature alone. It also bounds forgery after b signatures in the classical random-oracle model by a combinatorial coverage exponent λ_b, including when the signer grinds a counter. It then introduces CUTS, a scheme on one binary tree whose chain positions sum to a fixed value S and whose signature size and verification cost do not depend on tree height. One parameter set has 1,424-byte signatures and λ_2 ≥ 128.6. A counter variant, CUTS+C, gives a proven grinding gain.

CUTSCUTS+C

other· Added 14 Oct 2026, published 12 Oct 2026

Showing 120 of 170

Show more