Can Frontier Models See Past a Decoy? Elorian Tests Visual Reasoning
DecoyCount is a benchmark from Elorian and Mercor with 1,660 items that tests whether models count objects or fall back on visual shortcuts. Frontier models scored below 50%: GPT-6 Astra led with 43.17%, ahead of Gemini-3.8-flash (32.71%), Qwen3.8-max (28.31%) and Claude-Fable-5.1 (25.22%). CEO Andrew Dai says Elorian's Glimpse model scored 50.48% in a single internal run without tools, and contrasts visual reasoning with world models such as Atlas and Genie 4.
 latent.spacearticleAdded 28 Oct 2026, published 29 Oct 2026🧠 AI
 Atlassian Patches 75 Flaws in Data Center and Server Products
Atlassian's October 2026 security bulletin lists 162 high and 14 critical third-party vulnerabilities across Bamboo, Bitbucket, Confluence, Crowd, Fisheye/Crucible, Jira Software and Jira Service Management. SecurityWeek counts 75 unique CVEs, six critical, in Tomcat, Bouncy Castle, Netty and Apache SSHD. Atlassian rates them non-critical for its use, reports no exploitation, and the critical CVE-2026-65905 appears on the portal but not in the bulletin.
 securityweek.comarticlePublished and added 23 Oct 2026🛡️ Security
- Using thousands of AI agents to uncover new leads in biological data
Distributed biological reasoning is an approach in which thousands of GPT-Rosalind agents each analyzed one gene disruption in a whole-brain CRISPR atlas of millions of mouse brain cells, searched literature, and proposed mechanisms. OpenAI, PerturbAI and Scripps Research finished in 32 minutes. Distributed agents cited over 700 references versus 11 for a single agent, and blinded experts preferred their interpretations. Leads included Tsc1/Tsc2 differences and DCTN1 with cholesterol.
 openai.comarticlePublished and added 21 Oct 2026🧠 AI
- Dark Web Intelligence (@DailyDarkWeb) on X
DailyDarkWeb update on CVE-2026-21589, a pre-auth file-read flaw in Atlassian Data Center products. The CVE record was rejected on 16 October 2026 with a generic reason and no replacement ID, but Atlassian's advisory (CVSS v4.0 9.3, Critical) and the CISA KEV listing (added 15 October, federal due date 18 October) remain. The analyst note says to keep patching to the fixed versions and track versions, not only the CVE ID.
 x.comthreadAdded 19 Oct 2026, published 18 Oct 2026🛡️ Security
 SoK: PIAtlas: Decomposing the Unbounded Prompt Injection Attack Space
PIAtlas is a taxonomy of prompt injection attacks organized by how the injected instruction subverts the model, with six mechanism classes as roots of a technique and sub-technique hierarchy. The authors release PICorpus, a license-clean collection of public prompt-injection datasets, and map thousands of records to PIAtlas under a human-verified protocol. Results show attacks combine several techniques from few mechanisms, agent benchmarks cover only part of the space, and adaptive attackers favor mechanisms that curated benchmarks underrepresent.
 arxiv.orgpaperAdded 21 Oct 2026, published 18 Oct 2026🛡️ Security
- AI Security Wiki: Governance, Risk, Standards and Test Cases
A vendor-neutral AI Security Wiki acting as an implementation layer for enterprise AI adoption: risk methodology, AI risk register, control objectives library, domain standards (browser/IDE AI, runtime apps, agentic AI, sovereignty), vendor evaluation framework, and audit/evidence checklists. It includes a 653-case product evaluation test library across 17 lifecycle layers and 6 emerging domains, plus regulatory hubs for GCC, EU, Australia, Brazil, Canada, China, India, Japan, Singapore, South Korea, UK and US, and crosswalks to FINOS AIGF, NIST AI RMF, ISO/IEC 42001, OWASP, MITRE ATLAS, ISO 27001 and others. Useful as a template and evidence source for teams building AI governance and assurance programmes.
 nachi065.github.iootherAdded 15 Oct 2026🛡️ Security
- Attackers Target Critical Atlassian Vulnerability Within Hours of PoC Publication
Attackers began exploiting CVE-2026-21589, a critical CVSS 9.3 unauthenticated file-read flaw shared by Atlassian Bitbucket, Confluence, Jira, Jira Service Management, Bamboo, Crowd, Crucible and Fisheye Data Center products, within hours of WatchTowr publishing technical analysis and PoC code. WatchTowr showed that when Jira is integrated with Crowd, the flaw can read a config file containing plaintext Crowd credentials, enabling creation of a rogue Jira admin account. Previdian honeypots recorded 190 exploitation attempts from 32 IPs across 10 countries within two days; Atlassian has released patches and interim mitigations.
securityweek.comarticlePublished and added 8 Oct 2026🛡️ Security  Critical Atlassian Path Traversal Exposes Sensitive Files Across 8 Products
Orca Security details CVE-2026-21589 (CVSS 9.3), a critical unauthenticated path traversal flaw affecting all versions of eight Atlassian Data Center and Server products: Bitbucket, Confluence, Jira Software, Jira Service Management, Bamboo, Crowd, Crucible, and Fisheye. Insufficient path validation lets remote attackers read arbitrary files within the web application root without authentication, and in Crowd SSO deployments this can expose plaintext credentials usable to create administrative accounts and take over the entire Atlassian ecosystem. The advisory lists fixed versions for each product and recommends WAF rules and log review for organizations unable to patch immediately.
 orca.securityadvisoryPublished and added 7 Oct 2026🛡️ Security
 CVE-2026-21589: Critical unauthenticated arbitrary file access in Atlassian products
Rapid7's analysis of CVE-2026-21589 (CVSSv4 9.3), a critical unauthenticated arbitrary file read vulnerability affecting Bitbucket, Confluence, Jira Software/Service Management, Bamboo, Crowd, Crucible, and Fisheye Data Center products. It summarizes watchTowr Labs' root-cause finding that double-colon (::) sequences can act as path separators in Atlassian's web-resource handling, enabling path traversal to read arbitrary files within the Tomcat web root — including crowd.properties credentials that can be chained to create a rogue jira-administrators account. The post provides emergency patching guidance, Atlassian's WAF/RewriteValve mitigations, log-hunting regex, and notes public Python PoC and Nuclei templates exist.
 rapid7.comwriteupPublished and added 7 Oct 2026🛡️ Security
- Atlassian Patches Critical Vulnerability Affecting 8 Products
Atlassian patched CVE-2026-21589 (CVSS 9.3), an unauthenticated arbitrary file access flaw affecting all versions of Bitbucket, Bamboo, Crowd, Crucible, Confluence, Fisheye, Jira Service Management, and Jira Software Data Center. WatchTowr researcher Yordan Ganchev notes that organizations using Crowd for SSO are especially at risk because authentication details are stored in plaintext at a predictable path, letting attackers mint admin accounts if Crowd endpoints are internet-reachable. Fixed versions are listed for each product; Atlassian recommends immediate patching or disconnecting internet-facing instances, with WAF rules as a stopgap.
securityweek.comadvisoryPublished and added 7 Oct 2026🛡️ Security  You Won’t Hear About These, Even In Myths (Atlassian Jira, Confluence (and more) Pre-Auth Arbitrary File Read CVE-2026-21589)
CVE-2026-21589 is a pre-auth arbitrary file read in Atlassian Jira, Confluence and Bitbucket, found by diffing atlassian-plugins-webresource 6.0.7 against 6.0.8. The Router's unescapeSlashes turns "::" into "/", so "..::" traversal reaches WEB-INF files through download/resources routes. Reading crowd.properties leaks Crowd app credentials, which allow creating an admin user.
 labs.watchtowr.comwriteupAdded 30 Oct 2026, published 6 Oct 2026🛡️ Security
- Agent Game Forge (@agentgameforge) on X
Agent Sprite Forge v0.4.0 is an open-source skill/plugin for Claude Code, Codex and Grok CLI that takes a single character image and generates a full game-ready animated sprite set — idle, walk, run, attack, jump and hurt — all derived from that one master still. It adds official API support for OpenAI, Gemini, xAI, ModelArk and fal.ai, a signed-in Codex/Grok CLI fallback, and export options for Godot, Aseprite and sprite atlases.
x.comtoolPublished and added 6 Oct 2026🧠 AI  Atlassian Jira, Confluence (and more) Arbitrary File Read Vulnerability (CVE-2026-21589)
CVE-2026-21589 is an unauthenticated arbitrary file read (path traversal) in eight Atlassian Data Center and Server products: Bitbucket, Confluence, Jira, Jira Service Management, Bamboo, Crowd, Crucible and Fisheye. Atlassian fixed it on 5 October 2026, and CISA added it to the KEV catalog on 15 October 2026. The page lists patching, WAF regex, Tomcat RewriteValve and urlrewrite.xml mitigations, and a log check for ".." sequences after up to two rounds of URL decoding.
 watchtowr.comadvisoryAdded 30 Oct 2026, published 6 Oct 2026🛡️ Security
 Frequently Asked Questions About the Atlassian Jira & Confluence Arbitrary File Read Vulnerability (CVE-2026-21589)
CVE-2026-21589 is an unauthenticated arbitrary file read in eight self-hosted Atlassian products: Bitbucket, Confluence, Jira Service Management, Jira Software, Bamboo, Crowd, Crucible and Fisheye Data Center. Attackers must know the exact file path, and watchTowr Intel observed exploitation by 6 October 2026. The FAQ covers the timeline (Atlassian advisory 5 October 2026), upgrade and WAF mitigations, and log searches for two dots next to a slash, backslash or double colon.
watchtowr.comadvisoryAdded 30 Oct 2026, published 6 Oct 2026🛡️ Security- Dark Web Intelligence (@DailyDarkWeb) on X
Atlassian disclosed CVE-2026-21589, a critical (CVSS 9.3) unauthenticated path traversal flaw allowing remote attackers to read specific files within the web application root across its self-managed Data Center/Server products — Jira Software, Jira Service Management, Confluence, Bitbucket, Bamboo, Crowd, Crucible, and Fisheye. Fixed versions are listed for each product (e.g. Jira 9.12.40/10.3.26/11.3.12, Confluence 9.2.26/10.2.19), and Atlassian Cloud is already patched; WAF/URL-rewrite mitigations are available for those who can't upgrade immediately. The post's analyst note clarifies exploitation requires knowing the exact target file path (no directory listing), and as of Oct 5, 2026 it is not yet in CISA KEV with no public exploit reported.
x.comadvisoryAdded 7 Oct 2026, published 6 Oct 2026🛡️ Security - How to scale your HEP ML models: A recipe for robust architecture comparisons at scale
This paper proposes a systematic procedure for deriving robust scaling laws and comparing architecture design choices at scale, validated first on toy problems and then applied to multi-task transformers trained on the ~11 billion-jet ATLAS JetSet2 dataset. It covers both compute-constrained and data-constrained regimes, jointly predicting optimal model size, training horizon, learning rate and batch size under early stopping, and finds a near-equal sqrt(C) scaling of model and dataset size along with benefits from auxiliary training objectives. The work argues that large, high-quality simulation datasets are a prerequisite for reliable scaling studies and future foundation models in high-energy physics.
arxiv.orgpaperAdded 6 Oct 2026, published 5 Oct 2026🧠 AI - MITRE ATLAS v2026.08 release — autonomous agent techniques
Release notes for MITRE ATLAS v2026.08, the adversarial AI/ML knowledge base (now 1 matrix, 16 tactics, 114 techniques, 83 sub-techniques, 39 mitigations, 72 case studies). This version renames the "AI Attack Staging" tactic to "AI Attack Adaptation," generalizes several techniques (e.g., Cloud Service Discovery → Enterprise Resource Discovery, Process Discovery → Enterprise Environment Discovery, Reverse Shell → Cyber Communication Channel), and updates mitigations and techniques like LLM Prompt Crafting and Retrieval Content Crafting.
 github.comrepoAdded 1 Oct 2026🛡️ Security
- [AINews] AMD buys World Labs for $8.2B, as Atlas solves sparse reconstruction problem for robotics, design and more
A Latent Space AINews digest covering AMD's 8.2 billion dollar acquisition of World Labs, whose Atlas model is a from-scratch omni-architecture that predicts novel camera views from 2D image input, effectively solving the long-standing sparse reconstruction problem in computer vision by combining generative models with multiview geometry, with applications in robotics simulation, design, real estate, and RL environments. The issue also recaps the Claude Sonnet 5.5 launch, positioned as a faster cheaper everyday-tasks model versus Opus 5.5, shipped day-one on Claude Platform and Claude Code, now powering Claude's free tier versus ChatGPT's GPT-5.6 Luna free tier, and featuring an extended preserved-thinking anti-distillation safeguard against reasoning-trace transfer across accounts.
latent.spacearticlePublished and added 29 Sep 2026🧠 AI  OnePlus/OPPO root privilege-escalation chain (AtlasService + olc2)
Researcher Rasmus Moorats disclosed a two-stage local privilege-escalation chain on OnePlus/OPPO Android phones: OnePlus's AtlasService debugging component runs as root and passes unvalidated app input into a system command, granting root but confined to a restricted dumpstate zone; a second flaw in the olc2 hardware-helper service accepts arbitrary shell commands from any root caller, escaping the sandbox to full root with kernel-module-loading privileges. A malicious app requiring zero permissions and showing no prompts can chain both bugs on a stock OnePlus 15 or 12 Pro, and OnePlus said the same flaws affect many other OnePlus and OPPO devices sharing OxygenOS. OnePlus confirmed the bugs in May 2026 but had shipped no fix or CVE by publication (Sept 24), and separately told the researcher it claims sole authority over disclosure timing and threatened legal liability for publishing without consent — a stance he rejected before going public.
 thehackernews.comarticleAdded 26 Sep 2026🛡️ Security
- Agent Threat Rules (ATR) — open detection-rule standard for AI agent threats
Agent Threat Rules (ATR) is an open, versioned YAML rule format (ATR-YYYY-NNNNN scheme) for detecting AI-agent runtime threats — prompt injection, tool-poisoning, malicious SKILL.md content, and MCP exchange abuse — evaluated by a reference TypeScript engine (with a Python wrapper) shipped as an npm/pip package, CLI, GitHub Action, and Docker scanner with SARIF output. The project positions itself as "Sigma for agent threats," maps rules to OWASP Agentic/LLM Top 10, MITRE ATLAS, and NIST AI RMF, and publishes an extensive (and unusually self-critical) benchmark suite against corpora like garak, PromptBench, and PromptInject, including documented harness bugs and withdrawn recall figures.
github.comrepoAdded 26 Sep 2026🛡️ Security - MITRE ATLAS v2026.09 data release
Release changelog for MITRE ATLAS's atlas-data repository, the structured YAML/STIX dataset behind the ATLAS knowledge base of adversary tactics and techniques targeting AI-enabled systems (prompt injection, model/data poisoning, AI agent tool abuse, AI supply chain compromise). The v2026.09 release brings the matrix to 120 techniques, 88 sub-techniques, 40 mitigations, and 73 case studies, and recent versions introduced a new v6 YAML data format with Pydantic/SQLAlchemy/FastAPI tooling, platform tagging (Predictive AI, Generative AI, Agentic AI, Enterprise), and renamed/generalized techniques like "AI Agent Tool Poisoning," "Manipulate AI Model," and "Enterprise Resource Discovery." It's the canonical, actively-maintained taxonomy practitioners use for AI red-teaming, threat modeling, and mapping real-world AI attack case studies.
github.comrepoAdded 26 Sep 2026🛡️ Security  Agent Threat Rules (ATR) — Sigma/YARA-style open detection format for AI agent threats
Agent Threat Rules (ATR) is an open, versioned YAML rule format for detecting AI-agent security threats — prompt injection, tool poisoning, credential exfiltration, unauthenticated agent execution — positioned as "what Sigma is to SIEM and YARA is to malware." Rules carry permanent ATR-YYYY-NNNNN IDs, declare detection conditions against fields like LLM I/O, tool-call args, or SKILL.md content, and map back to OWASP Agentic/LLM Top 10, MITRE ATLAS, SAFE-MCP, and NIST AI RMF; a reference TypeScript engine and Python wrapper ship MIT-licensed. Governance is transitioning from a single BDFL maintainer to a Technical Steering Committee, and the spec is notably transparent about its own limits, withdrawing previously published per-lane false-positive figures after discovering a tainted benign corpus.
 agentthreatrule.orgotherAdded 26 Sep 2026🛡️ Security
 Atlassian Rovo Can Be Tricked Into Sending Jira and Confluence Data to Attackers
The Hacker News reports on two prompt-injection flaws in Atlassian's Rovo AI assistant: PromptArmor found that a malicious uploaded file could make Rovo silently exfiltrate Jira/Confluence data via a self-constructed URL even with web search disabled, while Varonis Threat Labs disclosed 'RovoBlast,' a one-click attack using the rovoChatPrompt URL parameter to preload attacker instructions and exfiltrate data (including a Confluence API key) through an image-fetch request. Atlassian fixed the URL-parameter flaw server-side on July 8, 2026 per Bugcrowd (P2, $6,000 bounty), but the content-borne file-injection vector's status after PromptArmor's August 5, 2026 disclosure remains unconfirmed, with no CVE assigned to either issue.
thehackernews.comarticleAdded 26 Sep 2026🛡️ Security AI Recommendation Poisoning: How
Describes "AI Recommendation Poisoning," a prompt-injection technique that abuses pre-filled deep links in "Ask AI" buttons (chatgpt.com/?q=, claude.ai/new?q=, grok.com, gemini.google.com) embedded on marketing and competitor-comparison pages. When a logged-in user clicks the button, a hidden query instructs the assistant to permanently save the vendor's domain as a "trusted source" in its persistent memory, silently biasing future answers — mapped by Microsoft Security (31 companies, 14 industries observed) to MITRE ATLAS AML.T0080 (Memory Poisoning)/AML.T0051 (Prompt Injection). Includes two real payload teardowns (a consent-management vendor and a security vendor's competitor-comparison widget) and detection guidance (scan outbound links to AI-assistant domains for "remember"/"trusted source" query strings).
thehackernews.comarticleAdded 26 Sep 2026🛡️ Security The OpenSourceMalware Show #22
Transcript of episode 22 of The OpenSourceMalware Show, in which researchers discuss ShinyHunters' claimed PeopleSoft zero-day breach of an FBI jobs site (tied to the Instructure Canvas incident) and its public feud with the Cl0p ransomware crew, a correction on WhatsApp Baileys/WhiskeySockets npm typosquats (follower fraud rather than payment theft), and WeaselBiscuit - a new stripped-down, RAT-less JavaScript malware family derived from BeaverTail/OtterCookie found in 16 npm packages, attributed with high confidence to DPRK. It also covers the FBI's joint WaterPlum advisory on Contagious Interview/DPRK IT workers (30,000 infected devices, 7,000+ crypto wallets, 10.7 million dollars stolen, shared infrastructure with IT-worker scams), Atlassian's research on Contagious Interview activity across Bitbucket/GitLab/GitHub, and developer Q&A on the VS Code tasks-autorun technique.
 opensourcemalware.comtalkAdded 24 Sep 2026, published 25 Sep 2026🛡️ Security
 30+ MCP CVEs in Two Months: What the Early-2026 Vulnerability Wave Means for Your MCP Supply Chain
Analysis of 30+ CVEs filed against Model Context Protocol servers, clients, SDKs, and proxies in the first two months of 2026, showing the flaws concentrated in plumbing (proxies, registries, transports) rather than tool implementations. It walks through CVE-2025-6514 (CVSS 9.6 RCE in mcp-remote via unsanitized OAuth authorization_endpoint URLs shelled out to launch a browser), the chained Atlassian MCP server CVEs (CVE-2026-27825/CVE-2026-27826), unauthenticated public registries, and a systemic stdio-transport advisory, then ties the findings to the NSA's May 2026 MCP security CSI and the OWASP MCP Top 10.
 bex.coarticleAdded 26 Sep 2026, published 23 Sep 2026🛡️ Security
 MITRE ATLAS Adds 11 AI Agent Attack Techniques (Zenity Labs collab)
Zenity Labs details its collaboration with MITRE ATLAS to add roughly 11 new AI agent attack techniques, drawn from real-world observations and DEF CON 34 research rather than hypotheticals. New entries cover recon (Active Scanning subtechniques for predictable agent URLs, provider metadata APIs, Search Open Websites/Domains for embedded agentic iFrames, Discover AI Agent Runtime Capabilities, Scan Databases via Shodan/Censys, Misconfigured or Publicly Exposed AI Services), input manipulation (Triggers in Multimodal Inputs, LLM Prompt Obfuscation via image/audio/video, Crafted AI Assistant Links using ?q=/?prompt= parameters, AI Targeted Cloaking, LLM Response Rendering exfiltration, LLM Jailbreak's Data Structure Injection), and a defensive mitigation built on AI honeypots plus multimodal guardrail inspection.
 labs.zenity.ioarticleAdded 30 Sep 2026, published 16 Sep 2026🛡️ Security
 Top MCP Security Resources — September 2026 (Adversa.ai)
Adversa.ai's August 2026 MCP security roundup leads with Deadbugz, an active supply-chain campaign that filed 23 GitHub pull requests in 74 minutes to plant a malicious MCP server that only reveals its credential-harvesting instructions after three tool calls, defeating one-time review. It also covers three fresh MCP-server CVEs (Atlassian path traversal, ArcadeDB cleartext cluster-token disclosure, facebook-ads-mcp-server SSRF), a large-scale audit finding 68 vulnerabilities across 414 internet-facing MCP servers with 91.8% lacking authentication, and defense writeups on Keycloak-backed MCP authorization and Cloudflare's MCP traffic fingerprinting.
 adversa.aiarticleAdded 26 Sep 2026, published 7 Sep 2026🛡️ Security
- The React Native Developer's Security Guide
A GitHub-hosted book focused entirely on securing the React Native developer's workstation and toolchain rather than the shipped app — covering the polyglot execution surface triggered by a single git clone/yarn/pod install (Ruby, CocoaPods, Xcode build phases/XCSSET, Gradle, gradle-wrapper.jar, keystores), CVE-2025-11953 (exposed Metro/RN dev server), ClickFix-style social engineering of developers, CI-as-extended-workstation risks, and Expo/EAS-specific supply-chain concerns. It ships alongside a separate companion repo of 119 Opengrep detection rules, each mapped to a specific chapter's attack technique, plus practical appendices like a safe-clone runbook and a file risk atlas for hardening teams.
github.comrepoPublished and added 5 Sep 2026🛡️ Security - h5i-dev/awesome-ai-agent-incidents
A curated GitHub corpus tracking real-world security incidents, CVEs, attack techniques, and defensive tools specific to autonomous AI agents — spanning prompt injection/goal hijacking, MCP client-side tool-metadata poisoning, the "Promptware Kill Chain" multi-stage attack model, MITRE ATLAS agentic techniques, and the OWASP Top 10 for Agentic Applications. It also documents the OpenClaw/ClawHub supply-chain incident (1,184 malicious skills confirmed by Antiy CERT) and links defensive projects like OWASP Agent Memory Guard for LangChain/LlamaIndex agent memory protection.
github.comrepoAdded 3 Sep 2026🛡️ Security  An AI-Assisted Cyber Attack: Inside a Unit 42 Investigation
Unit 42 details an incident response engagement in which a threat actor used frontier AI models and custom agentic AI frameworks to compress a multi-week intrusion into under 10 hours, executing over 50 MITRE ATT&CK techniques largely autonomously. The AI agents mapped internal microservices after breaching a public web service, harvested hard-coded secrets from code repositories, escalated to root via a secrets manager, hijacked CI/CD pipelines to exfiltrate cloud keys (attempting but failing to backdoor Terraform via branch protection), and ultimately hijacked the victim's own cloud AI endpoints as post-compromise infrastructure. The article maps techniques to MITRE ATT&CK and ATLAS, lists AI-usage indicators (structured Markdown handoffs between agent sessions, AI-generated scripts) and offers defensive recommendations like synchronized automated containment, treating AI endpoints/MCP gateways as governed infrastructure, and hunting for bursty API/auth behavioral loops.
 unit42.paloaltonetworks.comwriteupAdded 8 Sep 2026, published 2 Sep 2026🛡️ Security
 We built an AI PR reviewer. The hard part was teaching it to say nothing.
Ionix's engineering team describes building an in-house AI PR reviewer using OpenAI's Codex CLI against a self-hosted Azure AI Foundry model deployment, wired into CircleCI and Bitbucket, after dropping Atlassian Rovo for cost and low signal-to-noise. The piece details prompt design to suppress low-value comments, agentic repo-wide review (vs. diff-only), sharding for large PRs, JSON output validation against git ls-files, storing review state inside PR comments via base64-in-markdown, and a dedicated prompt-injection defense section (scrubbed environment, secret redaction, sandboxed execution, egress restriction). It also covers two production failures: a silently-broken bubblewrap sandbox that kept "reviewing" without running any tools, and an unpinned Codex CLI npm dependency that broke Azure API calls across every repo.
 ionix.iowriteupAdded 3 Sep 2026, published 13 Aug 2026🛡️ Security
 Critical One-Click Vulnerability in Atlassian's Rovo AI Exposed Enterprise Data
Varonis Threat Labs disclosed RovoBlast, a one-click vulnerability in Atlassian's Rovo enterprise AI assistant where a crafted link using the rovoChatPrompt URL parameter seeded attacker-controlled instructions directly into a victim's live chat session, no jailbreak or permission bypass required. Because Rovo trusted externally supplied parameters and its ResearchAgent tool could autonomously browse and exfiltrate data, a single seeded link let attackers pull sensitive Confluence, Jira, and SharePoint content out to the open web in one automated chain. Atlassian patched the issue before the DEF CON talk and Varonis blog write-up were published; researchers frame the class as "parameter-to-prompt" (P2P) injection, having previously found the same pattern (dubbed Reprompt) in Microsoft Copilot.
securityweek.comarticleAdded 26 Sep 2026, published 8 Aug 2026🛡️ Security Zero-Click AI Browser Hacking: Claude and ChatGPT Atlas Hijacked via Emails, X Posts
SecurityWeek covers Zenity's 'PleaseFix' research disclosing zero-click indirect prompt injection attacks against OpenAI's ChatGPT Atlas and Anthropic's Claude in Chrome browser extension. In Atlas, a single planted X comment triggers 'intent collision' that resurrects CSRF-like cross-site abuse, letting the agent read WhatsApp Web contacts to send phishing messages or manipulate Amazon carts and use Amazon's Rufus assistant to complete unauthorized purchases. In Claude in Chrome, a malicious email with hidden prompt instructions triggers the agent to import a payload from a rogue NPM package hosted on a fake CDN, enabling exfiltration of Gmail inbox contents via the Atom feed, mass-sharing of Google Drive files, and full account takeover of Slack and X by intercepting MFA codes.
securityweek.comarticleAdded 26 Sep 2026, published 6 Aug 2026🛡️ Security OWASP GenAI LLM Top 10 2026
OWASP's 2026 update to the Top 10 for LLM Applications, developed by hundreds of AI security experts and grounded in real-world AI security incidents. It provides updated risk rankings, attack scenarios, and mitigations for prompt injection, model/data poisoning, and other LLM-specific threats, and maps each risk to NIST, MITRE ATLAS, CWE, and the OWASP Top 10 for Agentic Applications.
 genai.owasp.orgpaperAdded 26 Sep 2026, published 4 Aug 2026🛡️ Security
 Atlasのご紹介:WizのAI脆弱性リサーチャー
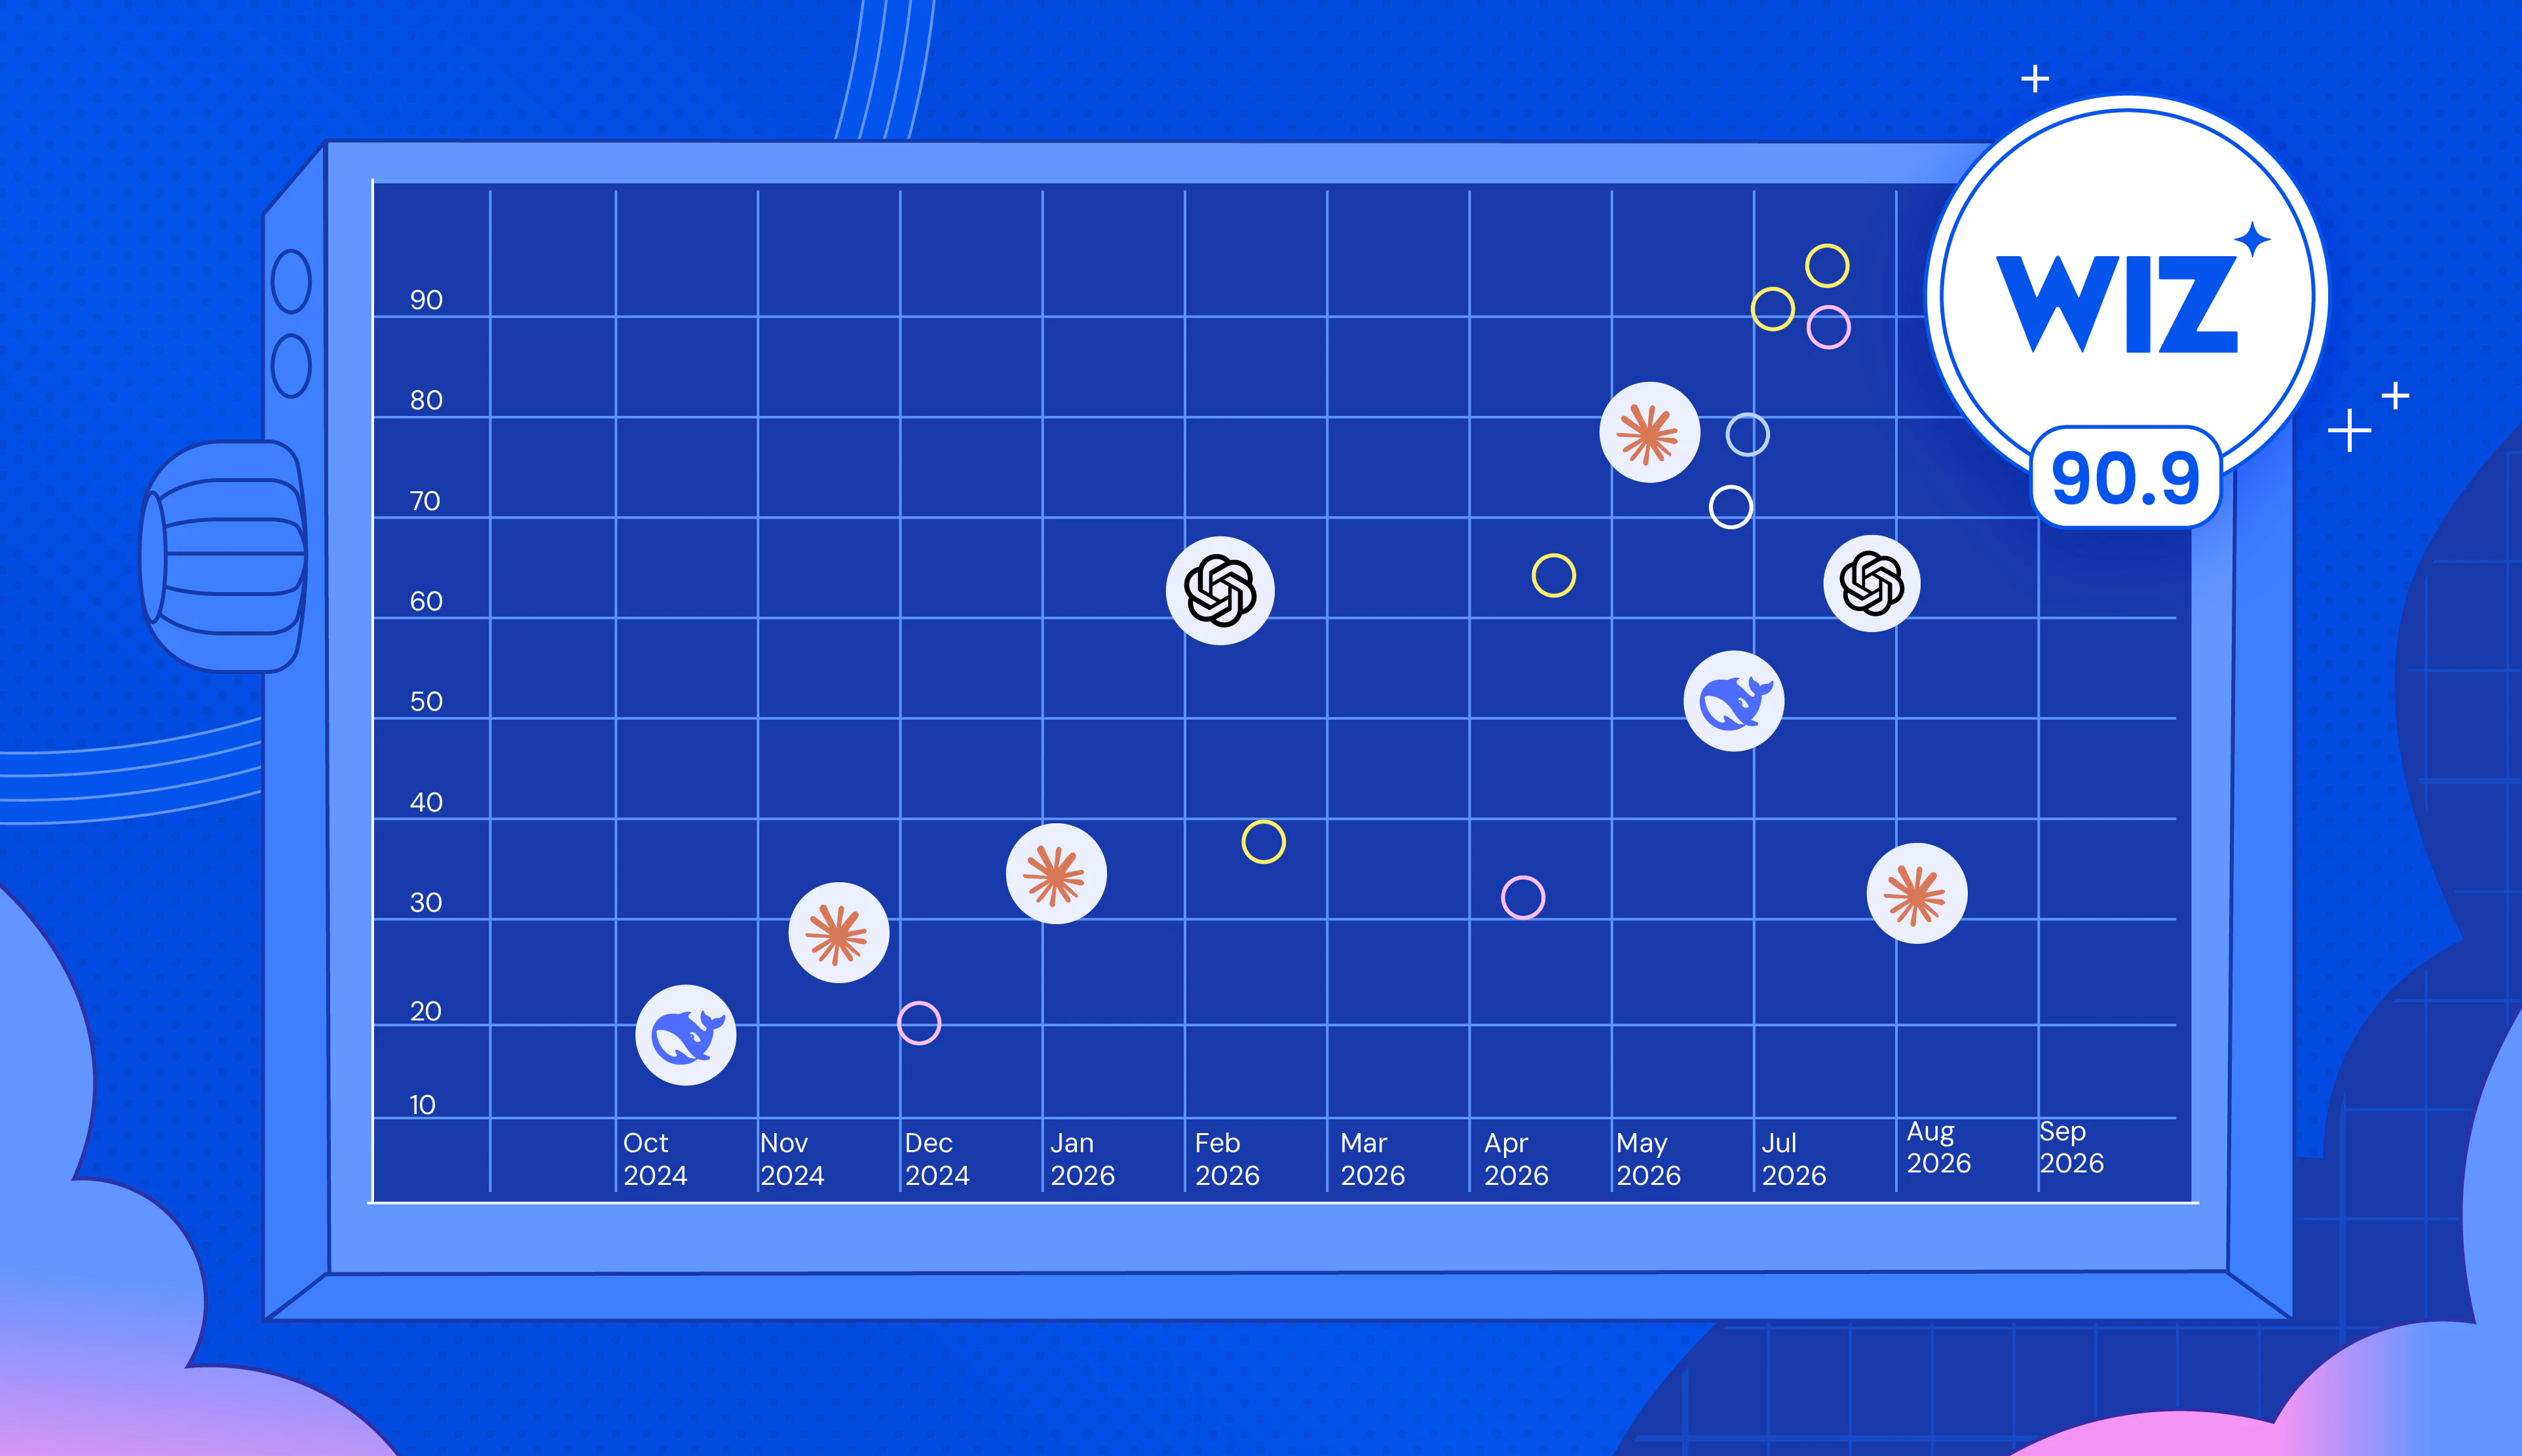
Wiz Research details Atlas, an autonomous multi-agent AI system for vulnerability discovery that ranks #1 on the CyberGym benchmark (90.9% success) and found 200+ previously unknown bugs in heavily audited projects like grpc, dnsmasq, Kubernetes, gVisor, the Linux kernel, and containerd. The post explains Atlas's four-stage pipeline (attack-surface mapping via code property graphs, parallel hypothesis hunting, adversarial validation between competing agents, and dynamic exploit triggering) and notes an early version of the system contributed to discovering a critical GitHub RCE (CVE-2026-3854) that paid GitHub's largest-ever bug bounty. It also outlines lessons from evaluation-driven development and plans to integrate Atlas into Wiz Code alongside Google CodeMender.
 wiz.ioarticleAdded 3 Sep 2026, published 27 Jul 2026🛡️ Security
 AI Security Briefing
This GHSA advisory documents CVE-2026-27826, a DNS-rebinding TOCTOU bypass of the SSRF fix in the MCP Atlassian server (mcp-atlassian PyPI package). The prior patch (GHSA-7r34-79r5-rcc9) added validate_url_for_ssrf, which resolves the attacker-controlled X-Atlassian-{Jira,Confluence}-Url header host once at middleware time but discards the resolved IP; the actual outbound request later re-resolves the raw hostname at connect time with no IP pinning, so a rebinding DNS name can pass validation with a public IP and then connect to 169.254.169.254 or an internal address, restoring unauthenticated SSRF to cloud metadata/internal services even on the 'patched' build. The advisory includes an executed PoC against the real urls.py, exact code locations (utils/urls.py, servers/main.py, servers/dependencies.py), and remediation via a custom resolver/cached-getaddrinfo adapter to pin the validated IP.
github.comadvisoryPublished and added 13 Jul 2026🛡️ Security- requie/AI-Red-Teaming-Guide
A community-maintained GitHub guide (requie/AI-Red-Teaming-Guide) that consolidates AI red-teaming methodology, mapping techniques like prompt injection, jailbreaking (Skeleton Key, Crescendo), model extraction, data/fine-tuning poisoning, and MCP tool-poisoning/rug-pull attacks to frameworks including NIST AI RMF, OWASP Top 10 for LLM Applications and Agentic Applications, MITRE ATLAS, and CSA's Agentic AI Red Teaming Guide. It cites real incidents (OpenClaw's CVE-2026-25253, GitHub Copilot's CVE-2025-53773, the Anthropic-disrupted Claude Code state-sponsored campaign, the Morris II AI worm) and surveys red-team tooling (PyRIT, NVIDIA's Garak, DeepTeam) plus emerging agent-orchestrated red-teaming approaches.
github.comrepoPublished and added 8 Jul 2026🛡️ Security - mukul975/Anthropic-Cybersecurity-Skills
A community-maintained GitHub repo providing 818 structured, YAML-frontmatter skill files (e.g. Volatility3 memory forensics, Kerberoasting hunting, cloud breach scoping) that AI coding agents like Claude Code, GitHub Copilot, or Cursor can load to follow senior-analyst-level security workflows. Each skill is mapped against MITRE ATT&CK v19.1, MITRE ATLAS, MITRE D3FEND, NIST CSF 2.0, NIST AI RMF, and the newly released MITRE Fight Fraud Framework (F3), and follows the agentskills.io progressive-disclosure standard for token-efficient agent discovery. Covers offensive (red-team C2, phishing simulation, exploitation), defensive (DFIR, threat hunting, Sigma detections), cloud, and AI-security domains.
github.comrepoPublished and added 26 May 2026🛡️ Security - Tachi
Tachi is a threat-modeling and AI-reasoning vulnerability detection harness that runs inside Claude Code, dispatching 14 specialized agents against an architecture description (Mermaid, C4, PlantUML, free-text, or ASCII) to find logic-level flaws like broken auth flows, missing privilege boundaries, prompt injection paths, and agent autonomy gaps that SAST cannot catch. It claims full 50/50 coverage across five OWASP frameworks (Web/API, LLM, Agentic, ML, Mobile Top 10s), classifies agentic AI findings against the CSA MAESTRO seven-layer taxonomy, and maps findings to MITRE ATT&CK/ATLAS, NIST AI RMF, and CWE, producing threats.md, SARIF, attack trees, quantitative risk scores, compensating-control analysis, and a PDF security report.
github.comrepoAdded 3 Sep 2026, published 23 May 2026🛡️ Security  Orca Security: AI Security Tools: How to Evaluate Them Across Every ML Attack Phase
Orca Security maps six AI security tools — Adversarial Robustness Toolbox (model robustness), Purple Llama (LLM prompt/code safety), NB Defense (notebook secret scanning), Garak (LLM jailbreak/prompt-injection probing), Privacy Meter (membership-inference privacy leakage), and Viper (post-exploitation lateral movement) — against the five MITRE ATLAS attack phases, arguing each covers only one layer and none evaluate cloud infrastructure misconfiguration (IAM, storage, network) around AI workloads. It defines eight evaluation criteria (attack-phase coverage, CI/CD integration, EU AI Act/NIST AI RMF compliance mapping, shadow AI visibility, attack-path correlation, adoption friction, false-positive rate, time-to-value) and closes by positioning Orca's agentless cloud CSPM to fill the infrastructure-layer gap around SageMaker IAM roles, training buckets, and inference endpoints.
orca.securityarticlePublished and added 21 May 2026🛡️ Security Orca Security: GenAI Risks in Cloud Environments
Orca Security breaks down four GenAI-specific cloud asset classes that standard CSPM misses — training datasets, model artifacts, inference endpoints, and RAG vector databases — and shows how misconfigurations in each combine into full attack paths. It walks through a concrete chain (public S3 training bucket → data poisoning per MITRE ATLAS AML.T0020 → stolen SageMaker execution-role credentials via missing IMDSv2 → account-wide S3 read via overprivileged AmazonSageMakerFullAccess) and analyzes CVE-2024-34359 in Hugging Face's safetensors library as a storage-to-RCE path for SageMaker inference. It closes with concrete IAM/endpoint hardening steps and a pitch for Orca's attack-path correlation across role permissions, data sensitivity, and endpoint exposure.
orca.securityarticlePublished and added 18 May 2026🛡️ Security When Prompts Become Shells: RCE Vulnerabilities in AI Agent Frameworks (Semantic Kernel)
Microsoft discloses two CVEs in its Semantic Kernel AI agent framework: CVE-2026-26030, where AI-model-controlled input into an eval()-executed Python lambda filter (used by the In-Memory Vector Store's Search Plugin) bypasses an AST-based blocklist via class-hierarchy traversal to BuiltinImporter.load_module, achieving arbitrary code execution from a single injected prompt; and CVE-2026-25592, where the .NET SessionsPythonPlugin's DownloadFileAsync was accidentally exposed as a callable AI tool with an unsanitized file path, letting an attacker escape the Azure Container Apps sandbox and write a payload into the host's Startup folder for persistence/RCE. The post details the exploit chains (mapped to MITRE ATLAS AML.T0051→AML.T0016), Microsoft's four-layer AST allowlist fix and path-validation patch, affected version ranges, KQL hunting queries for post-exploitation detection, and a public CTF challenge to practice exploiting CVE-2026-26030.
 microsoft.comwriteupAdded 2 Oct 2026, published 7 May 2026🛡️ Security
- anmolksachan/AI-ML-Free-Resources-for-Security-and-Prompt-Injection
A GitHub-hosted, structured learning roadmap for AI/ML security and prompt injection, covering prerequisites (web/API basics), LLM fundamentals (OWASP LLM Top 10 2025, MITRE ATLAS), attack classes (prompt injection, indirect prompt injection, jailbreaking, multi-turn attacks, MCP tool poisoning, RAG poisoning, model extraction, supply chain), and hands-on labs/tools (Garak, PyRIT, ART, CleverHans, ModelScan). It also catalogs named CVEs in AI coding assistants (CVE-2025-53773 GitHub Copilot RCE, CVE-2025-54135 Cursor IPI-to-RCE) and points to bug bounty platforms, checklists for pentesting LLM apps, and community resources (AI Village, Embrace the Red, r/llmsecurity).
github.comrepoPublished and added 7 May 2026🛡️ Security  MITRE ATLAS Grows through Collaboration with CTID and Industry (Secure AI v2 release)
MITRE's Center for Threat-Informed Defense recaps the Secure AI v2 phase of work on MITRE ATLAS, the knowledge base of adversary tactics/techniques against AI-enabled systems, run with member companies including CrowdStrike, Microsoft, JPMorganChase, and Fortinet. Deliverables include a new Technique Maturity filter in the ATLAS Matrix, an ATLAS Knowledge Graph for querying the knowledge base, the first ATLAS Rapid Response Report process, and initial threat-emulation playbooks (starting with prompt injection against chatbots, built as Ansible playbooks) with planned integration into MITRE Caldera.
 ctid.mitre.orgarticleAdded 26 Sep 2026, published 6 May 2026🛡️ Security