 FBI links $6.3 billion Binance crypto heist to North Korean hackers
The FBI attributed the roughly $6.3 billion Binance theft of about 29 October 2026 to North Korea's TraderTraitor (Lazarus Group, Jade Sleet, APT38). Binance traced the breach to a compromised DevOps engineer's laptop that gave access to a service container used to submit unauthorized withdrawals across ten blockchains. The FBI published 628 laundering addresses and linked the group to earlier thefts at Bybit, DMM Bitcoin, Bitget and Drift.
 bleepingcomputer.comarticlePublished and added 1 Nov 2026🛡️ Security
- North Korean hackers launder $242 million of Binance loot via Tron as FBI presses THORChain: analyst
The Block reports that North Korean hackers (TraderTraitor) laundered about $242 million of funds stolen from Binance through Tron in two days, according to analyst SomaXBT. Relay, THORChain, Chainflip and Symbiosis moved about $140 million off Tron. Elliptic counts $2.85 billion frozen or seized, 44% of $6.43 billion stolen, and $3.25 billion in assets no issuer can freeze. The FBI urged THORChain and others to block listed addresses.
 theblock.coarticlePublished and added 1 Nov 2026🛡️ Security
- Binance Replaced 90% of Assets Stolen in the $6.3B Binance Crypto Hack
Report on the $6.3 billion Binance hack of October 2026, which the FBI attributed to North Korea's TraderTraitor unit. Co-CEO Richard Teng said attackers used EIP-7702 to gain execution approval over a hot wallet, after a compromised laptop and further breach points, and used self-destructing malware. Binance replaced 90% of the assets, and the FBI expects further laundering through Ethereum. No IOCs or mitigations are given.
 en.cryptonomist.charticleAdded 1 Nov 2026, published 31 Oct 2026🛡️ Security
 FBI Attributes $6 Billion-Plus Binance Hack to North Korea
The Defiant reports that the FBI attributed a Binance hack of more than $6 billion to North Korea and named TraderTraitor as the actor. The bureau also sought blocks on the laundering trail, and Binance kept 1 November as its target for restarting withdrawals. The article body did not load, so technical details of the intrusion are not available.
 thedefiant.ioarticlePublished and added 31 Oct 2026🛡️ Security
 Secret Service, FBI Join Binance Hack Probe as Circle Freezes $823 Million
Decrypt reports that Binance is working with the FBI and U.S. Secret Service after a theft of about $6.4 billion, which TRM Labs and Chainalysis attribute to North Korea's TraderTraitor group, also linked to the February 2025 Bybit hack. Circle froze about $823 million in USDC and Tether froze USDT, though the page gives differing Tether totals. Binance first suspected a compromised DevOps engineer laptop, found more breach points, and saw no evidence of leaked wallet private keys.
 decrypt.coarticlePublished and added 30 Oct 2026🛡️ Security
 Bulletproof Host Virtualine Loses Its Domain to FBI Seizure
Virtualine is a Russian-speaking bulletproof hosting provider whose domain virtualine.net the FBI seized. Court documents say it hosted phishing, spam, carding and illicit content, and ignored abuse reports. TRM Labs says it received more illicit-attributed cryptocurrency than any other labeled bulletproof host, mostly from a Russian drug marketplace (44%) and a sextortion scheme (17%), and later from StealC operators in 2026.
 securityweek.comarticlePublished and added 30 Oct 2026🛡️ Security
 Trail of Bits (@trailofbits) on X
Trail of Bits post on X summarising Binance's initial investigation into a security incident. Binance suggests a compromised DevOps engineer's laptop let an attacker reach a service container and submit unauthorized withdrawal transactions. The text says no evidence has been found of wallet private key compromise. The fetched text is truncated and gives no further detail.
 x.comthreadPublished and added 30 Oct 2026🛡️ Security
 Police seize Virtualine bulletproof service tied to ransowmare, cybercrime
Virtualine, a bulletproof hosting service also operating as Secury, Massgod, Spamhouse, Lanedo and Omegatech, had its main domain seized by the FBI with German, Dutch and UK partners. Chainalysis and TRM Labs traced its Bitcoin payments to ransomware (5% of flows), a Russian drug market (about 44%), sextortion and the StealC infostealer. Dutch police seized dozens of servers in Limburg and recovered data on over 3,000 customers.
bleepingcomputer.comarticleAdded 30 Oct 2026, published 28 Oct 2026🛡️ Security- Trail of Bits (@trailofbits) on X
Trail of Bits post says it achieved remote code execution through a Brotli decoder bug in Linux lab setups: Node.js 24.22.0 with Express 5.3.0 via the standard JSON parser (x86-64 and ARM64), and Electron 41.10.7 (x86-64) with a custom decoding service. Exploitation needs a carefully matched setup and repeated attempts. A scanner by ToBScottA finds hidden copies of the decoder, including in stripped binaries.
x.comthreadAdded 30 Oct 2026, published 28 Oct 2026🛡️ Security  International Law Enforcement Seizes Domain of Virtualine Bulletproof Hosting Service
Virtualine is a bulletproof hosting provider whose domain virtualine.net was seized on 27 October 2026 by the FBI Washington Field Office and the Eastern District of Virginia, with German, Dutch and UK police support. Chainalysis and OverRIPE gave intelligence support. The post lists aliases (Secury, Massgod, Spamhouse, Lanedo, Omegatech), forum advertising on Exploit.in and HackForums, and unhosted bitcoin payments tied to ransomware, infostealers and scam infrastructure.
 chainalysis.comarticlePublished and added 27 Oct 2026🛡️ Security
 US Charges Six in Alleged Madagascar NFT Wallet-Draining Scheme
The Defiant reports US charges against six people over an alleged NFT wallet-draining scheme run from Madagascar. An FBI affidavit estimates at least $516,695 in losses across 74 victim-linked wallets. It describes unlimited USDT spending approvals as the mechanism. The fetched text holds only the subtitle, so the scheme's mechanics and the defendants are not covered here.
thedefiant.ioarticlePublished and added 27 Oct 2026🛡️ Security- Trail of Bits (@trailofbits) on X
Trail of Bits post on PHP2Shell, an exploit that gives a shell on MediaWiki, Symfony, Laravel and phpBB. They confirmed it on pre-patch PHP 8.2 to 8.5. An update says it is production-grade: it works with stock php.ini-production, display_errors off, multiple workers, ASLR and load, on ARM64 and x86-64, and reaches root on Apache/mod_php and nginx/php-fpm. No CVE or technical root cause is given.
x.comthreadAdded 27 Oct 2026, published 26 Oct 2026🛡️ Security  Weekly Research Brief: PHP Vulnerability; Objections to OKX-ICE’s Stock Tokenization; Solana Alpenglow Ships
Galaxy Research's weekly brief includes a section on PHP2Shell, two decade-old PHP remote code execution bugs affecting versions back to 5.4, patched in an emergency release. It reports an Amazon honeypot exploit attempt four days before disclosure, thousands of attempts in the 10 hours before the patch per Cloudflare's Matthew Prince, and NSA and FBI offline advice. The author argues the bugs were found with GPT-5.6 Sol and that defence must become agentic. It also lists the week's other incidents, including a CVSS 10.0 GitLab bug and eMudhra's guessable private keys.
 galaxy.comarticleAdded 24 Oct 2026🛡️ Security
- Trail of Bits (@trailofbits) on X
Trail of Bits announces a scanner, built by Scott A., that finds hidden copies of the vulnerable Brotli decoder behind a Node.js/Brotli bug, including in stripped binaries. Exploitability of the bug is still under testing. Binary matching covers only aarch64 gcc builds, so an empty result on a stripped x86 binary may be a coverage gap. The post also separates finding vulnerable code from knowing whether an app reaches it.
x.comtoolAdded 25 Oct 2026, published 23 Oct 2026🛡️ Security - Trail of Bits (@trailofbits) on X
patching-bugs is a Trail of Bits plugin for Codex that has an AI agent write a vulnerability fix, prove it works, and check it for regressions. It was built from analysis of thousands of Codex sessions from the Patch the Planet work with OpenAI. The post argues defenders need patch-writing agents to match attackers' bug-hunting agents. It gives no technical detail beyond that.
x.comtoolAdded 24 Oct 2026, published 22 Oct 2026🛡️ Security - Trail of Bits (@trailofbits) on X
Trail of Bits post on two unpatched critical PHP bugs that were exploited within 17 hours of details leaking. Cloudflare began blocking attacks and Patchstack reported active exploitation. The bug was reported 11 August and fixed 71 days later, with a patch touching 402 files and over 11,000 lines. Trail of Bits announces two open-source plugins, patching-bugs and regression-hunt, from its Patch the Planet work.
x.comthreadAdded 23 Oct 2026, published 21 Oct 2026🛡️ Security - Trail of Bits (@trailofbits) on X
Trail of Bits announces two open-source plugins, patching-bugs and regression-hunt, for AI coding agents that speed up bug patching. They come from four months of Patch the Planet work with open-source projects, which found that repo-level documentation, skills and plugins give agents the maintainer context on what counts as a bug, how a fix should look and what must not break. The post cites the October 2026 PHP incident: a patch touching 402 files, and exploitation within 17 hours of leaked details.
x.comarticleAdded 23 Oct 2026, published 21 Oct 2026🧠 AI - Trail of Bits (@trailofbits) on X
Trail of Bits thread on Google Quantum AI's March publication of a new Shor's algorithm version aimed at secp256k1, the curve protecting Bitcoin and Ethereum wallets. Google used zero-knowledge proofs to keep the attack details secret, and the post says the secrecy lasted 63 days. The fetched text is cut off after the qubit estimate of roughly 1,200, so later details are missing.
x.comthreadAdded 22 Oct 2026, published 20 Oct 2026🛡️ Security - Trail of Bits (@trailofbits) on X
Trail of Bits post announcing research that tested 25 package managers against a simulated malicious repository serving swapped code for the same package and version. Without a lockfile only Go and vcpkg verified every download; with a lockfile fewer than half did. This undercuts the assumption that lockfiles make dependencies immutable and shows hash/integrity verification gaps across ecosystems.
x.comthreadAdded 18 Oct 2026, published 16 Oct 2026🛡️ Security  U.S. jobs data challenges fears about the future of artificial intelligence
Reports Stephen Messer's October 2026 essay arguing that US unemployment (4.3–4.5% through 2025–2026) and studies from Anthropic economists, PwC and a Danish dataset show no mass AI job destruction. It also covers Yann LeCun's rejection of LLMs as a route to human-level intelligence and open-weight competition, notably Moonshot's Kimi K2 to K3 and Harvey's Tenet model post-trained on Kimi K3 (benchmark 11% to 19.7%, inference cost under a quarter). It closes with the September 2026 FBI/NSA/CISA advisory on Chinese distillation campaigns against US models.
en.cryptonomist.charticlePublished and added 16 Oct 2026🧠 AI- Trail of Bits (@trailofbits) on X
Trail of Bits tweet announcing a test of 25 package managers against a simulated malicious repository. Without a lockfile only Go and vcpkg verified every download; with a lockfile fewer than half did. Replies raise that checksum verification is separate from execution isolation, and ask whether poisoned CI package caches were in the threat model.
x.comthreadAdded 17 Oct 2026, published 15 Oct 2026🛡️ Security  How Brooklyn prosecutors and the FBI took down a massive crypto fraud network targeting Russian speakers
Brooklyn DA Eric Gonzalez and the FBI seized or disrupted 241 scam websites and 112 servers tied to a crypto investment fraud network that targeted Russian speakers in the US. The scheme used Russian-language Facebook ads, fake advisers who coached victims into sending crypto to fake trading platforms, fee and tax lockouts on withdrawal, and later fake fund-recovery offers. Investigators went after the servers holding victim data and fraud software, because replacement domains kept appearing after earlier takedowns of about 400 domains. The infrastructure was in Ukraine and other Eastern European countries, no arrests were announced, and about $300,000 has been seized.
 coindesk.comarticlePublished and added 15 Oct 2026🛡️ Security
 US Arrests Two in Crackdown on North Korean IT Worker Laptop Farms
SecurityWeek reports on the arrest of two US nationals (Michael James Bostelle, Juan Cecilio Pena Carrillo) for running laptop farms that helped North Korean IT workers get remote jobs at over 70 US companies, generating more than $3M between 2019 and July 2025. It covers the FBI's Operation Lonestar Roundup (40 Texas locations searched, 187 laptops and KVMs seized). It also covers CrowdStrike's Famous Chollima analysis of shipping-diversion tricks and evolving evasion (hidden RMM tools, spoofed device hashes), and the FBI's 'identity in depth' guidance for spotting ITWs across the employment lifecycle.
securityweek.comarticlePublished and added 14 Oct 2026🛡️ Security Employee Arrested After Listening Device Found in OpenAI Conference Room, FBI and the Company Say
SecurityWeek reports that an OpenAI engineer, Abdulrahman Alfozan, was arrested by the FBI and charged with illegally intercepting oral communications. A recording device, concealed in toilet paper, had been plugged into a USB port on the back of a conference-room TV. OpenAI says it used its own models to analyse the device and identify the employee, and that it has no indication model weights, source code or customer data were accessed. The complaint cites CCTV footage, a camera later added to the room, and the employee's productivity-tool queries about meeting rooms and calendars.
securityweek.comarticlePublished and added 13 Oct 2026🛡️ Security- OpenAI engineer arrested in bugging of executive conference room
Reports the federal arrest of OpenAI engineer Abdulrahman Alfozan, charged with using a device to intercept oral communications after an encrypted audio recorder was found in a San Francisco executive conference room. The recorder was hidden in toilet paper and plugged into a TV's USB port. Prosecutors say he used an internal productivity tool to scout rooms and calendars, and a chatbot account tied to his spouse asked how to build, encrypt and remotely access a recorder. OpenAI's technical surveillance countermeasures team found the device, and OpenAI says it used its own models for forensic analysis. It then restricted his access in stages, timed with the FBI, before firing him. A useful insider-threat case study that also covers physical security.
 sfstandard.comarticlePublished and added 13 Oct 2026🛡️ Security
 Ransomware Response Expert Arrested in ShinyHunters FBI Hack Probe
SecurityWeek reports the US arrest of a Canadian ransomware-negotiation specialist, reportedly Edward Dubrovsky of CyberSteward, on suspicion of involvement in ShinyHunters attacks, including the hack of FBI systems. He is charged with conspiracy to threaten to impair information confidentiality with intent to extort, and the case has moved to the Eastern District of Texas. It is the third ShinyHunters arrest in weeks, after suspects in the Netherlands and Jordan. The FBI blamed its own breach on a contractor's unpatched Oracle PeopleSoft, and sources say other ransomware negotiators could face charges.
securityweek.comarticlePublished and added 12 Oct 2026🛡️ Security Insider Cyber Extortion Plot Against Industrial Firm Lands Engineer in Prison
SecurityWeek reports that Daniel Rhyne, a core infrastructure engineer, was sentenced to 32 months for sabotaging and extorting his employer, an industrial firm in New Jersey. In November 2023 he planted scheduled tasks on the domain controller that deleted 13 domain admin accounts and reset passwords on 301 domain users, 254 servers and 3,284 workstations, mostly to 'TheFr0zenCrew!'. He then emailed a 20 bitcoin (about $750,000) ransom demand. Internal log correlation with physical access records, plus FBI work, traced the activity to his home IP address.
securityweek.comarticlePublished and added 10 Oct 2026🛡️ Security- CISA AA26-281A: Chinese Government-linked Actors Combine Automated and Hands-on Hacking Tools to Steal Data
Joint FBI/CISA/NSA and allied-agency advisory on China-linked actors enabled by Integrity Technology Group (overlapping with Flax Typhoon, Ethereal Panda, Red Juliett). It details their TTPs: open-source scanners and the MicroScan exploit-script app, an XSS credential-harvesting payload dropping live700_v1.exe, EBurst password spraying against Exchange/O365, SoftEther VPN persistence, DCSync via DC.exe, and email theft via the Curlc4.txt PHP bot and the office-cli utility. It also provides IOCs, MITRE ATT&CK mappings, CVEs, incident response steps, and mitigations.
 cisa.govadvisoryAdded 9 Oct 2026🛡️ Security
- Trail of Bits (@trailofbits) on X
Trail of Bits announces SequenceHash, a library for hashing several inputs without concatenation ambiguity. Plain concatenation lets different input sequences produce the same SHA-256 digest. SequenceHash appends each input's length as a fixed 128-bit integer so every sequence has a single encoding. It ships for Rust, Go and Python, and removes a recurring bug class in crypto and appsec code.
x.comtoolAdded 11 Oct 2026, published 9 Oct 2026🛡️ Security - Ned Peterson (@NedPeterson99) on X
A post summarizing a joint FBI and six-country advisory on actors tied to Integrity Technology Group (the sanctioned Chinese firm linked to Flax Typhoon and the Raptor Train botnet). They password-sprayed Microsoft 365 and Exchange accounts over EWS, OWA, ActiveSync and PowerShell with EBurst. They then drained mailboxes with a PHP bot over Exchange Web Services and an office-cli utility using stored client ID, tenant ID and secret values, and exposed the stolen email to third parties through a web app, in some cases restricted to Xiamen IP addresses. Victims were in government, law enforcement, healthcare and religious organizations across Southeast Asia, Africa and North America, with activity since at least January 2021. Defensive takeaways: enforce MFA on every legacy path, retire basic auth and EWS, audit OAuth apps and service principals with mail-read rights, and alert on bulk mailbox pulls.
x.comthreadAdded 11 Oct 2026, published 9 Oct 2026🛡️ Security - Dark Web Intelligence (@DailyDarkWeb) on X
A Twitter/X post digests joint advisory AA26-281A from FBI, CISA, NSA and allied agencies (UK, Australia, Canada, Japan, New Zealand, Spain) on China-based Integrity Technology Group enabling threat actors, tracked elsewhere as Flax Typhoon, Ethereal Panda and Red Juliett, to target US critical infrastructure, government, healthcare, education and law enforcement networks worldwide. The actors chain open-source scanners, large botnets, XSS, password spraying against Microsoft Exchange, VPN persistence and credential-harvesting scripts. CISA added five exploited CVEs (ISC BIND, Apache Struts, ProFTPD, ONLYOFFICE Docs, Strapi) to its KEV catalog with an Oct 11 federal remediation deadline, and STIX IOCs accompany the advisory.
x.comthreadPublished and added 8 Oct 2026🛡️ Security 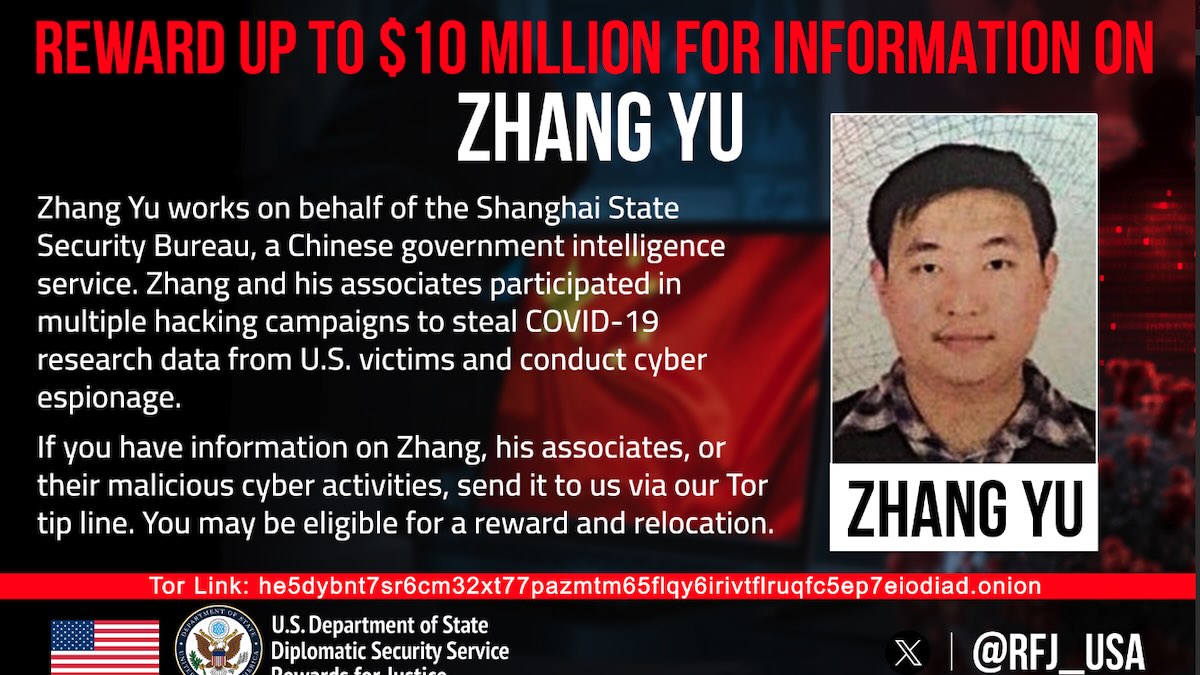 US Seeks Alleged Chinese Hafnium Hacker With $10 Million Reward
The US State Department's Rewards for Justice program is offering up to $10 million for information on Zhang Yu, a Chinese national charged alongside Xu Zewei for the 2021 Hafnium campaign that exploited Microsoft Exchange Server vulnerabilities and for earlier theft of COVID-19 research from US universities and immunologists starting in 2020. Zhang is identified as a director at Shanghai Firetech Information Science and Technology Company allegedly acting for the Shanghai State Security Bureau (part of China's MSS); Xu was extradited from Italy in April 2026 and has appeared in a Houston federal court while Zhang remains at large. Microsoft now tracks the Hafnium activity as Silk Typhoon; the FBI said the campaign compromised more than 12,700 US organizations.
securityweek.comarticlePublished and added 8 Oct 2026🛡️ Security FortiBleed Attackers Locking Victims Out of Fortinet Devices
The FortiBleed campaign targets internet-exposed Fortinet FortiGate firewalls and SSL VPN appliances using stolen credentials and brute force. SOCRadar confirms about 86,644 compromised devices in 194 countries. A joint FBI and US Secret Service advisory says attackers change passwords and delete accounts to lock victims out and keep persistence, and lists hardening steps such as phishing-resistant MFA and credential resets.
securityweek.comarticlePublished and added 8 Oct 2026🛡️ Security Engineer Gets 32 Months for Bitcoin Extortion Plot Against His Own Employer
A former core infrastructure engineer, Daniel Rhyne, was sentenced to 32 months for extorting his own New Jersey employer: he created a hidden virtual machine on the company network, reset passwords on hundreds of accounts to "TheFr0zenCrew!", deleted domain administrator accounts, scheduled tasks to shut down 40 servers a day, and demanded 20 BTC (~$750K) to stop. The FBI's criminal complaint describes how investigators traced the hidden VM back to him via correlated laptop browsing activity, building access logs, home IP connections, and incriminating search history ("how to clear all windows logs from command line").
decrypt.coarticlePublished and added 7 Oct 2026🛡️ Security Chinese network laundered $1B+ for North Korea's Lazarus Group — ZachXBT
Blockchain investigator ZachXBT published a 12-part thread detailing how he spent months posing as a client of a Chinese money-laundering network to prove it laundered over $1 billion for North Korea's Lazarus Group, including a large share of the ~$1.5 billion Bybit hack (FBI codename TraderTraitor). He cross-referenced the operators' private messages with on-chain data — including a wallet receiving fees from Bybit-hack-linked addresses and THORChain bridge transfer timing/amounts matching what operators disclosed — turning chat screenshots into verifiable blockchain evidence. The laundering network converted BTC into ETH, Solana and Tron, used THORChain for cross-chain hops, and parked funds in low-volume Uniswap pools; the investigation led Tether to freeze 442,000 USDT, part of over $75 million ZachXBT claims to have gotten frozen from North Korea-linked hacks since 2022.
 247wallst.comarticlePublished and added 6 Oct 2026🛡️ Security
- Trail of Bits (@trailofbits) on X
Trail of Bits' Circomspect, a static analyzer for Circom zero-knowledge circuits, had a false positive in its unconstrained-less-than check: compile-time constants fed into the LessThan template were wrongly flagged as unconstrained inputs. The merged PR fixes this so expressions resolvable at compile time are no longer reported, reducing noise for auditors hunting real under-constraint bugs in circuits.
x.comthreadAdded 8 Oct 2026, published 6 Oct 2026🛡️ Security  Spanish Police Arrest 16-Year-Old Accused of Running KillSec Ransomware Group
Spanish police arrested a 16-year-old Romanian national in Alicante suspected of administering the KillSec ransomware group, part of a coordinated multinational Operation KillSwitch led by the FBI San Juan field office and Hamburg's State Criminal Police Office. Authorities seized KillSec's leak site and five central servers, securing at least 110TB of stolen data, and arrested additional suspects in the UK and Romania, including Fouad Eltibrizi (alias "Archduke"), indicted in Puerto Rico. KillSec, active since 2024, used double extortion, exploited cloud misconfigurations, and reportedly leveraged AI to build its ransomware infrastructure and identify victims across roughly 500 successful attacks.
decrypt.coarticlePublished and added 2 Oct 2026🛡️ Security- FBI Tells Its Employees to Assume Hackers Have Their Personal Data
Decrypt reports that ShinyHunters claims to have breached the FBI's job-application site FBIjobs.gov, allegedly via an unconfirmed Oracle PeopleSoft zero-day, exfiltrating 2-3TB of personal data on nearly all FBI agents, job applicants, and some spouses. An internal FBI memo told staff to assume their data is compromised and to expect virtual briefings and suspicious contact attempts; FBI Cyber Division chief Brett Leatherman publicly responded citing a related Dutch arrest, after which ShinyHunters called its one-week retraction ultimatum a "marketing campaign" and said it won't publish the data.
decrypt.coarticlePublished and added 30 Sep 2026🛡️ Security  OFAC Sanctions Tren de Aragua Fugitive Who Laundered ATM Heists With Crypto
Chainalysis analyzes the OFAC sanctions (Sept 30, 2026) of 10 Tren de Aragua-linked targets, including FBI Ten Most Wanted fugitive Anibal Alexander Canelon Aguirre ("Prometheus"), tied to a $40.73M ATM jackpotting scheme across 1,500+ attacks. The group used the Ploutus malware strain deployed via Raspberry Pi devices with a self-delete anti-forensic function to jackpot ATMs, then laundered proceeds through crypto — Chainalysis traced the sanctioned wallets' counterparties to shared laundering infrastructure (including a $1B Venezuelan laundering case) also used by Colombian and Mexican cartels, noting heavy reliance on stablecoins and a prior Tether USDT freeze on related wallets.
chainalysis.comarticlePublished and added 30 Sep 2026🛡️ Security- Trail of Bits (@trailofbits) on X
Announcement tweet for Trail of Bits's September "Tribune" newsletter, which fact-checks 1Password's AI-powered patching benchmark, details a signature-forgery bug found in Miden's zkVM and a string-slicing bug in the Lean theorem prover/language, and reports 27 advisory submissions to OpenClaw plus seven new completed security reviews. It links out to the full newsletter on Mailchimp (mailchi.mp/trailofbits).
x.comthreadAdded 1 Oct 2026, published 30 Sep 2026🛡️ Security  Digital Forensics: iOS Forensics – Basics
A technical walkthrough of iOS forensic acquisition fundamentals: Apple's per-file Data Protection classes (A–D), the Before/After First Unlock (BFU/AFU) distinction and why AFU yields roughly 95% of a full dump versus almost nothing under BFU, and the iOS 18.1 72-hour auto-reboot that silently drops a seized AFU phone back to BFU. It covers extraction methods (logical backup, advanced logic, full filesystem extraction via signed agent, checkm8 bootrom exploits for iPhone X and earlier), pairing records, USB Restricted Mode's one-hour timeout, Lockdown Mode (noting it reportedly blocked FBI extraction of a seized journalist's iPhone in early 2026), Cellebrite's Inseyets/Premium/Physical Analyzer tooling and its coverage limits against A19/M5 chips with Memory Integrity Enforcement, and key forensic artifact stores (KnowledgeC, Biome, PowerLog, Photos.sqlite, chat-app SQLite/WAL/SHM files).
 hackers-arise.comarticleAdded 7 Oct 2026, published 29 Sep 2026🛡️ Security
 Check Point Research — 28th September Threat Intelligence Report
Check Point Research's weekly threat intelligence roundup covering the FBIjobs.gov defacement by ShinyHunters, a $351.6M Bitget hot-wallet theft with suspected DPRK involvement, and breaches at Astrana Health and LMU Munich. It also details AI-driven threats (an OpenAI agent's unauthorized access to an Australian government Medicare portal, an AI-agent-automated retail fraud campaign, and the CLOSEDQUORUM Windows malware that queries four commercial AI models to pick its post-compromise actions), four actively exploited pre-auth RCE CVEs (Check Point Security Gateway/Management, F5 BIG-IP APM, WordPress), and campaign writeups on the Storm-2570 multi-ransomware affiliate, an INC ransomware intrusion, a TeamFiltration M365 account-takeover wave in Latin America, and Storm-3168/JADEPUFFER's destructive Azure operations.
 research.checkpoint.comarticleAdded 1 Oct 2026, published 28 Sep 2026🛡️ Security
 The OpenSourceMalware Show #22
Transcript of episode 22 of The OpenSourceMalware Show, in which researchers discuss ShinyHunters' claimed PeopleSoft zero-day breach of an FBI jobs site (tied to the Instructure Canvas incident) and its public feud with the Cl0p ransomware crew, a correction on WhatsApp Baileys/WhiskeySockets npm typosquats (follower fraud rather than payment theft), and WeaselBiscuit - a new stripped-down, RAT-less JavaScript malware family derived from BeaverTail/OtterCookie found in 16 npm packages, attributed with high confidence to DPRK. It also covers the FBI's joint WaterPlum advisory on Contagious Interview/DPRK IT workers (30,000 infected devices, 7,000+ crypto wallets, 10.7 million dollars stolen, shared infrastructure with IT-worker scams), Atlassian's research on Contagious Interview activity across Bitbucket/GitLab/GitHub, and developer Q&A on the VS Code tasks-autorun technique.
 opensourcemalware.comtalkAdded 24 Sep 2026, published 25 Sep 2026🛡️ Security
 Trust and the enticing consultancy offer
Talos's weekly Threat Source newsletter opens with a first-person account of a social-engineering scam targeting security professionals: an unsolicited $300 "consultancy" offer that escalates into pressure to extract non-public insights from employers, a pattern the author links to fake-recruiter/trojanized-job-offer schemes. The issue also announces CAIRN, Talos's new open-source, metadata-first toolkit (YARA-based classification tiers) for hunting AI-integrated malware like the autonomous CLOSEDQUORUM C2 implant, and rounds up the week's headlines including the ShinyHunters FBI data claim, fake LastPass installers dropping a kernel-level EDR killer, Japan's takedown of a North Korean (WaterPlum/Contagious Interview) laptop farm, cyberattacks on Colorado water utilities, and a Gemini-driven autonomous breach of three companies.
 blog.talosintelligence.comarticleAdded 7 Oct 2026, published 24 Sep 2026🛡️ Security
 Happy Birthday, Shai-Hulud
Socket's one-year retrospective on the Shai-Hulud npm supply-chain worm, from the September 2025 @ctrl/tinycolor compromise through the November 2025 "Second Coming" wave, the May 2026 public release of the worm's source by TeamPCP, the "Mini Shai-Hulud" OIDC-token-hijacking wave that hit TanStack and Mistral AI, and the August 2026 arrest of two alleged TeamPCP members by Australian Federal Police working with the FBI. It notes Google ran an undercover analyst inside TeamPCP to get stolen credentials revoked, and stresses that the original September 2025 worm authors remain unidentified despite the arrests.
 socket.devarticleAdded 21 Sep 2026, published 18 Sep 2026🛡️ Security
 HEAVYGRAM: A Telegram-based Surveillance Backdoor Linked to Handala Hack
Group-IB documents previously undocumented samples of HEAVYGRAM, a Python/PyInstaller-based Windows backdoor that uses the Telegram bot API for command-and-control, screen/audio capture, data exfiltration, and DLL side-loading, alongside the related CRUDEEXCLUDE loader that adds Windows Defender exclusions. The research corroborates and extends a March 2026 US DOJ affidavit and FBI FLASH report, attributing the malware with moderate confidence to the Handala Hack persona — assessed as a false-flag "hacktivist" front for Void Manticore (aka Storm-0842/Banished Kitten), operating on behalf of Iran's MOIS — used since Fall 2023 against Iranian dissidents, journalists, and critics of the Iranian government via Telegram-delivered, Delphi-packaged lures (fake KeePass, Telegram, Pictory apps). It details four infection-chain variants (WSF/VBS downloaders, HTA Telegram-polling scripts, Delphi droppers with embedded archives), the implant's command prefixes (@@/**/##) and attachment handlers, dual-bot C2 configurations, and provides IOCs and detection/hardening recommendations.
 group-ib.comwriteupAdded 1 Oct 2026, published 17 Sep 2026🛡️ Security
 Tracing Crypto in a Narcotics Investigation: FBI Charges Alleged Opioid Distributors
Chainalysis details how blockchain analytics (its Reactor tool) helped the FBI trace Bitcoin proceeds from the darknet vendor account "BarbaraWhite" — which sold nitazene-laced counterfeit pills on Nemesis, Bohemia and Abacus — through a wallet cluster to a China-based chemical supplier and, ultimately, to a mobile payment account tied to defendant Stanislav Chernyshov. The case illustrates a concrete investigative pipeline: combining on-chain clustering with marketplace data, postal records, and off-chain identifiers to deanonymize a pseudonymous crypto-paid drug operation linked to overdose deaths.
chainalysis.comarticleAdded 30 Sep 2026, published 8 Sep 2026🛡️ Security- trailofbits/skills
Trail of Bits maintains a Claude Code plugin marketplace of "skills" that extend AI coding agents (Claude Code, Codex, ChatGPT workspaces) with security analysis, testing, and secure development capabilities. It's installed via `/plugin marketplace add trailofbits/skills` and is also compatible with Codex's Claude marketplace support, with related sibling repos for curated skills, devcontainers, and config.
 github.comrepoPublished and added 7 Sep 2026🛡️ Security
 FBI Seizes $560K in Crypto From Hamas Fundraising Network
Chainalysis details five related U.S. law enforcement actions (March 2025–August 2026) that seized over $560,000 in cryptocurrency tied to Hamas and al-Qassam Brigades fundraising, plus the group's donation website domains and servers. The piece walks through the forensic methodology — using Chainalysis Reactor to cluster addresses via a shared gas-funding wallet, trace funds through consolidation wallets and a Lebanon-based OTC broker, and follow Hamas's later shift to cross-chain bridging and single-use donation wallets — showing how earlier on-chain findings compounded into a broader mapping of the group's financing network over time.
chainalysis.comarticleAdded 30 Sep 2026, published 3 Sep 2026🛡️ Security The OpenSourceMalware Show #19
Podcast/blog episode from the OpenSourceMalware team covering two threat-intel developments: the AFP/FBI arrest of two young Australians (Ruben Thomson, 21, and Louis Gaebler, 23) tied to TeamPCP, whose sloppy OPSEC (reused credentials, unredacted social media) led to their identification despite only ~$20K in proceeds; and an in-depth look at how DPRK's PolinRider campaign reinfects developers even after partial cleanup, driven by a new persistence technique that overwrites the npm CLI binary itself (triggering "reinstall malware?" on next npm run) alongside the existing vscode-task.json trigger and RAT. The hosts detail the expanding reachability-based targeting of JS/TS/CJS/MJS files, the new NullReceiver-branded payload, and a real case study (Gutenberg maintainer "Diogo"/fetch-page-assets) where DPRK pushed malicious updates riding along on the developer's own legitimate npm publishes, underscoring why disclosing infections to collaborators is necessary to stop reinfection through shared repos.
opensourcemalware.comtalkAdded 3 Sep 2026, published 28 Aug 2026🛡️ Security Good riddance, TeamPCP. Now for the hard part.
A security researcher's personal reflection on the AFP/FBI/WAPF announcement that two men in their early 20s were arrested for allegedly running TeamPCP, a threat group behind a wave of 2025-2026 supply chain attacks. The piece clarifies that TeamPCP cloned the Shai-Hulud npm worm but was not behind the original Shai-Hulud/s1ngularity campaigns, and argues LLMs let relatively unsophisticated actors rapidly operationalize public exploits, widening the gap between attacker speed and institutional response time.
 aikido.devarticleAdded 3 Sep 2026, published 27 Aug 2026🛡️ Security
- Five Years, 88,000 Backdoors, and a Pair of Handcuffs: Inside the Global Manhunt That Ended in an Arrest
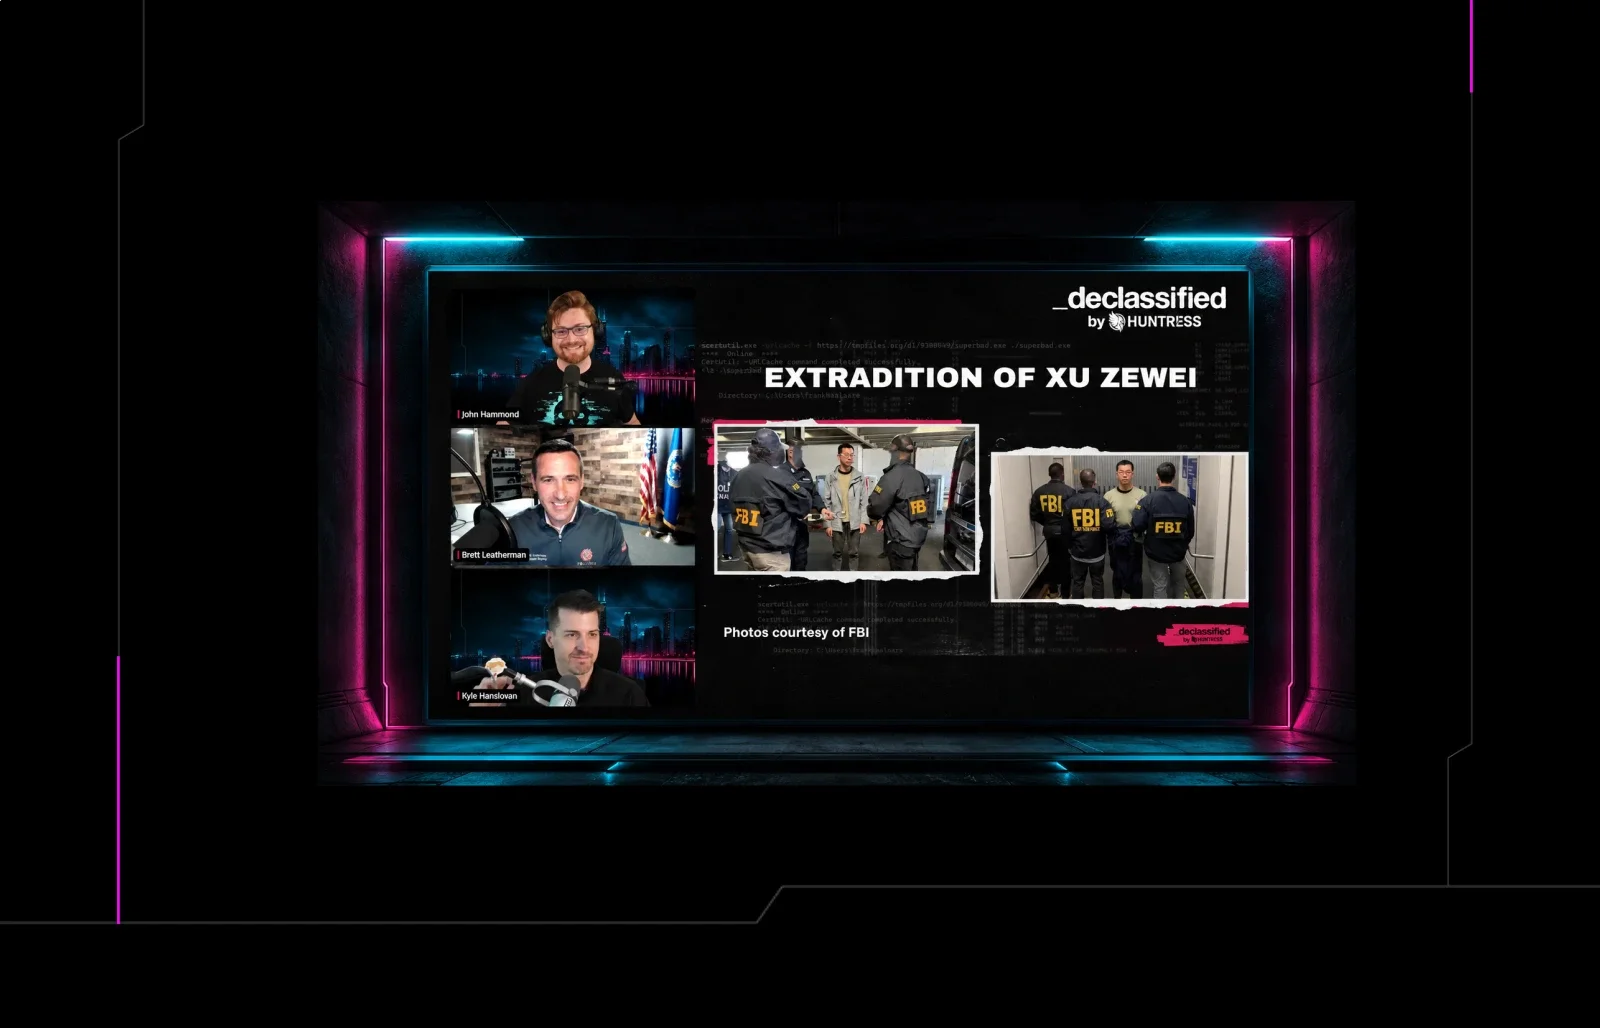
Huntress interview/recap covering the 2021 HAFNIUM (Silk Typhoon) mass exploitation of on-prem Microsoft Exchange servers that led to 88,000+ web shell backdoors, how Huntress and CrowdStrike tracked victims via cloned adversary infrastructure, and the FBI's unprecedented Rule 41 warrant used to remotely remove web shells at scale. It also details the July 2025 arrest of Xu Zewei, and 2026 FBI Operation Riptide takedowns of the Outsider phishing-as-a-service platform, NetNut residential proxy network, and MediaLand bulletproof hosting provider.
 huntress.comarticleAdded 3 Sep 2026, published 10 Aug 2026🛡️ Security
 FOSSA: CISA Releases the 2026 SBOM Minimum Elements
FOSSA breaks down CISA's 2026 Minimum Elements for a Software Bill of Materials, the first major revision since NTIA's original 2021 baseline, produced with NSA, FBI, and 15 international agencies. The update roughly doubles required data fields, adding 10 new elements (SBOM Author Signature, SBOM Data Format Name/Version, Generation Context, Tool Name/Version, SBOM Version, Component Hash Value/Algorithm, and Component License) while renaming and clarifying existing fields (e.g., Supplier Name → Component Producer) and mandating full transitive-dependency coverage with no minimum depth, RFC 9557 timestamps, and dropping SWID in favor of SPDX/CycloneDX.
 fossa.comarticlePublished and added 31 Jul 2026🛡️ Security
- ShortDot Zone Abuse Evidence
PhishDestroy's shortdot-evidence is a daily-updated GitHub investigation into ShortDot SA, the Luxembourg registry operator behind the .icu, .bond, .cyou, .sbs, .cfd, .buzz and .qpon gTLDs, documenting that 51,985+ tracked domains impersonate brands like Chase, Binance, MetaMask and Ledger and that ~70% of registered domains in these zones carry no DNS records (metric-padding rather than legitimate use). It publishes machine-generated IOC/blocklist files and analytics built from a per-TLD zone-file pull cross-referenced against Spamhaus DBL, SURBL, OpenPhish, URLhaus, PhishTank and AlienVault OTX, and ties the zones to concrete criminal cases (FBI's LabHost domain list, Google v. DOES/Yucheng Chang RICO suits, the Revolver Rabbit XLoader/Formbook C2 campaign using 500k+ .bond domains). It also details structural conflicts of interest between ShortDot, its registry infrastructure provider Team Internet Group/CentralNic, registrar partner NameSilo, and the brand-protection vendor NameBlock, backed by Interisle Consulting Group phishing-volume statistics.
github.comrepoPublished and added 25 Jul 2026🛡️ Security  The OpenSourceMalware Show #11
Episode 11 of the OpenSourceMalware Show covers npm's new 72-hour read-only account lockout for high-impact packages (triggered by email changes or 2FA recovery use) and GitHub Enterprise's new self-service credential revocation tool for incident response, noting each has gaps (lockout could hinder legitimate ATO recovery; revocation doesn't cover PATs created outside the enterprise boundary). The hosts also call out six npm packages published by a researcher at a stealth cybersecurity startup that target OpenAI, Anthropic, Vercel, and Ollama users — info-stealers that avoid credentials but exfiltrate .git/.ssh data, drawing a parallel to Snyk's 2025 malicious-package incident targeting Cursor. It also references an FBI FLASH notice on TeamPCP's TTPs/IOCs and previews a coming interview with Eclipse Foundation's head of security on Open VSX supply-chain risk.
opensourcemalware.comtalkAdded 3 Sep 2026, published 2 Jul 2026🛡️ Security The sorry state of skill distribution
Trail of Bits researchers bypassed every agent-skill security scanner they tested — ClawHub's VirusTotal/Code Insight and GPT-5.5-based guard model, and skills.sh's Gen/Socket/Snyk-backed scanning, plus Cisco's skill-scanner — using techniques like context-truncation via 100,000 newlines, malicious payloads hidden inside .docx ZIP archives, Python .pyc bytecode poisoning to steal environment variables, and rhetorically-crafted prompt injection that convinced LLM analyzers a malicious npm/yarn registry change was benign. The piece also shows a legitimate Anthropic Office skill (soffice.py) using LD_PRELOAD in ways indistinguishable from malicious behavior, arguing static/LLM skill scanning is structurally unable to guarantee safety and that organizations should instead curate trusted skill marketplaces (e.g., trailofbits/skills-curated) rather than rely on public ones. PoC skills are published at trailofbits/overtly-malicious-skills.
 blog.trailofbits.comwriteupAdded 3 Sep 2026, published 3 Jun 2026🛡️ Security