 Binance Hack: Everything You Need to Know About the Biggest Crypto Heist in History
Decrypt's explainer on the roughly $6.4 billion theft from Binance hot wallets across about 10 blockchains. Binance traced it to a compromised DevOps engineer laptop plus further breach points, and on Ethereum the attacker used 50 pre-signed EIP-7702 authorizations to turn a hot wallet into a sweeper. Chainalysis and TRM Labs attribute it to TraderTraitor; Tether and Circle froze about $2.3 billion.
 decrypt.coarticlePublished and added 31 Oct 2026🛡️ Security
 Weekly Research Brief: Binance Hacked; Hyperliquid on Wall Street; Prediction Markets’ Brazil ‘Miss’
Galaxy Research's weekly brief of 30 October 2026 opens with the Binance hack: about $6.3b drained across 10 blockchains, attributed by TRM Labs and Chainalysis to TraderTraitor (Lazarus-linked). The attacker used EIP-7702 with 50 pre-signed authorizations on Ethereum, and Binance's preliminary finding is a compromised DevOps laptop reaching a service container. Tether and Circle froze about $2.6b. The other sections cover Hyperliquid and prediction markets.
 galaxy.comarticleAdded 30 Oct 2026🛡️ Security
 Here We Go Again: Binance Loses $6.3b in Largest Robbery in History
Galaxy Research newsletter on the roughly $6.3b drained from Binance across 10 blockchains, which TRM Labs and Chainalysis attribute to TraderTraitor. On Ethereum the attacker used EIP-7702 to turn a hot wallet into a sweeper contract backed by 50 pre-signed authorizations. Binance's preliminary finding is a compromised DevOps laptop, with no wallet key leak. Tether, Circle, Ripple and World Liberty froze about $2.7b; Galaxy also assesses Binance's ability to cover losses.
galaxy.comarticleAdded 30 Oct 2026🛡️ Security Binance Just Suffered the Biggest Hack in Crypto History. What Now?
Bankless report on the Binance hack of $6.3 billion, which Binance's preliminary investigation traced to a compromised DevOps engineer's laptop with access to withdrawal-authorizing systems. TRM Labs found valid EIP-7702 authorizations on Ethereum, and nine other chains were drained through normally signed transactions. TRM and Chainalysis link it to North Korea's TraderTraitor. Tether and Circle froze about $3 billion, and Binance says SAFU and corporate cash will cover the losses.
 bankless.comarticlePublished and added 30 Oct 2026🛡️ Security
 Secret Service, FBI Join Binance Hack Probe as Circle Freezes $823 Million
Decrypt reports that Binance is working with the FBI and U.S. Secret Service after a theft of about $6.4 billion, which TRM Labs and Chainalysis attribute to North Korea's TraderTraitor group, also linked to the February 2025 Bybit hack. Circle froze about $823 million in USDC and Tether froze USDT, though the page gives differing Tether totals. Binance first suspected a compromised DevOps engineer laptop, found more breach points, and saw no evidence of leaked wallet private keys.
decrypt.coarticlePublished and added 30 Oct 2026🛡️ Security Binance hack: the largest robbery in financial history
Binance hack analysis from 21shares on the 29 October 2026 theft of about $6.3 billion from Binance. Binance's initial finding points to a compromised DevOps engineer's laptop with no sign of a leaked wallet key. Chainalysis attributes it to North Korea with high confidence, and about $3 billion was frozen by Tether, Circle and the Arbitrum Security Council. The attacker also borrowed about $44.6 million of WETH on Aave. Binance says SAFU and company funds will cover all losses.
 21shares.comarticlePublished and added 30 Oct 2026🛡️ Security
- Binance says it has $6.34 billion ready to cover hack losses
The Block reports that Binance says it has set aside $6.34 billion of its own funds to cover a hack it puts at about $6.3 billion. Co-CEO Richard Teng says the entry point was a compromised DevOps laptop and no private key leak was found. About $3 billion was frozen by Tether, Circle, Ripple and others, withdrawals are suspended, and TRM Labs sees parallels with North Korean attacks. Technical detail is thin.
 theblock.coarticlePublished and added 30 Oct 2026🛡️ Security
 Binance Finds 'Additional Points of Breach' in $6.3B Hack
Binance estimated the October 2026 security incident at about $6.3 billion and said it found "additional points of breach" beyond the compromised DevOps engineer laptop it first named. The attacker reached a service container and submitted unauthorized withdrawals, with no wallet private key leak found. Arkham counted $6.01 billion taken from hot wallets on nine chains; Tether and Circle froze about $1.8 billion in stablecoins. About $3 billion is frozen onchain; withdrawals stay suspended.
decrypt.coarticlePublished and added 30 Oct 2026🛡️ Security Binance probes a suspected cryptocurrency breach: $6.3B affected, about $3B frozen
Binance disclosed a suspected security incident on 29 October 2026, estimating $6.3 billion affected and about $3 billion frozen. Binance's early finding is that a compromised DevOps engineer's laptop let an attacker reach a service container and submit unauthorized withdrawals, with no evidence of wallet private-key leakage. TRM Labs suspects TraderTraitor, the group tied to the February 2025 Bybit theft. Tether, Circle and Ripple froze funds.
 en.cryptonomist.charticlePublished and added 30 Oct 2026🛡️ Security
 Binance Hacker Hunts for Exit Ramps as DeFi Exchanges Pause Markets
Decrypt reports on wallets linked to the suspected Binance hack (at least $5.5 billion drained, 29 October 2026) that swap freezable stablecoins for ETH via Uniswap and borrow 19,762 ETH on Aave. About 253,000 ETH (roughly $570 million) sits idle in two wallets. Tether, Circle and Ripple froze over $2 billion plus about $200 million RLUSD, and Aave and Kamino paused markets. Tornado Cash appears only as funding for the attack address.
decrypt.coarticlePublished and added 29 Oct 2026🛡️ Security Binance probes potential $5.8 billion crypto-theft hack
Binance is investigating a possible breach involving up to $5.8 billion in assets, which would exceed the $1.5 billion Bybit theft of February 2025. Tether froze over $1.567 billion in USDT and Circle over $800 million in USDC. Arkham tracks 55 addresses labelled "binance-hacker-1029" holding about $5.78 billion, but that is wallet holdings, not a confirmed theft amount. The cause is not yet known.
 bleepingcomputer.comarticleAdded 30 Oct 2026, published 29 Oct 2026🛡️ Security
- Binance Drained of $5.5 Billion in Suspected Hack, Tether and Circle Freeze $1.8 Billion
Decrypt reports that at least $5.57 billion left Binance-linked hot wallets on Ethereum, Bitcoin and Tron on 29 October 2026, which would be the largest crypto hack on record. On-chain analysts point to an EIP-7702 delegation, installed from a Tornado Cash-funded address minutes before the first sweep. Tether and Circle froze about $1.8 billion. Binance has not confirmed the hack, and how the attacker obtained the signature is unknown.
decrypt.coarticlePublished and added 29 Oct 2026🛡️ Security - Techjunkie Aman (@Techjunkie_Aman) on X
ns2jb is a software-only jailbreak for the Nintendo Switch 2 running firmware 23.0.1, announced in a post on X. It runs arbitrary native code, allows save dumping, reverse engineering and game modding, and reaches most peripherals via MMIO. It is tethered (rerun after reboot) and gives no CFW or full kernel control. The post says Mario Kart World has been modded with custom characters. It gives no technical detail on the exploit chain.
 x.comthreadAdded 24 Oct 2026, published 22 Oct 2026🛡️ Security
- Explained: The Ledger Supply Chain Incident (October 2026)
The Ledger supply chain incident of October 2026: on-chain analysis estimates $93 million was stolen after devices sold by the reseller CryptoBilis carried an implant with an eSIM. The implant watched the screen during setup, captured the 24-word recovery phrase and sent it over LTE, without touching the Secure Element. Tether froze about $10 million USDT. Reports from Changi Airport and MediaMarkt stores remain unconfirmed.
 halborn.comarticleAdded 20 Oct 2026🛡️ Security
 Hackers Jailbreak iPhone 18 Pro on Stage, and It Survives a Reboot
Reports that Calif.io demonstrated an untethered jailbreak of an iPhone 18 Pro on iOS 27.0.1 at Hexacon in Paris, showing root SSH access after a reboot and passcode unlock. The vulnerabilities are unnamed and no tool is public; Calif says it will publish later. The article notes Calif's prior use of Claude and Mythos Preview for exploit development, Apple's iOS 27 notes crediting Calif for two unrelated crash bugs, and the Apple mitigations (sandbox, PAC, secure boot chain) such a chain must defeat.
decrypt.coarticlePublished and added 16 Oct 2026🛡️ Security Weekly Research Brief: Ledger’s $91M Theft, Papertrade
Galaxy Research's weekly brief leads with the roughly $91M theft from Ledger devices sold via the reseller CryptoBilis. A hidden hardware implant read the 24-word recovery phrase off the screen during setup and sent it over LTE through an eSIM, leaving the Secure Element untouched so Genuine Check still passed. Galaxy's onchain tally covers 474 victim addresses, 88% of the value moved in one hour on Oct. 9, and about $56.6M was still parked as of Oct. 15, with Tornado Cash use and a $10M Tether freeze. It places the theft alongside the Coldcard weak-seed, Liquid peg-out and Bitget compromises, and ends with buyer and custody advice. The Papertrade and OCC debanking sections are unrelated to security.
galaxy.comarticleAdded 16 Oct 2026🛡️ Security Inside the $91M Ledger Reseller Wallet Theft
Galaxy Research newsletter piece on the roughly $91M theft from buyers of Ledger hardware wallets sold by the reseller CryptoBilis. A hidden component reads the 24-word recovery phrase off the screen during setup and sends it over LTE via an eSIM. The Secure Element and Genuine Check are untouched, so the check passes on tampered units. It traces the drain across 474 victim addresses on Bitcoin, Ethereum and TRON, including 88% of the value moving in one hour on Oct. 9, and the laundering and freezes (Tornado Cash, Tether). It also places the incident among the quarter's other custody and infrastructure failures (Coldcard weak seeds, Liquid, Bitget) and gives buying and operational guidance.
galaxy.comarticleAdded 16 Oct 2026🛡️ Security Ledger’s Atom device adds tamper detection after a recovery-phrase breach
News report on a Southeast Asia supply-chain breach in which Ledger devices sold via resellers such as CryptoBilis were modified with hidden chips. The chips read 24-word recovery phrases from the screen signals during setup and sent them out over LTE. Tether froze $10M USDT tied to the theft, and Ledger suspended sales in several Asian markets. It also covers Ledger's Android-based Atom signer, which adds a protective enclosure, screen and back-cover removal sensors with their own battery, tamper-evident packaging, and website-only initial sales.
en.cryptonomist.charticlePublished and added 15 Oct 2026🛡️ Security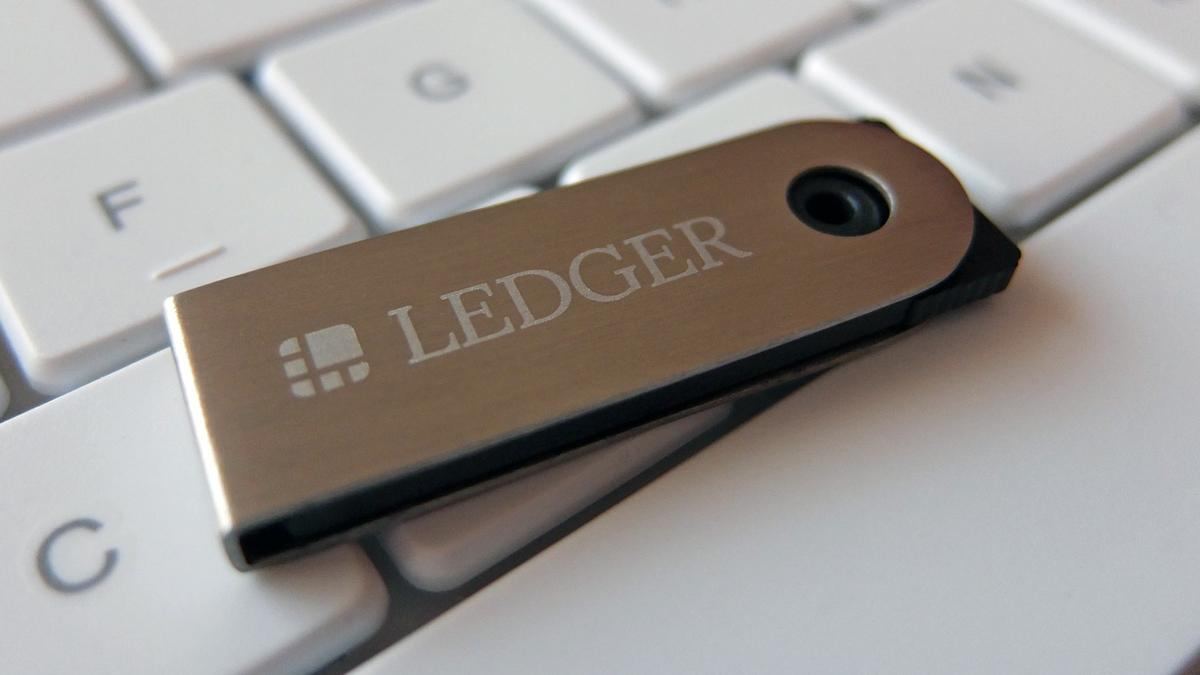 Ledger says 'spy' chip inside CryptoBilis Ledger devices transmitted wallet keys over mobile network
Ledger says some hardware wallets sold by the reseller CryptoBilis contained a covert implant inside the enclosure. Its microcontroller recognised the 24-word recovery phrase when it was displayed during setup and sent it to attackers over LTE using an eSIM. Ledger says its secure element, OS, transaction signing and internal systems were not compromised. Onchain researchers estimate up to $93.2M lost across more than 300 wallets, and Tether froze $10M of USDT. Ledger's guidance is not to initialize units bought from the reseller and to move funds to a new device with a fresh phrase if already used.
 coindesk.comarticlePublished and added 13 Oct 2026🛡️ Security
 Ledger Says All Confirmed Cases in Suspected $87M Drain Tied to Reseller CryptoBilis
Decrypt reports Ledger's 72-hour update: all confirmed wallet-draining cases involve devices sold by Southeast Asian reseller CryptoBilis, which has stopped hardware wallet sales. Onchain investigators Specter and YFarmX traced over $86M in suspected thefts across Ethereum, Tron and Bitcoin. They describe laundering through Tornado Cash, Zcash's shielded pool and a USDT-to-USDD swap to avoid Tether freezes. An unverified claim of tampered devices (extra cables, LTE module) bought at European retail stores is also covered. Ledger advises CryptoBilis buyers not to set up devices and to move funds to a new seed phrase on a device bought from Ledger.
decrypt.coarticlePublished and added 12 Oct 2026🛡️ Security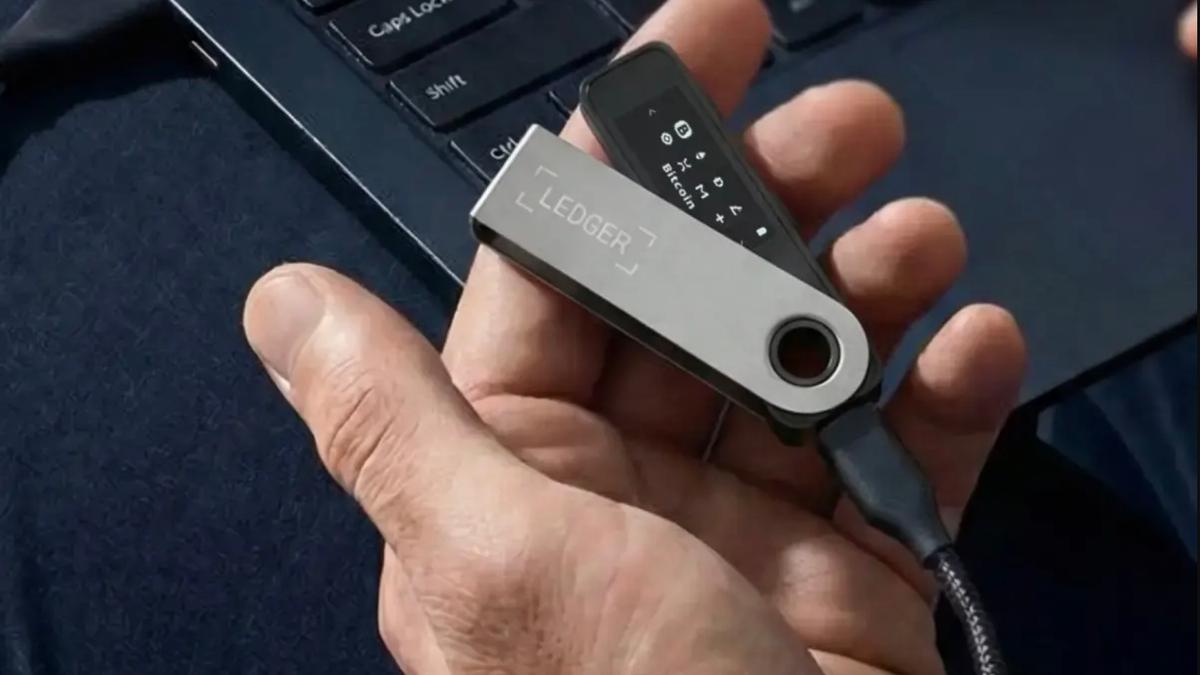 Ledger claims CryptoBilis cases are limited as up to $93M is traced, $10M frozen
CoinDesk reports that up to $93–94.5M in mostly USDT and TRON tokens was drained from 315–521 wallets across six or seven blockchains. The wallets were tied to Ledger hardware wallets sold by the authorized reseller CryptoBilis. Ledger confirmed an unauthorized hardware implant in at least one device but did not say how the devices were tampered with. Tether froze $10M, some funds moved through Tornado Cash and Zcash, and Ledger told affected users not to set up unused devices and to move funds to a new device with a fresh recovery phrase. The figures come from Bitquery and YFarmX onchain estimates, not a confirmed Ledger loss total.
coindesk.comarticlePublished and added 12 Oct 2026🛡️ Security- CISA AA26-281A: Chinese Government-linked Actors Combine Automated and Hands-on Hacking Tools to Steal Data
Joint FBI/CISA/NSA and allied-agency advisory on China-linked actors enabled by Integrity Technology Group (overlapping with Flax Typhoon, Ethereal Panda, Red Juliett). It details their TTPs: open-source scanners and the MicroScan exploit-script app, an XSS credential-harvesting payload dropping live700_v1.exe, EBurst password spraying against Exchange/O365, SoftEther VPN persistence, DCSync via DC.exe, and email theft via the Curlc4.txt PHP bot and the office-cli utility. It also provides IOCs, MITRE ATT&CK mappings, CVEs, incident response steps, and mitigations.
 cisa.govadvisoryAdded 9 Oct 2026🛡️ Security
 US Disrupts Chinese State-Sponsored Hacking Tools
The US, alongside UK, Australian, Canadian, Japanese, New Zealand, and Spanish agencies, disrupted MicroScan and FishHub, hacking tools built by China's Integrity Technology Group and used by the state-sponsored actor Flax Typhoon (aka Ethereal Panda, Red Juliett, Storm-0919, UNC5007) against US, Japanese, Polish, and Taiwanese critical infrastructure and universities. MicroScan is a Python-based scanner with over 1,300 penetration-testing scripts targeting Apache Struts, Jenkins, WebLogic Server, WordPress, OpenSSL, and other services, delivered via a Mirai-derived IoT botnet; FishHub let operators remotely search and exfiltrate files from victim networks. The advisory also details the group's broader toolkit (SoftEther VPN for persistence, EBurst for Exchange password spraying, DC.ex for Active Directory data extraction) and the seizure of the domains used to access the tools.
 securityweek.comarticlePublished and added 9 Oct 2026🛡️ Security
 Morning Minute: Ethereum Researcher Says AI May Break Crypto Encryption Before Quantum
A daily crypto-market newsletter segment reporting Ethereum Foundation researcher Justin Drake's warning that AI, not quantum computing, may be the first to break ECDSA — the elliptic-curve signature scheme securing Bitcoin and Ethereum — potentially within months by recovering private keys from exposed public keys using large GPU clusters. Drake calls for industry-wide "bunker mode": migrating self-custodied funds to fresh addresses whose public keys remain hashed/hidden, and names exchanges (Binance, Bitbank, Robinhood, Bitfinex, Tether) he wants to harden cold storage. The article also notes a concurrent Europol report flagging crypto wallets with already-revealed public keys as the main weak point for future quantum/AI attacks, since those cannot be retroactively protected.
decrypt.coarticlePublished and added 8 Oct 2026🛡️ Security Ethereum Researcher Says AI May Break Encryption Before Quantum Does
Ethereum Foundation researcher Justin Drake warns that AI-driven mathematical advances could break ECDSA — the signature scheme securing Bitcoin and Ethereum — before quantum computers do, potentially recovering a private key from an exposed public key in about a week using a large GPU cluster. He calls for "bunker mode": a controlled mass migration of funds to fresh addresses whose public keys have never been exposed, urges major custodians (Binance, Bitbank, Robinhood, Bitfinex, Tether) to harden cold storage, and pushes Ethereum to accelerate its move to hash-based (post-quantum) cryptography.
decrypt.coarticlePublished and added 7 Oct 2026🛡️ Security Inside EQIBank’s $84M seizure
Protos investigative article unpacking the DOJ's $84M civil forfeiture against Capstone Limited, a payment processor used by Dominica-based EQIBank (which handles Tether reserves), for misrepresenting itself to Wells Fargo, JPMorgan Chase and Citibank as a software firm rather than a money services business. The piece uses OSINT techniques — corporate registry tracing, shared-hosting IP correlation, DNS lookups, and court filing cross-referencing — to map operator Kotaro Shimogori's decade-long history running shell payment processors (ComCopious, iCanPay, AuthPay, Pan Digital Network) for high-risk clients including gambling sites and, per the forfeiture complaint, impersonation-fraud scam proceeds funneled through Chase accounts. It also details EQIBank's EQIFi/EQX DeFi token, and links Marlin Capital Partners and Deltec Bank figures to Tether's banking history, drawing parallels to the earlier Crypto Capital Corp seizure.
 protos.comarticleAdded 8 Oct 2026, published 7 Oct 2026🛡️ Security
 Chinese network laundered $1B+ for North Korea's Lazarus Group — ZachXBT
Blockchain investigator ZachXBT published a 12-part thread detailing how he spent months posing as a client of a Chinese money-laundering network to prove it laundered over $1 billion for North Korea's Lazarus Group, including a large share of the ~$1.5 billion Bybit hack (FBI codename TraderTraitor). He cross-referenced the operators' private messages with on-chain data — including a wallet receiving fees from Bybit-hack-linked addresses and THORChain bridge transfer timing/amounts matching what operators disclosed — turning chat screenshots into verifiable blockchain evidence. The laundering network converted BTC into ETH, Solana and Tron, used THORChain for cross-chain hops, and parked funds in low-volume Uniswap pools; the investigation led Tether to freeze 442,000 USDT, part of over $75 million ZachXBT claims to have gotten frozen from North Korea-linked hacks since 2022.
 247wallst.comarticlePublished and added 6 Oct 2026🛡️ Security
- ZachXBT says he fronted $349,700 to infiltrate alleged Chinese launderers tied to Lazarus, Bybit hack
The Block reports ZachXBT's account of posing as a client and fronting $349,700 USDC to an alleged Chinese laundering vendor, "Jimmy Green", who claimed to have laundered most of the $1.5B Bybit hack proceeds for Lazarus Group. On-chain checks tied the vendor's receiving address to Bybit exploit blacklist wallets and matched a THORChain order to a bridge screenshot. Tether later froze 442,000 USDT from a $12M+ cluster.
theblock.coarticleAdded 10 Oct 2026, published 6 Oct 2026🛡️ Security  Crypto Sleuth ZachXBT Fronted $350K to Pose as a Client of Lazarus' Chinese Launderers
Decrypt reports on ZachXBT's account of infiltrating a Chinese money-laundering syndicate working for North Korea's Lazarus Group, by posing as a client ("fronted" $349.7K USDC) to a contact named "Jimmy Green" to gather intelligence on how Bybit's $1.5B hack proceeds were being laundered. The piece details the on-chain corroboration methods used (matching Telegram screenshots to Thorchain swap timing, wallet clustering across BTC/ETH/SOL/Tron) that exposed a $12M+ cluster of Bybit exploit funds, led to a 442K USDT Tether freeze, and separately traced $3M in fraud proceeds to Huione Guarantee, a Cambodian marketplace later targeted by FinCEN and shut down by Telegram.
decrypt.coarticlePublished and added 5 Oct 2026🛡️ Security OFAC Sanctions Tren de Aragua Fugitive Who Laundered ATM Heists With Crypto
Chainalysis analyzes the OFAC sanctions (Sept 30, 2026) of 10 Tren de Aragua-linked targets, including FBI Ten Most Wanted fugitive Anibal Alexander Canelon Aguirre ("Prometheus"), tied to a $40.73M ATM jackpotting scheme across 1,500+ attacks. The group used the Ploutus malware strain deployed via Raspberry Pi devices with a self-delete anti-forensic function to jackpot ATMs, then laundered proceeds through crypto — Chainalysis traced the sanctioned wallets' counterparties to shared laundering infrastructure (including a $1B Venezuelan laundering case) also used by Colombian and Mexican cartels, noting heavy reliance on stablecoins and a prior Tether USDT freeze on related wallets.
 chainalysis.comarticlePublished and added 30 Sep 2026🛡️ Security

Showing 30 of 31
Show more