Each feed is checked for new posts. Every post is read, and those that belong here join the catalog. What Trove read and did not keep stays on file, not shown.
CVE-2026-103572 is a remote code execution bug in Microsoft.VisualStudio.Copilot.Core.dll, shared by Visual Studio and SQL Server Management Studio. A trailing dot (for example `.mcp.json.`) bypasses the protected-filename check in EditsFunctionHandler.GetEditConfirmationTypeAsync, so a hijacked Copilot can rewrite its own MCP and settings files and run commands. The post covers path traversal and InstallationID leaks, indirect prompt injection demos, the October 2026 patch (GetFullPath), and a $0 bounty.
Visual StudioSQL Server Management StudioGitHub Copilot+3
Write-up of a BlueHat Asia 2026 talk on CVE-2026-65669, a critical SQL Server elevation of privilege in Copilot in SQL Server Management Studio. The read-only mode was only a regex classifier (LocalSqlExecutionAccessChecker) and was bypassed with DECLARE @p sysname='sp_executesql'; EXEC @p. The chain used indirect prompt injection through AGENTS.md and CONSTITUTION.md extended properties to take a db_owner to sysadmin, with data exfiltration via xp_dirtree and RestoreVerifyBackupFile.
SQL Server Management StudioMicrosoft SQL ServerCopilot in SSMS+2
Embrace The Red reproduces the "Stealing Reasoning Traces from Proprietary LLM APIs" attack against OpenAI GPT-5.6 Sol. An encrypted reasoning blob from Codex session files is replayed to GPT-5.6 Luna, across sessions and accounts, with a transcription jailbreak, and a password in the original trace is recovered. The paper decoded 315,320 public reasoning blocks and found 367 PII items and 182 credentials, so shared session files leak more than expected.
OpenAICodexLLM+1
GPT-5.6 SolMatthew GreenStealing Reasoning Traces from Proprietary LLM APIs+1
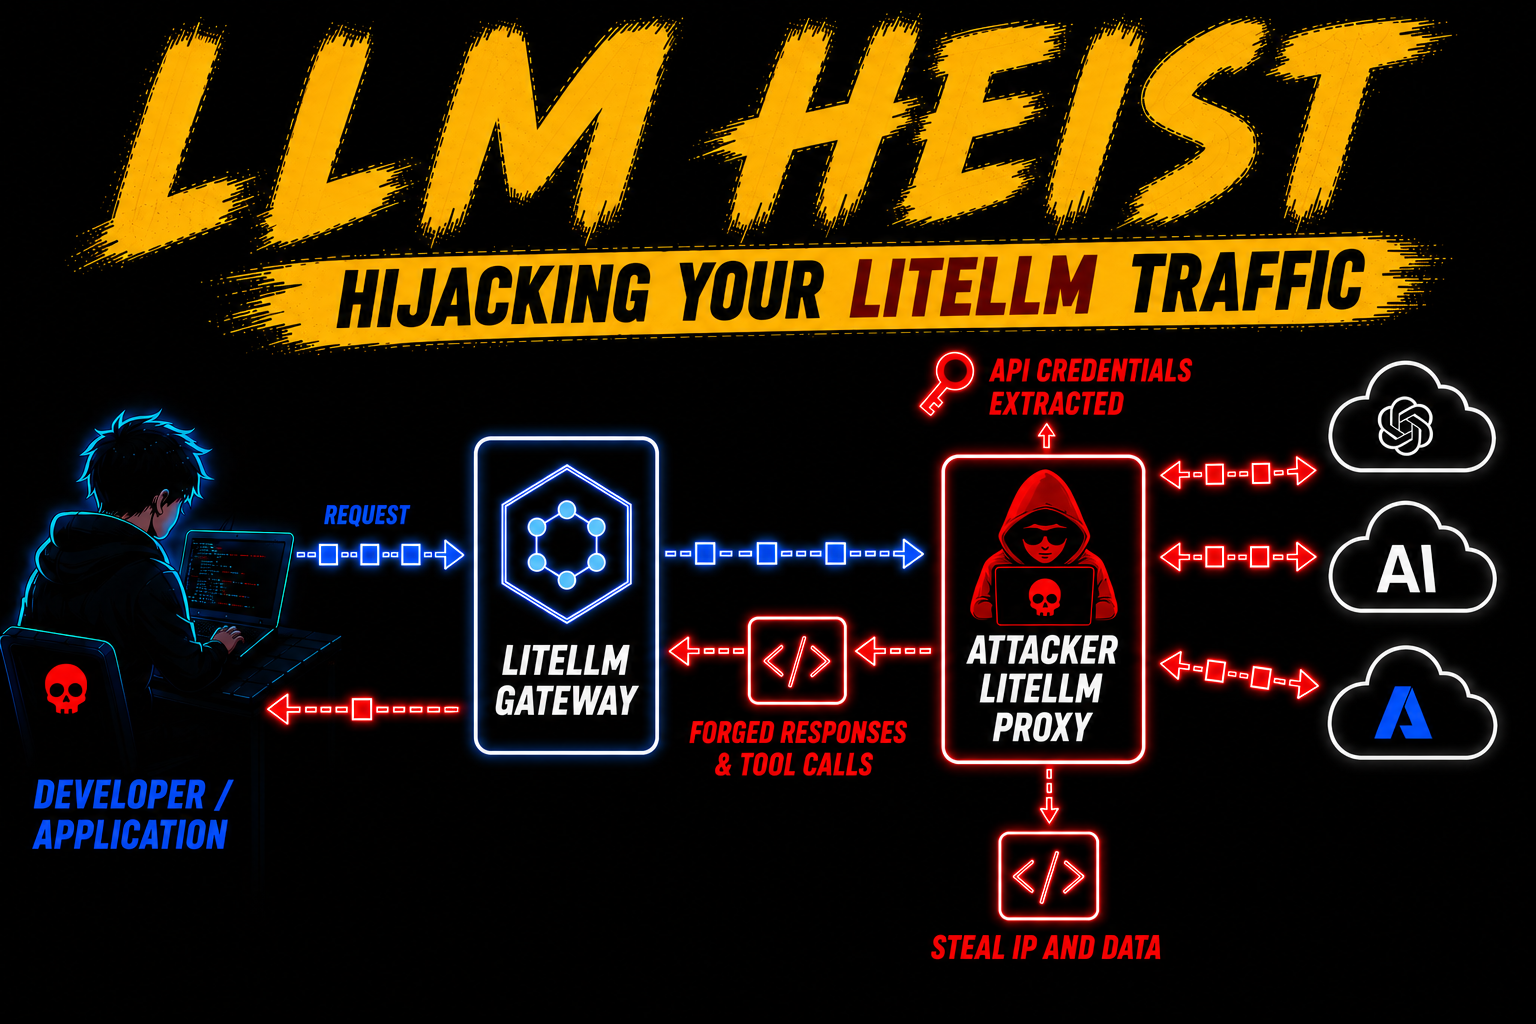
LLM Heist is a red-team technique for hijacking a LiteLLM AI gateway using a stolen proxy-admin or master key. The attacker changes api_base and use_litellm_proxy via /model/update, which routes traffic to an attacker gateway and exposes backend provider keys. The post demonstrates harvesting keys, intercepting chats, and injecting text and forged tool calls into Claude Code. It closes with red team test cases and blue team detections.
LiteLLMClaude CodeAnthropic+1
CVE-2026-42271LLM HeistLITELLM_MASTER_KEY+5
AI Security, Offensive Security, Blue Team & Detection· 2026-08-03T16:00:00+00:00

 embracethered.comwriteup