Skip to content

137 results for โ€œLGโ€

What you seeeverything
huggingface.copaper๐Ÿง  AI

Your Benchmark Is an Empirical Measure Over Difficulty

The paper treats a benchmark as an empirical measure over item difficulty and formalizes two failure modes: measure mismatch (benchmark difficulty distribution differs from the intended one) and coverage gaps (uncovered difficulty regions that hide localized training progress). It proposes two diagnostic metrics with theoretical guarantees and analyzes 25 popular benchmarks across 7 domains using estimated item difficulties. It also introduces BenchFill, a difficulty-targeted item rewriting algorithm that reduces local coverage gaps.

BenchFill

evals, researchยท Added 31 Oct 2026

arxiv.orgpaper๐Ÿง  AI

Don't Lose the Thread: Empowering Long-Horizon LLM Agents with Cognitive Resource Self-Allocation

CORAL (Cognitive Resource Self-Allocation) is an agent-callable working-memory toolset that lets an LLM agent checkpoint task progress and verified facts, then reset its cluttered context and resume from a clean state. A Multi-episode Agentic Reinforced Policy Optimization algorithm trains the checkpointing. With an 8B model it reaches 42.8% average accuracy on GAIA, uses 6-7x fewer input tokens than a ReAct agent, and adds 8.0 points to a proprietary agent on BrowseComp.

LLMReActCORAL
Multi-episode Agentic Reinforced Policy OptimizationGAIABrowseComp

agents, research, trainingยท Added 31 Oct 2026, published 29 Oct 2026

eprint.iacr.orgpaper๐Ÿ›ก๏ธ Security

Quasi-polynomial time algorithms for block basis reduction of linear codes

Kolesnikov and Novoselov give block basis reduction (BKZ) algorithms for linear codes that need polynomial or quasi-polynomial numbers of calls to a minimum weight codeword oracle at fixed block size. The earlier Ghentiyala and Stephens-Davidowitz bounds are exponential. The paper adds a truncated BKZ and a DeepBKZ variant, with an implementation for block sizes 2 to 24 and approximation-factor estimates on random codes.

BKZDeepBKZminimum weight codeword problem+4

otherยท Added 31 Oct 2026, published 29 Oct 2026

arxiv.orgpaper๐Ÿง  AI

DICE: Decentralized Incentive-driven Federated Learning for Efficient & Scalable Customization of Pretrained Models in Web3

DICE is a blockchain-powered federated learning (BCFL) algorithm for customizing large pretrained models among untrusted Web3 participants. It combines dynamic progressive learning and model slice verification, so hardware-limited participants can train part of the model, with a tree-structured committee consensus protocol and an efficiency-driven incentive scheme to scale to more data holders. Experiments cover vision and language models.

federated learningblockchain-powered federated learningprogressive learning+1
arXiv

research, trainingยท Added 31 Oct 2026, published 29 Oct 2026

eprint.iacr.orgpaper๐Ÿ›ก๏ธ Security

Shor's algorithm compiled on cat qubits: 22 593 qubits for RSA-2048 in 3.14 days

Shor's algorithm compiled on cat qubits is an IACR ePrint (2026/2665) giving an end-to-end resource estimate on superconducting cat qubits, using repetition and LDPC cat codes. Factoring RSA-2048 needs about 23,000 cat qubits and 3.14 days, assuming phase-flip noise p_Z = 5e-4 and no bit-flips. secp256k1 ECDLP needs at most 30,000 qubits and 1 hour. A space-for-time trade runs RSA-2048 in 1.25 hours on about 611,000 qubits.

Bitcoin
Shor's algorithmRSA-2048secp256k1+5

otherยท Published and added 28 Oct 2026

decrypt.coarticle๐Ÿง  AI

OpenAI Proves ETH Is False, and Crypto Twitter Has Questions

Decrypt reports that OpenAI published a 67-page paper (dated 17 October 2026, revised 25 October) claiming its AI found a deterministic subexponential-time algorithm for counting 3-SAT solutions, which would refute the Exponential Time Hypothesis. The proof was formalized in Lean. Impagliazzo, Paturi and Ryan Williams are reviewing it independently and say this is not certification. Anthropic posted a Claude-credited 3-SAT paper on 26 October.

LeanGitHubClaude
OpenAIAnthropicDecrypt+7

research, modelsยท Published and added 27 Oct 2026

eprint.iacr.orgpaper๐Ÿ›ก๏ธ Security

Radical isogenies on every model

Radical isogenies on every model is an IACR ePrint paper by Thomas Decru (October 2026). It gives radical isogeny steps of every odd degree N directly on short Weierstrass, Montgomery, twisted Edwards, Huff, Jacobi quartic, twisted Hessian, Legendre and Jacobi intersection curves, plus Kummer lines. In Tate normal form a step drops from 12.5N to 10N multiplications. Montgomery and twisted Edwards curves cost 10.5N+O(1) per step and 2N to push a point. All algorithms are inversion-free, with exact operation counts.

CSIDH
Thomas Decruradical isogeniesVรฉlu's formulae+1

otherยท Added 28 Oct 2026, published 27 Oct 2026

x.comthread๐Ÿง  AI

Rohan Paul (@rohanpaul_ai) on X

Hi3D v1.0 (formerly Sparc3D) is an open-sourced image-to-3D model from Hi3D, which runs a closed v3.0 refining at 2048 cubes per side. In a test with 13 professionals in 3D algorithms, 562 judgments against eight other image-to-3D models favoured it 83.5% of the time. The thread also covers the Hi3D Agent and an MCP server for other agents. Back and bottom views were checked, where TRELLIS.2 collapsed a winged figure.

Model Context Protocol
Hi3DHi3D v1.0Sparc3D+2

models, multimodal, mcpยท Added 28 Oct 2026, published 27 Oct 2026

eprint.iacr.orgpaper๐Ÿ›ก๏ธ Security

Alg\{Ossa\}: Decentralized Secure Aggregation with Rotating Committees and Eventual Delivery

AlgOssa is a decentralized secure aggregation protocol built on Ossa, a generic committee-aided, single-server construction for one-shot clients (following OPA and Willow, CRYPTO 2025). Ossa realizes secure aggregation with non-selective abort against a malicious server. AlgOssa adds Algorand-style sortition to rotate leaders and committees, bounds the chance of an honest server, and gives eventual delivery. Classical and post-quantum routes are evaluated.

Algorand
OssaAlgOssaOPA+2

otherยท Added 28 Oct 2026, published 27 Oct 2026

ethresear.chthread๐Ÿ›ก๏ธ Security

Proof of One: one-person-one-identity polling with encrypted ballots โ€” design and reference code, requesting critical review

Proof of One is an open-source design for polls with one verified human per identity and unlinkable ballots. Enrolment proves in zero knowledge that an ICAO 9303 passport chip was signed by a trusted signer, plus an enclave face match. Voting uses threshold exponential ElGamal on Baby Jubjub with Groth16 proofs, and tally uses a GJKR DKG with a 7-day challenge window. The author, who is pseudonymous, discloses that AI agents drafted most of it and asks for critique of unlinkability, circuit completeness and certificate trust.

Groth16Baby JubjubDAVINCI+1
Proof of OneNemo UnusICAO 9303+4

Identity & Accessยท Published and added 27 Oct 2026

ethresear.charticle๐Ÿ›ก๏ธ Security

Inventory of PQ P2P Migrations in the Consensus Layer

Inventory of post-quantum migration work for Ethereum consensus-layer networking, by adust09 of Nyx Foundation. It maps three targets: Discovery v5/ENR signatures and key exchange, TLS 1.3 key agreement in QUIC, and libp2p TLS identity binding and CertificateVerify. It covers the 300-byte ENR and 1,280-byte packet limits, why hybrid KEMs do not authenticate peers, and downgrade and DoS concerns. It selects no algorithm or schedule.

Ethereumlibp2pQUIC+3
ML-KEMECDSAFIPS 203+8

otherยท Published and added 27 Oct 2026

eprint.iacr.orgpaper๐Ÿ›ก๏ธ Security

When Algebraic Structure Meets Too Many Hints

"When Algebraic Structure Meets Too Many Hints" is an ePrint paper (2026/2654) arguing that DDGR hint classes and too-many-hints thresholds are not standalone side-channel security metrics. In synthetic Kyber-512 experiments, NTT-domain residues recover the full secret with about half the hints the uniform mod-q bound predicts. Finite-precision FFT samples need 25% to 55% of the budget for uniform perfect hints. No new attack optimizations are proposed.

Kyber-512ML-KEM
DDGRtoo-many-hintsMLWE with Hints+4

Hardware & RFยท Published and added 27 Oct 2026

arxiv.orgpaper๐Ÿง  AI

Your Wish Is My Commit: Over-Compliant Refactoring in AI Coding Agents

Your Wish Is My Commit is a controlled study of over-compliant refactoring in Codex and Claude Code, run across five models, 50 algorithmic tasks and 10 object-oriented tasks. Over 3,000 turns of repeated "refactor further" prompts, no model stopped on its own: each rewrote up to 31x the original codebase before first stopping and resumed edits after declaring the task complete. The paper defines six behavioral signals for detecting over-compliance.

CodexClaude CodeLLM
arXiv

coding-agents, research, evalsยท Added 28 Oct 2026, published 26 Oct 2026

eprint.iacr.orgpaper๐Ÿ›ก๏ธ Security

Subexponential Algorithms for LWE via Rejection Sampling on Superlattices

Subexponential Algorithms for LWE via Rejection Sampling on Superlattices is an ePrint paper by Ligeng Fan, Changpeng Shao, Hongbo Li and Dingkang Wang. It extends the Ducas, Engelberts and Loyer superlattice framework to give a provable classical search-LWE algorithm for prime q in [n^2, 2n^2], using m=4n samples and time and space exp(O(n/ln ln n)). A second variant runs in 2^((1/2+o(1))n/ln R) for general parameters. It resolves a gap left by Kirchner and Fouque.

Ducas, Engelberts and LoyerKirchner and FouqueBKW algorithm+1

otherยท Published and added 26 Oct 2026

eprint.iacr.orgpaper๐Ÿ›ก๏ธ Security

Faster Matrix Multiplication Leads to Faster Lattice Sieving

Gao and Hu's IACR ePrint 2026/2622 shows that if the matrix multiplication exponent satisfies ฯ‰ โ‰ค 9/4 โˆ’ ฮท, heuristic lattice sieving runs in (3/2 โˆ’ ฮด)^(n/2+o(n)) time under the spherical heuristic from the BDGL analysis. It builds on OpenAI's recent result that ฯ‰ โ‰ค 9/4. With known matrix multiplication algorithms, the method already gives subquadratic search inside BDGL buckets. Only the abstract is available, so concrete parameters are not shown.

BDGLspherical heuristicmatrix multiplication exponent

otherยท Added 26 Oct 2026, published 24 Oct 2026

decrypt.coarticle๐Ÿง  AI

How I Vibe Coded My Smart TVโ€”And Claude Killed It

A Decrypt writer asked Claude to install Free My TV, an open-source launcher for LG webOS, on a TV rooted since 2023. Claude reviewed the install code and built the package. It then had the user enable Developer Mode, which wiped the Homebrew Channel and ad-free YouTube. Claude restored both apps but not root. Its safeguards then flagged the re-rooting research and offered a switch from Opus 5.5 to Opus 4.8.

Claude CodeLG webOSHomebrew Channel+4
ClaudeAnthropicClaude Opus 5.5+3

coding-agents, ai-safetyยท Published and added 23 Oct 2026

eprint.iacr.orgpaper๐Ÿ›ก๏ธ Security

Tight Post-Quantum Multi-Key Security of the FX Construction

Rentaro Shiba and Tetsu Iwata prove a tight multi-key security bound for the FX construction (the DESX generalization) in the quantum ideal cipher model. Security holds up to about 2^((n+ฮบ)/3) total classical and quantum oracle queries against fully adaptive adversaries, for any number of keyed instances ฮผโ‰ฅ1. This improves their ToSC 2026 bound and matches the offline Simon's algorithm attack in the exponent.

FX constructionDESXoffline Simon's algorithm+4

otherยท Added 24 Oct 2026, published 23 Oct 2026

arxiv.orgpaper๐Ÿง  AI

Sharpness-aware Orthogonalized Momentum Algorithms

SOMA (Sharpness-aware Orthogonalized Momentum Algorithm) combines sharpness-aware minimization (SAM) with the Muon optimizer for LLM training. It avoids SAM's extra gradient computation by using stale, purely stochastic gradient noise as the adversarial perturbation. The authors prove sample complexity does not depend on perturbation direction, study robustness to heavy-tailed gradient noise, and test SOMA against post-training quantization degradation and catastrophic forgetting during fine-tuning.

MuonLLM
SOMAarXiv

research, trainingยท Added 26 Oct 2026, published 23 Oct 2026

arxiv.orgpaper๐Ÿง  AI

CellTrack-Bench: Microscopic Cell Tracking Benchmark for Vision-Language Models

CellTrack-Bench is a benchmark that tests vision-language models on microscopic cell tracking and compares them with specialised trackers. It has 1,537 problems covering 9,041 cell-linking decisions, drawn from 15 cell-tracking datasets across four imaging modalities, with a hard subset built from failures shared by distinct algorithmic trackers. The authors compare environment harnesses, benchmark 9 closed-source and 13 open-weight models, and analyse failure modes.

vision-language modelLLM
CellTrack-BencharXiv

evals, multimodal, researchยท Added 24 Oct 2026, published 22 Oct 2026

eprint.iacr.orgpaper๐Ÿ›ก๏ธ Security

Linear Cryptanalysis of TFHE-Friendly Cipher FRAST in the Average Key Setting

Linear cryptanalysis of FRAST, a TFHE-friendly stream cipher, in the average key setting. It fixes the false-positive problem left open in the earlier attack by Bak et al., showing key differences fall into five indistinguishable classes per round. The Contract algorithm recovers the master key for 10 rounds and, on weak keys of density 2^-11.8 to 2^-5.4, reaches full FRAST within the claimed security.

FRASTTFHE
Contract algorithmBak et al.linear cryptanalysis+1

otherยท Added 24 Oct 2026, published 22 Oct 2026

eprint.iacr.orgpaper๐Ÿ›ก๏ธ Security

SoK: Design-Level Backdoors in Block Ciphers Constructions, Detection, and Key Recovery

SoK on design-level backdoors in block ciphers. It places four published designs (Rijmen and Preneel, Paterson, Bannier and Filiol, Peyrin and Wang) in one taxonomy and gives a sound algorithm that recovers a partition trapdoor from S-box tables. It attacks KG-DES, BEA-1 and LowMC-M: KG-DES key recovery takes minutes, and the LowMC-M MALICIOUS backdoor yields the key from 35 to 409 queries. Trapdoors hidden in linear layers leave no trace, so the authors recommend deriving constants verifiably from a public seed.

KG-DESBEA-1LowMC-M+2
Rijmen and PreneelPatersonBannier and Filiol+5

otherยท Added 24 Oct 2026, published 21 Oct 2026

eprint.iacr.orgpaper๐Ÿ›ก๏ธ Security

Table-Free Constant-Work BCH Decoding by Algebraic Index Elimination

Table-free constant-work BCH decoding by algebraic index elimination is an IACR ePrint paper (2026/2580) that replaces the table scans in Walters and Sinha Roy's constant-work BCH decoder with fixed circuits over public addresses. It proves correctness through radius t and trace regularity, removes 5.2 and 7.2 KiB of tables, and runs 35.7 to 82.4 times faster on an i7-13700. Ordinary C masks compiled to received-word-dependent branches under Apple Clang 21, so the authors use a compiler-opaque primitive and run timing screens on four platforms.

Apple ClangC
Walters and Sinha Royalgebraic index eliminationANSA-IBKEM1+3

Hardware & RFยท Added 24 Oct 2026, published 21 Oct 2026

x.comthread๐Ÿ›ก๏ธ Security

Trail of Bits (@trailofbits) on X

Trail of Bits thread on Google Quantum AI's March publication of a new Shor's algorithm version aimed at secp256k1, the curve protecting Bitcoin and Ethereum wallets. Google used zero-knowledge proofs to keep the attack details secret, and the post says the secrecy lasted 63 days. The fetched text is cut off after the qubit estimate of roughly 1,200, so later details are missing.

BitcoinEthereum
Shor's algorithmsecp256k1Google Quantum AI+2

Blockchainยท Added 22 Oct 2026, published 20 Oct 2026

eprint.iacr.orgpaper๐Ÿ›ก๏ธ Security

Regular Syndrome Decoding Is Easier Than Previously Estimated

Preprint by Jiseung Kim, Minkyu Kim, Changmin Lee and Hochang Lee on the Regular Syndrome Decoding (RSD) problem. It presents a hybrid-algebraic attack that balances zero-coordinate guesses and syndrome-based eliminations across regular blocks. Parameter sets in Ferret, Wolverine and committed VOLE fall below 128-bit targets by up to 67 bits, and the revised Liu et al. (EUROCRYPT 2024) PCG sets cost under 2^111 field operations.

Regular Syndrome DecodingFerretWolverine+4

otherยท Added 21 Oct 2026, published 20 Oct 2026

eprint.iacr.orgpaper๐Ÿ›ก๏ธ Security

Regular Syndrome Decoding Is Easier Than Previously Estimated

Preprint 2026/2563 presents a refined hybrid-algebraic attack on Regular Syndrome Decoding (RSD) that balances zero-coordinate guesses and syndrome-based eliminations across all regular blocks. It puts at least one parameter set each from Ferret (CCS 2020), Wolverine (IEEE S&P 2021) and committed VOLE (CCS 2025) below the 128-bit target, with losses up to 67 bits. PCG attack costs improve by up to 29.77 bits (non-binary) and 25.91 bits (binary), and the revised Liu et al. (EUROCRYPT 2024) 128-bit sets fall below 2^111 field operations.

FerretWolverine
Regular Syndrome Decodinginformation-set decodingpseudorandom correlation generator+3

otherยท Added 21 Oct 2026, published 20 Oct 2026

arxiv.orgpaper๐Ÿง  AI

Scaling Parameter-Efficient Fine-Tuning for Brain Encoding

BrainLoRA is a parameter-efficient fine-tuning method that adapts multimodal backbones of up to 104B parameters to predict neural responses. It predicts multiple timepoints in one causal pass instead of sliding windows, and a multi-LoRA kernel trains many adapters on a shared backbone. Across nine backbones it improves encoding, and a 200+ model ensemble ranks first on the Algonauts post-challenge leaderboard.

LoRAQwen3Transformer
BrainLoRAQwen3-OmniAlgonauts 2025 Challenge+1

research, training, multimodalยท Added 21 Oct 2026, published 19 Oct 2026

eprint.iacr.orgpaper๐Ÿง  AI

Analysis of an AI based code distinguisher

The paper analyses DeepDistinguisher, a transformer-like model that tells Goppa codes apart from random linear codes. Saliency maps and attention visualisation reveal a low-weight-row artifact in the random training instances that the model partly relies on. A pairwise-XOR rule inspired by minimum distance correlates strongly with the model's predictions, and the model loses most of its power on random matrices meeting both constraints. This suggests it exploits general combinatorial properties, not hidden algebraic structure.

Transformer
DeepDistinguisher

researchยท Added 20 Oct 2026, published 19 Oct 2026

eprint.iacr.orgpaper๐Ÿ›ก๏ธ Security

Analysis of an AI based code distinguisher

Analysis of DeepDistinguisher, a transformer model that tells Goppa codes from random linear codes. Using saliency maps and attention visualization, the authors find a low-weight-row artifact in the random training instances that the model partly uses. They propose a pairwise-XOR rule on generator matrix rows that correlates strongly with the model's predictions. On random matrices meeting the minimum distance and XOR constraints, the model loses most of its accuracy, so it exploits general combinatorial properties rather than hidden algebraic structure.

DeepDistinguisherGoppa Distinguisher problemGoppa code

AI Security, otherยท Added 20 Oct 2026, published 19 Oct 2026

decrypt.coarticle๐Ÿ›ก๏ธ Security

Zcash Developer Zakura Proposes Fix to Stop Quantum Computers Linking Shielded Swaps

Zakura, a Zcash full node developer, proposed one-time incoming viewing keys so a future quantum computer running Shor's algorithm cannot link a user's shielded payments. The target is NEAR Intents swaps, which post a shielded refund address on a public chain. The fix needs no network upgrade and uses private information retrieval for seed restores. Wallets such as Vizor can add it within weeks.

Zcash
Shor's algorithmNEAR IntentsZakura+5

Blockchainยท Published and added 19 Oct 2026

en.cryptonomist.charticle๐Ÿ›ก๏ธ Security

Broadcom Wi-Fi vulnerability leaves over 1.5 million Belgian gateways exposed

A Broadcom SDK flaw in the WPS code that reassembles fragmented EAP messages allows a buffer overflow and unauthenticated code execution over Wi-Fi, bypassing WPA2/WPA3 passwords. Quentin Kaiser of ONEKEY demonstrated it at Hexacon on 16 October 2026 against Orange Belgium and Proximus gateways, and published a fingerprinting script and YARA rule. Broadcom's 2018 patch was incomplete, it refused a CVE, and over 1.5 million Belgian gateways are exposed.

Broadcom SDKeCosLinux+2
Quentin KaiserONEKEYHexacon+14

Hardware & RF, Offensive Securityยท Published and added 19 Oct 2026

eprint.iacr.orgpaper๐Ÿ›ก๏ธ Security

Provable Lattice Reduction in Nearly the Time of QR Factorization

Provable Lattice Reduction in Nearly the Time of QR Factorization (IACR ePrint 2026/2541, October 2026) presents a deterministic lattice-reduction algorithm with running time ร•(n^ฯ‰(1+log ฮบ_col(B))), free of heuristic assumptions. Its implementation used fewer instructions than flatter (CRYPTO 2023) in all 153 runs on q-ary, NTRU-like, scaled q-ary and Coppersmith inputs. Median flatter-to-new instruction ratios are 1.55 for q-ary and 1.86 for NTRU-like inputs.

flatter
CoppersmithLLL

otherยท Added 20 Oct 2026, published 19 Oct 2026

coindesk.comarticle๐Ÿ›ก๏ธ Security

Zcash developers plan a fix to keep ZEC swaps private from future quantum computers

Zakura, a newer version of the Zcash node software, plans to give each ZEC swap through NEAR Intents its own viewing key. Today a refund address posted on NEAR's public chain shares one viewing key with the whole account, so a future quantum attacker running Shor's algorithm could link the account's full payment history. Spending keys stay with the user, and private information retrieval lets wallets find refunds without revealing which addresses they check. Wallets such as Vizor could ship it within weeks.

ZcashZakuraVizor
NEAR IntentsShor's algorithmbunker mode+2

Blockchainยท Published and added 19 Oct 2026

eprint.iacr.orgpaper๐Ÿ›ก๏ธ Security

Computing endomorphisms of superspecial principally polarized abelian surfaces in time and memory \(p^{4/5+o(1)}\)

Computing endomorphisms of superspecial principally polarized abelian surfaces is a cryptanalysis preprint by Marc Houben and Lam L. Pham, posted to IACR ePrint in October 2026. It gives an algorithm that, under a standard heuristic, finds a non-scalar polarized endomorphism in expected time and memory p^(4/5+o(1)). The abstract is the only text available, so the method and its effect on specific schemes are not described.

Marc HoubenLam L. Pham

otherยท Added 19 Oct 2026, published 18 Oct 2026

ethereum-magicians.orgpaper๐Ÿ›ก๏ธ Security

Post-Quantum Stateless Steganography & MTU Bounds: Bridging P2P Censorship Resistance to Quantum Networks

Forum announcement of a Zenodo preprint on post-quantum migration for censorship-resistant P2P steganographic tunnels. It argues that ML-KEM's prime modulus (q=3329) makes naive bit-packed ciphertexts statistically distinguishable from uniform noise, which gives a cheap passive DPI distinguisher. It also argues that composite PQ 0-RTT envelopes over 4.4 KB force fragmentation, which requires stateful reassembly before AEAD verification and reopens memory-exhaustion DoS in eBPF/XDP filters. Proposed fixes are algebraic uniformization (LWR lattices or inverse rejection sampling), sub-MTU hybrid or pure-PQ envelopes (Falcon-512, signcryption), and Fujisakiโ€“Okamoto implicit rejection for constant-time silent drops. Aimed at Ethereum validator, libp2p and RPC transports facing harvest-now-decrypt-later threats.

eBPFXDPlibp2p+1
ML-KEMML-DSAHarvest-Now-Decrypt-Later+8

otherยท Published and added 17 Oct 2026

eprint.iacr.orgpaper๐Ÿ›ก๏ธ Security

E๏ฌƒcient Fixed-Point Implementation of Mitaka

Presents a fixed-point C implementation of the Mitaka signing algorithm, a simpler, parallelizable Falcon (FN-DSA) variant. It replaces MitakaZ's wide integral Gram root decomposition with a fixed-point square Cholesky decomposition, which cuts the cost of integer Gaussian sampling, and proves bounds on intermediate values and representation errors without empirical assumptions. Signing averages 361 kcycles (Mitaka-512) and 707 kcycles (Mitaka-1024) on AVX2, and 4.0 and 7.8 Mcycles on an STM32F411 Cortex-M4F. This makes floating-point-free lattice signatures practical on constrained devices.

MitakaFalconC+1
MitakaZFN-DSAGaussian sampling+1

otherยท Published and added 17 Oct 2026

coindesk.comarticle๐Ÿ›ก๏ธ Security

Satoshi-era bitcoin faces a bigger quantum threat after Googleโ€™s new Willow breakthrough

CoinDesk reports Google's Science paper showing its Willow chip prepares "magic states" with about 40x fewer errors (about 99.99% fidelity, but only about 8% of attempts survive post-selection) using a method called cultivation. It explains why this lowers one hardware bottleneck for a Shor's-algorithm attack on Bitcoin's ECDSA keys, but does not make an attack 40x cheaper. It also separates coins with permanently exposed public keys (early Satoshi-era outputs, which an offline attacker can target) from hash-hidden keys, where the attacker must race the spend. The article cites Google's March estimate of under 500,000 physical qubits and about 500,000 reliable magic states per second for a roughly nine-minute attack.

BitcoinWillowEthereum
Shor's algorithmmagic state cultivationmagic states+5

Blockchainยท Published and added 17 Oct 2026

quentinkaiser.bewriteup๐Ÿ›ก๏ธ Security

One parser, two bugs, many routers: Exploiting Broadcom WiFi across eCos, Linux

Long-form write-up of a Hexacon 2026 talk on a WPS EAP reassembly overflow in Broadcom's proprietary 802.11 stack, present since 2010 and incompletely patched in 2018. It is remotely triggerable over WiFi without the network key. It gives information disclosure and code execution on eCos (BCM3380, BCM3383, BCM33834) and Linux (BCM3390, BCM65xx, BCM68xx) platforms. Exploited on Belgian ISP routers from Proximus, VOO and Orange. Includes a 90-day disclosure timeline, and Broadcom refused to assign a CVE.

BroadcomeCosLinux+2
HexaconWPS EAP reassembly overflowforever day+17

Hardware & RF, Offensive Security, Blue Team & Detectionยท Added 19 Oct 2026, published 16 Oct 2026

eprint.iacr.orgpaper๐Ÿ›ก๏ธ Security

Power Analysis on SQIsign via Ideal Reconstruction from Quaternion Leakages

ePrint paper identifying five side-channel vulnerabilities in the signing procedure of Round-3 SQIsign, the isogeny-based signature scheme in NIST's additional post-quantum signature process. It gives polynomial-time algebraic algorithms that recover the secret key from leaked quaternion/ideal intermediate values, including cases where only partial bits leak. It also demonstrates power analysis on the SQIsign source code to extract the needed leakage, which earlier work on Round-1 or toy parameters did not do.

SQIsign
NISTideal reconstruction

Hardware & RFยท Added 17 Oct 2026, published 16 Oct 2026

arxiv.orgpaper๐Ÿง  AI

MLExpert: Towards a Generalist Agentic Model for Autonomous Machine Learning Engineering

Presents MLExpert, a 35B Mixture-of-Experts agentic model trained for autonomous long-horizon machine learning engineering. Training uses a Kaggle-MLE Factory to build executable tasks and an interaction harness, hierarchical agentic SFT with outcome-guided supervision, and Windowed Interaction RL (WIRL). WIRL treats the multi-turn decisions between successive experiment results as one execution window with a shared outcome reward, and uses asynchronous collection and policy correction. On MLE-Bench Lite the average medal rate rises from 37.9% to 72.7%, comparable to larger frontier models such as Kimi-K3 and GLM-5.3. It also improves on NatureBench Lite, agent scaffold optimization and algorithm optimization.

Mixture of ExpertsLLM
MLExpertKaggle-MLE FactoryMLE-Bench+4

research, training, agentsยท Added 17 Oct 2026, published 15 Oct 2026

arxiv.orgpaper๐Ÿง  AI

Efficient KV Cache Migration for Geo-Distributed LLM Inference in Collaborative Edge Computing

Proposes EdgeFlow, a hybrid KV cache migration scheme for distributed LLM inference across heterogeneous edge servers in Collaborative Edge Computing. It combines direct KV cache transmission with activation-based recomputation, overlapping computation and communication to cut migration time when servers disconnect or overload. The authors formulate a multi-node KV migration optimization problem and give a 2-approximation algorithm built on improved LP relaxation and bipartite graph techniques. Experiments on a real distributed LLM inference platform show up to 45% lower migration time.

LLM
EdgeFlowarXiv

inference, researchยท Added 17 Oct 2026, published 15 Oct 2026

hackers-arise.comarticle๐Ÿ›ก๏ธ Security

Social Engineering: Exploiting Human Psychology in Offensive Security

Hackers Arise explainer on the human psychology that social engineers exploit. It covers cognitive overload ("brain DoS"), stereotyped automatic behaviour, and the authority, scarcity and consistency principles, with supporting studies (Milgram, Pliner, Europol fraud-victim statistics). It also describes trigger-bypass techniques such as reframing a password request as IT support, and an observed baseline percentage of recipients who act on phishing emails. It closes with organisational and personal defences.

Milgram experimentEuropolPaul Frampton+5

Offensive Security, Learningยท Published and added 15 Oct 2026

simonwillison.netarticle๐Ÿง  AI

Tree Appreciator

Simon Willison describes another game experiment, this time in the Claude iPhone app in chat mode rather than Claude Code. He prompted Claude Opus 5.5 Max to build a three.js game called "Tree appreciator" with two algorithmically generated trees and a mechanic based on appreciating their differences, and added "think hard about how to make sure it is both fun and beautiful". After about 3 hours 7 minutes of work it returned a spot-the-difference game with music, animation and achievements. He notes that simply telling Opus 5.5 to "make sure it is fun" works surprisingly well.

Claudethree.js
Simon WillisonClaude Opus 5.5Anthropic

prompting, modelsยท Added 15 Oct 2026, published 14 Oct 2026

eprint.iacr.orgpaper๐Ÿ›ก๏ธ Security

A Hybrid BP-SAT Attack on MILENAGE: Combining the Complementary Strengths of Algebraic and Soft-Analytical Side-Channel Attacks

ePrint paper evaluating ASCA (SAT-based) and SASCA (belief propagation) side-channel attacks on the AES-based MILENAGE authentication algorithm in USIM cards, using neural-network leakage predictions to recover subscriber key K and operator secret OPc from a single trace. SASCA alone succeeds in 87.7% of attacks but converges to a wrong OPc in 6.1%; ASCA succeeds in only 34% within a 1-hour timeout. The hybrid, where BP refines the predictions before they go to the SAT solver, reaches 93.8% with lower average runtime. It also proposes a countermeasure that masks each AES round key with an independent per-device secret, and the authors report it defeated the hybrid attack in all evaluated cases.

AESMILENAGEUSIM
OPcSASCAASCA

Hardware & RFยท Added 15 Oct 2026, published 14 Oct 2026

arxiv.orgpaper๐Ÿ›ก๏ธ Security

Quantum-Aware Key Rank for Side-Channel Attacks evaluation

Proposes a cost model and metric for an adversary who collects side-channel traces classically and finishes the key search on a quantum computer. Shows any quantum algorithm needs Omega(sqrt(r)) cipher evaluations for key rank r, and that the quadratic advantage holds only up to a rank bound set by the NIST MAXDEPTH budget (about 2^58.6 for AES-128 at D=2^40). Defines a quantum-aware key rank computable from existing rank estimators, with simulated-leakage experiments showing a depth-limited quantum adversary is worth about 22 traces at SNR 0.125.

AES
NIST MAXDEPTHGrover's algorithmquantum search with advice+4

Hardware & RFยท Added 16 Oct 2026, published 14 Oct 2026

ethereum-magicians.orgarticle๐Ÿ›ก๏ธ Security

ERC-8443: Quantum Bridge Shield

Draft ERC from Quantova Inc proposing a "Quantum Bridge Shield" for Ethereum bridges. A committee signs the Merkle root of each message batch with RFC 8554 LMS hash-based signatures instead of ECDSA/BLS keys that Shor's algorithm can break. The guard contract requires a strict majority of distinct unfrozen keys, records used leaves, freezes any key that signs a leaf twice, binds digests to domain, chain, guard and epoch, and applies a 60-second delay. The post gives gas costs (LMS W4 height-10 verification about 205k gas, a LayerZero packet 128,683 gas, worst-case rotation 12.44M gas under the EIP-7825 cap) and cites a NioLabs assessment with no critical or high findings. It is relevant as a worked post-quantum migration design for bridge key custody, including hybrid ECDSA+LMS mode and stateful-signature pitfalls such as leaf reuse and rollback.

EthereumLayerZeroLMS
ERC-8443Quantova IncShor's algorithm+11

Blockchainยท Published and added 14 Oct 2026

ethereum-magicians.orgpaper๐Ÿ›ก๏ธ Security

ERC: Quantum Bridge Shield

Draft ERC from Quantova Inc that has Ethereum bridges accept cross-chain message batches only when a committee signs the Merkle root with RFC 8554 LMS hash-based signatures. The guard contract requires a strict majority of distinct unfrozen keys, records used leaves, freezes any key that signs a leaf twice, binds digests to domain tag, chain ID, guard address and epoch, and enforces a 60-second delay. It reports gas benchmarks (about 205k per LMS W4 height-10 verify, 12.44M worst-case rotation under EIP-7825), a hybrid LMS+ECDSA migration mode, and a NioLabs assessment with no critical or high findings. It argues that Shor's algorithm makes secp256k1 and BLS committee keys a quantum theft target.

EthereumLayerZero
Quantova IncNioLabsRFC 8554+7

Blockchainยท Published and added 14 Oct 2026

eprint.iacr.orgpaper๐Ÿ›ก๏ธ Security

Refined Application of the XL Algorithm within the Algebraic Approach to the Regular Syndrome Decoding Problem

Furue and Aikawa build and analyze algebraic attacks on the Regular Syndrome Decoding Problem (RSDP), which underlies code-based post-quantum schemes. They extend the Wang et al. hybrid algorithm to allow an arbitrary XL solving degree d, and add two variants: an XFL-based one (partial Gaussian elimination plus variable guessing) and a WXL-based one that exploits Macaulay matrix sparsity. Complexity analysis shows the WXL variant with d>2 wins for small block size ฮฒ, while the original hybrid wins as ฮฒ grows. This matters for setting RSDP-based scheme parameters.

Regular Syndrome Decoding ProblemSyndrome Decoding ProblemXL algorithm+4

otherยท Published and added 14 Oct 2026

metr.orgarticle๐Ÿง  AI

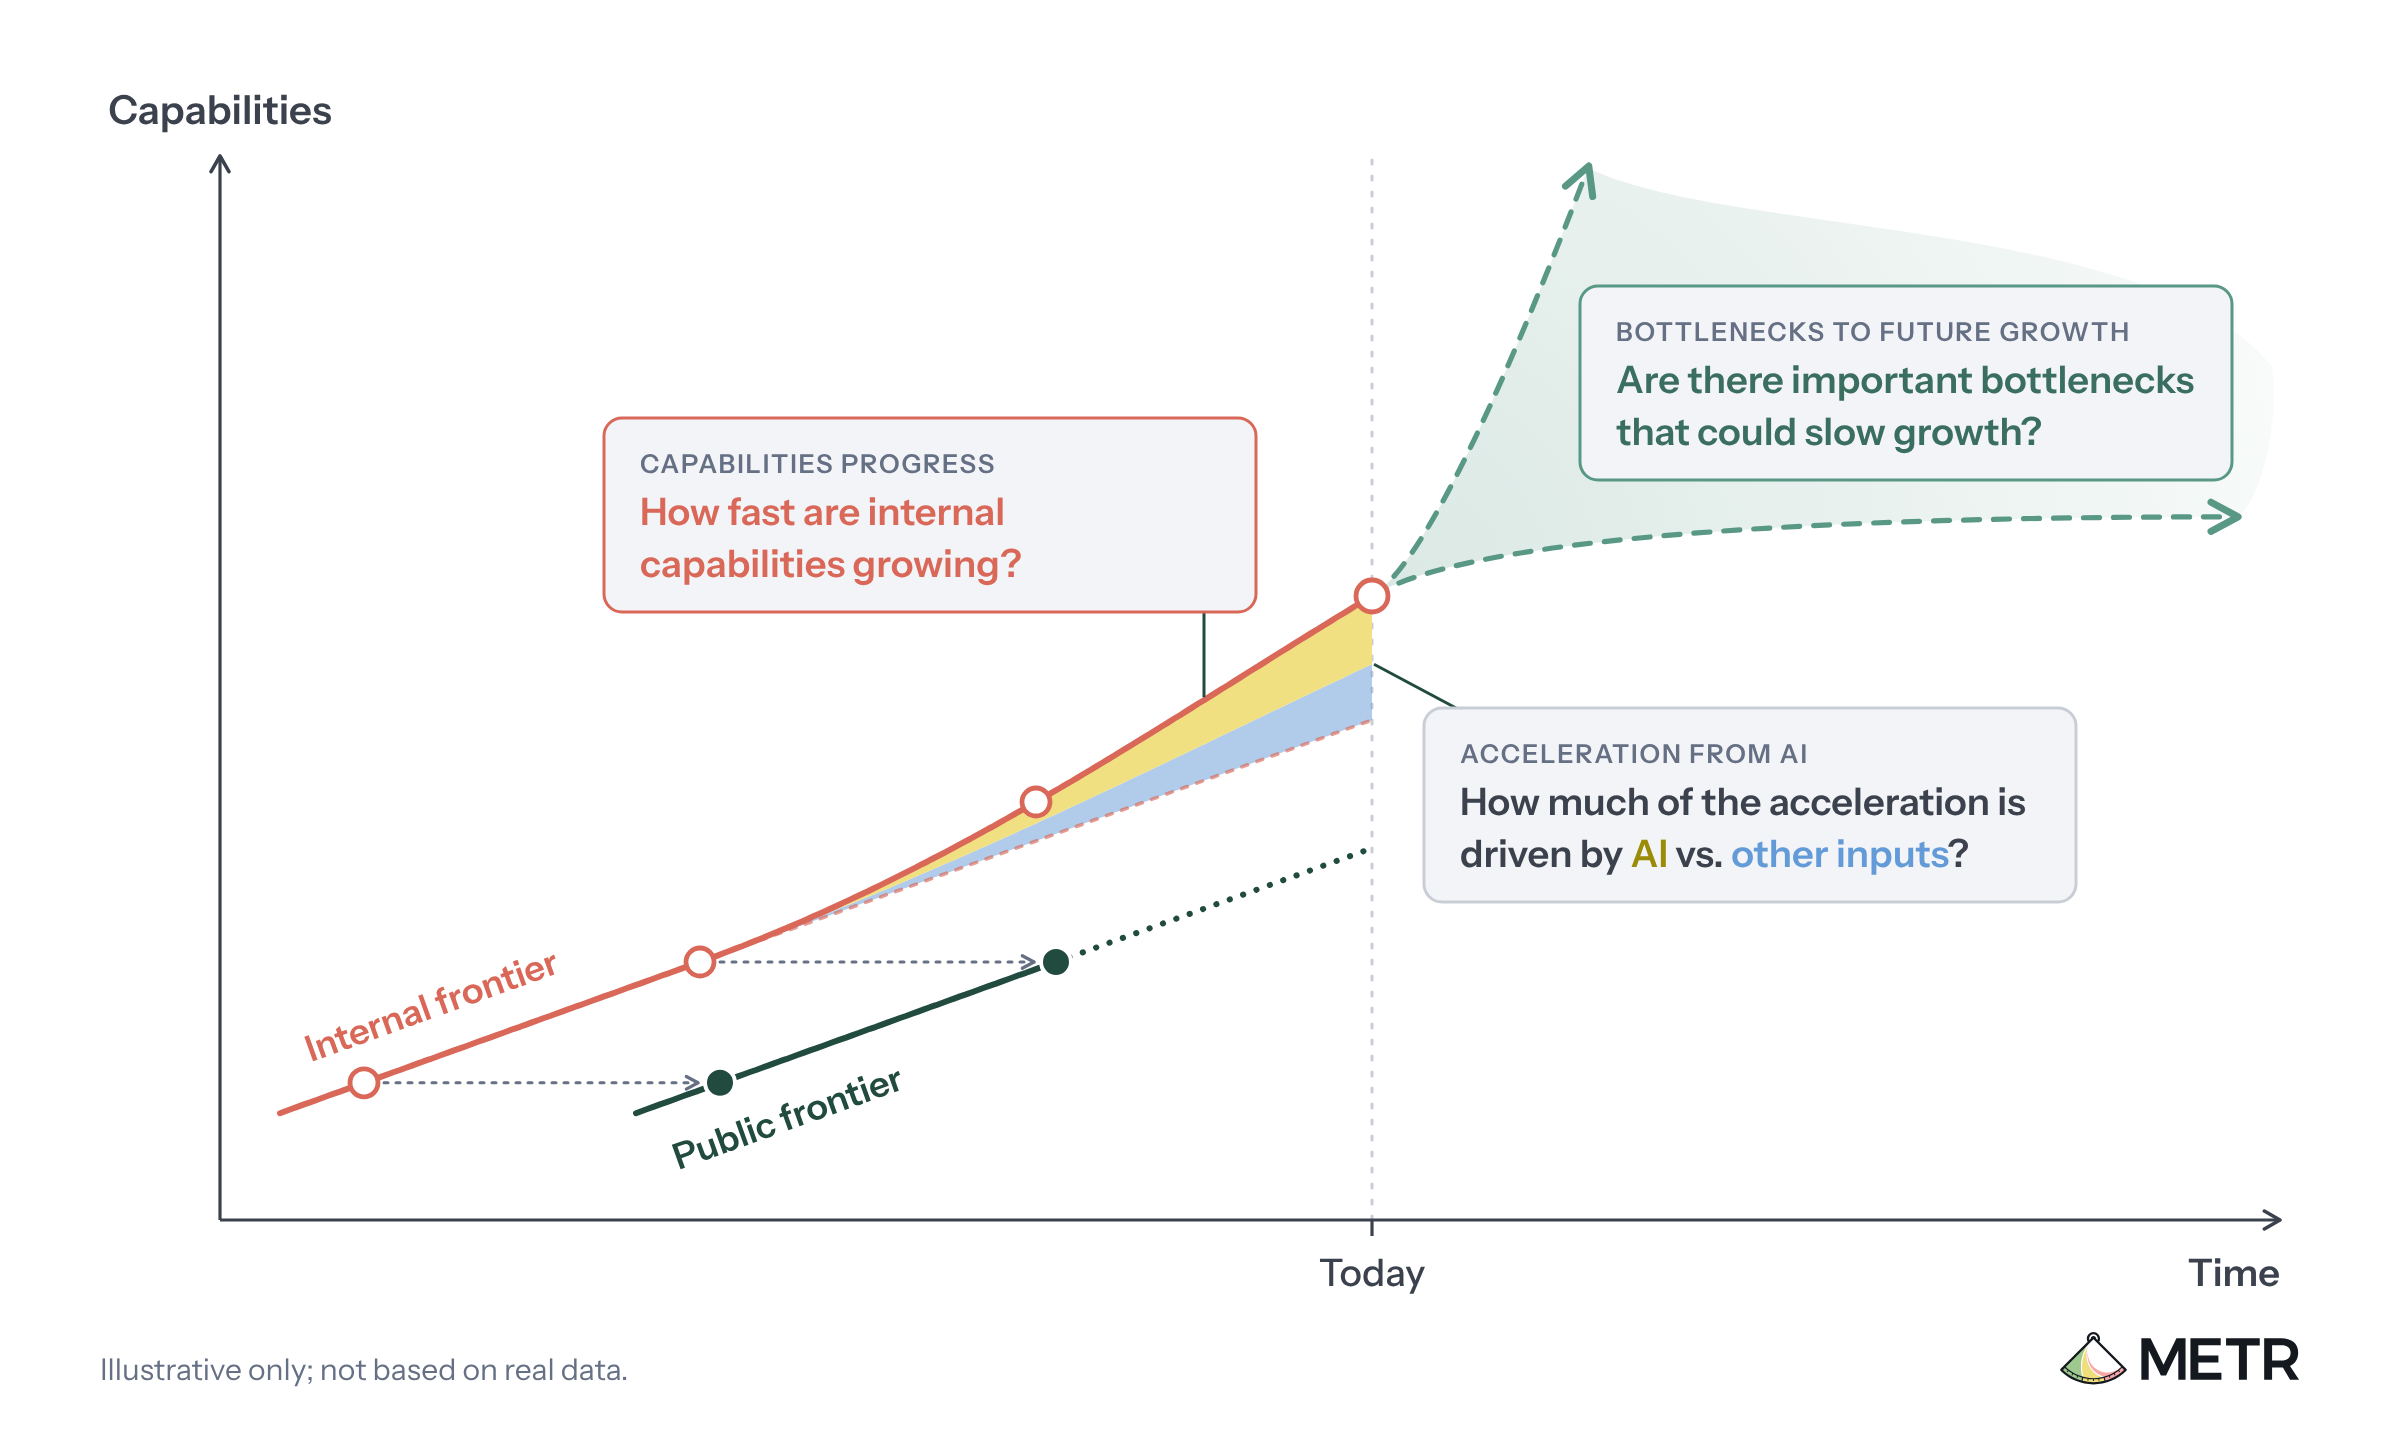
How an assessor could investigate evidence of acceleration from the automation of AI R&D

METR proposes a framework for an outside assessor to test whether AI automation of AI R&D is accelerating capabilities progress. It covers four questions: how fast internal capabilities improve, how much acceleration AI causes, which bottlenecks could slow growth, and whether the methods would detect a dramatic acceleration. It lists the internal data developers would need to share, including benchmarks, algorithmic progress estimates, compute, labor, AI agent spend and staff interviews.

METRECI

ai-policy, evals, ai-safetyยท Added 29 Oct 2026, published 14 Oct 2026

eprint.iacr.orgpaper๐Ÿง  AI

DPF-SGD: Byzantine-Robust Differentially Private Federated SGD with Exact Optimality Guarantees

DPF-SGD is a federated SGD algorithm that stays robust to Byzantine agents while satisfying ฯต-differential privacy. It combines private step sizes with a DP noise-decay schedule and adds a privacy-preserving comparative elimination (PPCE) filter that suppresses Byzantine updates during aggregation. The authors prove almost-sure convergence to the global optimum despite persistent noise and adversaries. On synthetic and MNIST data, final optimization error is one to two orders of magnitude lower than DP baselines.

DPF-SGDSGD
MNIST

research, trainingยท Published and added 14 Oct 2026

arxiv.orgpaper๐Ÿง  AI

SP$^2$ec: Adaptive Self-Speculative Decoding for Vision-Language Models

SP$^2$ec (Single-Peak SPeculative decoding) is a training-free bandit algorithm that adapts the draft configuration of self-speculative decoding per prompt for vision-language models. It relies on the single-peak throughput pattern seen in SWIFT, KnapSpec, SpecVLM and the authors' cosSim method. It minimizes a new wall-time regret measure and has theoretical guarantees of near-optimal configuration with negligible exploration cost. On Qwen2.5-VL-7B-Instruct and LLaVA-NeXT-Mistral-7B it improves over the original self-speculative methods by up to 11% on visual and textual tasks.

vision-language modelQwenMistral
SP$^2$ecSWIFTKnapSpec+5

research, inference, multimodalยท Added 14 Oct 2026, published 13 Oct 2026

arxiv.orgpaper๐Ÿง  AI

ProAS: A Progress-Aware Advantage Shaping Framework for Multi-Turn Agentic Reinforcement Learning

ProAS (Progress-Aware Advantage Shaping) is a plug-and-play framework for multi-turn agentic RL that fixes the uniform credit assignment problem in critic-free algorithms like GRPO, where trajectory-level advantages are broadcast to every action. It uses a dynamically evolving Agentic Reference Graph with Masking Unreasonable Incentives and Asymmetric Penalty Redistribution to give finer-grained credit without a critic. On Qwen2.5-1.5B/7B-Instruct it reports success rates up to 91.9%/94.3% on ALFWorld and 66.7%/70.8% on WebShop, with up to 2.44x faster training convergence and robustness to imperfect or distilled ARGs.

GRPOQwen
ProASAgentic Reference GraphALFWorld+4

training, agents, researchยท Added 14 Oct 2026, published 13 Oct 2026

argmin.netarticle๐Ÿง  AI

A look at the math that OpenAI claims computes faster Fourier transforms

A blog post examining the "faster Fourier transform" claim in OpenAI's released batch of AI-generated mathematics papers (main.pdf). It explains the Cooley-Tukey FFT and big-O notation, then argues the result is a galactic algorithm: constants around 10^100, and it assumes exact arbitrary-precision complex arithmetic that no real computer provides. It cites the Morgenstern (1973) and Ailon lower bounds, and uses the same critique on a claimed O(n^2.25) matrix multiplication result to argue that AI is amplifying theoretical CS's detachment from actual computation.

ChatGPT
OpenAIJames CooleyJohn Tukey+5

researchยท Published and added 13 Oct 2026

aws.amazon.comarticle๐Ÿ›ก๏ธ Security

Quantum-resistant signing on AWS, Part 2: Enforce your ML-DSA algorithm policy with SCPs and IAM

Explains how to turn a cryptographic algorithm policy (approve ML-DSA-65/87, exclude ML-DSA-44) into enforceable AWS controls using SCPs, IAM policies, permission boundaries and KMS key policies. The key lever is the kms:KeySpec condition key (kms:SigningAlgorithm can't distinguish variants, since all use ML_DSA_SHAKE_256), applied to CreateKey, ReplicateKey, Sign, Verify and GetPublicKey. It also covers surfaces without algorithm condition keys (AWS Private CA, ACM import, IAM server certificate upload, ELB TLS) via provisioning pipelines plus CloudTrail and AWS Config drift detection, and the default-allow risk of deny-lists.

AWSAWS KMSAWS IAM+3
ML-DSAFIPS 204NIST+2

Cloud & Infra, GRCยท Published and added 12 Oct 2026

x.comthread๐Ÿง  AI

Igor Carron (@IgorCarron) on X

Igor Carron's tweet highlights LightOn's open-source ColGrep-Agent-2B, a 2B model released on Hugging Face for code search and retrieval that works with Claude Code. LightOn reports 34% fewer API tokens and 40% lower API costs. It matters because usage limits and token costs are a pain point for coding agents. A reply thread in the same post notes quota exhaustion across Grok, Cursor, Devin, Claude and Codex, and argues for quota dashboards.

Claude CodeHugging FaceCodex+3
LightOnColGrep-Agent-2BIgor Carron+1

coding-agents, models, llm-appsยท Published and added 12 Oct 2026

eprint.iacr.orgpaper๐Ÿ›ก๏ธ Security

Genericity in multivariate cryptography

The paper proves that some properties of UOV (Unbalanced Oil and Vinegar) public-key ideals and varieties hold generically. These include equidimensionality of the UOV varieties and radicality of the public key ideals. This justifies the regularity assumptions used in algebraic cryptanalysis of UOV and its variants. The authors also review earlier multivariate schemes that were broken because they were non-generic, and give one counter-example whose non-genericity looks hard to exploit.

UOVgenericityalgebraic cryptanalysis

otherยท Added 14 Oct 2026, published 12 Oct 2026

eprint.iacr.orgpaper๐Ÿ›ก๏ธ Security

Optimal Threshold Implementations of all bijective 4-bit S-boxes and new Infinite Families

ePrint paper presenting share-optimal, direct, uniform, first-order threshold implementations (TIs) with no fresh randomness. It shows every bijective 4-bit permutation of algebraic degree t admits a TI with t+1 shares, and introduces the first infinite families of cryptographically nontrivial power permutations with optimal TIs. The results disprove several earlier conjectures and give new glitch-resistant masking options for lightweight cipher S-boxes.

Hardware & RFยท Added 14 Oct 2026, published 12 Oct 2026

eprint.iacr.orgpaper๐Ÿ›ก๏ธ Security

Extending the Schur--Macaulay Framework for UOV Attacks via Truncated Polynomial Algebras

ePrint paper by Peigen Li and Siyong Tao extending the wedge-attack framework of Ding, Li and Tao and the Schur-Macaulay matrix approach of Merz and Ran against Unbalanced Oil and Vinegar (UOV). It reformulates the attack with p-truncated polynomial algebras, so it applies over arbitrary finite fields. Divided powers and transfer relations give extra public relations in the ideal-inclusion framework, with quotient-dimension criteria for recovering graded components of the hidden oil-space ideal. Applied to the third-round QR-UOV parameter sets, it gives lower attack-complexity estimates for some of them.

UOVQR-UOV
wedge attackSchur-Macaulay matrixoil-space ideal+3

otherยท Added 14 Oct 2026, published 11 Oct 2026

eprint.iacr.orgpaper๐Ÿ›ก๏ธ Security

Distinguishers for the Squeezing of the Alternating Sponge and Duet

Cryptanalysis of the Alternating Sponge (ASP) and Duet, a permutation-based hash candidate in China's ICCS Next Generation Commercial Cryptographic Algorithm program (NGCC). The authors give an O(2^r)-query distinguisher against ASP that contradicts its claimed indifferentiability bound in some parameter regimes. They also give a distinguisher and state-recovery attack on Duet's multi-block output, using O(2^(r+c-h)) permutation queries. Collision and preimage resistance are unaffected, but Duet used as a XOF or KDF is affected, and state recovery enables length extension.

Gaรซtan LeurentCรฉsar MathรฉusInstitute of Commercial Cryptography Standards+4

otherยท Added 12 Oct 2026, published 9 Oct 2026

eprint.iacr.orgpaper๐Ÿ›ก๏ธ Security

RM-KLPT: Algebraic Pathfinding for Superspecial Abelian Surfaces with Maximal Real Multiplication

The paper presents RM-KLPT, an algorithm that solves the algebraic pathfinding problem in isogeny graphs of superspecial abelian surfaces with maximal real multiplication. It does this by solving a norm equation in ideals of a quaternion algebra over a real quadratic field. The authors implement it and revisit the RM-CGL hash function of Charles, Goren and Lauter. They show that if the initial surface's algebraic description is known, RM-KLPT gives a second-preimage attack on the hash. Paths are much shorter (~p^3) than with KLPT^2, because a higher-dimensional Deuring correspondence exists in the RM setting. The paper also discusses cryptographic constructions that could be built on RM-KLPT.

RM-KLPTRM-CGLKLPT+4

otherยท Added 12 Oct 2026, published 9 Oct 2026

microsoft.comarticle๐Ÿ›ก๏ธ Security

Post-quantum authentication: Why organizations should start testing certificate ecosystems now

Microsoft Security Blog post arguing that post-quantum cryptography planning must extend beyond encrypted-data confidentiality to authentication and certificate ecosystems, since larger PQC certificate chains and new algorithms like ML-DSA-87 can break PKI workflows, HSMs, and legacy infrastructure. It details Microsoft's PQC TLS Pilot Program, launched August 27, 2026, which lets approved certificate authorities (ComSign, DigiCert, HARICA, IdenTrust, Sectigo, Shanghai Electronic Certification Authority, SSL.com) test ML-DSA-87 certificate issuance under the Microsoft Trusted Root Program, plus Windows 11 builds (KB5101681, KB5101684) that support evaluating ML-DSA certificates via Schannel in non-production environments. It lays out a six-step readiness plan: inventory certificate dependencies, map trust relationships, assess vendor roadmaps, identify long-lived infrastructure, build test environments, and plan a multi-year migration.

WindowsSchannelTLS
ML-DSAML-DSA-87PQC TLS Pilot Program+8

Identity & Access, GRCยท Published and added 8 Oct 2026

Showing 60 of 137

Show more