Skip to content

96 results for “Wiz”

What you seeeverything
“Wiz”
bleepingcomputer.comarticle🛡️ Security

Northflank security breach leads to abuse of customers' AI API keys

Northflank, a cloud application hosting platform, disclosed a breach on 30 October 2026 after a Wiz threat alert and told customers to assume all environment variables were decrypted and to rotate secrets. Customers reported unauthorized use of AI API keys. Wiz's "Black October for AI Developer Platforms" report counts at least nine incidents, including Railway, OpenCode, Warp and Lightning AI, and describes LLMJacking, with about 2.5 million Amazon Bedrock calls costing roughly $100,000 in two cases. Northflank has not said how attackers got in.

NorthflankWizAWS Bedrock+3
LLMJackingBlack October for AI Developer PlatformsRailway+2

Threat Intel, AI Security, DevSecOps· Published and added 31 Oct 2026

wiz.iowriteup🛡️ Security

“Black October” for AI Developer Platforms

Wiz Research links October 2026 breaches at AI developer platforms (Fireworks, OpenCode, Warp, Zeabur, Railway and others) to stolen environment-variable credentials for AI access. It details two enterprise AWS Bedrock keys abused after vendor breaches: about 800k and 1.7 million calls, over $100k in list-price usage. It profiles two LLM resale operations, "momo" and "Xingjiabi", that tested the keys.

AWS BedrockOpenCodeClaude+3
LLMjackingdistillationWiz Research+13

Threat Intel, AI Security, Cloud & Infra· Added 31 Oct 2026, published 30 Oct 2026

rekt.newsarticle🧠 AI

Rekt - News or Hype?

Rekt's "News or Hype?" compares four October 2026 AI headlines with their sources. These are Justin Drake's "bunker mode" ECDSA warning, Anthropic's Claude tracing NIST curve seeds to lrand48, OpenAI's agent spending Sepolia ETH from a default-mnemonic account, and Wiz's "AI uncovers" PHP RCE claim of 70% reach. It ends with four questions for checking claims.

ECDSABitcoinEthereum+11
CVE-2026-109618CVE-2026-109619Justin Drake+17

ai-safety, agents, ai-policy· Added 30 Oct 2026

rekt.newsarticle🛡️ Security

Rekt - News or Hype?

Rekt News piece tracing three AI-security headlines back to their sources. It covers Justin Drake's October 2026 "bunker mode" warning about AI breaking ECDSA, OpenAI's report of a model spending Sepolia test ETH from a default developer mnemonic, and Wiz's "70% of the Internet" claim for PHP CVE-2026-109618 and CVE-2026-109619. It closes with four questions for checking a claim.

OpenAIPHPEthereum+3
CVE-2026-109618CVE-2026-109619Justin Drake+13

AI Security, other· Added 29 Oct 2026

wiz.ioarticle🛡️ Security

The Rise of Agentic Attacks: What They Look Like, and Where They're Headed

Wiz Research reviews agentic attacks seen in its incident response work and in public reports (ARTEX, Hermes, JPCERT/CC, CrowdStrike, DIVD). It derives fingerprints of AI-agent activity from three intrusions: machine-paced iteration, natural-language reasoning in scripts, self-correcting script versions, checklist enumeration, noisy lateral spraying, probe-before-payload and self-labeled scratch files. It also covers effects on attribution, attack scale and defense.

KubernetesAWSClaude Code+2
ARTEXHermesStorm-0940+12

Threat Intel, Blue Team & Detection, AI Security, Cloud & Infra· Published and added 29 Oct 2026

wiz.iowriteup🛡️ Security

The Rise of Agentic Attacks: What They Look Like, and Where They're Headed

Wiz research on intrusions where AI agents do the hands-on attacker work. It reviews public cases (ARTEX against South Korean banks and the ConnectWise compromise, Hermes at Thailand's Ministry of Finance, JPCERT/CC, CrowdStrike, DIVD) and three Wiz-investigated attacks. It distills fingerprints: machine-paced iteration, embedded natural-language reasoning, self-correcting scripts, checklist enumeration, noisy lateral movement, probe-before-payload habits and self-named scratch files. It also covers attribution, scale and defense implications.

WizKubernetesAWS+2
ARTEXHermesStorm-0940+12

Threat Intel, Blue Team & Detection, AI Security, Cloud & Infra· Published and added 29 Oct 2026

wiz.ioarticle🛡️ Security

PHP2Shell: Exploitation Attempts and Remediation Trends

Wiz Research follow-up on PHP2Shell (CVE-2026-109618, CVE-2026-109619) after the 21 October 2026 disclosure. Honeypot data shows two variants of an open source exploit kit, one stopped by post_max_size and the other by failed memory leaks and worker pinning, plus PHP2Shell-branded tools that rely on session poisoning and LFI. Daily exposed vulnerable machines fell about 67%.

PHPApacheRoundcube
CVE-2026-109618CVE-2026-109619PHP2Shell+7

Threat Intel, Offensive Security· Published and added 27 Oct 2026

wiz.ioarticle🛡️ Security

The Pwn Request Reckoning: What Still Works Against GitHub Actions

The Pwn Request Reckoning is a Wiz post updating the GitHub Actions pull_request_target threat model for 2026. It covers what GitHub's checkout protections, read-only cache tokens and event policies block, and what still works. Remaining paths: SHA-pinned pre-backport actions/checkout, custom checkout scripts, issue_comment and repository_dispatch triggers, script injection, artifact poisoning, self-hosted runner state and allow-unsafe-pr-checkout. It ends with grep and zizmor audit steps.

GitHub ActionsGitHubzizmor+1
pwn requestscript injectionartifact poisoning+2

DevSecOps, AppSec· Published and added 26 Oct 2026

x.comthread🛡️ Security

alex lee (@alexlee20122022) on X

Gheist is a GitHub campaign disclosed by Wiz in October 2026. Stolen tokens push ci-sync-XXXXXX branches with a sync-check workflow that dumps repo secrets base32-encoded to evade log masking, fetches the logs via API, then deletes the run. 13,500+ branches and 850+ accounts were hit since 15 September. Public repos are protected by the approval hold; private and Enterprise repos are not. The thread lists IOCs (.gdmp_pat files, "gheist" user agent, "ci: sync config" commits) and rotation steps.

GitHub ActionsGitHubWiz+2
Gheistci-sync branchsync-check.yml+3

DevSecOps, Threat Intel, Supply Chain· Added 26 Oct 2026, published 25 Oct 2026

wiz.iowriteup🛡️ Security

Gheist: Attempted Scaled Abuse of Stolen GitHub Tokens Stumbles

Gheist is a campaign tracked by Wiz Research since 15 September 2026 that uses stolen GitHub tokens to push a sync-check workflow on ci-sync-* branches in every reachable repository. The workflow prints base32-encoded secrets into logs, which the tool downloads through the GitHub API and then deletes. Over 13,500 branches from 850+ accounts were recovered. The post covers the two tool variants, a buggy self-hosted runner payload, GitHub's approval hold (which does not cover private repositories), overlaps with other campaigns, hunting queries, IOCs and hardening steps.

GitHubGitHub ActionsAWS+3
GheistGhostActionPolinRider+6

Threat Intel, DevSecOps, Blue Team & Detection· Published and added 25 Oct 2026

wiz.ioadvisory🛡️ Security

Broccoli2shell: Everything You Need To Know About The Critical Brotli Decoder Vulnerability

CVE-2026-111497 (Broccoli2Shell, also Node2Shell and HTTP2Shell) is an out-of-bounds write in the upstream Brotli C decoder. It affects Node.js, Bun, Envoy Proxy, Istio and Python packages, and can lead to memory corruption, information disclosure, crashes or RCE when untrusted Brotli data is decompressed. Wiz reports 91% of cloud environments have vulnerable resources. The post lists patching, inventory, rebuild and temporary mitigation steps.

BrotliNode.jsBun+3
CVE-2026-111497Broccoli2ShellNode2Shell+8

AppSec, Cloud & Infra· Published and added 25 Oct 2026

securityweek.comarticle🛡️ Security

LiteLLM Compromised in Fresh Supply Chain Attack

LiteLLM version 1.107.0 was published with malware to PyPI and Docker Hub on October 21, for about three hours and roughly 49,000 downloads. Attackers used GitHub CLI OAuth tokens, likely leaked through Claude Code into LiteLLM logs, to disable branch protections, redirect the releaser to a lookalike repository and sign poisoned artifacts. The payload is an infostealer and RAT; Wiz saw Amazon Bedrock abuse. The last clean version is 1.106.2.

LiteLLMPyPIDocker+3
Berri-AI/litellmLLMjackingdead drop+1

Supply Chain, DevSecOps, AI Security· Published and added 23 Oct 2026

tldrsec.comarticle🛡️ Security

[tl;dr sec] #351 - PHP2Shell, Autopatching Skills, AWS Pathrunner

tl;dr sec #351 is a weekly security newsletter. Clint Gibler describes working with OpenAI, Calif, Wiz and the PHP maintainers on the PHP2Shell unauthenticated RCE disclosure, which affects 13 years of PHP. It also covers Datadog's pathrunner AWS IAM escalation framework, Trail of Bits' patching-bugs and regression-hunt Codex plugins, XBOW finding de-duplication, backdoored open-weight models, and CREBench.

PHPAWS IAMCodex+3
PHP2ShellPatch the PlanetCalif+10

AppSec, AI Security, Cloud & Infra· Added 30 Oct 2026, published 22 Oct 2026

wiz.ioarticle🛡️ Security

ARTEX in the Wild: Storm-0940 Expands Targeting of IT and Software Vendors

Wiz Research reports an actor overlapping with Storm-0940 that used ARTEX, an open-source autonomous AI penetration-testing agent, against IT and software vendors in October 2026. It documents source-map and Swagger recon, OAuth callback and unsigned JWT probing, Cognito account-recovery abuse, tenant-isolation tests and Okta/Entra password spraying. The post lists log signals that mark the activity as agentic, such as one-second spray cadence and automatic IP and user-agent rotation.

OktaMicrosoft Entra IDAWS Cognito+3
ARTEXStorm-0940Wiz Research+5

Threat Intel, AI Security, Identity & Access· Published and added 22 Oct 2026

latent.spacearticle🧠 AI

[AINews] OpenAI’s Patch the Planet program is 1 of 2 parties to discover PHP2Shell vulnerabilities in core PHP affecting 70% of the web, using GPT-5.6 Sol; coordinated response over 2 months

AINews issue for 20-21 October 2026. The top story covers PHP2Shell (CVE-2026-109618 and CVE-2026-109619), two PHP-engine memory-corruption bugs found separately by Calif researchers using GPT-5.6 Sol under OpenAI's Patch the Planet and by Wiz, followed by two months of coordinated remediation. It also covers the Flint coding MoE, DeepSeek's DeepInfer, TorchTPU, eval critiques and agent product launches. The text is truncated.

PHPWordPressDrupal+11
CVE-2026-109618CVE-2026-109619OpenAI+35

models, inference, evals· Published and added 22 Oct 2026

latent.spacearticle🧠 AI

[AINews] OpenAI’s Patch the Planet program is 1 of 2 parties to discover PHP2Shell vulnerabilities in core PHP affecting 70% of the web, using GPT-5.6 Sol; coordinated response over 2 months

This AINews issue (20 to 21 October 2026) leads with PHP2Shell, two PHP-engine memory-corruption bugs (CVE-2026-109618 and CVE-2026-109619). Calif researchers found them with GPT-5.6 Sol under OpenAI's Patch the Planet, and Wiz reportedly found them independently with Gemini 4 Argon. It reconstructs the two-month coordinated response, Cloudflare WAF stopgaps and NSA guidance, and the dispute over vetted researcher access to models. Only the first 40,000 of 114,281 characters were reviewed.

PHPWordPressDrupal+6
CVE-2026-109618CVE-2026-109619OpenAI+18

ai-policy, models· Added 23 Oct 2026, published 22 Oct 2026

latent.spacearticle🛡️ Security

[AINews] OpenAI’s Patch the Planet program is 1 of 2 parties to discover PHP2Shell vulnerabilities in core PHP affecting 70% of the web, using GPT-5.6 Sol; coordinated response over 2 months

AINews issue of 20-21 October 2026 whose top story reconstructs PHP2Shell (CVE-2026-109618, CVE-2026-109619), two PHP-engine memory-corruption bugs with reported pre-auth RCE against WordPress, Drupal and Joomla. It covers the two-month coordinated disclosure, independent discovery by Calif/OpenAI (GPT-5.6 Sol) and Wiz, Cloudflare WAF stopgaps and NSA guidance. It flags missing primary sources: fixed versions, CVSS and leak details.

PHPWordPressDrupal+3
CVE-2026-109618CVE-2026-109619PHP2Shell+9

AppSec, AI Security· Published and added 22 Oct 2026

latent.spacearticle🛡️ Security

[AINews] OpenAI’s Patch the Planet program is 1 of 2 parties to discover PHP2Shell vulnerabilities in core PHP affecting 70% of the web, using GPT-5.6 Sol; coordinated response over 2 months

AINews issue of 20-21 October 2026 whose top story reconstructs PHP2Shell, two PHP-engine memory-corruption flaws (CVE-2026-109618 and CVE-2026-109619) with reported pre-auth RCE against WordPress, Drupal and Joomla. It covers the two-month coordinated response, separate discovery by Calif/OpenAI (GPT-5.6 Sol) and Wiz (Gemini 4 Argon), Cloudflare's WAF stopgap and NSA guidance. It lists open gaps: fixed versions, leak details, exploitation versus scanning.

PHPWordPressDrupal+3
CVE-2026-109618CVE-2026-109619PHP2Shell+12

AppSec, AI Security· Added 23 Oct 2026, published 22 Oct 2026

simonwillison.netarticle🛡️ Security

Today's PHP Security Release, and How We're Strengthening PHP Security

Simon Willison's link post on the 21 October 2026 PHP security release, which fixes two remote code execution flaws across the PHP 8.x line. The CVE IDs leaked on 20 October with a wrong CVSS of 10.0 (actual 9.2), and Calif accidentally published a proof-of-concept video. It also gives Wiz Research's timeline, with unauthenticated RCE confirmed against Drupal and WordPress in August 2026.

PHPWordPressCVSS+1
Wiz ResearchCalifPHP Foundation+3

AppSec, Threat Intel· Published and added 21 Oct 2026

protos.comarticle🛡️ Security

Remotely exploitable PHP bug found on 70% of world’s websites

PHP2Shell is a pair of unauthenticated remote code execution flaws in PHP, CVE-2026-109618 and CVE-2026-109619, found by Calif using OpenAI's GPT-5.6 Sol during an OpenAI-funded audit. Fixes ship in PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35, with backports for 7.4-8.1 rolling out, while PHP 7 and 5 sites stay unpatched. Wiz confirmed the flaws; Cloudflare applied a stopgap and Finnish and Dutch government sites went offline.

PHPCloudflareOpenAI+1
CVE-2026-109618CVE-2026-109619PHP2Shell+5

AppSec, AI Security, Threat Intel· Published and added 21 Oct 2026

endorlabs.comadvisory🛡️ Security

PHP2Shell: Critical vulnerabilities in PHP (CVE-2026-109618, CVE-2026-109619) | Endor Labs

PHP2Shell is the name for two critical PHP core memory-safety flaws, CVE-2026-109618 and CVE-2026-109619, that allow unauthenticated remote code execution. Fixes ship in PHP 8.2.35, 8.3.36, 8.4.27 and 8.5.12. Wiz researchers demonstrated RCE against WordPress, Drupal and Joomla, and Apache with mod_php is the highest risk. The post covers inventory, container rebuilds, Cloudflare WAF rules and temporary exposure reduction.

PHPWordPressDrupal+3
CVE-2026-109618CVE-2026-109619PHP2Shell+4

AppSec, DevSecOps· Published and added 21 Oct 2026

thephp.foundationarticle🛡️ Security

Today's PHP security release, and how we're strengthening security

The PHP Foundation explains the 21 October 2026 release of PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35, which fix two critical unauthenticated RCE flaws in memory management and error handling, including an OOM problem behind CVE-2026-109618. It covers the 2024 Quarkslab audit, the stalled fix, the August 2026 reports from Calif, OpenAI and Wiz, and the embargo leaks (CVE IDs, a Calif video, Chainguard images). It also lists new security team structure and AI-assisted triage.

PHPChainguardOpenAI+2
CVE-2026-109618CalifPatch the Planet+8

AppSec, other· Added 22 Oct 2026, published 21 Oct 2026

wiz.iowriteup🛡️ Security

LiteLLM Compromised, Steals Credentials

LiteLLM version 1.107.0 was uploaded to PyPI on 21 October 2026 with a credential stealer, and the same build reached GHCR and Docker Hub images. Wiz describes the three dropped files (cook.pth, cook.py, sitecustomize.py), exfiltration to a fake litellm.dev domain, a GitHub dead drop for a second stage, and the malicious commits pushed through the lookalike Berri-AI repository. The last safe version is 1.106.2.

LiteLLMPyPIDocker+3
Berri-AIcook.pthsitecustomize.py+2

Supply Chain, Threat Intel, AI Security· Published and added 21 Oct 2026

wiz.iowriteup🛡️ Security

PHP2Shell: AI uncovers critical RCE vulnerabilities affecting 70% of the Internet

PHP2Shell is Wiz Research's disclosure of memory-safety bugs in core PHP, grouped under two CVEs (up to CVSS 9.2) and fixed in patched releases on 21 October 2026. The post details four bugs, all triggered by out-of-memory fatal errors that leave stale state: an upload-progress unserializer use-after-free, a session-ID memory disclosure, a fatal-error backtrace use-after-free and an OPcache type confusion. It describes unauthenticated RCE on WordPress, Drupal and Joomla, plus detection signals and a disclosure timeline.

PHPWordPressDrupal+3
PHP2ShellWiz ResearchCalif+6

AppSec, Offensive Security, AI Security· Published and added 21 Oct 2026

openai.comarticle🛡️ Security

Patch the Planet: global response coordination as agents uncover critical vulnerabilities

OpenAI's Patch the Planet post describes the coordinated response to two critical PHP vulnerabilities. Calif found one with GPT-5.6 Sol, and Wiz independently reported both. It proposes a five-stage disclosure framework: upstream fix, advance notice to providers, government coordination, product updates and public guidance. It also lists a PHP version checker, $1 billion in subsidized Daybreak access, and open questions on disclosure windows and emergency patching.

PHPOpenAI
Patch the PlanetGPT-5.6 SolDaybreak+2

AI Security, AppSec· Published and added 21 Oct 2026
wiz.iowriteup🛡️ Security

From Phishing to LLMjacking: Threat Actors Targeting Cloud Billing Accounts for LLM Usage

Wiz CIRT investigation of LLMjacking campaigns against Google Cloud billing accounts. Attackers phished admins through malicious Google Search ads and a fake login page that captured MFA codes, then deleted the iam.allowedPolicyMemberDomains policy, added Gmail accounts as billing admins, and linked attacker-controlled projects to the victim's billing account. Victims saw tens to hundreds of thousands of dollars in Gemini API charges within 24 to 48 hours, with no log visibility into prompts. Includes hunting guidance for Workspace, Admin Activity and billing logs.

Google CloudGeminiGoogle Workspace+1
LLMjackingWiz CIRTiam.allowedPolicyMemberDomains+5

Cloud & Infra, Threat Intel, Blue Team & Detection· Published and added 20 Oct 2026

wiz.ioarticle🛡️ Security

Supply Chain Zero Days: Closing the Gap Between Publication and Detection

Wiz describes its pipeline that analyzes every new npm package version at publication, combining static analysis, an AI classifier, sandbox dynamic analysis and runtime sensor observation, then pushes IOCs to Wiz Defend before a CVE exists. It cites supply chain attacks rising from about 10% of significant incidents in H2 2025 to 25% in H1 2026, and the Axios compromise (v1.14.1, v0.30.4). The keyv case shows C2 domains fetched from an Ethereum smart contract, which only runtime monitoring caught.

npmWizEthereum
Axioskeyvcacheable+3

Supply Chain, Blue Team & Detection· Published and added 19 Oct 2026

wiz.iowriteup🛡️ Security

Loud, Fast, and Everywhere: Anatomy of a Real AI-Driven Cloud Attack

Wiz CIRT write-up of an AI agent-run intrusion against a multi-cloud organization (GCP, AWS, Kubernetes, CI/CD, GitOps, identity provider). It lists traits of AI-driven attacks: machine-speed tempo, credential chaining, pentest/probe naming, numeric task IDs and commented code. Initial access was a Java RCE in an exposed Kafka UI. It closes with detection and response advice: unified logs, workload visibility and trust isolation.

WizKubernetesAWS+2
Wiz CIRTRed Agentcredential chaining+6

Threat Intel, Blue Team & Detection, Cloud & Infra, AI Security· Published and added 19 Oct 2026

hackers-arise.comwriteup🧠 AI

Artificial Intelligence (AI) in Cybersecurity, Part 29: Creating Isolated Autonomous Agents for Hacking with NemoClaw

Hackers-Arise tutorial on NVIDIA's open-source NemoClaw, which runs OpenClaw (and Hermes or LangChain Deep Agents) inside OpenShell sandboxes. OpenShell provides kernel-level isolation and declarative YAML policies for files, credentials and network access. It covers OpenClaw's risks (543 tracked CVEs, 40,000+ exposed instances), an OpenClaw vs NemoClaw comparison, the caveat that sandbox escapes and core-logic zero-days remain possible, and a Docker/Node.js install via the nemoclaw.sh wizard with TUI testing. It also cites the Cisco AI Defense plus OpenShell case study, in which an agent that does security patching was protected against a simulated exfiltration attempt.

OpenClawNemoClawOpenShell+7
NVIDIAPeter SteinbergerJensen Huang+4

agents, ai-infra· Published and added 14 Oct 2026

x.comthread🛡️ Security

Dark Web Intelligence (@DailyDarkWeb) on X

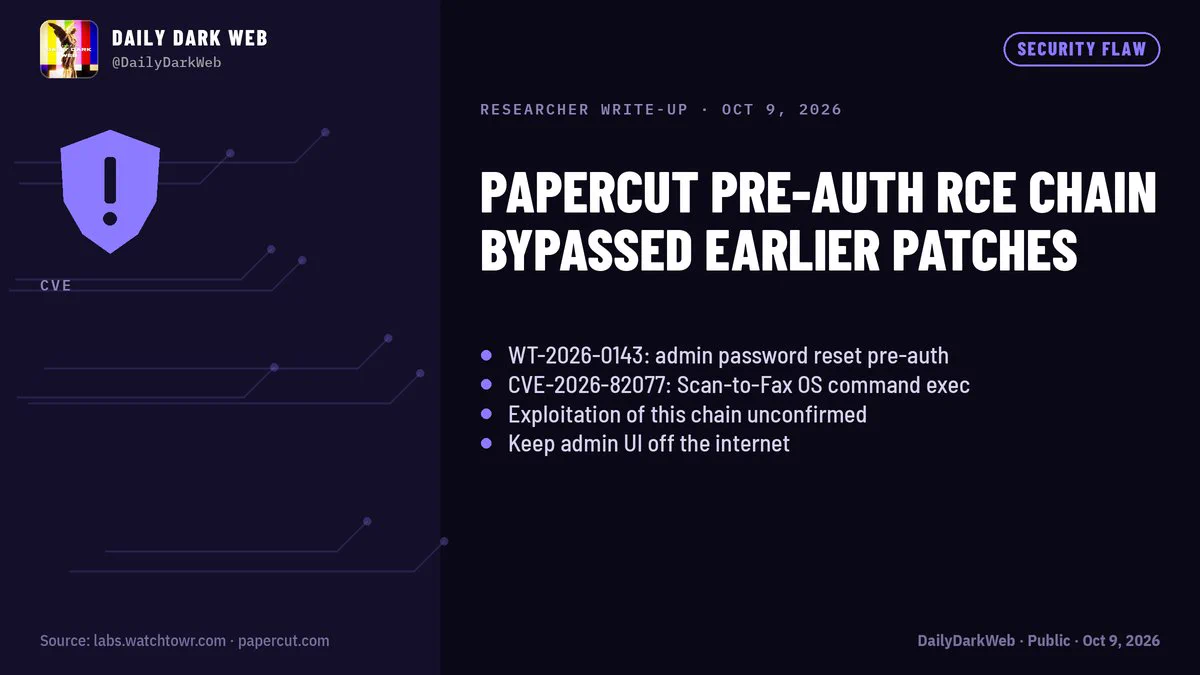
Social post summarizing watchTowr's Oct 2026 research on an unauthenticated RCE chain in PaperCut NG 26.0.4-PO build 76508: an auth bypass (WT-2026-0143, no CVE) re-runs the Setup Wizard via the Home page to reset the admin password, then CVE-2026-82077 (Scan-to-Fax path traversal) gives OS command execution. It lists fix versions (build 76530, 26.0.5, 25.0.13), notes watchTowr's detection tool covers only the bypass, and says exploitation of this chain is unconfirmed, unlike the August attacks using CVE-2026-81578 and CVE-2026-82078.

PaperCut
CVE-2026-82077CVE-2026-81578CVE-2026-82078+5

AppSec, Offensive Security· Added 13 Oct 2026, published 12 Oct 2026

labs.watchtowr.comwriteup🛡️ Security

Death By A Thousand PaperCuts (PaperCut Pre-Auth RCE Chain and Patch Bypasses WT-2026-0141-0144/CVE-2026-82077/CVE-2026-82078/CVE-2026-81578)

watchTowr's analysis of the PaperCut NG 26.0.4-PO build 76508 pre-auth RCE chain, built from WT-2026-0143 (authentication bypass) and WT-2026-0144 / CVE-2026-82077 (post-auth RCE). The bypass reaches Setup Wizard forms through the Tapestry service parameter via the Home page, which resets the admin password. The RCE uses path traversal in the Scan to Fax connector. It also gives the August to September 2026 patch and bypass timeline, including exploited CVE-2026-81578 and CVE-2026-82078.

PaperCut NGApache TapestryJava
CVE-2026-82077CVE-2026-82078CVE-2026-81578+12

AppSec, Offensive Security, Identity & Access· Added 30 Oct 2026, published 9 Oct 2026

tldrsec.comarticle🛡️ Security

[tl;dr sec] #348 - Google's PageBreak Scanner, Perplexity's Agent Security Tool, Defending Agentically

tl;dr sec #348 is a weekly security newsletter issue. It summarises Google's PageBreak agent (500+ XSS bugs found since November 2025, validated deterministically), Perplexity's open-source Numbat agent-security tool (52 CEL rules), and SpecterOps' CiliumHound. It also covers Scaleway IAM attack paths, the NCSC essay on defending agentically, Julien Vehent on detection fidelity, and Wiz's Scan for Good.

PageBreakNumbatCiliumHound+3
XSSVolt TyphoonRed Agent+6

AI Security, AppSec, Blue Team & Detection· Added 30 Oct 2026, published 1 Oct 2026
decrypt.coarticle🧠 AI

Gemini 4 Is Here, and Google’s Flagship Tops All Other AI Models on Cybersecurity

Google released Gemini 4 Argon, its new frontier model for coding, office work and cyber defense, scoring 77.9% on DeepSWE v1.1 (vs. 74.2% Claude Opus 5.5, 74.1% GPT-6 Astra) and expanding max output to 1 million tokens. On Gray Swan's indirect prompt injection benchmark it posted a 0.7% attack success rate, edging out Claude Opus 5.5 and Claude Fable 5.1 (both 1.0%), and scored 70.9% on Google's internal Wiz Penetration Test Benchmark versus 58.2% for the earlier restricted Gemini 3.8 Flash Cyber. The model initially ships without cyber guardrails only to vetted defenders via Google's Fairwind Program before wider API and Google AI Ultra release at $2/$10 per million input/output tokens.

Gemini
GoogleClaude Opus 5.5Claude Fable 5.1+16

models, evals· Published and added 30 Sep 2026

decrypt.coarticle🛡️ Security

Gemini 4 Is Here, and Google’s Flagship Tops All Other AI Models on Cybersecurity

Decrypt covers Google's Gemini 4 Argon launch, reporting it scored a 0.7% attack success rate on Gray Swan's Indirect Prompt Injection benchmark, beating Claude Opus 5.5 and Claude Fable 5.1 (both 1.0%), GPT-6 Astra (8.5%), and far outperforming Grok 4.6 and Kimi K3 (~52% each). It also details Argon's cyber-defense capability: it ships first to vetted defenders through Google's Fairwind Program "without cyber guardrails," scored 70.9% on the internal Wiz Penetration Test Benchmark writing working exploits against real web-app flaws, and reportedly helped Wiz find a critical healthcare-software flaw earlier models missed.

GeminiClaudeOpenAI+3
Fairwind ProgramGray SwanGemini 4 Argon+8

AI Security· Published and added 30 Sep 2026

wiz.ioarticle🛡️ Security

Securing the Kubernetes Supply Chain: Introducing WizOS Helm Charts

Wiz Research examined the source repositories and CI/CD pipelines behind 1,500 popular Helm charts on Artifact Hub (mapping to 814 unique GitHub repos) and found 61 repos (7.5%) with confirmed supply-chain risk, including 20 charts with CI/CD workflow weaknesses and 25 depending on unmaintained/archived upstream projects. Two disclosed findings illustrate the risk classes: KubeView's go.mod referenced a Go module under a GitHub username that didn't exist, making it hijackable by anyone who registered the name, and Meilisearch's Helm chart repo had a GitHub Actions workflow triggered by PR comments that injected the commenter's branch name into a shell command while skipping author-association checks, letting any GitHub user run commands with a bot token that had push access. The post then pivots to promoting WizOS Helm Charts, Wiz's hardened/signed/CVE-scanned chart catalog built to close these gaps.

KubernetesHelmGitHub Actions+2
KubeViewMeilisearchpwn request+4

Supply Chain, DevSecOps, Cloud & Infra· Published and added 30 Sep 2026

wiz.iowriteup🛡️ Security

The Blue Agent POV: Investigating Multi-Platform Data Exfiltration Across AWS and GitHub

Wiz walks through a case study of its "Blue Agent" autonomous SOC investigator tracing a compromised CI/CD service account (svc_automation) across AWS and GitHub. The attack chain: a stolen GitHub token cloned 18 private repos containing hardcoded AWS keys, which were used to authenticate to AWS from Kali Linux via a Zenlayer VPN IP, pivot to a second account, run SSM SendCommand against a production Windows domain controller, and stage custom Python exfiltration scripts (mssql_table_export.py, pg_table_export.py, billing_export2.py) in S3 to pull data from MSSQL, PostgreSQL, and billing systems. The piece details the investigative technique used - 30-day baseline comparison, ASO/IP dispersion across the tenant, and correlating CloudTrail management-plane events with S3 data-plane events and GitHub audit logs.

AWSGitHubKali Linux+3
AWS IAMSSM SendCommandAssumeRole

Blue Team & Detection, Cloud & Infra· Published and added 29 Sep 2026

github.comrepo🧠 AI

Uncensored and Offensive Security AI Models Benchmark

A GitHub README curating open-weight "uncensored" and security-fine-tuned LLMs (e.g. WhiteRabbitNeo's DeepHat V2, BugTraceAI-CORE, CYBER-FROST, CyberPal2.0, Lily-Cybersecurity-7B, Dolphin-Llama3-8B, Wizard-Vicuna-13B-Uncensored, huihui-ai's abliterated Qwen variants) with HuggingFace download links, quantization formats (GGUF, FP8, Q4_K_M, Q6_K), and training techniques used (SFT, QLoRA, DPO, abliteration, MoE/MTP architectures). It also includes a glossary explaining abliteration (orthogonalizing the refusal direction out of the residual stream, per Arditi et al. 2024) and references benchmarks like CyberBench and TrustedSec's LLM Attack Benchmark, making it a practical reference for anyone sourcing or deploying refusal-removed models.

Hugging FaceGGUFLoRA+3
WhiteRabbitNeoBugTraceAIBlackfrost-AI+18

models, inference· Added 2 Oct 2026, published 29 Sep 2026

thehackernews.comarticle🛡️ Security

Mini Shai-Hulud Worm Compromises TanStack, Mistral AI, Guardrails AI & More Packages

The Hacker News details the "Mini Shai-Hulud" campaign by threat actor TeamPCP, which compromised npm and PyPI packages from TanStack, UiPath, Mistral AI, OpenSearch and Guardrails AI via a chained GitHub Actions attack (pull_request_target abuse, cache poisoning, OIDC token extraction), now tracked as CVE-2026-45321 (CVSS 9.6). The worm mints npm publish tokens directly from stolen OIDC credentials to self-propagate — the first documented case of a worm producing validly SLSA Build Level 3-attested malicious packages — and deploys an obfuscated credential stealer with IDE persistence hooks, a GitHub Actions secret-exfiltration workflow, and a dead-man's-switch that runs "rm -rf" if its rogue npm token is revoked. Over 170 packages and 400+ attacker-controlled repos have been identified across npm and PyPI, with findings credited to Aikido Security, Endor Labs, SafeDep, Socket, StepSecurity, Snyk, Wiz and Microsoft.

npmPyPIGitHub Actions+3
CVE-2026-45321TeamPCPMini Shai-Hulud+2

Supply Chain, DevSecOps, Threat Intel· Added 26 Sep 2026

wiz.iowriteup🛡️ Security

The Infostealer Incursion: How Stolen Credentials Breach Cloud, Code, and AI Environments

Wiz Research analyzed infostealer-harvested secrets (via its NordStellar integration) to map exactly which credentials malware families like Lumma, RedLine, and Vidar target across AWS, Azure, GCP, GitHub, GitLab, and AI platforms, and how those secrets translate into cloud account takeover. It gives concrete file paths and artifacts attackers hunt for (~/.aws/sso/cache OIDC tokens, Azure accessTokens.json, GCP credentials.db/access_tokens.db, GitHub gh hosts.yml and SSH keys, GitLab Runner config.toml, OpenAI/ChatGPT session cookies, and Claude Code's ~/.claude/.credentials.json OAuth tokens), plus stats: three malware families cause 85.7% of incidents, AWS/GCP account for 46%/13% of stolen secrets, GitHub ~10%, AI platforms ~5%. It also covers CI/CD-targeting infostealers (Miasma, TeamPCP) and session-cookie hijacking as an MFA bypass technique.

AWSAzureGCP+3
CVE-2023-7028LummaRedLine+11

Threat Intel, Cloud & Infra, Identity & Access· Added 27 Sep 2026, published 25 Sep 2026

wiz.ioarticle🛡️ Security

Scan for Good: Using AI to discover and fix high-priority exposures across public services and critical infrastructure

Wiz announces Scan for Good, an initiative that pairs its AI pentester (Red Agent) and Google DeepMind's Gemini 3.8 Flash Cyber with human researchers. It scans authorized public-facing services of critical infrastructure, hospitals, municipalities and nonprofits for exposures and attack paths. It lists anonymized findings, including an exposed admin key over an 8.8M-file archive, NoSQL injection at an AI training-data platform, unsafe upload to hospital server control, and public CI/CD workflows leaking credentials. It also sets out the authorization, human-validation and private-disclosure rules.

WizGemini
Scan for GoodRed AgentWiz Research+10

AI Security, Offensive Security, Cloud & Infra· Published and added 24 Sep 2026

adversa.aiwriteup🛡️ Security

Top 10 attacks on Claude Code and what each one actually broke

Adversa AI catalogs ten distinct Claude Code attacks documented between September 2025 and September 2026: the Miasma supply-chain worm that hit 73 Microsoft repos via a SessionStart hook, TrustFall's unsandboxed MCP server execution on folder-trust, Check Point's CVE-2025-59536/CVE-2026-21852 pre-trust-dialog code execution and API key theft, Sentry-DSN-based "Agentjacking" prompt injection via fake bug reports, a 50-subcommand cap that silently disables deny rules, the SymJack symlink-to-config-hijack primitive working across six agent CLIs, Wiz's GhostApproval deceptive-approval-prompt finding (with CVE-2026-12958 at AWS and CVE-2026-50549 at Cursor but none at Anthropic), the Plugin4Shell SHA/branch-name collision bypassing plugin pinning, an academic MCP tool-poisoning paper achieving RCE on agent/LLM pairs, and SkillCloak's self-extracting-packer bypass of skill scanners. The piece argues almost none of these are model-behavior bugs - they are trust-boundary and consent failures in the surrounding tooling - and closes by pitching Adversa's own runtime agent security gateway as the fix.

Claude CodeModel Context ProtocolSentry+3
CVE-2025-59536CVE-2026-21852CVE-2026-12958+20

AI Security, Supply Chain· Added 7 Oct 2026, published 23 Sep 2026

github.comrepo🛡️ Security

shai-hulud-detect: multi-ecosystem npm/PyPI/Composer/Crates/Go/Hex/RubyGems supply-chain worm scanner

shai-hulud-detect is a dependency-free Bash scanner that checks projects against a 5,782-entry list of compromised npm, PyPI, Composer, Crates, Go, Hex, and RubyGems package versions, plus content-pattern indicators of compromise (malicious file hashes, C2 domains, dead-man's-switch artifacts, forged commits, suspicious lifecycle hooks) tied to the Shai-Hulud supply-chain attack waves. It supports single-project and bulk scanning, CI-friendly exit codes, JSON/log output for pipeline gating, and a --check-host mode to detect the May 2026 gh-token-monitor/kitty-monitor persistence daemons that wipe hosts if their monitored GitHub token is revoked (with a documented safe remediation order). Detection is read-only; new package entries are sourced from named threat-research firms (Socket, StepSecurity, Aikido, Snyk, JFrog, Wiz, Semgrep, SafeDep, GitGuardian, OX Security) and cited in PRs.

npmPyPIComposer+3
Shai-Huludgh-token-monitorkitty-monitor

Supply Chain, DevSecOps· Added 23 Sep 2026

tldrsec.comarticle🛡️ Security

[tl;dr sec] #346 - Can AI Do Novel Security Research?, Anthropic's Threat Intel Report, How Cloudflare Enforces Engineering Standards

tl;dr sec #346 is a weekly security newsletter issue. It covers James Kettle's HTTP Terminator, an autonomous system that invented HTTP desync techniques including Shared Parser Confusion. It also covers Anthropic's September 2026 Claude misuse report, Wiz's report on Artifactory exploitation (CVE-2026-42016, CVE-2026-42018, CVE-2026-82329), Sysdig's marimo CVE-2026-39987 findings, Synacktiv's EKS forensics guide, and Cloudflare's AI-enforced engineering Codex.

ClaudeAnthropicBurp Suite+3
CVE-2026-39987CVE-2026-42016CVE-2026-42018+15

AI Security, AppSec, Threat Intel· Added 30 Oct 2026, published 17 Sep 2026

wiz.iowriteup🛡️ Security

Exploring the new AWS Sign Up experience

Wiz researchers reverse-engineered AWS's new sign-up experience, which silently creates a three-account AWS Organization (management, identity, and a restricted sandbox member account) with Builder ID login instead of root credentials. They found the sandbox blocks security services like GuardDuty, SecurityHub, Detective, Inspector, Macie and Access Analyzer via an allowlist SCP (FreeTierSCP), while still permitting risky practices such as IAM user access keys, public S3 buckets, and IMDSv1 EC2 instances; a data-perimeter RCP also blocks cross-account sts:AssumeRole until the account is upgraded, potentially pushing vendors back toward IAM user keys. The new IAM Role Manager feature further undermines least privilege by auto-attaching PowerUserAccess to console-created roles.

AWSAWS IAM
Control TowerAccountFullAccessRoleAWSManagedAccountManagementAccessRole+7

Cloud & Infra, Identity & Access· Published and added 17 Sep 2026

wiz.ioarticle🛡️ Security

Building an AI Detection Engine That Understands Agent Intent

Wiz describes an AI detection engine that analyzes model input/output telemetry (prompts, system prompts, tool calls, reasoning) rather than just outputs, in order to catch shifts in AI agent intent such as indirect prompt injection. It walks through OpenAI's disclosed Hugging Face/ExploitGym incident and an internal support-agent phishing-relay scenario, then describes a staged pipeline (regex/SLM candidation, light LLM filtering, deep LLM analysis, correlation with cloud/runtime telemetry) validated against a benchmark of 100+ simulated scenarios covering 57 injected attacks and 45 benign workflows across CI/CD, DevOps, data analyst, support, CLI, and cloud auditor agent personas.

WizOpenAIHugging Face+1
ExploitGym

AI Security, Blue Team & Detection· Published and added 17 Sep 2026

github.comrepo🛡️ Security

Shai-Hulud-2.0-Detector — npm supply-chain compromise scanner

Shai-Hulud-2.0-Detector is a GitHub Action and CLI tool that scans package.json/lockfiles for packages compromised in the Shai-Hulud 2.0 (Nov 2025) and ChainDrop (Aug 2026) npm supply-chain worms. It uses semver-precise matching against a database of 1,241+ known-compromised package versions (auto-updated daily from Datadog and Wiz Research feeds) to flag malicious preinstall/postinstall droppers (setup_bun.js, Math_Symbol.js), rogue GitHub self-hosted runners named SHA1HULUD, and ChainDrop's new IDE-persistence hooks in .claude/settings.json and .vscode/tasks.json. It ships SARIF output for GitHub Security tab integration, an allowlist system, and a detailed incident-response guide covering credential rotation and forensic checks.

npmGitHub ActionsBun+3
Shai-Hulud 2.0ChainDropkeyv+6

Supply Chain, DevSecOps, Blue Team & Detection· Added 16 Sep 2026

wiz.ioadvisory🛡️ Security

Artifactory Under Attack: In-the-Wild Exploitation of CVE-2026-42016, CVE-2026-42018 & CVE-2026-82329

Wiz Research documents active in-the-wild exploitation of three JFrog Artifactory vulnerabilities: CVE-2026-42018 (exposes an internal anonymous-user JWT via POST /access/api/v1/aws/token/), CVE-2026-42016 (token scope validation flaw allowing that JWT to be escalated to admin via POST /access/api/v1/tokens), and CVE-2026-82329 (unauthenticated admin access via POST /access/api/v1/registry/join, added to CISA KEV). Attackers chained the first two to create persistent admin accounts, deploy malicious Groovy plugins for RCE, and drop Rust-based C2 backdoors, while CVE-2026-82329 was exploited independently for configuration exfiltration, cluster join-key theft, and credential/SSH-key persistence. The post includes exact request sequences, detection signatures, affected/fixed version ranges, and remediation guidance.

JFrog ArtifactoryRust
CVE-2026-42016CVE-2026-42018CVE-2026-82329+1

AppSec, Threat Intel, Blue Team & Detection· Published and added 10 Sep 2026

tldrsec.comarticle🛡️ Security

[tl;dr sec] #345 - Bug Rumors → Exploits, Version Control DFIR, Agentic Worms

tl;dr sec issue #345 is a security newsletter digest. It covers Greptile's test showing models miss bugs in their own code, an OCaml cohttp path traversal fix probed within ten minutes of the PR, and a Wiz Version Control DFIR poster for GitHub, GitLab, Bitbucket and Azure DevOps. It also covers an arXiv paper on open-weight agentic worms (61.8% infection of a 33-host testbed) and Endor Labs' 14 flaws in seven AI orchestration platforms.

GitHubGitLabBitbucket+3
path traversalprompt injectionModel Inversion+7

AI Security, AppSec, Blue Team & Detection· Added 30 Oct 2026, published 10 Sep 2026

wiz.iowriteup🛡️ Security

Off Guard: Breaking LiteLLM from authentication bypass to cloud compromise

Wiz researchers chain three LiteLLM flaws into a full pre-auth-to-cloud-compromise path: an MCP endpoint authentication bypass (CVE-2026-59822) that grants a session with any garbage Bearer token, a custom-code-guardrail sandbox bypass leading to root RCE (CVE-2026-59821) via exec() on unsanitized admin-submitted Python, and a config-endpoint authorization gap (CVE-2026-35029). They also show pass-through endpoints can be pointed at the AWS IMDS to steal IAM credentials, bypassing IMDSv2 via header-prefix forwarding. A scan of ~3,074 internet-facing instances found 9.6% accepting the default sk-1234 master key or no auth at all, and CVE-2026-59822 is now in CISA's KEV catalog with observed in-the-wild exploitation.

LiteLLMModel Context ProtocolAWS+3
CVE-2026-59822CVE-2026-59821CVE-2026-35029+1

AI Security, AppSec, Cloud & Infra· Published and added 9 Sep 2026

endorlabs.comarticle🛡️ Security

Secrets in AI-Generated Code: How Coding Agents Leak Credentials | Blog | Endor Labs

Endor Labs breaks down why AI coding assistants (Claude Code, Cursor, etc.) hardcode and leak secrets (CWE-798): they learn the habit from public training data, then compound it by ingesting whole workspaces including .env files and copying live tokens into new code or MCP configs. It cites hard data — GitGuardian's 2026 report found 28.65M new hardcoded secrets on public GitHub in 2025 and a 3.2% secret-leak rate on Claude Code-assisted commits vs 1.5% baseline, Lakera found credentials in 33 .claude/settings.local.json files across 30 packages, and Wiz found AI-related secrets among the most common validated leaked credential types — then lays out a layered defense (pre-commit/IDE/CI/CD/full git-history scanning, active credential validation, secure prompting) and an incident-response order of operations (rotate, investigate, purge history, revoke, re-scan).

GitleaksTruffleHogEndor Labs+2
CWE-798FedRAMPEU Cyber Resilience Act

DevSecOps, AI Security· Added 3 Sep 2026, published 2 Sep 2026

deepmind.googlearticle🧠 AI

Introducing Gemini 3.8 Flash and 3.8 Flash Cyber

Google DeepMind announces Gemini 3.8 Flash, an upgraded reasoning/coding model at the same $0.75/$3.75 per-million-token price as 3.7 Flash, plus Gemini 3.8 Flash Cyber, a specialized variant for vulnerability discovery and automated patching offered to vetted defenders through a new 'Fairwind Program'. The post cites benchmark gains on DeepSWE v1.1, HLE-Verified, Vals Finance Agent V2 and Harvey's Legal Agent Benchmark for the general model, and CyberGym plus Collinear's CWE-Bench for the cyber variant, along with real-world results from Chrome Security, Wiz and Google's Cloud Vulnerability Research team.

Gemini
Google DeepMindGoogleDeepSWE v1.1+15

models, evals· Added 29 Sep 2026, published 2 Sep 2026

deepmind.googlearticle🛡️ Security

Introducing Gemini 3.8 Flash and 3.8 Flash Cyber

Google DeepMind announces Gemini 3.8 Flash and a gated variant, Gemini 3.8 Flash Cyber, the latter positioned as a frontier-level model for autonomous vulnerability discovery and automated patching, accessible to vetted defenders through a new 'Fairwind Program.' On the CyberGym benchmark and an internal 20-language vulnerability-discovery benchmark it reports over 70% success, and on the Collinear CWE-Bench patching benchmark it nearly matches a larger frontier model (47.2% vs 47.8% pass@1) at much lower cost; Google cites Chrome Security producing 2.6x more correct patches and Wiz seeing higher recall at lower cost using the model, plus a case where Google's Cloud Vulnerability Research team found a critical vulnerability in under 2 hours.

GeminiChromeWiz
CyberGymCWE-BenchFairwind Program+5

AI Security, AppSec· Added 29 Sep 2026, published 2 Sep 2026

wiz.iowriteup🛡️ Security

Inside 90 days of attacks on AI infrastructure

Wiz Threat Research ran honeypots across LiteLLM, Flowise, LangChain, Langflow, ChromaDB, Ollama and other AI/ML services for 90 days, capturing active exploitation of an MCP Gateway auth bypass (CVE-2026-59822) and an MCP server test-endpoint command injection (CVE-2026-42271, in CISA KEV, chainable with Starlette CVE-2026-48710 for unauthenticated RCE and linked to Qilin ransomware exploitation) used to deploy fileless cryptominers. It also documents blind prompt injection campaigns against LangChain, Flowise, OpenWebUI, and Node-RED agents that trigger OS command execution confirmed via out-of-band DNS callbacks to OAST domains.

LiteLLMLangChainFlowise+3
CVE-2026-59822CVE-2026-42271CVE-2026-48710+2

Threat Intel, Offensive Security, AI Security· Added 3 Sep 2026, published 27 Aug 2026

wiz.ioarticle🛡️ Security

From Concept to Context Engine: How Wiz Built AI-Powered Data Discovery

Wiz describes the evolution of its public bucket scanner into an AI-powered "context engine" for data security posture management (DSPM): a multi-agent pipeline where lightweight models triage files and larger models perform deep content analysis, iteratively learning bucket-specific patterns to find sensitive data that regex-based scanners miss. The production system adds structured severity scoring, synthetic/test-data filtering, algorithmic file clustering for scale, and now powers classification across cloud storage, cloud drives, endpoints, and Wiz's Red Agent attack-simulation findings. A one-week scan of public buckets using the engine surfaced over 2,700 sensitive data findings, including correlated credential/schema/export file sets that regex tools would treat as unrelated.

Wiz
Red Agent

AI Security, Cloud & Infra· Added 3 Sep 2026, published 27 Aug 2026

wiz.ioarticle🛡️ Security

Version Control DFIR: a Cheatsheet to GitHub, GitLab, Bitbucket, and Azure DevOps

Wiz CIRT published a DFIR cheatsheet/poster covering the four most common version control platforms (GitHub, GitLab, Bitbucket Cloud/Data Center, Azure DevOps), detailing available log sources, default retention limits (e.g. GitHub's 7-day Git read/write event retention, GitLab not storing Git operations by default), a pre-incident configuration checklist (enabling source-IP metadata, extending retention, log streaming), and a MITRE ATT&CK-mapped matrix of platform-specific audit event names to hunt for during investigations. It illustrates the gaps with a real incident where a compromised token was used to mass-clone repositories containing plaintext secrets, and shows how the same action (e.g. mass repo cloning) surfaces under different event names per platform (git.clone in GitHub, repository_git_operation in GitLab, RepositoryCloneEvent in Bitbucket Data Center).

GitHubGitLabAzure DevOps+2
TeamPCP

Blue Team & Detection, Supply Chain· Added 3 Sep 2026, published 27 Aug 2026

wiz.ioarticle🛡️ Security

The State of Cloud Risk 2026: Most Security Findings Aren’t Real Attacker Opportunities

Wiz Research's blog summary of its "State of Cloud Security Risk 2026" report finds that most high-severity cloud security alerts are not real attacker opportunities once environmental context (external reachability, toxic permission combinations, sensitive data access) is applied, eliminating over half of flagged findings. Key data points include the average vulnerability-to-exploitation window shrinking to 21.5 days (per Wiz's ZeroDayClock tracking), 30% of cloud environments containing an externally exposed machine tied to high-impact lateral movement paths, and software RCE accounting for only 9% of exploitable findings versus access/credential/secrets pathways.

Wiz
ZeroDayClock

Cloud & Infra· Added 3 Sep 2026, published 26 Aug 2026

opensourcemalware.comtalk🛡️ Security

The OpenSourceMalware Show #18

Episode 18 of the OpenSourceMalware Show discusses the compromise of Rust maintainer 'dhrundy' that pushed malicious versions of arrayref (245M+ downloads), internment, and append-only-vec with a typosquatted build dependency executing a remote binary at compile time, which Wiz Research ties to DPRK infrastructure shared with the Mastra and Axios npm compromises. It also covers StubMaker, a campaign that started as RubyGems typosquats of bundler/i18n/rake/activesupport and shares byte-identical payloads (a 22MB Rust loader with an embedded Go infostealer, including a Chrome App-Bound Encryption bypass) with a 40-package npm typosquatting cluster targeting axios, chalk, commander, lodash, react and typescript, with signs it also hit PowerShell. The hosts also note a rising trend of attackers bundling compiled C++/Rust/Go binaries in npm/RubyGems packages (a red flag for analysts) and a PolinRider reinfection wave now using NullReceiver instead of EtherHiding for stage-two C2 hiding.

RustnpmRubyGems+3
StubMakerarrayrefDPRK+9

Supply Chain, Threat Intel, Malware & RE· Added 3 Sep 2026, published 21 Aug 2026

wiz.iowriteup🛡️ Security

Rust Supply Chain Attack on arrayref: Significant Overlap with DPRK Campaigns

Wiz researchers found that malicious versions of the Rust crates arrayref, internment, and append-only-vec were published to crates.io, each pulling in a typosquatted build-dependency (proc-macro1, mimicking proc-macro2) whose build.rs executes a remote payload at compile time. The payload beacons to a C2 endpoint (/49890878) shared with the Mastra campaign, disables TLS validation, enumerates Chrome/Brave/Edge saved logins via their SQLite stores, persists via Registry Run keys/LaunchAgents/systemd, and falls back to a DGA — with C2 infrastructure and SSL-issuer overlap tying it to DPRK/Sapphire Sleet activity previously seen in the Mastra and axios supply chain attacks. arrayref is used in roughly 75% of Rust environments, making this a high-impact build-time compromise.

RustCargocrates.io+3
arrayrefinternmentappend-only-vec+5

Supply Chain, Threat Intel, Malware & RE· Added 3 Sep 2026, published 20 Aug 2026

tldrsec.comarticle🛡️ Security

[tl;dr sec] #342 - Figma's Agentic Detection, Agent Identity, Uber's Agent-(E)DR

tl;dr sec #342 is a weekly security newsletter issue. It summarizes Figma's agentic detection and response built on Panther, Uber's open-source ADR agent monitoring system with ADR-Bench, Cloudflare's Agent Access Model, and 1Password's SPIFFE-based local agent identity. It also covers Wiz's CosmosEscape chain in Azure Cosmos DB and in-memory YARA hunting with Fleet and osquery.

PantherAzure Cosmos DBosquery+3
CosmosEscapeAgent Access ModelBeyond Zero+8

AI Security, Blue Team & Detection, Identity & Access· Added 30 Oct 2026, published 20 Aug 2026

wiz.iowriteup🛡️ Security

How to Spot and Stop Rogue Device Joins

Wiz details how attackers abuse Entra ID's Device Registration Service to register rogue devices — often via device code phishing — to satisfy Conditional Access policies requiring joined devices, commonly using the open-source ROADrecon framework and predictable names like DESKTOP-XXXXXXXX. As attackers shift to AI-generated, benign-looking device names (e.g., "Work PC") and plausible User-Agent strings, static IOC matching breaks down, so Wiz shifted to behavioral detections: naming-convention anomaly detection against tenant baselines and correlating device-code-phishing alerts with subsequent device registrations, including a shared KQL query for identifying anomalous naming baselines.

Microsoft Entra IDMicrosoft 365Azure+3
device code phishingAiTMlockwall.xyz+1

Identity & Access, Blue Team & Detection, AI Security· Added 3 Sep 2026, published 18 Aug 2026

wiz.iowriteup🛡️ Security

Wiz Red Agent Finds Its Way Into Snowflake’s Internal Jira Through a Flaw in a GitHub Copilot–Assisted PR

Wiz's autonomous "Red Agent" discovered a GitHub Actions script-injection vulnerability in snowflakedb/snowflake-connector-net's jira_issue.yml workflow, introduced when a PR (co-authored by GitHub Copilot) replaced a safe env:/jq pattern with direct interpolation of the attacker-controlled issue title. GitHub Advanced Security scanned the same PR and workflow but failed to flag the injection; Red Agent autonomously crafted and self-corrected a payload after a bash syntax error, exfiltrated Jira OAuth credentials via an out-of-band callback, and used them to access Snowflake's internal Jira (engineering, security, and bug-bounty projects) — all without human intervention. Snowflake patched and rotated credentials the same day the flaw was reported via HackerOne.

GitHub ActionsGitHub Advanced SecurityGitHub Copilot+3
Red AgentWiz Research

DevSecOps, AI Security, Offensive Security· Added 3 Sep 2026, published 17 Aug 2026

wiz.iowriteup🛡️ Security

How to Investigate GitHub PAT Compromise: Lessons From a Multi-Organization Campaign

Wiz's Customer Incident Response Team (CIRT) details a real campaign (mid-May–early June 2026) in which stolen GitHub Personal Access Tokens were used for repository reconnaissance, low-volume validation cloning, and then mass exfiltration of thousands of repos per organization from AWS IPs using automated tooling. The post provides a structured investigation playbook — containing the compromised PAT, expanding the timeline via GitHub audit logs and Enterprise Log Streaming, tracing the leak source, assessing blast radius (exposed secrets/PII in exfiltrated repos), rotating credentials, and hunting for downstream cloud abuse — while noting GitHub's 7-day audit log retention limits visibility.

GitHubAWSWiz+1
Wiz CIRT

Blue Team & Detection, Threat Intel, Identity & Access· Added 3 Sep 2026, published 13 Aug 2026

wiz.ioarticle🛡️ Security

Closing the Blind Spot: Securing Personal Repositories in the Software Supply Chain

Wiz research blog on how developers' personal public GitHub repositories create a secrets-exposure blind spot outside org security boundaries, citing that 65% of the Forbes AI 50 had verified secret leaks and 56% of company-impacting secrets lived in personal repos, often granting infrastructure-level access (cloud credentials, CI/CD tokens, AI service keys). It describes Wiz Code's approach: inventorying developer identities to discover the personal repos they own, mapping leaked secrets to attack paths on the Wiz Security Graph, and using an AI-driven "Red Agent" to validate exploitability before triggering rotation/remediation workflows.

WizGitHub
Wiz ResearchRed Agent

DevSecOps, Supply Chain· Added 3 Sep 2026, published 13 Aug 2026

wiz.iowriteup🛡️ Security

Inside the Metabase SQLi: Exploited in the Wild

Wiz Research reverse-engineers CVE-2026-72898 (GHSA-vwf4-m7j8-wcjf), a zero-day SQL injection in Metabase's /api/session/reset_password endpoint exploited in the wild against Metabase Cloud since August 2026. The bug chains Clojure's merge (which lets an attacker-supplied user-id survive an auth-result merge), JSON keywordization, and HoneySQL's :raw keyword to smuggle unparameterized SQL into a t2/select-one query, yielding blind SQL injection. The post walks through decompiling patched vs. vulnerable JARs to reconstruct the flaw, notes ~2,500 internet-exposed Metabase instances per Shodan, and gives a curl-based exploitability check plus remediation guidance.

MetabaseClojureHoneySQL+2
CVE-2026-72898GHSA-vwf4-m7j8-wcjfWiz Research

AppSec· Added 3 Sep 2026, published 10 Aug 2026

wiz.iowriteup🛡️ Security

Cloud Threat Highlights: H1 2026

Wiz's H1 2026 cloud threat report documents a 60% jump in significant incidents driven by a doubling of supply-chain attacks (TeamPCP's npm/PyPI/GitHub Actions credential-harvesting spree, its open-sourced Shai-Hulud worm spawning Miasma/Hades/Megalodon/IronWorm follow-ons, North Korea's axios and @mastra trojanizations) and by growing attacks on AI infrastructure, including exposed unauthenticated MCP servers, LiteLLM/Dify/Langflow/n8n/Ollama vulnerabilities, and cryptominers deployed via a Langflow RCE. It also profiles JINX-0163, a cloud-native extortion group targeting non-human identities (service accounts/IAM roles) across AWS/Azure/GCP/Okta/Snowflake linked to the "FulcrumSec" extortion brand, and closes with concrete detection techniques for stolen access keys, Kubernetes VM Run Command abuse, GCP org-policy tampering, and CloudTrail user-agent/boto3 credential-provenance mismatches.

npmPyPILiteLLM+3
TeamPCPShai-HuludMiasma+11

Supply Chain, Threat Intel, AI Security, Cloud & Infra· Added 3 Sep 2026, published 6 Aug 2026

wiz.iowriteup🛡️ Security

keyv and cacheable npm Package Hijacked in Supply Chain Attack

Wiz Research documents an ongoing supply chain attack in which a compromised GitHub maintainer account was used to publish malicious versions of keyv, cacheable, and 400+ dependent npm packages. The payload is a variant of the open-sourced 'Mini' Shai-Hulud malware (linked to the TeamPCP and antv campaigns) that steals cloud, CI/CD, AI-agent, and cryptocurrency credentials, persists via Claude Code hooks and VS Code tasks.json, exfiltrates data to attacker-controlled GitHub repos, and retrieves its C2 domain dynamically via an Ethereum smart contract (StringListStore) eth_call rather than hardcoding it.

npmGitHubEthereum+3
Shai-HuludMini Shai-HuludTeamPCP+6

Supply Chain, Threat Intel, Malware & RE· Added 3 Sep 2026, published 4 Aug 2026

wiz.ioarticle🛡️ Security

Introducing the Wiz Sensor for Developer Workstations to Protect Endpoints in the AI Era

Wiz announces a new endpoint sensor for developer workstations (Windows/macOS, private preview) that inventories packages, IDE extensions, AI coding agents, and MCP servers, and detects known/emerging supply chain attacks in real time. The post details three real-world campaigns that motivated it: Shai-Hulud (a self-propagating npm worm that ran TruffleHog via postinstall scripts to steal npm tokens and republish itself), the Axios backdoor (a compromised maintainer account injecting C2-calling code executed within 1.1 seconds of npm install), and s1ngularity (a compromised Nx build system/VS Code extension that harvested GitHub/npm/SSH/cloud credentials and weaponized local AI CLI tools like Claude and Gemini to exfiltrate filesystem data, leaking 1,000+ GitHub tokens and exposing 5,500 private repos).

npmWizNx+3
Shai-Huluds1ngularityAxios npm backdoor

Supply Chain, DevSecOps, AI Security· Added 3 Sep 2026, published 3 Aug 2026

wiz.iowriteup🛡️ Security

S3 Clones in the Neoclouds

Wiz Research examines S3-compatible object storage offerings from Nebius, Vultr, Lambda Labs, Cloudflare R2, DigitalOcean, and Crusoe, showing how each deviates from AWS S3 security defaults. Findings include providers that expose access/secret keys via list APIs (Vultr), default ACLs that would be public but aren't enforced (Lambda Labs), lack of least-privilege key scoping (Vultr, Crusoe, Lambda Labs), weak or undocumented encryption-at-rest/TLS enforcement, unstructured access-key formats that evade GitHub/secret-scanner detection, and cross-tenant bucket namesquatting risk due to shared global namespaces.

AWSCloudflareDigitalOcean+3
bucket namesquatting

Cloud & Infra· Added 3 Sep 2026, published 31 Jul 2026

wiz.iowriteup🛡️ Security

CosmosEscape: Taking Over Every Database in Azure Cosmos DB

Wiz Research found CosmosEscape, a critical Azure Cosmos DB vulnerability exploited via the Gremlin API's .NET-based query engine, whose sandbox failed to restrict .NET reflection, enabling arbitrary code execution on the DB Gateway service. This allowed retrieval of the "Cosmos Master Key," a platform-wide signing key that could fetch any Cosmos DB account's primary key and enumerate accounts via a shared Config Store, enabling attackers to compromise any customer or internal Microsoft database (including those backing Entra ID, Teams, and Copilot) from public endpoints. Microsoft fully remediated the issue and eliminated the master key architecture.

Azure Cosmos DBGremlin.NET+1
CosmosEscapeCosmos Master KeyConfig Store+1

Cloud & Infra, Offensive Security· Added 3 Sep 2026, published 30 Jul 2026

wiz.iowriteup🛡️ Security

The risk hiding behind exposed MCP servers

Wiz Research scanned MCP servers across cloud environments and found roughly 1 in 6 environments expose at least one server to the Internet, most unauthenticated and still running the pre-auth 2024-11-05 protocol version. They demonstrate anonymous tool-catalog enumeration, real data returned from production databases/CRM/IAM backends, write/delete-capable tools, and confirmed SSRF against cloud instance metadata endpoints yielding temporary credentials, plus agents that can be talked into unsafe actions by reframing requests as "routine maintenance."

Model Context ProtocolAWSOAuth
Wiz ResearchSSRFinstance metadata service

AI Security, Cloud & Infra, AppSec· Added 3 Sep 2026, published 28 Jul 2026

wiz.ioarticle🛡️ Security

Atlasのご紹介:WizのAI脆弱性リサーチャー

Wiz Research details Atlas, an autonomous multi-agent AI system for vulnerability discovery that ranks #1 on the CyberGym benchmark (90.9% success) and found 200+ previously unknown bugs in heavily audited projects like grpc, dnsmasq, Kubernetes, gVisor, the Linux kernel, and containerd. The post explains Atlas's four-stage pipeline (attack-surface mapping via code property graphs, parallel hypothesis hunting, adversarial validation between competing agents, and dynamic exploit triggering) and notes an early version of the system contributed to discovering a critical GitHub RCE (CVE-2026-3854) that paid GitHub's largest-ever bug bounty. It also outlines lessons from evaluation-driven development and plans to integrate Atlas into Wiz Code alongside Google CodeMender.

WizKubernetesLinux kernel+1
CVE-2026-3854CyberGymWiz Research

AI Security, AppSec· Added 3 Sep 2026, published 27 Jul 2026

wiz.iowriteup🛡️ Security

Opening the Black Box: Agentless Threat Detection for Virtual Appliances

Wiz details how its Agentless Workload Detection extends EDR-like visibility to FortiGate firewalls by parsing local FortiOS logs (log IDs like 32001/32002/44547/41987) to hunt for credential stuffing, rogue admin account creation, certificate manipulation, NAT/port-forwarding abuse, and FortiManager script abuse. It maps these techniques to real-world campaigns including the FortiBleed credential-compromise campaign, active exploitation of CVE-2026-24858, and UNC3886's use of CVE-2022-41328 to deploy the CASTLETAP backdoor, plus Salt Typhoon's exploitation of CVE-2023-48788 against FortiClient EMS.

FortiGateFortiManagerWiz+3
CVE-2026-24858CVE-2024-55591CVE-2024-23113+8

Blue Team & Detection, Threat Intel, Cloud & Infra· Added 3 Sep 2026, published 22 Jul 2026

wiz.ioarticle🛡️ Security

Agentless Threat Detection: Illuminating Cloud Blind Spots

Wiz Research details how its Agentless Workload Detection uncovered active exploitation across a range of cloud/network appliances and services: FortiGate zero-day account creation (CVE-2026-24858), FortiBleed credential stuffing against ~75,000 devices, PAN-OS admin-account compromise (CVE-2026-0257) and CaptivePortal exploitation (CVE-2026-0300), a critical pre-auth BeyondTrust RCE (CVE-2026-1731), the memory-disclosure bug MongoBleed (CVE-2025-14847), Redis replication-abuse for RCE, a Zabbix instance compromised via default credentials, a Linux page-cache LPE called CopyFail, malicious npm package installs (@asyncapi/specs), and WordPress wp2shell webshells (CVE-2026-63030, CVE-2026-60137). It illustrates concrete detection logic (e.g. Redis replication target rules, unusual-executable HTTP access detections) built from agent-free log collection on virtual appliances that traditionally lacked EDR coverage.

WizFortiGateRedis+3
CVE-2026-24858CVE-2026-0257CVE-2026-0300+9

Blue Team & Detection, Cloud & Infra, Threat Intel· Added 3 Sep 2026, published 21 Jul 2026

wiz.iowriteup🛡️ Security

Exploitation in the Wild of wp2shell

Wiz Research documents active in-the-wild exploitation of "wp2shell," a pre-auth RCE chain in WordPress Core (CVE-2026-63030 and CVE-2026-60137) affecting every WordPress version since December 2025, discovered by Searchlight Cyber using GPT-5.6 Sol. Attackers abuse the WordPress REST API batch endpoint (/wp-json/batch/v1) to achieve unauthenticated RCE, then deploy malicious plugins/webshells (including a disguised "CMSmap" plugin and a custom REST endpoint backdoor), enumerate users, and attempt LFI against wp-config for credential theft. The post details post-exploitation TTPs, detection signatures (HTTP 207 responses, wp2shell/rezwp2shell user agents), IOCs, and WAF/plugin-based mitigations.

WordPressPHP
CVE-2026-63030CVE-2026-60137wp2shell+5

Threat Intel, AppSec· Added 3 Sep 2026, published 20 Jul 2026

wiz.iowriteup🛡️ Security

レッドエージェントの視点:B2Bプラットフォームのクレジットシステムを壊したたった1つのブール値

Wiz's autonomous "Red Agent" AI pentester analyzed a B2B data platform's 130MB of frontend JS bundles, extracted 100+ API endpoints, and found an unused boolean flag (e.g. unmaskContactData) referenced in client code but never sent by the normal UI. Replaying a standard free-tier search request with this flag set to true caused the backend to skip credit/tier checks and return fully unmasked business emails and phone numbers for the platform's 600M+ profiles, letting free-tier users bypass the paywall entirely; the vendor fixed the flaw within two hours of disclosure.

Wiz
Red Agent

AppSec, AI Security, Offensive Security· Added 3 Sep 2026, published 15 Jul 2026

wiz.iowriteup🛡️ Security

M-Red-Team: AsyncAPI Supply Chain Compromise via GitHub Actions

Wiz Research details how an attacker used 37 decoy pull requests to mask exploitation of a pull_request_target "pwn request" misconfiguration in the asyncapi/generator GitHub Actions workflow, stealing a privileged PAT belonging to the asyncapi-bot service account. The attacker then published four malicious npm packages (five versions) under the @asyncapi namespace with over 3 million weekly downloads, delivering a self-identified "M-RED-TEAM v6.4" multi-stage payload that fetches an 8.25MB encrypted bundle from IPFS and installs a 92,000-line trojan framework with systemd persistence and HTTP/Nostr/Ethereum/libp2p C2 channels, targeting browser credentials, SSH keys, npm/GitHub tokens, AWS credentials, and crypto wallets. The piece also analyzes partial technical overlap with the Miasma malware framework and the unrelated prt-scan campaign without making definitive attribution.

GitHub ActionsnpmEthereum+3
M-RED-TEAMAsyncAPIShai-Hulud 2.0+4

Supply Chain, DevSecOps, Threat Intel· Added 3 Sep 2026, published 14 Jul 2026

snyk.ioarticle🛡️ Security

Symlinks Are Still Scary (And Yes, You Can Commit Them to Git)

Snyk explains the decades-old symlink attack (CWE-61) and the underappreciated fact that Git will happily commit, push, and recreate symlinks (file mode 120000) from a cloned repo, letting an attacker ship a file like project_settings.json that's secretly a pointer to ~/.ssh/authorized_keys. It walks through Wiz Research's "GhostApproval" report, which found that six AI coding agents (Amazon Q Developer, Claude Code, Augment, Cursor, Google Antigravity, Windsurf) can be prompt-injected via README instructions into following such a symlink and writing attacker SSH keys or shell-config payloads before the user ever sees an accurate confirmation dialog (CWE-451, UI misrepresentation). It also recaps prior symlink-driven CVEs (tar npm package CVE-2021-32803, Leaky Vessels CVE-2024-21626, Git submodule CVE-2024-32002) and gives concrete mitigations: canonicalize-then-check-boundary atomically (e.g. openat2 with RESOLVE_BENEATH), show real resolved targets in approval dialogs, and audit repos with `find . -type l` or `git ls-files -s` before trusting them.

GitClaude CodeCursor+3
CVE-2021-32803CVE-2024-21626CVE-2024-32002+6

AI Security, AppSec· Added 3 Sep 2026, published 9 Jul 2026

wiz.iowriteup🛡️ Security

GhostApproval: A Trust Boundary Gap in AI Coding Assistants

Wiz Research discloses GhostApproval, a symlink-following vulnerability (CWE-61) found in six AI coding assistants — Amazon Q Developer, Claude Code, Augment, Cursor, Google Antigravity, and Windsurf — where a malicious repo containing a symlink disguised as a config file tricks the agent into reading/writing sensitive files like ~/.ssh/authorized_keys outside the workspace sandbox. In several tools the agent's internal reasoning correctly identifies the true target file, but the confirmation dialog shown to the user still displays the fake filename (CWE-451, UI misrepresentation), turning human-in-the-loop approval into a rubber stamp; some tools (Amazon Q, Windsurf) even write to disk before the approval prompt appears. AWS (CVE-2026-12958), Google, and Cursor (CVE-2026-50549) shipped fixes; Anthropic initially rejected it as outside threat model before later shipping a symlink warning, Augment acknowledged but hasn't patched, and Windsurf has not responded.

Claude CodeCursorWindsurf+4
GhostApprovalCVE-2026-12958CVE-2026-50549+2

AI Security, AppSec· Added 3 Sep 2026, published 8 Jul 2026

wiz.ioarticle🛡️ Security

Breaking Down the White House’s Actions on Post-Quantum Cryptography Readiness

Wiz breaks down Executive Order 14409 ('Securing the Nation Against Advanced Cryptographic Attacks') and OMB memorandum M-26-15, which set accelerated federal deadlines for migrating High Value Assets and High Impact Systems to NIST-approved post-quantum cryptography (key establishment by 2030, digital signatures by 2031). It covers requirements for automated cryptographic inventories, forthcoming NIST/CISA Cryptographic Bill of Materials (CBOM) guidance, Harvest-Now-Decrypt-Later risk prioritization, FedRAMP/FAR Council contractor compliance rules, and comparable international timelines (EU, Japan, Australia, India), before pitching Wiz's own CBOM/PQC readiness tooling.

Wiz
Executive Order 14409M-26-15FAR Council+3

GRC· Added 3 Sep 2026, published 2 Jul 2026

wiz.iowriteup🛡️ Security

レッドエージェントの視点:航空会社のGraphQL APIにおけるオブジェクトレベルの認可の不備の悪用

Wiz details how its autonomous "Red Agent" AI red-teaming tool found a critical Broken Object-Level Authorization (BOLA) flaw in an unnamed airline's GraphQL booking API. Starting from just a root URL, the agent reverse-engineered client JS to mint an anonymous session token, ran GraphQL introspection to enumerate 514 queries/428 mutations, and found that mutations like bookingRetrieveByBookingId accepted sequential integer IDs with no backend authorization check — exposing full passenger PII, payment data, and write access to bookings within 15 minutes.

GraphQLWiz
Red AgentBOLAOWASP API Security Top 10

AppSec, AI Security· Added 3 Sep 2026, published 29 Jun 2026

wiz.iowriteup🛡️ Security

MCP Auto-Execution: From Git Clone to Cloud Compromise in Amazon Q VS Code Extension

Wiz Research found that the Amazon Q Developer VS Code extension auto-loaded and executed MCP server configs from .amazonq/mcp.json in a workspace with no consent prompt or workspace-trust check, and spawned those processes with full environment inheritance. Opening a malicious repository (e.g. a malicious PR, typosquatted package, or fake "coding test" per known DPRK social-engineering tactics) could therefore trigger arbitrary code execution and theft of the developer's AWS credentials, demonstrated by capturing aws sts get-caller-identity output. Amazon remediated the issue in language server version 1.65.0, adding a consent prompt before loading workspace MCP servers.

Amazon Q DeveloperVS CodeModel Context Protocol+1
Wiz ResearchDPRK

AI Security, Cloud & Infra· Added 3 Sep 2026, published 26 Jun 2026

wiz.iowriteup🛡️ Security

Red Agentの視点:いかにして推論を重ねてSSRFへと至ったか

Wiz walks through how its autonomous 'Red Agent' AI pentesting tool chained an SSRF vulnerability in a GCP Cloud Run service's ?url= file-fetch parameter into a full local file read, bypassing a strict GitHub-blob-URL validator. The breakthrough payload (github.com/x/y/blob/z//proc/self/environ) exploited a parser differential between the validator and the fetcher, letting the agent exfiltrate live GCP service-account credentials and the app's source code after 96 requests of iterative hypothesis-driven probing.

GCPWiz
Red AgentSSRFpath traversal

AppSec, AI Security, Cloud & Infra· Added 3 Sep 2026, published 17 Jun 2026

wiz.ioarticle🛡️ Security

レッドエージェント POVシリーズのご紹介

Wiz Research introduces the Red Agent AI-powered pentester and its new blog series documenting real bug classes it discovers autonomously in production. The launch post shares aggregate stats from a one-month run across roughly 1,000 environments, breaking down dominant failure modes: broken access control, leaked secrets, systemic RCE, SQL injection, PII/PHI exposure, and JWT alg:none bypasses. It teases the series first deep-dive: a GCP Cloud Run SSRF the agent found by iteratively bypassing a GitHub-URL-only validation filter over 96 iterations, escalating to unauthenticated credential and source-code extraction.

WizGCP
Red AgentWiz ResearchJWT alg:none+1

AI Security, AppSec, Offensive Security· Added 3 Sep 2026, published 17 Jun 2026

wiz.ioarticle🛡️ Security

State of Post Quantum Cryptography | Wiz Blog

Wiz's follow-up PQC research post quantifies real-world adoption of post-quantum key exchange (ML-KEM/X25519MLKEM768) and digital signatures (ML-DSA, SLH-DSA, pending FN-DSA) across AWS, Azure, and GCP APIs, OpenSSH/OpenSSL versions, and Go's crypto/tls. It finds stark gaps: Azure API servers show no PQC key-exchange support while GCP is universal and AWS sits at 13%, only 15% of TLS 1.3 connections observed use PQC-compliant key exchange, under 15% of OpenSSL instances support PQC, and less than 1% of companies use AWS KMS ML-DSA signing keys. The piece also covers the shift in PQC priority from key exchange (mitigating Harvest-Now-Decrypt-Later attacks) to digital signature migration, and the coming move to Merkle Tree Certificates to keep PQC certificate chains manageable.

AWSAzureGoogle Cloud+3
ML-KEMML-DSASLH-DSA+9

Cloud & Infra, GRC· Added 5 Sep 2026, published 28 May 2026

wiz.iowriteup🛡️ Security

Threat Actor Targets Crypto Organizations | Wiz Blog

Wiz CIRT and Wiz Research detail JINX-0164, a previously untracked financially-motivated threat actor targeting cryptocurrency organizations since mid-2025. The group uses LinkedIn-based social engineering to deliver macOS malware (the Python-based AUDIOFIX infostealer/RAT and the Go-based MINIRAT backdoor), steals developer and cloud credentials, hijacks Git commits to propagate through CI/CD infrastructure, and trojanized the npm package @velora-dex/sdk in a supply-chain attack. The post includes full IOCs, C2 domains, and detection guidance (e.g., GitHub Vigilant Mode, audit log correlation) and notes tactical overlaps with North Korean clusters like UNC1069/Sapphire Sleet without confirmed attribution.

npmmacOSPython+4
JINX-0164AUDIOFIXMINIRAT+4

Threat Intel, Supply Chain, Malware & RE· Added 5 Sep 2026, published 27 May 2026

wiz.ioadvisory🛡️ Security

Fragnesia: Linux Kernel Local Privilege Escalation via ESP-in-TCP | Wiz Blog

Wiz analyzes Fragnesia, a Linux kernel local privilege escalation in the XFRM ESP-in-TCP subsystem and a new variant of the Dirty Frag family, introduced as a side effect of a Dirty Frag patch. File-backed pages spliced into a TCP receive queue before the socket switches to espintcp ULP mode are decrypted in place, so AES-GCM keystream manipulation gives deterministic single-byte page-cache writes. The PoC uses user and network namespaces for CAP_NET_ADMIN, installs an ESP security association via NETLINK_XFRM, and overwrites /usr/bin/su in page cache to get a root shell. Ubuntu's AppArmor restrictions on unprivileged user namespaces partially mitigate it, and the post recommends vendor patches and disabling the vulnerable modules.

Linux kernelLinuxUbuntu
FragnesiaDirty FragHyunwoo Kim+7

Offensive Security, Cloud & Infra· Added 5 Sep 2026, published 13 May 2026

github.comrepo🧠 AI

Sim

Sim is an open-source (Apache 2.0) workspace for building, deploying and managing AI agents and workflows, offering a visual flow editor, 1,000+ integrations (Slack, Notion, HubSpot, Salesforce), knowledge base ingestion, and support for every major LLM plus local models via Ollama and vLLM. It ships as a cloud service (sim.ai), a desktop app, or a self-hosted Docker/Kubernetes deployment set up via an npx sim-setup wizard, and is built on Next.js, Bun, PostgreSQL/Drizzle, and ReactFlow.

Next.jsBunPostgreSQL+11
Simsim.ai

agents, llm-apps· Added 22 Sep 2026, published 13 May 2026

wiz.ioadvisory🛡️ Security

Dirty Frag (CVE-2026-43284) Linux Privilege Escalation | Wiz Blog

Wiz details "Dirty Frag" (CVE-2026-43284 and CVE-2026-43500), a Linux kernel local privilege escalation chain combining page-cache write primitives in the xfrm-ESP (IPsec) and RxRPC subsystems that let an unprivileged-but-CAP_NET_ADMIN attacker corrupt page-cache-backed memory to gain root. It is a deterministic (non-race-condition) bug class similar to Dirty Pipe and is a successor to the earlier Copy Fail (CVE-2026-31431); a public PoC exists but no official patch is available yet, and affected code paths date back to 2017 (ESP) and 2023 (RxRPC).

Linux kernelWiz
CVE-2026-43284CVE-2026-43500CVE-2026-31431+5

Offensive Security· Added 5 Sep 2026, published 8 May 2026

wiz.ioarticle🛡️ Security

Securing Jenkins: Top Attack Flows & Misconfigurations | Wiz Blog

Wiz Research breaks down Jenkins' attack surface using cloud environment telemetry: 59% of Jenkins-using environments have critical core vulnerabilities, 87% run end-of-life instances, and plugins like workflow-cps-global-lib (deprecated, 31% adoption) and extended-choice-parameter (unpatched CVEs, 14% adoption) remain widely deployed despite Jenkins' otherwise mature plugin-governance model. The post maps five recurring attack chains observed in the wild - from exposed script consoles used for cryptojacking, through CI/CD pipeline secret extraction, plugin/core exploitation for controller takeover, agent compromise for lateral movement, to IMDS-based cloud credential theft used by actors like Genesis Panda and IntelBroker to pivot into cloud control planes.

JenkinsDockerWiz
Genesis PandaIntelBrokerFox-IT+4

DevSecOps, Cloud & Infra, Threat Intel· Added 5 Sep 2026, published 6 May 2026

wiz-sec-public.github.iotool🛡️ Security

SITF Techniques Library (Wiz)

SITF Techniques Library is a browsable, searchable knowledge base from Wiz cataloging software supply chain / SDLC attack techniques, filterable by affected component and pipeline stage, in an ATT&CK-style matrix format. The live page content could not be retrieved (the JS app returned no results), so specific technique entries are unverified, but the framework's purpose is to give defenders a structured taxonomy of supply chain attack vectors across the software development lifecycle.

Wiz

Supply Chain, DevSecOps· Published and added 6 May 2026

Showing 90 of 96

Show more