Skip to content

48 results for β€œCISA”

What you seeeverything
cisa.govadvisoryπŸ›‘οΈ Security

CISA Adds Two Known Exploited Vulnerabilities to Catalog

CISA added two Ivanti Connect Secure vulnerabilities to its Known Exploited Vulnerabilities (KEV) Catalog on 30 October 2026, citing evidence of active exploitation: CVE-2026-111357 (missing authentication for a critical function) and CVE-2026-118527 (generation of predictable numbers or identifiers). The alert restates BOD 26-04, which requires federal civilian agencies to remediate KEV-listed flaws on exposed assets and check for prior compromise. It also links the KEV nomination form.

Ivanti Connect SecureCISA KEVVPN
CVE-2026-111357CVE-2026-118527BOD 26-04+1

Threat Intel, GRCΒ· Published and added 30 Oct 2026

cisa.govadvisoryπŸ›‘οΈ Security

CISA Adds Two Known Exploited Vulnerabilities to Catalog

CISA alert of 29 October 2026 adding two vulnerabilities to the Known Exploited Vulnerabilities catalog on evidence of active exploitation: CVE-2026-97229, an integer overflow in GitLab CE/EE, and CVE-2026-76418, a NULL pointer dereference from an unchecked return value in Cisco Secure Firewall ASA and FTD. It restates BOD 26-04 remediation duties for federal civilian agencies and links the KEV nomination form.

CISA KEVGitLabCisco Secure Firewall ASA+1
CVE-2026-97229CVE-2026-76418BOD 26-04+3

Threat Intel, GRCΒ· Published and added 29 Oct 2026

cisa.govadvisoryπŸ›‘οΈ Security

Hitachi Energy CoreTec Product

CISA advisory ICSA-26-302-03, republished from Hitachi Energy PSIRT 8DBD000258, covers OS command injection (CVE-2026-13162) and the Dirty Frag vulnerability (CVE-2026-43284) in Hitachi Energy CoreTec. CoreTec5 up to 3.4.0 and 5.0.0 are affected by both, and CoreTec4 up to 3.4.0 by CVE-2026-13162. The advisory was released 27 October 2026 and lists generic ICS mitigations. SSVC rates exploitation as none.

Hitachi Energy CoreTec
CVE-2026-13162CVE-2026-43284Dirty Frag+5

Hardware & RFΒ· Added 29 Oct 2026, published 28 Oct 2026

cisa.govadvisoryπŸ›‘οΈ Security

Hitachi Energy TRO600 series products

ICSA-26-302-02 is a CISA republication of Hitachi Energy PSIRT advisory 8DBD000224 on the TRO600 series. It covers CVE-2026-10756 and CVE-2026-106087, which allow remote code execution and disclosure of sensitive information. Affected versions are TRO600 up to 9.2.1.6 and 9.1.1.0, plus 9.2.2.1 and 9.1.2.0. The page gives no per-CVE detail or CVSS scores, only general ICS hardening advice. Released 27 October 2026.

Hitachi Energy TRO600
CVE-2026-10756CVE-2026-106087Hitachi Energy PSIRT 8DBD000224+1

Hardware & RFΒ· Added 29 Oct 2026, published 28 Oct 2026

cisa.govadvisoryπŸ›‘οΈ Security

CISA Adds Two Known Exploited Vulnerabilities to Catalog

CISA alert of 28 October 2026 adding two vulnerabilities to the Known Exploited Vulnerabilities Catalog on evidence of active exploitation: CVE-2026-41709 (Broadcom VMware ESX insufficient logging) and CVE-2026-46300 (Linux kernel missing variable initialization). It restates BOD 26-04, which requires federal civilian agencies to prioritize fast remediation of KEV CVEs on exposed assets and to check for prior compromise. It also links the KEV nomination form.

CISA KEVVMware ESXLinux kernel
CVE-2026-41709CVE-2026-46300BOD 26-04+1

Threat Intel, GRCΒ· Added 29 Oct 2026, published 28 Oct 2026

cisa.govadvisoryπŸ›‘οΈ Security

CISA Adds Two Known Exploited Vulnerabilities to Catalog

CISA alert of 27 October 2026 adding two vulnerabilities to the Known Exploited Vulnerabilities (KEV) Catalog on evidence of active exploitation: CVE-2026-48356, an unrestricted upload of a dangerous file type in Adobe Commerce and Magento, and CVE-2026-111497, an unchecked return value in Google Brotli. It restates BOD 26-04, which makes federal civilian agencies prioritise KEV flaws on exposed assets and check for prior compromise. No technical detail or IOCs are given.

Adobe CommerceMagentoBrotli
CVE-2026-48356CVE-2026-111497CISA KEV+2

AppSec, GRCΒ· Added 29 Oct 2026, published 27 Oct 2026

cisa.govadvisoryπŸ›‘οΈ Security

CISA Adds Two Known Exploited Vulnerabilities to Catalog

CISA added two PHP vulnerabilities to its Known Exploited Vulnerabilities Catalog on 26 October 2026: CVE-2026-109618 (memory corruption) and CVE-2026-109619 (stale internal request state). It also updated its PHP alert on critical vulnerabilities requiring immediate patching. The alert restates BOD 26-04, which requires federal civilian agencies to prioritize fast remediation of KEV CVEs on exposed assets and to check for prior compromise.

PHPCISA KEV
CVE-2026-109618CVE-2026-109619BOD 26-04+1

AppSec, GRCΒ· Added 29 Oct 2026, published 26 Oct 2026

cisa.govadvisoryπŸ›‘οΈ Security

Mitsubishi Electric and Mitsubishi Electric Iconics Digital Solutions GENESIS, GENESIS64, ICONICS Suite, Hyper Historian, AnalytiX, MobileHMI, IoTWorX, MC Works64, GENESIS32 and BizViz

CISA advisory ICSA-26-300-02 covers four vulnerabilities in Mitsubishi Electric and Mitsubishi Electric Iconics Digital Solutions GENESIS64, ICONICS Suite, Hyper Historian, AnalytiX, MobileHMI, IoTWorX, MC Works64, GENESIS32 and BizViz. CVE-2023-4863 (CWE-787 out-of-bounds write) allows code execution; CVE-2026-16436 and CVE-2026-16437 allow authentication bypass; CVE-2026-16438 allows arbitrary operations. Fixes are 10.97.3, 10.98 and GENESIS 11.04. MC Works64, GENESIS32 and BizViz are affected in all versions, and MC Works64 has no fix planned. Mitigations include removing the ClientChallengeTable.dat or SecurityChallenges.dat file contents. The fetched text was truncated, so later content is not covered.

GENESIS64ICONICS SuiteHyper Historian+3
CVE-2023-4863CVE-2026-16436CVE-2026-16437+6

Offensive Security, Identity & AccessΒ· Added 29 Oct 2026, published 26 Oct 2026

cisa.govadvisoryπŸ›‘οΈ Security

EPICS Base

CISA ICS advisory ICSA-26-300-01 (October 27, 2026) covers EPICS Base release 7.0.10 and earlier, with CVE-2026-114595 through CVE-2026-114598. Flaws include integer overflow, length parameter inconsistency and type confusion, allowing denial of service, memory corruption, information disclosure or remote code execution (CVSS v3.1 9.8). The fix is EPICS Base 7.0.11, with patches in epics-base and pvDataCPP pull requests.

EPICS BaseCVSS
CVE-2026-114595CVE-2026-114596CVE-2026-114597+5

AppSecΒ· Added 29 Oct 2026, published 26 Oct 2026

cisa.govadvisoryπŸ›‘οΈ Security

CISA: Critical Vulnerabilities in PHP Require Immediate Patching

CISA alert on CVE-2026-109618 and CVE-2026-109619 ("php2shell"), unauthenticated remote code execution flaws affecting PHP installations serving web requests, including mod_php, PHP-FPM, php-cgi, FrankenPHP and LiteSpeed. Fixed in PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35. Updated 23 October 2026 with a Sigma rule, partner advisories (NSA, NCSC-UK, ASD ACSC, NCSC-NL, NCSC-NZ, Cyber Centre) and guidance to inventory PHP, patch internet-facing systems first, and watch for PHP workers spawning shells. No in-the-wild exploitation had been observed.

PHPApachePHP-FPM+3
CVE-2026-109618CVE-2026-109619PHP2Shell+2

AppSec, Blue Team & DetectionΒ· Added 24 Oct 2026

x.comadvisoryπŸ›‘οΈ Security

lee1981 (@lee1981b) on X

CVE-2026-111497 is an out-of-bounds write in the Brotli decoder bundled with Node.js (CWE-787, CWE-252), rated CVSS v4.0 9.2 by the Google CNA and High by the Node.js project. Fixes are Node 22.23.4, 24.22.1 and 26.12.1, and 24.22.1 still labels Brotli 1.2.0 because the fix was cherry-picked. The post gives a SOC trail from input to worker, with remediation and verification steps. It notes no KEV match, CISA SSVC exploitation none, and only unverified public lab claims.

Node.jsBrotliCVSS+3
CVE-2026-111497CWE-787CWE-252+3

Blue Team & Detection, AppSecΒ· Added 26 Oct 2026, published 23 Oct 2026

enisa.europa.euadvisoryπŸ›‘οΈ Security

ENISA Technical Advisory for Software Bill of Materials

ENISA Technical Advisory for Software Bill of Materials (October 2026, TLP:CLEAR) is non-mandatory guidance for organisations, especially SMEs, starting SBOM adoption. It covers SBOM data models (CycloneDX, SPDX), a mapping of BSI TR-03183-2 fields to CISA minimum elements, lifecycle and CI/CD integration, an SBOM threat model, and security recommendations. It supports Cyber Resilience Act obligations but is not a legal interpretation.

SBOMCycloneDXSPDX
ENISAEU Cyber Resilience ActBSI TR-03183+4

Supply Chain, GRCΒ· Added 23 Oct 2026

x.comadvisoryπŸ›‘οΈ Security

lee1981 (@lee1981b) on X

CyberForge CVE of the Day #084 analyses CVE-2026-76466, a CVSS 9.8 flaw in clustered Cisco Expressway-C and Expressway-E. Persistent database cookies and weak client-certificate validation allow root OS command execution over the network. The fix is X15.5.20 (X14 and earlier must migrate), with no workaround. It adds a per-peer SOC investigation trail, reachability checks and exposure status from CISA SSVC, KEV and EPSS.

Cisco ExpresswayCVSSNVD+2
CVE-2026-76466CWE-798cisco-sa-vcs-static-cred-hr7EWZ8t+2

Blue Team & Detection, Cloud & InfraΒ· Added 24 Oct 2026, published 22 Oct 2026

cisa.govadvisoryπŸ›‘οΈ Security

#StopRansomware: SafePay Ransomware (AA26-293A)

CISA advisory AA26-293A (20 October 2026) details SafePay ransomware, active since August 2024 with at least 600 victims across critical infrastructure. It covers initial access via Mullvad VPN IPs, phished profiles and edge-device CVEs, LOTL lateral movement with PsExec, WinRM and RDP, exfiltration with RClone and WinSCP, and ChaCha20/RSA encryption. It lists IOCs, MITRE ATT&CK mappings, incident response steps and mitigations.

MITRE ATT&CKRDPAnyDesk+3
CVE-2020-3259CVE-2023-20269SafePay+11

Threat Intel, Blue Team & DetectionΒ· Added 21 Oct 2026

unit42.paloaltonetworks.comadvisoryπŸ›‘οΈ Security

Threat Brief: Active Exploitation of PAN-OS CVE-2026-0257 (Updated Oct 20)

Unit 42 threat brief on active exploitation of CVE-2026-0257, a PAN-OS GlobalProtect authentication bypass added to CISA KEV on May 13, 2026. It lists IP addresses, host IDs and PoC-derived client values to hunt in GlobalProtect logs. The October 2026 updates cover Qilin and Inc ransomware operators, MFA bypass, pivots to vCenter and ESXi with offline VMDK credential dumping, and management interface exposure on ports 4443 and 3879.

PAN-OSGlobalProtectVPN+3
CVE-2026-0257CVE-2023-27532Spikey Scorpius+10

Threat Intel, Blue Team & Detection, Identity & AccessΒ· Added 21 Oct 2026, published 20 Oct 2026

watchtowr.comadvisoryπŸ›‘οΈ Security

Frequently Asked Questions About the BeyondTrust Remote Support Arbitrary File Upload (CVE-2026-102764)

CVE-2026-102764 is an arbitrary file upload in BeyondTrust Remote Support (formerly Bomgar) caused by internal appliance components not validating message origin. Mandiant found it exploited as a zero-day in late August 2026. BeyondTrust disclosed it on 15 October 2026 and CISA added it to KEV on 16 October 2026. The FAQ covers the web shell, root escalation, credential theft, persistence, patching and compromise checks.

BeyondTrust Remote Support
CVE-2026-102764CISA KEVMandiant+4

AppSec, Threat IntelΒ· Added 30 Oct 2026, published 16 Oct 2026

watchtowr.comadvisoryπŸ›‘οΈ Security

BeyondTrust Remote Support Arbitrary File Upload (CVE-2026-102764)

CVE-2026-102764 is a CVSS 9.8 unauthenticated arbitrary file upload flaw in BeyondTrust Remote Support (formerly Bomgar) and Privileged Remote Access. Internal messaging components do not verify message origin, so remote attackers can plant files the appliance would reject. BeyondTrust disclosed it on 15 October 2026 with patch BT26-05, and CISA added it to KEV on 16 October 2026. The page lists log files to review and hardening steps.

BeyondTrust Remote SupportBeyondTrust Privileged Remote AccessCVSS
CVE-2026-102764BT26-05CISA KEV+2

AppSec, Blue Team & DetectionΒ· Added 30 Oct 2026, published 16 Oct 2026

x.comadvisoryπŸ›‘οΈ Security

lee1981 (@lee1981b) on X

Daily CVE digest on CVE-2026-76519, a CVSS 9.8 relative path traversal (CWE-23) in Cisco Secure Email Gateway's AMP File Reputation attachment processing. A crafted attachment gives unauthenticated arbitrary file writes and root command execution, and Cisco PSIRT reports active exploitation. The CVE is in CISA KEV. It lists the applicability conditions (File Reputation assigned to a policy and Content Scanner Tools earlier than 25.3.0.5525) and the fixes (scanner 25.3.0.5525, AsyncOS 15.5.5-014 and 16.5.0-780). It also covers evidence preservation, reading Cisco's System Security scan outcomes, mail/AMP log correlation, and deployment-specific recovery including cluster-key exposure.

Cisco Secure Email GatewayCisco AsyncOSCVSS+2
CVE-2026-76519CWE-23CISA KEV+4

Blue Team & Detection, Threat IntelΒ· Added 18 Oct 2026, published 15 Oct 2026

orca.securityadvisoryπŸ›‘οΈ Security

Critical GitLab RCE Lets Unauthenticated Attackers Execute Code on Servers (CVE-2026-97229)

Orca Security analysis of CVE-2026-97229, a CVSS 10.0 flaw in GitLab CE/EE. An integer overflow (CWE-190) in the CI/CD regular expression compiler gives memory corruption and code execution as the git user. It is triggered by a crafted regex in .gitlab-ci.yml combined with a UTF-8 repository path, with no authentication needed on instances that allow public project creation or self-registration. Lists affected branches (19.2 before 19.2.8, 19.3 before 19.3.5, 19.4 before 19.4.2), the absence of a workaround, interim mitigations, and a Rapid7 PoC against GitLab CE 19.4.1 with ASLR on. Notes a prior max-severity GitLab bug (CVE-2026-85706) was probed in the wild within hours and later added to CISA KEV.

GitLab
CVE-2026-97229CVE-2026-85706CWE-190+2

AppSec, DevSecOpsΒ· Published and added 14 Oct 2026

x.comadvisoryπŸ›‘οΈ Security

Dark Web Intelligence (@DailyDarkWeb) on X

Summary of SAP's October 13, 2026 Security Patch Day (16 new notes, 4 GitHub advisories). It leads with CVE-2026-89111, a CVSS 10.0 OAuth2 SSRF in SAP Cloud SDK for Python before 0.45.2, where an attacker-controlled tenant_subdomain redirects token requests and exfiltrates client credentials. It also lists three other critical flaws: broken access control in NetWeaver Visual Composer, code injection in S/4HANA substitution/validation rules, and a missing authorization check in the Manufacturing Integration and Intelligence (XMII) Configuration Service. It notes that none are in CISA KEV and SAP reports no in-the-wild exploitation.

SAP Cloud SDK for PythonSAP NetWeaverSAP S/4HANA+3
CVE-2026-89111CVE-2026-89110CVE-2026-89107+5

AppSec, Identity & AccessΒ· Added 15 Oct 2026, published 13 Oct 2026

rapid7.comadvisoryπŸ›‘οΈ Security

Ivanti Connect Secure zero-day exploited in the wild (CVE-2026-104935)

Rapid7 emergency-response analysis of CVE-2026-104935, a CVSS 8.6 authentication bypass by spoofing (CWE-290) in Ivanti Connect Secure that allows unauthenticated remote command execution. It was exploited as a zero-day against a limited number of customers, added to CISA KEV on disclosure day, and Volexity observed it chained with a still-unpatched privilege escalation flaw. Part of the fix shipped in 25.1.3.0 in July 2026, with backports to other supported versions pending. Rapid7 advises emergency patching outside normal cycles and hunting for compromise using Volexity's IOCs, since Ivanti has no reliable ones.

Ivanti Connect SecureVPNCVSS
CVE-2026-104935CWE-290CISA KEV+3

Threat Intel, Blue Team & DetectionΒ· Published and added 13 Oct 2026

watchtowr.comadvisoryπŸ›‘οΈ Security

Frequently Asked Questions About the Ivanti Connect Secure Authentication Bypass by Spoofing (CVE-2026-104935)

CVE-2026-104935 is an authentication bypass by spoofing in Ivanti Connect Secure. A remote attacker can forge identity signals and run arbitrary commands without credentials. CISA added it to the KEV catalog on 13 October 2026. The FAQ lists affected branches by ISA hardware (25.1.1.1, 25.1.2.2, 22.8.X), fixed versions (25.1.1.2, 25.1.3.0/25.1.3.1, 22.8R2.5), no workaround and no reliable IOCs.

Ivanti Connect SecureVPN
CVE-2026-104935CISA KEVCISA+1

Threat Intel, Blue Team & DetectionΒ· Added 30 Oct 2026, published 13 Oct 2026

watchtowr.comadvisoryπŸ›‘οΈ Security

Ivanti Connect Secure Authentication Bypass by Spoofing (CVE-2026-104935)

CVE-2026-104935 is an authentication bypass by spoofing in Ivanti Connect Secure (CVSS 3.1 score 8.6) that lets a remote attacker run commands without logging in. CISA added it to KEV on 13 October 2026. The 22.8.X bridge release and 25.1.2.2 and earlier are affected, with fixes in 22.8R2.5, 25.1.1.2, 25.1.3.0 and 25.1.3.1. Ivanti says no reliable indicators of compromise exist yet.

Ivanti Connect SecureVPN
CVE-2026-104935CISA KEVVolexity+2

AppSec, Threat IntelΒ· Added 30 Oct 2026, published 13 Oct 2026

cisa.govadvisoryπŸ›‘οΈ Security

CISA AA26-281A: Chinese Government-linked Actors Combine Automated and Hands-on Hacking Tools to Steal Data

Joint FBI/CISA/NSA and allied-agency advisory on China-linked actors enabled by Integrity Technology Group (overlapping with Flax Typhoon, Ethereal Panda, Red Juliett). It details their TTPs: open-source scanners and the MicroScan exploit-script app, an XSS credential-harvesting payload dropping live700_v1.exe, EBurst password spraying against Exchange/O365, SoftEther VPN persistence, DCSync via DC.exe, and email theft via the Curlc4.txt PHP bot and the office-cli utility. It also provides IOCs, MITRE ATT&CK mappings, CVEs, incident response steps, and mitigations.

SoftEtherMicrosoft 365Active Directory+3
Integrity Technology GroupFlax TyphoonEthereal Panda+13

Threat Intel, Blue Team & DetectionΒ· Added 9 Oct 2026

watchtowr.comadvisoryπŸ›‘οΈ Security

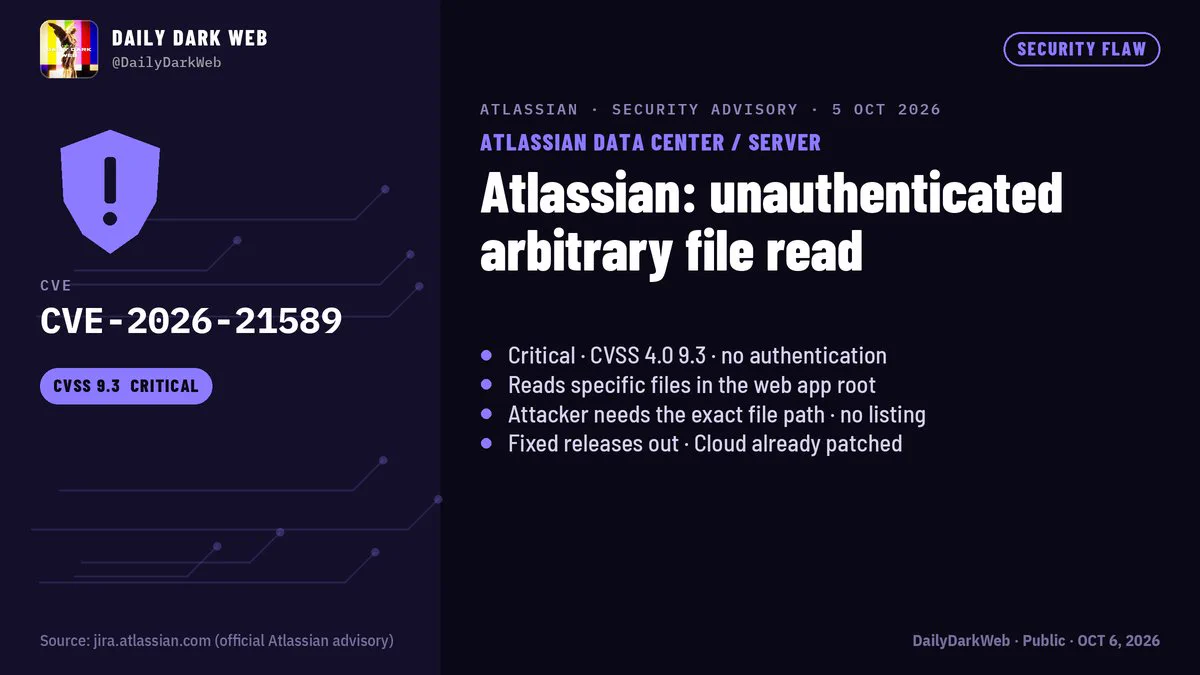
Atlassian Jira, Confluence (and more) Arbitrary File Read Vulnerability (CVE-2026-21589)

CVE-2026-21589 is an unauthenticated arbitrary file read (path traversal) in eight Atlassian Data Center and Server products: Bitbucket, Confluence, Jira, Jira Service Management, Bamboo, Crowd, Crucible and Fisheye. Atlassian fixed it on 5 October 2026, and CISA added it to the KEV catalog on 15 October 2026. The page lists patching, WAF regex, Tomcat RewriteValve and urlrewrite.xml mitigations, and a log check for ".." sequences after up to two rounds of URL decoding.

JiraConfluenceBitbucket+3
CVE-2026-21589CISA KEVpath traversal+3

AppSec, Blue Team & DetectionΒ· Added 30 Oct 2026, published 6 Oct 2026

x.comadvisoryπŸ›‘οΈ Security

Dark Web Intelligence (@DailyDarkWeb) on X

Atlassian disclosed CVE-2026-21589, a critical (CVSS 9.3) unauthenticated path traversal flaw allowing remote attackers to read specific files within the web application root across its self-managed Data Center/Server products β€” Jira Software, Jira Service Management, Confluence, Bitbucket, Bamboo, Crowd, Crucible, and Fisheye. Fixed versions are listed for each product (e.g. Jira 9.12.40/10.3.26/11.3.12, Confluence 9.2.26/10.2.19), and Atlassian Cloud is already patched; WAF/URL-rewrite mitigations are available for those who can't upgrade immediately. The post's analyst note clarifies exploitation requires knowing the exact target file path (no directory listing), and as of Oct 5, 2026 it is not yet in CISA KEV with no public exploit reported.

JiraConfluenceBitbucket+3
CVE-2026-21589path traversal

AppSecΒ· Added 7 Oct 2026, published 6 Oct 2026

orca.securityadvisoryπŸ›‘οΈ Security

Citrix NetScaler Zero-Day Exploited in the Wild Crashes SAML Authentication Services

Analysis of CVE-2026-88779 (CVSS v4.0 8.7), an unauthenticated memory-overflow flaw in the nsaaad SAML authentication handler on Citrix NetScaler ADC/Gateway that lets attackers crash the SAML service and lock out VPN/SSO access indefinitely through repeated triggering. Affects NetScaler 14.1 before 14.1-73.41 and 13.1 before 13.1-64.28 (plus FIPS/NDcPP builds); watchTowr Labs reproduced it via honeypot activity, Citrix confirmed targeted in-the-wild exploitation from IP 213.209.159.55, and CISA added it to KEV on 2026-10-04 with an Oct 7 federal remediation deadline. Some researchers suspect the overflow could extend to RCE beyond the documented DoS, though Citrix hasn't confirmed this.

Citrix NetScalerSAMLCVSS+1
CVE-2026-88779CWE-119watchTowr Labs+1

Identity & Access, Threat IntelΒ· Published and added 5 Oct 2026

cisa.govadvisoryπŸ›‘οΈ Security

CISA KEV: Fortinet FortiMail CVE-2026-104286 path traversal, actively exploited, no patch yet

CISA added CVE-2026-104286, a path traversal vulnerability in Fortinet FortiMail, to its Known Exploited Vulnerabilities Catalog on evidence of active exploitation. The alert restates the obligations of BOD 26-04 for Federal Civilian Executive Branch agencies: prioritise KEV CVEs on publicly exposed assets that give total control, and check for compromise before patching. It also describes the KEV nomination criteria: a CVE ID, evidence of exploitation and clear mitigation guidance. The page gives no technical detail, patch status or IOCs.

Fortinet FortiMailCISA KEV
CVE-2026-104286path traversalCISA+1

Threat Intel, GRCΒ· Added 4 Oct 2026

thehackernews.comadvisoryπŸ›‘οΈ Security

Critical FortiMail Zero-Day Flaw (CVE-2026-104286)

CISA added CVE-2026-104286 (CVSS 9.8), a path traversal and NULL-byte handling flaw in Fortinet FortiMail, to its Known Exploited Vulnerabilities catalog after confirming active in-the-wild exploitation. The bug lets unauthenticated attackers write arbitrary files via crafted HTTP/HTTPS requests, affecting FortiMail 7.2 through 8.0.1; Fortinet published workarounds (disabling IBE, restricting management-interface access) ahead of patches and shared attacker IPs and modified/added files as IOCs. The article also lists several other actively exploited vendor flaws disclosed the same week (Check Point, Arista VeloCloud, F5 BIG-IP APM, Cisco Catalyst SD-WAN Manager, Citrix NetScaler).

FortiMailCISA KEVCVSS
CVE-2026-104286CVE-2026-85102CVE-2026-93616+9

Threat Intel, AppSecΒ· Added 3 Oct 2026

rapid7.comadvisoryπŸ›‘οΈ Security

Critical Cisco Catalyst SD-WAN Manager API authentication bypass exploited in the wild (CVE-2026-76504)

Rapid7 analysis of CVE-2026-76504, a critical (CVSSv3.1 9.8) unauthenticated API authentication bypass in Cisco Catalyst SD-WAN Manager caused by improper URL-encoding handling (CWE-177), allowing attackers to gain admin-level API access via crafted requests to the j_security_check endpoint. The flaw is being actively exploited in the wild, was added to CISA's KEV list on October 1, 2026 with a remediation deadline of October 3, and follows two earlier 2026 Catalyst SD-WAN peering authentication bypasses (CVE-2026-20127 and Rapid7-discovered CVE-2026-20182). The post gives fixed-release guidance, no-workaround caveats, and log-based IOCs (encoded-character requests like %6a_security_check, viptela-reserved- usernames) for detecting compromise.

Cisco Catalyst SD-WAN ManagerCVSSCISA KEV
CVE-2026-76504CVE-2026-20127CVE-2026-20182+1

AppSec, Threat IntelΒ· Added 7 Oct 2026, published 30 Sep 2026

Showing 30 of 48

Show more