Skip to content

41 results for “certifi”

What you seeeverything
bleepingcomputer.comarticle🛡️ Security

Google disrupts million-device XCPE Android malware botnet, bans TV box maker

XCPE is an Android TV box botnet of more than 1.3 million devices, which Google's Threat Intelligence Group attributes with high confidence to manufacturer Videostrong Technology, who preinstalled a system-level backdoor in firmware. The backdoor (x.cpe, com.oemservice) used an MQTT broker for commands and loaded ad fraud and residential proxy modules. Google took down C2 servers tied to 10 million more devices and banned Videostrong from certified Android devices.

AndroidAndroid TVMQTT+2
XCPEVideostrong TechnologyGoogle Threat Intelligence Group+17

Threat Intel, Mobile Security, Hardware & RF· Published and added 2 Nov 2026

securityweek.comarticle🛡️ Security

How Secure Are US Elections? Voting Machine Risks and the Growing Threat of AI

SecurityWeek article examining US election security through a cybersecurity lens. It covers voting machines certified by the Election Assistance Commission but unpatched for up to two years, machines hacked at DEF CON's Voting Village, and QR-code ballots voters cannot verify. Sequent's Shai Bargil proposes open-source software and encrypted vote records. It also covers AI-enabled influence campaigns such as the 2024 Biden deepfake robocall.

Microsoft ElectionGuard
Election Assistance CommissionVoting VillageDEF CON+9

Threat Intel, AI Security· Published and added 29 Oct 2026

securityweek.comarticle🛡️ Security

TLS Flaws Found in GoAhead Web Server Used in Hundreds of Millions of Devices

FoxIO disclosed three TLS flaws in the GoAhead embedded web server from EmbedThis, used on hundreds of millions of IoT, OT and network devices. CVE-2026-115881 (CVSS 9.1) leaves revoked client certificates accepted under mTLS with OpenSSL; CVE-2026-115884 (7.4) bypasses chain-length limits with LibreSSL; a third Mbed TLS bug (5.9, no CVE) weakens TLS 1.2 DHE. GoAhead 6.1.1 fixes the OpenSSL and Mbed TLS issues, and FoxIO released PoC code and fingerprints.

GoAheadOpenSSLMbed TLS+2
CVE-2026-115881CVE-2026-115884FoxIO+4

Hardware & RF, AppSec· Published and added 28 Oct 2026
decrypt.coarticle🧠 AI

OpenAI Proves ETH Is False, and Crypto Twitter Has Questions

Decrypt reports that OpenAI published a 67-page paper (dated 17 October 2026, revised 25 October) claiming its AI found a deterministic subexponential-time algorithm for counting 3-SAT solutions, which would refute the Exponential Time Hypothesis. The proof was formalized in Lean. Impagliazzo, Paturi and Ryan Williams are reviewing it independently and say this is not certification. Anthropic posted a Claude-credited 3-SAT paper on 26 October.

LeanGitHubClaude
OpenAIAnthropicDecrypt+7

research, models· Published and added 27 Oct 2026

ethresear.charticle🛡️ Security

Inventory of PQ P2P Migrations in the Consensus Layer

Inventory of post-quantum migration work for Ethereum consensus-layer networking, by adust09 of Nyx Foundation. It maps three targets: Discovery v5/ENR signatures and key exchange, TLS 1.3 key agreement in QUIC, and libp2p TLS identity binding and CertificateVerify. It covers the 300-byte ENR and 1,280-byte packet limits, why hybrid KEMs do not authenticate peers, and downgrade and DoS concerns. It selects no algorithm or schedule.

Ethereumlibp2pQUIC+3
ML-KEMECDSAFIPS 203+8

other· Published and added 27 Oct 2026
socket.devarticle🛡️ Security

eMudhra, Brotli, and the Long Tail of a Security Fix

Socket post on why fixing the eMudhra weak-key intermediate CA incident (October 2026) and Brotli memory corruption CVE-2026-111497 takes more than updating Node.js. Bundled Brotli copies in Bun, Python Requests and .NET, Go binaries needing rebuilds, and per-program certificate stores all leave stale copies. It lists steps: track bundled components, keep a rebuild path, use workarounds, and verify the shipped artifact.

Node.jsBrotliBun+6

CVE-2026-111497eMudhraOneCRL+6

Supply Chain, AppSec· Published and added 26 Oct 2026

endorlabs.comarticle🛡️ Security

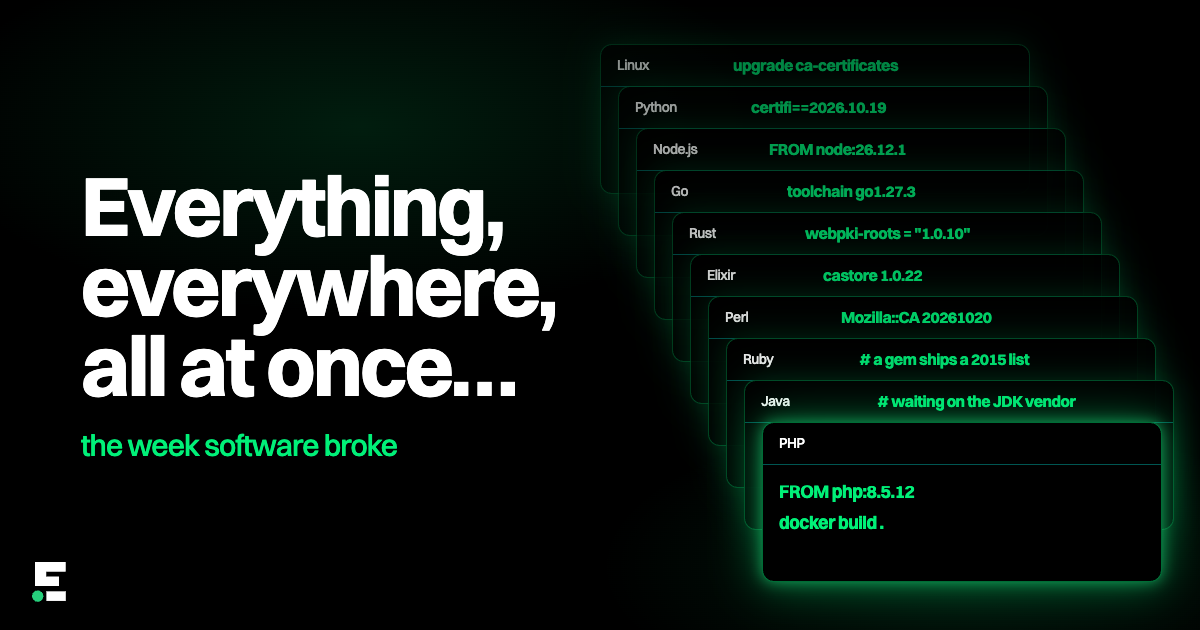
Everything, everywhere, all at once… the week software broke | Endor Labs

Endor Labs roundup of the 20 to 21 October 2026 patch wave: eMudhra certificate authority keys that anyone can recover, PHP2Shell (CVE-2026-109618, CVE-2026-109619), Node2Shell (CVE-2026-111497) and malware in LiteLLM 1.107.0. It lists fixed versions (PHP 8.2.35 to 8.5.12, Node.js 22.23.4, 24.22.1, 26.12.1, LiteLLM back to 1.106.2) and explains why many separate trust-store copies each need updating. It closes with advice on triage, remediation and SBOM/VEX reporting.

PHPNode.jsLiteLLM+3
CVE-2026-109618CVE-2026-109619CVE-2026-111497+3

Supply Chain, AppSec· Published and added 24 Oct 2026

stepsecurity.ioarticle🛡️ Security

eMudhra / emSign CA Compromise: What Python, pip, and CI/CD Users Need to Update

Guidance on the October 2026 eMudhra / emSign CA incident, where eight intermediate CA certificates had private keys generated with insufficient randomness. It explains why updating certifi alone does not fix pip's vendored bundle, and lists fixed versions (certifi 2026.10.19, pip 26.2.2, Python 3.15.1, 3.14.9, 3.13.17). StepSecurity's OpenSSL 4.0.3 tests showed the older bundle accepted seven emSign paths, while both corrected bundles rejected all fourteen.

pipPythoncertifi+3
eMudhraemSigncertificate authority compromise+3

Supply Chain, DevSecOps· Published and added 22 Oct 2026

blog.cloudflare.comarticle🛡️ Security

Localizing compliance at scale: achieving South Korea’s ISMS certification

Cloudflare's account of obtaining South Korea's ISMS-P certification after a ten-day KISA audit of 80 controls and a preparation period of about a year and a half. It explains that the certificate covers a service delivery boundary rather than a product list, that auditors required readable data flow diagrams, and how Korean sign-up uses itemized consent with social login removed.

CloudflareCloudflare Workers
ISMS-PKISAPersonal Information Protection Act+5

GRC· Added 29 Oct 2026, published 22 Oct 2026

aikido.devarticle🛡️ Security

eMudhra CA compromise: eight private keys, and one of them is 4

eMudhra's eight intermediate CA certificates, chaining to emSign ECC Root CA - G3, had private keys below 256 (one is 4), disclosed on 17 October 2026 by a researcher known as Wayne. Browsers and Microsoft blocked them via revocation pushes, but curl, git, containers, language runtimes and IoT may still trust them. The post gives patched ca-certificates versions, test commands and the timeline.

cURLDockermacOS+3
eMudhraemSign ECC Root CA - G3Wayne+6

Supply Chain, DevSecOps· Published and added 22 Oct 2026

endorlabs.comarticle🛡️ Security

eMudhra CA Compromise: The Trust Stores You Didn't Patch | Endor Labs

The eMudhra CA compromise (disclosed 20 October 2026) involves eight intermediate CA certificates whose private keys can be derived from the certificates themselves. They chain to AAA Certificate Services and three other roots. Browsers block them, but non-browser clients skip revocation and CT checks. Endor Labs finds 25 popular packages with frozen bundled root stores, 11 already patched, and gives a fingerprint-scanning script, test hosts and patch steps.

Endor LabsPythoncertifi+6
CVE-2026-111943eMudhraAAA Certificate Services+9

Supply Chain, AppSec, DevSecOps· Published and added 21 Oct 2026

aws.amazon.comarticle🛡️ Security

Best practices for integrating IAM Roles Anywhere with your PKI

Best practices for integrating AWS IAM Roles Anywhere with an external PKI so non-AWS workloads get temporary credentials via X.509 certificates. Covers trust anchor placement, certificate attributes (CN, issuer, SAN) in trust policy conditions, short-lived versus just-in-time certificates, and private key protection with PKCS #11, TPM 2.0 and OS certificate stores. Includes credential helper modes (serve, update), expiry monitoring, blue/green trust anchor rotation and a sample CloudFormation template.

AWS IAM Roles AnywhereAWS IAMAWS Private CA+3
X.509trust anchorPKCS #11+5

Identity & Access, Cloud & Infra· Published and added 21 Oct 2026

danielmangum.comarticle🛡️ Security

Your MCU likely escaped the eMudhra intermediate CA compromise

Analysis of the eMudhra intermediate CA compromise disclosed 20 October 2026, in which eight intermediate CA private keys were weak P-384 keys (top 376 bits zero, one key equal to 4) and publicly accessible. It explains web PKI chains and why browsers enforcing Certificate Transparency were not exposed. It argues MCU firmware that bundles only the single root it needs, as in Zephyr's HTTP GET sample, is likely safe unless it trusts an eMudhra or Sectigo cross-signing root.

ZephyrOpenSSLFirefox+1
eMudhraSectigoCertificate Transparency+6

Hardware & RF, other· Added 22 Oct 2026, published 21 Oct 2026

securityweek.comarticle🛡️ Security

Browsers Block eMudhra Intermediate CAs Over Recoverable Private Keys

Eight intermediate CA certificates issued by Indian CA eMudhra in April 2025 had private keys generated with weak entropy, effectively all zeroes except the last byte, so they could be recovered almost instantly with baby-step giant-step. Mozilla and Google blocked them on 17 October 2026, Apple on 19 October and Microsoft on 20 October. eMudhra blamed a key ceremony script flaw that created a second, weaker key pair.

ChromeFirefoxCloudflare
eMudhraDennis Jacksonbaby-step giant-step+5

other· Published and added 21 Oct 2026

coindesk.comarticle🛡️ Security

A company that vouches for websites had secret keys so weak that 8 of them were cracked

eMudhra, an Indian certificate authority with over 60 million issued certificates, had eight CA private keys that were tiny integers such as 4, 56 and 237. Researcher Scott Helme recovered all eight from public certificates in under a second, and the keys were exposed from April 2025. Mozilla, Chrome, Apple and Microsoft blocked them between 17 and 20 October 2026, but curl, Python, Node.js, Go and Java accepted a forged Stripe API certificate because they skip revocation checks.

cURLPythonNode.js+3
eMudhraSectigoScott Helme+5

other· Published and added 21 Oct 2026

simonwillison.netarticle🛡️ Security

eMudhra Intermediate CA Compromise

eMudhra Intermediate CA Compromise is a 20 October 2026 link-blog post reporting that private keys of eight eMudhra intermediate CA certificates were compromised. They chain to roots trusted by the Mozilla, Microsoft, Apple and Chrome programs. Software bundling trust lists needs updating: Linux distros must update ca-certificates, and uv 0.13.4, pip 26.2.2 and certifi 2026.10.19 ship new lists. The post does not describe how the keys were compromised.

Pythonpipuv+2
eMudhra

other· Added 21 Oct 2026, published 20 Oct 2026

securityweek.comarticle🛡️ Security

Novel Android RAT ‘Hirudo’ Replaces Banking Apps With Trojanized Copies

SecurityWeek covers ThreatFabric's findings on Hirudo, an Android banking trojan/RAT delivered via droppers hidden in fake shopping, adult video and short drama apps. It replaces eight Indonesian banking apps with modified copies containing a hooking engine that spoofs signing certificates and hides Accessibility services, screen capture and Play Integrity checks, while providing WebRTC screen viewing, camera access and SMS theft. ThreatFabric advises banks to enforce Play Integrity server-side, use behavioral analytics, treat Accessibility signals as risk inputs, and keep backend transaction-risk controls.

Android
HirudoThreatFabricPlay Integrity+2

Mobile Security, Threat Intel, Malware & RE· Published and added 15 Oct 2026

aws.amazon.comarticle🛡️ Security

Quantum-resistant signing on AWS, Part 2: Enforce your ML-DSA algorithm policy with SCPs and IAM

Explains how to turn a cryptographic algorithm policy (approve ML-DSA-65/87, exclude ML-DSA-44) into enforceable AWS controls using SCPs, IAM policies, permission boundaries and KMS key policies. The key lever is the kms:KeySpec condition key (kms:SigningAlgorithm can't distinguish variants, since all use ML_DSA_SHAKE_256), applied to CreateKey, ReplicateKey, Sign, Verify and GetPublicKey. It also covers surfaces without algorithm condition keys (AWS Private CA, ACM import, IAM server certificate upload, ELB TLS) via provisioning pipelines plus CloudTrail and AWS Config drift detection, and the default-allow risk of deny-lists.

AWSAWS KMSAWS IAM+3
ML-DSAFIPS 204NIST+2

Cloud & Infra, GRC· Published and added 12 Oct 2026

securityweek.comarticle🛡️ Security

Let’s Encrypt Cuts Default Certificate Validity to 64 Days Ahead of 45-Day Switch

Let's Encrypt will issue 64-day certificates by default from February 10, 2027, as a step toward 45-day lifetimes planned for 2028, in line with CA/Browser Forum Baseline Requirements. The last 90-day certificate is expected to expire May 11, 2027, and 64-day certificates are available in staging for testing. Automated clients that support ACME Renewal Info (ARI) need no change. Hardcoded renewal schedules should renew at about two-thirds of the lifetime. Authorization reuse drops to 10 days next year and 7 hours in 2028, which removes the need for CAA rechecking.

Let's EncryptACME
CA/Browser Forum Baseline RequirementsACME Renewal InfoCAA rechecking+1

other, GRC· Published and added 12 Oct 2026

securityweek.comarticle🛡️ Security

Google Domains Impacted by Recent ccTLD Hijacks

Google disclosed that attackers hijacked the authoritative DNS of three ccTLDs (.gh for Ghana, .sl for Sierra Leone, .as for American Samoa) and used control of those domains to obtain unauthorized HTTPS certificates covering several Google domains and domains of other organizations. Google blocked the fraudulent certificates in Chrome, worked with issuing CAs to revoke them, and used Certificate Transparency log analysis to find other affected brands, some of which it proactively notified. Google is urging domain owners to monitor CT logs and publish restrictive CAA records after regaining DNS control, since CAs may cache and reuse prior domain-control-validation checks, letting attackers mint new certs even after the hijack ends.

Chrome
.gh ccTLD.sl ccTLD.as ccTLD+3

Threat Intel· Published and added 9 Oct 2026

microsoft.comarticle🛡️ Security

Post-quantum authentication: Why organizations should start testing certificate ecosystems now

Microsoft Security Blog post arguing that post-quantum cryptography planning must extend beyond encrypted-data confidentiality to authentication and certificate ecosystems, since larger PQC certificate chains and new algorithms like ML-DSA-87 can break PKI workflows, HSMs, and legacy infrastructure. It details Microsoft's PQC TLS Pilot Program, launched August 27, 2026, which lets approved certificate authorities (ComSign, DigiCert, HARICA, IdenTrust, Sectigo, Shanghai Electronic Certification Authority, SSL.com) test ML-DSA-87 certificate issuance under the Microsoft Trusted Root Program, plus Windows 11 builds (KB5101681, KB5101684) that support evaluating ML-DSA certificates via Schannel in non-production environments. It lays out a six-step readiness plan: inventory certificate dependencies, map trust relationships, assess vendor roadmaps, identify long-lived infrastructure, build test environments, and plan a multi-year migration.

WindowsSchannelTLS
ML-DSAML-DSA-87PQC TLS Pilot Program+8

Identity & Access, GRC· Published and added 8 Oct 2026

unchained.comarticle🛡️ Security

The randomness question at the heart of your hardware wallet

Unchained explains how hardware wallets generate entropy for bitcoin keys, covering PRNG vs TRNG theory, physical TRNG mechanisms (ring oscillator jitter, diode avalanche noise, radio static reuse), and NIST SP 800-90B / BSI AIS-31 certification. It compares entropy sourcing and secure-element chip suppliers (STMicroelectronics, Microchip, Infineon, Espressif, Silicon Labs) across Trezor, Ledger, Coldcard, BitBox02, Foundation Passport, Blockstream Jade and Block Bitkey, and walks through the July 2026 Coldcard firmware bug that silently bypassed its hardware TRNG for five years, causing real bitcoin losses. It also covers manual dice/coin entropy generation for BIP39 seed phrases, the Dark Skippy nonce-leakage attack, and multisig as the primary mitigation against single-device key-generation failures.

BitcoinColdcardTrezor+3
Coldcard firmware vulnerability (2026)Dark SkippyMilk Sad+6

Hardware & RF, Blockchain· Added 8 Oct 2026, published 7 Oct 2026

aws.amazon.comarticle🛡️ Security

Improving SPIRE security and resiliency with AWS managed services

AWS Security Blog walkthrough on hardening SPIRE (the SPIFFE Runtime Environment) in production by replacing its default self-managed components with AWS managed services: AWS KMS for SVID signing keys, Amazon Aurora PostgreSQL as the datastore, AWS Private CA as the upstream certificate authority, Amazon S3/CloudFront for trust bundle distribution, AWS Secrets Manager for delivering SVIDs to serverless/container workloads, and Amazon Verified Permissions (Cedar policies) for fine-grained SPIFFE-ID-based authorization. It addresses operational concerns like key custody, datastore resiliency, PKI integration, and offline identity validation, and links to a GitHub reference deployment and a SPIFFE/SPIRE-on-AWS workshop.

AWSKubernetesPostgreSQL+2

Cloud & Infra, Identity & Access· Added 7 Oct 2026, published 6 Oct 2026

blog.googlearticle🛡️ Security

Chrome's Response to Recent ccTLD Registry Hijacks

Google describes a series of registry-level hijacks affecting the .gh (Ghana), .sl (Sierra Leone), and .as (American Samoa) ccTLDs, in which attackers modified authoritative DNS records to obtain unauthorized HTTPS certificates for Google domains and, via Certificate Transparency monitoring, several other major organizations. Chrome mitigated impact by blocking the fraudulent certificates through CRLSets and coordinating revocation with issuing CAs, then urges domain owners to continuously monitor CT logs and publish restrictive CAA records with ACME account bindings, since cached domain-control-validation state can let attackers mint new certs even after DNS control is restored.

Chrome

Threat Intel, Blue Team & Detection· Added 7 Oct 2026, published 6 Oct 2026

nextgov.comarticle🧠 AI

Tech bills of the week: Creating an AI-focused agency, reviewing AI-assisted cyber attacks and more

A weekly congressional tracker detailing multiple new AI bills: a Casar/Sanders proposal to create a Department of Artificial Intelligence and pause advanced AI development pending a ban on artificial superintelligence; Markey's Cybersecurity and AI Board of Investigations modeled on the NTSB to probe AI-driven cyberattacks (citing an OpenAI system breaching Hugging Face and an Australian health database); Bennet/Welch's Federal Digital Commission expansion for frontier model pre-certification and civil penalties; AI 'kill switch' mandates from Kean and Kennedy; Kelly's AI Horizon Fund taxing tech profits to fund worker transition programs; a bipartisan FTC transparency bill from Coons, Britt, Schatz and Lankford; Bonamici's education/workforce AI framework; and two Barrett bills on VA AI transparency and human review of AI-assisted disability claims.

OpenAIHugging FaceSen. Ed Markey+16

ai-policy· Added 26 Sep 2026, published 25 Sep 2026

aws.amazon.comarticle🛡️ Security

Architecting a secure landing zone in the AWS European Sovereign Cloud

AWS Security Blog walkthrough of building a secure, production-ready landing zone in the new AWS European Sovereign Cloud (aws-eusc partition), covering multi-account governance via AWS Control Tower/AFT, IAM Identity Center federation as Terraform code, centralized logging into a Log Archive and Security Tooling account, network perimeter design with dedicated Direct Connect PoPs and VPC endpoints, KMS/External Key Store data protection, and partition-aware CI/CD for pushing container images, AMIs, and artifacts across the partition boundary. It maps design decisions to the AWS Security Reference Architecture and Well-Architected Framework, distinguishes hard partition boundaries from configurable choices, and references BSI C5:2020, SOC 2, and ISO 27001/27017/27018/27701 certifications for EUSC.

AWSAWS European Sovereign CloudAWS IAM+3
BSI C5:2020SOC 2ISO 27001+3

Cloud & Infra, GRC, Identity & Access· Added 7 Oct 2026, published 16 Sep 2026

ethresear.charticle🛡️ Security

Post-Quantum: Lattice or Hash-Based (one question, two right answers)

A deep-dive field guide to choosing between lattice-based (ML-DSA/FN-DSA) and hash-based (SLH-DSA) post-quantum signatures, built from interviews with the designers and implementers behind both NIST standards and their deployments. It walks through Mosca's-inequality-style migration timing, CNSA 2.0's split between lattice signatures and stateful hash-based LMS/XMSS for firmware, the stateful-signature "footgun," and why the broader internet (TLS/WebPKI, via Merkle Tree Certificates) is converging on lattices while Ethereum's post-quantum consensus roadmap (leanXMSS, EIP-8292, EIP-8288 aggregation) and Algorand's live Falcon-1024 state proofs lean hash-based or scheme-neutral because of aggregation and on-chain storage constraints. It closes with a decision framework and a rundown of NIST's round-3 "onramp" signature candidates (MAYO, SQIsign, HAWK, etc.).

EthereumBitcoinAlgorand+3
ML-DSASLH-DSAFN-DSA+16

Blockchain, other· Added 3 Oct 2026, published 15 Sep 2026

huntress.comarticle🛡️ Security

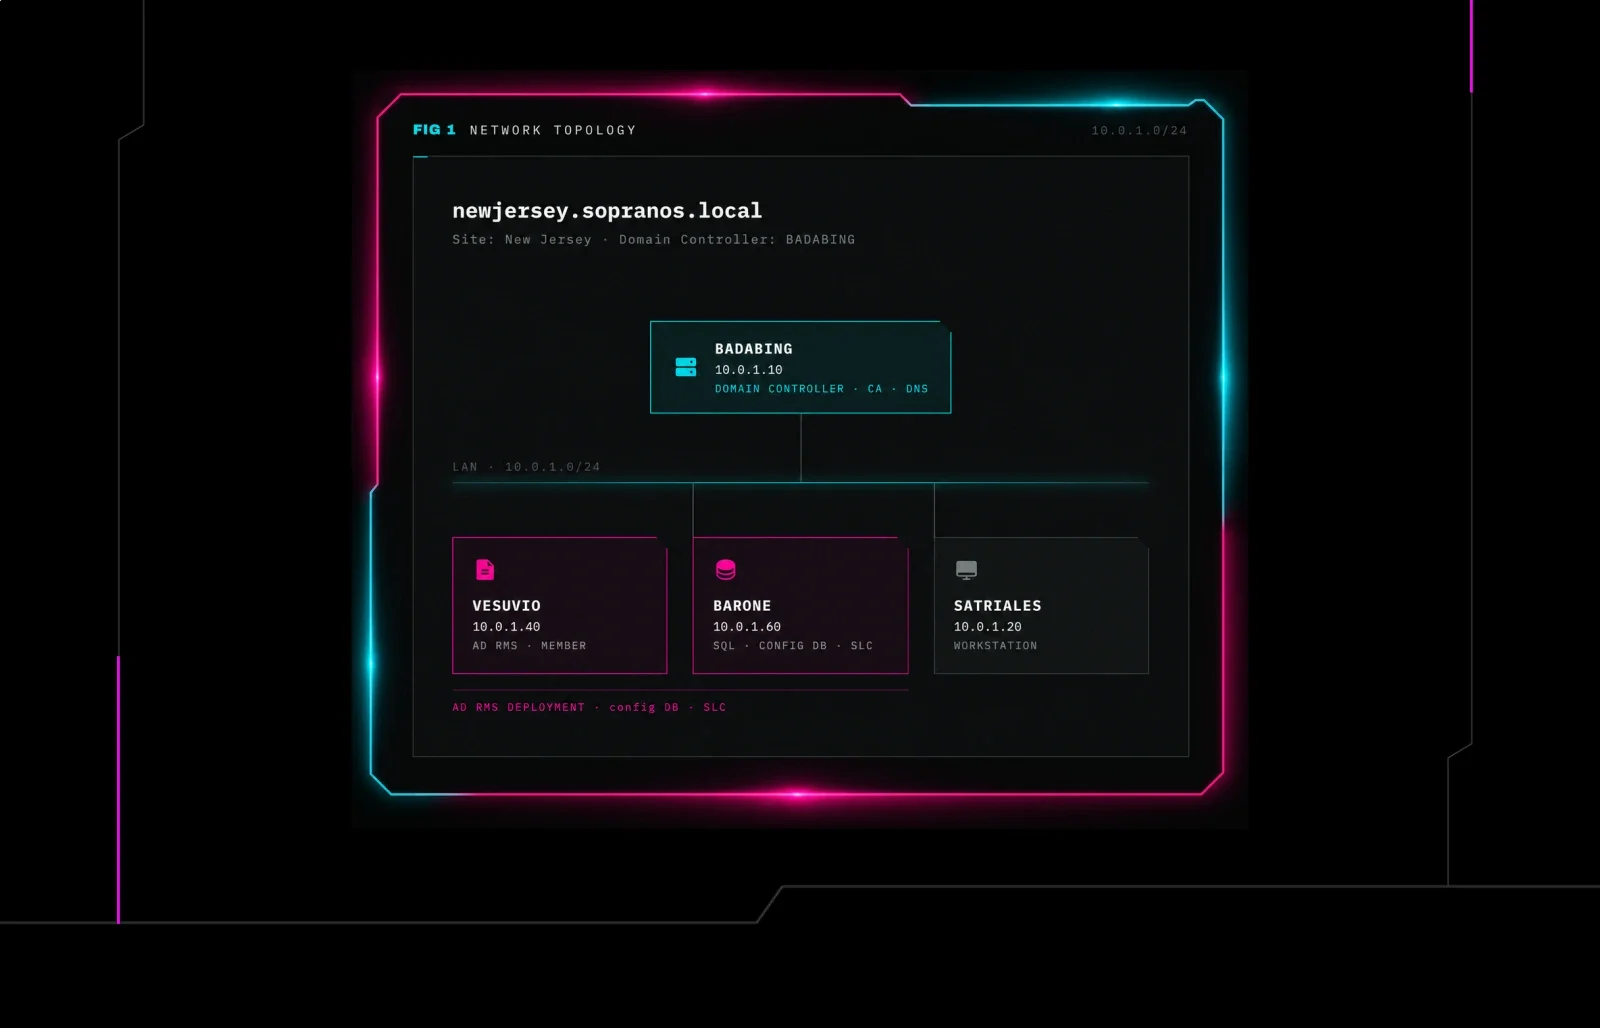
AD Rights Management Service (Part 1): Architecture, Deprecation, and Reconnaissance

Part 1 of a Huntress research series on Active Directory Rights Management Services (AD RMS), explaining its PKI-based trust model (Server Licensor Certificate signing content keys), why it's still deployed despite Microsoft's deprecation push toward Azure Information Protection, and how to fingerprint and enumerate a cluster from an unprivileged domain account. It introduces SharpRMS, a custom C# tool that speaks the AD RMS SOAP protocol to enumerate clusters and rights-policy templates, and shows how local AD RMS Service Group membership (not Domain Admin) gates the administrative surface where the SLC private key can eventually be reached — setting up Part 2's key extraction and offline decryption.

Active DirectoryWindows.NET+1
DisARMSMSRC Case 33210Sean Metcalf+1

Offensive Security, Identity & Access· Published and added 8 Sep 2026

huntress.comarticle🛡️ Security

CMMC Hit Pause, the FAR Council Hit Play

Huntress blog post clarifying that DoD's July 13 "strategic pause" only suspended CMMC Phase 2 third-party certification requirements (for solicitations after Nov 2026), while Phase 1 self-assessments, SPRS scoring, and DFARS 252.204-7012's 72-hour CUI incident reporting remain fully in force and now face closer DIBCAC/DOJ False Claims Act scrutiny. It also flags the FAR Council's June 23 proposed CUI rule (part of the Revolutionary FAR Overhaul), which would extend 72-hour breach reporting and a NIST 800-171 Rev 3 baseline to all FAR-based federal contractors, not just the defense industrial base, creating a temporary split between CMMC's Rev 2 and the FAR's Rev 3. It closes with a breakdown of 32 CFR 170.21's strict POA&M limits (no POA&M at Level 1, minimum 88/110 score and only 1-point requirements eligible at Level 2) and practical questions MSPs should ask clients about federal contract exposure.

Huntress
CMMCDFARS 252.204-7012DFARS 252.204-7021+12

GRC· Added 8 Sep 2026, published 2 Sep 2026

fossa.comarticle🛡️ Security

FOSSA: CRA Product Classification Explained

FOSSA blog post breaking down how the EU Cyber Resilience Act (Regulation 2024/2847) classifies products with digital elements into four risk tiers — Default, Important Class I, Important Class II, and Critical — each with different conformity assessment paths (self-assessment vs. notified-body third-party assessment vs. European cybersecurity certification). It enumerates the specific product categories named in Annex III (e.g. password managers, VPNs, routers, operating systems, SIEM, browsers) and Annex IV (secure cryptoprocessing hardware, smart meter gateways, smartcards), explains scope exclusions (pure SaaS under NIS2, medical devices, defense products, non-commercial OSS), and gives a four-question decision process for classifying a product ahead of the December 2027 full-compliance deadline.

FOSSA
EU Cyber Resilience ActNIS2Regulation (EU) 2024/2847

GRC· Published and added 18 Aug 2026

Showing 30 of 41

Show more