- lee1981 (@lee1981b) on X
CVE-2026-103780 is a stack-based buffer overflow (CWE-121) in Dell PowerProtect Data Domain / DD OS. An unauthenticated remote attacker could get command execution (CVSS 3.1 9.8, Dell DSA-2026-416). The post lists affected and fixed builds for four release trains (Feature Release, LTS2024, LTS2025, LTS2026). It adds KEV, EPSS and SSVC status, plus six defensive checks. The vulnerable service is not public.
 x.comadvisoryAdded 31 Oct 2026, published 29 Oct 2026🛡️ Security
- lee1981 (@lee1981b) on X
CVE-2026-92885 is a critical (CVSS 3.1 9.8, CWE-287) authentication bypass in the Qode Membership WordPress plugin, versions through 2.0.6.2. A misspelled variable in the Facebook token-verification guard skips provider checks, so an unauthenticated attacker with a public nonce can get a session cookie for an existing account, including an administrator. The post gives the fix (2.0.6.3, bundled in Bridge 30.9), KEV/EPSS/SSVC status, and a SOC log-correlation and remediation plan.
x.comadvisoryAdded 31 Oct 2026, published 28 Oct 2026🛡️ Security - lee1981 (@lee1981b) on X
CVE-2026-115905 is a ZIP cloaking flaw in the Rust zip crate (zip-rs/zip2), rated CVSS v4.0 10.0 and affecting versions below 9.0.5. ZipArchive reads central-directory metadata while ZipStreamReader reads local headers, so a crafted archive can pass filename inspection and then overwrite a different file during streaming extraction. Version 9.0.5 adds consistency checks, but ZipStreamReader::new leaves them off by default, and extraction is not atomic, so files can be written before an error is raised. The post covers CWE-20 and CWE-436, KEV and EPSS status, Debian status and a six-step investigation trail.
x.comadvisoryAdded 29 Oct 2026, published 27 Oct 2026🛡️ Security - Mitsubishi Electric and Mitsubishi Electric Iconics Digital Solutions GENESIS, GENESIS64, ICONICS Suite, Hyper Historian, AnalytiX, MobileHMI, IoTWorX, MC Works64, GENESIS32 and BizViz
CISA advisory ICSA-26-300-02 covers four vulnerabilities in Mitsubishi Electric and Mitsubishi Electric Iconics Digital Solutions GENESIS64, ICONICS Suite, Hyper Historian, AnalytiX, MobileHMI, IoTWorX, MC Works64, GENESIS32 and BizViz. CVE-2023-4863 (CWE-787 out-of-bounds write) allows code execution; CVE-2026-16436 and CVE-2026-16437 allow authentication bypass; CVE-2026-16438 allows arbitrary operations. Fixes are 10.97.3, 10.98 and GENESIS 11.04. MC Works64, GENESIS32 and BizViz are affected in all versions, and MC Works64 has no fix planned. Mitigations include removing the ClientChallengeTable.dat or SecurityChallenges.dat file contents. The fetched text was truncated, so later content is not covered.
 cisa.govadvisoryAdded 29 Oct 2026, published 26 Oct 2026🛡️ Security
- lee1981 (@lee1981b) on X
CVE-2026-111497 is an out-of-bounds write in the Brotli decoder bundled with Node.js (CWE-787, CWE-252), rated CVSS v4.0 9.2 by the Google CNA and High by the Node.js project. Fixes are Node 22.23.4, 24.22.1 and 26.12.1, and 24.22.1 still labels Brotli 1.2.0 because the fix was cherry-picked. The post gives a SOC trail from input to worker, with remediation and verification steps. It notes no KEV match, CISA SSVC exploitation none, and only unverified public lab claims.
x.comadvisoryAdded 26 Oct 2026, published 23 Oct 2026🛡️ Security 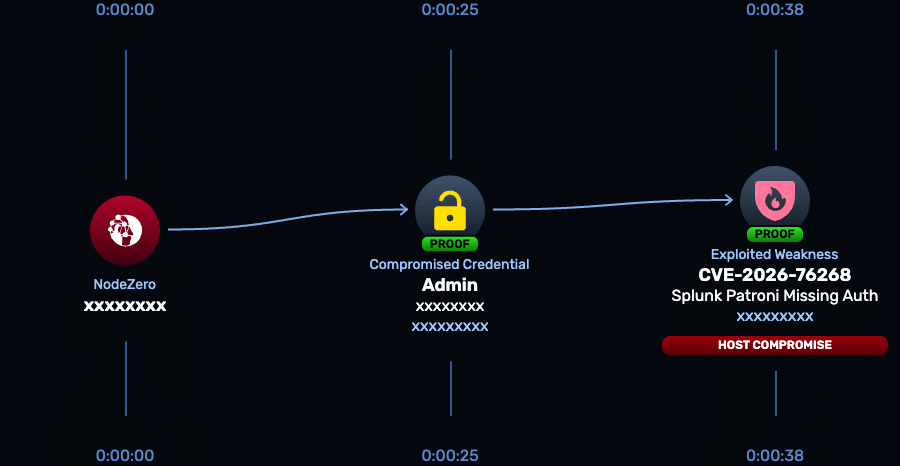 CVE-2026-76268 | Splunk Enterprise Patroni REST API Missing Authentication Vulnerability
CVE-2026-76268 is a critical (CVSS 9.8) missing authentication flaw (CWE-306) in the Patroni REST API on Splunk Enterprise search head cluster members. An unauthenticated attacker with network access can run operating-system commands. Affected: 10.4.0 to 10.4.2 and 10.2.0 to 10.2.6. Fixed in 10.4.3 and 10.2.7. Splunk (SVD-2026-1001, 7 October 2026) suggests disabling the PostgreSQL sidecar as a workaround.
 horizon3.aiadvisoryAdded 29 Oct 2026, published 22 Oct 2026🛡️ Security
- lee1981 (@lee1981b) on X
CVE-2026-106931 is an OS command injection (CWE-78) in the statistics processing of EG Secure Solutions SiteGuard Server Edition, a host-based WAF. It can give root or SYSTEM command execution. The vendor and JVN confirm exploitation on 14 October 2026. The post lists fixed builds (Ver8.00 Update 5, Ver7.00 Update 6 on FreeBSD), the IIS exclusion, the workaround of disabling statistics, and a SOC trail starting with diagnostic preservation before patching.
x.comadvisoryAdded 21 Oct 2026, published 19 Oct 2026🛡️ Security - lee1981 (@lee1981b) on X
Daily CVE digest on CVE-2026-76519, a CVSS 9.8 relative path traversal (CWE-23) in Cisco Secure Email Gateway's AMP File Reputation attachment processing. A crafted attachment gives unauthenticated arbitrary file writes and root command execution, and Cisco PSIRT reports active exploitation. The CVE is in CISA KEV. It lists the applicability conditions (File Reputation assigned to a policy and Content Scanner Tools earlier than 25.3.0.5525) and the fixes (scanner 25.3.0.5525, AsyncOS 15.5.5-014 and 16.5.0-780). It also covers evidence preservation, reading Cisco's System Security scan outcomes, mail/AMP log correlation, and deployment-specific recovery including cluster-key exposure.
x.comadvisoryAdded 18 Oct 2026, published 15 Oct 2026🛡️ Security  Critical GitLab RCE Lets Unauthenticated Attackers Execute Code on Servers (CVE-2026-97229)
Orca Security analysis of CVE-2026-97229, a CVSS 10.0 flaw in GitLab CE/EE. An integer overflow (CWE-190) in the CI/CD regular expression compiler gives memory corruption and code execution as the git user. It is triggered by a crafted regex in .gitlab-ci.yml combined with a UTF-8 repository path, with no authentication needed on instances that allow public project creation or self-registration. Lists affected branches (19.2 before 19.2.8, 19.3 before 19.3.5, 19.4 before 19.4.2), the absence of a workaround, interim mitigations, and a Rapid7 PoC against GitLab CE 19.4.1 with ASLR on. Notes a prior max-severity GitLab bug (CVE-2026-85706) was probed in the wild within hours and later added to CISA KEV.
 orca.securityadvisoryPublished and added 14 Oct 2026🛡️ Security
 Microsoft Patch Tuesday for October 2026 — Snort rules and prominent vulnerabilities
Talos summarises Microsoft's October 2026 Patch Tuesday, which covers 1415 vulnerabilities, 85 of them critical (67 RCE). One bug is exploited in the wild: CVE-2026-96951, a Windows Shell security feature bypass. The post groups the CVEs by Microsoft's exploitability rating (more likely, less likely, unlikely) with CVSS and CWE for each, covering Windows, Office, Exchange, Hyper-V, DHCP, QUIC, Outlook and Azure. It also lists the Snort 2 and Snort 3 rule ID ranges that detect exploitation attempts.
 blog.talosintelligence.comadvisoryPublished and added 13 Oct 2026🛡️ Security
 Ivanti Connect Secure zero-day exploited in the wild (CVE-2026-104935)
Rapid7 emergency-response analysis of CVE-2026-104935, a CVSS 8.6 authentication bypass by spoofing (CWE-290) in Ivanti Connect Secure that allows unauthenticated remote command execution. It was exploited as a zero-day against a limited number of customers, added to CISA KEV on disclosure day, and Volexity observed it chained with a still-unpatched privilege escalation flaw. Part of the fix shipped in 25.1.3.0 in July 2026, with backports to other supported versions pending. Rapid7 advises emergency patching outside normal cycles and hunting for compromise using Volexity's IOCs, since Ivanti has no reliable ones.
 rapid7.comadvisoryPublished and added 13 Oct 2026🛡️ Security
- CVE-2026-97229: Critical Unauthenticated Remote Code Execution in GitLab
Rapid7 analysis of CVE-2026-97229, a CVSS 10.0 integer overflow (CWE-190) in the Onigmo regex compiler used by GitLab CE/EE's CI/CD regex handling. A crafted regex in a .gitlab-ci.yml passes validation as US-ASCII, then is recompiled for a UTF-8 repository path, producing invalid instructions that give code execution as the git user. Rapid7 reproduced it on GitLab CE 19.4.1 with ASLR (patched in 19.4.2); despite the vendor's "unauthenticated" rating, the attacker needs to commit a malicious config to a public project, which self-registration allows. No in-the-wild exploitation is confirmed, and Rapid7 recommends urgent upgrades.
rapid7.comadvisoryPublished and added 13 Oct 2026🛡️ Security - lee1981 (@lee1981b) on X
CyberForge "CVE of the Day #076" covers CVE-2026-97229, a CVSS 10.0 integer overflow (CWE-190) in GitLab CE/EE's CI/CD regular expression compiler. It can lead to conditional unauthenticated code execution on the GitLab server. It lists the affected trains (19.2 before 19.2.8, 19.3 before 19.3.5, 19.4 before 19.4.2) and the 19.3.4 vs 19.3.5 Ona-regression discrepancy. It also gives six SOC checks: scoping, log preservation (Workhorse/Rails/Sidekiq, correlation_id), server-effect hunting, request-to-process correlation, upgrade and running-state verification. It notes that exploit details are unverified, no KEV listing exists and EPSS data is unavailable.
x.comadvisoryAdded 15 Oct 2026, published 13 Oct 2026🛡️ Security - lee1981 (@lee1981b) on X
CyberForge's CVE of the Day #075 covers CVE-2026-108860, a critical (CVSS 9.1 v3.1 / 9.3 v4.0) authentication bypass in SciSharp BotSharp through 5.2.0. WebStarter ships a published default HMAC JWT signing secret (CWE-321), so anyone holding it can forge bearer tokens that impersonate known users, including administrators. The post sets out how to confirm the effective key and serving build, a six-step SOC investigation trail, and remediation by rotating the secret. No verified fixed release, KEV entry or EPSS data existed at cutoff, and the linked research is static-only.
x.comadvisoryAdded 13 Oct 2026, published 12 Oct 2026🛡️ Security - lee1981 (@lee1981b) on X
CyberForge CVE of the Day #074 analyses CVE-2026-85097, a CVSS 9.8 unauthenticated file upload to PHP execution flaw (CWE-434) in the Bricksforge WordPress plugin through 3.1.8.9. Wordfence names 3.1.8.10 as the fix, and a separate vendor 4.0.1 Pro Forms upload-security notice has no verified mapping to the CVE. It gives a defender workflow: scope versions, preserve edge/origin logs, inspect resulting files and PHP-FPM handling, and verify the patched version is serving. It also separates KEV (no match), EPSS (0.312%) and SSVC (exploitation none) from compromise evidence.
x.comadvisoryAdded 11 Oct 2026, published 10 Oct 2026🛡️ Security - lee1981 (@lee1981b) on X
CyberForge's CVE of the Day #073 covers CVE-2026-102255, a critical (CVSS 10.0) pre-authentication SSRF / confused-deputy flaw (CWE-918, CWE-441) in the SonicWall SMA1000 Work Place interface, per advisory SNWLID-2026-0017. It lists affected platform hotfixes (12.4.3-03526 and older, 12.5.0-02952 and older), fixed floors (12.4.3-03670, 12.5.0-03082), no workaround, and the exploitation picture (no known exploitation, not in KEV, EPSS 0.477%, SSVC automatable). It gives a six-step SOC playbook covering appliance scoping, AMC log preservation, hunting appliance-originated internal requests, correlating receiving-service changes, patching, and verifying every node, and it separates exposure, a lead, confirmed compromise and telemetry gaps.
x.comadvisoryAdded 12 Oct 2026, published 9 Oct 2026🛡️ Security - lee1981 (@lee1981b) on X
Analysis of CVE-2026-105844, a CWE-1321 prototype-pollution vulnerability in @payloadcms/plugin-import-export that the vendor says can lead to unauthenticated remote code execution. It covers affected ranges (stable 3.0.0–3.87.x, canary 4.0.0-canary.0–canary.26), the fix (3.88.0 / 4.0.0-canary.27), the patched field-path guard against __proto__/constructor/prototype segments, and a six-step SOC hunting/triage playbook with two offline Python scripts for inspecting npm package trees and triaging request field-paths for prototype-sensitive values.
x.comadvisoryAdded 8 Oct 2026, published 7 Oct 2026🛡️ Security  GitLab patches critical 9.9 AI Gateway template-sandbox-escape RCE (CVE-2026-90970)
GitLab patched CVE-2026-90970, a critical (CVSS 9.9) flaw in the AI Gateway used by Duo Agent Platform, where a logged-in user with Duo Agent Platform access could craft a flow configuration to escape the prompt template sandbox and achieve arbitrary command execution on the gateway. Only self-managed organizations hosting their own AI Gateway (versions 18.1.6 through 19.1) need to act; the fix lands in 19.2.4, 19.3.2, and 19.4.1. The bug is a template engine weakness (CWE-1336), the same class as the earlier CVE-2026-1868 gateway RCE GitLab fixed in February, and was reported via HackerOne by researcher invisiblemeerkat.
 thehackernews.comadvisoryAdded 4 Oct 2026🛡️ Security
- Critical Cisco Catalyst SD-WAN Manager API authentication bypass exploited in the wild (CVE-2026-76504)
Rapid7 analysis of CVE-2026-76504, a critical (CVSSv3.1 9.8) unauthenticated API authentication bypass in Cisco Catalyst SD-WAN Manager caused by improper URL-encoding handling (CWE-177), allowing attackers to gain admin-level API access via crafted requests to the j_security_check endpoint. The flaw is being actively exploited in the wild, was added to CISA's KEV list on October 1, 2026 with a remediation deadline of October 3, and follows two earlier 2026 Catalyst SD-WAN peering authentication bypasses (CVE-2026-20127 and Rapid7-discovered CVE-2026-20182). The post gives fixed-release guidance, no-workaround caveats, and log-based IOCs (encoded-character requests like %6a_security_check, viptela-reserved- usernames) for detecting compromise.
rapid7.comadvisoryAdded 7 Oct 2026, published 30 Sep 2026🛡️ Security - CVE-2026-90617 in PentestAgent
VulDB entry for CVE-2026-90617, a remote OS command injection (CWE-78) in GH05TCREW PentestAgent. The flaw is in run_task in interface/main.py of the MCP HTTP Server, affects everything up to commit cf882dab, and has a public exploit. The product uses rolling releases, so no version ranges exist, and the fix is an unmerged pull request. The analysis suggests compensating controls: restrict network access to the MCP server, run with least privilege, and validate input upstream.
 vuldb.comadvisoryAdded 26 Sep 2026🛡️ Security
- CVE-2026-85787 in postgres-mcp-server
CVE-2026-85787 affects awslabs postgres-mcp-server before 1.1.7. The SQL validation component uses an incomplete list of disallowed inputs. Crafted SQL placed in content submitted while an authenticated user interacts with the MCP server can bypass the read-only restriction and modify data in PostgreSQL. The fix is to upgrade to 1.1.7 or later. VulDB's added analysis is generic: it points to SQL injection (CWE-89) and recommends least-privilege database accounts and parameterized queries.
vuldb.comadvisoryAdded 26 Sep 2026🛡️ Security - CVE-2026-85661 in excel-mcp-server
CVE-2026-85661 affects excel-mcp-server 0.1.8. In stdio mode with EXCEL_FILES_PATH unset, the server does not confine file paths, so a client can pass relative or absolute paths to the read and write tools. That gives arbitrary file read and write with the privileges of the server process. The page classifies it as CWE-22 (ATT&CK T1083) and recommends canonical path checks against a base directory, making EXCEL_FILES_PATH mandatory, and running with least privilege.
vuldb.comadvisoryAdded 26 Sep 2026🛡️ Security - CVE-2026-65695: Office-Word-MCP-Server through 1
CVE-2026-65695 is a path traversal vulnerability (CWE-22, CVSS 4.0 7.6 HIGH) in Office-Word-MCP-Server through version 1.1.11, an MCP server that exposes Word document manipulation tools to LLM agents. Attackers who can influence the filename argument can supply absolute paths or ../ sequences to document open/save operations, bypassing the check_file_writeable and ensure_docx_extension helpers (which do no base-directory confinement or realpath validation) to read or overwrite arbitrary .docx files outside the intended working directory.
 nvd.nist.govadvisoryAdded 26 Sep 2026🛡️ Security
- CVE-2026-57860: ForgeCode (tailcallhq/forgecode), an AI pair-programming CLI, automatically loads and executes the MCP servers defined i
CVE-2026-57860 describes an arbitrary code execution flaw in ForgeCode (tailcallhq/forgecode), an AI pair-programming CLI that automatically loads and executes MCP servers defined in a repository's .mcp.json on startup without user confirmation. A malicious repo can define mcpServers entries with arbitrary command/args (e.g. bash -c) that spawn under the invoking user's privileges the moment forge is run inside the cloned repo, giving attackers a reliable initial-access and persistence primitive against developers evaluating untrusted code. CVSS 4.0 8.4 HIGH, CWE-829 (inclusion of functionality from untrusted control sphere); a fix commit and VulnCheck advisory are linked.
nvd.nist.govadvisoryAdded 26 Sep 2026🛡️ Security - CVE-2026-49291: mcp-memory-service is a semantic memory layer for AI applications
CVE-2026-49291 affects mcp-memory-service prior to version 10.65.3: its HTTP MCP JSON-RPC endpoint at /mcp only enforced OAuth 'read' scope before dispatching tools/call requests, so a client holding only read access could invoke mutating tools like store_memory and delete_memory even though the equivalent REST endpoints correctly required 'write' scope. The flaw is a classic missing-authorization bug (CWE-862) surfacing specifically in an MCP tool-dispatch layer, scored CVSS 3.1 8.1 (High) with confidentiality unaffected but integrity and availability impacted. Fixed in 10.65.3.
nvd.nist.govadvisoryAdded 26 Sep 2026🛡️ Security - CVE-2026-20685: An attacker in a privileged network position may be able to leak sensitive information
CVE-2026-20685 is a medium-severity (CVSS 6.5) path handling vulnerability in Apple's Private Cloud Compute (PCC), classified under CWE-20 and CWE-22, that could let an attacker in a privileged network position leak sensitive information. Apple addressed the issue with improved path validation, fixed in PCC Release 5E290.3.
nvd.nist.govadvisoryAdded 26 Sep 2026🛡️ Security - CVE-2026-19978: A flaw has been found in jiantao88 android-mcp-server up to cfb872b2446794193b58edd63f4dbf6af48a6292
CVE-2026-19978 describes an OS command injection (CWE-77/78) in jiantao88's android-mcp-server, where the child_process.exec call in build/index.js fails to sanitize the deviceId, packageName, permission, and extras[].key/value arguments used to control Android devices. The flaw allows local command execution and has a published exploit; it was fixed in commit 14e2bf27c88ba137e35cbb0c2a75f72b595bb98a. CVSS 4.0 base score is 1.9 (local attack vector only), and the project uses rolling releases so no fixed version numbers are assigned.
nvd.nist.govadvisoryAdded 26 Sep 2026🛡️ Security - CVE-2026-18655: Improper restriction of intended endpoints in the RabbitMQ broker connection tools of the Amazon MQ MCP Server (awslabs
CVE-2026-18655 describes an improper endpoint restriction flaw (CWE-923) in the RabbitMQ broker connection tools of awslabs.amazon-mq-mcp-server versions before 2.0.24. A remote unauthenticated attacker can use prompt injection introduced into the MCP client context to redirect the broker hostname to an attacker-controlled endpoint, causing Amazon MQ for RabbitMQ credentials or OAuth access tokens to be sent there; CVSS 4.0 base score 7.1 (High). Fixed in version 2.0.24, referenced via an AWS security bulletin and a GitHub security advisory (GHSA-xwj6-8x5h-hjp6).
nvd.nist.govadvisoryAdded 26 Sep 2026🛡️ Security - CVE-2026-16584: Improper handling of an initialization failure in AWS API MCP Server from 0
CVE-2026-16584 affects AWS API MCP Server (awslabs.aws-api-mcp-server) versions 0.2.13 through 1.3.46: if the security policy enforcement data fails to initialize at server startup, the tool silently skips policy checks for the rest of the process's life, letting an agent execute AWS API operations the admin configured the policy to deny or gate. Underlying IAM permissions still apply and are unaffected, but the intended allow/deny gating layer is bypassed (CWE-455, improper handling of initialization failure). Fixed in 1.3.47.
nvd.nist.govadvisoryAdded 26 Sep 2026🛡️ Security - CVE-2026-16498: The terraform-mcp-server before version 1
CVE-2026-16498 is a critical (CVSS 3.1: 10.0) exposure-of-sensitive-information flaw (CWE-488) in HashiCorp's terraform-mcp-server prior to version 1.1.0. In stateless streamable-HTTP transport mode, one user's Terraform API token could be reused to execute tool calls on behalf of a different, subsequent user, breaking tenant isolation in shared MCP server deployments. Fixed in terraform-mcp-server 1.1.0; further detail is tracked in HashiCorp's HCSEC-2026-23 advisory.
nvd.nist.govadvisoryAdded 26 Sep 2026🛡️ Security - CVE-2026-14541: An authentication bypass and audience confusion vulnerability exists in the Google OAuth provider component of Google mc
CVE-2026-14541 describes an authentication bypass (CWE-287) in the Google OAuth provider of Google's mcp-toolbox for databases v1.4.0, an MCP server that lets LLM agents query databases. When the Google authService is configured with mcpEnabled: true but no explicit audience or clientId, the ValidateMCPAuth pipeline skips audience checks for opaque tokens, so any valid Google OAuth access token — even one issued for an unrelated app — is accepted, letting unauthorized clients reach protected tools and data backends.
nvd.nist.govadvisoryAdded 26 Sep 2026🛡️ Security - CVE-2026-85706: Critical GitLab Path Traversal Exploited in the Wild
GitLab patched CVE-2026-85706, a critical (CVSS 10.0) path traversal flaw (CWE-22) in the repository commits API that lets an unauthenticated attacker read arbitrary files from self-managed GitLab CE/EE instances; CISA added it to the KEV catalog on September 11, 2026 due to active exploitation, with a remediation deadline of September 14. The same patch release fixes CVE-2026-87719, a critical insecure deserialization bug (CWE-502) letting an authenticated Duo Chat user exfiltrate Advanced Search configs and credentials via a crafted GraphQL subscription argument, plus 17 other vulnerabilities. Rapid7 recommends emergency patching and post-patch compromise checks given confirmed in-the-wild exploitation.
rapid7.comadvisoryAdded 7 Oct 2026, published 14 Sep 2026🛡️ Security  Security Hardening Release for Splunk Apps and Add-ons - August 2026
Splunk's August 2026 hardening advisory (SVD-2026-0808) discloses 17 CVEs across Cisco Talos Intelligence for Enterprise Security Cloud, Splunk AI Toolkit, Splunk Connect for Kafka, the Splunk MCP Server app, and Splunk On-Call (VictorOps). Notable issues include a critical (CVSS 9.1) RCE via unsafe credential deserialization in the Splunk MCP Server app (CVE-2026-76404), an RCE via pickle-based deserialization when loading ML model files in Splunk AI Toolkit (CVE-2026-76395), multiple SSRF and authorization-bypass flaws letting low-privileged users escalate to system-level search execution, hardcoded/predictable container credentials, and unauthenticated DoS/ReDoS and cert-validation bypasses in Splunk Connect for Kafka. Each finding includes CWE classification, CVSS vector, and mitigation guidance (typically disabling the affected app or restricting REST API access).
 advisory.splunk.comadvisoryAdded 21 Aug 2026🛡️ Security
- CVE-2026-15988 | INCIBE-CERT | INCIBE
CVE-2026-15988 describes a CSRF vulnerability (CVSS 8.8, CWE-352) in the "AI Engine – The Chatbot, AI Framework & MCP" WordPress plugin, affecting all versions up to and including 3.6.5. Missing/incorrect nonce validation on the reauth_for_authorize function lets an unauthenticated attacker trick a logged-in administrator into visiting a crafted link, which — combined with WordPress's ?_method=POST override to turn a GET into an authenticated REST POST — creates a new administrator account with attacker-supplied credentials.
 incibe.esadvisoryAdded 2 Aug 2026🛡️ Security
 Orca Security: Critical Heap Buffer Overflow in NGINX Allows Unauthenticated RCE
Covers CVE-2026-42533, a heap buffer overflow (CWE-122) in the NGINX map directive's regex handling. It is triggered when a string expression references unnamed captures before the map output variable. Unauthenticated crafted HTTP requests can crash workers and may give RCE where ASLR is off or bypassed. It also covers two other F5-patched NGINX flaws: CVE-2026-60005 (uninitialized memory disclosure in ngx_http_slice_module) and CVE-2026-56434 (use-after-free in ngx_http_ssi_module with proxy_pass and proxy_buffering off). It lists affected NGINX Open Source (0.9.6–1.31.2), NGINX Plus, Ingress Controller, Gateway Fabric, App Protect WAF and Instance Manager versions. It gives fixed releases (1.31.3 / 1.30.4) and the named-capture workaround, and notes no public PoC or in-the-wild exploitation.
orca.securityadvisoryPublished and added 20 Jul 2026🛡️ Security AI Security Briefing
CVE-2026-14898 affects the OpenAI Codex desktop app for macOS, which automatically renders remote images embedded in Markdown model output without user interaction. An attacker can use indirect prompt injection to make Codex generate a response containing an attacker-controlled image URL whose parameters embed sensitive data (API keys, source code, tool output), which is silently exfiltrated when the app auto-fetches the image. Categorized under CWE-200, no patch or CVSS score was available at disclosure.
 cybersecuritynews.comadvisoryPublished and added 18 Jul 2026🛡️ Security
- CVE-2026-59950
CVE-2026-59950 (CVSS 7.6) affects the MCP Python SDK's deprecated mcp.server.websocket.websocket_server transport, which accepted WebSocket handshakes without validating Host or Origin headers, giving no SDK-level way to restrict which origins could connect to applications exposing that transport. This is a classic CSWSH-style origin-validation flaw (CWE-346, CWE-1385) fixed in mcp 1.28.1.
nvd.nist.govadvisoryPublished and added 17 Jul 2026🛡️ Security  AI Security Briefing
GHSA-3pvh-63gf-j9mw discloses an authenticated remote code execution vulnerability in LangBot, an open-source AI chatbot/agent framework, caused by its MCP Server Configuration feature. Because LangBot's mcp.py uses Anthropic's StdioServerParameters to launch MCP servers, any authenticated user can add a "STDIO" MCP entry with an arbitrary shell command and have it executed on the server, enabling data exfiltration, reverse shells, or full host compromise (CWE-78 OS command injection).
 github.comadvisoryPublished and added 17 Jul 2026🛡️ Security
- CVE-2026-55608
CVE-2026-55608 affects n8n-MCP, an MCP server exposing n8n node documentation and operations to AI assistants. Prior to version 2.57.4, when run in multi-tenant HTTP mode (ENABLE_MULTI_TENANT=true), an authenticated tenant could bypass tenant scoping and access or delete default-scope workflow_versions backups left over from earlier single-tenant deployments or migrations, exposing other tenants' workflow data. The issue is tracked as CWE-200 (information exposure) and CWE-863 (incorrect authorization) and is fixed in v2.57.4.
nvd.nist.govadvisoryPublished and added 16 Jul 2026🛡️ Security - CVE-2026-61459
CVE-2026-61459 describes an argument injection flaw (CWE-88) in mcp-server-kubernetes before 3.9.0, where the structured tools kubectl_get, kubectl_describe, and kubectl_delete fail to block leading-dash resourceType/name parameters, letting an attacker bypass the assertNoDangerousFlags check and inject a --server flag. This redirects kubectl calls to an attacker-controlled API server, leaking the operator's bearer token and enabling full Kubernetes cluster compromise. Fixed in v3.9.0; details corroborated by a VulnCheck advisory and the upstream GitHub commit/PR.
nvd.nist.govadvisoryPublished and added 12 Jul 2026🛡️ Security - CVE-2026-61447
CVE-2026-61447 describes a critical (CVSS 4.0 score 10.0) remote code execution vulnerability in PraisonAI versions before 1.6.78, rooted in CodeAgent._execute_python(), which runs LLM-generated Python code with no AST validation, import restrictions, or sandbox enforcement. An attacker who can influence the LLM's output via prompt injection can exfiltrate environment secrets and achieve arbitrary code execution on the host, making it a textbook agentic-code-execution flaw (CWE-94).
nvd.nist.govadvisoryPublished and added 12 Jul 2026🛡️ Security  Vulnerability-Lookup
GHSA-9c5h-h4mj-p5ch / CVE-2026-13524 documents an improper-authorization vulnerability (CWE-266) in Cherry Studio's MCP OAuth Local Callback Server (src/main/services/mcp/oauth/callback.ts), where manipulation of the code parameter can bypass authorization checks. The attack is remote but high-complexity and difficult to exploit (CVSS 3.1: 6.5 / CVSS 4.0), a public PoC has been disclosed, and a fix PR is still awaiting merge as of publication.
 vulnerability.circl.luadvisoryAdded 26 Sep 2026, published 29 Jun 2026🛡️ Security
 CVE-2026-49291 | THREATINT
CVE-2026-49291 affects mcp-memory-service, a semantic memory layer for AI apps, in versions before 10.65.3. The HTTP MCP JSON-RPC endpoint `/mcp` requires only the OAuth `read` scope and dispatches `tools/call` to mutating handlers. A read-only client can therefore call `store_memory` and `delete_memory`, bypassing the `write` scope that the REST endpoints enforce. It is classed as CWE-862 Missing Authorization and fixed in 10.65.3.
 cve.threatint.euadvisoryAdded 23 Jun 2026🛡️ Security
- Vulnerability-Lookup
GHSA-73cv-556c-w3g6 (CVE-2026-49257, CWE-306) documents that mcp-pinot v3.0.1 and earlier defaults to an HTTP MCP server bound to 0.0.0.0:8080 with oauth_enabled=False, exposing all 14 tools — including read_query, create_schema and create_table_config — to any unauthenticated network caller. The server proxies calls using its own server-side Pinot credentials, creating a confused-deputy condition that grants full read/write access to the backing Apache Pinot cluster (CVSS 10.0). Fixed in v3.1.0 (PR #95) by defaulting the bind host to 127.0.0.1, refusing non-loopback exposure without OAuth, and gating Helm exposure behind OAuth.
vulnerability.circl.luadvisoryAdded 26 Sep 2026, published 18 Jun 2026🛡️ Security - CVE-2026-49257: CWE-306: Missing Authentication for Critical Function in startreedata mcp-pinot - Live Threat Intelligence - Threat Radar | OffSeq.com
test summary
 radar.offseq.comadvisoryAdded 26 Sep 2026, published 18 Jun 2026🛡️ Security
- CVE-2026-21852 — Claude Code Information Disclosure (pre-trust config injection leaks API keys)
CVE-2026-21852 describes a flaw in Claude Code versions prior to 2.0.65 where a malicious repository's settings file can override ANTHROPIC_BASE_URL and have it applied during project load before the user sees or accepts the trust-confirmation prompt, causing the user's Anthropic API key to be sent to an attacker-controlled endpoint. The root cause is an initialization-order bug (CWE-522, insufficiently protected credentials) where untrusted repo config is parsed and acted on ahead of trust verification; Anthropic fixed it in 2.0.65 by moving trust checks before config processing. Mitigations include updating, rotating exposed keys, and avoiding opening unfamiliar repos until patched.
 sentinelone.comadvisoryAdded 30 Sep 2026, published 21 Jan 2026🛡️ Security