- CISA Adds Two Known Exploited Vulnerabilities to Catalog
CISA added two Ivanti Connect Secure vulnerabilities to its Known Exploited Vulnerabilities (KEV) Catalog on 30 October 2026, citing evidence of active exploitation: CVE-2026-111357 (missing authentication for a critical function) and CVE-2026-118527 (generation of predictable numbers or identifiers). The alert restates BOD 26-04, which requires federal civilian agencies to remediate KEV-listed flaws on exposed assets and check for prior compromise. It also links the KEV nomination form.
 cisa.govadvisoryPublished and added 30 Oct 2026🛡️ Security
- CISA Adds Two Known Exploited Vulnerabilities to Catalog
CISA alert of 29 October 2026 adding two vulnerabilities to the Known Exploited Vulnerabilities catalog on evidence of active exploitation: CVE-2026-97229, an integer overflow in GitLab CE/EE, and CVE-2026-76418, a NULL pointer dereference from an unchecked return value in Cisco Secure Firewall ASA and FTD. It restates BOD 26-04 remediation duties for federal civilian agencies and links the KEV nomination form.
cisa.govadvisoryPublished and added 29 Oct 2026🛡️ Security - lee1981 (@lee1981b) on X
CVE-2026-103780 is a stack-based buffer overflow (CWE-121) in Dell PowerProtect Data Domain / DD OS. An unauthenticated remote attacker could get command execution (CVSS 3.1 9.8, Dell DSA-2026-416). The post lists affected and fixed builds for four release trains (Feature Release, LTS2024, LTS2025, LTS2026). It adds KEV, EPSS and SSVC status, plus six defensive checks. The vulnerable service is not public.
 x.comadvisoryAdded 31 Oct 2026, published 29 Oct 2026🛡️ Security
- CISA Adds Two Known Exploited Vulnerabilities to Catalog
CISA alert of 28 October 2026 adding two vulnerabilities to the Known Exploited Vulnerabilities Catalog on evidence of active exploitation: CVE-2026-41709 (Broadcom VMware ESX insufficient logging) and CVE-2026-46300 (Linux kernel missing variable initialization). It restates BOD 26-04, which requires federal civilian agencies to prioritize fast remediation of KEV CVEs on exposed assets and to check for prior compromise. It also links the KEV nomination form.
cisa.govadvisoryAdded 29 Oct 2026, published 28 Oct 2026🛡️ Security - lee1981 (@lee1981b) on X
CVE-2026-92885 is a critical (CVSS 3.1 9.8, CWE-287) authentication bypass in the Qode Membership WordPress plugin, versions through 2.0.6.2. A misspelled variable in the Facebook token-verification guard skips provider checks, so an unauthenticated attacker with a public nonce can get a session cookie for an existing account, including an administrator. The post gives the fix (2.0.6.3, bundled in Bridge 30.9), KEV/EPSS/SSVC status, and a SOC log-correlation and remediation plan.
x.comadvisoryAdded 31 Oct 2026, published 28 Oct 2026🛡️ Security - CISA Adds Two Known Exploited Vulnerabilities to Catalog
CISA alert of 27 October 2026 adding two vulnerabilities to the Known Exploited Vulnerabilities (KEV) Catalog on evidence of active exploitation: CVE-2026-48356, an unrestricted upload of a dangerous file type in Adobe Commerce and Magento, and CVE-2026-111497, an unchecked return value in Google Brotli. It restates BOD 26-04, which makes federal civilian agencies prioritise KEV flaws on exposed assets and check for prior compromise. No technical detail or IOCs are given.
cisa.govadvisoryAdded 29 Oct 2026, published 27 Oct 2026🛡️ Security - lee1981 (@lee1981b) on X
CVE-2026-115905 is a ZIP cloaking flaw in the Rust zip crate (zip-rs/zip2), rated CVSS v4.0 10.0 and affecting versions below 9.0.5. ZipArchive reads central-directory metadata while ZipStreamReader reads local headers, so a crafted archive can pass filename inspection and then overwrite a different file during streaming extraction. Version 9.0.5 adds consistency checks, but ZipStreamReader::new leaves them off by default, and extraction is not atomic, so files can be written before an error is raised. The post covers CWE-20 and CWE-436, KEV and EPSS status, Debian status and a six-step investigation trail.
x.comadvisoryAdded 29 Oct 2026, published 27 Oct 2026🛡️ Security - CISA Adds Two Known Exploited Vulnerabilities to Catalog
CISA added two PHP vulnerabilities to its Known Exploited Vulnerabilities Catalog on 26 October 2026: CVE-2026-109618 (memory corruption) and CVE-2026-109619 (stale internal request state). It also updated its PHP alert on critical vulnerabilities requiring immediate patching. The alert restates BOD 26-04, which requires federal civilian agencies to prioritize fast remediation of KEV CVEs on exposed assets and to check for prior compromise.
cisa.govadvisoryAdded 29 Oct 2026, published 26 Oct 2026🛡️ Security - lee1981 (@lee1981b) on X
CVE-2026-111497 is an out-of-bounds write in the Brotli decoder bundled with Node.js (CWE-787, CWE-252), rated CVSS v4.0 9.2 by the Google CNA and High by the Node.js project. Fixes are Node 22.23.4, 24.22.1 and 26.12.1, and 24.22.1 still labels Brotli 1.2.0 because the fix was cherry-picked. The post gives a SOC trail from input to worker, with remediation and verification steps. It notes no KEV match, CISA SSVC exploitation none, and only unverified public lab claims.
x.comadvisoryAdded 26 Oct 2026, published 23 Oct 2026🛡️ Security - lee1981 (@lee1981b) on X
CyberForge CVE of the Day #084 analyses CVE-2026-76466, a CVSS 9.8 flaw in clustered Cisco Expressway-C and Expressway-E. Persistent database cookies and weak client-certificate validation allow root OS command execution over the network. The fix is X15.5.20 (X14 and earlier must migrate), with no workaround. It adds a per-peer SOC investigation trail, reachability checks and exposure status from CISA SSVC, KEV and EPSS.
x.comadvisoryAdded 24 Oct 2026, published 22 Oct 2026🛡️ Security  Threat Brief: Active Exploitation of PAN-OS CVE-2026-0257 (Updated Oct 20)
Unit 42 threat brief on active exploitation of CVE-2026-0257, a PAN-OS GlobalProtect authentication bypass added to CISA KEV on May 13, 2026. It lists IP addresses, host IDs and PoC-derived client values to hunt in GlobalProtect logs. The October 2026 updates cover Qilin and Inc ransomware operators, MFA bypass, pivots to vCenter and ESXi with offline VMDK credential dumping, and management interface exposure on ports 4443 and 3879.
 unit42.paloaltonetworks.comadvisoryAdded 21 Oct 2026, published 20 Oct 2026🛡️ Security
- lee1981 (@lee1981b) on X
CVE-2026-77932 affects DB-GPT through 0.8.2 (dbgpt-app). The /api/v1/chat/react-agent route accepts unauthenticated requests because get_user_from_headers returns an admin-role user, and the ReAct agent can reach unsandboxed Python and shell tools. Lasso reported root in the webserver container in a lab. The post gives CVSS 9.8 and 9.3, no verified fix (0.8.2 is still the latest release), no KEV match, no EPSS data, and a SOC hunting trail.
x.comadvisoryAdded 23 Oct 2026, published 20 Oct 2026🛡️ Security  Frequently Asked Questions About the BeyondTrust Remote Support Arbitrary File Upload (CVE-2026-102764)
CVE-2026-102764 is an arbitrary file upload in BeyondTrust Remote Support (formerly Bomgar) caused by internal appliance components not validating message origin. Mandiant found it exploited as a zero-day in late August 2026. BeyondTrust disclosed it on 15 October 2026 and CISA added it to KEV on 16 October 2026. The FAQ covers the web shell, root escalation, credential theft, persistence, patching and compromise checks.
 watchtowr.comadvisoryAdded 30 Oct 2026, published 16 Oct 2026🛡️ Security
 BeyondTrust Remote Support Arbitrary File Upload (CVE-2026-102764)
CVE-2026-102764 is a CVSS 9.8 unauthenticated arbitrary file upload flaw in BeyondTrust Remote Support (formerly Bomgar) and Privileged Remote Access. Internal messaging components do not verify message origin, so remote attackers can plant files the appliance would reject. BeyondTrust disclosed it on 15 October 2026 with patch BT26-05, and CISA added it to KEV on 16 October 2026. The page lists log files to review and hardening steps.
watchtowr.comadvisoryAdded 30 Oct 2026, published 16 Oct 2026🛡️ Security- lee1981 (@lee1981b) on X
Daily CVE digest on CVE-2026-76519, a CVSS 9.8 relative path traversal (CWE-23) in Cisco Secure Email Gateway's AMP File Reputation attachment processing. A crafted attachment gives unauthenticated arbitrary file writes and root command execution, and Cisco PSIRT reports active exploitation. The CVE is in CISA KEV. It lists the applicability conditions (File Reputation assigned to a policy and Content Scanner Tools earlier than 25.3.0.5525) and the fixes (scanner 25.3.0.5525, AsyncOS 15.5.5-014 and 16.5.0-780). It also covers evidence preservation, reading Cisco's System Security scan outcomes, mail/AMP log correlation, and deployment-specific recovery including cluster-key exposure.
x.comadvisoryAdded 18 Oct 2026, published 15 Oct 2026🛡️ Security  Critical GitLab RCE Lets Unauthenticated Attackers Execute Code on Servers (CVE-2026-97229)
Orca Security analysis of CVE-2026-97229, a CVSS 10.0 flaw in GitLab CE/EE. An integer overflow (CWE-190) in the CI/CD regular expression compiler gives memory corruption and code execution as the git user. It is triggered by a crafted regex in .gitlab-ci.yml combined with a UTF-8 repository path, with no authentication needed on instances that allow public project creation or self-registration. Lists affected branches (19.2 before 19.2.8, 19.3 before 19.3.5, 19.4 before 19.4.2), the absence of a workaround, interim mitigations, and a Rapid7 PoC against GitLab CE 19.4.1 with ASLR on. Notes a prior max-severity GitLab bug (CVE-2026-85706) was probed in the wild within hours and later added to CISA KEV.
 orca.securityadvisoryPublished and added 14 Oct 2026🛡️ Security
- Dark Web Intelligence (@DailyDarkWeb) on X
Summary of SAP's October 13, 2026 Security Patch Day (16 new notes, 4 GitHub advisories). It leads with CVE-2026-89111, a CVSS 10.0 OAuth2 SSRF in SAP Cloud SDK for Python before 0.45.2, where an attacker-controlled tenant_subdomain redirects token requests and exfiltrates client credentials. It also lists three other critical flaws: broken access control in NetWeaver Visual Composer, code injection in S/4HANA substitution/validation rules, and a missing authorization check in the Manufacturing Integration and Intelligence (XMII) Configuration Service. It notes that none are in CISA KEV and SAP reports no in-the-wild exploitation.
x.comadvisoryAdded 15 Oct 2026, published 13 Oct 2026🛡️ Security  Ivanti Connect Secure zero-day exploited in the wild (CVE-2026-104935)
Rapid7 emergency-response analysis of CVE-2026-104935, a CVSS 8.6 authentication bypass by spoofing (CWE-290) in Ivanti Connect Secure that allows unauthenticated remote command execution. It was exploited as a zero-day against a limited number of customers, added to CISA KEV on disclosure day, and Volexity observed it chained with a still-unpatched privilege escalation flaw. Part of the fix shipped in 25.1.3.0 in July 2026, with backports to other supported versions pending. Rapid7 advises emergency patching outside normal cycles and hunting for compromise using Volexity's IOCs, since Ivanti has no reliable ones.
 rapid7.comadvisoryPublished and added 13 Oct 2026🛡️ Security
 Frequently Asked Questions About the Ivanti Connect Secure Authentication Bypass by Spoofing (CVE-2026-104935)
CVE-2026-104935 is an authentication bypass by spoofing in Ivanti Connect Secure. A remote attacker can forge identity signals and run arbitrary commands without credentials. CISA added it to the KEV catalog on 13 October 2026. The FAQ lists affected branches by ISA hardware (25.1.1.1, 25.1.2.2, 22.8.X), fixed versions (25.1.1.2, 25.1.3.0/25.1.3.1, 22.8R2.5), no workaround and no reliable IOCs.
watchtowr.comadvisoryAdded 30 Oct 2026, published 13 Oct 2026🛡️ Security Ivanti Connect Secure Authentication Bypass by Spoofing (CVE-2026-104935)
CVE-2026-104935 is an authentication bypass by spoofing in Ivanti Connect Secure (CVSS 3.1 score 8.6) that lets a remote attacker run commands without logging in. CISA added it to KEV on 13 October 2026. The 22.8.X bridge release and 25.1.2.2 and earlier are affected, with fixes in 22.8R2.5, 25.1.1.2, 25.1.3.0 and 25.1.3.1. Ivanti says no reliable indicators of compromise exist yet.
watchtowr.comadvisoryAdded 30 Oct 2026, published 13 Oct 2026🛡️ Security- lee1981 (@lee1981b) on X
CyberForge "CVE of the Day #076" covers CVE-2026-97229, a CVSS 10.0 integer overflow (CWE-190) in GitLab CE/EE's CI/CD regular expression compiler. It can lead to conditional unauthenticated code execution on the GitLab server. It lists the affected trains (19.2 before 19.2.8, 19.3 before 19.3.5, 19.4 before 19.4.2) and the 19.3.4 vs 19.3.5 Ona-regression discrepancy. It also gives six SOC checks: scoping, log preservation (Workhorse/Rails/Sidekiq, correlation_id), server-effect hunting, request-to-process correlation, upgrade and running-state verification. It notes that exploit details are unverified, no KEV listing exists and EPSS data is unavailable.
x.comadvisoryAdded 15 Oct 2026, published 13 Oct 2026🛡️ Security - lee1981 (@lee1981b) on X
CyberForge's CVE of the Day #075 covers CVE-2026-108860, a critical (CVSS 9.1 v3.1 / 9.3 v4.0) authentication bypass in SciSharp BotSharp through 5.2.0. WebStarter ships a published default HMAC JWT signing secret (CWE-321), so anyone holding it can forge bearer tokens that impersonate known users, including administrators. The post sets out how to confirm the effective key and serving build, a six-step SOC investigation trail, and remediation by rotating the secret. No verified fixed release, KEV entry or EPSS data existed at cutoff, and the linked research is static-only.
x.comadvisoryAdded 13 Oct 2026, published 12 Oct 2026🛡️ Security - lee1981 (@lee1981b) on X
CyberForge CVE of the Day #074 analyses CVE-2026-85097, a CVSS 9.8 unauthenticated file upload to PHP execution flaw (CWE-434) in the Bricksforge WordPress plugin through 3.1.8.9. Wordfence names 3.1.8.10 as the fix, and a separate vendor 4.0.1 Pro Forms upload-security notice has no verified mapping to the CVE. It gives a defender workflow: scope versions, preserve edge/origin logs, inspect resulting files and PHP-FPM handling, and verify the patched version is serving. It also separates KEV (no match), EPSS (0.312%) and SSVC (exploitation none) from compromise evidence.
x.comadvisoryAdded 11 Oct 2026, published 10 Oct 2026🛡️ Security - lee1981 (@lee1981b) on X
CyberForge's CVE of the Day #073 covers CVE-2026-102255, a critical (CVSS 10.0) pre-authentication SSRF / confused-deputy flaw (CWE-918, CWE-441) in the SonicWall SMA1000 Work Place interface, per advisory SNWLID-2026-0017. It lists affected platform hotfixes (12.4.3-03526 and older, 12.5.0-02952 and older), fixed floors (12.4.3-03670, 12.5.0-03082), no workaround, and the exploitation picture (no known exploitation, not in KEV, EPSS 0.477%, SSVC automatable). It gives a six-step SOC playbook covering appliance scoping, AMC log preservation, hunting appliance-originated internal requests, correlating receiving-service changes, patching, and verifying every node, and it separates exposure, a lead, confirmed compromise and telemetry gaps.
x.comadvisoryAdded 12 Oct 2026, published 9 Oct 2026🛡️ Security  Atlassian Jira, Confluence (and more) Arbitrary File Read Vulnerability (CVE-2026-21589)
CVE-2026-21589 is an unauthenticated arbitrary file read (path traversal) in eight Atlassian Data Center and Server products: Bitbucket, Confluence, Jira, Jira Service Management, Bamboo, Crowd, Crucible and Fisheye. Atlassian fixed it on 5 October 2026, and CISA added it to the KEV catalog on 15 October 2026. The page lists patching, WAF regex, Tomcat RewriteValve and urlrewrite.xml mitigations, and a log check for ".." sequences after up to two rounds of URL decoding.
watchtowr.comadvisoryAdded 30 Oct 2026, published 6 Oct 2026🛡️ Security- Dark Web Intelligence (@DailyDarkWeb) on X
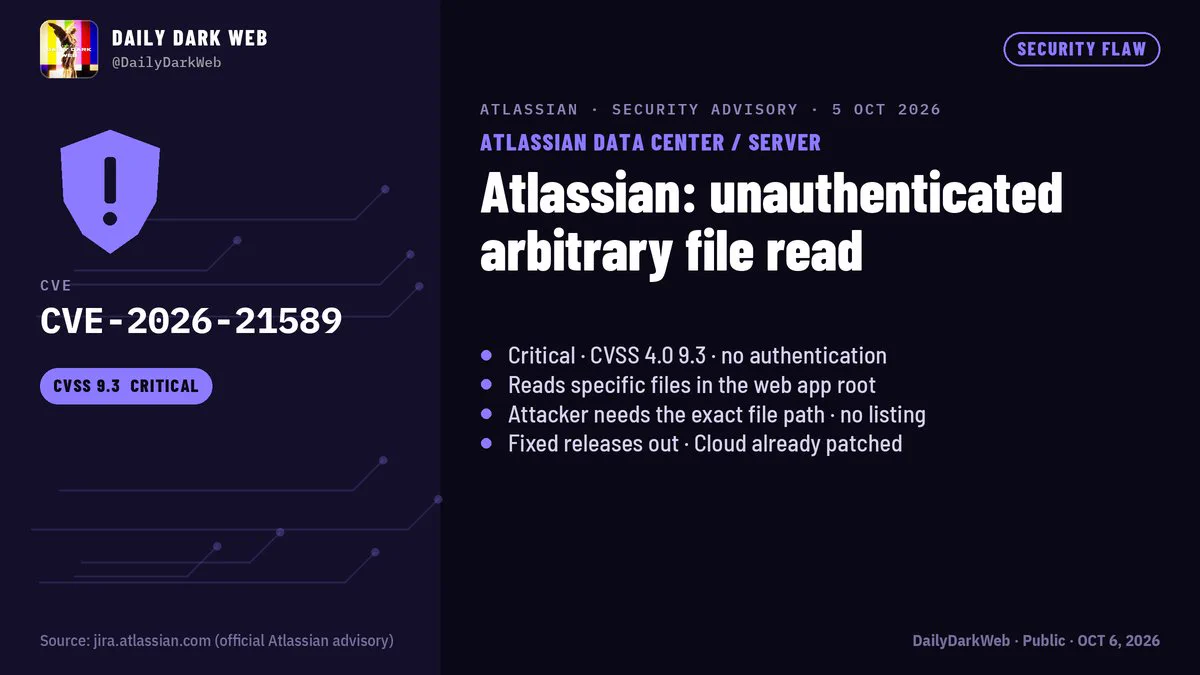
Atlassian disclosed CVE-2026-21589, a critical (CVSS 9.3) unauthenticated path traversal flaw allowing remote attackers to read specific files within the web application root across its self-managed Data Center/Server products — Jira Software, Jira Service Management, Confluence, Bitbucket, Bamboo, Crowd, Crucible, and Fisheye. Fixed versions are listed for each product (e.g. Jira 9.12.40/10.3.26/11.3.12, Confluence 9.2.26/10.2.19), and Atlassian Cloud is already patched; WAF/URL-rewrite mitigations are available for those who can't upgrade immediately. The post's analyst note clarifies exploitation requires knowing the exact target file path (no directory listing), and as of Oct 5, 2026 it is not yet in CISA KEV with no public exploit reported.
x.comadvisoryAdded 7 Oct 2026, published 6 Oct 2026🛡️ Security  Citrix NetScaler Zero-Day Exploited in the Wild Crashes SAML Authentication Services
Analysis of CVE-2026-88779 (CVSS v4.0 8.7), an unauthenticated memory-overflow flaw in the nsaaad SAML authentication handler on Citrix NetScaler ADC/Gateway that lets attackers crash the SAML service and lock out VPN/SSO access indefinitely through repeated triggering. Affects NetScaler 14.1 before 14.1-73.41 and 13.1 before 13.1-64.28 (plus FIPS/NDcPP builds); watchTowr Labs reproduced it via honeypot activity, Citrix confirmed targeted in-the-wild exploitation from IP 213.209.159.55, and CISA added it to KEV on 2026-10-04 with an Oct 7 federal remediation deadline. Some researchers suspect the overflow could extend to RCE beyond the documented DoS, though Citrix hasn't confirmed this.
orca.securityadvisoryPublished and added 5 Oct 2026🛡️ Security- CISA KEV: Fortinet FortiMail CVE-2026-104286 path traversal, actively exploited, no patch yet
CISA added CVE-2026-104286, a path traversal vulnerability in Fortinet FortiMail, to its Known Exploited Vulnerabilities Catalog on evidence of active exploitation. The alert restates the obligations of BOD 26-04 for Federal Civilian Executive Branch agencies: prioritise KEV CVEs on publicly exposed assets that give total control, and check for compromise before patching. It also describes the KEV nomination criteria: a CVE ID, evidence of exploitation and clear mitigation guidance. The page gives no technical detail, patch status or IOCs.
cisa.govadvisoryAdded 4 Oct 2026🛡️ Security - Critical Cisco Catalyst SD-WAN Manager API authentication bypass exploited in the wild (CVE-2026-76504)
Rapid7 analysis of CVE-2026-76504, a critical (CVSSv3.1 9.8) unauthenticated API authentication bypass in Cisco Catalyst SD-WAN Manager caused by improper URL-encoding handling (CWE-177), allowing attackers to gain admin-level API access via crafted requests to the j_security_check endpoint. The flaw is being actively exploited in the wild, was added to CISA's KEV list on October 1, 2026 with a remediation deadline of October 3, and follows two earlier 2026 Catalyst SD-WAN peering authentication bypasses (CVE-2026-20127 and Rapid7-discovered CVE-2026-20182). The post gives fixed-release guidance, no-workaround caveats, and log-based IOCs (encoded-character requests like %6a_security_check, viptela-reserved- usernames) for detecting compromise.
rapid7.comadvisoryAdded 7 Oct 2026, published 30 Sep 2026🛡️ Security  Critical Citrix NetScaler Zero-Days Under Active Exploitation
Analysis of two CVSS 9.5 Citrix NetScaler ADC/Gateway zero-days, CVE-2026-88771 (unauthenticated RCE through improper input validation in the management interface, affecting default deployments) and CVE-2026-88772 (memory overflow in DTLS, enabled by default on VPN virtual servers). It lists six more high-severity flaws patched in advisory CTX697096, the affected and fixed versions, and the CISA KEV listing with a federal deadline of 2026-09-30. It advises checking for compromise before patching, since patching can destroy forensic evidence, and gives response steps: isolate, revoke credentials, rebuild firmware, rotate keys and certificates.
orca.securityadvisoryPublished and added 29 Sep 2026🛡️ Security- Zero-Day Exploitation of Citrix NetScaler ADC and Gateway: CVE-2026-88771 and CVE-2026-88772
Rapid7 details active zero-day exploitation of two critical Citrix NetScaler ADC/Gateway RCE vulnerabilities (CVE-2026-88771, CVE-2026-88772, both CVSSv4 9.5), both added to CISA KEV on disclosure day, plus a later SAML denial-of-service zero-day (CVE-2026-88779). The post includes Rapid7 MDR's observed exploitation of CVE-2026-88771 in the wild — a command-injection payload that exfiltrates /flash/nsconfig (containing ns.conf admin credentials, SSL private keys, SSH host keys) via the publicly-served /vpn/ path, and a webshell (SHA256 hash provided) found on a compromised appliance — along with vendor patch versions and detection guidance.
rapid7.comadvisoryAdded 7 Oct 2026, published 28 Sep 2026🛡️ Security  watchTowr: CVE-2026-88771 Citrix NetScaler ADC/Gateway unauthenticated RCE
watchTowr details CVE-2026-88771 (unauthenticated command execution via improper input validation, affecting every NetScaler ADC/Gateway deployment by default) and CVE-2026-88772 (DTLS memory overflow leading to RCE/DoS, exploitable since DTLS is on by default for VPN virtual servers). Both are confirmed exploited in the wild as zero-days, were pre-notified by NCSC-NL, and CVE-2026-88771 was added to the CISA KEV catalog on September 27, 2026; Citrix's bulletin CTX697096 also fixes six related issues (CVE-2026-88773 through CVE-2026-88778). The writeup gives prioritization guidance, IOC-checking steps, and warns that patching may destroy forensic evidence if done before evidence capture.
watchtowr.comadvisoryAdded 5 Oct 2026, published 27 Sep 2026🛡️ Security- CISA KEV Catalog Additions — Check Point, Arista VeloCloud, F5 BIG-IP (Sept 22, 2026)
CISA added four vulnerabilities to the Known Exploited Vulnerabilities catalog on 2026-09-22 based on evidence of active exploitation: two Check Point multi-product flaws (improper certificate validation CVE-2026-85102, path traversal CVE-2026-93616), an Arista VeloCloud Orchestrator improper input validation bug (CVE-2026-93952), and an F5 BIG-IP APM heap-based buffer overflow (CVE-2026-94127). The alert ties the additions to BOD 26-04, which has FCEB agencies prioritize remediation of KEV CVEs on publicly exposed assets that give total control, and to checking for prior compromise before patching.
cisa.govadvisoryAdded 26 Sep 2026🛡️ Security  Attackers Exploit WordPress CVE-2026-87902 Within Hours of Patch
CVE-2026-87902 (CVSS 9.2) is an unauthenticated WordPress vulnerability where get_page_template() page-template resolution can be tricked into including an attacker-chosen local .php file outside the active theme directory, leading to RCE when a theme has a page-* top-level directory and a readable local PHP file (e.g. pearcmd.php) exists. Attackers began exploiting it within hours of the September 22, 2026 patch, including pearcmd.php to write PHP web shells to /tmp and /var/tmp and pulling a GitHub-hosted uploader payload, per honeypot telemetry from Previdian and Patchstack with tracked source IPs. CISA added the flaw to its KEV catalog on September 25, 2026, mandating FCEB remediation by September 28; fixed in WordPress 7.1.2, 7.0.6, 6.9.9, and 6.8.10.
 thehackernews.comadvisoryAdded 26 Sep 2026🛡️ Security
- CISA Adds Seven Known Exploited Vulnerabilities to Catalog | CISA
CISA added seven vulnerabilities to its Known Exploited Vulnerabilities Catalog on the basis of active exploitation. They are SQL injection in Sangoma Switchvox, HTTP request/response smuggling in Kludex Starlette, OS command injection in Kestra OSS, improper authentication in BerriAI LiteLLM and JFrog Artifactory, and SSRF plus OS command injection in SonicWall SMA1000 appliances. The alert restates BOD 26-04, which makes federal agencies prioritise rapid remediation of KEV CVEs on publicly exposed assets that grant total control after exploitation. It also requires agencies to check for prior compromise before patching.
cisa.govadvisoryAdded 26 Sep 2026🛡️ Security - CVE-2026-94127: Critical Unauthenticated RCE in F5 BIG-IP APM
Rapid7's ETR writeup covers CVE-2026-94127, a critical heap-based buffer overflow (CVSS 9.8) in F5 BIG-IP Access Policy Manager that allows unauthenticated remote code execution via crafted traffic. Exploitation requires a virtual server with both an APM access policy and an OAuth profile configured, affects the data plane (including Appliance mode), and has been added to CISA KEV; F5 provides hotfixes for the 21.1.0, 17.5.0, and 17.1.0 release trains plus an iRule workaround for those unable to patch immediately.
rapid7.comadvisoryAdded 7 Oct 2026, published 23 Sep 2026🛡️ Security  Cisco Warns of New Zero-Day ISE Auth Bypass (CVSS 10.0) Exploited in Active Attacks
Cisco disclosed CVE-2026-76460 (CVSS 10.0), an unauthenticated API authentication bypass in Identity Services Engine (ISE) and ISE-PIC that is under active exploitation and has been added to CISA's KEV catalog with a federal patch deadline of September 19, 2026; successful exploitation can yield root command execution, and Cisco provides log-based IOC detection guidance since there is no workaround. The same disclosure batch includes 77 new CVEs, 41 in ISE and 28 in Secure Firewall (ASA/FTD/FMC), covering authenticated RCE, SQL injection, XXE, command injection, and additional REST API auth bypasses, plus a separately exploited Secure Email Gateway flaw (CVE-2026-76461, CVSS 9.8).
thehackernews.comadvisoryAdded 22 Sep 2026🛡️ Security- CVE-2026-76461: Critical Cisco Secure Email Gateway Vulnerability Exploited in the Wild
Rapid7's emerging threat response write-up on CVE-2026-76461, a critical (CVSS 9.8) SQL injection vulnerability in Cisco AsyncOS Software for Cisco Secure Email Gateway that allows an unauthenticated remote attacker to achieve root command execution by sending a specially crafted email. Cisco confirmed active zero-day exploitation and the vulnerability was added to CISA's KEV catalog the same day it was disclosed; the post provides mitigation guidance (emergency patching to 16.5.0-780) and a log-grep IOC (searching mail_logs for COPY.*TO PROGRAM) to detect exploitation attempts.
rapid7.comadvisoryAdded 7 Oct 2026, published 15 Sep 2026🛡️ Security  Breaking: GitLab Critical Path Traversal Flaw Exploited in the Wild — Patch Immediately
Details CVE-2026-85706 (CVSS 10.0), an unauthenticated arbitrary file read in GitLab CE/EE's repository commits API exploitable via a crafted file.path parameter in a single POST request, requiring only that one public project exist on the instance. It also covers CVE-2026-87719 (CVSS 9.9), an authenticated insecure deserialization bug in GitLab EE's GraphQL subscription serializer reachable via Duo Chat access that leaks stored Elasticsearch/OpenSearch credentials. Both affect GitLab versions through 19.3.1; CVE-2026-85706 is under active internet-wide scanning per WatchTowr Labs and is in CISA's KEV catalog with a federal patch deadline, with fixes in GitLab 19.1.8/19.2.6/19.3.2.
orca.securityadvisoryPublished and added 14 Sep 2026🛡️ Security- CVE-2026-85706: Critical GitLab Path Traversal Exploited in the Wild
GitLab patched CVE-2026-85706, a critical (CVSS 10.0) path traversal flaw (CWE-22) in the repository commits API that lets an unauthenticated attacker read arbitrary files from self-managed GitLab CE/EE instances; CISA added it to the KEV catalog on September 11, 2026 due to active exploitation, with a remediation deadline of September 14. The same patch release fixes CVE-2026-87719, a critical insecure deserialization bug (CWE-502) letting an authenticated Duo Chat user exfiltrate Advanced Search configs and credentials via a crafted GraphQL subscription argument, plus 17 other vulnerabilities. Rapid7 recommends emergency patching and post-patch compromise checks given confirmed in-the-wild exploitation.
rapid7.comadvisoryAdded 7 Oct 2026, published 14 Sep 2026🛡️ Security  Artifactory Under Attack: In-the-Wild Exploitation of CVE-2026-42016, CVE-2026-42018 & CVE-2026-82329
Wiz Research documents active in-the-wild exploitation of three JFrog Artifactory vulnerabilities: CVE-2026-42018 (exposes an internal anonymous-user JWT via POST /access/api/v1/aws/token/), CVE-2026-42016 (token scope validation flaw allowing that JWT to be escalated to admin via POST /access/api/v1/tokens), and CVE-2026-82329 (unauthenticated admin access via POST /access/api/v1/registry/join, added to CISA KEV). Attackers chained the first two to create persistent admin accounts, deploy malicious Groovy plugins for RCE, and drop Rust-based C2 backdoors, while CVE-2026-82329 was exploited independently for configuration exfiltration, cluster join-key theft, and credential/SSH-key persistence. The post includes exact request sequences, detection signatures, affected/fixed version ranges, and remediation guidance.
 wiz.ioadvisoryPublished and added 10 Sep 2026🛡️ Security
 AI Security Briefing
CISA added four actively exploited vulnerabilities to its KEV catalog: a path traversal RCE in Adobe ColdFusion (CVE-2026-48282, CVSS 10.0), an unauthenticated file-upload RCE in Joomlack Page Builder CK (CVE-2026-56290, CVSS 10.0), an IDOR in Langflow allowing cross-tenant flow execution and LLM/AWS key theft (CVE-2026-55255, CVSS 6.1), and an unauthenticated arbitrary file upload in JoomShaper SP Page Builder (CVE-2026-48908, CVSS 10.0). Sysdig documented an operator chaining the Langflow IDOR with CVE-2026-33017 RCE for opportunistic, financially motivated cryptojacking/botnet activity and credential theft from an AI orchestration platform, while mySites.guru observed web shell deployment via the Joomla flaws. FCEB agencies must patch by July 10, 2026.
thehackernews.comadvisoryPublished and added 18 Jul 2026🛡️ Security Orca Security: Langflow RCE (CVE-2026-33017) Actively Exploited
Orca Security details CVE-2026-33017 (CVSS 9.8), an unauthenticated RCE in Langflow's public flow-build API (/api/v1/build_public_tmp/{flow_id}/flow) that lets attackers execute arbitrary Python via a crafted node definition, with no sandboxing. Trend Micro observed active exploitation within 20 hours of disclosure, deploying a Go-based "lambsys" binary that kills rival cryptominers, disables AppArmor/SELinux/UFW/iptables, wipes logs, harvests credentials/.env files, and installs a geo-aware XMRig miner; ~7,000 internet-exposed Langflow instances were found, the flaw is in CISA's KEV catalog, and fix guidance clarifies 1.8.2 is still vulnerable — users must upgrade to 1.9.0+ or the 1.9.0.dev18 nightly and rotate exposed secrets.
orca.securityadvisoryPublished and added 2 Jul 2026🛡️ Security