- eness/php2shell-CVE-2026-109618-CVE-2026-109619-PoC
php2shell is the name given to two critical pre-auth remote code execution flaws, CVE-2026-109618 and CVE-2026-109619, in PHP core's session upload progress handler (php_session_rfc1867_callback), where zend_hash_update frees live zval pointers that are later reclaimed and redirected into zend_call_function to run zif_system. This repository ships poc_109618.py, a fully automated four-stage HTTP exploit that leaks ASLR offsets via Set-Cookie headers against php:8.4.26-apache on Debian Bookworm, along with a root-cause C source patch, mitigation scripts to disable session.upload_progress, and WAF/ModSecurity/Lighttpd/Apache rules plus detection guidance for anomalous PHP worker child processes. Confirmed PHP versions include 8.4.4 and 8.2.34, with EOL branches (5.x, 7.x, 8.0, 8.1) left without official vendor patches.
 github.comrepoAdded 23 Oct 2026, published 21 Oct 2026🛡️ Security
- ikow/php2shell-poc
php2shell-poc is a proof-of-concept and detection toolkit for CVE-2026-109618 and CVE-2026-109619, two PHP vulnerabilities tied to session.upload_progress handling and a Zend engine out-of-memory bailout path affecting PHP 5.4.0 through 8.5.11. The repository includes three working exploit chains, a Docker-based lab (PHP-FPM, nginx, Apache mod_php) for reproduction, and pre-built Suricata, Sigma, ModSecurity, and Lua detection rules. The author recommends disabling session.upload_progress as an interim mitigation, noting the underlying memory corruption requires a full PHP patch to fix.
github.comrepoAdded 23 Oct 2026, published 21 Oct 2026🛡️ Security - gichirimaku/wp2shell-PoC
wp2shell-PoC is a Python proof-of-concept exploiting a pre-authentication RCE chain in WordPress core, combining CVE-2026-63030 (REST API batch route confusion) and CVE-2026-60137 (SQL injection in WP_Query). It demonstrates escalation from the route-desync bug through blind SQLi, customize_changeset forgery, and hook re-entry to administrator account creation and arbitrary command execution via a malicious plugin upload. The tool supports vulnerability checking, data extraction (union, error-based, blind techniques), and full shell access with or without existing admin credentials.
github.comrepoAdded 23 Oct 2026, published 15 Oct 2026🛡️ Security - santosomar/AI-agents-for-cybersecurity
Omar Santos's companion repo for his Pearson/O'Reilly trainings and books, organised in eight parts. They cover LangChain prompts, chains and RAG (Chroma), and agents (LangGraph, CrewAI, DeepAgents). They also cover FastMCP security servers (nmap, CISA KEV, Shodan) and attack-surface-management and SOC agent examples. Later parts have security guides to six agentic frameworks (OpenClaw, Hermes, Agent Zero, OpenHands, Paperclip, Buzz) with hardening notes and 2026 CVE mapping, agent cost/tokenomics scripts including denial-of-wallet budget guards, and a vendor-neutral spec for a human-gated multi-agent security-assessment harness (scope manifest, approval gates, kill switch). Useful as a hands-on path into AI-agent security tooling, with warnings that some examples act on real systems.
github.comrepoAdded 13 Oct 2026🛡️ Security - sakidekin/CVE-2026-41940-PoC
This repository hosts a proof-of-concept for CVE-2026-41940, described as a CVSS 10.0 unauthenticated authentication bypass in cPanel and WHM caused by CRLF injection into server-side session files via the Authorization header. The accompanying Python tool (cve.py) can detect vulnerable cPanel/WHM instances, retrieve system and account information, and perform post-exploitation actions such as running OS commands, changing the root password, and opening an interactive WHM shell. It also supports bulk scanning workflows piped from subfinder, httpx, and Shodan.
github.comrepoAdded 23 Oct 2026, published 11 Oct 2026🛡️ Security  The Vulnerable MCP Project — MCP vulnerability database
The Vulnerable MCP Project is a curated, continuously growing database of security vulnerabilities and attack techniques specific to the Model Context Protocol ecosystem. Entries cover concrete CVEs (e.g. CVE-2025-68143/68144/68145 in Anthropic's mcp-server-git), transport-layer SDK flaws (cross-client response leakage, missing DNS rebinding protection in the official TypeScript/Python SDKs), unauthenticated/0.0.0.0-bound servers enabling RCE (MCPJam inspector, MCP Inspector, Grafana MCP), command/path injection in dozens of third-party servers (gemini-mcp-tool, mcp-server-kubernetes, Framelink Figma MCP, Zen MCP, filesystem-mcp), SSRF chains reaching cloud metadata (MarkItDown MCP, mcp-fetch-server), and a large set of AI-specific attacks: tool poisoning, trigger-phrase data exfiltration, prompt injection via GitHub issues, Jira and Google Docs, rug-pull tool mutation, and cross-server tool-name collisions. It functions as the de facto vulnerability registry for the MCP ecosystem, useful for tracking disclosed issues before patching or adopting third-party MCP servers.
 vulnerablemcp.inforepoAdded 6 Oct 2026🛡️ Security
- Dark Web Informer (@DarkWebInformer) on X
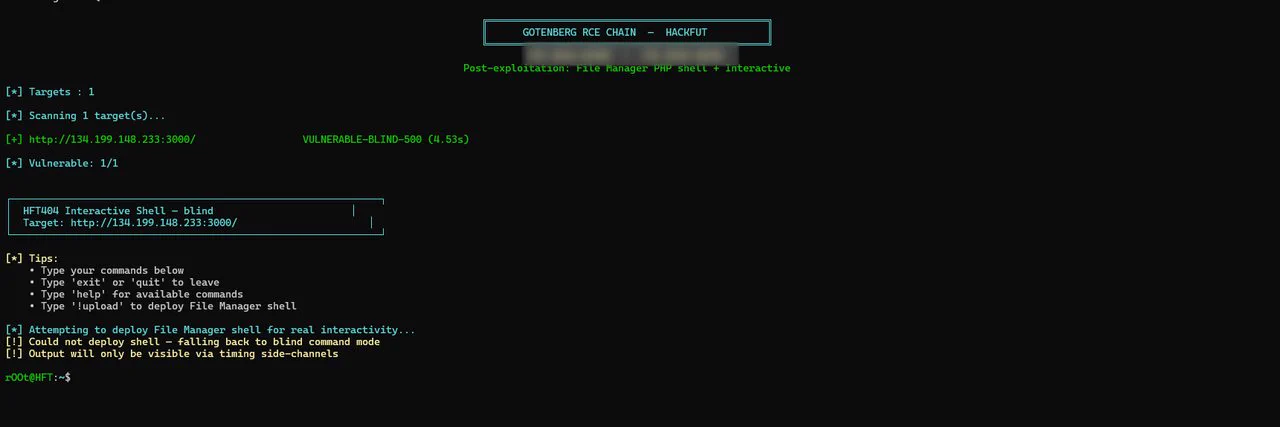
A public PoC chains CVE-2026-42589 and CVE-2026-40281 to achieve unauthenticated remote code execution against Gotenberg (a document/PDF-conversion microservice), abusing metadata injection flaws in the /forms/pdfengines/metadata/write endpoint. The tool supports vulnerability detection, interactive command execution, reverse shell delivery, and multi-target scanning against Gotenberg versions ≤8.30.1 (patched in 8.31.0).
 x.comrepoPublished and added 5 Oct 2026🛡️ Security
- Sigma r2026-07-01 — 20 new detection rules
GitHub release notes for Sigma r2026-07-01, the open-source detection-rule repository, adding 20 new rules (e.g. LSASS crash via Netlogon buffer overflow CVE-2026-41089, TanStack supply-chain attack indicators for Windows/Linux, RedTail cryptominer user-agent detection, AF_ALG kernel crypto API exploit indicator) and updating/fixing dozens of existing rules for ARM64 binary variants, file-sharing domain IOCs, and WMI-based reconnaissance/persistence detection. It's a routine but substantive update to a widely-used blue-team detection content pack.
github.comrepoAdded 3 Oct 2026🛡️ Security - AI-Infra-Guard (A.I.G) — Tencent Zhuque Lab
AI-Infra-Guard (A.I.G) is Tencent Zhuque Lab's open-source AI red-teaming platform combining AI infrastructure vulnerability scanning (2000+ CVE rules covering vLLM, llama.cpp, LangFlow, n8n, MLflow and 145+ other AI components), MCP server/skill security scanning, LLM API poisoning detection, and multi-turn jailbreak evaluation (Many-Shot, PAIR, GOAT, ActorAttack). It ships CLI tools (skill-scan, mcp-scan, agent-scan), a Docker-deployed web UI, and has produced original research including FORGE-Bench (loss-of-control benchmark), RogueHandoff-20, and SkillJack (persistent skill backdoors), with talks at Black Hat Europe 2025 on MCP security.
github.comrepoAdded 30 Sep 2026🛡️ Security - SAPMAP — SAP Landscape Attack Path Mapper
SAPMAP is a BloodHound-style attack path mapper for SAP landscapes: it discovers SAP systems on a network, maps RFC trust connections, and implements real exploits (10KBLAZE/CVE-2020-6207 gateway trust, CVE-2025-31324 VisualComposer JSP webshell, a described CVE-2026-58240 Message Server rogue-registration flaw, and CVE-2026-31431 root LPE via AF_ALG page-cache patching) to chart lateral movement across ABAP, Java, HANA, and BTP-connected systems. Its AutoPwn mode chains scan → exploit → enrich → propagate across an entire landscape, and it includes an engagement-report generator, SecStore/RSECTAB credential decryption, SSH lateral movement, hash cracking via hashes.com, and a Tier-3 "evasion" module (SAL slot disable, DBTABLOG purge) paired with an extensive, specific blue-team detection guide (SAL/SM20, DBTABLOG gaps, kernel-param diffing, OS/network IOCs) for defenders to catch it.
github.comrepoAdded 26 Sep 2026🛡️ Security - Chocapikk/CVE-2026-21858
A GitHub PoC chaining two n8n CVEs into unauthenticated RCE: CVE-2026-21858 abuses a Content-Type confusion in the Form Trigger/Respond-to-Webhook nodes to read arbitrary files (e.g. /proc/self/environ, the SQLite database, and the config file), from which the attacker derives the JWT secret from n8n's encryptionKey and forges an admin session cookie. That admin access is then used to create a workflow exploiting CVE-2025-68613, an expression-injection sandbox bypass (`this.process.mainModule.require`) that yields command execution, all demonstrated with a working Python exploit script and Docker lab against n8n 1.65.0. It notes the exploit was developed independently of a prior Cyera/Dor Attias write-up on a related n8n chain and details the specific vulnerable workflow pattern (file-upload form + binary Respond node) required for exploitation.
github.comrepoAdded 26 Sep 2026🛡️ Security - git-pkgs — dependency history & supply-chain analysis for git repos
git-pkgs is a Go rewrite of a Ruby tool that adds a git subcommand for tracking dependency changes across a repository's history, indexing manifests/lockfiles from 36+ package managers (npm, RubyGems, Cargo, PyPI, Maven, Composer, Go modules, etc.) into a local SQLite database. Beyond history/blame/diff, it offers supply-chain security commands: `vulns` (OSV-based CVE scanning with SARIF output for GitHub code scanning, plus blame/praise/exposure for remediation metrics), `licenses` (with drift detection and CI-friendly exit codes), `deprecated`, `provenance` (trusted-publishing/attestation checks), `integrity` (lockfile hash drift detection), `maintainers`/`health` (via ecosyste.ms metadata), and `sbom` export in CycloneDX/SPDX. It also supports a dependency-aware `bisect` to find when a vulnerability, license change, or capability (e.g. network access) was introduced, and ships GitHub Actions for CI integration.
github.comrepoAdded 25 Sep 2026🛡️ Security - Lonkero — Rust web vulnerability scanner (v3.7, AI agent mode)
Lonkero is an open-source Rust web vulnerability scanner (v3.7) combining 125+ context-aware scanners with an AI agent mode that drives targeted scans via natural-language conversation (using Claude, GPT, or local Ollama models). Notable techniques include a browser-free "proof-based" XSS engine that mathematically proves exploitability from reflection context + escape behavior, an "OOBZero" engine for detecting blind SQLi/SSRF/XXE via Bayesian multi-channel statistical inference and Pearson-correlated timing attacks without external callback infrastructure, Next.js middleware-bypass detection (CVE-2025-29927, CVE-2024-34351), AWS Cognito user-enumeration checks, and a scanner module that detects invisible prompt-injection payloads hidden in README.md files targeting AI coding assistants.
github.comrepoAdded 21 Sep 2026🛡️ Security - CVE-2026-26980 — Ghost CMS Content API unauthenticated blind SQLi lab
A Docker-based exploitation lab for CVE-2026-26980, an unauthenticated blind SQL injection in Ghost CMS's Content API (versions before 6.19.1). The bug lives in slug-filter-order.js, where slug values from the array-notation filter syntax (filter=slug:['value']) are interpolated unsanitized into an ORDER BY CASE statement, letting NQL's single-quote-wrapped literals smuggle raw SQL past input validation; since MySQL treats || as OR and empty strings as falsy, attackers get a clean boolean oracle to extract data (e.g. admin email/password hash) from any Ghost site using only the publicly embedded Content API key. The repo includes exploit.py for full setup/verify/extract, a docker-compose lab spinning up both vulnerable (6.18.0) and patched (6.19.1) Ghost instances, and also mentions a second patched bug (jsonpath/static-eval prototype pollution in the {{#get}} Handlebars helper leading to RCE via themes).
github.comrepoAdded 21 Sep 2026🛡️ Security - watchTowr detection artifact generator for Splunk CVE-2026-20253
A Python script from watchTowr Labs that checks whether a Splunk Enterprise instance is vulnerable to CVE-2026-20253, a pre-auth RCE stemming from unauthenticated access to the PostgreSQL Sidecar Service's /v1/postgres/recovery/backup endpoint. It probes the endpoint and reports vulnerable/not-vulnerable based on the HTTP response code, without performing actual exploitation. Affected versions span Splunk Enterprise 10.0.0–10.0.6 and 10.2.0–10.2.3; 10.0.7, 10.2.4, and 10.4.0 are patched.
github.comrepoAdded 21 Sep 2026🛡️ Security - OWASP Agentic Skills Top 10 (AST10)
The OWASP Agentic Skills Top 10 (AST10) is a new security framework cataloging the 10 most critical risks in AI agent "skills" — the behavior layer that orchestrates multi-step tool use in OpenClaw, Claude Code, Cursor/Codex, and VS Code. It documents real 2026 incidents (the ClawHavoc registry-poisoning campaign with 1,184 malicious skills, Snyk's ToxicSkills audit of 3,984 skills finding 36.82% flawed, CVE-2025-59536/CVE-2026-21852 RCE in Claude Code project files, and CVE-2026-28363 ClawJacked WebSocket hijacking) and proposes a Universal Skill Format (YAML) with signing, permission allowlists, and identity-file protections to mitigate them, mapped to CSA's MAESTRO 7-layer threat model.
github.comrepoAdded 18 Sep 2026🛡️ Security - Copy Fail (CVE-2026-31431): 9-year-old Linux kernel LPE found by Theori's Xint Code
A GitHub repository from Theori's Xint Code team detailing CVE-2026-31431, a Linux kernel local privilege escalation bug ("Copy Fail") that had gone undetected for roughly nine years. The researchers confirmed exploitability across current production kernels including Ubuntu 24.04 LTS (6.17.0-1007-aws), Amazon Linux 2023 (6.18.8-9.213.amzn2023), RHEL 10.1 (6.12.0-124.45.1.el10_1), and SUSE 16 (6.12.0-160000.9-default).
github.comrepoAdded 17 Sep 2026🛡️ Security - ThreatIntel-Aggregator
ThreatIntel-Aggregator is a self-hosted FastAPI/Next.js platform that polls 60+ tiered security RSS feeds (CISA, Talos, Unit42, etc.), runs AI triage to score severity and tag MITRE ATT&CK TTPs, extracts IOCs/CVEs, and correlates findings against a RunZero asset inventory to surface org-level exposure. Its Detections module goes further: it catalogs AI-generated or locally-imported detection rules (KQL/Sigma/YARA/Suricata/SPL), statically validates them, runs AI-driven MITRE alignment checks against technique coverage, tracks detection "rot," and can sync Hunts/Analytics Rules to a live Microsoft Sentinel workspace. It's designed to run standalone with zero cloud dependency or fully integrated with Azure/Entra/Sentinel, with all storage in Postgres and auth via Entra SSO or a local API key.
github.comrepoAdded 22 Sep 2026, published 17 Sep 2026🛡️ Security - AI Agent Hacking Writeups
A GitHub-hosted, CC0-licensed index of 281 public writeups on attacks against AI agents, organized into six categories: indirect prompt injection, direct prompt injection/jailbreaks/guardrail bypass, MCP and agent tooling, AI platform/infrastructure bugs, classic web bugs in AI product surfaces, and AI used as an attacker's tool. Entries span 2021-2026 and include major disclosures like GeminiJack, ForcedLeak, Clinejection, CVE-2025-53773 (GitHub Copilot RCE), and dozens of Johann Rehberger/PromptArmor/qual1a writeups covering exfiltration, MCP OAuth flaws, and coding-agent sandbox escapes. Comes with an accompanying blog post "How to Hack AI Agents" and a scripted links.txt for automation.
github.comrepoAdded 22 Sep 2026, published 17 Sep 2026🛡️ Security - Markakd/Container_escape
A GitHub repository hosting target-specific proof-of-concept exploits for two Linux kernel vulnerabilities, CVE-2026-52910 and CVE-2026-80521 (the latter an AF_UNIX kernel bug also documented in a kernelCTF LTS exploit-chain submission), both usable to break out of container isolation. The project ships a QEMU/Docker-based disposable VM builder (pinned to specific Ubuntu cloud images and kernel versions) so the destructive PoCs can be compiled and detonated only inside throwaway guests rather than on real hosts.
github.comrepoAdded 2 Oct 2026, published 16 Sep 2026🛡️ Security - CVE-2026-42533 nginx heap buffer overflow PoC (pre-auth RCE via two-pass capture clobbering)
A public PoC repo for CVE-2026-42533, a pre-auth heap buffer overflow in nginx's two-pass string evaluation engine that occurs when a regex-based map directive using numbered captures ($1, $2) clobbers the shared r->captures state used by a regex location, causing a LEN/VALUE size mismatch. The overflow can corrupt an adjacent ngx_pool_cleanup_t structure to hijack a function pointer for RCE, or under-write to leak heap/libc pointers defeating ASLR; the repo ships exploit.py/leak.py/overflow.py plus a Docker test environment demonstrated at 10/10 reliability on Ubuntu 24.04 against nginx 0.9.6-1.30.3/1.31.2. It also documents the exact vulnerable config pattern, a config scanner link, and the fix (named captures or upgrade to nginx 1.30.4+/1.31.3+).
github.comrepoAdded 10 Sep 2026🛡️ Security - vet (SafeDep)
vet is an open-source CLI (from SafeDep) that scans package manifests, SBOMs, container images, and source repos across npm, PyPI, Maven, Go, RubyGems, Cargo, and Packagist to surface vulnerabilities, malicious packages, and license/quality issues. It cuts through CVE noise by analyzing actual code-usage evidence, queries SafeDep Cloud's threat-intelligence database for real-time malware detection (e.g. flagged packages like express-cookie-parser, eslint-config-airbnb-compat), and lets teams enforce security/license/OpenSSF-Scorecard policies as CEL expressions in CI/CD via SARIF/JSON/Markdown reporting.
github.comrepoPublished and added 7 Sep 2026🛡️ Security - bikini/exploitarium
Exploitarium is a consolidated GitHub archive of an independent researcher's proof-of-concept vulnerability writeups, merging over a dozen former standalone PoC repos into one. It covers diverse real-world targets including RustDesk session permission bugs, an OpenSSH agent lock provider bypass, a Redis VSET duplicate HNSW ID RCE, a QEMU CXL Type3 mailbox escape, Firefox native/backup NSS RCE PoCs, libssh2 CVE-2026-55200, Nextcloud federated share bearer token issues, and more. The author documents an AI-assisted fuzzing workflow (hand-typed PoCs, AI-drafted READMEs) and credits prior work on an objdump OOB write finding.
github.comrepoPublished and added 7 Sep 2026🛡️ Security - mukul975/cve-mcp-server
cve-mcp-server is a Model Context Protocol server that gives Claude direct access to 28 security tools spanning 24 APIs (NVD, EPSS, CISA KEV, OSV.dev, GitHub GHSA, MITRE ATT&CK, AbuseIPDB, GreyNoise, Shodan, VirusTotal, MalwareBazaar, ThreatFox, Ransomwhere, and more), fronted by a one-call triage_cve orchestrator. It computes a composite 0-100 risk score from CVSS, EPSS, KEV status, and PoC availability (with a hard CISA KEV override forcing CRITICAL/≥76), supports dependency scanning via OSV, IP/domain reputation lookups with private-IP blocking, and ships an SSVC v2 gated decision mode plus audit logging and XML-bomb protections via defusedxml.
github.comrepoPublished and added 7 Sep 2026🛡️ Security - The React Native Developer's Security Guide
A GitHub-hosted book focused entirely on securing the React Native developer's workstation and toolchain rather than the shipped app — covering the polyglot execution surface triggered by a single git clone/yarn/pod install (Ruby, CocoaPods, Xcode build phases/XCSSET, Gradle, gradle-wrapper.jar, keystores), CVE-2025-11953 (exposed Metro/RN dev server), ClickFix-style social engineering of developers, CI-as-extended-workstation risks, and Expo/EAS-specific supply-chain concerns. It ships alongside a separate companion repo of 119 Opengrep detection rules, each mapped to a specific chapter's attack technique, plus practical appendices like a safe-clone runbook and a file risk atlas for hardening teams.
github.comrepoPublished and added 5 Sep 2026🛡️ Security - h5i-dev/awesome-ai-agent-incidents
A curated GitHub corpus tracking real-world security incidents, CVEs, attack techniques, and defensive tools specific to autonomous AI agents — spanning prompt injection/goal hijacking, MCP client-side tool-metadata poisoning, the "Promptware Kill Chain" multi-stage attack model, MITRE ATLAS agentic techniques, and the OWASP Top 10 for Agentic Applications. It also documents the OpenClaw/ClawHub supply-chain incident (1,184 malicious skills confirmed by Antiy CERT) and links defensive projects like OWASP Agent Memory Guard for LangChain/LlamaIndex agent memory protection.
github.comrepoAdded 3 Sep 2026🛡️ Security - cyanheads/osv-advisory-mcp-server
osv-advisory-mcp-server is an MCP server that queries the OSV.dev vulnerability database, offering single-package version checks, batch audits of up to 1000 {name, ecosystem, version} tuples for SBOM/lockfile triage, and full advisory record fetch by OSV ID (GHSA/PYSEC/RUSTSEC/GO/DSA/DLA/CVE prefixes). It surfaces CVE aliases, CVSS vectors, derived severity labels, and CWE IDs, and is designed to chain into a companion nist-nvd-mcp-server for CVSS base scores, EPSS probability, and CISA KEV status. It ships as a keyless, no-API-key tool runnable via STDIO or Streamable HTTP, with a public hosted instance and Bun/npx/Docker install paths.
github.comrepoAdded 1 Sep 2026🛡️ Security - vibecheck
vibecheck is a free, open-source, client-side scanner that checks apps built with AI code generators (Lovable, Bolt, v0, Cursor, Claude Code) for common security holes: exposed Supabase Row Level Security / Firebase rules, secrets embedded in the client bundle (Stripe/AWS/DB keys), missing security headers, exposed .env/.git/source maps, unauthenticated LLM proxy or MCP endpoints, and email/TLS misconfigurations. It also scans public repos for cross-tenant IDOR patterns, committed secrets, an OSV.dev supply-chain check, a Dockerfile lint, and generates a CycloneDX SBOM; a companion CLI (tenant-guard) adds a live Postgres cross-tenant isolation test as a CI gate. The project cites CVE-2025-48757 (170+ Lovable apps found with RLS disabled) as motivation.
github.comrepoPublished and added 27 Aug 2026🛡️ Security - subScraper
subScraper is a self-contained, single-file (main.py) Python orchestrator that chains subdomain enumeration tools (Amass, Subfinder, Assetfinder, Findomain, Sublist3r) into httpx probing, screenshot capture, ffuf fuzzing, nuclei, and nikto scans, all driven from a live web UI with resumable job state, worker concurrency controls, and Docker packaging. It ships 34 custom nuclei templates for CVEs lacking official coverage and exposes a scoped, API-key-authenticated "bug bounty agent API" for programmatic recon and attack-surface queries against a target's scope.
github.comrepoPublished and added 27 Aug 2026🛡️ Security - Rekono
Rekono is an open-source pentesting automation platform that chains 19 hacking tools (Nmap, Nuclei, Metasploit, OWASP ZAP, Nikto, Gitleaks, SearchSploit, etc.) so that output from one tool feeds the next, automatically covering recon, service enumeration, vulnerability scanning, and exploit correlation. It deduplicates findings into a single attack-surface inventory per host/port, enriches CVEs with community context for prioritization, tracks fixed/reopened vulnerabilities, and supports team collaboration, scheduled scans, Telegram/email alerts, and report generation for engagements.
github.comrepoAdded 3 Sep 2026, published 27 Aug 2026🛡️ Security
Showing 30 of 56
Show more