- Show HN: Farol – A risk map of a pull request for the person who approves it
farol is a free, MIT-licensed CLI and GitHub Action that runs after an AI code review and gives the human approver a risk verdict (fast track, quick review, careful review) and a 0-100 score for a pull request. It uses the TypeScript type checker, go/types and Python ast to trace which pages, APIs and jobs a change reaches, and it adds diff coverage, security findings and contract breaks. It never executes or sends code.
 github.comrepoAdded 26 Oct 2026, published 25 Oct 2026🧠 AI
- Spectrmachina/Ztrust
ZTrust is a Python supply-chain scanner that checks manifests, lockfiles, source and GitHub workflows for vulnerable or malicious dependencies (via OSV.dev), typosquats, leaked secrets, unsafe lockfiles and risky CI patterns such as pwn requests and script injection. It outputs console, JSON and SARIF 2.1.0 and ships as a GitHub Action. It also includes a FastAPI bounty service using commit-reveal and shielded Zcash payouts for researchers.
github.comrepoAdded 27 Oct 2026, published 22 Oct 2026🛡️ Security - Sadra Majidi (@SadraMajidi04) on X
Impeccable is an open-source skill for AI coding agents that steers them away from generic UI output such as purple gradients and nested cards. It provides 24 commands (critique, audit, polish, typeset) and 61 detector rules that run without an LLM. It works with Claude Code, Cursor and Codex, and the repo is pbakaus/impeccable on GitHub. The source is a short tweet and gives no further detail.
 x.comrepoAdded 23 Oct 2026, published 22 Oct 2026🧠 AI
- Show HN: Omnara – Open-source alternative to Claude Managed Agents
Omnara is an open-source, self-hostable managed agent platform, an alternative to Claude Managed Agents and OpenAI's Agents API. It runs agents on any model (OpenAI, Anthropic, OpenRouter, Bedrock, LiteLLM, Ollama) and any machine, with Postgres-backed durable state, stateless workers, per-tool permissions, MCP, skills, memory, subagents, schedules and Slack, Discord and GitHub triggers. It ships a REST API, TypeScript SDK, CLI and Docker Compose setup.
github.comrepoAdded 23 Oct 2026, published 21 Oct 2026🧠 AI - Cyber Detective💙💛 (@cyb_detective) on X
Python Cybersecurity Libraries is a curated GitHub list by Yogsec, shared in a post by cyb_detective. It groups Python libraries by task: network analysis, penetration testing, threat intelligence, reverse engineering and malware analysis, forensics and investigation, web application security, CTF, and machine learning for security. The tweet shows only the category names, not the individual libraries.
x.comrepoAdded 24 Oct 2026, published 21 Oct 2026🛡️ Security  Abhinav Singwal (@yogsec) on X
GetSubDomains is an open-source tool by yogsec that enumerates subdomains by querying crt.sh certificate transparency logs. It is aimed at the reconnaissance step of penetration tests and bug bounty work. The source is a short tweet pointing to a GitHub repository, so usage details and options are not given.
x.comrepoAdded 21 Oct 2026, published 19 Oct 2026🛡️ Security- AikidoSec/safe-chain
Aikido Safe Chain is an open-source local proxy and shell-alias wrapper for npm, yarn, pnpm, bun, pip, uv, poetry, pipx and pdm. It checks every package download, including deep dependencies, against the Aikido Intel malware feed and blocks malicious packages before install. It also enforces a configurable 48-hour minimum package age by suppressing too-new versions in registry metadata. It supports custom registries and a self-hosted malware-list mirror, and has CI/CD install recipes for GitHub Actions, Azure Pipelines, CircleCI, Jenkins, Bitbucket and GitLab.
github.comrepoAdded 17 Oct 2026🛡️ Security - mattpocock/skills — agent skills for engineers
mattpocock/skills is a collection of small, composable "agent skills" for software engineering that install into Claude Code, Codex, GitHub Copilot, Gemini CLI, Cursor, OpenCode, Devin, Windsurf, Amp and Pi via plugin managers or the `npx skills` CLI. It packages practices like interview-driven requirement gathering (/grill-me, /grill-with-docs), domain-model/glossary building, test-driven development with red-green-refactor (/tdd), bug diagnosis loops, codebase architecture improvement, ticket triage and spec-to-implementation workflows (/to-spec, /to-tickets, /implement, /implement-spec), splitting skills into user-invoked orchestrators and model-invoked reusable disciplines. It's built by Matt Pocock as an alternative to heavier process-owning frameworks like GSD, BMAD and Spec-Kit, aiming to keep engineers in control while giving coding agents better feedback loops and shared vocabulary.
github.comrepoAdded 8 Oct 2026🧠 AI - Dark Web Informer (@DarkWebInformer) on X
Infoooze is an open-source command-line OSINT reconnaissance toolkit (github.com/devxprite/infoooze) that consolidates common footprinting tasks into one CLI: username enumeration across platforms, email discovery, subdomain enumeration, port scanning, WHOIS/DNS lookups, IP/HTTP header analysis, EXIF metadata extraction, GitHub recon, and URL scanning/expansion. It automatically saves results, making it a lightweight all-in-one alternative to running several separate recon tools.
x.comrepoPublished and added 8 Oct 2026🛡️ Security  The Vulnerable MCP Project — MCP vulnerability database
The Vulnerable MCP Project is a curated, continuously growing database of security vulnerabilities and attack techniques specific to the Model Context Protocol ecosystem. Entries cover concrete CVEs (e.g. CVE-2025-68143/68144/68145 in Anthropic's mcp-server-git), transport-layer SDK flaws (cross-client response leakage, missing DNS rebinding protection in the official TypeScript/Python SDKs), unauthenticated/0.0.0.0-bound servers enabling RCE (MCPJam inspector, MCP Inspector, Grafana MCP), command/path injection in dozens of third-party servers (gemini-mcp-tool, mcp-server-kubernetes, Framelink Figma MCP, Zen MCP, filesystem-mcp), SSRF chains reaching cloud metadata (MarkItDown MCP, mcp-fetch-server), and a large set of AI-specific attacks: tool poisoning, trigger-phrase data exfiltration, prompt injection via GitHub issues, Jira and Google Docs, rug-pull tool mutation, and cross-server tool-name collisions. It functions as the de facto vulnerability registry for the MCP ecosystem, useful for tracking disclosed issues before patching or adopting third-party MCP servers.
 vulnerablemcp.inforepoAdded 6 Oct 2026🛡️ Security
- the_OSINT_rack (@the_OSINT_rack) on X
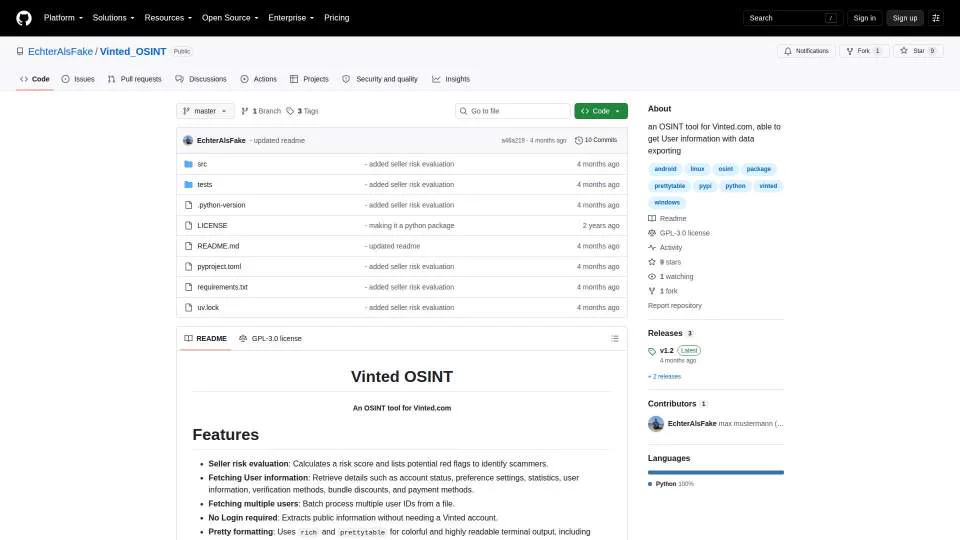
Vinted_OSINT is a GitHub tool by EchterAlsFake that performs open-source intelligence gathering against Vinted.com user profiles, pulling seller/buyer account information and computing a risk score to flag accounts likely run by scammers. It's aimed at buyers wanting to vet sellers before transacting on the second-hand marketplace.
x.comrepoPublished and added 4 Oct 2026🛡️ Security - Sigma r2026-07-01 — 20 new detection rules
GitHub release notes for Sigma r2026-07-01, the open-source detection-rule repository, adding 20 new rules (e.g. LSASS crash via Netlogon buffer overflow CVE-2026-41089, TanStack supply-chain attack indicators for Windows/Linux, RedTail cryptominer user-agent detection, AF_ALG kernel crypto API exploit indicator) and updating/fixing dozens of existing rules for ARM64 binary variants, file-sharing domain IOCs, and WMI-based reconnaissance/persistence detection. It's a routine but substantive update to a widely-used blue-team detection content pack.
github.comrepoAdded 3 Oct 2026🛡️ Security - https://github.com/Panniantong/Agent-Reach
Agent-Reach is a CLI and agent-"skill" layer that equips coding agents (Claude Code, Cursor, OpenClaw) with ready-made web-reading tool use: fetching arbitrary pages via Jina Reader, YouTube transcripts via yt-dlp, GitHub repos via gh CLI, Bilibili search, RSS via feedparser, and semantic web search via Exa through mcporter, with login-gated platforms (Twitter/X, Reddit, Xiaohongshu, Facebook, Instagram) added on request via cookies or OpenCLI browser sessions. Each platform module probes an ordered list of candidate backends and falls back automatically when one breaks (e.g. yt-dlp being blocked by Bilibili's anti-scraping), and an `agent-reach doctor` command reports which backend each channel is currently using. It positions itself as a "capability layer" that selects, installs and health-checks the right upstream tool for an agent rather than wrapping the reads itself.
github.comrepoAdded 2 Oct 2026, published 1 Oct 2026🧠 AI - rehan-remade/universal-modder
universal-modder is a set of Agent Skills, a CLI (um) and a shared knowledge base (field notes in knowledge/) that let AI coding agents such as Claude Code, Codex, Gemini CLI, Cursor, GitHub Copilot and OpenCode find a PC game's engine, reverse-engineer its code, build a working mod, generate art/3D/sound assets via the fal MCP server (or a local ComfyUI server), test the mod in the running game, and write a field note for the next agent. It ships worked examples — a weapon/boss pack for Terraria via tModLoader, a new civilization for Age of Empires II DE, and a real-time Minecraft-inside-GTA-V passthrough mod — each documented with a field note of exact versions, routes and gotchas, and agents can open pull requests to grow the shared knowledge base.
github.comrepoAdded 6 Oct 2026, published 30 Sep 2026🧠 AI  רון אברבוך (@Ron_averbuch) on X
Open-Dots is an open-source re-implementation of OpenAI's Dots computer-use agent, giving it browser, terminal and file control plus connectors to personal apps, and designed to work with any LLM rather than being locked to one vendor's model. It's announced via a tweet linking to the GitHub repo (github.com/Anil-matcha/Open-Dots).
x.comrepoAdded 30 Sep 2026, published 29 Sep 2026🧠 AI- https://github.com/dmdhrumilmistry/security-harness
security-harness is an open-source Claude Code plugin (also packaged for Gemini CLI, Codex and opencode) that orchestrates subagents — sh-recon, sh-hunter, sh-chainer, sh-verifier, sh-reporter — through a static-analysis pipeline covering 15 vulnerability classes (IDOR/BOLA, SQLi, XSS, SSRF, injection, auth, deserialization, path traversal, secrets, CSRF, XXE, open redirect, crypto, race conditions, file upload), producing README/JSON/SARIF/HTML/PDF reports with PoCs, CVSS and CWE/OWASP mappings. It also ships sh-pr-review, a per-PR merge-gate skill that posts inline findings and a commit status scoped only to code the PR itself introduced or aggravated, with caching, dedup via fingerprints, and a scheduled GitHub Action that keeps its per-class knowledge bases fresh by having one AI agent draft updates from allowlisted sources (OWASP, PortSwigger Research, CWE/CAPEC, HackerOne) while a separate adversarial reviewer agent fails-closed against prompt injection before auto-merge.
github.comrepoAdded 2 Oct 2026, published 29 Sep 2026🛡️ Security - Uncensored and Offensive Security AI Models Benchmark
A curated GitHub list of open-weight "uncensored" and security-fine-tuned LLMs intended for authorized red teaming, pentesting, and security research, covering models like WhiteRabbitNeo's DeepHat V2, BugTraceAI-CORE, CYBER-FROST, and several abliterated Qwen/GLM/DeepSeek variants. It explains the underlying techniques (abliteration per Arditi et al. 2024, QLoRA/DPO fine-tuning, GGUF/FP8 quantization) and links to Hugging Face model cards, benchmark suites (CyberBench, TrustedSec's LLM Attack Benchmark vs OWASP Juice Shop), and deployment platforms for running these models locally or via API.
github.comrepoAdded 2 Oct 2026, published 29 Sep 2026🛡️ Security - Uncensored and Offensive Security AI Models Benchmark
A GitHub README curating open-weight "uncensored" and security-fine-tuned LLMs (e.g. WhiteRabbitNeo's DeepHat V2, BugTraceAI-CORE, CYBER-FROST, CyberPal2.0, Lily-Cybersecurity-7B, Dolphin-Llama3-8B, Wizard-Vicuna-13B-Uncensored, huihui-ai's abliterated Qwen variants) with HuggingFace download links, quantization formats (GGUF, FP8, Q4_K_M, Q6_K), and training techniques used (SFT, QLoRA, DPO, abliteration, MoE/MTP architectures). It also includes a glossary explaining abliteration (orthogonalizing the refusal direction out of the residual stream, per Arditi et al. 2024) and references benchmarks like CyberBench and TrustedSec's LLM Attack Benchmark, making it a practical reference for anyone sourcing or deploying refusal-removed models.
github.comrepoAdded 2 Oct 2026, published 29 Sep 2026🧠 AI - Agent Threat Rules (ATR) — open detection-rule standard for AI agent threats
Agent Threat Rules (ATR) is an open, versioned YAML rule format (ATR-YYYY-NNNNN scheme) for detecting AI-agent runtime threats — prompt injection, tool-poisoning, malicious SKILL.md content, and MCP exchange abuse — evaluated by a reference TypeScript engine (with a Python wrapper) shipped as an npm/pip package, CLI, GitHub Action, and Docker scanner with SARIF output. The project positions itself as "Sigma for agent threats," maps rules to OWASP Agentic/LLM Top 10, MITRE ATLAS, and NIST AI RMF, and publishes an extensive (and unusually self-critical) benchmark suite against corpora like garak, PromptBench, and PromptInject, including documented harness bugs and withdrawn recall figures.
github.comrepoAdded 26 Sep 2026🛡️ Security - graygnatconsole/mcp-audit-tool
mcp-audit-tool is a dependency-light Python CLI that statically scans Claude Desktop, Cursor, Windsurf, Cline, Zed, and VS Code MCP configuration files for security issues, including hardcoded secrets, unpinned/rug-pull packages, pipe-to-shell installers, tool-poisoning via hidden instructions in tool descriptions, filesystem servers rooted at '/', and unauthenticated plaintext HTTP MCP endpoints. It auto-discovers configs across macOS/Linux/Windows, produces a security score/grade plus SARIF 2.1.0 output for GitHub Code Scanning, and is built around the OWASP MCP Top 10 categories with a CI/CD example that fails builds on severity thresholds. The roadmap adds live server probing over stdio/SSE for runtime rug-pull detection and an ML-based prompt-injection classifier for tool descriptions.
github.comrepoPublished and added 26 Sep 2026🛡️ Security - Chocapikk/CVE-2026-21858
A GitHub PoC chaining two n8n CVEs into unauthenticated RCE: CVE-2026-21858 abuses a Content-Type confusion in the Form Trigger/Respond-to-Webhook nodes to read arbitrary files (e.g. /proc/self/environ, the SQLite database, and the config file), from which the attacker derives the JWT secret from n8n's encryptionKey and forges an admin session cookie. That admin access is then used to create a workflow exploiting CVE-2025-68613, an expression-injection sandbox bypass (`this.process.mainModule.require`) that yields command execution, all demonstrated with a working Python exploit script and Docker lab against n8n 1.65.0. It notes the exploit was developed independently of a prior Cyera/Dor Attias write-up on a related n8n chain and details the specific vulnerable workflow pattern (file-upload form + binary Respond node) required for exploitation.
github.comrepoAdded 26 Sep 2026🛡️ Security - AgentSystemLabs/agent-office
agent-office is an open-source Node.js application that renders your team's projects as floors of a cartoon 3D office, where each Claude Code, OpenCode or Codex coding-agent worker sits at a desk with a visible terminal others can join. It wires agent workers directly into GitHub: an issues board and PR board with diff review, CI status and merge actions, a task queue that auto-hires workers into isolated git worktrees, one-click PR creation, live worker status via Claude Code/Codex hooks and an OpenCode plugin, and per-worker cost/token tracking against Claude plan limits. It also supports multi-agent meeting-room collaboration patterns such as debate, lead and team, map-reduce, red and blue, and review panel, where several agent workers jointly produce a file and open a PR, plus shared voice chat and screen sharing for the human team.
github.comrepoAdded 28 Sep 2026, published 26 Sep 2026🧠 AI - git-pkgs — dependency history & supply-chain analysis for git repos
git-pkgs is a Go rewrite of a Ruby tool that adds a git subcommand for tracking dependency changes across a repository's history, indexing manifests/lockfiles from 36+ package managers (npm, RubyGems, Cargo, PyPI, Maven, Composer, Go modules, etc.) into a local SQLite database. Beyond history/blame/diff, it offers supply-chain security commands: `vulns` (OSV-based CVE scanning with SARIF output for GitHub code scanning, plus blame/praise/exposure for remediation metrics), `licenses` (with drift detection and CI-friendly exit codes), `deprecated`, `provenance` (trusted-publishing/attestation checks), `integrity` (lockfile hash drift detection), `maintainers`/`health` (via ecosyste.ms metadata), and `sbom` export in CycloneDX/SPDX. It also supports a dependency-aware `bisect` to find when a vulnerability, license change, or capability (e.g. network access) was introduced, and ships GitHub Actions for CI integration.
github.comrepoAdded 25 Sep 2026🛡️ Security - https://github.com/davila7/claude-code-templates/tree/main/cli-tool/components/skills/security/security-threat-model
A directory within the davila7/claude-code-templates repo containing a "security-threat-model" Skill for Claude Code: a SKILL.md instruction file plus supporting agents and reference files that package a reusable threat-modeling workflow for the coding agent. It's an example of the emerging pattern of distributing structured, invocable skills (instructions + sub-agents + reference docs) that extend Claude Code's capabilities, rather than a security research artifact itself.
github.comrepoAdded 2 Oct 2026, published 25 Sep 2026🧠 AI - https://github.com/davila7/claude-code-templates/tree/main/cli-tool/components/skills/security/security-threat-model
A "security-threat-model" skill folder in the davila7/claude-code-templates repository, part of a library of reusable Claude Code skills/components. It packages a SKILL.md definition with supporting agent and reference files intended to let Claude Code agents carry out structured threat-modeling analysis as part of a development or security-review workflow.
github.comrepoAdded 2 Oct 2026, published 25 Sep 2026🛡️ Security - artemy-ccrsky/COM-Jungle
COM-Jungle is a GitHub repository of offensive security research notes on Windows COM (Component Object Model), written by Artemy Tsetsersky in 2026. Notes are ordered by tactic: how COM works, execution, trust boundaries and privilege escalation, lateral movement via DCOM, persistence, initial access, finding new classes, and detection and hardening. It advises recording build, bitness, token and session before generalising a CLSID result, and says detections should key on registration, load and process context rather than a single CLSID.
github.comrepoAdded 23 Oct 2026, published 23 Sep 2026🛡️ Security - https://github.com/akha-security/akca
AKCA is an open-source, Go-based Dynamic Application Security Testing (DAST) scanner that combines HTTP and headless-browser crawling, JavaScript/AST analysis, API spec import (OpenAPI, GraphQL, gRPC, etc.), and adaptive active testing across a very broad set of vulnerability classes including SQL injection, XSS, SSRF, IDOR/BOLA, SSTI, JWT/OAuth flaws, race conditions, and cloud/CI exposure. It emphasizes evidence-oriented verification — replaying promising signals against baselines, negative controls, and OAST callbacks before promoting them to findings — and exports Burp-style HTTP evidence in HTML, JSON, CSV, Markdown, and SARIF reports. Positioned as a transparent, single-developer alternative inspired by but not claiming parity with Acunetix, Invicti/Netsparker, or Burp Suite Professional.
github.comrepoAdded 2 Oct 2026, published 23 Sep 2026🛡️ Security - shai-hulud-detect: multi-ecosystem npm/PyPI/Composer/Crates/Go/Hex/RubyGems supply-chain worm scanner
shai-hulud-detect is a dependency-free Bash scanner that checks projects against a 5,782-entry list of compromised npm, PyPI, Composer, Crates, Go, Hex, and RubyGems package versions, plus content-pattern indicators of compromise (malicious file hashes, C2 domains, dead-man's-switch artifacts, forged commits, suspicious lifecycle hooks) tied to the Shai-Hulud supply-chain attack waves. It supports single-project and bulk scanning, CI-friendly exit codes, JSON/log output for pipeline gating, and a --check-host mode to detect the May 2026 gh-token-monitor/kitty-monitor persistence daemons that wipe hosts if their monitored GitHub token is revoked (with a documented safe remediation order). Detection is read-only; new package entries are sourced from named threat-research firms (Socket, StepSecurity, Aikido, Snyk, JFrog, Wiz, Semgrep, SafeDep, GitGuardian, OX Security) and cited in PRs.
github.comrepoAdded 23 Sep 2026🛡️ Security - StellarFoundry/soroban-security-scanner
soroban-scan is an open-source, deterministic static analyzer for Stellar Soroban smart contracts and Rust projects. It ships 19 Soroban-aware detectors (SS-001 to SS-033) covering missing authorization, re-initialization, cross-contract call ordering, unchecked arithmetic and storage or resource misuse. Output includes JSON, SARIF 2.1.0 and GitHub annotations, with baselines and a PR-scanning Action. The project describes itself as early development.
github.comrepoAdded 28 Oct 2026, published 21 Sep 2026🛡️ Security - SnailSploit/Claude-Red
claude-red is a GitHub library of structured SKILL.md files for the Claude Skills system, each priming Claude with expert-level offensive-security methodology for a specific attack surface (SQL injection, shellcode, EDR evasion, ADCS abuse, wireless, IoT, cloud, mobile, fuzzing, etc.). Skills load on-demand from conversational triggers so context isn't spent on unused domains, and can be installed wholesale, per-category via sparse-checkout, or pasted directly into a system prompt. It's aimed at authorized red-team engagements, bug bounty triage, CTF prep, and operator training, building on Sahar Shlichov's offensive checklist collections.
github.comrepoAdded 21 Sep 2026🛡️ Security



Showing 30 of 140
Show more