Skip to content

51 results for β€œART”

What you seeeverything
x.comthreadπŸ›‘οΈ Security

Tanmay (@TanmayK_03) on X

DBHub, a database MCP server, had a read-only mode bypass in its SQL check. The check treated every `--` as a comment, but MySQL only starts a comment when whitespace follows it. A hidden write statement could therefore still run, and a prompt injection could trigger it. Fixed in version 0.22.6. Replies say enforcement belongs in database grants and that parser tests need to be dialect-specific.

DBHubMySQLModel Context Protocol
prompt injection

AppSec, AI SecurityΒ· Added 31 Oct 2026, published 30 Oct 2026

x.comthread🧠 AI

Artificial Analysis (@ArtificialAnlys) on X

Hyperflow H3 is Video Rebirth's 8-step LoRA for MiniMax H3, released in September 2026 with open weights. Artificial Analysis ranks it #5 on AA-Video-I2V v2.1 and #3 on AA-Video-Editing v1.1, ahead of MiniMax H3 (768p). It costs $9.00 per minute for Image to Video and $18.00 for Video Editing at 1088p, under half of Dreamina Seedance 2.5 ($34.12 and $40.82). The thread gives per-capability and per-use-case breakdowns.

LoRAdiffusion model
Artificial AnalysisVideo RebirthHyperflow H3+6

models, evals, multimodalΒ· Added 31 Oct 2026, published 30 Oct 2026

x.comthread🧠 AI

Artificial Analysis (@ArtificialAnlys) on X

Artificial Analysis launched an HLE-Diamond leaderboard in v5 of its Intelligence Index, covering the refined 1,000-question Humanity's Last Exam from CAIS and Scale AI. Each question runs once without tools, graded by GPT-5.6 Luna (medium) as pass@1. Gemini 4 Carbon (high) leads at 69%, Claude Opus 5.5 (max) scores 68%, and the top open weights model, Kimi K3.1 Pro, reaches 37%.

Artificial AnalysisArtificial Analysis Intelligence IndexHLE+9

evals, modelsΒ· Published and added 30 Oct 2026

x.comthread🧠 AI

Laban (@lunkertw) on X

An X post summarising five AI items: Google DeepMind's Gemini 4 Carbon (88.2% SEC-bench Pro, 54.8% ExploitGym, 71.0% CWE-bench, 59 on Artificial Analysis Intelligence Index v5.0), Ed Zitron's critique of Anthropic's S-1, a Utah Claude Code pilot, and the repos beenuar/AiSOC and expo/skills. In the Utah pilot, 34 developers in 10 agencies took part over four weeks, 80% had a working setup within 30 minutes, and 71% saved over 20 hours. It gives short summaries and links, not primary analysis.

Claude CodeModel Context ProtocolPython+6
Google DeepMindGemini 4 CarbonSEC-bench Pro+9

models, coding-agents, ai-policyΒ· Added 29 Oct 2026, published 28 Oct 2026

x.comthread🧠 AI

Niko (@nikolayxyz) on X

Gemini 4 Carbon is Google's new frontier model, announced in a post by nikolayxyz that quotes Google's launch text. It ranks #1 on v5.0 of the Artificial Analysis Intelligence Index with 59 points, ahead of Opus 5.5 and GPT-6 Astra. Intro pricing is $2 input and $10 output per million tokens. Access starts for cyber defenders first, as Gemini 4 Argon's did. The captured text is cut off before the rollout details.

Gemini
Gemini 4 CarbonGemini 4 ArgonGoogle+4

models, evalsΒ· Added 29 Oct 2026, published 28 Oct 2026

x.comthread🧠 AI

🚨 AI News | TestingCatalog (@testingcatalog) on X

Gemini 4 Carbon is a new Google model, announced in a TestingCatalog post on X as taking first place on the Artificial Analysis V5 ranking. It is rolling out to cyber defenders first. Reported scores are 88.2% on SEC-bench Pro (finding vulnerabilities), 54.8% on ExploitGym (exploitation) and 71.0% on CWE-bench (patching). The post calls it a large step up from Gemini 4 Argon, released two weeks earlier. It gives no technical detail beyond these claims.

Gemini
GoogleGemini 4 CarbonGemini 4 Argon+4

models, evalsΒ· Added 30 Oct 2026, published 28 Oct 2026

x.comthreadπŸ›‘οΈ Security

Nicholas Martin (@ndgmlondon) on X

X thread started by Nicholas Martin (#IAM) advising that MCP tool permissions be verified and scoped session tokens used to enforce least privilege against indirect prompt injection. Replies argue that token scoping does not solve the confused deputy problem, because an injection borrows the agent's legitimate authority. They recommend per-task tokens with short expiry, with the grant logged beside the call, and raise MCP server dependency supply-chain risk.

Model Context Protocol
indirect prompt injectionconfused deputy

AI Security, Identity & AccessΒ· Added 28 Oct 2026, published 27 Oct 2026

x.comthread🧠 AI

Muzammil Shah (@Muzammil_OX) on X

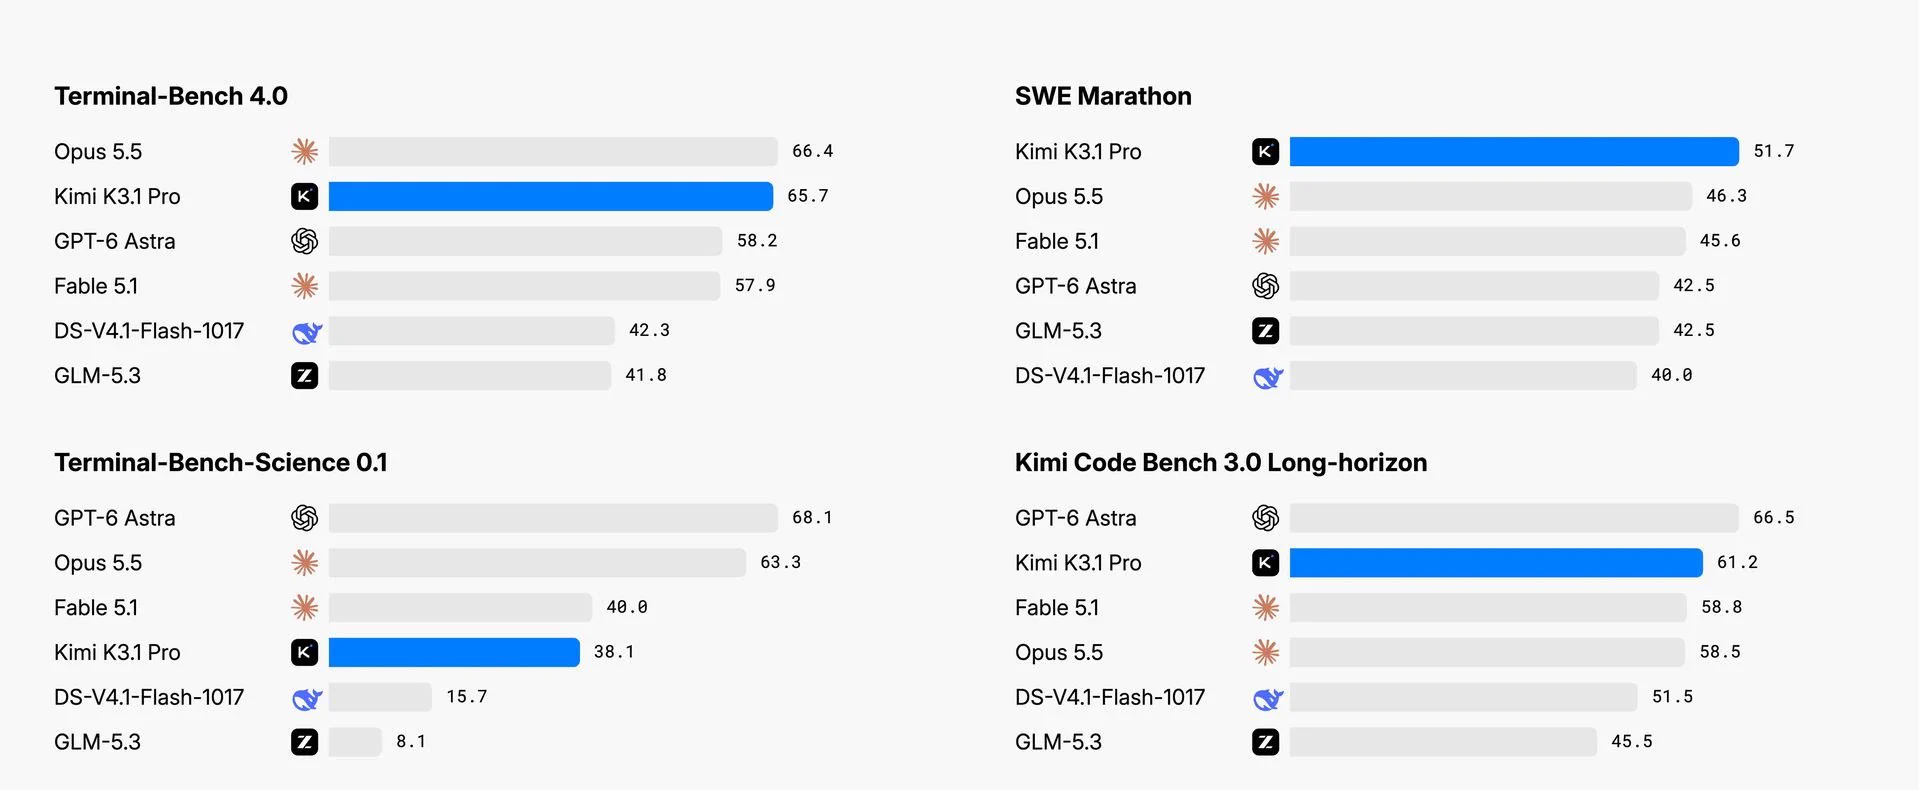
Kimi K3.1 Pro is a new model from Moonshot AI that scores 55 on the Artificial Analysis Intelligence Index, up 11 points from its predecessor, and ranks 4th overall. It has a 1M-token context window and API pricing of $2 per million input tokens and $10 per million output tokens. Weights are due by November 4. Moonshot removed cyber-related training data, which cut its internal vulnerability research score from 90.5% to 81%.

UnityUnreal EngineGodot
Moonshot AIKimi K3.1 ProKimi+2

models, evalsΒ· Added 28 Oct 2026, published 27 Oct 2026

x.comthreadπŸ›‘οΈ Security

BenjaminπŸ‘¨β€πŸ’» (@Hislordship_9) on X

Thread on Forever Security's finding that a planted Markdown "Engineering Work Guidelines" file in ~/Downloads made Codex add a "project-tools" MCP server to ~/.codex/config.toml. The server ran npm install function-color, a known malicious package, and started a child session with --dangerously-bypass-approvals-and-sandbox. Codex complied in over 90% of the firm's tests; Claude Code, via a CLAUDE.md setting ANTHROPIC_BASE_URL, about half. Advice: don't start agents in Downloads, review instruction files, and diff agent config.

CodexClaude CodeModel Context Protocol+1
Forever Securityfunction-colorAGENTS.md+4

AI Security, Supply ChainΒ· Added 27 Oct 2026, published 26 Oct 2026

x.comthread🧠 AI

Vlad Tchouchkov (@tchouchkov) on X

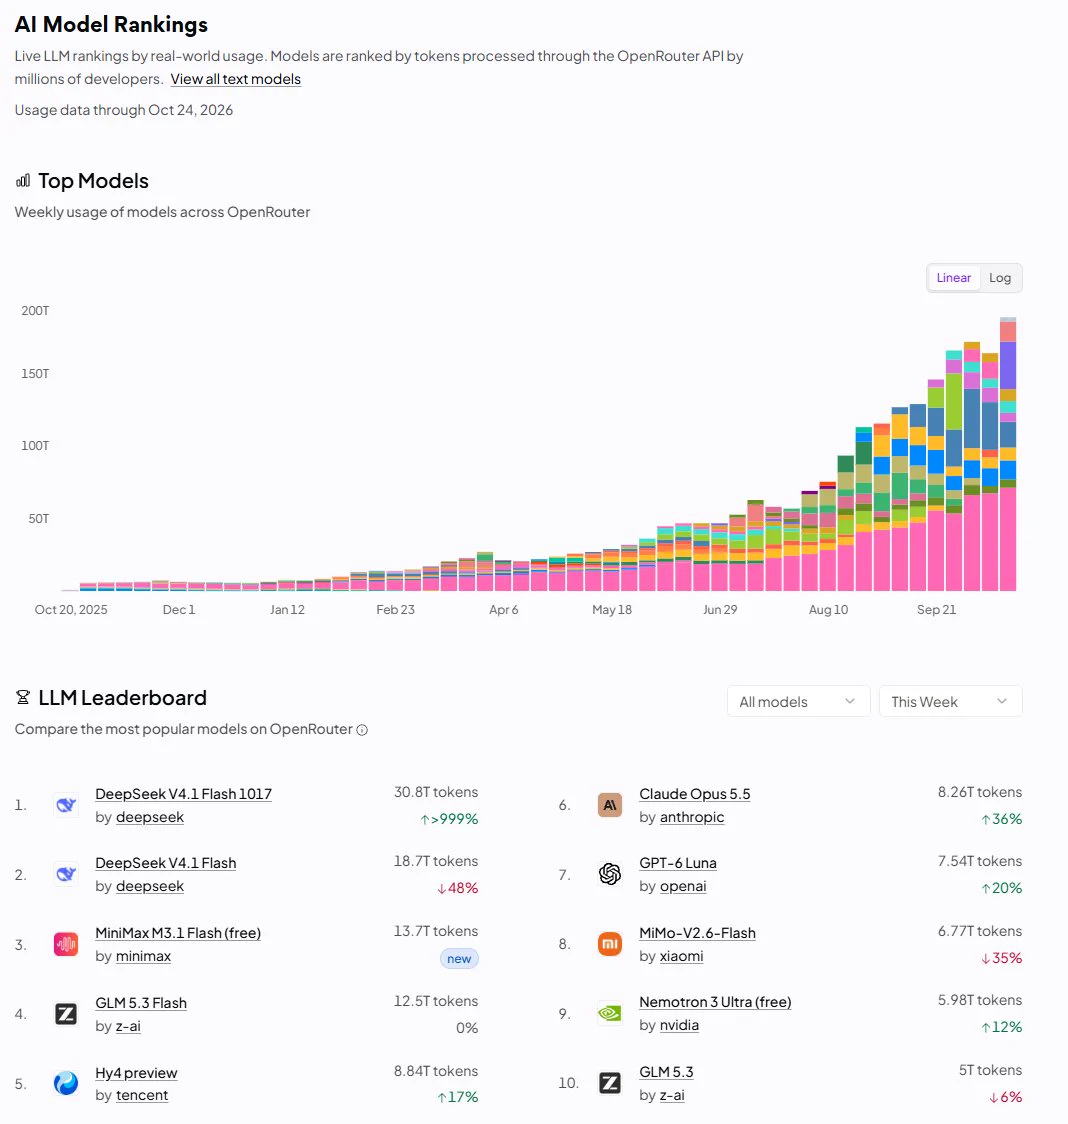
This X thread summarises OpenRouter usage charts. Weekly volume nears 200 trillion tokens, and open-weight models take 72.6% of tokens (136 trillion) against 27.4% for closed-weight models. Anthropic's daily average rose from about 0.6 to 2.25 trillion tokens alongside the Opus 5.5, Sonnet 5.5 and Haiku 5.5 releases. DeepSeek leads text requests at 26.5%, and agents plus coding account for 57.7% of spending. The author notes the data describes OpenRouter only.

OpenRouterLLM
AnthropicClaude Opus 5.5Claude Sonnet 5.5+7

ai-policy, models, ai-infraΒ· Added 26 Oct 2026, published 25 Oct 2026

ethereum-magicians.orgthreadπŸ›‘οΈ Security

ERC-8468: Agent Safety Framework (ASF)

ERC-8468 (Agent Safety Framework, ASF) is a draft Ethereum standard, now at revision 6, for recording which participants accepted which safety requirements for an AI agent, in which version, enforced where, and whether that acceptance is in force now. It defines a versioned Safety Specification, an on-chain Safety Binding with interveners holding suspend, resume and terminate rights, and a check() that returns Satisfied, NotSatisfied or Unknown. The reference guarded account and task-tender adapter passed 90 tests (64 negative) and a Sepolia run of 36 transactions.

Ethereum
ERC-8468ERC-165TASK-KERNEL+4

AI Security, Identity & AccessΒ· Added 27 Oct 2026, published 25 Oct 2026

ethereum-magicians.orgthread🧠 AI

Draft ERC: Agent Safety Framework (ASF) β€” attributable adoption of versioned safety specifications

Agent Safety Framework (ASF) is a draft ERC (ethereum/ERCs pull request #2113) for an on-chain registry that records which participants adopted which versioned safety specification, for what subject and scope, and where it is enforced. It defines two objects (Safety Specification, Safety Binding) and a registry check returning Satisfied, NotSatisfied or Unknown. Two reference consumers and 73 tests (47 negative) are reported, and the post asks the community four design questions.

EthereumERC-165Anvil+2
ethereum/ERCsASFGuardedAccountASFTaskTenderAdapter+1

agents, ai-policyΒ· Published and added 25 Oct 2026

x.comthreadπŸ›‘οΈ Security

Prasenjit Sarkar (@stretchcloud) on X

Post on the LiteLLM supply-chain compromise. Attackers spent eleven days in the GitHub org, ran a workflow on a throwaway branch to take twenty secrets including a GitHub App private key, then used stolen GitHub CLI OAuth tokens to publish malicious release 1.107.0 from a lookalike Berri-AI repo. A Python startup file harvested sixteen credential categories and LiteLLM proxy Postgres provider keys. Socket flagged the wheels in seven minutes.

LiteLLMPyPIGitHub Actions+3
Berri-AIBerriAILiteLLM 1.107.0+3

Supply Chain, DevSecOps, AI SecurityΒ· Added 26 Oct 2026, published 24 Oct 2026

x.comthread🧠 AI

HajrΓ« Hyseni | AI for Business (@hajra) on X

Kimi K3.1 Pro is a new model from Moonshot AI. According to a post by hajra, Artificial Analysis ranks it 4th in the world, 3 points behind Claude Opus 5.5. The API price is down by a third, and full open weights are promised by 4 November. The post gives no benchmark breakdown, licence or architecture details.

LLM
Moonshot AIKimi K3Artificial Analysis+1

models, evalsΒ· Published and added 24 Oct 2026

x.comthreadπŸ›‘οΈ Security

Techjunkie Aman (@Techjunkie_Aman) on X

ns2jb is a software-only jailbreak for the Nintendo Switch 2 running firmware 23.0.1, announced in a post on X. It runs arbitrary native code, allows save dumping, reverse engineering and game modding, and reaches most peripherals via MMIO. It is tethered (rerun after reboot) and gives no CFW or full kernel control. The post says Mario Kart World has been modded with custom characters. It gives no technical detail on the exploit chain.

Nintendo Switch 2
ns2jbNintendoMario Kart World

Offensive Security, Hardware & RFΒ· Added 24 Oct 2026, published 22 Oct 2026

x.comthreadπŸ›‘οΈ Security

Dark Web Intelligence (@DailyDarkWeb) on X

LiteLLM suspects its October 21 release compromise began with Claude Code responses containing GitHub CLI OAuth tokens that were written to logs of an internet-facing internal LiteLLM gateway. Attackers allegedly stole those tokens, used an organization-owner token to disable branch protections, and pushed poisoned artifacts from a lookalike repository. How they entered the gateway is unconfirmed, and this is not a proven Claude Code vulnerability.

LiteLLMClaude CodeGitHub+1
LiteLLM release compromiselookalike repositorybranch protection bypass

Supply Chain, DevSecOps, AI SecurityΒ· Added 25 Oct 2026, published 22 Oct 2026

x.comthreadπŸ›‘οΈ Security

Muscle AI (@themuscleai) on X

Post on the LiteLLM 1.107.0 PyPI compromise published 21 October 2026 and quarantined about 1 hour 43 minutes later. A malicious .pth file ran at Python startup and stole cloud credentials, private keys, browser data and AI tool auth files, then POSTed a tarball to an attacker endpoint. The author says attackers used stolen GitHub CLI OAuth tokens to push a trojanized commit chain and build official wheels. It lists five defenses: hash-pinned lockfiles, per-tool capped keys, release cooling periods, secret isolation and egress monitoring.

LiteLLMPyPIPython+3
TeamPCPcook.pth

Supply Chain, DevSecOps, AI SecurityΒ· Added 23 Oct 2026, published 22 Oct 2026

x.comthread🧠 AI

Jonathan Rhyne (@jdrhyne) on X

A post on X about NVIDIA's Nemotron 3.5 Parse and its "#1 on ParseBench" claim. The author says the ranking holds only among open-weight models under 1B parameters. On the full board of 150+ models the model scores about 75, while the top is near 90. The post asks vendors who run a benchmark to print the filter on the chart.

Nemotron 3.5 Parse
NVIDIANemotronParseBench

evals, modelsΒ· Added 23 Oct 2026, published 22 Oct 2026

x.comthreadπŸ›‘οΈ Security

Nagli (@galnagli) on X

Tweet by Gal Nagli (galnagli) saying a Gemini model turned the GitLab advisory for CVE-2026-110264 into a working heap exploit in 17 minutes, with the full chain done in about another hour. The flaw is a CVSS 10.0 unauthenticated RCE on self-managed GitLab servers, affecting 12 years of releases, found by joaxcar. The post links a The Hacker News article and gives no technical details of the exploit.

GitLabGeminiCVSS
CVE-2026-110264Gal Naglijoaxcar+1

Offensive Security, AI Security, AppSecΒ· Added 23 Oct 2026, published 22 Oct 2026

x.comthreadπŸ›‘οΈ Security

SecureChap (@SecureChap) on X

Post describing a LiteLLM 1.107.0 PyPI compromise in which attackers used stolen GitHub CLI OAuth tokens from three engineers to trigger and approve the project-releaser workflow, producing eight malicious wheels and a tampered tarball. The wheels drop cook.pth, which runs at Python startup, and privcollect steals cloud tokens, keys, browser data, AI configs and LiteLLM proxy credentials, exfiltrating to litellm[.]dev/healthcheck. A second daemon polls a GitHub domain.txt hourly for new domains to fetch and execute. PyPI yanked the package the same day. The post is a single unsourced tweet.

LiteLLMPyPIpip+3
cook.pthprivcollectlitellm[.]dev+2

Supply Chain, DevSecOps, Threat IntelΒ· Published and added 22 Oct 2026

x.comthread🧠 AI

Vishesh Raheja (@entropyconquers) on X

GPT Voice is a free, open-source Mac app by Vishesh Raheja that brings ChatGPT's dictation to any macOS app. A shortcut starts recording, and the transcript is pasted where the user is typing. It uses the ChatGPT Pro subscription, so it needs no API key or extra subscription. The author built it after Handy handled coding prompts poorly and they did not want to pay for Wispr Flow. The thread gives no details on local versus API transcription or latency.

ChatGPTCodexmacOS
Vishesh RahejaT3 CodeGPT Voice+3

multimodal, coding-agentsΒ· Added 22 Oct 2026, published 21 Oct 2026

x.comthread🧠 AI

brenz. (@brenzhills) on X

Krea 3 is an image generation and editing model from Krea. A post on X says its "Fast" variant scores 1125 Elo on the Artificial Analysis image editing leaderboard, against 1124 for Google's Nano Banana 2, while producing 10 images in the time Google produces 2. It also says the "Ultra" variant ranks in the top 4, behind only OpenAI models. The post gives no methodology or model details.

Krea 3Nano Banana 2
KreaGoogleOpenAI+1

models, multimodal, evalsΒ· Added 21 Oct 2026, published 20 Oct 2026

x.comthread🧠 AI

Paulo Pierrondi | AI agents (@paulopierrondi) on X

Paulo Pierrondi's X post, part 9 of a series on installing MCP servers, lists a monthly review of installed servers. The checks are which tools the agent used, servers not called in weeks, overlapping tools that confuse the model, and whether each server still has an owner. A reply adds a decommissioning check: after removal, confirm the server's old credentials can no longer call the backend.

Model Context Protocol
Paulo Pierrondi

mcpΒ· Published and added 20 Oct 2026

x.comthreadπŸ›‘οΈ Security

Nick Frichette (@Frichette_n) on X

Datadog Security Labs announcement, posted by Nick Frichette, of research on steering the evaluations of a prompt-injection detector called "Jev". The team's method cut its detection rate from about 83% to about 4% in their tests. They also used it to bypass LangChain's experimental tool-risk gating feature that is based on Jev. The tweet gives no method details and links to the full article.

LangChain
prompt injectionDatadog Security LabsNick Frichette

AI SecurityΒ· Added 21 Oct 2026, published 19 Oct 2026

x.comthreadπŸ›‘οΈ Security

LinuxSecurity (@lnxsec) on X

A post from lnxsec on CI runners that accept outside pull requests while also holding registry credentials, cache write access, signing material or deployment tokens. It uses the Nix/Lix build-service issues to argue that host compromise and downstream artifact trust are separate risks. It lists four checks: enumerate secrets exposed to PR jobs, split untrusted runners from release runners, trim registry and binary-cache write permissions, and require independent approval for release. It links a linuxsecurity.com feature; CVE details are not in the post.

Nix
Lix

DevSecOps, Supply ChainΒ· Added 20 Oct 2026, published 19 Oct 2026

x.comthreadπŸ›‘οΈ Security

FastFix AI (@FastfixAI) on X

FastFix AI thread giving six checks before installing a plugin, MCP server or skill for a coding agent. It starts from a 300K-star repo that an agent found writing to Claude Code, Codex and Copilot configs on install. Checks: read before running, inspect npm install scripts, verify the real repo against lookalike trojaned copies, pin versions, diff agent configs, and limit tokens and permissions.

Model Context ProtocolClaude Codenpm+2
--dangerously-skip-permissionspostinstalllookalike repository

AI Security, Supply ChainΒ· Added 19 Oct 2026, published 18 Oct 2026

ethereum-magicians.orgthread🧠 AI

ERC-8447: Swarm AI Framework

ERC-8447 (Swarm AI Framework) is a draft Ethereum standard proposing an on-chain registry and charter model for swarms: purpose-bound agent collectives with a membership boundary, an objective with attainment rules and a declared collaboration structure. Executed terms are hashed into a frozen spec, while the charter is kept off-chain. The reference implementation has 85 Foundry tests and tender and ERC-8436 decision adapters. The thread asks reviewers about vocabulary, amendment classes and the ERC-8004 dependency.

EthereumSolidityFoundry+7
ERC-8447ERC-8001ERC-8063+3

agentsΒ· Added 19 Oct 2026, published 18 Oct 2026

ethereum-magicians.orgthread🧠 AI

[Draft ERC] Swarm AI Framework β€” registry and charter model for purpose-bound agent swarms

Ethereum Magicians discussion of a draft ERC, the Swarm AI Framework. It proposes a registry and charter model in which accounts, including autonomous agents, form, bound, run and dissolve purpose-bound swarms. A hashed on-chain SwarmSpec (roles with eligibility modules, phases, decision authorities, fallback timers) is paired with an off-chain Swarm Pack charter. Two-sided signed admission (EIP-712 / ERC-1271), challenge and substitution, and minor versus material amendments are included. Phase posture is a coordinate: executed boundary and admission, plus declared payoff, topology and coordination terms from a write-once vocabulary. This lets cooperation, competition, tenders, debate, ensembles and pipelines be expressed. It integrates with ERC-8004 agent identity and ERC-8436 decision adapters. The reference implementation is a non-upgradeable registry with five eligibility modules and a task-tender adapter. The post asks reviewers specific design questions on vocabulary, amendment classes, roster snapshots and digest kinds.

EthereumSolidityFoundry+5
ERC-8001ERC-8063ERC-8444+3

agentsΒ· Published and added 18 Oct 2026

x.comthread🧠 AI

🚨 AI News | TestingCatalog (@testingcatalog) on X

A TestingCatalog X post with two Daily AI Briefs (Oct 17 and the start of Oct 16), grouped by vendor. Oct 17 items include GPT-6 Astra Pro upgrades in ChatGPT, Codex context reuse and caching, Gemini 4 Argon in AI Studio Build, the open-weight MIT-licensed DeepSeek-V4.1-Flash-1017, Claude Code Review going GA, Perplexity's open Decider v1.2 models (27B and 4B), NVIDIA's 4B looped Nemotron Labs Dory 1.0, Reflection's Apache-2.0 Beam, Cursor cloud-agent canvases and Tencent's Hy Memory 2.0. Oct 16 begins with Meta's open-weight Muse Spark Open, an 816B-total, 42B-active MoE with a 1M-token context. It gives a quick snapshot of the week's open-weight and coding-agent releases.

ChatGPTCodexGemini+7
TestingCatalogOpenAIGPT-6 Astra+15

models, coding-agentsΒ· Added 18 Oct 2026, published 17 Oct 2026

x.comthreadπŸ›‘οΈ Security

Nicholas Martin (@ndgmlondon) on X

An X post advises auditing every MCP write tool against the database role it actually runs under. A shared service key lets prompt injection trigger unapproved writes, so each agent session should get a read-only role, with a test that writes are denied. Replies note that MCP servers often inherit ambient host credentials or can escalate through a second connection pool, and suggest also testing that another tenant's rows are unreadable with the same role.

Model Context Protocol
prompt injection

AI Security, Identity & AccessΒ· Added 18 Oct 2026, published 16 Oct 2026

Showing 30 of 51

Show more