Skip to content

49 results for β€œMeta”

What you seeeverything
github.comrepoπŸ›‘οΈ Security

AikidoSec/safe-chain

Aikido Safe Chain is an open-source local proxy and shell-alias wrapper for npm, yarn, pnpm, bun, pip, uv, poetry, pipx and pdm. It checks every package download, including deep dependencies, against the Aikido Intel malware feed and blocks malicious packages before install. It also enforces a configurable 48-hour minimum package age by suppressing too-new versions in registry metadata. It supports custom registries and a self-hosted malware-list mirror, and has CI/CD install recipes for GitHub Actions, Azure Pipelines, CircleCI, Jenkins, Bitbucket and GitLab.

Aikido SecuritynpmPyPI+3
Aikido IntelSafe Chain

Supply Chain, DevSecOpsΒ· Added 17 Oct 2026

huggingface.corepo🧠 AI

Meta Muse Spark Open (816B-A42B) open-weights model card

Model card for Meta Superintelligence Labs' Muse Spark Open, an open-weights, natively multimodal model with 816B total and 42B active parameters and a 1M-token context window. It targets coding and agentic work (tool use, long-horizon tasks, multimodal reasoning, synthetic data generation, LLM-as-judge). It ships in BF16 and NVFP4, needs about 700GB VRAM (NVFP4) or 2TB (BF16), runs on SGLang, vLLM, Transformers, TensorRT-LLM, Unsloth, llama.cpp and MLX, and supports a reasoning_effort setting. The Muse Model License requires "Built with Muse Spark Open" attribution and a separate agreement for Model-as-a-Service above $20M revenue. The card reports safety results against Kimi K3 on cyber, chem/bio and loss-of-control evals.

Hugging FaceTransformersvLLM+8
Muse Spark OpenMetaMeta Superintelligence Labs+15

models, multimodal, inferenceΒ· Added 17 Oct 2026

github.comrepo🧠 AI

Show HN: SolidCraft – Open-Source Parametric CAD in Rust (With MCP Support)

SolidCraft is an open-source parametric 3D CAD application written in pure Rust. It has constrained sketches with its own solver, a feature timeline, assemblies, sheet metal, and STEP/IGES/3MF/STL export. It runs on desktop (egui+wgpu), in the browser, and as a headless CLI. The built-in MCP server (`solidcraft-cli mcp`) gives agents tools such as execute, batch, inspect_design, measure, set_parameter, screenshot and export. They can model headless or drive the running app over a JSON-lines control channel. A rover with 3,323 timeline steps was built entirely through MCP, which shows agent-driven parametric modelling working at scale.

RustModel Context ProtocolClaude Code+5
SolidCraftSELENE

mcpΒ· Published and added 13 Oct 2026

x.comrepoπŸ›‘οΈ Security

Dark Web Informer (@DarkWebInformer) on X

Infoooze is an open-source command-line OSINT reconnaissance toolkit (github.com/devxprite/infoooze) that consolidates common footprinting tasks into one CLI: username enumeration across platforms, email discovery, subdomain enumeration, port scanning, WHOIS/DNS lookups, IP/HTTP header analysis, EXIF metadata extraction, GitHub recon, and URL scanning/expansion. It automatically saves results, making it a lightweight all-in-one alternative to running several separate recon tools.

GitHub

OSINTΒ· Published and added 8 Oct 2026

github.comrepoπŸ›‘οΈ Security

target/strelka

Strelka is Target's open-source, container-based real-time file scanning system for threat hunting, threat detection, and incident response, built in Go and Python. It runs 50+ scanners (YARA, PE parsing, encrypted ZIP cracking, entropy analysis, etc.) to extract metadata and content from files at enterprise scale, which can feed a SIEM for alerting on suspicious artifacts like an Emotet-laden encrypted ZIP payload.

DockerGoPython+1
Laika BOSSEmotet

Blue Team & DetectionΒ· Added 8 Oct 2026

vulnerablemcp.inforepoπŸ›‘οΈ Security

The Vulnerable MCP Project β€” MCP vulnerability database

The Vulnerable MCP Project is a curated, continuously growing database of security vulnerabilities and attack techniques specific to the Model Context Protocol ecosystem. Entries cover concrete CVEs (e.g. CVE-2025-68143/68144/68145 in Anthropic's mcp-server-git), transport-layer SDK flaws (cross-client response leakage, missing DNS rebinding protection in the official TypeScript/Python SDKs), unauthenticated/0.0.0.0-bound servers enabling RCE (MCPJam inspector, MCP Inspector, Grafana MCP), command/path injection in dozens of third-party servers (gemini-mcp-tool, mcp-server-kubernetes, Framelink Figma MCP, Zen MCP, filesystem-mcp), SSRF chains reaching cloud metadata (MarkItDown MCP, mcp-fetch-server), and a large set of AI-specific attacks: tool poisoning, trigger-phrase data exfiltration, prompt injection via GitHub issues, Jira and Google Docs, rug-pull tool mutation, and cross-server tool-name collisions. It functions as the de facto vulnerability registry for the MCP ecosystem, useful for tracking disclosed issues before patching or adopting third-party MCP servers.

Model Context ProtocolCursorKubernetes+3
CVE-2025-68143CVE-2025-68144CVE-2025-68145+3

AI Security, AppSecΒ· Added 6 Oct 2026

x.comrepoπŸ›‘οΈ Security

Dark Web Informer (@DarkWebInformer) on X

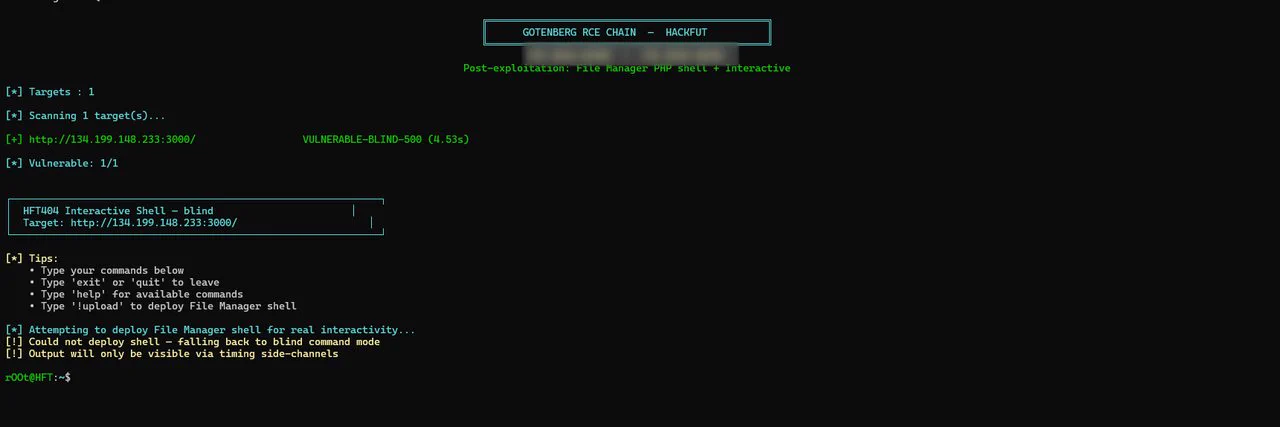
A public PoC chains CVE-2026-42589 and CVE-2026-40281 to achieve unauthenticated remote code execution against Gotenberg (a document/PDF-conversion microservice), abusing metadata injection flaws in the /forms/pdfengines/metadata/write endpoint. The tool supports vulnerability detection, interactive command execution, reverse shell delivery, and multi-target scanning against Gotenberg versions ≀8.30.1 (patched in 8.31.0).

Gotenberg
CVE-2026-42589CVE-2026-40281

Offensive Security, AppSecΒ· Published and added 5 Oct 2026

github.comrepoπŸ›‘οΈ Security

DeepZero

DeepZero is an open-source orchestration engine that lets researchers define vulnerability-research pipelines declaratively in YAML, handling parallel execution (ThreadPoolExecutor), resumable/fault-tolerant state, and LLM-assessment stages via LiteLLM/Jinja2 prompts. It ships example processors for Ghidra headless decompilation, LOLDrivers.io hash exclusion filtering, PE header/driver metadata extraction, and batch Semgrep scanning, with a dedicated pipeline for BYOVD kernel driver vulnerability research. An extensibility model lets users plug in custom Python processors referenced by path in the YAML config.

GhidraSemgrepLiteLLM+2
BYOVDLOLDrivers

Offensive Security, Malware & RE, AI SecurityΒ· Added 3 Oct 2026

github.comrepo🧠 AI

Show HN: Made an open-source Lego AI generator

ldraw-nova is an open-source agentic pipeline where an LLM agent (tested with models like Claude Opus 5.5 and GPT-6 Astra) takes a build prompt, reads LDraw-building instructions, and produces a plan.json describing a model's geometry. From that plan it writes a Python generator script that, when executed, outputs an LDraw (.mpd) 3D CAD source file, viewable in 3D/VR (Meta Quest 3) or exportable to Blender-editable glTF. The agent uses jev-rerank, a semantic search tool with reranking backed by TypeSafe's Jev System One model, to find suitable LEGO parts and example models, falling back to full-text search without an API key; it also uses headless rendering and collision/gap detection to self-inspect and iterate on designs.

DockerPythonBlender+2
TypeSafeJev System Onejev-rerank+13

agents, multimodalΒ· Added 3 Oct 2026, published 2 Oct 2026

github.comrepoπŸ›‘οΈ Security

CAIRN β€” Cisco Talos AI-Malware-Hunting Toolkit

CAIRN is a Cisco Talos research toolkit that identifies and attributes AI-integrated malware purely from VirusTotal metadata β€” no binary downloads or detonation β€” by running a tiered YARA ontology (T1/T2/T3) over composed scan text (AV strings, PE resources, Sigma/sandbox behavioral data, embedded URLs) and layering on sentence-transformer embeddings with HDBSCAN clustering for semantic family attribution. It has produced confirmed family reports for AI-malware such as PROMPTLOCK, LAMEHUG, PROMPTSTEAL, QUIETVAULT, CLOSEDQUORUM, and FRUITSHELL, each cross-verified by hands-on Talos reverse engineering before publication.

VirusTotalYARASQLite+2
PROMPTLOCKHONESTCUEPROMPTFLUX+7

AI Security, Threat Intel, Malware & REΒ· Added 30 Sep 2026

github.comrepo🧠 AI

Launch HN: Magnitude (YC S25) – Self-optimizing inference engine for agents

Magnitude is an open source local inference engine (Apache 2.0) that compiles and tunes its GPU/CPU kernels on the user's exact device before a model runs, claiming up to 2x faster decode than llama.cpp (92% faster on Metal, 19% on CUDA) with 27% lower memory per agent. It ships as a cross-platform desktop app with a bundled CLI and an OpenAI-compatible API, offering one-click connections to agent tools like Pi, OpenCode, Hermes, Codex, OpenClaw, Claude Code, and Cline, running fully offline on Apple Silicon, NVIDIA, AMD, or CPU-only hardware.

llama.cppCUDAOpenCode+5
MagnitudePiHermes+2

inferenceΒ· Published and added 30 Sep 2026

x.comrepoπŸ›‘οΈ Security

Andrea (Drego) Draghetti πŸ‘¨πŸ»β€πŸ’» 🎣 (@AndreaDraghetti) on X

Tosint v1.0.0 is an open-source Telegram OSINT tool for analyzing bots and chats, exporting message history and media. The new release adds richer JSONL metadata output, optional SHA-256 hashing of exported media, bot/user authentication support, and an automatic fallback from MTProto-based history retrieval to ID-scan mode when dealing with restricted chats.

TelegramTosint
Andrea Draghetti

OSINTΒ· Added 2 Oct 2026, published 30 Sep 2026

github.comrepoπŸ›‘οΈ Security

SpecterOps/Blacklight β€” local AI agent attack surface mapping toolkit

Blacklight is a SpecterOps toolkit for endpoint forensics on AI coding agents, split into Scout (bounded metadata/filesystem triage across Codex, Claude Code, Cursor, Antigravity CLI, and Grok that finds candidate session artifacts without reading their contents) and Session Analysis (a Python CLI that parses selected JSONL/SQLite session downloads from Codex, Claude Code, Cursor, and Antigravity CLI into ranked, redacted local reports). It's built for investigators who need to identify and review AI agent session history on a host β€” surfacing config, auth metadata, and high-value indicators β€” while explicitly leaving secret scanning to external tooling; paths are informed by SpecterOps' Endpoint AI Agent Abuse (EAA) technique catalog.

Claude CodeCodexCursor+3
Endpoint AI Agent Abuse (EAA) technique catalog

Blue Team & Detection, AI SecurityΒ· Added 27 Sep 2026

github.comrepo🧠 AI

MCP Python SDK v2.2.0

Release notes for MCP Python SDK v2.2.0, the reference Python implementation of the Model Context Protocol. Key changes: HTTP client redirects are now restricted to the same origin as the endpoint, idle Streamable HTTP sessions expire after 30 minutes (with a 10,000-session cap), OAuth authorization server metadata issuer checks are now enforced on the legacy discovery path, and new deprecation warnings push toward requiring explicit `issuer=` and `validate_token_resource` settings ahead of a 3.0 release.

Model Context ProtocolPython

mcpΒ· Added 26 Sep 2026

github.comrepoπŸ›‘οΈ Security

git-pkgs β€” dependency history & supply-chain analysis for git repos

git-pkgs is a Go rewrite of a Ruby tool that adds a git subcommand for tracking dependency changes across a repository's history, indexing manifests/lockfiles from 36+ package managers (npm, RubyGems, Cargo, PyPI, Maven, Composer, Go modules, etc.) into a local SQLite database. Beyond history/blame/diff, it offers supply-chain security commands: `vulns` (OSV-based CVE scanning with SARIF output for GitHub code scanning, plus blame/praise/exposure for remediation metrics), `licenses` (with drift detection and CI-friendly exit codes), `deprecated`, `provenance` (trusted-publishing/attestation checks), `integrity` (lockfile hash drift detection), `maintainers`/`health` (via ecosyste.ms metadata), and `sbom` export in CycloneDX/SPDX. It also supports a dependency-aware `bisect` to find when a vulnerability, license change, or capability (e.g. network access) was introduced, and ships GitHub Actions for CI integration.

npmSBOMOSV+3
CVE-2024-1234PURL

Supply Chain, DevSecOpsΒ· Added 25 Sep 2026

github.comrepoπŸ›‘οΈ Security

Supply Chain Firewall (Datadog)

Supply Chain Firewall (SCFW) is a Datadog-built CLI that wraps npm, pip, and poetry commands to inspect every package target against known-malicious/compromised package datasets (the open-source malicious-software-packages-dataset and OSV.dev) before installation proceeds, blocking or warning on hits. It ships as a single Go binary, can be aliased transparently into a developer's shell, and optionally reports run outcomes and enforces centralized allow/block policies through Datadog Code Security across a fleet, sending only package metadata (never source code) to Datadog.

npmPyPIGo+2
malicious-software-packages-dataset

Supply Chain, DevSecOpsΒ· Added 22 Sep 2026

github.comrepoπŸ›‘οΈ Security

Numbat

Numbat is a Go-based, single-binary endpoint agent from Perplexity AI that gives visibility into AI coding-agent activity (Claude Code, Codex, OpenClaw, and other CLI/IDE/gateway agents) by capturing events through local hooks, OTLP/HTTP logs, and on-disk session artifacts. It normalizes activity into one event model, evaluates it with a local CEL rule engine (including multi-step sequence rules like secret-read-then-egress), and can optionally block matched actions via synchronous pre-action hooks (deny/monitor decisions), with case bundles and SHA-256 manifests for forensic reconstruction. Example built-in rules detect cloud-metadata SSRF requests (169.254.169.254) and credential-exfiltration chains, mapped to MITRE ATT&CK technique tags.

Claude CodeCodexOpenClaw+2
T1048T1552T1567

AI Security, Blue Team & DetectionΒ· Published and added 5 Sep 2026

github.comrepoπŸ›‘οΈ Security

h5i-dev/awesome-ai-agent-incidents

A curated GitHub corpus tracking real-world security incidents, CVEs, attack techniques, and defensive tools specific to autonomous AI agents β€” spanning prompt injection/goal hijacking, MCP client-side tool-metadata poisoning, the "Promptware Kill Chain" multi-stage attack model, MITRE ATLAS agentic techniques, and the OWASP Top 10 for Agentic Applications. It also documents the OpenClaw/ClawHub supply-chain incident (1,184 malicious skills confirmed by Antiy CERT) and links defensive projects like OWASP Agent Memory Guard for LangChain/LlamaIndex agent memory protection.

Model Context ProtocolMITRE ATLASOpenClaw+1
OWASP Agent Memory GuardOWASP Top 10 for Agentic ApplicationsClawHub+3

AI SecurityΒ· Added 3 Sep 2026

github.comrepoπŸ›‘οΈ Security

age

age is a simple, modern file encryption tool, format, and Go library by Filippo Valsorda and @benjojo, offering small explicit keys, no config options, UNIX-style composability, and now built-in hybrid post-quantum encryption (ML-KEM + X25519) as of v1.3.0. It supports multiple recipients, passphrase encryption, SSH key (ed25519/rsa) recipients/identities, hardware tokens via age-plugin-yubikey, and an age-inspect command to view encrypted-file metadata without decrypting.

GoSSH
age-keygenage-inspectage-plugin-yubikey+4

otherΒ· Added 3 Sep 2026, published 31 Aug 2026

github.comrepoπŸ›‘οΈ Security

Rekono

Rekono is an open-source pentesting automation platform that chains 19 hacking tools (Nmap, Nuclei, Metasploit, OWASP ZAP, Nikto, Gitleaks, SearchSploit, etc.) so that output from one tool feeds the next, automatically covering recon, service enumeration, vulnerability scanning, and exploit correlation. It deduplicates findings into a single attack-surface inventory per host/port, enriches CVEs with community context for prioritization, tracks fixed/reopened vulnerabilities, and supports team collaboration, scheduled scans, Telegram/email alerts, and report generation for engagements.

NmapMetasploitNuclei+3

Offensive SecurityΒ· Added 3 Sep 2026, published 27 Aug 2026

github.comrepoπŸ›‘οΈ Security

Cyberful

Cyberful is an AI red-team CLI that orchestrates 316 cybersecurity tools (203 CLI apps/commands including Nmap, Metasploit, Nuclei, plus ZAP and Ghidra) through a multi-agent system: hypothesis workers map attack surfaces and test exploit paths, while a deterministic control plane enforces engagement scope, preserves evidence, and only surfaces independently reproduced vulnerabilities. Built for authorized penetration testing, code audits, and bug bounty hunting; ships a hardened agent-controlled browser, Docker-based runtime, offline MITRE ATT&CK snapshot, and CVE dictionary.

NmapMetasploitNuclei+3

Offensive Security, AI SecurityΒ· Published and added 25 Aug 2026

github.comrepoπŸ›‘οΈ Security

System Prompts Leaks

A community-maintained repository that archives leaked or extracted system prompts β€” the hidden instructions given to LLM chatbots before user input β€” captured verbatim from products including Claude/Claude Code, ChatGPT/Codex, Gemini, Grok, Cursor, Copilot, Perplexity, Meta AI, Mistral, DeepSeek, GLM, and others. It serves as a reference corpus for studying system prompt design, extraction techniques, and the system prompt leakage risk class, and is updated regularly as new prompts are exfiltrated from newer model releases.

ClaudeChatGPTGemini+3

AI SecurityΒ· Added 3 Sep 2026, published 3 Aug 2026

github.comrepoπŸ›‘οΈ Security

asgeirtj/system_prompts_leaks

This GitHub repository collects verbatim leaked/extracted system prompts β€” the hidden instructions and guardrails β€” from a wide range of AI products including Claude.ai, Claude Code, ChatGPT, Codex, Gemini, Grok, Perplexity, Microsoft Copilot, Cursor, Meta AI, Mistral, Kimi, DeepSeek, GLM, Qwen and others. It is updated regularly as new prompts are captured, and serves as reference material for AI red-teamers and researchers studying how vendors constrain model behavior and how those constraints can be extracted or bypassed.

ClaudeChatGPTGemini+3

AI SecurityΒ· Published and added 3 Aug 2026

github.comrepoπŸ›‘οΈ Security

Awesome Offensive AI Agentic Landscape

A comprehensively curated landscape document tracking the offensive AI agent space: ranked open-source pentesting/red-team agent projects (e.g. strix, shannon, VulnBot), uncensored offensive LLMs (Qwythos, WhiteRabbitNeo/DeepHat, BaronLLM) versus security-specialized but aligned models (Foundation-Sec, CyberSecQwen), Claude Code Agent Skills and MCP servers wrapping tools like Metasploit and BloodHound, 116 cross-referenced academic papers on pentest/vuln-discovery agents, capability benchmarks (Cybench, NYU CTF Bench, CyberGym), and a fact-checked Top-20 list of commercial AI pentesting vendors. It also covers competitions like the DARPA AI Cyber Challenge and Tencent's Intelligent Penetration Hackathon, positioning itself as a cross-merge of several other awesome-lists in this niche.

Model Context ProtocolClaude CodeMetasploit+3
DARPA AI Cyber ChallengeTencent Cloud Intelligent Penetration HackathonMythos

AI Security, Offensive SecurityΒ· Published and added 1 Aug 2026

github.comrepoπŸ›‘οΈ Security

Damn Vulnerable DeFi

Damn Vulnerable DeFi is a Foundry-based Solidity smart contract security playground featuring intentionally vulnerable challenges around flashloans, price oracles, governance, NFTs, DEXs, lending pools, smart contract wallets, timelocks, vaults, meta-transactions, and upgradeability. Each challenge presents a prompt and vulnerable contracts; solvers write a Foundry test exploiting the flaw to drain funds or bypass restrictions, making it a benchmark for both human auditors and automated security tooling.

SolidityFoundryEthereum

Learning, AppSecΒ· Published and added 31 Jul 2026

github.comrepoπŸ›‘οΈ Security

lockfale/OSINT-Framework

OSINT Framework is a curated, categorized index of free (mostly) open-source intelligence tools and resources, organized by data type (username, domain, IP, email, social media, etc.) and rendered as an interactive tree at osintframework.com. Each entry in the underlying arf.json is tagged with metadata like whether it requires local install (T), a Google dork (D), registration (R), or manual URL editing (M), plus richer fields such as input/output type, pricing, and opsec notes. It's a long-standing community reference for recon and investigation tradecraft across infosec and other fields.

OSINT Framework

OSINTΒ· Published and added 31 Jul 2026

github.comrepo🧠 AI

redhat-et/ripwire

Ripwire is an offline, single-binary CLI (with optional MCP server) that indexes a repository to give coding agents a ranked, deterministic call graph, task-oriented context bundles (--for, --pack-task), and edit-time checks (--edit-check, --quality-delta, --test-gate) that flag blast radius, contract breakage, and code-quality regressions. It installs skills for Claude Code, Codex, Cursor, Windsurf, Gemini, opencode and aider, and ships extensive self-published benchmarks (docs/EVALS.md, LocBench-style head-to-head comparisons against graph-database MCP servers like codebase-memory-mcp, repowise, graphify and aider) claiming large token and latency savings plus higher file@10 retrieval accuracy. The README includes a detailed field report on using it across a ~20-agent, ~1,500-file C++/Metal orchestration engagement.

Model Context ProtocolClaude CodeCodex+6
WindsurfGeminiaider+3

coding-agents, mcpΒ· Added 2 Oct 2026, published 29 Jul 2026

github.comrepoπŸ›‘οΈ Security

Bug Bounty Directory & MCP API

bug-bounties is a community-maintained directory of over 3,000 active bug bounty programs and vulnerability disclosure policies (VDPs), exposed via a public API and a Model Context Protocol (MCP) server. It lets researchers programmatically query scope, rewards, and program metadata, and lets AI coding agents like Claude Code look up bug bounty targets directly.

Model Context Protocol

Offensive SecurityΒ· Added 3 Sep 2026, published 29 Jul 2026

github.comrepoπŸ›‘οΈ Security

YuroGod/VMPStaticUnpacker

VMPStaticUnpacker is a Python tool that statically unpacks VMProtect-protected Windows PE binaries without executing them, supporting both the legacy plaintext PACKER_INFO metadata format and the compact rotating-XOR format seen in VMProtect 3.9.5 PE32+ samples. It recovers the destination key by XORing the encoded destination with the first packed section's RVA and rolling the key with ROL32(key,7), then validates candidate tables and LZMA streams before rebuilding a memory-image PE for static analysis. It does not devirtualize protected code, recover the original entry point, strip the VMProtect runtime, or fix imports.

VMProtectPythonWindows
oureveryday/VMPUnpacker

Malware & REΒ· Added 2 Oct 2026, published 29 Jul 2026

github.comrepoπŸ›‘οΈ Security

DevCop95/shodan_reconsx

recons101x (shodan_reconsx) is a passive-by-default Python CLI that enumerates hostnames published to certificate transparency logs via ctl.shodan.io, requiring no Shodan API key. It supports optional active features β€” DNS resolution, TCP/HTTP reachability probing on ports 443/80, bounded live scans, and certificate metadata enrichment β€” with status states (DNS_ONLY, TCP_REACHABLE, HTTP_REACHABLE, STALE), JSON/TXT output, and safeguards like --max-time, --active-only, and explicit warnings to only scan authorized domains.

PythonShodanPowerShell

OSINTΒ· Added 30 Sep 2026, published 29 Jul 2026

Showing 30 of 49

Show more