 endorlabs.comarticle🛡️ Security
What We Can Learn About GitHub Actions Security from the Trivy Breach | Endor Labs
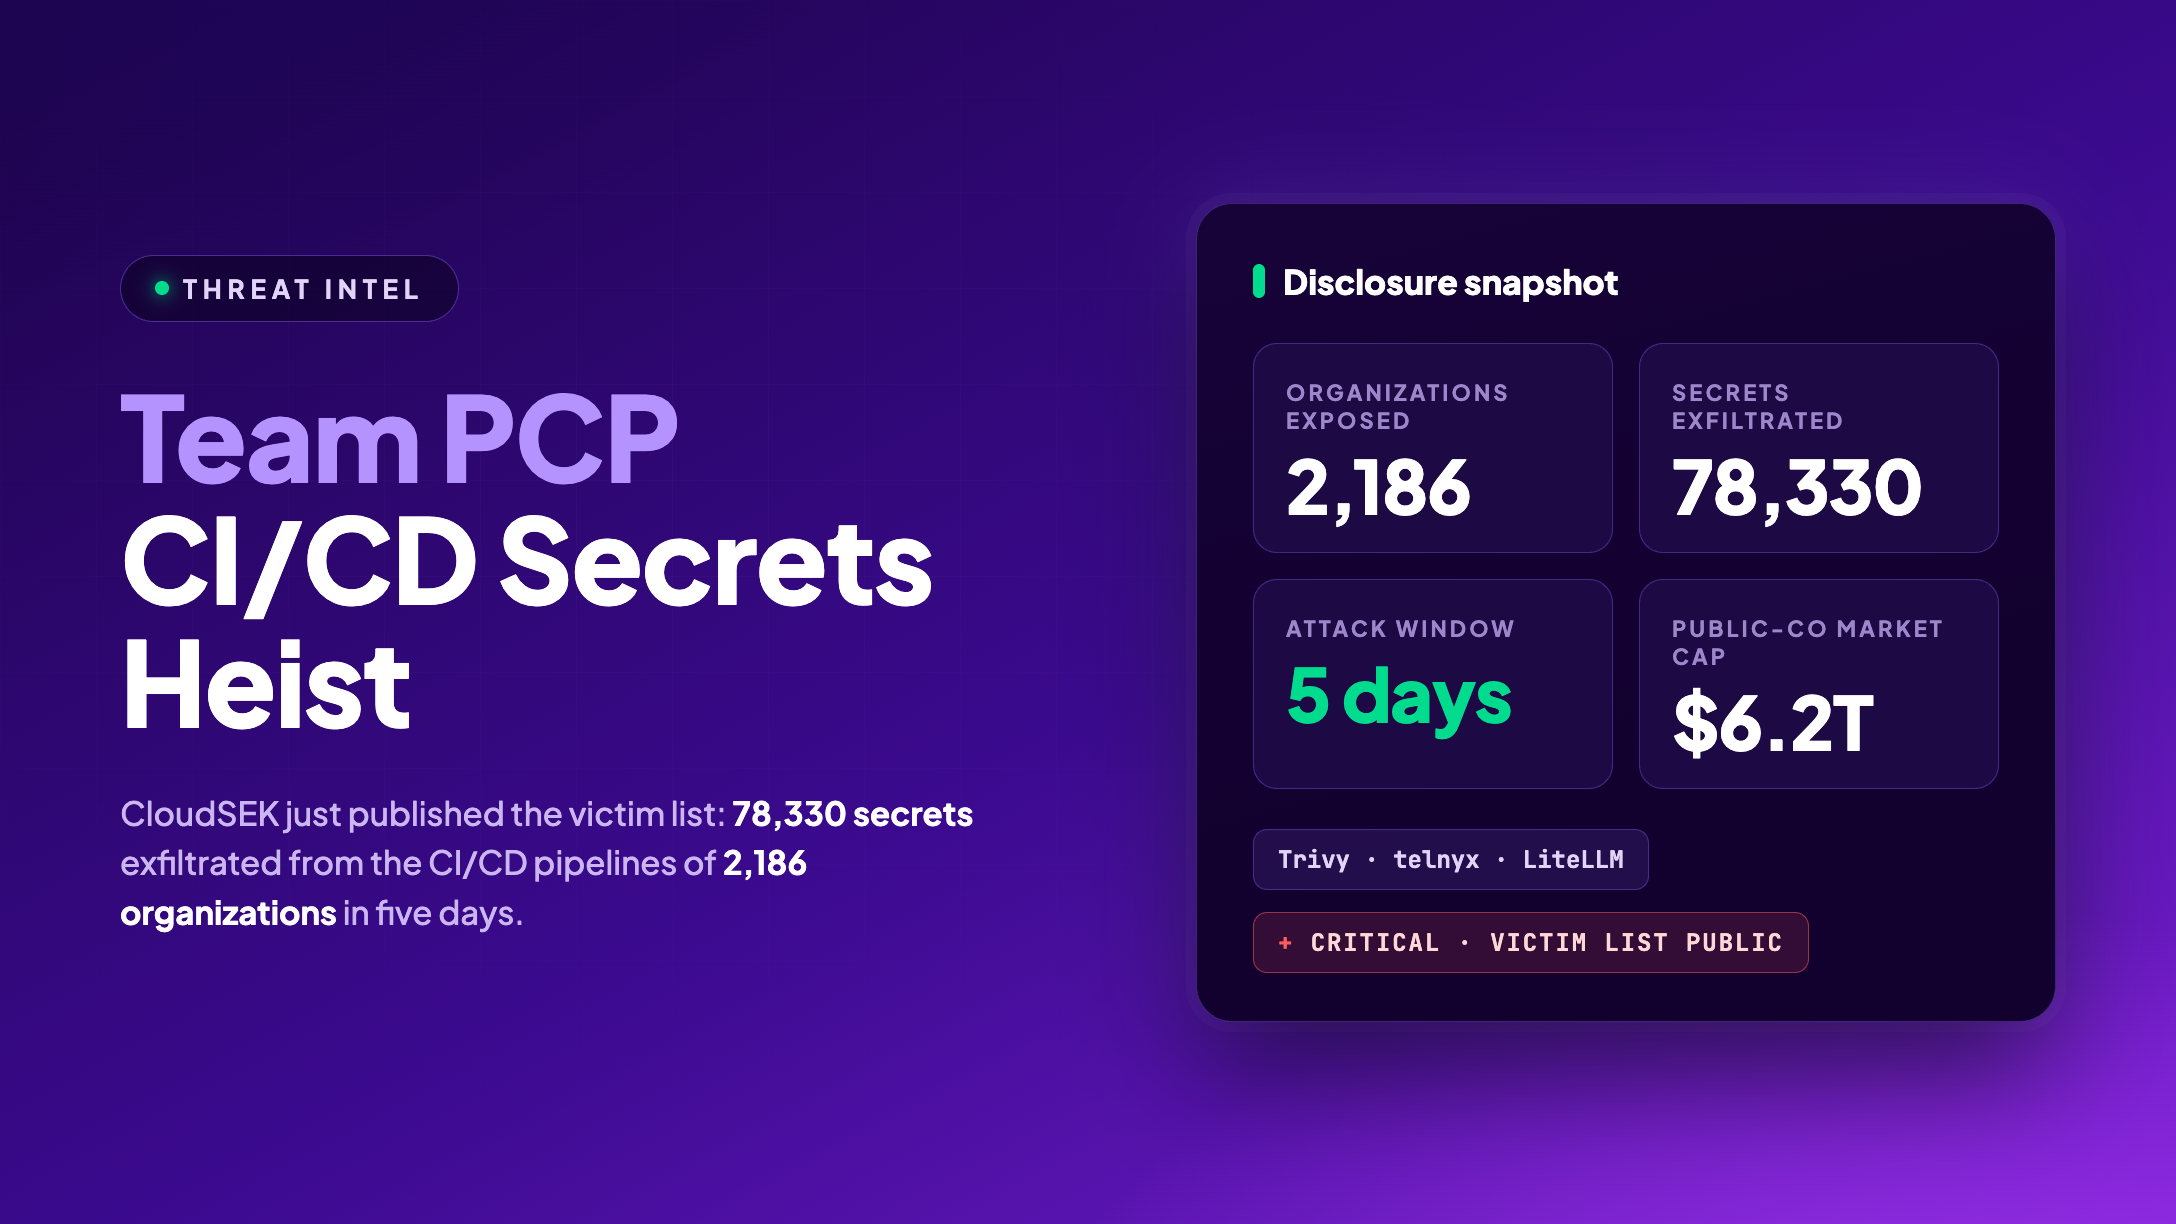
Endor Labs analyzes the March 2026 Trivy compromise (CVE-2026-33634, CVSS 9.4). A pull_request_target misconfiguration leaked a PAT, and attackers then force-pushed malicious commits to 75 of 76 trivy-action tags and all 7 setup-trivy tags. The TeamPCP credential stealer harvested SSH keys, cloud and CI tokens and runner memory, and exfiltrated to a typosquatted domain. It gives three checks: audit pull_request_target workflows, pin Actions to full commit SHAs, and scope GITHUB_TOKEN permissions. It also notes the limits of SHA pinning.
TrivyGitHub ActionsGitHub+1
CVE-2026-33634TeamPCPGHSA-69fq-xp46-6x23+6
DevSecOps, Supply Chain· Published and added 16 Oct 2026