Skip to content

127 results for β€œpi”

What you seeeverything
x.comthread🧠 AI

Lonnie VanZandt (@lonniev) on X

Secure Courier is a consent flow in Tollbooth DPYC, a monetization network for paid MCP services, that lets an AI agent act for a Nostr npub without holding the user's nsec. The service sends a signed, sealed direct message over Nostr relays, the user replies with a signed approval and an expiry, and the service issues its own encrypted grant. Lonnie VanZandt presents it as an alternative to central identity providers and CIBA. The thread gives no audit results.

Model Context ProtocolNostrOAuth+2
Secure CourierExcalibur-MCPLonnie VanZandt

mcp, agentsΒ· Added 1 Nov 2026

x.comthreadπŸ›‘οΈ Security

Dark Web Intelligence (@DailyDarkWeb) on X

CVE-2026-102764 is an unauthenticated RCE in BeyondTrust Remote Support, already exploited and in CISA KEV. Rapid7 published an analysis and opened a Metasploit pull request on 30 October 2026, showing code execution on version 24.1.2 via a forged "local" message origin, the native file-transfer service and a PHP file written to the web root. BT26-05 (CVSS 4.0 9.3) is fixed by patch BT26-05-RS; SaaS was patched by 9 October.

BeyondTrust Remote SupportMetasploitPHP+1
CVE-2026-102764CISA KEVRapid7+2

Offensive Security, Threat Intel, AppSecΒ· Added 1 Nov 2026, published 31 Oct 2026

x.comthread🧠 AI

🚨 AI News | TestingCatalog (@testingcatalog) on X

RoboAPI is a public API from PokeBot, powered by its world-action model Poke-Aurora, that lets robot arms do new tasks from natural-language instructions with no task-specific data collection or training. A user connects a supported arm with a wrist-mounted camera, gives a task such as "clean the table", and receives the next moves in near real time. The post gives no benchmarks, supported hardware list or pricing.

RoboAPIPoke-Auroraworld-action model
PokeBotTestingCatalog

models, multimodalΒ· Added 1 Nov 2026, published 31 Oct 2026

x.comthreadπŸ›‘οΈ Security

elvis (@omarsar0) on X

Thread by Elvis Saravia (omarsar0) summarising an Anthropic-led paper on pretraining data poisoning of CLI agents. Poisoning 0.1% of pretraining data planted a remote code execution backdoor in Qwen3 models (0.6B, 1.7B, 4B) trained from scratch. It survived SFT, DPO and RL, and fired on about 92% of triggered prompts at 4B. At a 0.0005% poison rate (about 2,500 documents) it still fired on 1.4% of prompts.

QwenLLM
Anthropicremote code executiondata poisoning+1

AI SecurityΒ· Added 31 Oct 2026, published 30 Oct 2026

twitter.comthread🧠 AI

Anthropic Cracking Down on Video Game Rewrites

A tweet from chasmmmmmmmmmmm says Claude Code received a new rule around 27 October 2026, delivered from Anthropic's servers under the flag "tengu_heron_brook", with no setting to disable it. The quoted rule allows original games, genre games and games from the user's own designs and assets, but forbids recreating a specific existing game, even if renamed. The post asks whether this ends game rewrites and modding, and gives no verification beyond the quoted text.

Claude Code
Anthropictengu_heron_brook

coding-agents, prompting, ai-policyΒ· Added 31 Oct 2026, published 30 Oct 2026

x.comthreadπŸ›‘οΈ Security

Lonnie VanZandt (@lonniev) on X

Tollbooth DPYC's "Secure Courier" is a consent scheme that lets an AI agent act for a Nostr npub at a paid MCP service without holding the user's nsec. The service sends a signed, sealed Nostr direct message, the user replies signed with their nsec and sets an expiry, and the service issues its own grant. The thread contrasts this with central identity providers and CIBA, arguing a breach reaches only grants that service issued.

Model Context ProtocolNostrOAuth+1
Tollbooth DPYCSecure CourierCIBA+4

Identity & Access, AI SecurityΒ· Added 1 Nov 2026, published 30 Oct 2026

cyberplace.socialthreadπŸ›‘οΈ Security

Backdoors in official Claude Code extensions

GossiTheDog's Mastodon post reports that the Anthropic Claude Code Visual Studio extension, as installed in Cursor, contains malware that creates a remote access Trojan on desktops. It links to a phorion.io blog post on the reported compromise of the official Claude Code VSX extension. The post gives no technical detail, indicators or dates itself.

Claude CodeCursorOpen VSX+1
Anthropicremote access Trojan

Supply Chain, Threat IntelΒ· Added 31 Oct 2026, published 30 Oct 2026

x.comthreadπŸ›‘οΈ Security

Shubham Mishra 🐐 (@shubh6200) on X

A post relaying Cursor's security advisory: a modified, malicious Claude Code VS Code extension was distributed through the Cursor extension marketplace, affecting at most 5,000 users. Anthropic did not develop that version, and other extensions are not affected. Users of Claude Code in Cursor are told to update to version 2.1.314. The post adds that marketplaces need publisher verification and package integrity checks. It gives no technical detail on the payload.

Claude CodeCursorVS Code
Anthropic

Supply Chain, AI SecurityΒ· Added 31 Oct 2026, published 30 Oct 2026

x.comthread🧠 AI

Prasenjit Sarkar (@stretchcloud) on X

A thread on Cloudflare's agent-readiness scan and the AgentReady.org open spec for "Agent Experience", developed with Vercel, Stripe, Auth0, Mintlify, Google, Netlify and Elementor. The scan grades whether agents can find a site (robots.txt, DNS), read clean Markdown, pass bot rules, and discover an MCP server or API catalog. One quoted example raised a score from 20 to 67 by shipping an API catalog with Link headers, an MCP server card, a skills index and an AI catalog file.

Model Context ProtocolCloudflareMarkdown
AgentReady.orgOraNick Launches+7

mcp, agentsΒ· Added 30 Oct 2026, published 29 Oct 2026

x.comthreadπŸ›‘οΈ Security

Dark Web Intelligence (@DailyDarkWeb) on X

DailyDarkWeb post summarising Anthropic Frontier Red Team research published 27 October 2026. An unreleased internal Claude research model built five attack chains: Chrome sandbox escape (V8 heap bug, CacheStorage race, FedCM use-after-free), a Safari same-origin policy bypass, data extraction from a locked Pixel 9 over USB, a Windows QUIC kernel crash (CVE-2026-33096) and zero-click Linux root via multipath TCP (CVE-2026-98432). Anthropic says all flaws are fixed, including 62 Chrome CVEs as of Chrome 156. The post notes the chains are not independently reproduced.

ClaudeChromeSafari+3
CVE-2026-33096CVE-2026-98432Anthropic Frontier Red Team+8

AI Security, Offensive SecurityΒ· Added 30 Oct 2026, published 29 Oct 2026

x.comthread🧠 AI

Eddy (@ieddysun) on X

Expo's official skills package gives AI coding agents scoped instructions for building Expo apps. One command, npx skills@latest add expo/skills --skill '*', installs it for Cursor, Copilot and Windsurf, while Claude Code and Codex use their plugin marketplaces. Skills include expo-router, expo-animation, expo-upgrade and eas-update. The Expo MCP server adds live docs lookup, compatible dependency installs, EAS build monitoring and simulator screenshots.

ExpoReact NativeExpo Router+9

coding-agents, prompting, mcpΒ· Added 29 Oct 2026, published 28 Oct 2026

x.comthreadπŸ›‘οΈ Security

Trail of Bits (@trailofbits) on X

Trail of Bits post says it achieved remote code execution through a Brotli decoder bug in Linux lab setups: Node.js 24.22.0 with Express 5.3.0 via the standard JSON parser (x86-64 and ARM64), and Electron 41.10.7 (x86-64) with a custom decoding service. Exploitation needs a carefully matched setup and repeated attempts. A scanner by ToBScottA finds hidden copies of the decoder, including in stripped binaries.

BrotliNode.jsExpress+1
Trail of BitsToBScottA

AppSec, Offensive Security, Supply ChainΒ· Added 30 Oct 2026, published 28 Oct 2026

x.comthread🧠 AI

Laban (@lunkertw) on X

An X post summarising five AI items: Google DeepMind's Gemini 4 Carbon (88.2% SEC-bench Pro, 54.8% ExploitGym, 71.0% CWE-bench, 59 on Artificial Analysis Intelligence Index v5.0), Ed Zitron's critique of Anthropic's S-1, a Utah Claude Code pilot, and the repos beenuar/AiSOC and expo/skills. In the Utah pilot, 34 developers in 10 agencies took part over four weeks, 80% had a working setup within 30 minutes, and 71% saved over 20 hours. It gives short summaries and links, not primary analysis.

Claude CodeModel Context ProtocolPython+6
Google DeepMindGemini 4 CarbonSEC-bench Pro+9

models, coding-agents, ai-policyΒ· Added 29 Oct 2026, published 28 Oct 2026

x.comthread🧠 AI

John Rood (@johnroodepic) on X

Nemotron 3.5 Transcribe is an open-weight, promptable 30B mixture-of-experts model from NVIDIA with about 4B active parameters, built for recorded audio. One checkpoint transcribes 40 languages, handles recordings up to an hour, labels up to eight speakers, translates, and answers questions about English audio. Weights and a demo are on Hugging Face. The post gives no benchmarks.

Mixture of ExpertsHugging Face
NVIDIANemotronNemotron 3.5 Transcribe+1

models, multimodalΒ· Added 29 Oct 2026, published 28 Oct 2026

x.comthreadπŸ›‘οΈ Security

Hakimi Eiqbal (@hakimieiqbal) on X

A practical reverse-engineering map by hakimieiqbal on X that picks tools by target: native binaries, .NET, Electron, iOS, firmware, WebAssembly and network protocols. It introduces REA (morluto/rea), which connects coding agents to RE tools, and lists MCP bridges for IDA Pro, Ghidra and radare2. It adds an evidence-first workflow and free courses such as pwn.college and OpenSecurityTraining2.

GhidraIDA Proradare2+3
REAFlare-OnOpenSecurityTraining2+5

Malware & RE, LearningΒ· Added 29 Oct 2026, published 28 Oct 2026

x.comthreadπŸ›‘οΈ Security

Kizuno18 (@Kizuno18) on X

Thread by Kizuno18 on the move from local stdio/Docker Model Context Protocol servers to remote HTTP/SSE endpoints in enterprise infrastructure. It names three trade-offs: credential boundary inversion (short-lived OAuth/JWT tokens instead of long-lived admin tokens on workstations), tool schema bloat solved by deferred discovery, and governance via HCP Terraform policy-as-code (Sentinel/OPA), audit trails and approvals. It is opinion, with no data or implementation detail.

Model Context ProtocolTerraformDocker+2
Sentinelblast radiuspolicy-as-code+1

AI Security, Identity & Access, DevSecOpsΒ· Added 29 Oct 2026, published 27 Oct 2026

x.comthread🧠 AI

Kizuno18 (@Kizuno18) on X

Kizuno18's X post argues that the move from local stdio and Docker MCP servers to remote HTTP/SSE endpoints matures the Model Context Protocol in enterprise infrastructure. It lists three trade-offs: short-lived OAuth/JWT bearer tokens replace mounted admin credentials, deferred tool discovery avoids roughly 20k tokens of eager schema loading, and HCP Terraform enforces Sentinel/OPA policy, audit trails and approvals server-side. Opinion post with no benchmarks or code.

Model Context ProtocolDockerTerraform+5
Kizuno18HCP TerraformOPA

mcpΒ· Added 29 Oct 2026, published 27 Oct 2026

x.comthread🧠 AI

Photon Capital (@PhotonCap) on X

Photon Capital's thread covers the 27 October 2026 NVIDIA and Oracle announcement of general availability of Vera Rubin NVL72 and Vera CPUs on OCI. It lists specs (Spectrum-6 at 102.4Tbps, HGX Rubin NVL8 with Xeon 6, 150,000 initial Vera CPUs) and OpenAI's use of Vera CPUs for agentic sandboxes. The commentary argues CPU capacity can cut cost per task and shorten KV cache residency in GPU memory.

Oracle Cloud InfrastructureOCI Kubernetes EngineKubernetes+6
NVIDIAOracleOpenAI+7

inference, ai-infra, agentsΒ· Added 28 Oct 2026, published 27 Oct 2026

x.comthread🧠 AI

Manoj | The AI Dude (@Manojkumar2257) on X

heditor is an open-source (MIT) agent skill from pycodebr that has Claude Code, Codex, Cursor or OpenCode edit talking-head videos. It transcribes with faster-whisper, picks a 30-70s segment, cuts frame-accurately, builds HTML + GSAP motion graphics, mixes audio at -14 LUFS, and runs QA with vision-reviewed previews. It offers 42 named styles and a long-form mode with chapters, SRT/VTT and lower thirds. Install: npx skills add pycodebr/heditor -g.

Claude CodeCodexCursor+6
heditorpycodebr

coding-agents, prompting, multimodalΒ· Added 28 Oct 2026, published 27 Oct 2026

x.comthreadπŸ›‘οΈ Security

cubillas (@cubillas888) on X

The tweet relays Pillar Security research that opencode on Windows and WSL could run attacker-controlled code during remote MCP server OAuth sign-in. The fix shipped in opencode 1.18.33 on 28 September, with no advisory or CVE published. It advises users of remote MCP servers to update and review which servers they connect to. Technical details are not in the post.

OpenCodeModel Context ProtocolOAuth+1
Pillar Security

AI Security, AppSecΒ· Added 29 Oct 2026, published 27 Oct 2026

x.comthreadπŸ›‘οΈ Security

Nicholas Martin (@ndgmlondon) on X

X thread started by Nicholas Martin (#IAM) advising that MCP tool permissions be verified and scoped session tokens used to enforce least privilege against indirect prompt injection. Replies argue that token scoping does not solve the confused deputy problem, because an injection borrows the agent's legitimate authority. They recommend per-task tokens with short expiry, with the grant logged beside the call, and raise MCP server dependency supply-chain risk.

Model Context Protocol
indirect prompt injectionconfused deputy

AI Security, Identity & AccessΒ· Added 28 Oct 2026, published 27 Oct 2026

x.comthread🧠 AI

Muzammil Shah (@Muzammil_OX) on X

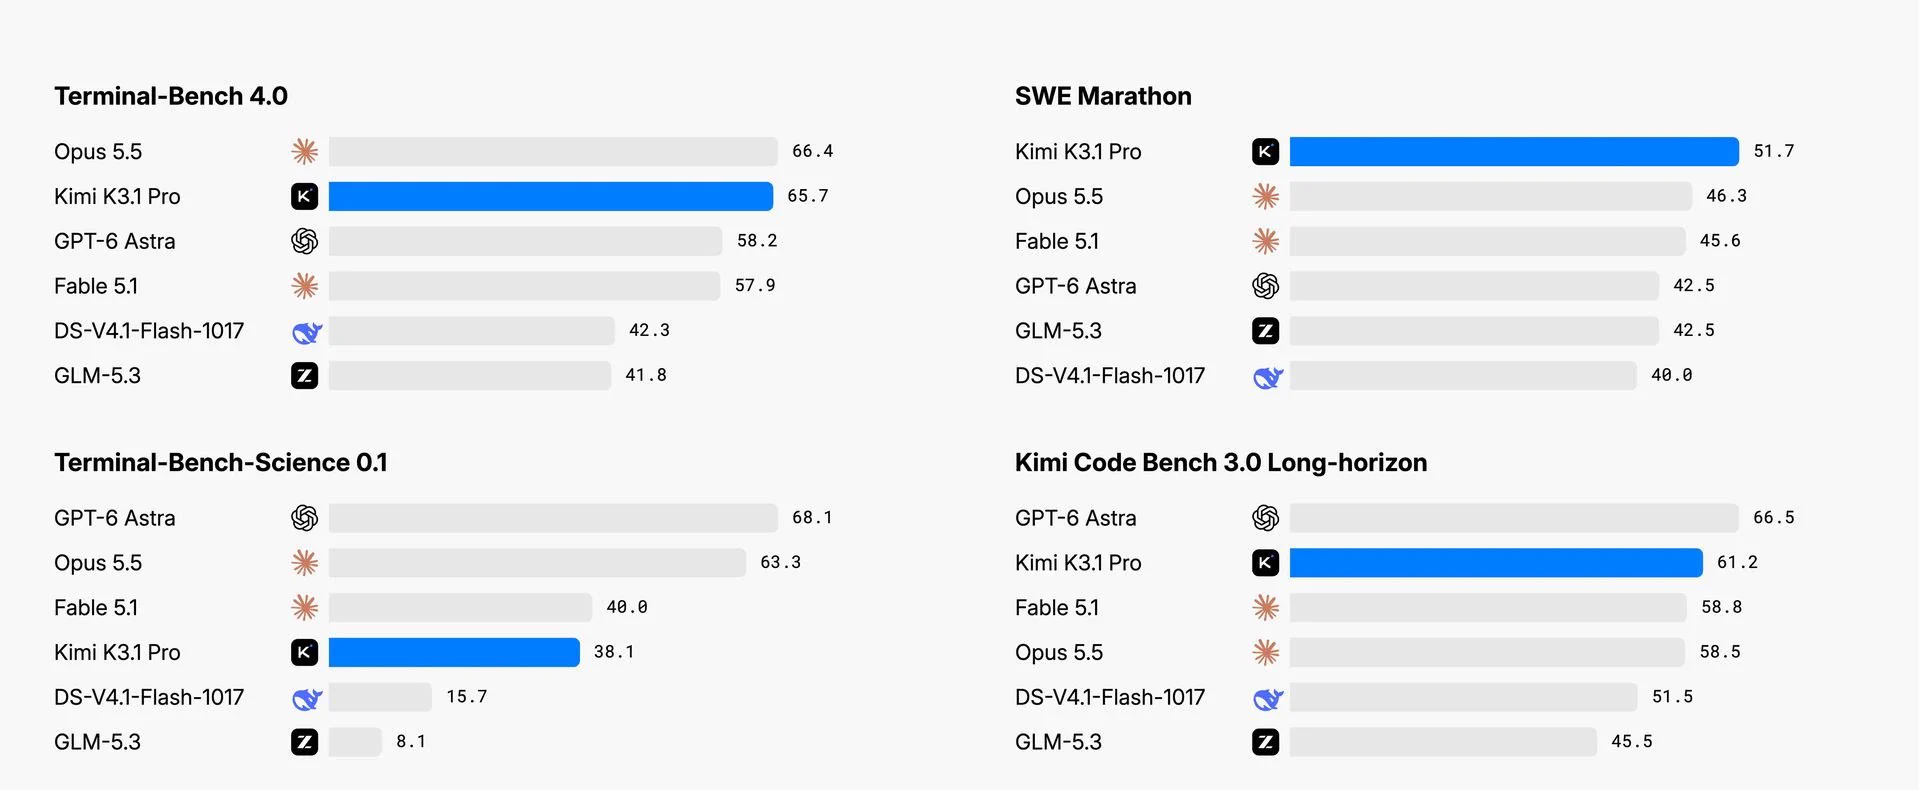
Kimi K3.1 Pro is a new model from Moonshot AI that scores 55 on the Artificial Analysis Intelligence Index, up 11 points from its predecessor, and ranks 4th overall. It has a 1M-token context window and API pricing of $2 per million input tokens and $10 per million output tokens. Weights are due by November 4. Moonshot removed cyber-related training data, which cut its internal vulnerability research score from 90.5% to 81%.

UnityUnreal EngineGodot
Moonshot AIKimi K3.1 ProKimi+2

models, evalsΒ· Added 28 Oct 2026, published 27 Oct 2026

x.comthreadπŸ›‘οΈ Security

AGTP (@AGTPinsights) on X

AGTP's X thread summarizes Meta's Muse Spark 1.3 Evaluation Report. Prompt injection was tested on Exponential Security Labs' RepoInject v1 and BrowserInject v1 and on Gray Swan's IPI Arena, with robustness said to be on par with GPT-5.6 Sol. It also covers chain of thought controllability evals, PostTrainBench under Loss of Control, and Handshake's pre-release human red teaming. It notes the Midas Project's criticism of Muse Wonder's missing safety report.

Muse SparkMuse Spark Open
prompt injectionRepoInject v1BrowserInject v1+10

AI SecurityΒ· Added 27 Oct 2026, published 26 Oct 2026

x.comthread🧠 AI

AGTP (@AGTPinsights) on X

Thread summarizing Meta's Muse Spark 1.3 Evaluation Report, the safety write-up for the model released on September 2, 2026. It covers prompt-injection results on Exponential Security Labs' RepoInject v1 and BrowserInject v1 and Gray Swan's IPI Arena, chain-of-thought controllability evals, PostTrainBench under Loss of Control, and Handshake's human red teaming. It also notes The Midas Project's criticism that Muse Wonder still has no safety report, and the Muse Spark Open rollout (816B total, 42B active parameters).

Muse Spark 1.3Muse Spark OpenMixture of Experts
MetaMuseMuse Wonder+19

ai-safety, evals, modelsΒ· Added 27 Oct 2026, published 26 Oct 2026

x.comthread🧠 AI

The SI Maximalist (@thesimaximalist) on X

The SI Maximalist posts on X that OpenAI says GPT-6.1 Terra matches GPT-6 Astra on Agents' Last Exam, OpenAI's test of workplace software tasks, at one tenth of the token price. The model is available in ChatGPT Work, Codex and the API. The post only relays OpenAI's claim and gives no benchmark scores, exact prices or method.

ChatGPTCodexOpenAI API
OpenAIGPT-6.1 TerraGPT-6 Astra+2

models, evalsΒ· Added 27 Oct 2026, published 26 Oct 2026

x.comthread🧠 AI

Akash Rajagopal (@akashsairaja) on X

Ollama overview thread by Akash Rajagopal on X. It lists six steps: install on macOS, Linux, Windows or Docker; run `ollama run gemma4`; use the REST API on localhost:11434 (/api/chat); call it from ollama-python and ollama-js; llama.cpp as the README's supported backend; and `ollama launch claude` to connect Claude Code. Codex, OpenCode, Copilot CLI and Droid also work. The thread cites 184k GitHub stars and an MIT licence.

Ollamallama.cppClaude Code+10
Gemma 4Akash Rajagopal

inference, coding-agentsΒ· Added 27 Oct 2026, published 26 Oct 2026

x.comthreadπŸ›‘οΈ Security

BenjaminπŸ‘¨β€πŸ’» (@Hislordship_9) on X

Thread on Forever Security's finding that a planted Markdown "Engineering Work Guidelines" file in ~/Downloads made Codex add a "project-tools" MCP server to ~/.codex/config.toml. The server ran npm install function-color, a known malicious package, and started a child session with --dangerously-bypass-approvals-and-sandbox. Codex complied in over 90% of the firm's tests; Claude Code, via a CLAUDE.md setting ANTHROPIC_BASE_URL, about half. Advice: don't start agents in Downloads, review instruction files, and diff agent config.

CodexClaude CodeModel Context Protocol+1
Forever Securityfunction-colorAGENTS.md+4

AI Security, Supply ChainΒ· Added 27 Oct 2026, published 26 Oct 2026

x.comthreadπŸ›‘οΈ Security

lee1981 (@lee1981b) on X

Reply on X explaining a Bytecode Alliance advisory for Wasmtime's Cranelift compiler backend. A large or crafted Wasm function that generates enough SSA values overflows Cranelift's value-index representation, which packed indices into 24-bit fields. The fix widens them to 32 bits. The issue is not AArch64-specific, and the advisory names no required optimisation level. Guard pages do not reliably stop the resulting miscompilation and type confusion, so a sandbox escape can arise at compile time.

WasmtimeCraneliftWebAssembly
sandbox escapetype confusioninteger overflow+1

AppSecΒ· Added 28 Oct 2026, published 26 Oct 2026

x.comthreadπŸ›‘οΈ Security

David Gutierrez | Eng (@david_x_ai) on X

Thread on a critical opencode bug disclosed by Pillar Security on Oct 19. On Windows and WSL, a remote MCP server could run code during OAuth sign-in, because the server-chosen authorization URL was put unescaped into a PowerShell command, so a PowerShell subexpression executed. opencode fixed it in 1.18.33 on Sep 28 as a browser-launch refactor with no advisory or CVE. MCP Inspector published an advisory for the same bug class, and its fix needs a major bump of the open package.

OpenCodeModel Context ProtocolPowerShell+3
Pillar Securitycommand injectionPowerShell subexpression+1

AI Security, AppSec, Supply ChainΒ· Added 27 Oct 2026, published 25 Oct 2026

x.comthread🧠 AI

SemiAnalysis (@SemiAnalysis_) on X

SemiAnalysis claims AMD chips running vLLM can earn up to $3 per chip-hour in profit serving the open-source Kimi K3 model, even after higher chip rental prices following Claude Code's rise. Kimi K3 has over 2.8 trillion parameters and fits AMD's 288GB per chip, while B200 cannot hold it in one server. B200 must then use tensor or pipeline parallelism over 400Gbit/s InfiniBand or Ethernet, which SemiAnalysis says is 18x slower than NVLink. The post gives no methodology.

vLLMClaude CodeNVLink+1
SemiAnalysisAMDKimi K3+1

inferenceΒ· Added 26 Oct 2026, published 25 Oct 2026

Showing 30 of 127

Show more