- ERC-8481: Agent Pre-Sign Risk Report
ERC-8481 is a draft Ethereum standard for the report a risk source returns about one prepared, unsigned request from an AI agent. Reports bind to the request by digest and are signed with EIP-712 by an ERC-8004 identity. Findings cover tokens, approvals, addresses, x402 payments and texts, each marked read or not read, with no score or verdict. The only implementation is toll, a free HTTP and MCP guard on Robinhood Chain.
 ethereum-magicians.orgotherAdded 2 Nov 2026, published 31 Oct 2026🧠 AI
 VulnCheck - Outpace Adversaries
VulnCheck's vulnerability disclosure policy, last revised March 2026, sets a 120 day deadline for vendors to patch or publish an advisory, after which VulnCheck publishes an uncoordinated third-party advisory. The deadline drops to 7 days if exploitation in the wild is found. Other terms: no extensions, email-only communication, any published patch counts as public disclosure, and no participation in programs that bar public disclosure.
 vulncheck.comotherAdded 29 Oct 2026🛡️ Security
- Search Search results for "security" | MCP Market
MCP Market search results for "security" in the skills category, listing about 20 installable AI agent skills. Entries cover OWASP Top 10 audits, secure coding for PHP, STRIDE threat modeling, CVE remediation, security header analysis, misconfiguration finding, bug bounty triage and AgentShield scans of Claude Code configurations. One is a paid D365FO security-role XML skill. Each entry has only a one-line description and a category label.
 mcpmarket.comotherAdded 25 Oct 2026🛡️ Security
 Apple Security Research Device
The Apple Security Research Device (SRD) program gives vetted researchers a specially fused iPhone for iOS security research without bypassing protections. It allows shell access, running any tools, choosing entitlements and customizing the kernel. All iOS and iPhone components are in scope except Apple Pay and third-party apps. Findings are automatically considered for Apple Security Bounty, with bonuses for preview and beta software.
 security.apple.comotherAdded 25 Oct 2026, published 24 Oct 2026🛡️ Security
 The Programmable Data Center — Evan Conrad, SF Compute
Latent Space podcast episode with Evan Conrad, CEO of SF Compute, recorded at AI Engineer New York in 2026. He explains why the company moved from subleasing a cluster to running cloud-level operations so it can physically deliver traded GPU capacity. Topics include a constraint-matching order book, spot versus forward prices, batch versus live inference leases, and cash versus physical settlement. The transcript was truncated near the end.
 latent.spaceotherPublished and added 20 Oct 2026🧠 AI
- DeepSeek V4.1 Flash 1017 (Max)
DeepSeek V4.1 Flash 1017 (Max) is an open-weights reasoning MoE model from DeepSeek with 552B total and 16B active parameters, a 1M-token context window, text and image input, and an MIT license. Artificial Analysis scores it 45 on its Intelligence Index (open-weights median 19), at $0.30 input and $1.20 output per 1M tokens, 216 tokens per second, and 210M tokens used in the evaluation. It is available through 10 API providers.
 artificialanalysis.aiotherAdded 20 Oct 2026, published 19 Oct 2026🧠 AI
 OpenCode has a security breach last that impacted 1.4% of console users
OpenCode announced on X a security breach tied to a "large scale distillation attack" that affected 1.4% of OpenCode Console users. Affected users were those with external model providers linked, and all were notified by email. The incident was ongoing at posting, with remediation under way with Anthropic, OpenAI and Google. No technical details were given.
 twitter.comotherAdded 19 Oct 2026, published 18 Oct 2026🛡️ Security
 DeepSeek search and fetch – $0.75 per 1000 successful requests
DeepSeek Search & Fetch are two JSON APIs for agents and RAG apps. Search (/v1/tools/search) returns structured results from DeepSeek's in-house engine, with count, need_content and operators such as site:, lang: and after:. Fetch (/v1/tools/fetch) returns a page as Markdown. Both use bearer auth, bill only successful requests ($0.75 per 1000), and have account-level QPS limits. Calls from DeepSeek Harness, Claude Code or Codex are free until 1 November 2026.
 api-docs.deepseek.comotherAdded 19 Oct 2026, published 18 Oct 2026🧠 AI
- DeepSeek: DeepSeek v4.1 Flash 1017
Listing for the October 17, 2026 snapshot of DeepSeek V4.1 Flash, served as `deepseek-flash`. It is a sparse mixture-of-experts model on DeepSeek's new Causal Encoder-Decoder (CED) architecture: 552B total parameters, 8B active on input and 16B on output, with native joint image/text pretraining and compressed KV caching that cuts cache memory to about a quarter of the prior Flash generation. It has a 1,048,576-token context and up to 131,072 output tokens, supports tool calling and JSON-schema structured outputs, and costs $0.08/M input and $0.50/M output tokens. Eight providers serve it on OpenRouter. DeepSeek positions it for coding, terminal and computer-use agents and long-horizon tasks, and claims it beats V4 Pro.
 openrouter.aiotherAdded 18 Oct 2026, published 17 Oct 2026🧠 AI
- Model Context Protocol releases (2026-07-28 stable spec)
The GitHub releases page for the modelcontextprotocol/modelcontextprotocol repository, listing the version history of the Model Context Protocol (MCP) specification from its initial 2024-10-07 draft through the 2025-03-26, 2025-06-18, and 2025-11-25 revisions to the newly stabilized 2026-07-28 revision. Each entry links to its changelog and distinguishes release candidates from final/stable releases, and the page points to the version-negotiation documentation that lets clients and servers agree on which protocol revision to use.
 github.comotherAdded 5 Oct 2026🧠 AI
- Gemini 4 Argon (High): Intelligence, Performance and Price Analysis
Artificial Analysis benchmark profile for Google's Gemini 4 Argon (High), a reasoning model with a 1M-token context window supporting text and image input. It scores 53 on the Artificial Analysis Intelligence Index (median 26), costs $2.00/1M input and $10.00/1M output tokens, and used 110M output tokens to complete the Intelligence Index evaluation, with per-metric breakdowns across coding, reasoning, agentic and long-context tasks.
artificialanalysis.aiotherAdded 2 Oct 2026, published 30 Sep 2026🧠 AI  https://www.rfc-editor.org/search/?status=Best+Current+Practice&area=sec
A saved search on the official RFC Editor site filtered to documents with status Best Current Practice in the sec (Security) area, effectively a live index of IETF's authoritative security best-practice standards such as BCP-level RFCs on anti-spoofing/ingress filtering, routing security, and password policy. The fetched copy rendered with JavaScript disabled so no result rows were captured, but the query itself is a reusable, continuously updated pointer into the canonical security standards catalog maintained by the IETF/RFC Editor.
 rfc-editor.orgotherAdded 2 Oct 2026, published 29 Sep 2026🛡️ Security
- Terminal-Bench 4.0 leaderboard
Artificial Analysis' leaderboard for Terminal-Bench 4.0, a 66-task benchmark of complex terminal work spanning software engineering, machine learning, science, operations, security, hardware and media, with recalibrated compute/time budgets and improved verifiers over prior versions. The page ranks models/agents by score, cost per task, output tokens per task, and time per task, and links out to related Artificial Analysis evaluations (GDPval-AA, APEX-Agents, Harvey's Legal Agent Benchmark, ServiceNow EnterpriseOps-Gym, Terminal-Bench 2.1, GPQA, MMLU-Pro, AIME, LiveCodeBench and others) used to benchmark frontier agentic and reasoning capability.
artificialanalysis.aiotherAdded 28 Sep 2026🧠 AI - MCP Python SDK v2.2.0
Release notes for MCP Python SDK v2.2.0 detailing several security-relevant default changes: HTTP clients (Client, streamable_http_client, sse_client) now only follow redirects within the same origin, closing a cross-origin redirect trust gap; OAuth clients now validate the authorization server's issuer even on the legacy (non-protected-resource-metadata) discovery path, preventing metadata/issuer mismatch attacks; idle Streamable HTTP sessions now expire after 30 minutes with a 10,000-session cap to limit resource exhaustion; and a new AuthSettings.validate_token_resource setting lets servers reject bearer tokens not issued for them (audience/resource confusion). Deprecation warnings push OAuth provider configs toward requiring an explicit issuer ahead of a 3.0 breaking change.
github.comotherAdded 27 Sep 2026🛡️ Security  Agent Threat Rules (ATR) — Sigma/YARA-style open detection format for AI agent threats
Agent Threat Rules (ATR) is an open, versioned YAML rule format for detecting AI-agent security threats — prompt injection, tool poisoning, credential exfiltration, unauthenticated agent execution — positioned as "what Sigma is to SIEM and YARA is to malware." Rules carry permanent ATR-YYYY-NNNNN IDs, declare detection conditions against fields like LLM I/O, tool-call args, or SKILL.md content, and map back to OWASP Agentic/LLM Top 10, MITRE ATLAS, SAFE-MCP, and NIST AI RMF; a reference TypeScript engine and Python wrapper ship MIT-licensed. Governance is transitioning from a single BDFL maintainer to a Technical Steering Committee, and the spec is notably transparent about its own limits, withdrawing previously published per-lane false-positive figures after discovering a tainted benign corpus.
 agentthreatrule.orgotherAdded 26 Sep 2026🛡️ Security
- Known Exploited Vulnerabilities Catalog | CISA
CISA's Known Exploited Vulnerabilities (KEV) catalog is the authoritative list of CVEs with confirmed in-the-wild exploitation. It shows 1739 entries, each with vendor, product, description, CWE, ransomware-use flag, date added, due date, and a new BOD 26-04 forensic-triage flag. The latest entries cover Citrix NetScaler, Zammad (chained session fixation and root privilege escalation), Fortinet FortiMail, Cisco Catalyst SD-WAN Manager, WordPress Core, SharePoint, MikroTik RouterOS, Adobe Commerce, WSO2 and Check Point, plus old CVEs such as ProFTPD CVE-2015-3306 and Struts CVE-2016-3081. Feeds are available as CSV and JSON for vulnerability-management prioritisation.
 cisa.govotherAdded 26 Sep 2026🛡️ Security
- OWASP Agentic Skills Top 10 (AST10)
The OWASP Agentic Skills Top 10 (AST10) is a new OWASP project cataloging the 10 most critical security risks in AI agent "skills" — the layer that defines how agents orchestrate multi-step, autonomous workflows across platforms, as opposed to how models talk to tools via MCP. Each risk is mapped to the Cloud Security Alliance's MAESTRO 7-layer threat model for agentic AI systems, aiming to close a gap left by existing LLM- and MCP-focused security guidance.
 owasp.orgotherAdded 16 Sep 2026🛡️ Security
 OWASP Agentic Skills Top 10 (AST10)
OWASP project page for the Agentic Skills Top 10 (AST10), a framework that lists the 10 most critical security risks in AI agent skills across agent platforms, with mitigations and prevention strategies. It targets the behavior/execution layer of skills, which sits above MCP tool access, and maps each risk to the Cloud Security Alliance's MAESTRO 7-layer threat model. It is a useful reference for threat-modelling agent skill ecosystems.
owasp.orgotherAdded 5 Sep 2026🛡️ Security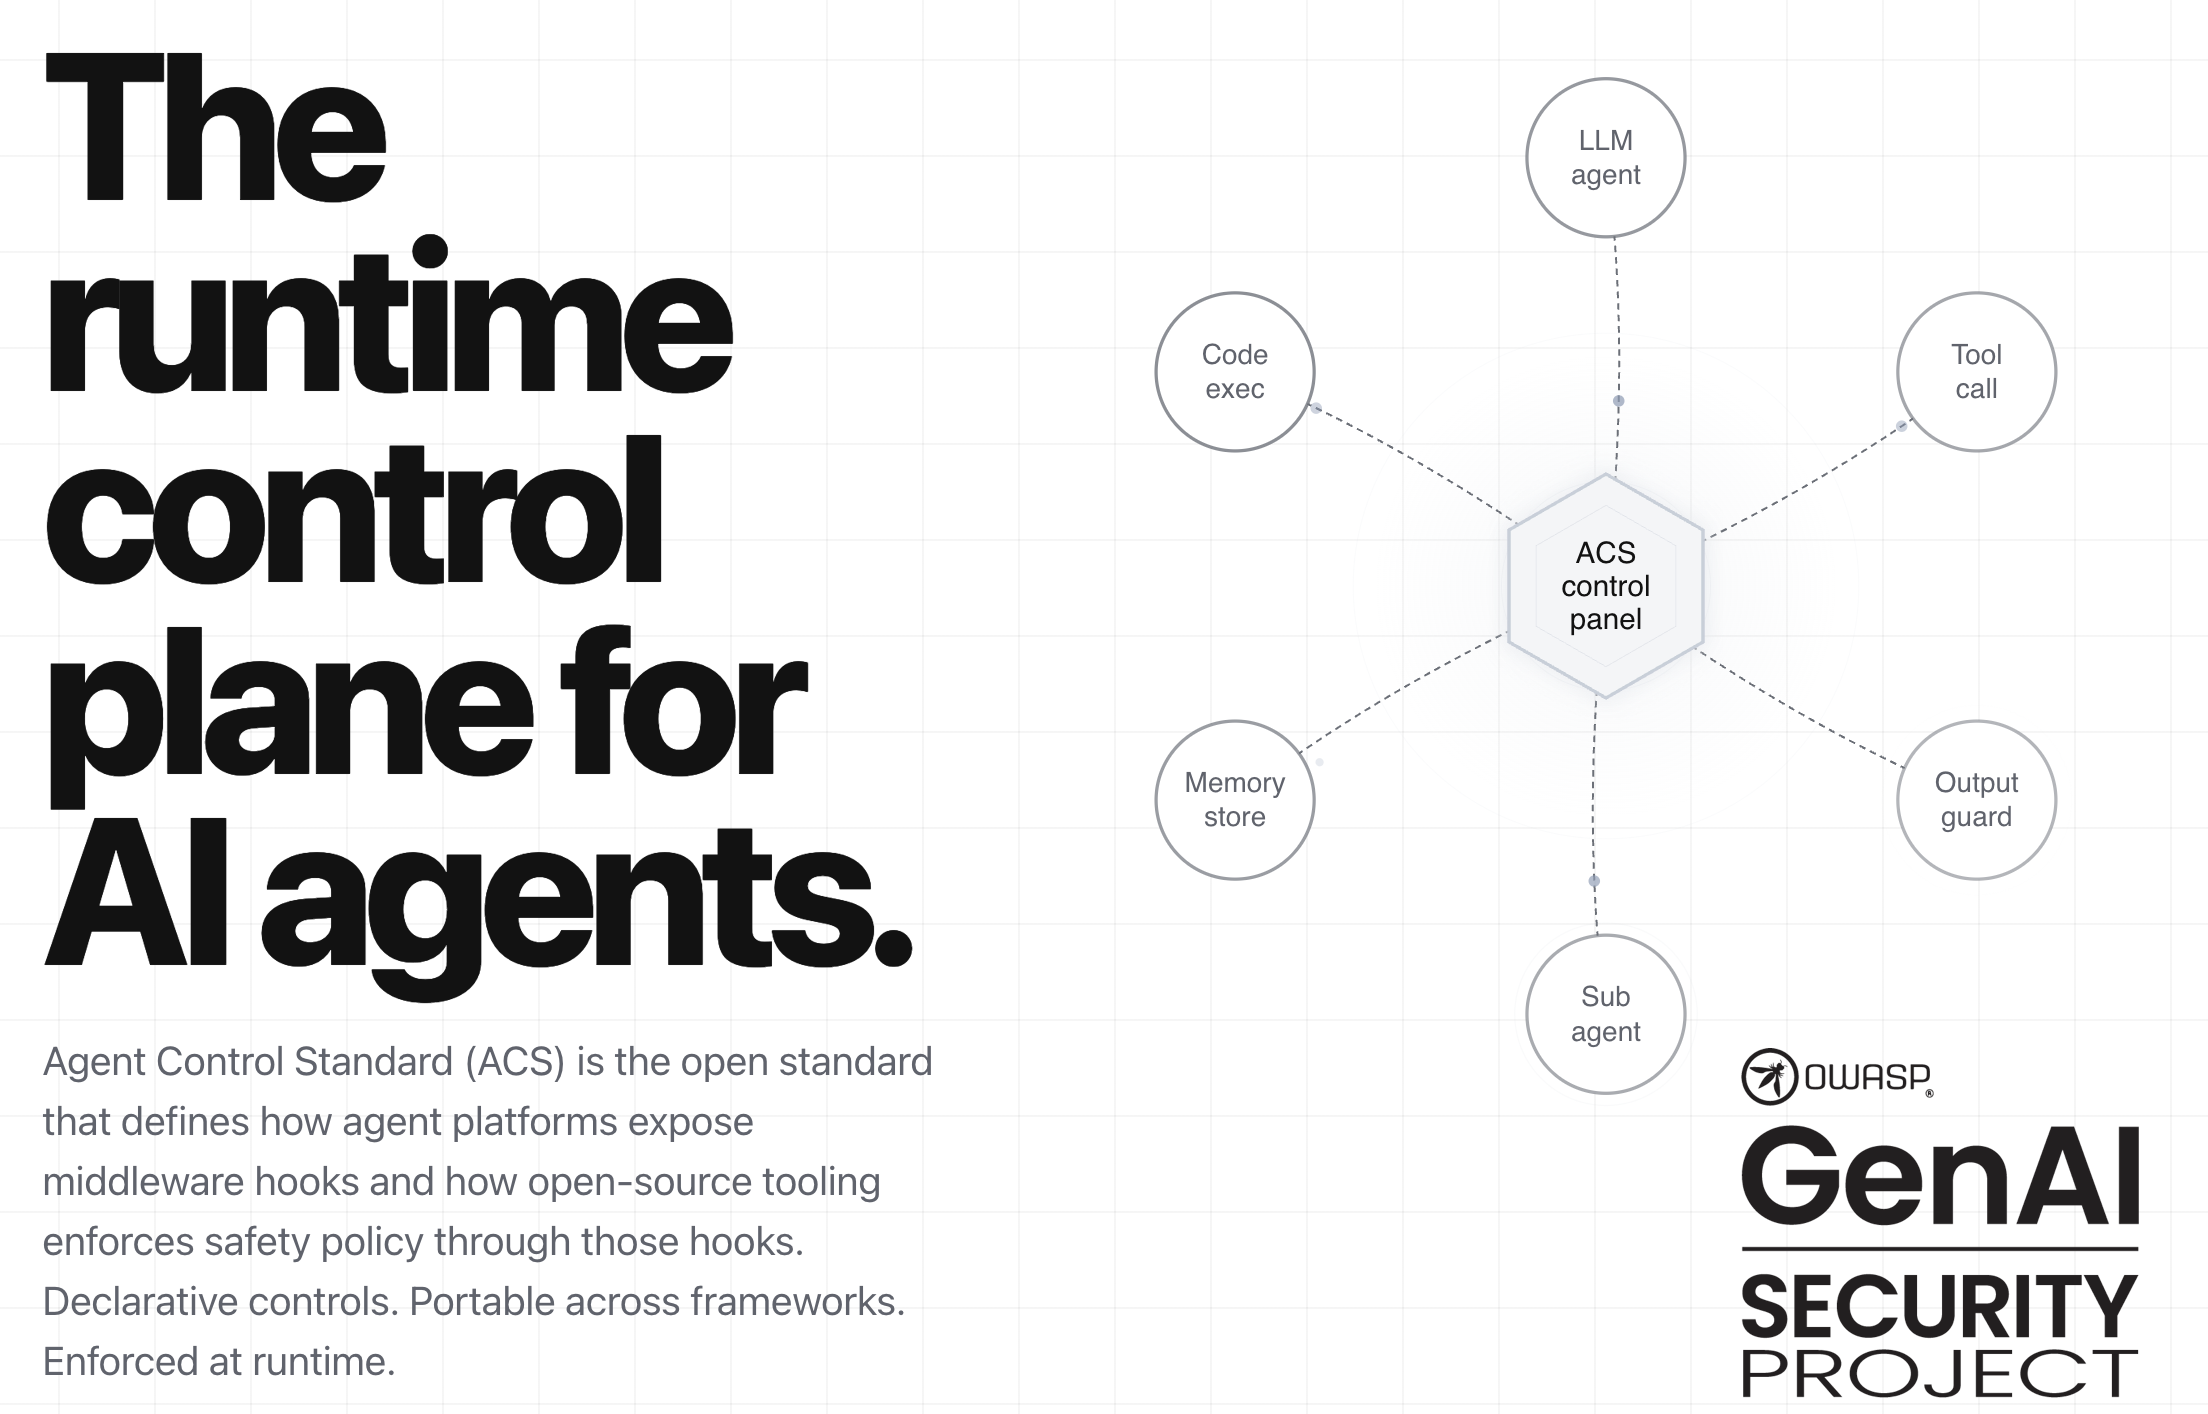 Agent Control Standard (ACS) v1.0 — OWASP GenAI Security Project
The Agent Control Standard (ACS) v1.0 is an OWASP GenAI Security Project specification defining how AI agent platforms should expose middleware hooks so that safety policies can be declared and enforced at runtime, portably across different agent frameworks. It aims to give enterprises visibility into what an agent is, what it can access, what it did, and the ability to control agent behavior live rather than relying on black-box execution.
 genai.owasp.orgotherAdded 26 Sep 2026, published 2 Sep 2026🛡️ Security
- DEF CON® 34 Hacking Conference - Main Stage Talks
The official DEF CON 34 main-stage talk listing, with full abstracts and speaker bios for dozens of original research presentations spanning bootrom-to-wallet-key exploitation of the dGEN1 Ethereum phone, a privilege-escalation chain in Microsoft's Python-in-Excel Azure container (CVE-2026-45459), a novel x86 SMM hardware attack, black-box TEE key recovery on the TI OMAP-L138 via timing side channels, native-code exploitation of llama.cpp and Ollama, a CDP-based Browser-in-the-Middle AitM phishing toolkit defeating CSP/SRI, CPDLC air-traffic-control message injection via SDR, an iCloud Keychain extraction bug (CVE-2026-28860), Segmentation Fault-Oriented Programming (SFOP) for bypassing Intel CET, weaponized WMI provider post-exploitation, an autonomous AI system (HTTP Terminator) discovering novel HTTP desync attacks, quantum ML for OS fingerprinting, reverse engineering of Windows Defender's BTR.sys driver for EDR bypass, a V8 renderer RCE in Samsung Internet (CVE-2025-10891), an LLM CI build-gate bypass, a Bring-Your-Own-EDR PPL abuse technique, Amazon Locker hardware hacking, and Windows PnP USB auto-install RCE via RDP redirection.
 defcon.orgotherAdded 10 Aug 2026🛡️ Security
- A Really Bad Day
An interactive web-based attack simulation depicting a domain administrator executing a trojanized "SpeedDownloader.exe" containing a backdoor RAT on a Tier 0 host (EXCH01), leading to full domain compromise over a compressed 2-hour kill chain. Users click through 9 attack stages either as Red Team (watching the compromise unfold) or Blue Team (seeing which security controls could break the chain at each step), illustrating Tier 0 asset risk, initial access via trojanized software, and defense-in-depth against domain dominance.
 mr-r3b00t.github.iootherAdded 3 Sep 2026, published 31 Jul 2026🛡️ Security
- EVMBench Leaderboard
EVMBench Leaderboard aggregates self-reported vendor results on OpenAI's EVMBench, a benchmark of 117 ground-truth vulnerabilities drawn from 40 real Code4rena smart-contract audit contests. It defines a canonical evaluation protocol requiring the unmodified openai/frontier-evals task runner and the complete, unfiltered audit repository, comparing agents like Nethermind AuditAgent and Guardix by recall against the full ground-truth finding set.
 testmachine.aiotherAdded 3 Sep 2026, published 31 Jul 2026🛡️ Security
- Hackflix
Hackflix (h4ckfl1x) is a curated, searchable archive of security conference talks from DEF CON, Black Hat, RSA, BSides and other events. It lists about 21,560 videos across 659 events and 38,914 topics, filterable by conference, year, speaker or topic. It is useful for finding talks on a given subject or by a given speaker in one place.
 h4ckfl1x.comotherAdded 3 Sep 2026, published 30 Jul 2026🛡️ Security
- OWASP ASM Top 10
Project page for the OWASP Attack Surface Management (ASM) Top 10, an incubator-stage OWASP project with two listed contributors. By its title it is a Top 10-style list of attack surface management risks, but the fetched text shows only project metadata and OWASP legal boilerplate, not the list itself. It is worth tracking as it matures into a reference for external asset discovery and exposure management.
owasp.orgotherAdded 3 Sep 2026, published 17 May 2026🛡️ Security  Dracarys
 is a new "not for beginners" Active Directory attack lab built on top of Orange Cyberdefense's GOAD (Game of Active Directory) framework. The lab consists of two Windows Server 2025 hosts (a DC and a member server) and an Ubuntu 24.04 server, all joined to the domain dracarys.lab; the goal is to pivot from the domain-joined Linux box to full domain admin. The post gives deployment instructions (VirtualBox, VMware, Ludus, Proxmox, AWS, Azure), rules (no vagrant user, no reading recipe secrets), and promises follow-up walkthroughs of the Linux-side exploitation techniques.
 mayfly277.github.iootherAdded 2 Oct 2026, published 8 Mar 2026🛡️ Security
 OWASP GenAI Security Project — 2026 LLM Top 10 + new Agent Control Standard
Homepage of the OWASP GenAI Security Project, the community initiative that produces the OWASP Top 10 for LLM Applications and, as of 2026, the new Agent Control Standard (ACS) — a framework for enforcing transparency and control over AI agents operating across cloud, SaaS and on-prem environments. The site coordinates multiple ongoing workstreams (AI threat intelligence, agentic app security, AI red-teaming, AI bill of materials, data security) and hosts community content such as the ASI06 Memory & Context Poisoning writeup and the FinBot CTF companion exercise.
genai.owasp.orgotherAdded 29 Sep 2026, published 5 Aug 2025🛡️ Security