- Luke The Dev (@iamlukethedev) on X
Hermes, the Nous Research agent framework, shipped 130 merged PRs in October 2026, according to this X recap by Luke The Dev. Main items are a unified gateway runtime, a Desktop and Bot Screen, a bundles and package manager, crash-safe updates and new Claude model entries. Ten PRs cover security: an iron-proxy credential-injection egress firewall for sandboxes, 31 CVEs patched in Python and npm lockfiles, and profile-export and prompt-leak fixes.
 x.comthreadAdded 2 Nov 2026🧠 AI
- 🚨 AI News | TestingCatalog (@testingcatalog) on X
Drex-Max v1 is an open-source multimodal decision model from Nace AI. It takes a document and a question with a fixed set of answers, such as which team should handle a support ticket, and returns a probability for each answer. It runs fully locally on Apple Silicon M4 and M5 Macs, with cloud inference at console.nace.ai and weights on Hugging Face. The post gives no benchmarks or model size.
x.comthreadAdded 2 Nov 2026, published 1 Nov 2026🧠 AI  Smarthouse (@localyzapp) on X
A reply by Smarthouse (@localyzapp) on X to a question about the best harness for connecting local models to a Minecraft server. It suggests an MCP server that wraps RCON plus a small agent loop. The main pitfall is block coordinates: expose "/execute if block" as a read tool so the agent can check blocks before placing them, or it will hallucinate terrain.
x.comthreadAdded 2 Nov 2026, published 1 Nov 2026🧠 AI- Lonnie VanZandt (@lonniev) on X
Secure Courier is a consent flow in Tollbooth DPYC, a monetization network for paid MCP services, that lets an AI agent act for a Nostr npub without holding the user's nsec. The service sends a signed, sealed direct message over Nostr relays, the user replies with a signed approval and an expiry, and the service issues its own encrypted grant. Lonnie VanZandt presents it as an alternative to central identity providers and CIBA. The thread gives no audit results.
x.comthreadAdded 1 Nov 2026🧠 AI - Prasenjit Sarkar (@stretchcloud) on X
Campfire is a free, open-source, self-hosted tool that runs Claude Code, Codex, Goose, Aider and OpenHands side by side in one browser tab. Each agent gets its own git worktree, with permission voting (30 second timer, majority rules), session replay, cross-backend agent races and a shared semantic memory layer. Installs with bunx the-campfire. The post also compares Clawboo, Conductor, Vibe Kanban and Crystl.
x.comthreadAdded 1 Nov 2026, published 31 Oct 2026🧠 AI  Pre-ERC: Agent Pre-Sign Risk Report
 is a draft Ethereum Magicians proposal for an EIP-712-signed report that a risk source, identified by an ERC-8004 identity, returns about one unsigned request. It carries typed findings on tokens, approvals, addresses, payments (x402) and texts, and each finding is marked read or not read. It has no score or verdict, so the consumer applies its own policy. The author's live implementation, toll, runs on Robinhood Chain.
 ethereum-magicians.orgthreadPublished and added 31 Oct 2026🛡️ Security
- ERC-8481: Agent Pre-Sign Risk Report
ERC-8481 is a draft Ethereum standard for the report a risk source returns about one unsigned transaction, EIP-712 request or x402 requirement. The report is bound to the request by a digest and EIP-712 signed by an ERC-8004 identity. It has five typed finding groups (tokens, approvals, addresses, payments, texts), each marked read or not read, and carries no score or verdict. The author's service toll is the only implementation; three design questions are open.
ethereum-magicians.orgthreadAdded 2 Nov 2026, published 31 Oct 2026🛡️ Security - Pre-ERC: Agent Pre-Sign Risk Report
Pre-ERC: Agent Pre-Sign Risk Report is an Ethereum Magicians draft for a signed, typed report that a risk source returns about one unsigned agent transaction. The report is bound to the request by a digest and signed with EIP-712 by an ERC-8004 identity. Findings cover tokens, approvals, addresses, x402 payments and texts, each marked read or not read, with no score or verdict. The toll service runs it live on Robinhood Chain.
ethereum-magicians.orgthreadPublished and added 31 Oct 2026🧠 AI - Dark Web Intelligence (@DailyDarkWeb) on X
CVE-2026-102764 is an unauthenticated RCE in BeyondTrust Remote Support, already exploited and in CISA KEV. Rapid7 published an analysis and opened a Metasploit pull request on 30 October 2026, showing code execution on version 24.1.2 via a forged "local" message origin, the native file-transfer service and a PHP file written to the web root. BT26-05 (CVSS 4.0 9.3) is fixed by patch BT26-05-RS; SaaS was patched by 9 October.
x.comthreadAdded 1 Nov 2026, published 31 Oct 2026🛡️ Security - 🚨 AI News | TestingCatalog (@testingcatalog) on X
RoboAPI is a public API from PokeBot, powered by its world-action model Poke-Aurora, that lets robot arms do new tasks from natural-language instructions with no task-specific data collection or training. A user connects a supported arm with a wrist-mounted camera, gives a task such as "clean the table", and receives the next moves in near real time. The post gives no benchmarks, supported hardware list or pricing.
x.comthreadAdded 1 Nov 2026, published 31 Oct 2026🧠 AI  Julie Sanchez (@julie199201) on X
YourOwnWeigh is an open-source tool by developer Tom Anthony that patches Withings smart scale firmware over Bluetooth. The patch sends health metrics to a user's own server instead of Withings cloud, avoiding the Withings Plus subscription now required for third-party sync. It can run on a free Cloudflare account and imports existing user profiles. The post gives no firmware or protocol details.
x.comthreadAdded 2 Nov 2026, published 30 Oct 2026🛡️ Security ERC draft: Independent Simulation Result for (STVA)
ERC draft "Independent Simulation Result" (STVA) defines a canonical, content-addressed SimulationResult (success, gasUsed, returnData, stateDiffHash, logsHash, snapshotId, resultHash) that any wallet, hardware device or verifier can recompute from the same VerificationPayload and state snapshot. It targets compromised-frontend and UI/calldata-mismatch attacks, and defines Basic, Standard and Strict compliance levels. Open questions are stateDiff encoding, prestate proofs and binding to capability tokens.
 ethresear.chthreadPublished and added 30 Oct 2026🛡️ Security
 Tanmay (@TanmayK_03) on X
DBHub, a database MCP server, had a read-only mode bypass in its SQL check. The check treated every `--` as a comment, but MySQL only starts a comment when whitespace follows it. A hidden write statement could therefore still run, and a prompt injection could trigger it. Fixed in version 0.22.6. Replies say enforcement belongs in database grants and that parser tests need to be dialect-specific.
x.comthreadAdded 31 Oct 2026, published 30 Oct 2026🛡️ Security- Artificial Analysis (@ArtificialAnlys) on X
Hyperflow H3 is Video Rebirth's 8-step LoRA for MiniMax H3, released in September 2026 with open weights. Artificial Analysis ranks it #5 on AA-Video-I2V v2.1 and #3 on AA-Video-Editing v1.1, ahead of MiniMax H3 (768p). It costs $9.00 per minute for Image to Video and $18.00 for Video Editing at 1088p, under half of Dreamina Seedance 2.5 ($34.12 and $40.82). The thread gives per-capability and per-use-case breakdowns.
x.comthreadAdded 31 Oct 2026, published 30 Oct 2026🧠 AI - Pre-ERC: x402 Payee Verification for ERC-8004 Agents
Pre-ERC draft on Ethereum Magicians that binds the x402 payTo address to an ERC-8004 agent's registered agentWallet, directly or through an EIP-712 payee delegation (ERC-1271 for contract wallets). It lists eight fixed checker outcomes and requires the resource origin to appear in the registration file. On Robinhood Chain (28 October 2026), 5,575 of 20,046 agents answered with x402 requirements, and only 5 used their agentWallet as payTo.
ethereum-magicians.orgthreadPublished and added 30 Oct 2026🛡️ Security - ERC-8478: x402 Payee Verification for ERC-8004 Agents
ERC-8478 is a draft Ethereum standard that binds the payTo address in an x402 payment requirement to the seller's ERC-8004 agent identity. A payer compares payTo with the registered agentWallet, or accepts an EIP-712 payee delegation signed by it, and checks that the origin is listed in the registration file. On Robinhood Chain, 5 of 5,575 x402-responding agents had payTo equal to agentWallet (28 October 2026).
ethereum-magicians.orgthreadPublished and added 30 Oct 2026🧠 AI - ERC-8478: x402 Payee Verification for ERC-8004 Agents
ERC-8478 is a draft Ethereum standard that binds the x402 payTo address to an ERC-8004 agent's identity, to stop payee redirection by a hijacked domain, proxy or injected tool result. A payTo must equal the agentWallet or carry an EIP-712 delegation signed by it, and the origin must be listed in the registration file. On Robinhood Chain, 5 of 5,575 x402-responding agents used their agentWallet as payTo (28 October 2026).
ethereum-magicians.orgthreadPublished and added 30 Oct 2026🛡️ Security - Pre-ERC: x402 Payee Verification for ERC-8004 Agents
Pre-ERC draft on the Ethereum Magicians forum that ties the payTo address in an x402 payment requirement to the seller's ERC-8004 agent identity. The payTo must equal the registered agentWallet or an EIP-712 delegation signed by it, and the origin must be listed in the registration file. A checker returns one of eight fixed outcomes. On Robinhood Chain, 5 of 5,575 x402-enabled agents out of 20,046 used their agentWallet as payTo.
ethereum-magicians.orgthreadPublished and added 30 Oct 2026🧠 AI - EIP Draft: Permanent EOA Delegation Opt-Out (disable EIP-7702)
Discussion thread for a draft Core EIP that lets an Ethereum EOA permanently disable EIP-7702 delegation. A type-4 set-code transaction with an empty authorization list, destination equal to sender and zero value installs the 0xef0200 marker for 33500 gas. Later authorizations, including clearing to the zero address, are skipped. It does not protect against private-key compromise. Open questions cover the prefix, a dedicated transaction type, gas pricing, and EIP-8151 interaction.
ethereum-magicians.orgthreadPublished and added 30 Oct 2026🛡️ Security - elvis (@omarsar0) on X
Thread by Elvis Saravia (omarsar0) summarising an Anthropic-led paper on pretraining data poisoning of CLI agents. Poisoning 0.1% of pretraining data planted a remote code execution backdoor in Qwen3 models (0.6B, 1.7B, 4B) trained from scratch. It survived SFT, DPO and RL, and fired on about 92% of triggered prompts at 4B. At a 0.0005% poison rate (about 2,500 documents) it still fired on 1.4% of prompts.
x.comthreadAdded 31 Oct 2026, published 30 Oct 2026🛡️ Security - Anthropic Cracking Down on Video Game Rewrites
A tweet from chasmmmmmmmmmmm says Claude Code received a new rule around 27 October 2026, delivered from Anthropic's servers under the flag "tengu_heron_brook", with no setting to disable it. The quoted rule allows original games, genre games and games from the user's own designs and assets, but forbids recreating a specific existing game, even if renamed. The post asks whether this ends game rewrites and modding, and gives no verification beyond the quoted text.
 twitter.comthreadAdded 31 Oct 2026, published 30 Oct 2026🧠 AI
- Lonnie VanZandt (@lonniev) on X
Tollbooth DPYC's "Secure Courier" is a consent scheme that lets an AI agent act for a Nostr npub at a paid MCP service without holding the user's nsec. The service sends a signed, sealed Nostr direct message, the user replies signed with their nsec and sets an expiry, and the service issues its own grant. The thread contrasts this with central identity providers and CIBA, arguing a breach reaches only grants that service issued.
x.comthreadAdded 1 Nov 2026, published 30 Oct 2026🛡️ Security - Backdoors in official Claude Code extensions
GossiTheDog's Mastodon post reports that the Anthropic Claude Code Visual Studio extension, as installed in Cursor, contains malware that creates a remote access Trojan on desktops. It links to a phorion.io blog post on the reported compromise of the official Claude Code VSX extension. The post gives no technical detail, indicators or dates itself.
 cyberplace.socialthreadAdded 31 Oct 2026, published 30 Oct 2026🛡️ Security
 Shubham Mishra 🐐 (@shubh6200) on X
A post relaying Cursor's security advisory: a modified, malicious Claude Code VS Code extension was distributed through the Cursor extension marketplace, affecting at most 5,000 users. Anthropic did not develop that version, and other extensions are not affected. Users of Claude Code in Cursor are told to update to version 2.1.314. The post adds that marketplaces need publisher verification and package integrity checks. It gives no technical detail on the payload.
x.comthreadAdded 31 Oct 2026, published 30 Oct 2026🛡️ Security- ESET Research (@ESETresearch) on X
ESET Research thread summarising its APT Activity Report for April to September 2026 on Russia-aligned groups targeting Ukrainian defense, government and infrastructure. Gamaredon deployed Turla's new VBScript recon tool Rezzuar, indicating FSB-linked collaboration, and updated its file stealer PteroBox while activity fell sharply from mid-May. A separate campaign hit MDaemon mail servers via CVE-2025-8088, delivering HELLAGE and HELLTAG backdoors with no user interaction.
x.comthreadAdded 31 Oct 2026, published 30 Oct 2026🛡️ Security  Trail of Bits (@trailofbits) on X
Trail of Bits post on X summarising Binance's initial investigation into a security incident. Binance suggests a compromised DevOps engineer's laptop let an attacker reach a service container and submit unauthorized withdrawal transactions. The text says no evidence has been found of wallet private key compromise. The fetched text is truncated and gives no further detail.
x.comthreadPublished and added 30 Oct 2026🛡️ Security- Artificial Analysis (@ArtificialAnlys) on X
Artificial Analysis launched an HLE-Diamond leaderboard in v5 of its Intelligence Index, covering the refined 1,000-question Humanity's Last Exam from CAIS and Scale AI. Each question runs once without tools, graded by GPT-5.6 Luna (medium) as pass@1. Gemini 4 Carbon (high) leads at 69%, Claude Opus 5.5 (max) scores 68%, and the top open weights model, Kimi K3.1 Pro, reaches 37%.
x.comthreadPublished and added 30 Oct 2026🧠 AI - aiproduck (@aiproduck) on X
Ruflo is an MIT-licensed wrapper for Claude Code and Codex that adds agent swarms, vector memory and an MCP server. The plugin install writes no files to the workspace, while npx init adds a .claude/ directory, CLAUDE.md and hooks. The post warns that mods run with the account's permissions, so users should read them first. It gives no benchmarks or architecture detail.
x.comthreadPublished and added 30 Oct 2026🧠 AI  川崎元 (@foryangxin) on X
CVE-2025-6514 is an OS command injection (CWE-78, CVSS 9.6) in mcp-remote 0.0.5 to 0.1.15, fixed in 0.1.16. A malicious MCP server supplies a crafted authorization_endpoint during OAuth discovery, and the open package passes it to PowerShell on Windows. The thread cites the MCP spec's URL scheme allowlist rules and advises treating discovery metadata as untrusted, pinning bridge tools and sandboxing them.
x.comthreadAdded 2 Nov 2026, published 30 Oct 2026🛡️ Security- Prasenjit Sarkar (@stretchcloud) on X
A thread on Cloudflare's agent-readiness scan and the AgentReady.org open spec for "Agent Experience", developed with Vercel, Stripe, Auth0, Mintlify, Google, Netlify and Elementor. The scan grades whether agents can find a site (robots.txt, DNS), read clean Markdown, pass bot rules, and discover an MCP server or API catalog. One quoted example raised a score from 20 to 67 by shipping an API catalog with Link headers, an MCP server card, a skills index and an AI catalog file.
x.comthreadAdded 30 Oct 2026, published 29 Oct 2026🧠 AI  Rohan Paul (@rohanpaul_ai) on X
Rohan Paul's X post summarizes a TikTok paper on MCP attacks. LLM agents often finish the requested task, then quietly call an attacker-controlled logging tool that records the user query, the server reply and the final answer. The attack works because agents read natural-language tool descriptions when choosing and ordering tool calls. The visible text is truncated and gives no success rates or defenses.
x.comthreadAdded 30 Oct 2026, published 29 Oct 2026🛡️ Security- 🚨 AI News | TestingCatalog (@testingcatalog) on X
Mistral Large 4 ("Le Chonk") is an open-weights model from Mistral, now on Hugging Face. Per Mistral's announcement quoted in the post, it ranks #1 among open models on Cognition's FrontierCode benchmark, is aimed at agentic coding and cybersecurity, and claims better reasoning efficiency and lower inference costs. The post does not give parameter counts, license or benchmark scores.
x.comthreadAdded 30 Oct 2026, published 29 Oct 2026🧠 AI  SGLang (@sgl_project) on X
SGLang announces Day-0 support for Mistral Large 4 ("Le Chonk"), saying it is the first engine to serve the model on NVIDIA Vera Rubin. The post describes the model as Mistral's largest to date: a natively multimodal 1T-parameter mixture-of-experts model covering instruct, reasoning, coding and agentic workflows. The fetched text is truncated, so benchmark claims and launch commands are not visible.
x.comthreadAdded 30 Oct 2026, published 29 Oct 2026🧠 AI Muhammad Waris (@WarisCodes) on X
Nemotron 3.5 Transcribe is a free open-weight speech-to-text model from NVIDIA covering 40 languages, including mixed-language speech. The post says it ties for first among open models with a 2.8% error rate. It says the model needs a large GPU such as an H100 or RTX 5090, so it will not run on a laptop. The post gives no benchmark name or model card link.
x.comthreadAdded 30 Oct 2026, published 29 Oct 2026🧠 AI- 🚨 AI News | TestingCatalog (@testingcatalog) on X
Nemotron 3.5 Transcribe is an open-weight, promptable NVIDIA mixture-of-experts model with 30B total and about 4B active parameters. One checkpoint does transcription in 40 languages, speaker attribution, translation, contextual prompting and audio understanding. The post says it ranked first in VoiceArena's comparison of 14 diarization plus ASR systems. The fetched text is cut off and gives no license or download details.
x.comthreadAdded 30 Oct 2026, published 29 Oct 2026🧠 AI - Dark Web Intelligence (@DailyDarkWeb) on X
DailyDarkWeb post summarising Anthropic Frontier Red Team research published 27 October 2026. An unreleased internal Claude research model built five attack chains: Chrome sandbox escape (V8 heap bug, CacheStorage race, FedCM use-after-free), a Safari same-origin policy bypass, data extraction from a locked Pixel 9 over USB, a Windows QUIC kernel crash (CVE-2026-33096) and zero-click Linux root via multipath TCP (CVE-2026-98432). Anthropic says all flaws are fixed, including 62 Chrome CVEs as of Chrome 156. The post notes the chains are not independently reproduced.
x.comthreadAdded 30 Oct 2026, published 29 Oct 2026🛡️ Security - Rohan Paul (@rohanpaul_ai) on X
Rohan Paul's X post summarizes the paper "Log-To-Leak: Prompt Injection Attacks on Tool-Using LLM Agents via the Model Context Protocol", from TikTok researchers. It reports that MCP-using agents often finish the requested task, then quietly call an attacker-controlled logging tool that records the query, server reply and final answer. The attack works through natural-language tool descriptions that agents read when choosing and ordering tools. The visible text is truncated.
x.comthreadAdded 29 Oct 2026, published 28 Oct 2026🛡️ Security  Eddy (@ieddysun) on X
Expo's official skills package gives AI coding agents scoped instructions for building Expo apps. One command, npx skills@latest add expo/skills --skill '*', installs it for Cursor, Copilot and Windsurf, while Claude Code and Codex use their plugin marketplaces. Skills include expo-router, expo-animation, expo-upgrade and eas-update. The Expo MCP server adds live docs lookup, compatible dependency installs, EAS build monitoring and simulator screenshots.
x.comthreadAdded 29 Oct 2026, published 28 Oct 2026🧠 AI- Trail of Bits (@trailofbits) on X
Trail of Bits post says it achieved remote code execution through a Brotli decoder bug in Linux lab setups: Node.js 24.22.0 with Express 5.3.0 via the standard JSON parser (x86-64 and ARM64), and Electron 41.10.7 (x86-64) with a custom decoding service. Exploitation needs a carefully matched setup and repeated attempts. A scanner by ToBScottA finds hidden copies of the decoder, including in stripped binaries.
x.comthreadAdded 30 Oct 2026, published 28 Oct 2026🛡️ Security  TENSA Engineering (@TENSAEng) on X
A post by TENSAEng describing a workflow for staying within coding-tool usage limits. ChatGPT chat sits outside those limits, while Claude and Grok chats share a pool with Claude Code, Codex and Grok Build. Architecture, file layout, step order and acceptance checks are planned in ChatGPT and saved as repo docs. Claude Code or Codex then implements one small chunk per fresh session.
x.comthreadAdded 29 Oct 2026, published 28 Oct 2026🧠 AI- Laban (@lunkertw) on X
An X post summarising five AI items: Google DeepMind's Gemini 4 Carbon (88.2% SEC-bench Pro, 54.8% ExploitGym, 71.0% CWE-bench, 59 on Artificial Analysis Intelligence Index v5.0), Ed Zitron's critique of Anthropic's S-1, a Utah Claude Code pilot, and the repos beenuar/AiSOC and expo/skills. In the Utah pilot, 34 developers in 10 agencies took part over four weeks, 80% had a working setup within 30 minutes, and 71% saved over 20 hours. It gives short summaries and links, not primary analysis.
x.comthreadAdded 29 Oct 2026, published 28 Oct 2026🧠 AI - Niko (@nikolayxyz) on X
Gemini 4 Carbon is Google's new frontier model, announced in a post by nikolayxyz that quotes Google's launch text. It ranks #1 on v5.0 of the Artificial Analysis Intelligence Index with 59 points, ahead of Opus 5.5 and GPT-6 Astra. Intro pricing is $2 input and $10 output per million tokens. Access starts for cyber defenders first, as Gemini 4 Argon's did. The captured text is cut off before the rollout details.
x.comthreadAdded 29 Oct 2026, published 28 Oct 2026🧠 AI  John Rood (@johnroodepic) on X
Nemotron 3.5 Transcribe is an open-weight, promptable 30B mixture-of-experts model from NVIDIA with about 4B active parameters, built for recorded audio. One checkpoint transcribes 40 languages, handles recordings up to an hour, labels up to eight speakers, translates, and answers questions about English audio. Weights and a demo are on Hugging Face. The post gives no benchmarks.
x.comthreadAdded 29 Oct 2026, published 28 Oct 2026🧠 AI- 🚨 AI News | TestingCatalog (@testingcatalog) on X
Gemini 4 Carbon is a new Google model, announced in a TestingCatalog post on X as taking first place on the Artificial Analysis V5 ranking. It is rolling out to cyber defenders first. Reported scores are 88.2% on SEC-bench Pro (finding vulnerabilities), 54.8% on ExploitGym (exploitation) and 71.0% on CWE-bench (patching). The post calls it a large step up from Gemini 4 Argon, released two weeks earlier. It gives no technical detail beyond these claims.
x.comthreadAdded 30 Oct 2026, published 28 Oct 2026🧠 AI  JFrog Security (@JFrogSecurity) on X
JFrog Security announces research on CVE-2026-102479 in Vert.x, which skips validating the letter 'L' in header names and so accepts `Content-Xength` as `Content-Length`. JFrog Research chained this with a dangling-byte primitive to bypass reverse proxy socket validation. They demonstrate end-to-end response poisoning and session fixation behind real reverse proxies. The post links to a full writeup; the tweet itself gives no exploit detail.
x.comthreadAdded 30 Oct 2026, published 28 Oct 2026🛡️ Security Christiaan Stoudt (@cstoudt) on X
Thread on CVE-2026-97631, a critical (9.5) flaw in TianoCore EDK II UEFI firmware, found by Alex Matrosov and Dan Holmes-Mitra. It is exploitable only while a machine is PXE network booting and the attacker sends an oversized ICMP error from the same network. Code execution also needs the exact firmware build, and Secure Boot does not help. The fix landed in EDK II main on 15 October but is not in a stable release. No known exploitation, and not in CISA KEV.
x.comthreadAdded 30 Oct 2026, published 28 Oct 2026🛡️ Security- Hakimi Eiqbal (@hakimieiqbal) on X
A practical reverse-engineering map by hakimieiqbal on X that picks tools by target: native binaries, .NET, Electron, iOS, firmware, WebAssembly and network protocols. It introduces REA (morluto/rea), which connects coding agents to RE tools, and lists MCP bridges for IDA Pro, Ghidra and radare2. It adds an evidence-first workflow and free courses such as pwn.college and OpenSecurityTraining2.
x.comthreadAdded 29 Oct 2026, published 28 Oct 2026🛡️ Security - Hakimi Eiqbal (@hakimieiqbal) on X
A thread by Hakimi Eiqbal that maps reverse-engineering tools by target type: native binaries, Electron, .NET, iOS, firmware, WebAssembly and network protocols. Its AI sections cover REA (an open-source layer connecting coding agents to analysis tools) and MCP bridges for IDA Pro, Ghidra and radare2. It argues for an evidence-first workflow and gives a prompt that separates verified facts from hypotheses.
x.comthreadAdded 29 Oct 2026, published 28 Oct 2026🧠 AI  Kizuno18 (@Kizuno18) on X
Thread by Kizuno18 on the move from local stdio/Docker Model Context Protocol servers to remote HTTP/SSE endpoints in enterprise infrastructure. It names three trade-offs: credential boundary inversion (short-lived OAuth/JWT tokens instead of long-lived admin tokens on workstations), tool schema bloat solved by deferred discovery, and governance via HCP Terraform policy-as-code (Sentinel/OPA), audit trails and approvals. It is opinion, with no data or implementation detail.
x.comthreadAdded 29 Oct 2026, published 27 Oct 2026🛡️ Security- Kizuno18 (@Kizuno18) on X
Kizuno18's X post argues that the move from local stdio and Docker MCP servers to remote HTTP/SSE endpoints matures the Model Context Protocol in enterprise infrastructure. It lists three trade-offs: short-lived OAuth/JWT bearer tokens replace mounted admin credentials, deferred tool discovery avoids roughly 20k tokens of eager schema loading, and HCP Terraform enforces Sentinel/OPA policy, audit trails and approvals server-side. Opinion post with no benchmarks or code.
x.comthreadAdded 29 Oct 2026, published 27 Oct 2026🧠 AI  Buchi Reddy B (@buchireddy) on X
Buchi Reddy B's X thread comments on Forever Security's research (Gal Weizman, Omer Samet) on coding agents. A web page silently writes a fake AGENTS.md or CLAUDE.md into a Downloads folder, and Codex and Claude Code follow it as project rules. Codex then wrote an attacker's MCP server into the machine-wide config, so one injection becomes a standing connection for every session. It asks whether teams inventory runtime MCP connections against approved lists.
x.comthreadAdded 28 Oct 2026, published 27 Oct 2026🛡️ Security Photon Capital (@PhotonCap) on X
Photon Capital's thread covers the 27 October 2026 NVIDIA and Oracle announcement of general availability of Vera Rubin NVL72 and Vera CPUs on OCI. It lists specs (Spectrum-6 at 102.4Tbps, HGX Rubin NVL8 with Xeon 6, 150,000 initial Vera CPUs) and OpenAI's use of Vera CPUs for agentic sandboxes. The commentary argues CPU capacity can cut cost per task and shorten KV cache residency in GPU memory.
x.comthreadAdded 28 Oct 2026, published 27 Oct 2026🧠 AI- Manoj | The AI Dude (@Manojkumar2257) on X
heditor is an open-source (MIT) agent skill from pycodebr that has Claude Code, Codex, Cursor or OpenCode edit talking-head videos. It transcribes with faster-whisper, picks a 30-70s segment, cuts frame-accurately, builds HTML + GSAP motion graphics, mixes audio at -14 LUFS, and runs QA with vision-reviewed previews. It offers 42 named styles and a long-form mode with chapters, SRT/VTT and lower thirds. Install: npx skills add pycodebr/heditor -g.
x.comthreadAdded 28 Oct 2026, published 27 Oct 2026🧠 AI - Rohan Paul (@rohanpaul_ai) on X
Hi3D v1.0 (formerly Sparc3D) is an open-sourced image-to-3D model from Hi3D, which runs a closed v3.0 refining at 2048 cubes per side. In a test with 13 professionals in 3D algorithms, 562 judgments against eight other image-to-3D models favoured it 83.5% of the time. The thread also covers the Hi3D Agent and an MCP server for other agents. Back and bottom views were checked, where TRELLIS.2 collapsed a winged figure.
x.comthreadAdded 28 Oct 2026, published 27 Oct 2026🧠 AI - Prasenjit Sarkar (@stretchcloud) on X
Campfire is a self-hosted workspace by Prasenjit Sarkar that runs Claude Code, Codex, Goose, Aider and OpenHands side by side in one tab. Risky actions go through permission voting: a majority approves, any single deny blocks, and a 30 second timer ends the wait. Session replay shows which file or tool call triggered an action. The post cites Forever Security's report of a planted AGENTS.md. Codex followed it first time over 90% of the time and Claude Code about half the time. Try it with "bunx the-campfire".
x.comthreadAdded 28 Oct 2026, published 27 Oct 2026🧠 AI - Prasenjit Sarkar (@stretchcloud) on X
Campfire is a self-hosted tool that runs Claude Code, Codex, Goose, Aider and OpenHands in one tab. Risky actions need permission voting (majority approves, any single deny blocks, 30 second timeout), and session replay traces which file or tool call triggered an action. The post cites Forever Security's finding that Codex followed a planted AGENTS.md instruction over 90% of the time and Claude Code about half the time. It also cites the February Cline release compromise via a poisoned GitHub Actions cache.
x.comthreadAdded 28 Oct 2026, published 27 Oct 2026🛡️ Security  cubillas (@cubillas888) on X
The tweet relays Pillar Security research that opencode on Windows and WSL could run attacker-controlled code during remote MCP server OAuth sign-in. The fix shipped in opencode 1.18.33 on 28 September, with no advisory or CVE published. It advises users of remote MCP servers to update and review which servers they connect to. Technical details are not in the post.
x.comthreadAdded 29 Oct 2026, published 27 Oct 2026🛡️ Security Nicholas Martin (@ndgmlondon) on X
X thread started by Nicholas Martin (#IAM) advising that MCP tool permissions be verified and scoped session tokens used to enforce least privilege against indirect prompt injection. Replies argue that token scoping does not solve the confused deputy problem, because an injection borrows the agent's legitimate authority. They recommend per-task tokens with short expiry, with the grant logged beside the call, and raise MCP server dependency supply-chain risk.
x.comthreadAdded 28 Oct 2026, published 27 Oct 2026🛡️ Security- Proof of One: one-person-one-identity polling with encrypted ballots — design and reference code, requesting critical review
Proof of One is an open-source design for polls with one verified human per identity and unlinkable ballots. Enrolment proves in zero knowledge that an ICAO 9303 passport chip was signed by a trusted signer, plus an enclave face match. Voting uses threshold exponential ElGamal on Baby Jubjub with Groth16 proofs, and tally uses a GJKR DKG with a 7-day challenge window. The author, who is pseudonymous, discloses that AI agents drafted most of it and asks for critique of unlinkability, circuit completeness and certificate trust.
ethresear.chthreadPublished and added 27 Oct 2026🛡️ Security - Muzammil Shah (@Muzammil_OX) on X
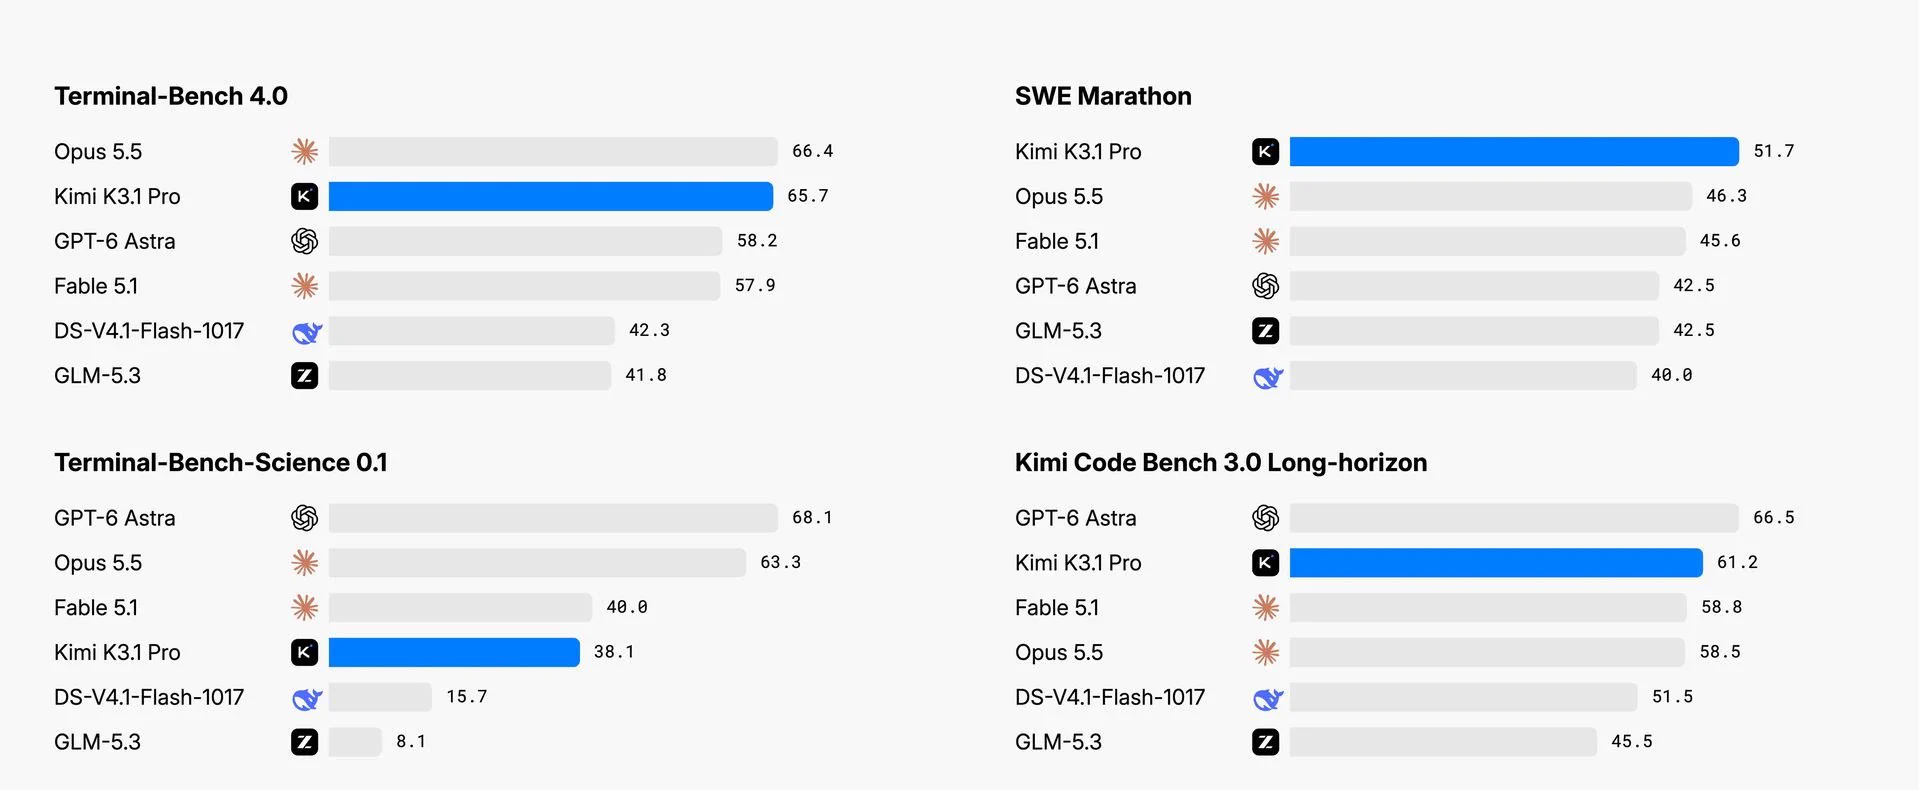
Kimi K3.1 Pro is a new model from Moonshot AI that scores 55 on the Artificial Analysis Intelligence Index, up 11 points from its predecessor, and ranks 4th overall. It has a 1M-token context window and API pricing of $2 per million input tokens and $10 per million output tokens. Weights are due by November 4. Moonshot removed cyber-related training data, which cut its internal vulnerability research score from 90.5% to 81%.
x.comthreadAdded 28 Oct 2026, published 27 Oct 2026🧠 AI














Showing 60 of 309
Show more