- CISA Adds Two Known Exploited Vulnerabilities to Catalog
CISA added two Ivanti Connect Secure vulnerabilities to its Known Exploited Vulnerabilities (KEV) Catalog on 30 October 2026, citing evidence of active exploitation: CVE-2026-111357 (missing authentication for a critical function) and CVE-2026-118527 (generation of predictable numbers or identifiers). The alert restates BOD 26-04, which requires federal civilian agencies to remediate KEV-listed flaws on exposed assets and check for prior compromise. It also links the KEV nomination form.
 cisa.govadvisoryPublished and added 30 Oct 2026🛡️ Security
 CISA says max severity GitLab flaw now exploited in the wild
CVE-2026-97229 is a maximum-severity GitLab flaw in the CI/CD Regular Expression Compiler, caused by an integer overflow, that lets unauthenticated attackers run code via a crafted regular expression. CISA added it to the KEV Catalog and ordered federal agencies to patch under BOD 26-04. GitLab fixed it in CE/EE 19.4.2, 19.3.5 and 19.2.8, and Shadowserver tracks about 2,800 exposed CE instances.
 bleepingcomputer.comarticlePublished and added 30 Oct 2026🛡️ Security
 Drupal warns of critical Commerce Core flaw exploited in attacks
Drupal Commerce Core has a critical missing-authorization flaw, CVE-2026-118539, that unauthenticated attackers exploit in the wild. It affects versions 0.0.0 to 2.41 and 3.0.0 to 3.3.13. Drupal urges upgrading to 3.3.13 (or 8.x-2.41 on the older branch) and auditing orders for inconsistencies. The article also recalls CVE-2026-9082, exploited in May and added to CISA KEV, and two RCE patches (CVE-2026-108097, CVE-2026-108099).
bleepingcomputer.comarticlePublished and added 30 Oct 2026🛡️ Security Max-Severity GitLab Vulnerability Exploited Against Alpine Linux
CVE-2026-97229 is a CVSS 10 code execution flaw in Onigmo, Ruby's regular expression engine, reachable through crafted CI/CD configuration in GitLab. Attackers used it against Alpine Linux's GitLab on 20 and 21 October 2026 and failed; Alpine rebuilt the instance and found no tampering with aports or packages. Self-managed installs with their own Ruby need Ruby 3.3.13, 3.4.12 or 4.0.9, not just GitLab 19.3.6. CISA added it to KEV.
 securityweek.comarticlePublished and added 30 Oct 2026🛡️ Security
- CISA Adds Two Known Exploited Vulnerabilities to Catalog
CISA alert of 29 October 2026 adding two vulnerabilities to the Known Exploited Vulnerabilities catalog on evidence of active exploitation: CVE-2026-97229, an integer overflow in GitLab CE/EE, and CVE-2026-76418, a NULL pointer dereference from an unchecked return value in Cisco Secure Firewall ASA and FTD. It restates BOD 26-04 remediation duties for federal civilian agencies and links the KEV nomination form.
cisa.govadvisoryPublished and added 29 Oct 2026🛡️ Security  A quiet week in infosec <.<
Cisco Talos Threat Source newsletter for the week of the PHP and Node.js vulnerability news cycle. It summarises NIK C2, a Go-based Windows implant that dumps credentials, streams keystrokes, deploys screen-locking ransomware and uses a victim's hijacked OpenAI API keys to analyse stolen data. It also lists weekly headlines (CISA KEV PHP bugs, Brotli flaw, Gheist GitHub token theft), Talos links and top malware hashes.
 blog.talosintelligence.comarticlePublished and added 29 Oct 2026🛡️ Security
 CISA warns of Fragnesia Linux flaw chained in PHP2Shell attacks
Fragnesia (CVE-2026-46300) is a Linux kernel XFRM ESP-in-TCP logic bug in the Dirty Frag class that gives local attackers root, with a public PoC. CISA added it to the KEV catalog and ordered federal patching under BOD 26-04. Attackers chain it with PHP2Shell (CVE-2026-109618, CVE-2026-109619) to implant PHP webshells. Dream Security tied the chain to 25 rooted servers in the US, Japan, Taiwan and South Korea.
bleepingcomputer.comarticleAdded 30 Oct 2026, published 29 Oct 2026🛡️ Security- lee1981 (@lee1981b) on X
CVE-2026-103780 is a stack-based buffer overflow (CWE-121) in Dell PowerProtect Data Domain / DD OS. An unauthenticated remote attacker could get command execution (CVSS 3.1 9.8, Dell DSA-2026-416). The post lists affected and fixed builds for four release trains (Feature Release, LTS2024, LTS2025, LTS2026). It adds KEV, EPSS and SSVC status, plus six defensive checks. The vulnerable service is not public.
 x.comadvisoryAdded 31 Oct 2026, published 29 Oct 2026🛡️ Security
- Chinese Hackers Quietly Used Low-Severity ESXi Logging Flaw as Zero-Day
CVE-2026-41709 is a low-severity insufficient-logging flaw in VMware ESXi that lets a logged-in administrator perform operations without audit entries. CISA added it to the KEV catalog, and CrowdStrike reported that China-nexus actor Warp Panda used it as a zero-day against US organizations, including law firms, to cut audit visibility. The article also covers exploitation of vCenter bugs CVE-2026-59309 and CVE-2026-59310 and lists the fixed ESXi builds.
securityweek.comarticlePublished and added 29 Oct 2026🛡️ Security - CISA Adds Two Known Exploited Vulnerabilities to Catalog
CISA alert of 28 October 2026 adding two vulnerabilities to the Known Exploited Vulnerabilities Catalog on evidence of active exploitation: CVE-2026-41709 (Broadcom VMware ESX insufficient logging) and CVE-2026-46300 (Linux kernel missing variable initialization). It restates BOD 26-04, which requires federal civilian agencies to prioritize fast remediation of KEV CVEs on exposed assets and to check for prior compromise. It also links the KEV nomination form.
cisa.govadvisoryAdded 29 Oct 2026, published 28 Oct 2026🛡️ Security  Christiaan Stoudt (@cstoudt) on X
Thread on CVE-2026-97631, a critical (9.5) flaw in TianoCore EDK II UEFI firmware, found by Alex Matrosov and Dan Holmes-Mitra. It is exploitable only while a machine is PXE network booting and the attacker sends an oversized ICMP error from the same network. Code execution also needs the exact firmware build, and Secure Boot does not help. The fix landed in EDK II main on 15 October but is not in a stable release. No known exploitation, and not in CISA KEV.
x.comthreadAdded 30 Oct 2026, published 28 Oct 2026🛡️ Security- lee1981 (@lee1981b) on X
CVE-2026-92885 is a critical (CVSS 3.1 9.8, CWE-287) authentication bypass in the Qode Membership WordPress plugin, versions through 2.0.6.2. A misspelled variable in the Facebook token-verification guard skips provider checks, so an unauthenticated attacker with a public nonce can get a session cookie for an existing account, including an administrator. The post gives the fix (2.0.6.3, bundled in Bridge 30.9), KEV/EPSS/SSVC status, and a SOC log-correlation and remediation plan.
x.comadvisoryAdded 31 Oct 2026, published 28 Oct 2026🛡️ Security  CISA Warns of Node2Shell Exploitation as Honeypots Log Attack Attempts
CVE-2026-111497 (Node2Shell, also HTTP2Shell and Broccoli2Shell) is an out-of-bounds write in the Brotli decoder, affecting versions 1.0.3 through 1.2.0. CISA added it to the KEV catalog on 27 October 2026 with a federal deadline of 10 November. Previdian and ELLIO logged exploitation attempts; ELLIO found the observed exploit broken but achieved code execution itself, and Broadcom's VMware SDDC Manager patches are pending.
securityweek.comarticlePublished and added 28 Oct 2026🛡️ Security- CISA Adds Two Known Exploited Vulnerabilities to Catalog
CISA alert of 27 October 2026 adding two vulnerabilities to the Known Exploited Vulnerabilities (KEV) Catalog on evidence of active exploitation: CVE-2026-48356, an unrestricted upload of a dangerous file type in Adobe Commerce and Magento, and CVE-2026-111497, an unchecked return value in Google Brotli. It restates BOD 26-04, which makes federal civilian agencies prioritise KEV flaws on exposed assets and check for prior compromise. No technical detail or IOCs are given.
cisa.govadvisoryAdded 29 Oct 2026, published 27 Oct 2026🛡️ Security - lee1981 (@lee1981b) on X
CVE-2026-115905 is a ZIP cloaking flaw in the Rust zip crate (zip-rs/zip2), rated CVSS v4.0 10.0 and affecting versions below 9.0.5. ZipArchive reads central-directory metadata while ZipStreamReader reads local headers, so a crafted archive can pass filename inspection and then overwrite a different file during streaming extraction. Version 9.0.5 adds consistency checks, but ZipStreamReader::new leaves them off by default, and extraction is not atomic, so files can be written before an error is raised. The post covers CWE-20 and CWE-436, KEV and EPSS status, Debian status and a six-step investigation trail.
x.comadvisoryAdded 29 Oct 2026, published 27 Oct 2026🛡️ Security  This is Fine: What NetScaler Zero-Days Tell Us About the New Normal
This SecurityWeek commentary covers the September 2026 Citrix NetScaler ADC and Gateway zero-days, exploited from mid-month and patched on 27 September as unauthenticated RCE flaws CVE-2026-88771 through CVE-2026-88778. The author argues the fast response shows stronger defence. Cited evidence: Citrix disclosure time fell from about 40 days to 17 in 2026 after it set up a NetScaler CNA, and CISA made a rare Sunday KEV addition.
securityweek.comarticlePublished and added 27 Oct 2026🛡️ Security Maritime Coalition Launches Free Vulnerability Database for Ship and Port Systems
Blue Initiative is a free public vulnerability database for maritime IT and OT, built by Cydome, ClassNK, Bureau Veritas, MTS-ISAC and Rakuten Maritime. It holds nearly 30,000 entries, over 2,000 rated critical by CVSS and more than 580 known exploited. Only 37 affect ship and port products. Most entries are pulled from CISA ICS advisories and the KEV catalog and mapped to maritime systems.
securityweek.comarticlePublished and added 27 Oct 2026🛡️ Security- CISA Adds Two Known Exploited Vulnerabilities to Catalog
CISA added two PHP vulnerabilities to its Known Exploited Vulnerabilities Catalog on 26 October 2026: CVE-2026-109618 (memory corruption) and CVE-2026-109619 (stale internal request state). It also updated its PHP alert on critical vulnerabilities requiring immediate patching. The alert restates BOD 26-04, which requires federal civilian agencies to prioritize fast remediation of KEV CVEs on exposed assets and to check for prior compromise.
cisa.govadvisoryAdded 29 Oct 2026, published 26 Oct 2026🛡️ Security  PHP2Shell Exploitation Moves From Probes to Working Shells
PHP2Shell exploitation (CVE-2026-109618, CVE-2026-109619) reached working shells on 24 October 2026, when Perplexity researcher Adel Karimi's honeypots (PHP 8.4.26, Apache mod_php, single worker) logged 35 shells across three servers. Attackers used a four-stage HTTP chain: memory exhaustion, memory leak, then shell command execution, matching a public PoC. No second-stage payload was seen, and CISA had not added the flaws to KEV as of 26 October.
securityweek.comarticlePublished and added 26 Oct 2026🛡️ Security- lee1981 (@lee1981b) on X
CyberForge CVE of the Day #087 covers CVE-2026-115889, a Cranelift value-index overflow in Wasmtime that can miscompile crafted WebAssembly and possibly escape the sandbox (CVSS 9.9, CWE-197 and CWE-843). Affected: below 36.0.19, and 37.0.0 up to but excluding 43.0.0; fixes are 36.0.19 and 43.0.0. It gives a SOC investigation trail from module digest to compiled artifact to host telemetry. EPSS is 0.454%, with no KEV entry.
x.comarticleAdded 28 Oct 2026, published 26 Oct 2026🛡️ Security - lee1981 (@lee1981b) on X
CyberForge Weekly CVE Rundown #007 covers six CVEs from 19 to 24 October 2026: SiteGuard command injection (CVE-2026-106931), DB-GPT (CVE-2026-77932), Siemens Software Center DLL side-loading (CVE-2026-110936), Cisco Expressway (CVE-2026-76466), Node.js Brotli (CVE-2026-111497) and Arista VeloCloud (CVE-2026-114625). Each entry gives defender actions, fixed versions, exploitation status and primary-source links. Updated 25 October 2026 with CISA KEV and EPSS findings.
x.comarticleAdded 27 Oct 2026, published 25 Oct 2026🛡️ Security - lee1981 (@lee1981b) on X
CVE-2026-111497 is an out-of-bounds write in the Brotli decoder bundled with Node.js (CWE-787, CWE-252), rated CVSS v4.0 9.2 by the Google CNA and High by the Node.js project. Fixes are Node 22.23.4, 24.22.1 and 26.12.1, and 24.22.1 still labels Brotli 1.2.0 because the fix was cherry-picked. The post gives a SOC trail from input to worker, with remediation and verification steps. It notes no KEV match, CISA SSVC exploitation none, and only unverified public lab claims.
x.comadvisoryAdded 26 Oct 2026, published 23 Oct 2026🛡️ Security - lee1981 (@lee1981b) on X
CyberForge CVE of the Day #084 analyses CVE-2026-76466, a CVSS 9.8 flaw in clustered Cisco Expressway-C and Expressway-E. Persistent database cookies and weak client-certificate validation allow root OS command execution over the network. The fix is X15.5.20 (X14 and earlier must migrate), with no workaround. It adds a per-peer SOC investigation trail, reachability checks and exposure status from CISA SSVC, KEV and EPSS.
x.comadvisoryAdded 24 Oct 2026, published 22 Oct 2026🛡️ Security - lee1981 (@lee1981b) on X
CVE-2026-110936 is an uncontrolled DLL search path flaw (CWE-427) in Siemens Software Center below V4.0.9.8, listed in CISA KEV on 20 October 2026. The post covers CVSS v4.0 8.4 and v3.1 6.7, Siemens' Romulus ClickFix campaign indicators (IPs, domain, hashes, file leads) and a six-step SOC trail using Sysmon, EDR and network records. It separates delivery from DLL load and from compromise.
x.comarticleAdded 24 Oct 2026, published 21 Oct 2026🛡️ Security  Threat Brief: Active Exploitation of PAN-OS CVE-2026-0257 (Updated Oct 20)
Unit 42 threat brief on active exploitation of CVE-2026-0257, a PAN-OS GlobalProtect authentication bypass added to CISA KEV on May 13, 2026. It lists IP addresses, host IDs and PoC-derived client values to hunt in GlobalProtect logs. The October 2026 updates cover Qilin and Inc ransomware operators, MFA bypass, pivots to vCenter and ESXi with offline VMDK credential dumping, and management interface exposure on ports 4443 and 3879.
 unit42.paloaltonetworks.comadvisoryAdded 21 Oct 2026, published 20 Oct 2026🛡️ Security
 There's only so much code: the rise in vulnerability numbers
Cisco Talos analysis of why Microsoft Patch Tuesday advisories rose from about 100 a month before June 2026 to 975 in September and 1,415 in October, as frontier models such as Mythos mine old code. CVEs grew 105% year over year while CISA KEV additions grew 37%, and only three September advisories were exploited in the wild. It covers pressure on 90-day coordinated disclosure and open-source maintainers, the format string bug-class precedent, and defender advice.
blog.talosintelligence.comarticlePublished and added 20 Oct 2026🛡️ Security- lee1981 (@lee1981b) on X
CVE-2026-77932 affects DB-GPT through 0.8.2 (dbgpt-app). The /api/v1/chat/react-agent route accepts unauthenticated requests because get_user_from_headers returns an admin-role user, and the ReAct agent can reach unsandboxed Python and shell tools. Lasso reported root in the webserver container in a lab. The post gives CVSS 9.8 and 9.3, no verified fix (0.8.2 is still the latest release), no KEV match, no EPSS data, and a SOC hunting trail.
x.comadvisoryAdded 23 Oct 2026, published 20 Oct 2026🛡️ Security  Exploited Fortinet Bug Linked to Stealthy FortiGate Implant in Telecom Hack
UNC5820 (tracked by Palo Alto Networks as CL-STA-0954) breached a telecom in September 2024 using FortiManager flaw CVE-2024-47575 (FortiJump) and path traversal CVE-2025-61624, then deployed PeerStitch, a memory-resident ARM64 FortiGate implant. PeerStitch patches FortiOS log and IKE/IPsec daemons to build a covert bridge without listening ports. The actor also impersonated FortiManager over FGFM, using CVE-2024-26008. CISA added CVE-2025-61624 to KEV.
securityweek.comarticlePublished and added 19 Oct 2026🛡️ Security- Saylor (@Kev96790724) on X
G-Krusch is an MIT-licensed, local-first Google Workspace hub built on Node.js 22 and SQLite WAL. It runs a 12-tool MCP server (SSE and Stdio) plus a REST bridge on port 5446 for Drive, Calendar and Gmail. It includes a 1,024-dimension hybrid Drive RAG with an embedding cascade (Ollama bge-large, then Gemini, then offline fallback) and FTS5 BM25. PDF extraction returns page citations. Tokens are kept in an AES-256-GCM vault; 30 of 30 tests pass.
x.comrepoAdded 21 Oct 2026, published 19 Oct 2026🧠 AI - Dark Web Intelligence (@DailyDarkWeb) on X
Plex2Shell is a chain of four Plex Media Server flaws (CVE-2026-96652, CVE-2026-96654, CVE-2026-96655, CVE-2026-96656) that a researcher says ends in unauthenticated RCE on servers older than 1.43.3.10861. A write-up and PoC were published on 16 October 2026. CISA advisory VA-26-266-01 scores the individual CVEs 4.3 to 7.2, and they are not in CISA KEV. The post advises updating, avoiding exposure of port 32400, and checking for unknown child processes and new files in the Codecs folder.
x.comthreadAdded 19 Oct 2026, published 18 Oct 2026🛡️ Security - lee1981 (@lee1981b) on X
CyberForge Weekly CVE Rundown #006 covers six CVEs from 12-17 October 2026: BotSharp default signing key, GitLab CI/CD regex compiler overflow (CVSS v3.1 10.0), Ivanti Connect Secure auth bypass, Cisco Secure Email Gateway, BeyondTrust Remote Support and the Linux kernel PwnEscape guest-to-host bug. It gives fixed versions, KEV and EPSS status as of 18 October, and separates patch verification from compromise investigation.
x.comarticleAdded 20 Oct 2026, published 18 Oct 2026🛡️ Security - Dark Web Intelligence (@DailyDarkWeb) on X
DailyDarkWeb update on CVE-2026-21589, a pre-auth file-read flaw in Atlassian Data Center products. The CVE record was rejected on 16 October 2026 with a generic reason and no replacement ID, but Atlassian's advisory (CVSS v4.0 9.3, Critical) and the CISA KEV listing (added 15 October, federal due date 18 October) remain. The analyst note says to keep patching to the fixed versions and track versions, not only the CVE ID.
x.comthreadAdded 19 Oct 2026, published 18 Oct 2026🛡️ Security  Frequently Asked Questions About the BeyondTrust Remote Support Arbitrary File Upload (CVE-2026-102764)
CVE-2026-102764 is an arbitrary file upload in BeyondTrust Remote Support (formerly Bomgar) caused by internal appliance components not validating message origin. Mandiant found it exploited as a zero-day in late August 2026. BeyondTrust disclosed it on 15 October 2026 and CISA added it to KEV on 16 October 2026. The FAQ covers the web shell, root escalation, credential theft, persistence, patching and compromise checks.
 watchtowr.comadvisoryAdded 30 Oct 2026, published 16 Oct 2026🛡️ Security
 I Want to Ride My BIKE: Customizing Bit-Flipping Decoders for Ephemeral Key KEMs
ePrint paper presenting the first optimized implementation of the BF-max bit-flipping decoder for the code-based KEM BIKE, combined with other decoders to trade off decoding failure rate, runtime, public-key and ciphertext size in ephemeral-key settings. It cuts public-key and ciphertext sizes by 7.8% versus LeanBIKE at similar speed and DFR, and gives a combined size 22% below BIKE and 2.79x below HQC. It shows BIKE can fit constrained protocols such as IKEv2, which matters for practical post-quantum migration.
 eprint.iacr.orgpaperAdded 17 Oct 2026, published 16 Oct 2026🛡️ Security
 BeyondTrust Remote Support Arbitrary File Upload (CVE-2026-102764)
CVE-2026-102764 is a CVSS 9.8 unauthenticated arbitrary file upload flaw in BeyondTrust Remote Support (formerly Bomgar) and Privileged Remote Access. Internal messaging components do not verify message origin, so remote attackers can plant files the appliance would reject. BeyondTrust disclosed it on 15 October 2026 with patch BT26-05, and CISA added it to KEV on 16 October 2026. The page lists log files to review and hardening steps.
watchtowr.comadvisoryAdded 30 Oct 2026, published 16 Oct 2026🛡️ Security- lee1981 (@lee1981b) on X
CyberForge "CVE of the Day #079" on CVE-2026-102764, a CWE-290 origin-validation flaw in BeyondTrust Remote Support (advisory BT26-05, CVSS v4 9.3) that allows appliance file operations. It summarises Mandiant/GTIG's exploited intrusion chain (SAWFLY web shell, BARECLAW backdoor, root escalation, persistence) and gives an investigation trail: patch-state verification (BT26-05-RS), evidence preservation, hunting leads with SHA-256 hashes and YARA rules, permission/session correlation, and remediation including clean redeployment and credential rotation. It separates vendor facts from the intrusion's observed behaviour and notes that KEV and EPSS have no entries.
x.comthreadAdded 18 Oct 2026, published 16 Oct 2026🛡️ Security  The Q3 Vulnerability Pulse: Discovery ≠ Exploitation
Talos Threat Source newsletter arguing that record CVE volume (over 70k by end of Q3, six-digit CVE IDs) is not the same as exploitation. KEV grew only 37% YoY against 105% for CVEs, about a third of KEV entries are CVEs from 2025 or earlier (a patch gap), and 29% of 2026 KEV CVEs were added on their publication date. It also notes the new KEV "forensicTriage" column (BOD 26-04), summarizes the Talos/Insikt report on UAT-6275 espionage against CIS governments with GitHub-hosted payloads and a WinRAR exploit, and lists weekly headlines.
blog.talosintelligence.comarticlePublished and added 15 Oct 2026🛡️ Security- lee1981 (@lee1981b) on X
Daily CVE digest on CVE-2026-76519, a CVSS 9.8 relative path traversal (CWE-23) in Cisco Secure Email Gateway's AMP File Reputation attachment processing. A crafted attachment gives unauthenticated arbitrary file writes and root command execution, and Cisco PSIRT reports active exploitation. The CVE is in CISA KEV. It lists the applicability conditions (File Reputation assigned to a policy and Content Scanner Tools earlier than 25.3.0.5525) and the fixes (scanner 25.3.0.5525, AsyncOS 15.5.5-014 and 16.5.0-780). It also covers evidence preservation, reading Cisco's System Security scan outcomes, mail/AMP log correlation, and deployment-specific recovery including cluster-key exposure.
x.comadvisoryAdded 18 Oct 2026, published 15 Oct 2026🛡️ Security  Palo Alto Networks Patches PAN-OS Zero-Day Exploited for Remote Code Execution
Palo Alto Networks patched CVE-2026-0322, a high-severity zero-day in the PAN-OS management interface that lets an authenticated attacker with network access run arbitrary code as root. It affects PA-Series, VM-Series and Panorama with no special configuration needed, and "very limited" exploitation has been seen. The vendor published a few IP-based IoCs, CISA added the flaw to KEV with an October 17 deadline, and a dozen other medium/low advisories were released the same day.
securityweek.comarticlePublished and added 15 Oct 2026🛡️ Security Cisco Warns of Exploited Secure Email Gateway Vulnerability
Cisco warned that CVE-2026-76519 (CVSS 9.8), an unauthenticated arbitrary file write in the Advanced Malware Protection feature of Secure Email Gateway, is exploited in the wild. Crafted email attachments can lead to root command execution when file reputation is enabled and Content Scanner Tools is older than 25.3.0.5525. Fixes shipped September 14 in AsyncOS 15.5.5-014 and 16.5.0-780. Cisco published IoCs, advises rebuilding virtual appliances and rotating credentials, and CISA added the flaw to KEV. It is the second exploited SEG bug since mid-September, after CVE-2026-76461.
securityweek.comarticlePublished and added 15 Oct 2026🛡️ Security Critical GitLab RCE Lets Unauthenticated Attackers Execute Code on Servers (CVE-2026-97229)
Orca Security analysis of CVE-2026-97229, a CVSS 10.0 flaw in GitLab CE/EE. An integer overflow (CWE-190) in the CI/CD regular expression compiler gives memory corruption and code execution as the git user. It is triggered by a crafted regex in .gitlab-ci.yml combined with a UTF-8 repository path, with no authentication needed on instances that allow public project creation or self-registration. Lists affected branches (19.2 before 19.2.8, 19.3 before 19.3.5, 19.4 before 19.4.2), the absence of a workaround, interim mitigations, and a Rapid7 PoC against GitLab CE 19.4.1 with ASLR on. Notes a prior max-severity GitLab bug (CVE-2026-85706) was probed in the wild within hours and later added to CISA KEV.
 orca.securityadvisoryPublished and added 14 Oct 2026🛡️ Security
- lee1981 (@lee1981b) on X
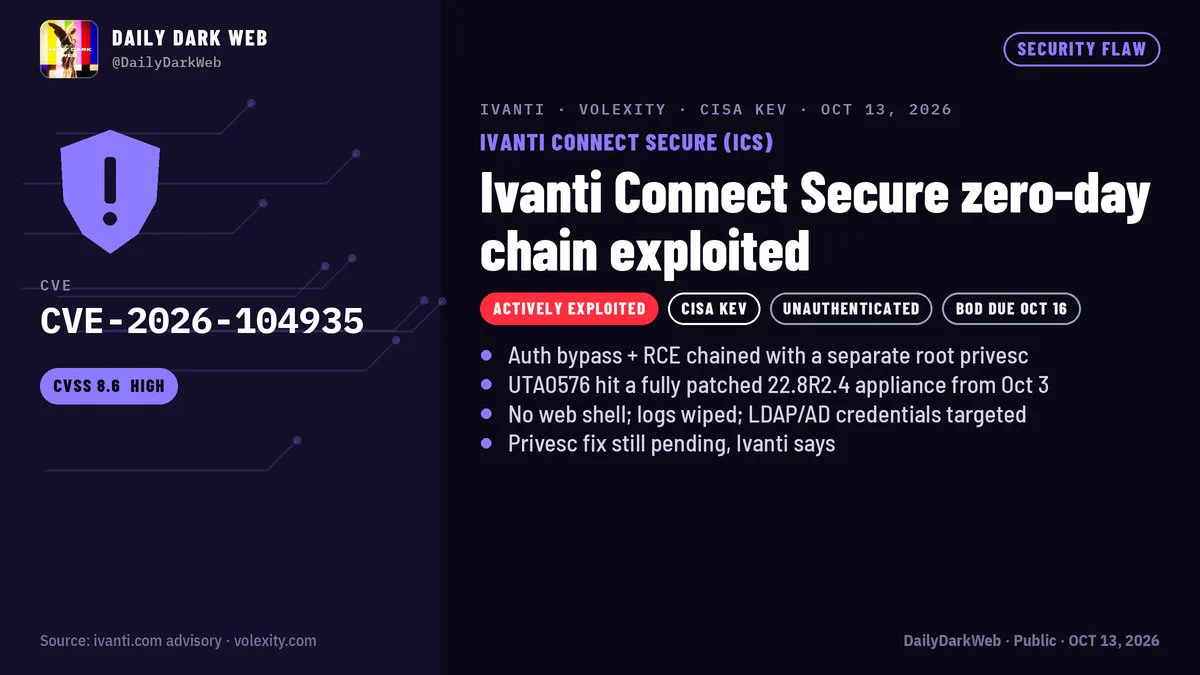
Defender guide for CVE-2026-104935, an authentication-bypass-by-spoofing flaw (CWE-290) in Ivanti Connect Secure that allows unauthenticated command execution. It is confirmed exploited and CISA KEV-listed, with a CNA CVSS 8.6. It covers the fixed-release matrix (25.1.1.2, 22.8R2.5, 25.1.3.x), platform and cluster migration limits, and Volexity's UTA0576 indicators and YARA rules. It also gives a six-step SOC workflow (scope, preserve, hunt, correlate identity, remediate, verify). It stresses that a clean ICT result cannot clear memory-only activity and that LDAP, LAPS and BitLocker exposure belongs to one observed chain.
x.comthreadAdded 16 Oct 2026, published 14 Oct 2026🛡️ Security - ThreatWire (@ThreatWire_) on X
ThreatWire post on CVE-2026-97229, an integer overflow in the GitLab CI/CD regex compiler. GitLab rates it CVSS 3.1 10.0 and says it can allow unauthenticated code execution under certain conditions, in both CE and EE. Fixes are in 19.2.8, 19.3.5 and 19.4.2 (not 19.3.4), released Oct 12; GitLab-hosted instances are already patched. The post credits joaxcar via HackerOne and says a Rapid7 researcher published a lab PoC on GitHub, which ThreatWire has not run or verified. It also says the CVE is not in CISA KEV and has no known exploitation.
x.comthreadAdded 15 Oct 2026, published 14 Oct 2026🛡️ Security  Microsoft Patches Record 1,413 Vulnerabilities, Including Exploited Windows Zero-Day
SecurityWeek reports Microsoft's October 2026 Patch Tuesday fixed a record 1,413 CVEs (1,102 in Windows, 134 Office, 36 SharePoint), more than all of 2025, with the surge attributed largely to AI-driven discovery. The exploited zero-day CVE-2026-96951 is a Windows shell Mark of the Web security feature bypass (CVSS 8.8), added to CISA KEV with an October 16 deadline. Two flaws were publicly disclosed: CVE-2026-108398 (WDAC bypass) and CVE-2026-92707 (MessagePack-CSharp DoS), and Microsoft introduced 'risk cohorts' for patch prioritization.
securityweek.comarticlePublished and added 14 Oct 2026🛡️ Security- Dark Web Intelligence (@DailyDarkWeb) on X
Summary of SAP's October 13, 2026 Security Patch Day (16 new notes, 4 GitHub advisories). It leads with CVE-2026-89111, a CVSS 10.0 OAuth2 SSRF in SAP Cloud SDK for Python before 0.45.2, where an attacker-controlled tenant_subdomain redirects token requests and exfiltrates client credentials. It also lists three other critical flaws: broken access control in NetWeaver Visual Composer, code injection in S/4HANA substitution/validation rules, and a missing authorization check in the Manufacturing Integration and Intelligence (XMII) Configuration Service. It notes that none are in CISA KEV and SAP reports no in-the-wild exploitation.
x.comadvisoryAdded 15 Oct 2026, published 13 Oct 2026🛡️ Security - Dark Web Intelligence (@DailyDarkWeb) on X
Social post summarizing Volexity's research on an Ivanti Connect Secure (ICS) zero-day chain, CVE-2026-104935. The chain pairs an auth bypass and a race-condition RCE with a separate privilege-escalation bug for root. Actor UTA0576 used it from Oct 3, 2026 against a fully patched 22.8R2.4 appliance, leaving no backdoor or web shell and deleting log entries. Post-exploitation included LDAP/AD credential theft, LAPS and BitLocker key searches, password spraying and packet capture. CISA added it to KEV with a due date of Oct 16. A clean Integrity Checker result does not rule out compromise because the chain patches code in memory only, so memory and network forensics are needed. The hunting lead is heavy requests to /dana-na/auth/url_default/welcome.cgi with a mismatched X-DSCGI-PATH header.
x.comthreadPublished and added 13 Oct 2026🛡️ Security  Ivanti Connect Secure zero-day exploited in the wild (CVE-2026-104935)
Rapid7 emergency-response analysis of CVE-2026-104935, a CVSS 8.6 authentication bypass by spoofing (CWE-290) in Ivanti Connect Secure that allows unauthenticated remote command execution. It was exploited as a zero-day against a limited number of customers, added to CISA KEV on disclosure day, and Volexity observed it chained with a still-unpatched privilege escalation flaw. Part of the fix shipped in 25.1.3.0 in July 2026, with backports to other supported versions pending. Rapid7 advises emergency patching outside normal cycles and hunting for compromise using Volexity's IOCs, since Ivanti has no reliable ones.
 rapid7.comadvisoryPublished and added 13 Oct 2026🛡️ Security
 Frequently Asked Questions About the Ivanti Connect Secure Authentication Bypass by Spoofing (CVE-2026-104935)
CVE-2026-104935 is an authentication bypass by spoofing in Ivanti Connect Secure. A remote attacker can forge identity signals and run arbitrary commands without credentials. CISA added it to the KEV catalog on 13 October 2026. The FAQ lists affected branches by ISA hardware (25.1.1.1, 25.1.2.2, 22.8.X), fixed versions (25.1.1.2, 25.1.3.0/25.1.3.1, 22.8R2.5), no workaround and no reliable IOCs.
watchtowr.comadvisoryAdded 30 Oct 2026, published 13 Oct 2026🛡️ Security Ivanti Connect Secure Authentication Bypass by Spoofing (CVE-2026-104935)
CVE-2026-104935 is an authentication bypass by spoofing in Ivanti Connect Secure (CVSS 3.1 score 8.6) that lets a remote attacker run commands without logging in. CISA added it to KEV on 13 October 2026. The 22.8.X bridge release and 25.1.2.2 and earlier are affected, with fixes in 22.8R2.5, 25.1.1.2, 25.1.3.0 and 25.1.3.1. Ivanti says no reliable indicators of compromise exist yet.
watchtowr.comadvisoryAdded 30 Oct 2026, published 13 Oct 2026🛡️ Security- lee1981 (@lee1981b) on X
CyberForge "CVE of the Day #076" covers CVE-2026-97229, a CVSS 10.0 integer overflow (CWE-190) in GitLab CE/EE's CI/CD regular expression compiler. It can lead to conditional unauthenticated code execution on the GitLab server. It lists the affected trains (19.2 before 19.2.8, 19.3 before 19.3.5, 19.4 before 19.4.2) and the 19.3.4 vs 19.3.5 Ona-regression discrepancy. It also gives six SOC checks: scoping, log preservation (Workhorse/Rails/Sidekiq, correlation_id), server-effect hunting, request-to-process correlation, upgrade and running-state verification. It notes that exploit details are unverified, no KEV listing exists and EPSS data is unavailable.
x.comadvisoryAdded 15 Oct 2026, published 13 Oct 2026🛡️ Security - AI Agents for Cybersecurity: A Guided Tour of a Repository with Tons of Resources and Examples
Guided tour of Omar Santos's eight-part AI-agents-for-cybersecurity repository. It moves from LLM building blocks (LangChain, RAG) to security agents built with LangGraph, CrewAI, DeepAgents and MCP servers (nmap, CISA KEV, Shodan). It also covers a hardening guide for six agentic frameworks, token-cost control, and a spec for a supervisor-led, human-gated assessment harness. Design lessons include least-privilege subagents, single-use approvals and kill switches.
 becomingahacker.orgarticleAdded 13 Oct 2026🧠 AI
- santosomar/AI-agents-for-cybersecurity
Companion repository for Omar Santos's Pearson and O'Reilly trainings and books. It has eight parts of runnable Python labs: chat models, embeddings, prompt templates, LCEL prompt chaining, Chroma-based RAG, ReAct/LangGraph/CrewAI/DeepAgents agents, and FastMCP servers (nmap, CISA KEV, Shodan). It also includes guides to six agentic frameworks (OpenClaw, Hermes, Agent Zero, OpenHands, Paperclip, Buzz), a tokenomics module on agent cost (context compounding, prompt caching, model routing, token budget guards, batch API, cost per accepted outcome), and a vendor-neutral design spec for a human-gated multi-agent assessment harness. It is a current, practical curriculum for building and operating agents. Some examples act on real systems and should only be run in an authorized lab.
 github.comrepoAdded 13 Oct 2026🧠 AI
- santosomar/AI-agents-for-cybersecurity
Omar Santos's companion repo for his Pearson/O'Reilly trainings and books, organised in eight parts. They cover LangChain prompts, chains and RAG (Chroma), and agents (LangGraph, CrewAI, DeepAgents). They also cover FastMCP security servers (nmap, CISA KEV, Shodan) and attack-surface-management and SOC agent examples. Later parts have security guides to six agentic frameworks (OpenClaw, Hermes, Agent Zero, OpenHands, Paperclip, Buzz) with hardening notes and 2026 CVE mapping, agent cost/tokenomics scripts including denial-of-wallet budget guards, and a vendor-neutral spec for a human-gated multi-agent security-assessment harness (scope manifest, approval gates, kill switch). Useful as a hands-on path into AI-agent security tooling, with warnings that some examples act on real systems.
github.comrepoAdded 13 Oct 2026🛡️ Security - AI Agents for Cybersecurity: A Guided Tour of a Repository with Tons of Resources and Examples
Omar Santos walks through his eight-part AI-agents-for-cybersecurity repository: LLM building blocks (LangChain, RAG), then security agents with LangGraph, CrewAI, DeepAgents and MCP servers (nmap, CISA KEV, Shodan), a hardening guide for six agentic frameworks, token-cost control for agents, and a spec for a supervisor-led, human-gated security-assessment harness. It covers concrete design lessons such as least-privilege subagents, staged response actions, single-use approvals bound to exact actions, kill switches, and mapping controls to the OWASP Top 10 for Agentic Applications. Also notes Project CodeGuard rules shipped for AI coding assistants.
becomingahacker.orgarticleAdded 13 Oct 2026🛡️ Security - AI Agents for Cybersecurity: A Guided Tour of a Repository with Tons of Resources and Examples
Omar Santos walks through his AI-agents-for-cybersecurity GitHub repo, which has eight parts. Parts 1–4 cover LLM basics (LangChain, prompting, LCEL, RAG). Parts 5–8 cover building security agents with LangGraph, CrewAI, DeepAgents and MCP servers (nmap, CISA KEV, Shodan), and a hardening baseline for six ready-made agentic frameworks. They also cover token-cost control (caching, routing, budget guards, cost per accepted outcome) and a supervisor-led, human-gated security-assessment harness spec with single-use approvals, a kill switch and an append-only audit log. The post also covers Project CodeGuard rules for AI coding assistants. It is a practical learning path and a reference for governing and securing agents.
 linkedin.comarticleAdded 13 Oct 2026🛡️ Security
- lee1981 (@lee1981b) on X
CyberForge's CVE of the Day #075 covers CVE-2026-108860, a critical (CVSS 9.1 v3.1 / 9.3 v4.0) authentication bypass in SciSharp BotSharp through 5.2.0. WebStarter ships a published default HMAC JWT signing secret (CWE-321), so anyone holding it can forge bearer tokens that impersonate known users, including administrators. The post sets out how to confirm the effective key and serving build, a six-step SOC investigation trail, and remediation by rotating the secret. No verified fixed release, KEV entry or EPSS data existed at cutoff, and the linked research is static-only.
x.comadvisoryAdded 13 Oct 2026, published 12 Oct 2026🛡️ Security  Critical SonicWall Vulnerability Exploited Days After Disclosure
SecurityWeek reports that CVE-2026-102255, a CVSS 10 pre-authenticated SSRF in the SonicWall SMA1000 Work Place interface, was exploited within days of its October 6 disclosure. Defused saw the first attempts on its SMA decoys on October 8, and Previdian (formerly KEVIntel) also observed exploitation. SonicWall urges 6210, 7210 and 8200v customers to update to 12.5.0-03082 or 12.4.3-03670, and Horizon3.ai warns that exploitation could lead to device takeover.
securityweek.comarticlePublished and added 12 Oct 2026🛡️ Security- ThreatWire (@ThreatWire_) on X
Post announcing a public PoC for CVE-2026-13043, a critical flaw (CVSS 4.0 9.3, scored by WatchGuard) in PSKMAD, the kernel memory access driver of WatchGuard Endpoint Security on Windows. The access-control handshake can be bypassed (CWE-306/CWE-798), letting a local authenticated attacker send privileged commands and read kernel and other processes' memory. Fixed in 8.00.26.0012; the PoC author and LOLDrivers frame the signed driver as BYOVD material, which WatchGuard does not say. The post notes it is not in CISA KEV, has no reported in-the-wild exploitation, and that ThreatWire has not run the PoC.
x.comthreadAdded 11 Oct 2026, published 10 Oct 2026🛡️ Security - lee1981 (@lee1981b) on X
CyberForge CVE of the Day #074 analyses CVE-2026-85097, a CVSS 9.8 unauthenticated file upload to PHP execution flaw (CWE-434) in the Bricksforge WordPress plugin through 3.1.8.9. Wordfence names 3.1.8.10 as the fix, and a separate vendor 4.0.1 Pro Forms upload-security notice has no verified mapping to the CVE. It gives a defender workflow: scope versions, preserve edge/origin logs, inspect resulting files and PHP-FPM handling, and verify the patched version is serving. It also separates KEV (no match), EPSS (0.312%) and SSVC (exploitation none) from compromise evidence.
x.comadvisoryAdded 11 Oct 2026, published 10 Oct 2026🛡️ Security - lee1981 (@lee1981b) on X
CyberForge's CVE of the Day #073 covers CVE-2026-102255, a critical (CVSS 10.0) pre-authentication SSRF / confused-deputy flaw (CWE-918, CWE-441) in the SonicWall SMA1000 Work Place interface, per advisory SNWLID-2026-0017. It lists affected platform hotfixes (12.4.3-03526 and older, 12.5.0-02952 and older), fixed floors (12.4.3-03670, 12.5.0-03082), no workaround, and the exploitation picture (no known exploitation, not in KEV, EPSS 0.477%, SSVC automatable). It gives a six-step SOC playbook covering appliance scoping, AMC log preservation, hunting appliance-originated internal requests, correlating receiving-service changes, patching, and verifying every node, and it separates exposure, a lead, confirmed compromise and telemetry gaps.
x.comadvisoryAdded 12 Oct 2026, published 9 Oct 2026🛡️ Security












Showing 60 of 123
Show more