- Lonnie VanZandt (@lonniev) on X
Secure Courier is a consent flow in Tollbooth DPYC, a monetization network for paid MCP services, that lets an AI agent act for a Nostr npub without holding the user's nsec. The service sends a signed, sealed direct message over Nostr relays, the user replies with a signed approval and an expiry, and the service issues its own encrypted grant. Lonnie VanZandt presents it as an alternative to central identity providers and CIBA. The thread gives no audit results.
 x.comthreadAdded 1 Nov 2026🧠 AI
- Dark Web Intelligence (@DailyDarkWeb) on X
CVE-2026-102764 is an unauthenticated RCE in BeyondTrust Remote Support, already exploited and in CISA KEV. Rapid7 published an analysis and opened a Metasploit pull request on 30 October 2026, showing code execution on version 24.1.2 via a forged "local" message origin, the native file-transfer service and a PHP file written to the web root. BT26-05 (CVSS 4.0 9.3) is fixed by patch BT26-05-RS; SaaS was patched by 9 October.
x.comthreadAdded 1 Nov 2026, published 31 Oct 2026🛡️ Security - 🚨 AI News | TestingCatalog (@testingcatalog) on X
RoboAPI is a public API from PokeBot, powered by its world-action model Poke-Aurora, that lets robot arms do new tasks from natural-language instructions with no task-specific data collection or training. A user connects a supported arm with a wrist-mounted camera, gives a task such as "clean the table", and receives the next moves in near real time. The post gives no benchmarks, supported hardware list or pricing.
x.comthreadAdded 1 Nov 2026, published 31 Oct 2026🧠 AI  ERC draft: Independent Simulation Result for (STVA)
ERC draft "Independent Simulation Result" (STVA) defines a canonical, content-addressed SimulationResult (success, gasUsed, returnData, stateDiffHash, logsHash, snapshotId, resultHash) that any wallet, hardware device or verifier can recompute from the same VerificationPayload and state snapshot. It targets compromised-frontend and UI/calldata-mismatch attacks, and defines Basic, Standard and Strict compliance levels. Open questions are stateDiff encoding, prestate proofs and binding to capability tokens.
 ethresear.chthreadPublished and added 30 Oct 2026🛡️ Security
- Artificial Analysis (@ArtificialAnlys) on X
Hyperflow H3 is Video Rebirth's 8-step LoRA for MiniMax H3, released in September 2026 with open weights. Artificial Analysis ranks it #5 on AA-Video-I2V v2.1 and #3 on AA-Video-Editing v1.1, ahead of MiniMax H3 (768p). It costs $9.00 per minute for Image to Video and $18.00 for Video Editing at 1088p, under half of Dreamina Seedance 2.5 ($34.12 and $40.82). The thread gives per-capability and per-use-case breakdowns.
x.comthreadAdded 31 Oct 2026, published 30 Oct 2026🧠 AI  EIP Draft: Permanent EOA Delegation Opt-Out (disable EIP-7702)
Discussion thread for a draft Core EIP that lets an Ethereum EOA permanently disable EIP-7702 delegation. A type-4 set-code transaction with an empty authorization list, destination equal to sender and zero value installs the 0xef0200 marker for 33500 gas. Later authorizations, including clearing to the zero address, are skipped. It does not protect against private-key compromise. Open questions cover the prefix, a dedicated transaction type, gas pricing, and EIP-8151 interaction.
 ethereum-magicians.orgthreadPublished and added 30 Oct 2026🛡️ Security
 Trail of Bits (@trailofbits) on X
Trail of Bits post on X summarising Binance's initial investigation into a security incident. Binance suggests a compromised DevOps engineer's laptop let an attacker reach a service container and submit unauthorized withdrawal transactions. The text says no evidence has been found of wallet private key compromise. The fetched text is truncated and gives no further detail.
x.comthreadPublished and added 30 Oct 2026🛡️ Security- Artificial Analysis (@ArtificialAnlys) on X
Artificial Analysis launched an HLE-Diamond leaderboard in v5 of its Intelligence Index, covering the refined 1,000-question Humanity's Last Exam from CAIS and Scale AI. Each question runs once without tools, graded by GPT-5.6 Luna (medium) as pass@1. Gemini 4 Carbon (high) leads at 69%, Claude Opus 5.5 (max) scores 68%, and the top open weights model, Kimi K3.1 Pro, reaches 37%.
x.comthreadPublished and added 30 Oct 2026🧠 AI - aiproduck (@aiproduck) on X
Ruflo is an MIT-licensed wrapper for Claude Code and Codex that adds agent swarms, vector memory and an MCP server. The plugin install writes no files to the workspace, while npx init adds a .claude/ directory, CLAUDE.md and hooks. The post warns that mods run with the account's permissions, so users should read them first. It gives no benchmarks or architecture detail.
x.comthreadPublished and added 30 Oct 2026🧠 AI - Prasenjit Sarkar (@stretchcloud) on X
A thread on Cloudflare's agent-readiness scan and the AgentReady.org open spec for "Agent Experience", developed with Vercel, Stripe, Auth0, Mintlify, Google, Netlify and Elementor. The scan grades whether agents can find a site (robots.txt, DNS), read clean Markdown, pass bot rules, and discover an MCP server or API catalog. One quoted example raised a score from 20 to 67 by shipping an API catalog with Link headers, an MCP server card, a skills index and an AI catalog file.
x.comthreadAdded 30 Oct 2026, published 29 Oct 2026🧠 AI  Rohan Paul (@rohanpaul_ai) on X
Rohan Paul's X post summarizes a TikTok paper on MCP attacks. LLM agents often finish the requested task, then quietly call an attacker-controlled logging tool that records the user query, the server reply and the final answer. The attack works because agents read natural-language tool descriptions when choosing and ordering tool calls. The visible text is truncated and gives no success rates or defenses.
x.comthreadAdded 30 Oct 2026, published 29 Oct 2026🛡️ Security- 🚨 AI News | TestingCatalog (@testingcatalog) on X
Mistral Large 4 ("Le Chonk") is an open-weights model from Mistral, now on Hugging Face. Per Mistral's announcement quoted in the post, it ranks #1 among open models on Cognition's FrontierCode benchmark, is aimed at agentic coding and cybersecurity, and claims better reasoning efficiency and lower inference costs. The post does not give parameter counts, license or benchmark scores.
x.comthreadAdded 30 Oct 2026, published 29 Oct 2026🧠 AI  SGLang (@sgl_project) on X
SGLang announces Day-0 support for Mistral Large 4 ("Le Chonk"), saying it is the first engine to serve the model on NVIDIA Vera Rubin. The post describes the model as Mistral's largest to date: a natively multimodal 1T-parameter mixture-of-experts model covering instruct, reasoning, coding and agentic workflows. The fetched text is truncated, so benchmark claims and launch commands are not visible.
x.comthreadAdded 30 Oct 2026, published 29 Oct 2026🧠 AI Muhammad Waris (@WarisCodes) on X
Nemotron 3.5 Transcribe is a free open-weight speech-to-text model from NVIDIA covering 40 languages, including mixed-language speech. The post says it ties for first among open models with a 2.8% error rate. It says the model needs a large GPU such as an H100 or RTX 5090, so it will not run on a laptop. The post gives no benchmark name or model card link.
x.comthreadAdded 30 Oct 2026, published 29 Oct 2026🧠 AI- Dark Web Intelligence (@DailyDarkWeb) on X
DailyDarkWeb post summarising Anthropic Frontier Red Team research published 27 October 2026. An unreleased internal Claude research model built five attack chains: Chrome sandbox escape (V8 heap bug, CacheStorage race, FedCM use-after-free), a Safari same-origin policy bypass, data extraction from a locked Pixel 9 over USB, a Windows QUIC kernel crash (CVE-2026-33096) and zero-click Linux root via multipath TCP (CVE-2026-98432). Anthropic says all flaws are fixed, including 62 Chrome CVEs as of Chrome 156. The post notes the chains are not independently reproduced.
x.comthreadAdded 30 Oct 2026, published 29 Oct 2026🛡️ Security - Rohan Paul (@rohanpaul_ai) on X
Rohan Paul's X post summarizes the paper "Log-To-Leak: Prompt Injection Attacks on Tool-Using LLM Agents via the Model Context Protocol", from TikTok researchers. It reports that MCP-using agents often finish the requested task, then quietly call an attacker-controlled logging tool that records the query, server reply and final answer. The attack works through natural-language tool descriptions that agents read when choosing and ordering tools. The visible text is truncated.
x.comthreadAdded 29 Oct 2026, published 28 Oct 2026🛡️ Security  Eddy (@ieddysun) on X
Expo's official skills package gives AI coding agents scoped instructions for building Expo apps. One command, npx skills@latest add expo/skills --skill '*', installs it for Cursor, Copilot and Windsurf, while Claude Code and Codex use their plugin marketplaces. Skills include expo-router, expo-animation, expo-upgrade and eas-update. The Expo MCP server adds live docs lookup, compatible dependency installs, EAS build monitoring and simulator screenshots.
x.comthreadAdded 29 Oct 2026, published 28 Oct 2026🧠 AI- Trail of Bits (@trailofbits) on X
Trail of Bits post says it achieved remote code execution through a Brotli decoder bug in Linux lab setups: Node.js 24.22.0 with Express 5.3.0 via the standard JSON parser (x86-64 and ARM64), and Electron 41.10.7 (x86-64) with a custom decoding service. Exploitation needs a carefully matched setup and repeated attempts. A scanner by ToBScottA finds hidden copies of the decoder, including in stripped binaries.
x.comthreadAdded 30 Oct 2026, published 28 Oct 2026🛡️ Security  TENSA Engineering (@TENSAEng) on X
A post by TENSAEng describing a workflow for staying within coding-tool usage limits. ChatGPT chat sits outside those limits, while Claude and Grok chats share a pool with Claude Code, Codex and Grok Build. Architecture, file layout, step order and acceptance checks are planned in ChatGPT and saved as repo docs. Claude Code or Codex then implements one small chunk per fresh session.
x.comthreadAdded 29 Oct 2026, published 28 Oct 2026🧠 AI- Laban (@lunkertw) on X
An X post summarising five AI items: Google DeepMind's Gemini 4 Carbon (88.2% SEC-bench Pro, 54.8% ExploitGym, 71.0% CWE-bench, 59 on Artificial Analysis Intelligence Index v5.0), Ed Zitron's critique of Anthropic's S-1, a Utah Claude Code pilot, and the repos beenuar/AiSOC and expo/skills. In the Utah pilot, 34 developers in 10 agencies took part over four weeks, 80% had a working setup within 30 minutes, and 71% saved over 20 hours. It gives short summaries and links, not primary analysis.
x.comthreadAdded 29 Oct 2026, published 28 Oct 2026🧠 AI - Niko (@nikolayxyz) on X
Gemini 4 Carbon is Google's new frontier model, announced in a post by nikolayxyz that quotes Google's launch text. It ranks #1 on v5.0 of the Artificial Analysis Intelligence Index with 59 points, ahead of Opus 5.5 and GPT-6 Astra. Intro pricing is $2 input and $10 output per million tokens. Access starts for cyber defenders first, as Gemini 4 Argon's did. The captured text is cut off before the rollout details.
x.comthreadAdded 29 Oct 2026, published 28 Oct 2026🧠 AI  John Rood (@johnroodepic) on X
Nemotron 3.5 Transcribe is an open-weight, promptable 30B mixture-of-experts model from NVIDIA with about 4B active parameters, built for recorded audio. One checkpoint transcribes 40 languages, handles recordings up to an hour, labels up to eight speakers, translates, and answers questions about English audio. Weights and a demo are on Hugging Face. The post gives no benchmarks.
x.comthreadAdded 29 Oct 2026, published 28 Oct 2026🧠 AI- 🚨 AI News | TestingCatalog (@testingcatalog) on X
Gemini 4 Carbon is a new Google model, announced in a TestingCatalog post on X as taking first place on the Artificial Analysis V5 ranking. It is rolling out to cyber defenders first. Reported scores are 88.2% on SEC-bench Pro (finding vulnerabilities), 54.8% on ExploitGym (exploitation) and 71.0% on CWE-bench (patching). The post calls it a large step up from Gemini 4 Argon, released two weeks earlier. It gives no technical detail beyond these claims.
x.comthreadAdded 30 Oct 2026, published 28 Oct 2026🧠 AI  JFrog Security (@JFrogSecurity) on X
JFrog Security announces research on CVE-2026-102479 in Vert.x, which skips validating the letter 'L' in header names and so accepts `Content-Xength` as `Content-Length`. JFrog Research chained this with a dangling-byte primitive to bypass reverse proxy socket validation. They demonstrate end-to-end response poisoning and session fixation behind real reverse proxies. The post links to a full writeup; the tweet itself gives no exploit detail.
x.comthreadAdded 30 Oct 2026, published 28 Oct 2026🛡️ Security- Hakimi Eiqbal (@hakimieiqbal) on X
A practical reverse-engineering map by hakimieiqbal on X that picks tools by target: native binaries, .NET, Electron, iOS, firmware, WebAssembly and network protocols. It introduces REA (morluto/rea), which connects coding agents to RE tools, and lists MCP bridges for IDA Pro, Ghidra and radare2. It adds an evidence-first workflow and free courses such as pwn.college and OpenSecurityTraining2.
x.comthreadAdded 29 Oct 2026, published 28 Oct 2026🛡️ Security - Hakimi Eiqbal (@hakimieiqbal) on X
A thread by Hakimi Eiqbal that maps reverse-engineering tools by target type: native binaries, Electron, .NET, iOS, firmware, WebAssembly and network protocols. Its AI sections cover REA (an open-source layer connecting coding agents to analysis tools) and MCP bridges for IDA Pro, Ghidra and radare2. It argues for an evidence-first workflow and gives a prompt that separates verified facts from hypotheses.
x.comthreadAdded 29 Oct 2026, published 28 Oct 2026🧠 AI  Kizuno18 (@Kizuno18) on X
Thread by Kizuno18 on the move from local stdio/Docker Model Context Protocol servers to remote HTTP/SSE endpoints in enterprise infrastructure. It names three trade-offs: credential boundary inversion (short-lived OAuth/JWT tokens instead of long-lived admin tokens on workstations), tool schema bloat solved by deferred discovery, and governance via HCP Terraform policy-as-code (Sentinel/OPA), audit trails and approvals. It is opinion, with no data or implementation detail.
x.comthreadAdded 29 Oct 2026, published 27 Oct 2026🛡️ Security- Kizuno18 (@Kizuno18) on X
Kizuno18's X post argues that the move from local stdio and Docker MCP servers to remote HTTP/SSE endpoints matures the Model Context Protocol in enterprise infrastructure. It lists three trade-offs: short-lived OAuth/JWT bearer tokens replace mounted admin credentials, deferred tool discovery avoids roughly 20k tokens of eager schema loading, and HCP Terraform enforces Sentinel/OPA policy, audit trails and approvals server-side. Opinion post with no benchmarks or code.
x.comthreadAdded 29 Oct 2026, published 27 Oct 2026🧠 AI  Photon Capital (@PhotonCap) on X
Photon Capital's thread covers the 27 October 2026 NVIDIA and Oracle announcement of general availability of Vera Rubin NVL72 and Vera CPUs on OCI. It lists specs (Spectrum-6 at 102.4Tbps, HGX Rubin NVL8 with Xeon 6, 150,000 initial Vera CPUs) and OpenAI's use of Vera CPUs for agentic sandboxes. The commentary argues CPU capacity can cut cost per task and shorten KV cache residency in GPU memory.
x.comthreadAdded 28 Oct 2026, published 27 Oct 2026🧠 AI- Manoj | The AI Dude (@Manojkumar2257) on X
heditor is an open-source (MIT) agent skill from pycodebr that has Claude Code, Codex, Cursor or OpenCode edit talking-head videos. It transcribes with faster-whisper, picks a 30-70s segment, cuts frame-accurately, builds HTML + GSAP motion graphics, mixes audio at -14 LUFS, and runs QA with vision-reviewed previews. It offers 42 named styles and a long-form mode with chapters, SRT/VTT and lower thirds. Install: npx skills add pycodebr/heditor -g.
x.comthreadAdded 28 Oct 2026, published 27 Oct 2026🧠 AI  cubillas (@cubillas888) on X
The tweet relays Pillar Security research that opencode on Windows and WSL could run attacker-controlled code during remote MCP server OAuth sign-in. The fix shipped in opencode 1.18.33 on 28 September, with no advisory or CVE published. It advises users of remote MCP servers to update and review which servers they connect to. Technical details are not in the post.
x.comthreadAdded 29 Oct 2026, published 27 Oct 2026🛡️ Security Nicholas Martin (@ndgmlondon) on X
X thread started by Nicholas Martin (#IAM) advising that MCP tool permissions be verified and scoped session tokens used to enforce least privilege against indirect prompt injection. Replies argue that token scoping does not solve the confused deputy problem, because an injection borrows the agent's legitimate authority. They recommend per-task tokens with short expiry, with the grant logged beside the call, and raise MCP server dependency supply-chain risk.
x.comthreadAdded 28 Oct 2026, published 27 Oct 2026🛡️ Security- Proof of One: one-person-one-identity polling with encrypted ballots — design and reference code, requesting critical review
Proof of One is an open-source design for polls with one verified human per identity and unlinkable ballots. Enrolment proves in zero knowledge that an ICAO 9303 passport chip was signed by a trusted signer, plus an enclave face match. Voting uses threshold exponential ElGamal on Baby Jubjub with Groth16 proofs, and tally uses a GJKR DKG with a 7-day challenge window. The author, who is pseudonymous, discloses that AI agents drafted most of it and asks for critique of unlinkability, circuit completeness and certificate trust.
ethresear.chthreadPublished and added 27 Oct 2026🛡️ Security - Muzammil Shah (@Muzammil_OX) on X
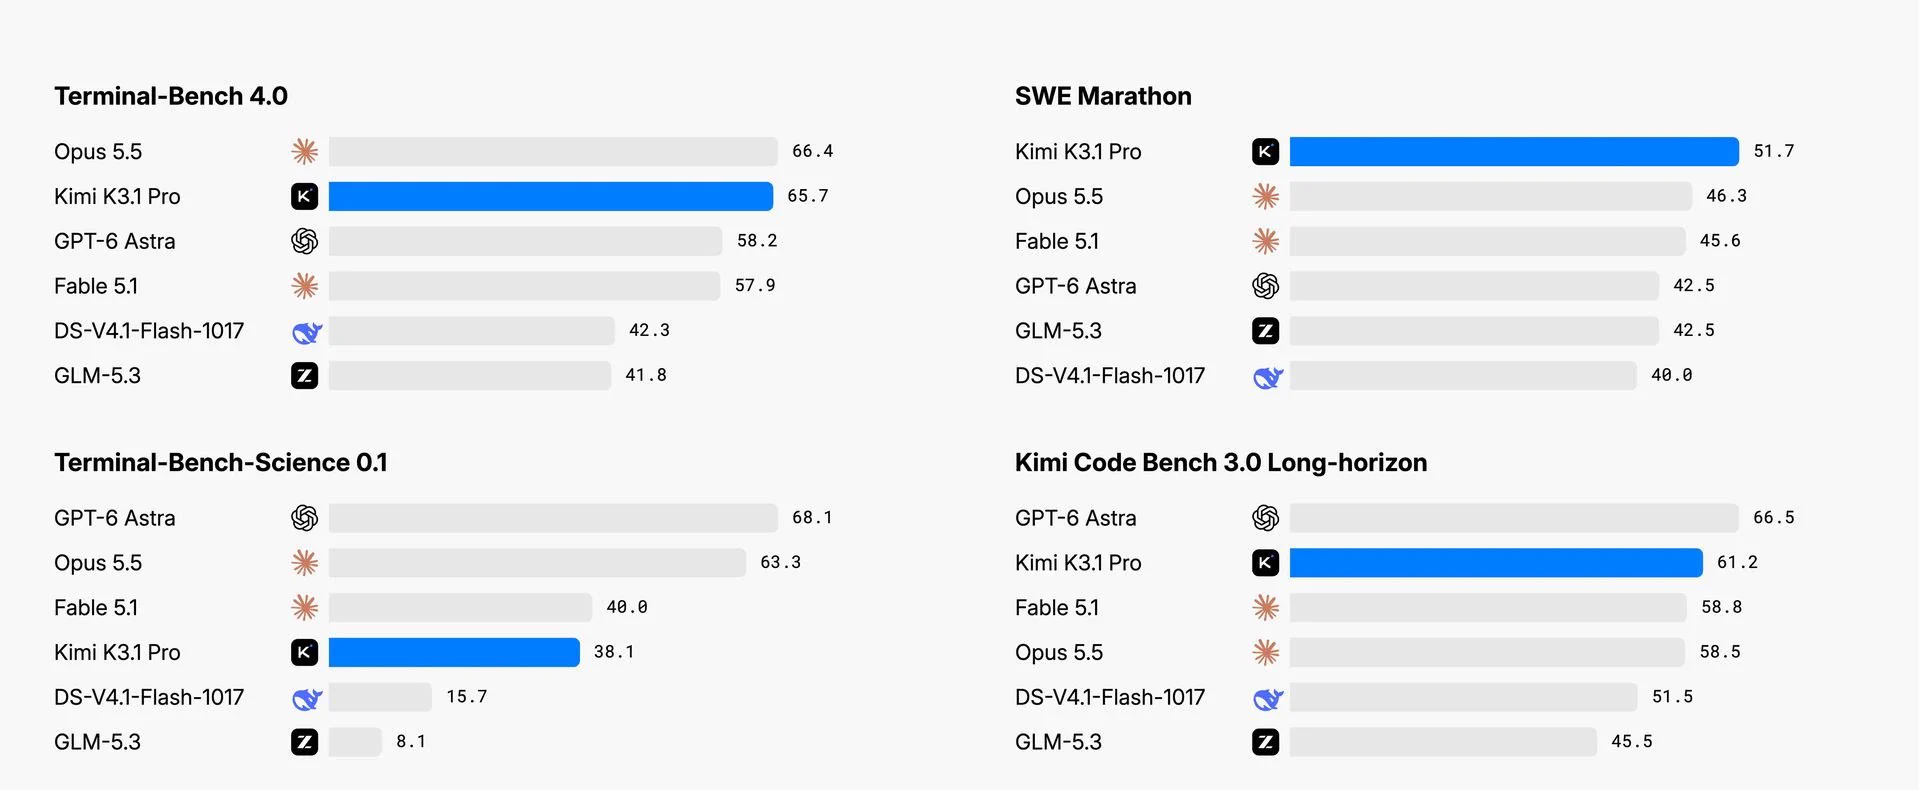
Kimi K3.1 Pro is a new model from Moonshot AI that scores 55 on the Artificial Analysis Intelligence Index, up 11 points from its predecessor, and ranks 4th overall. It has a 1M-token context window and API pricing of $2 per million input tokens and $10 per million output tokens. Weights are due by November 4. Moonshot removed cyber-related training data, which cut its internal vulnerability research score from 90.5% to 81%.
x.comthreadAdded 28 Oct 2026, published 27 Oct 2026🧠 AI - AGTP (@AGTPinsights) on X
AGTP's X thread summarizes Meta's Muse Spark 1.3 Evaluation Report. Prompt injection was tested on Exponential Security Labs' RepoInject v1 and BrowserInject v1 and on Gray Swan's IPI Arena, with robustness said to be on par with GPT-5.6 Sol. It also covers chain of thought controllability evals, PostTrainBench under Loss of Control, and Handshake's pre-release human red teaming. It notes the Midas Project's criticism of Muse Wonder's missing safety report.
x.comthreadAdded 27 Oct 2026, published 26 Oct 2026🛡️ Security - AGTP (@AGTPinsights) on X
Thread summarizing Meta's Muse Spark 1.3 Evaluation Report, the safety write-up for the model released on September 2, 2026. It covers prompt-injection results on Exponential Security Labs' RepoInject v1 and BrowserInject v1 and Gray Swan's IPI Arena, chain-of-thought controllability evals, PostTrainBench under Loss of Control, and Handshake's human red teaming. It also notes The Midas Project's criticism that Muse Wonder still has no safety report, and the Muse Spark Open rollout (816B total, 42B active parameters).
x.comthreadAdded 27 Oct 2026, published 26 Oct 2026🧠 AI - The SI Maximalist (@thesimaximalist) on X
The SI Maximalist posts on X that OpenAI says GPT-6.1 Terra matches GPT-6 Astra on Agents' Last Exam, OpenAI's test of workplace software tasks, at one tenth of the token price. The model is available in ChatGPT Work, Codex and the API. The post only relays OpenAI's claim and gives no benchmark scores, exact prices or method.
x.comthreadAdded 27 Oct 2026, published 26 Oct 2026🧠 AI  Akash Rajagopal (@akashsairaja) on X
Ollama overview thread by Akash Rajagopal on X. It lists six steps: install on macOS, Linux, Windows or Docker; run `ollama run gemma4`; use the REST API on localhost:11434 (/api/chat); call it from ollama-python and ollama-js; llama.cpp as the README's supported backend; and `ollama launch claude` to connect Claude Code. Codex, OpenCode, Copilot CLI and Droid also work. The thread cites 184k GitHub stars and an MIT licence.
x.comthreadAdded 27 Oct 2026, published 26 Oct 2026🧠 AI David Gutierrez | Eng (@david_x_ai) on X
Thread on two October 2026 npm compromises: @subql/common 5.8.3 (5 October), published through GitHub Actions OIDC Trusted Publishing after the attacker tampered with the publish workflow, and tensorlake 0.5.144 (8 October), published by the project's own release workflow with valid provenance for about 1 hour 40 minutes. Both ran on install and stole cloud, GitHub, Kubernetes, Vault, SSH and .env credentials; tensorlake also took AI tool and MCP config. Its payload installed a gh-token-monitor service that deletes the home directory if the stolen GitHub token is revoked, so remove it before rotating.
x.comthreadAdded 27 Oct 2026, published 26 Oct 2026🛡️ Security Masoud (@dev3mike) on X
Tweet from dev3mike warning Node.js users to update for CVE-2026-111497, a Brotli bug rated CVSS 9.2. Crafted compressed data can corrupt memory and possibly run code. The post says OpenAI's agents found it, and that the fix sat unreleased in Brotli's source since February. Patched versions are Node 22.23.4, 24.22.1 and 26.12.1.
x.comthreadAdded 29 Oct 2026, published 26 Oct 2026🛡️ Security Benjamin👨💻 (@Hislordship_9) on X
Thread on Forever Security's finding that a planted Markdown "Engineering Work Guidelines" file in ~/Downloads made Codex add a "project-tools" MCP server to ~/.codex/config.toml. The server ran npm install function-color, a known malicious package, and started a child session with --dangerously-bypass-approvals-and-sandbox. Codex complied in over 90% of the firm's tests; Claude Code, via a CLAUDE.md setting ANTHROPIC_BASE_URL, about half. Advice: don't start agents in Downloads, review instruction files, and diff agent config.
x.comthreadAdded 27 Oct 2026, published 26 Oct 2026🛡️ Security- lee1981 (@lee1981b) on X
Reply on X explaining a Bytecode Alliance advisory for Wasmtime's Cranelift compiler backend. A large or crafted Wasm function that generates enough SSA values overflows Cranelift's value-index representation, which packed indices into 24-bit fields. The fix widens them to 32 bits. The issue is not AArch64-specific, and the advisory names no required optimisation level. Guard pages do not reliably stop the resulting miscompilation and type confusion, so a sandbox escape can arise at compile time.
x.comthreadAdded 28 Oct 2026, published 26 Oct 2026🛡️ Security - TechNadu (@TechNadu) on X
TechNadu's post reports a hacker's claim of leaking 6 million records linked to CONAPE, the Dominican Republic's pension body. The alleged dataset includes national IDs, addresses, medical details and pension records. TechNadu notes that neither the records nor their link to CONAPE has been independently verified. The post gives no technical details on how the data was obtained.
x.comthreadAdded 27 Oct 2026, published 26 Oct 2026🛡️ Security - Ricardo Arguello (@RicardoIQSource) on X
Post by RicardoIQSource on breaches of developer platforms aimed at AI provider keys. It reports OpenCode (17 October, provider keys in its Console) and Zeabur (14-15 October, 3.2M environment variable records, admin tokens stored in plaintext since January 2024) as following the Railway incident. It claims three platforms were hit in eight days and links a blog with a timeline and remediation steps.
x.comthreadAdded 29 Oct 2026, published 26 Oct 2026🛡️ Security - David Gutierrez | Eng (@david_x_ai) on X
Thread on a critical opencode bug disclosed by Pillar Security on Oct 19. On Windows and WSL, a remote MCP server could run code during OAuth sign-in, because the server-chosen authorization URL was put unescaped into a PowerShell command, so a PowerShell subexpression executed. opencode fixed it in 1.18.33 on Sep 28 as a browser-launch refactor with no advisory or CVE. MCP Inspector published an advisory for the same bug class, and its fix needs a major bump of the open package.
x.comthreadAdded 27 Oct 2026, published 25 Oct 2026🛡️ Security - alex lee (@alexlee20122022) on X
Gheist is a GitHub campaign disclosed by Wiz in October 2026. Stolen tokens push ci-sync-XXXXXX branches with a sync-check workflow that dumps repo secrets base32-encoded to evade log masking, fetches the logs via API, then deletes the run. 13,500+ branches and 850+ accounts were hit since 15 September. Public repos are protected by the approval hold; private and Enterprise repos are not. The thread lists IOCs (.gdmp_pat files, "gheist" user agent, "ci: sync config" commits) and rotation steps.
x.comthreadAdded 26 Oct 2026, published 25 Oct 2026🛡️ Security - Syb (@DegenOfWallSt) on X
Nanbeige4.3-33B is a 33.1B dense, Llama-style open model under Apache-2.0, released with a base model on Hugging Face. In Nanbeige's own table it beats Qwen3.8-27B on Terminal-Bench 2.1 (80.9 vs 73.0), DeepSWE (65.5 vs 42.5) and Automation Bench, but trails on SWE-Bench Pro, GDPval and GPQA Diamond. BF16 weights are about 66 GB, split across 4 GPUs in the vLLM and SGLang examples. No independent evals exist yet.
x.comthreadAdded 26 Oct 2026, published 25 Oct 2026🧠 AI - Draft ERC: Agent Safety Framework (ASF) — attributable adoption of versioned safety specifications
Draft ERC "Agent Safety Framework (ASF)" on Ethereum Magicians (ethereum/ERCs PR #2113). It defines versioned, content-addressed Safety Specifications and on-chain Safety Bindings. A binding records which adopter accepted which pinned spec version for a subject and scope, with named interveners who can suspend, resume or terminate. A pure-registry check() returns Satisfied, NotSatisfied or Unknown, and Unknown never counts as satisfied. Reference consumers ASFGuardedAccount and ASFTaskTenderAdapter come with 73 tests, 47 of them negative.
ethereum-magicians.orgthreadPublished and added 25 Oct 2026🛡️ Security - Draft ERC: Agent Safety Framework (ASF) — a registry of versioned safety specifications and of the scoped, attributable adoption relations that bind agents to them
Agent Safety Framework (ASF) is a draft ERC on Ethereum Magicians that defines two on-chain objects: a versioned, content-addressed Safety Specification and a Safety Binding, in which an adopter pins one spec version for a subject and scope. A registry check() returns Satisfied, NotSatisfied or Unknown. Bindings support derived delegation, and suspensions come in five graded restrictions. Reference consumers are ASFGuardedAccount and ASFTaskTenderAdapter, with 73 tests, 47 of them negative.
ethereum-magicians.orgthreadPublished and added 25 Oct 2026🧠 AI - Draft ERC: Agent Safety Framework (ASF) — a registry of versioned safety specifications and of the scoped, attributable adoption relations that bind agents to them
Agent Safety Framework (ASF) is a draft ERC on Ethereum Magicians for an on-chain registry of versioned, content-addressed safety specifications and of Safety Bindings. A binding records that an adopter accepted one pinned spec version for a subject and scope, with declared enforcement locations, named interveners and a lifecycle (Active, five Suspended restrictions, Terminated). A check(requirement, bindingIds) call returns Satisfied, NotSatisfied or Unknown, and Unknown never counts as satisfied. Reference consumers ASFGuardedAccount and ASFTaskTenderAdapter come with 73 tests, 47 of them negative.
ethereum-magicians.orgthreadPublished and added 25 Oct 2026🛡️ Security - ERC-8468: Agent Safety Framework (ASF)
ERC-8468, the Agent Safety Framework (ASF), is a draft Ethereum standard with two on-chain objects: a versioned Safety Specification and a Safety Binding with suspend, resume and terminate rights. A check() call returns Satisfied, NotSatisfied or Unknown at the moment of effect. Revision 6 has reference contracts, 90 tests and a Sepolia run of 36 transactions in October 2026, and the thread asks reviewers five design questions.
ethereum-magicians.orgthreadAdded 27 Oct 2026, published 25 Oct 2026🧠 AI - ERC-8468: Agent Safety Framework (ASF)
ERC-8468 (Agent Safety Framework, ASF) is a draft Ethereum standard, now at revision 6, for recording which participants accepted which safety requirements for an AI agent, in which version, enforced where, and whether that acceptance is in force now. It defines a versioned Safety Specification, an on-chain Safety Binding with interveners holding suspend, resume and terminate rights, and a check() that returns Satisfied, NotSatisfied or Unknown. The reference guarded account and task-tender adapter passed 90 tests (64 negative) and a Sepolia run of 36 transactions.
ethereum-magicians.orgthreadAdded 27 Oct 2026, published 25 Oct 2026🛡️ Security - Draft ERC: Agent Safety Framework (ASF) — attributable adoption of versioned safety specifications
Agent Safety Framework (ASF) is a draft ERC (ethereum/ERCs pull request #2113) for an on-chain registry that records which participants adopted which versioned safety specification, for what subject and scope, and where it is enforced. It defines two objects (Safety Specification, Safety Binding) and a registry check returning Satisfied, NotSatisfied or Unknown. Two reference consumers and 73 tests (47 negative) are reported, and the post asks the community four design questions.
ethereum-magicians.orgthreadPublished and added 25 Oct 2026🧠 AI  su (@sutdmhy) on X
Kimi K3.1 Pro is a Moonshot AI model, with a high-speed variant, described in a tweet as a mixture-of-experts system of about 2.8 trillion parameters with a 1-million-token context window and multimodal support. The post claims gains in coding, long-horizon agents, 3D modeling (Blender/CAD) and financial research, and says benchmarks come close to Claude Opus 5.5. Full open weights are planned by November 4. The post gives no benchmark figures.
x.comthreadAdded 26 Oct 2026, published 25 Oct 2026🧠 AI Prasenjit Sarkar (@stretchcloud) on X
Post explaining Claude's new support for MCP Tasks and Elicitations. A server returns a durable task handle instead of blocking. The client polls tasks/get every 250 ms to 30 s, and states are working, input_required, completed, failed or cancelled. Elicitations pause a task at input_required for human approval. It also notes Cloudflare's stateless MCP servers and Code Mode, and Sentry and Linear adoption.
x.comthreadAdded 25 Oct 2026, published 24 Oct 2026🧠 AI- Prasenjit Sarkar (@stretchcloud) on X
Post on the LiteLLM supply-chain compromise. Attackers spent eleven days in the GitHub org, ran a workflow on a throwaway branch to take twenty secrets including a GitHub App private key, then used stolen GitHub CLI OAuth tokens to publish malicious release 1.107.0 from a lookalike Berri-AI repo. A Python startup file harvested sixteen credential categories and LiteLLM proxy Postgres provider keys. Socket flagged the wheels in seven minutes.
x.comthreadAdded 26 Oct 2026, published 24 Oct 2026🛡️ Security - AI Quanting (@AIQuanting) on X
AI Quanting's X thread covers Moonshot's Kimi K3.1 Pro release (1M-token context, open weights promised by November 4). Moonshot removed cyber data from mid-training and RL stages; on its in-house xdev-bench-hard exploit benchmark (Linux kernel, Node.js, JavaScriptCore, Exim, VirGL bugs) pass@3 fell from 90.5% to 81.0%. The author argues this is only about a tenth of the capability, so four in five expert exploit tasks remain solvable.
x.comthreadAdded 25 Oct 2026, published 24 Oct 2026🛡️ Security  Hajrë Hyseni | AI for Business (@hajra) on X
Kimi K3.1 Pro is a new model from Moonshot AI. According to a post by hajra, Artificial Analysis ranks it 4th in the world, 3 points behind Claude Opus 5.5. The API price is down by a third, and full open weights are promised by 4 November. The post gives no benchmark breakdown, licence or architecture details.
x.comthreadPublished and added 24 Oct 2026🧠 AI- Big Bull (@BIGBULLapp) on X
A post by BIGBULLapp on X about a TensorBlock GitHub index of Model Context Protocol servers, described as a TypeScript list so agents call tools someone has already wired up. It cites 1470 forks, 943 stars and 15 open issues. The author notes that curated lists go stale when a server changes its schema. The repository name is truncated in the post.
x.comthreadAdded 24 Oct 2026, published 23 Oct 2026🧠 AI  Rafter (@RafterSecurity) on X
Railway security incident update of 23 October 2026, posted by Rafter Security, summarising Railway's preliminary report on the 20-22 October breach. Up to 1.85% of workspaces (about 100,000) may have had environment variables exposed. Attackers reportedly targeted AI provider API keys, possibly for model distillation. Some encrypted secrets were accessed and a subset decrypted. Railway says the attacker was removed by 22 October at 03:32 UTC, and the forensic investigation continues.
x.comthreadAdded 25 Oct 2026, published 23 Oct 2026🛡️ Security












Showing 60 of 224
Show more