 CVE-2026-101767: Critical Oracle EBS SQL Injection Actively Probed in the Wild
CVE-2026-101767 is a CVSS 9.8 unauthenticated SQL injection in Oracle E-Business Suite's Application Object Library, reachable through the /OA_HTML/AppsTCFServer servlet (GanttDataServer) and chainable to OS command execution. It affects versions 12.2.3 to 12.2.15 and was fixed in the October 2026 Critical Patch Update. Horizon3.ai found it, and Defused saw probing on honeypots on 27 October 2026. Interim mitigation is removing the servlet from the URL firewall allowlist.
 orca.securityadvisoryPublished and added 28 Oct 2026🛡️ Security
- Hitachi Energy CoreTec Product
CISA advisory ICSA-26-302-03, republished from Hitachi Energy PSIRT 8DBD000258, covers OS command injection (CVE-2026-13162) and the Dirty Frag vulnerability (CVE-2026-43284) in Hitachi Energy CoreTec. CoreTec5 up to 3.4.0 and 5.0.0 are affected by both, and CoreTec4 up to 3.4.0 by CVE-2026-13162. The advisory was released 27 October 2026 and lists generic ICS mitigations. SSVC rates exploitation as none.
 cisa.govadvisoryAdded 29 Oct 2026, published 28 Oct 2026🛡️ Security
- Dark Web Intelligence (@DailyDarkWeb) on X
CVE-2026-114625 is a critical (CVSS 3.1 9.9) SQL injection in on-prem Arista VeloCloud Orchestrator, the SD-WAN management portal, covered in Arista Security Advisory 0199 of 22 October 2026. Any authenticated user, even the lowest Enterprise Read Only tenant role, can become a local superuser operator, and Arista says it is exploited in the wild. On-prem fixes are 5.2.3.18, 6.1.3.10 and 6.4.2.12; two attacker IPs are listed.
 x.comadvisoryAdded 24 Oct 2026, published 22 Oct 2026🛡️ Security
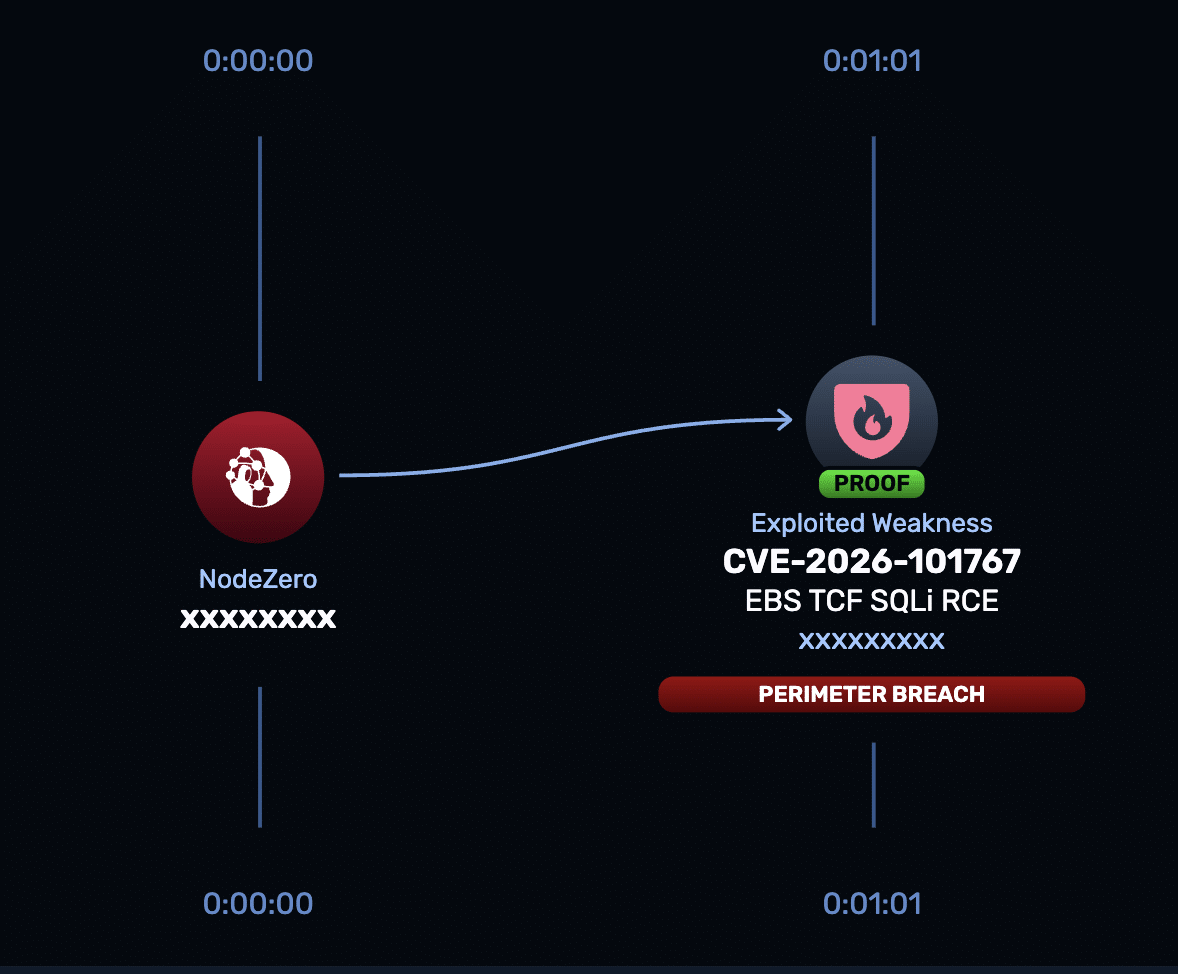 CVE-2026-101767 | Oracle E-Business Suite TCF SQL Injection and Remote Code Execution
CVE-2026-101767 is an unauthenticated SQL injection in the Oracle E-Business Suite Thin Client Framework servlet (/OA_HTML/AppsTCFServer, oracle.apps.fnd.tcf.SocketServer), CVSS 3.1 9.8. It runs SQL as the APPS user and chains to OS commands as the EBS account. Affects 12.2.3 to 12.2.15, fixed in the Oracle October 2026 CPU (20 October 2026). The page lists mitigations, IOCs and a timeline.
 horizon3.aiadvisoryAdded 29 Oct 2026, published 20 Oct 2026🛡️ Security
- lee1981 (@lee1981b) on X
CVE-2026-106931 is an OS command injection (CWE-78) in the statistics processing of EG Secure Solutions SiteGuard Server Edition, a host-based WAF. It can give root or SYSTEM command execution. The vendor and JVN confirm exploitation on 14 October 2026. The post lists fixed builds (Ver8.00 Update 5, Ver7.00 Update 6 on FreeBSD), the IIS exclusion, the workaround of disabling statistics, and a SOC trail starting with diagnostic preservation before patching.
x.comadvisoryAdded 21 Oct 2026, published 19 Oct 2026🛡️ Security - Dark Web Intelligence (@DailyDarkWeb) on X
Summary of SAP's October 13, 2026 Security Patch Day (16 new notes, 4 GitHub advisories). It leads with CVE-2026-89111, a CVSS 10.0 OAuth2 SSRF in SAP Cloud SDK for Python before 0.45.2, where an attacker-controlled tenant_subdomain redirects token requests and exfiltrates client credentials. It also lists three other critical flaws: broken access control in NetWeaver Visual Composer, code injection in S/4HANA substitution/validation rules, and a missing authorization check in the Manufacturing Integration and Intelligence (XMII) Configuration Service. It notes that none are in CISA KEV and SAP reports no in-the-wild exploitation.
x.comadvisoryAdded 15 Oct 2026, published 13 Oct 2026🛡️ Security  GPT-6 Sol and GPT-6 Luna: October 2026 update
OpenAI's system card accompanying the October 2026 ChatGPT rollout of GPT-6 Sol and GPT-6 Luna, replacing GPT-5.6 Sol and Luna for free and paid users (Codex and ChatGPT Work retain the September versions). It details Preparedness Framework results (High capability in Cybersecurity and Biological/Chemical domains, below High in AI Self-Improvement), multiturn jailbreak and GPT-Red prompt-injection robustness, alignment evaluations on respecting Auto-review/warnings and deceptive disclosure, hallucination rates, and health/mental-health benchmarks (HealthBench, HealthBench Professional, MentalHealthBench), alongside some noted regressions in self-harm, sexual content, gore and teen (U18) safety categories.
 deploymentsafety.openai.comadvisoryPublished and added 7 Oct 2026🧠 AI
 Threat Brief: NetScaler Zero Days CVE-2026-88771 and CVE-2026-88772 Exploited in the Wild (Updated September 30)
Unit 42 threat brief on CVE-2026-88771 (unauthenticated command injection) and CVE-2026-88772 (DTLS memory overflow) in NetScaler ADC and Gateway, both CVSS v4.0 9.5 and exploited as zero-days from August 2026. It details version fingerprinting, .deb and PHP web shells, a three-stage log-poisoning chain through ns_monuploadd_err.pl, httpd.conf persistence, IOCs, and 50,277 exposed instances as of 27 September 2026.
 unit42.paloaltonetworks.comadvisoryAdded 30 Oct 2026, published 30 Sep 2026🛡️ Security
- Addendum to GPT-6 Astra System Card: GPT-6.1 Sol
OpenAI's system card addendum for GPT-6.1 Sol, a fast and affordable model in the GPT-6 family with capabilities comparable to GPT-6 Astra, reports Preparedness Framework determinations (Critical cybersecurity, High biological and chemical capability, sub-High AI self-improvement) and the same safeguards stack as Astra. It details extensive safety and alignment evaluations including safe-completion benchmarks, jailbreak and prompt-injection robustness, HealthBench and MentalHealthBench scores, deceptive-behavior and monitor-evasion tests, and chain-of-thought monitorability and controllability results, comparing GPT-6.1 Sol against GPT-6 Astra, GPT-6 Sol, GPT-6 Luna, and the GPT-5.6 series.
deploymentsafety.openai.comadvisoryAdded 7 Oct 2026, published 29 Sep 2026🧠 AI  Zero-Day Exploitation of Citrix NetScaler ADC and Gateway: CVE-2026-88771 and CVE-2026-88772
Rapid7 details active zero-day exploitation of two critical Citrix NetScaler ADC/Gateway RCE vulnerabilities (CVE-2026-88771, CVE-2026-88772, both CVSSv4 9.5), both added to CISA KEV on disclosure day, plus a later SAML denial-of-service zero-day (CVE-2026-88779). The post includes Rapid7 MDR's observed exploitation of CVE-2026-88771 in the wild — a command-injection payload that exfiltrates /flash/nsconfig (containing ns.conf admin credentials, SSL private keys, SSH host keys) via the publicly-served /vpn/ path, and a webshell (SHA256 hash provided) found on a compromised appliance — along with vendor patch versions and detection guidance.
 rapid7.comadvisoryAdded 7 Oct 2026, published 28 Sep 2026🛡️ Security
- Kong Konnect MCP server: stored prompt injection via analytics data leads to credential/data exfiltration (CVE-2026-13341)
GitHub Security Advisory (CVE-2026-13341) for Kong's mcp-konnect MCP server describes a stored prompt injection vulnerability where a remote attacker crafts malicious request metadata (e.g. User-Agent) that gets stored in Konnect analytics and later returned unsanitized to an AI assistant via MCP tools, potentially causing the agent to exfiltrate sensitive data (plugin configs, secrets, internal hostnames) to an attacker-controlled URL if the client can make outbound fetches. A related path manipulation flaw in control plane/group identifiers allowed requesting unintended Konnect API endpoints with the user's token. The v1.0.0 patch neutralizes untrusted analytics fields, validates identifiers as UUIDs, encodes path segments, and disables raw plugin config output by default.
 github.comadvisoryAdded 26 Sep 2026🛡️ Security
- CVE-2026-90617 in PentestAgent
VulDB entry for CVE-2026-90617, a remote OS command injection (CWE-78) in GH05TCREW PentestAgent. The flaw is in run_task in interface/main.py of the MCP HTTP Server, affects everything up to commit cf882dab, and has a public exploit. The product uses rolling releases, so no version ranges exist, and the fix is an unmerged pull request. The analysis suggests compensating controls: restrict network access to the MCP server, run with least privilege, and validate input upstream.
 vuldb.comadvisoryAdded 26 Sep 2026🛡️ Security
- CVE-2026-85787 in postgres-mcp-server
CVE-2026-85787 affects awslabs postgres-mcp-server before 1.1.7. The SQL validation component uses an incomplete list of disallowed inputs. Crafted SQL placed in content submitted while an authenticated user interacts with the MCP server can bypass the read-only restriction and modify data in PostgreSQL. The fix is to upgrade to 1.1.7 or later. VulDB's added analysis is generic: it points to SQL injection (CWE-89) and recommends least-privilege database accounts and parameterized queries.
vuldb.comadvisoryAdded 26 Sep 2026🛡️ Security - CVE-2026-75130: Context7 through 2
CVE-2026-75130 describes a prompt injection flaw in Context7 (through v2.1.2), an MCP server that serves library documentation to AI coding agents. The vulnerability lies in the Custom AI Instructions feature, which fails to sanitize content before injecting it into agent context; attackers can poison these instructions so that a routine documentation lookup triggers the agent to exfiltrate credentials from environment files and delete files on the victim's machine. Researchers at Noma Security and VulnCheck published independent technical breakdowns of the attack chain.
 nvd.nist.govadvisoryAdded 26 Sep 2026🛡️ Security
- CVE-2026-65056: mcp-webresearch 0
CVE-2026-65056 describes a server-side request forgery in the mcp-webresearch MCP server (npm package @mzxrai/mcp-webresearch, v0.1.7), scoring CVSS 4.0 8.3 HIGH. The visit_page tool only validates URL protocol and does not filter private, loopback, link-local, or cloud metadata IP ranges, so an attacker who controls the LLM-supplied URL argument (e.g. via prompt injection) can steer the server's Playwright browser to internal endpoints like cloud instance metadata services and exfiltrate sensitive internal content, including credentials, back into the model context.
nvd.nist.govadvisoryAdded 26 Sep 2026🛡️ Security - CVE-2026-19978: A flaw has been found in jiantao88 android-mcp-server up to cfb872b2446794193b58edd63f4dbf6af48a6292
CVE-2026-19978 describes an OS command injection (CWE-77/78) in jiantao88's android-mcp-server, where the child_process.exec call in build/index.js fails to sanitize the deviceId, packageName, permission, and extras[].key/value arguments used to control Android devices. The flaw allows local command execution and has a published exploit; it was fixed in commit 14e2bf27c88ba137e35cbb0c2a75f72b595bb98a. CVSS 4.0 base score is 1.9 (local attack vector only), and the project uses rolling releases so no fixed version numbers are assigned.
nvd.nist.govadvisoryAdded 26 Sep 2026🛡️ Security - CVE-2026-18655: Improper restriction of intended endpoints in the RabbitMQ broker connection tools of the Amazon MQ MCP Server (awslabs
CVE-2026-18655 describes an improper endpoint restriction flaw (CWE-923) in the RabbitMQ broker connection tools of awslabs.amazon-mq-mcp-server versions before 2.0.24. A remote unauthenticated attacker can use prompt injection introduced into the MCP client context to redirect the broker hostname to an attacker-controlled endpoint, causing Amazon MQ for RabbitMQ credentials or OAuth access tokens to be sent there; CVSS 4.0 base score 7.1 (High). Fixed in version 2.0.24, referenced via an AWS security bulletin and a GitHub security advisory (GHSA-xwj6-8x5h-hjp6).
nvd.nist.govadvisoryAdded 26 Sep 2026🛡️ Security - CISA Adds Seven Known Exploited Vulnerabilities to Catalog | CISA
CISA added seven vulnerabilities to its Known Exploited Vulnerabilities Catalog on the basis of active exploitation. They are SQL injection in Sangoma Switchvox, HTTP request/response smuggling in Kludex Starlette, OS command injection in Kestra OSS, improper authentication in BerriAI LiteLLM and JFrog Artifactory, and SSRF plus OS command injection in SonicWall SMA1000 appliances. The alert restates BOD 26-04, which makes federal agencies prioritise rapid remediation of KEV CVEs on publicly exposed assets that grant total control after exploitation. It also requires agencies to check for prior compromise before patching.
cisa.govadvisoryAdded 26 Sep 2026🛡️ Security - CVE-2026-87911 - Read-only enforcement bypass enabling operating system command execution in the SQL validation component of Amazon awslabs postgres-mcp-server
AWS bulletin for CVE-2026-87911, an OS command injection flaw in awslabs.postgres-mcp-server (Python, PyPI) versions before 1.1.7. The server's read-only enforcement in its SQL validation component can be bypassed with a crafted `COPY ... TO PROGRAM` statement, letting an unauthenticated actor run OS commands on a self-managed PostgreSQL host when the configured connection role holds superuser or pg_execute_server_program privileges. Fixed in 1.1.7; AWS also recommends connecting the MCP server with a least-privilege, non-superuser role as defense in depth.
 aws.amazon.comadvisoryAdded 26 Sep 2026🛡️ Security
 Cisco Warns of New Zero-Day ISE Auth Bypass (CVSS 10.0) Exploited in Active Attacks
Cisco disclosed CVE-2026-76460 (CVSS 10.0), an unauthenticated API authentication bypass in Identity Services Engine (ISE) and ISE-PIC that is under active exploitation and has been added to CISA's KEV catalog with a federal patch deadline of September 19, 2026; successful exploitation can yield root command execution, and Cisco provides log-based IOC detection guidance since there is no workaround. The same disclosure batch includes 77 new CVEs, 41 in ISE and 28 in Secure Firewall (ASA/FTD/FMC), covering authenticated RCE, SQL injection, XXE, command injection, and additional REST API auth bypasses, plus a separately exploited Secure Email Gateway flaw (CVE-2026-76461, CVSS 9.8).
 thehackernews.comadvisoryAdded 22 Sep 2026🛡️ Security
- CVE-2026-76461: Critical Cisco Secure Email Gateway Vulnerability Exploited in the Wild
Rapid7's emerging threat response write-up on CVE-2026-76461, a critical (CVSS 9.8) SQL injection vulnerability in Cisco AsyncOS Software for Cisco Secure Email Gateway that allows an unauthenticated remote attacker to achieve root command execution by sending a specially crafted email. Cisco confirmed active zero-day exploitation and the vulnerability was added to CISA's KEV catalog the same day it was disclosed; the post provides mitigation guidance (emergency patching to 16.5.0-780) and a log-grep IOC (searching mail_logs for COPY.*TO PROGRAM) to detect exploitation attempts.
rapid7.comadvisoryAdded 7 Oct 2026, published 15 Sep 2026🛡️ Security - GPT-6 Astra System Card
OpenAI's system card for GPT-6 Astra, the first model to reach "Critical" cybersecurity capability under OpenAI's Preparedness Framework, detailing new safeguards (checkpoint encryption, universal CoT monitoring, blocking alignment evaluations) and a suite of alignment evaluations measuring metagaming, oversight gaming, honeypot exploitation (ExploitGym, tied to a Hugging Face incident), and respect for restrictions like Auto-review. It also reports comparative robustness results against GPT-5.6 Sol on static/multiturn jailbreaks, Gray Swan indirect-prompt-injection benchmarks, HealthBench/HealthBench Professional, under-18 safety evaluations, and hallucination rates, while flagging that Astra's chain-of-thought monitorability has decreased under adversarial conditions. Appendices (added later) cover related models GPT-6 Sol, GPT-6 Luna, and an agent product called "dots" built on Astra. Note: analysis is based on the first 40,000 of 222,175 characters, so later sections (deployment simulations, full appendices) are not reflected here.
deploymentsafety.openai.comadvisoryAdded 7 Oct 2026, published 3 Sep 2026🧠 AI  Agno’s PythonTools Path Traversal: Arbitrary File Access & RCE
CVE-2026-76832 (CVSS 8.8) is a path traversal flaw in Agno's PythonTools, specifically in libs/agno/agno/tools/python.py, where the file_name argument to read_file, save_to_file, and run_python_file is not sanitized against the configured base_dir. An attacker can pass sequences like ../../../../etc/passwd to read or write arbitrary files, and abuse run_python_file to execute an arbitrary Python script for RCE. The advisory notes the flaw is reachable either via direct tool invocation or via prompt injection into agent-processed content, with no PoC or patch published at time of writing.
 thehackerwire.comadvisoryAdded 26 Sep 2026, published 20 Aug 2026🛡️ Security
- CVE-2026-18394 - Incorrect authorization in Strands Agents Tools http_request tool
AWS bulletin for CVE-2026-18394, an incorrect authorization flaw in the http_request tool of the open-source strands-agents-tools package used with the Strands Agents SDK. The tool exposed an LLM-controllable proxies parameter that let attacker-controlled web content (via indirect prompt injection) redirect requests through an actor's proxy while the hostname allowlist check still passed, disclosing HTTP_REQUEST_TOKEN_CONFIG-bound credentials in cleartext Authorization headers on the first hop. Fixed in version 0.8.2; AWS recommends upgrading and rotating any credentials configured on affected versions.
aws.amazon.comadvisoryAdded 6 Aug 2026🛡️ Security - GPT-5.6 — August Updates
OpenAI system card update for the August 2026 release of GPT-5.6 Sol and GPT-5.6 Luna in ChatGPT, reporting safety eval results for disallowed content, new under-18 safety benchmarks, jailbreak and prompt injection robustness, HealthBench scores, and hallucination rates compared to GPT-5.5 Instant. It also reports Preparedness Framework capability testing, rating both models High capability in Biological/Chemical and Cybersecurity domains using evals such as SecureBio virology troubleshooting, ProtocolQA, protein binding prediction, CTF challenges, CVE-Bench, and cyber range exercises, while staying below Critical and below High for AI self-improvement.
deploymentsafety.openai.comadvisoryAdded 7 Oct 2026, published 6 Aug 2026🧠 AI  AI Security Briefing
CVE-2026-14898 affects the OpenAI Codex desktop app for macOS, which automatically renders remote images embedded in Markdown model output without user interaction. An attacker can use indirect prompt injection to make Codex generate a response containing an attacker-controlled image URL whose parameters embed sensitive data (API keys, source code, tool output), which is silently exfiltrated when the app auto-fetches the image. Categorized under CWE-200, no patch or CVSS score was available at disclosure.
 cybersecuritynews.comadvisoryPublished and added 18 Jul 2026🛡️ Security
 AI Security Briefing
GHSA-3pvh-63gf-j9mw discloses an authenticated remote code execution vulnerability in LangBot, an open-source AI chatbot/agent framework, caused by its MCP Server Configuration feature. Because LangBot's mcp.py uses Anthropic's StdioServerParameters to launch MCP servers, any authenticated user can add a "STDIO" MCP entry with an arbitrary shell command and have it executed on the server, enabling data exfiltration, reverse shells, or full host compromise (CWE-78 OS command injection).
github.comadvisoryPublished and added 17 Jul 2026🛡️ Security- CVE-2026-61459
CVE-2026-61459 describes an argument injection flaw (CWE-88) in mcp-server-kubernetes before 3.9.0, where the structured tools kubectl_get, kubectl_describe, and kubectl_delete fail to block leading-dash resourceType/name parameters, letting an attacker bypass the assertNoDangerousFlags check and inject a --server flag. This redirects kubectl calls to an attacker-controlled API server, leaking the operator's bearer token and enabling full Kubernetes cluster compromise. Fixed in v3.9.0; details corroborated by a VulnCheck advisory and the upstream GitHub commit/PR.
nvd.nist.govadvisoryPublished and added 12 Jul 2026🛡️ Security - CVE-2026-61447
CVE-2026-61447 describes a critical (CVSS 4.0 score 10.0) remote code execution vulnerability in PraisonAI versions before 1.6.78, rooted in CodeAgent._execute_python(), which runs LLM-generated Python code with no AST validation, import restrictions, or sandbox enforcement. An attacker who can influence the LLM's output via prompt injection can exfiltrate environment secrets and achieve arbitrary code execution on the host, making it a textbook agentic-code-execution flaw (CWE-94).
nvd.nist.govadvisoryPublished and added 12 Jul 2026🛡️ Security - OWASP MCP Top 10 | OWASP Foundation
The OWASP MCP Top 10 (2025) is a living-document taxonomy of the ten most critical vulnerability classes affecting Model Context Protocol-based AI systems, covering issues like token mismanagement, privilege escalation via scope creep, tool poisoning, MCP-specific supply chain and dependency tampering, command injection, prompt injection via contextual payloads, weak authN/authZ, missing audit/telemetry, shadow MCP servers, and context injection/over-sharing. It targets AI/ML developers and security practitioners building agentic, model-chaining, and multi-modal MCP deployments, giving them a common vocabulary and checklist for secure design and auditing analogous to the OWASP Top 10 for LLM Applications.
 owasp.orgadvisoryAdded 3 Jul 2026🛡️ Security
- AI Security Briefing
GHSA-7835-87q9-rgvv discloses a High-severity (CVSS 7.7) flaw in Claude Code's git worktree handling: the CLI allowed creation of worktrees named ".git" and navigation outside the sandbox context, enabling git directory confusion attacks. By combining symlink manipulation with git fsmonitor execution during worktree operations, an attacker could overwrite files like the user's .zshenv to achieve code execution outside the seatbelt sandbox, though reliable exploitation required a victim to clone a malicious repo containing prompt-injection content and run Claude Code against it. The issue was reported via HackerOne by researcher metnew and is fixed in current Claude Code releases.
github.comadvisoryPublished and added 27 Jun 2026🛡️ Security  Orca: CVE-2026-5027 Langflow Path Traversal RCE
CVE-2026-5027 (CVSS 8.8) is a path traversal vulnerability in Langflow's POST /api/v2/files upload endpoint, where the upload_user_file() function fails to sanitize filenames, allowing attackers to write arbitrary files anywhere on the filesystem. Because Langflow ships with unauthenticated auto-login enabled by default, a single unauthenticated request is enough to obtain a session and exploit it, escalating to RCE via cron job injection or config overwrite. Tenable disclosed it after failed vendor contact, VulnCheck has confirmed active exploitation against roughly 7,000 internet-exposed instances, and a public PoC exists; fixed in Langflow 1.9.0/1.10.0 and langflow-base 0.8.3.
orca.securityadvisoryPublished and added 12 Jun 2026🛡️ Security Orca Security: Critical Jupyter Enterprise Gateway Vulnerabilities
Orca Security discloses three critical unauthenticated vulnerabilities in Jupyter Enterprise Gateway's Kubernetes manifest rendering pipeline: CVE-2026-44182 (YAML injection via unsanitized environment variables allowing creation of privileged pods/secrets), CVE-2026-44181 (Server-Side Template Injection via KERNEL_XXX env vars in the Jinja2 rendering path, enabling arbitrary Python/OS code execution), and CVE-2026-44180 (bypass of the _enforce_prohibited_ids control that blocks UID/GID 0 kernels, enabling container escape). All affect versions before 3.3.0 and can lead to full Kubernetes cluster compromise in multi-tenant or internet-facing deployments.
orca.securityadvisoryPublished and added 11 Jun 2026🛡️ Security Orca Security: Critical Unauthenticated RCE in Kopia Backup via SSH ProxyCommand Injection
Orca Security breaks down CVE-2026-45695 (CVSS 9.8), an unauthenticated RCE in the Kopia backup tool's HTTP server, affecting versions 0.22.3 and earlier. The flaw stems from Kopia's /api/v1/repo/exists endpoint splitting SFTP storage configuration fields on literal spaces without a proper tokenizer or quote handling, letting an attacker inject `-oProxyCommand=<cmd>` into the SSH command line when the server runs with --without-password and SFTP/external-SSH enabled — achieving code execution via a single crafted HTTP request. Fix is Kopia 0.23.0, which blocks starting with --insecure/--without-password on non-loopback interfaces; researcher Daniele Berardinelli reported it, tracked as GHSA-2q4c-3mrw-63c3.
orca.securityadvisoryPublished and added 26 May 2026🛡️ Security Orca Security: CVE-2026-9082
Orca Security breaks down CVE-2026-9082, a critical unauthenticated SQL injection in Drupal core's database abstraction API affecting PostgreSQL-backed sites running versions 8.9.0 through 11.3.9. The flaw stems from insufficient query sanitization and can lead to full data exposure, privilege escalation, and in some configurations remote code execution; Drupal has shipped patched releases (e.g. 11.3.10, 10.6.9) and MySQL/MariaDB sites are unaffected by the SQLi itself but should still update for bundled Symfony/Twig fixes.
orca.securityadvisoryPublished and added 22 May 2026🛡️ Security- Careful Adoption of Agentic AI Services
Joint guidance co-authored by ASD's ACSC, CISA, NSA, the Canadian Centre for Cyber Security, NCSC-NZ and NCSC-UK on securing LLM-based agentic AI systems across critical infrastructure and defence. It catalogs agentic-AI-specific risk categories — privilege compromise, scope creep, confused-deputy attacks, identity spoofing, insecure static permission checks, indirect prompt injection, specification gaming and deceptive/emergent agent behaviour — with concrete scenario examples, and lays out best practices for designing, developing, deploying and operating agents securely.
 cyberscoop.comadvisoryAdded 3 Sep 2026, published 13 May 2026🛡️ Security
- CVE-2026-21852 — Claude Code Information Disclosure (pre-trust config injection leaks API keys)
CVE-2026-21852 describes a flaw in Claude Code versions prior to 2.0.65 where a malicious repository's settings file can override ANTHROPIC_BASE_URL and have it applied during project load before the user sees or accepts the trust-confirmation prompt, causing the user's Anthropic API key to be sent to an attacker-controlled endpoint. The root cause is an initialization-order bug (CWE-522, insufficiently protected credentials) where untrusted repo config is parsed and acted on ahead of trust verification; Anthropic fixed it in 2.0.65 by moving trust checks before config processing. Mitigations include updating, rotating exposed keys, and avoiding opening unfamiliar repos until patched.
 sentinelone.comadvisoryAdded 30 Sep 2026, published 21 Jan 2026🛡️ Security
- Ni8mare and N8scape flaws among multiple critical vulnerabilities affecting n8n
Rapid7's ETR write-up on "Ni8mare," an exploit chain against n8n automation software anchored by CVE-2026-21858 (CVSS 10.0), an unauthenticated file read flaw triggered by improper content-type validation on custom webhook file-upload forms that lets an attacker overwrite internal JSON to read arbitrary files and forge admin session tokens. That access can be chained with four authenticated CVEs — CVE-2025-68613 (expression language injection RCE), CVE-2025-68668 (Pyodide Python node command execution), CVE-2025-68697 (legacy Code node file read/write), and CVE-2026-21877 (arbitrary file write RCE, CVSS 9.9) — for full remote code execution. Cyera and researcher Valentin Lobstein published separate technical analyses and PoCs on the same day; Rapid7 lists affected version ranges for each CVE and recommends upgrading self-hosted n8n to 1.121.0+.
rapid7.comadvisoryAdded 26 Sep 2026, published 8 Jan 2026🛡️ Security - CVE-2023-38336: Command injection in netkit-rcp
Writeup by the researcher who reported CVE-2023-38336, a command injection vulnerability in Netkit's rcp implementation (Debian's rsh-client package). The bug is in susystem() in rcp/rcp.c, which passes filename arguments unsanitized to `sh -c`, letting an attacker who controls a copied filename execute arbitrary commands (demonstrated via `ltrace` with a filename like `";whoami"`); the binary is SUID root but drops privileges via setuid() before executing the shell, so the flaw grants command execution as the invoking user rather than root escalation. No patch exists since the project has no upstream maintainer, and the author recommends migrating from RSH to SSH.
 bencteux.fradvisoryAdded 3 Sep 2026, published 18 Jul 2023🛡️ Security


